Categories
Blog

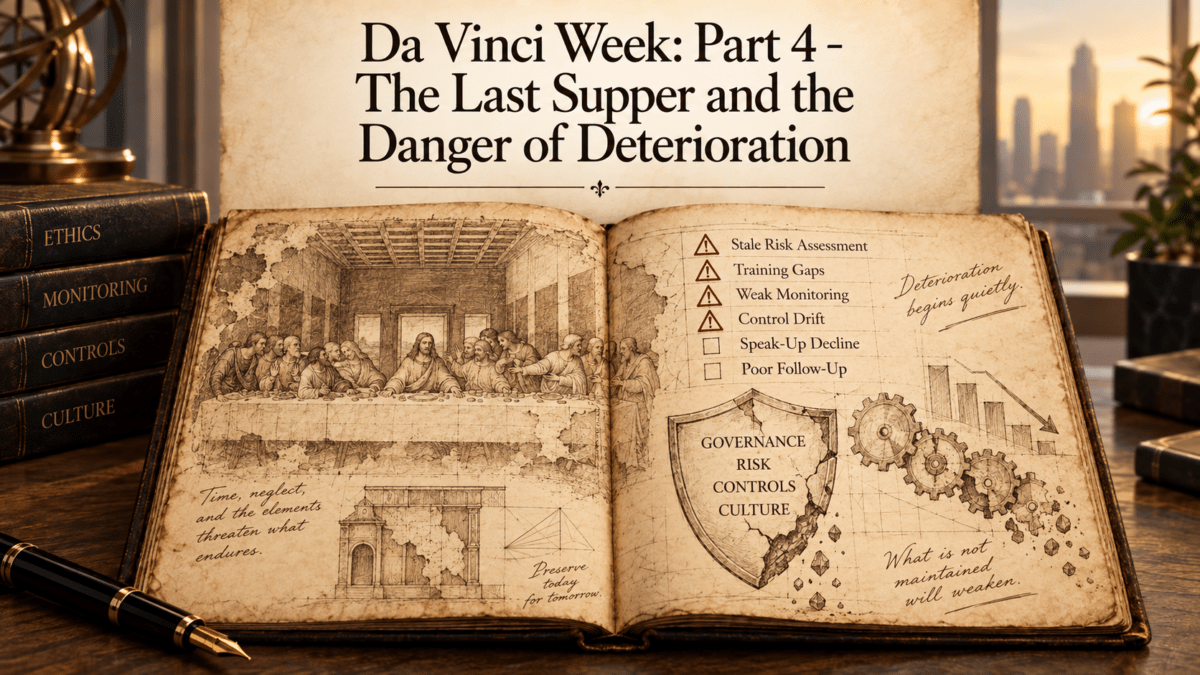
Da Vinci Week: Part 4 – The Last Supper and the Danger of Deterioration

In the previous post in the Leonardo Compliance Framework, Leonardo’s flying machines gave us Innovate, the principle that Compliance should help organizations capture the benefits of emerging technology while establishing governance appropriate to the risks. Yet approving and deploying a new technology, control, or compliance process does not demonstrate that it will remain effective over time. The organization must continue to evaluate whether the system operates as intended as the business and its risk environment change. That brings us to the fourth principle in the Leonardo Compliance Framework: Monitor.

For this lesson, we turn to Leonardo’s The Last Supper. Leonardo experimented with a painting technique that provided greater artistic flexibility than conventional fresco methods. The result was extraordinary, but the physical work proved vulnerable to deterioration, and environmental conditions and later damage compounded those problems.

For compliance professionals, the lesson is not that experimentation was a mistake. It is that implementation marks the beginning of the control lifecycle, not its end. A system that operates effectively when introduced may weaken as people, processes, technology, incentives, and business conditions change. Modern compliance program effectiveness therefore requires more than evidence that a control exists. Management needs evidence that the control continues to work.

Implementation Is Not Effectiveness

Companies appropriately recognize major implementation milestones. A new third-party platform goes live, an updated Code of Conduct is launched, an investigation protocol is approved, or a sanctions-screening system is installed. These accomplishments demonstrate that the organization has taken action, but they do not establish that the underlying risk is being managed effectively.

Consider a third-party due diligence system implemented across a global enterprise. At launch, the workflow operates as designed. Business sponsors submit required information, higher-risk third parties receive enhanced review, approvals are documented, and Compliance can monitor the process. Two years later, an acquisition may have added thousands of vendors, employees may have developed workarounds because they consider the process too slow, regional teams may interpret risk classifications differently, and data feeds may no longer operate consistently. The system still exists, and the policy remains in force, but the control environment has changed.

This is the central monitoring challenge. Controls operate inside dynamic organizations. A gifts and entertainment process may become inadequate when the company enters markets involving greater interaction with government officials. Sanctions controls may require adjustment following significant geopolitical developments. A conflict-of-interest process may become less effective after an acquisition substantially expands the workforce. Controls designed for one business model may no longer fit another.

Effective monitoring should therefore connect directly to risk assessment. When the company’s risk environment changes, management should evaluate whether the controls designed for the previous environment remain appropriate. Successful implementation at one point in time cannot establish continuing effectiveness.

Monitoring and Testing Provide Different Evidence

Compliance professionals should distinguish between monitoring and testing because each provides different information about the control environment. Monitoring is generally continuous or recurring. It observes transactions, trends, exceptions, employee behavior, third-party activity, hotline information, investigation patterns, and other indicators that may reveal changes in risk or control performance. Testing is more focused and determines whether a particular control is appropriately designed and operating as intended.

Consider a control requiring enhanced approval for high-risk third parties. Monitoring may reveal how many high-risk relationships are approved, how long reviews take, which business units generate the most exceptions, and whether particular patterns are developing. Testing may examine a sample of approved relationships to determine whether required due diligence was performed, red flags were resolved appropriately, approvals occurred at the correct level, and documentation supports the final decision.

Monitoring provides signals about what may be changing. Testing provides evidence about whether specific controls perform as expected. Together, they allow the CCO to move beyond control existence and assess effectiveness.

That distinction matters most when presenting compliance information to senior management and the board. Activity metrics may demonstrate that processes are operating, but control testing provides a stronger basis for determining whether those processes are managing the intended risk.

Ownership Turns Monitoring Into Accountability

Monitoring becomes considerably less effective when control ownership is unclear. This is a recurring compliance problem because responsibilities often cross functional boundaries. Compliance may own the policy, Procurement may operate the process, IT may own the technology, Finance may process the payment, and the business may own the commercial relationship. When the control fails, each function may reasonably believe another function was responsible.

Effective control design should therefore identify an accountable owner responsible for ensuring that the control operates as intended. Compliance may provide oversight and challenge, and Internal Audit may provide independent assurance, but first-line functions should understand their responsibility for managing the underlying business risk.

Ownership should extend to the results of monitoring and testing. If testing identifies repeated exceptions, someone must determine whether the process requires modification. If a data feed fails, someone must restore it. If employees routinely circumvent a control, management must address the underlying behavior or process weakness. Monitoring without ownership produces information without accountability. The objective is not simply to identify control deficiencies but to drive a management response.

Use Data to Identify Deterioration Earlier

Data analytics has significantly expanded compliance functions’ ability to identify changes in risk and control performance. Traditional monitoring often depended on periodic reviews of relatively small samples. Modern analytics can help organizations identify patterns across larger populations and, in some circumstances, detect changes earlier.

Payment data may reveal unusual transaction patterns, while procurement information can identify repeated overrides or vendor concentrations. Third-party data may identify expired due diligence or changes in risk characteristics. Hotline and investigation data can reveal shifts in allegations and recurring root causes, while HR information may signal retaliation or cultural issues.

The objective is not to collect the greatest possible volume of information or create the most sophisticated dashboard. The purpose is to identify data that help management determine whether risks are changing or controls are weakening. Exceptions are particularly valuable in this respect. An individual exception is not necessarily evidence of misconduct because legitimate business circumstances may justify deviation from a standard process. Patterns of exceptions, however, can reveal important information about the control environment.

If one business unit generates substantially more third-party exceptions than comparable operations, Compliance should understand the reason. Repeated overrides near quarter-end may indicate commercial pressure. Due diligence consistently completed after engagement may indicate that the formal process no longer reflects how the business actually operates.

A mature program should therefore examine the frequency, rationale, approving authority, concentration, and recurrence of significant exceptions. When exceptions become routine, they can create an unofficial alternative process that exists alongside the formal control environment. Data become valuable when they reveal that divergence early enough for management to respond.

Investigations, Monitoring, and Remediation Should Form a Feedback Loop

Investigations provide some of the strongest evidence about how controls operate under actual business conditions. Their findings should therefore influence what a compliance program monitors. If an investigation discovers that employees circumvented third-party controls by classifying consultants as ordinary vendors, remediation should address the immediate classification weakness, while monitoring should examine whether comparable patterns exist elsewhere. If an investigation identifies improper discounts used to create funds for inappropriate payments, transaction monitoring can be adjusted to identify similar discount patterns. If a retaliation investigation reveals adverse employment consequences shortly after an employee raised a concern, a compliance professional could consider whether HR data can identify comparable patterns.

This creates a feedback loop. Investigations explain how a control failed in a particular case, monitoring helps determine whether the same weakness exists elsewhere or is recurring, and remediation addresses the underlying problem. Monitoring has limited value if the organization does not act on what it learns. When testing identifies a significant deficiency, management should understand why it occurred, whether it is systemic, what risk it creates, what corrective action is required, and who owns that remediation. The organization should then validate that the corrective action addressed the weakness.

This last step is important because remediation completion and remediation effectiveness are different concepts. Issuing a revised procedure or completing additional training may satisfy a project milestone without solving the underlying problem. Follow-up testing provides evidence that the remediation worked.

The compliance learning cycle should therefore move from investigation to monitoring, from monitoring to remediation, and from remediation to validation.

AI Requires Continuing Monitoring

AI provides a particularly clear example of why approval and implementation cannot end the governance process. A company may conduct extensive review before deploying an AI application by assessing the vendor, testing the system, evaluating data use, classifying risk, and establishing human oversight. Those steps are important, but the system and its operating environment can change after deployment.

Vendors may update models, employees may develop new uses, data may change, integrations may expand access, and capabilities may increase. For higher-risk applications, monitoring should therefore match the potential consequences. It may include performance testing, incident monitoring, reviewing material overrides, validating outputs, and reassessing after significant changes in functionality or use.

Agentic systems deserve particular attention because monitoring may need to address not only output quality but also the actions a system performs, the permissions it exercises, and whether it remains within its approved authority. The broader principle is the same as for any other compliance control. Governance should continue for as long as the organization relies upon the system.

Culture Also Requires Monitoring

Corporate culture presents a different monitoring challenge because no single metric establishes whether an organization has a strong ethical culture. Hotline reporting rates provide useful information but require interpretation. High reporting may indicate significant problems or employee confidence in the reporting system. Low reporting may reflect a healthy environment or fear of speaking up. Employee surveys provide additional information but capture sentiment at a particular moment, while investigation data reflect only matters that become known.

Compliance should therefore build a broader picture using multiple indicators, including reporting trends, employee surveys, exit interviews, focus groups, disciplinary information, HR data, investigation findings, and management assessments. Changes across these indicators may reveal emerging issues in particular business units, management teams, or employee populations.

Culture monitoring is especially important after leadership changes, acquisitions, restructurings, layoffs, or significant incentive changes because these events can quickly alter employee perceptions and behavior. Formal policies may remain unchanged while the operating culture deteriorates. As with other compliance risks, the objective is not perfect measurement. It is obtaining enough reliable information to identify material changes and respond appropriately.

The Danger of Deterioration

The Last Supper reminds us that implementation captures a moment in time while organizations continue to evolve. Personnel, technology, incentives, business models, markets, and risks change, and controls that once worked can weaken in response. An effective compliance program therefore needs monitoring, testing, clear ownership, useful data, and validated remediation. These disciplines allow the organization to identify deterioration before a control weakness becomes a larger compliance failure.

The practical lesson for the CCO is that implementation should never be confused with effectiveness. Monitoring and testing should provide different but complementary evidence about control performance. Ownership should ensure findings produce action, analytics should identify meaningful changes rather than simply populate dashboards, and remediation should be validated before the organization concludes the underlying problem is solved. That is Monitor, the fourth principle of the Leonardo Compliance Framework. A control deserves continuing confidence only when the organization has continuing evidence that it works.

From Monitoring to Documentation

Monitoring tells the organization what is happening, but institutional learning depends upon preserving what the organization learns. A company may conduct an effective investigation, identify a root cause, redesign a control, test the remediation, and reach a thoughtful risk decision. Yet, much of that value can disappear if the reasoning exists only in the memories of the people involved.

That brings us to the fifth and final Leonardo principle: Document. In Blog Post Five, Leonardo’s Notebooks: Documentation the Defensible Compliance Program, we will use Leonardo’s extraordinary record of observations, drawings, experiments, and ideas to examine documentation as a governance discipline. The discussion will focus on preserving significant compliance reasoning, establishing accountability, creating institutional memory, documenting remediation and AI governance decisions, and ensuring that what the organization learns today remains available to the people responsible for managing its risks tomorrow.
Categories
Blog

The Future of Continuous Monitoring: AI-Driven Compliance is Here to Stay

The compliance function has officially crossed the Rubicon. Artificial intelligence is no longer an experimental technology on the compliance periphery; it is at the center of forward-thinking compliance programs. We are witnessing a seismic shift in managing risk, detecting misconduct, and maintaining corporate integrity. AI enables real-time monitoring, uncovering subtle anomalies, and delivering the kind of automated oversight previously confined to PowerPoint dreams. As we enter 2025, the question is not whether your compliance function should adopt AI but how quickly you can make it central to your operations.

This blog post explores how compliance professionals can use AI to power a future-ready, continuously monitored compliance program. Today, we will explore five powerful lessons supported by real-world case examples and framed within current regulatory expectations. As Andrew McBride described, we are entering the “Holy Grail” era of compliance, where due diligence, internal and external data, and communications can be monitored holistically through AI agents trained to detect abnormalities and investigate unethical behavior.

Lesson 1: AI Enhances Risk Detection

AI doesn’t just speed up compliance; it sharpens it. Traditional compliance teams have long struggled to keep up with massive amounts of structured and unstructured data. From financial transactions to email threads, vendor records, and chat logs, there are risk indicators that no human team could feasibly monitor in real-time. Enter AI and machine learning.

With natural language processing (NLP), AI systems can read between the lines. They detect shifts in sentiment, keyword patterns, and coded language that may indicate bribery, fraud, or circumvented controls. Matt Galvan emphasizes this as a game-changer, especially when GenAI tools synthesize background due diligence with transactional anomalies to flag red flags early before misconduct manifests.

Better still, AI eliminates the “needle in a haystack” problem. It builds outliers into profiles, detects slush fund behavior, and creates actionable summaries with supporting documentation. You are not simply faster, and you are smarter. But here’s the kicker: the quality of AI outputs depends on the quality of your inputs—poor data = poor detection. AI must be trained on clean, complete, and bias-aware datasets. And AI should never operate in a vacuum. Human judgment remains essential to interpret findings and assess the business context.

The bottom line is that AI transforms compliance from reactive to proactive. It is no longer about catching up; it is about staying ahead.

Lesson 2: Regulators Expect AI-Driven Compliance

If you need a business case for AI, start with the Department of Justice (DOJ) and its 2024 Evaluation of Corporate Compliance Programs (2024 ECCP). The DOJ has moved beyond encouragement and now expects companies to adopt real-time, AI-powered compliance monitoring. Failing to implement these tools could soon be seen as a failure to meet basic compliance standards.

This isn’t just about the DOJ. The SEC, FinCEN, OCC, Federal Reserve Board, and the Financial Action Task Force (FATF) are pushing toward a future where real-time compliance tools are a baseline requirement, not a nice-to-have. What’s more, regulators are now asking companies to explain their AI. What data powers your algorithms? How are decisions made? Can you justify why one transaction was flagged and another was not? Transparency and audibility are no longer optional; they are regulatory imperatives.

Regulators understand that AI can reduce legal risk and enhance oversight. They expect you to understand it, too.

Lesson 3: AI Identifies Emerging Geopolitical Risks

Welcome to the volatility vortex of 2025. What was a low-risk jurisdiction on Friday can be a sanctioned country by Monday. Supply chains bend and sometimes break under the weight of sanctions, tariffs, and political upheaval.

Traditional compliance programs cannot react fast enough. This is where AI earns its keep. AI flags emerging geopolitical risks before they bite by ingesting thousands of data points from news, regulatory alerts, trade databases, and internal procurement systems. Andrew McBride’s example of a virtual bill of materials is especially prescient: imagine knowing exactly where a conflict mineral is buried in your supply chain and being alerted when a regulatory status changes.

AI makes it possible. Galvan pointed out that the same data sets used to optimize supply chains can be re-leveraged for compliance risk analysis. In other words, compliance teams should not operate with less information than procurement or logistics. If you are waiting for geopolitical risk to reach your front door, sadly, you are already behind. AI enables a proactive posture to protect your business from international surprises.

Lesson 4: Automating Compliance Reduces Costs and Increases Efficiency

Efficiency is often an underappreciated outcome of effective compliance. But let’s be clear: automation isn’t just about doing things faster; it is about doing them better and cheaper. AI automates transaction monitoring, scans for real-time anomalies, and triages cases for deeper review. No more relying on random audits or static checklists. AI helps compliance programs scale, especially for global companies managing thousands of vendors and counterparties.

Consider regulatory reporting: AI can automate data collection and reporting preparation, ensuring timely submissions and reducing the burden on internal teams. These efficiencies translate directly into cost savings while improving quality.

McBride’s point about AI-driven NLP catching potential bribery schemes in real-time is a glimpse into what’s already possible. Emails, Teams messages, and Slack conversations are goldmines of risk insight when monitored responsibly and legally. Just-in-time risk flags make compliance not only real-time but also real-impact.

AI is your accelerator if you want a leaner, faster, and smarter compliance function.

Lesson 5: Early Adoption of AI Is a Competitive and Ethical Advantage

Finally, we come to the business case. Early adopters of AI-driven compliance are already reaping the rewards. Not just in regulatory peace of mind but in market leadership.

AI enables transparency, consistency, and accountability. It allows organizations to demonstrate good governance, not just say they care about it. That builds trust with investors, customers, and regulators alike. It also helps embed a culture of integrity. By quickly catching issues and addressing them, AI empowers ethics to be lived, not laminated on a wall. And companies that bake ethics into their business model outperform over the long term.

The inverse is also true: those who delay AI adoption will soon find themselves scrambling to catch up, facing increased regulatory scrutiny and higher costs. The future of compliance is not five years away. It’s now. Organizations that embrace AI today will be tomorrow’s industry leaders in ethics, governance, and profitability.

AI is not simply a tool; rather, it is transformational. It allows compliance professionals to do more, do it faster, and do it better. But success requires more than just buying technology. It requires thoughtful integration, rigorous oversight, and a strategic mindset. Continuous monitoring is the future, and the future has arrived. Together, let us build compliance programs that are not only compliant but also resilient, efficient, and ethical.

The above is from my latest book, Upping Your Game: How Compliance and Risk Management Move to 2030 and Beyond, available from Amazon.com.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – AI Driven Compliance Monitoring

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

We begin a week of looking at how AI can impact your compliance program in 2025. Today, we consider how AI can improve your compliance monitoring.

For more information on the Ethico Toolkit for Middle Managers, available at no charge, click here.

Categories
Blog

AI Game-Changing Compliance: Part 1 – AI-Driven Compliance Monitoring

Last week, I looked at five things a Chief Compliance Officer (CCO) or compliance professional could do at little or no cost to ‘Up Their (Compliance) Game.’ I want to continue this theme this week but want to tackle it differently. I will look at five innovations for compliance professionals around Artificial Intelligence (AI). AI has moved from an emerging trend to a fundamental component of modern corporate compliance programs. Today, we begin with the use of AI for ongoing monitoring.

In 2025, organizations will no longer experiment with AI-driven compliance tools but will embed them into daily operations to monitor transactions, detect anomalies, and flag potential violations in real-time. The shift has been driven by increasing regulatory scrutiny, growing data complexity, and recognizing that traditional compliance methods, such as manual audits and periodic risk assessments, are no longer sufficient to address today’s evolving threats.

One of the most significant innovations in AI-powered compliance is using machine learning algorithms to analyze vast amounts of financial, transactional, and communications data. These tools can detect patterns of misconduct that would be nearly impossible for human reviewers to identify. AI-driven systems are particularly effective in identifying red flags associated with bribery, fraud, money laundering, and insider trading. For example, financial institutions such as JPMorgan Chase have implemented AI-based surveillance systems that analyze trader communications and transaction records to detect potential misconduct before it escalates.

Beyond monitoring, AI is transforming how organizations conduct internal investigations. Generative AI tools can now analyze employee emails, chat logs, and phone transcripts to identify risk-related language and patterns of unethical behavior. These tools can generate initial investigative reports, summarize key findings, and suggest next steps for compliance teams, significantly reducing the time and effort required to conduct in-depth inquiries. This capability is particularly valuable in responding to whistleblower complaints, as it enables companies to quickly assess a report’s credibility and determine whether further action is needed.

From a regulatory perspective, enforcement agencies are also embracing AI and, in turn, expecting corporations to do the same. No matter what might happen to the Department of Justice (DOJ) 2024 Evaluation of Corporate Compliance Programs (ECCP), this document clarified the importance of data-driven compliance monitoring. The bottom line is that regulators worldwide now expect companies to leverage advanced analytics and AI-driven tools to proactively identify misconduct rather than relying solely on traditional audit-based detection methods.

Lessons for Compliance Professionals

  1. AI is a Compliance Enabler, not a Replacement for Human Oversight. While AI can significantly enhance risk detection and investigative efficiency, it is not a substitute for experienced compliance professionals. Organizations must implement AI with human oversight and contextual analysis to assess and address flagged risks properly.
  2. Regulators Expect AI-Driven Compliance, and Ignorance is No Longer an Excuse. No matter what the Trump Administration would do to eviscerate the FCPA, the DOJ, and other enforcement agencies increasingly view AI-based monitoring as a best practice. Companies that fail to invest in these tools may be disadvantaged in regulatory investigations.
  3. Data Integrity and Bias Mitigation are Critical. AI models are only as effective as the data they are trained on. Compliance teams must ensure that their AI systems are not reinforcing biases or producing false positives that could lead to unnecessary investigations or missed risks.
  4. AI Can Improve Whistleblower Response Times and Investigations. Organizations that integrate AI into their whistleblower response programs can triage reports faster, prioritize high-risk cases, and ensure whistleblowers receive timely feedback, which aligns with the DOJ’s increased focus on whistleblower protections.
  5. Early Adoption Provides a Competitive and Ethical Advantage. Companies that invest in AI-driven compliance now will be better positioned to mitigate risks, meet regulatory expectations, and demonstrate a commitment to ethical business practices. Early adopters will also benefit from cost savings in reducing manual compliance efforts and avoiding costly enforcement actions.

The Future is Here

These lessons are not pie-in-the-sky prognostications but are based on real-world examples of how AI is used in business operations today.

  1. Citi’s AI-Powered Risk Analytics in Anti-Money Laundering (AML) Compliance. Citi has integrated predictive analytics and AI-driven risk assessment models into its AML compliance efforts. Citi’s system can identify potential money laundering activities by analyzing customer transaction histories, social connections, and geographic risk factors before they escalate. These predictive models help compliance officers prioritize high-risk cases and focus on investigating the most likely sources of financial crime. The result is a more efficient and effective AML compliance program, reducing false positives and improving regulatory compliance.
  2. Walmart’s Predictive Supply Chain Risk Management. Walmart uses predictive analytics to identify compliance risks within its global supply chain. By analyzing supplier performance data, shipment delays, and external risk factors such as weather disruptions, political instability, and labor violations, Walmart can proactively mitigate risks that could lead to regulatory violations or reputational damage. For example, the company can detect early warning signs of forced labor risks or environmental non-compliance and take corrective action before an issue triggers an investigation.
  3. Lockheed Martin’s Predictive Cyber Risk Modeling. Lockheed Martin has developed a predictive analytics framework for cybersecurity compliance. The company’s system uses machine learning algorithms to assess network traffic, employee behaviors, and external threat intelligence sources to predict potential cyberattacks before they occur. This predictive approach enables compliance teams to implement targeted security measures, ensuring compliance with strict defense industry regulations such as NIST 800-171 and the Cybersecurity Maturity Model Certification (CMMC).
  4. Pfizer’s Predictive Analytics for Drug Compliance and Pharmacovigilance uses predictive analytics to ensure regulatory compliance in drug development and distribution. The company’s models analyze clinical trial data, patient feedback, and adverse event reports to predict potential medication safety issues before regulatory agencies intervene. This proactive approach helps Pfizer stay ahead of FDA compliance requirements, minimize risks of drug recalls, and protect patient safety.
  5. Uber’s Predictive Risk Model for Regulatory Compliance has implemented predictive risk assessment models to monitor driver compliance with safety and licensing regulations across different jurisdictions. By analyzing driver behavior, customer complaints, and local regulatory trends, Uber can predict which regions will likely impose stricter regulations or where driver misconduct risks may increase. This allows the company to proactively adjust its compliance strategy, update policies, and strengthen enforcement measures before facing regulatory penalties.
  6. General Electric’s Predictive Compliance for Industrial Safety. GE has integrated predictive maintenance and compliance analytics into its industrial equipment operations. GE can predict when equipment failures or safety violations might occur by analyzing sensor data from turbines, jet engines, and manufacturing plants. This ensures regulatory compliance with occupational safety and environmental laws, reducing workplace accidents and avoiding hefty regulatory fines.

Predictive Compliance is a Game-Changer

The bottom line is that these examples demonstrate that predictive analytics is not just a theoretical concept; it is actively transforming compliance programs across industries. From financial institutions and global supply chains to healthcare, cybersecurity, and industrial safety, businesses use AI-powered insights to anticipate compliance risks and take proactive action.

The era of AI-powered compliance has arrived, and organizations that fail to embrace it risk being left behind. By leveraging AI-driven monitoring, predictive analytics, and investigative tools, compliance teams can enhance their ability to detect and prevent misconduct, streamline investigations, and strengthen their overall compliance posture. As regulators continue to raise expectations, companies must view AI not as a futuristic concept but as an essential component of a modern, proactive compliance regime.

Categories
FCPA Compliance Report

Scott Garland on Sanctions, Cyber, Fraud, and Ethics Compliance & Monitoring at AMI


In this episode of the FCPA Compliance Report, I am joined by Scott Garland, Managing Director, Sanctions, Cyber, Fraud, and Ethics Compliance & Monitoring at Affiliated Monitors, Inc. Some of the areas we discuss include Garland’s professional background and current role. We look at some of his work at the DOJ including his role as the Deputy Chief, National Security Cyber Specialist and his work as Office’s Professional Responsibility Officer. We discuss his move to AMI and the types of monitorships Garland hopes to work on, as well as his thoughts on the role of a monitor. We conclude with some of Garland’s top recollections from UM Law School.
Resources
 Scott Garland bio on AMI.
Affiliated Monitors Inc.

Categories
Digging Deeper

Digging Deeper Episode 9: From Hurricane Sandy to a Pandemic – The Role of Integrity Monitoring


When natural disasters or crises hit, governments deploy resources rapidly to try remediating current or to mitigate future damage. But who watches where the money goes? Tejah Duckworth spent the early part of her career in the public sector, notably overseeing Rapid Repairs Program in NYC after Hurricane Sandy. She took lessons from the public sector and now uses them in the private sector, most recently helping governments monitor pandemic-related funds.

In this episode, Tejah shares some of the key stories from her career and the role of integrity monitoring. Tune into Digging Deeper, episode 9 to hear more.
Listen to more episodes of Digging Deeper:

Digging Deeper, an investigative podcast series by K2 Integrity, helps shine a light on the investigations industry as few can: via the real-world, exceptional practitioners who, day in and day out, conduct this work across sectors and around the globe. Listen in to each episode where guests explore unique cases and share what they uncovered along the way to crack the code for clients. Learn more by clicking here, or subscribe on Apple Podcasts, SoundCloud, Spotify or Stitcher. 
 

Categories
The Affiliated Monitors Expert Podcast

Proactive Monitoring in Healthcare


In this episode we discuss how an independent integrity review can be helpful for organizations that may be facing actual or potential compliance issues. We consider some of the following are whether an independent integrity review and monitoring be helpful where a healthcare organization may have reason to believe it has an actual or potential compliance problem, but has not yet been subject to an enforcement action or a corporate integrity agreement imposed by the government? How can engaging an independent integrity monitor help an organization in dealing with an enforcement agency? Why do government enforcement and regulatory agencies prefer not to exclude important health care providers who have compliance issues?

Categories
31 Days to More Effective Compliance Programs

Monitoring of third-parties


How can data analytics be used for continuous improvement where the primary sales force used by a company is third-parties? A clear majority of FCPA violations and related enforcement actions have come from the use of third-parties. While sham contracting (i.e., using a third-party to conduit the payment of a bribe) has lessened in recent years, there are related data analysis that can be performed to ascertain whether a third-party is likely performing legitimate services for your company. There are several more analytics that can be run in combination to identify suspicious third-parties and some of the simplest can be to look for duplicate or erroneous payments, all of which can lead to continuous improvement. Here we focus on the question posed by the 2019 Guidance, How does the company monitor its third parties?
The final concept of finding patterns that can be discerned through the aggregation of huge amounts of transactions, is the next step for compliance functions. Yet data analysis does far more than simply allow you to follow the money. It can be a part of your third-party ongoing monitoring as well by allowing you to partner the information on third-parties who might come into your company where there was no proper compliance vetting. The opportunity for continuous improvement through a feedback loop is obvious and a clear step you should take going forward.
 Three key takeaways:

  1. Always remember to follow the money to see where a pot of money could be created to fund a bribe.
  2. Transaction monitoring techniques around fraud monitoring translate to data analysis for compliance.
  3. Do not forget to check names against known PEP and SDN lists.
Categories
FCPA Compliance Report

Emerging Issues in Healthcare Compliance and Monitoring-Episode 1–Focus on Opioid Prescribing – Regulatory and Liability Risks

In this special five-part podcast series, sponsored by Affiliated Monitors, Inc., I visit with AMI Managing Director Jesse Caplan on emerging issues in healthcare compliance and monitoring. Healthcare provider organizations and practices face many different types of potential regulatory and liability risks – in this first episode we focus on the risks posed by opioid prescribing. We consider the some of the following issues: 

What are the risks to providers and health care organizations from opioid prescribing? 

  1. Policymakers and the healthcare industry are trying to address the opioid crisis in a number of different ways. One of those ways is to focus on the prescribing of opioids, with the goal of significantly reducing the number of people who are prescribed opioids and become addicted or who divert legally prescribed drugs. 
  2. Health care providers who engage in inappropriate opioid prescribing are increasingly subject to discipline by professional medical boards. They face restrictions on their licenses to practice, and in certain cases, have had their licenses suspended or revoked. 
  3. Where patients are harmed, providers face civil medical malpractice liability.
  4. And in the most egregious cases, providers have been prosecuted criminally, either under the federal Controlled Substances Act or state criminal laws. 

What has been the response of the Department of Justice? 

  1. The Department of Justice (DOJ), both in Washington and in individual United States Attorney’s Offices, have become more aggressive at identifying providers with problematic or suspicious opioid prescribing records.
  2. For example, in 2017, then Attorney General Jeff Sessions announced the formation of the Opioid Fraud and Abuse Detection Unit.In his announcement the Attorney General stated DOJ would use data analytics to identify physicians who are writing opioid prescriptions at a rate that exceeds other physicians, and how many of a doctor’s patients died within 60-days of an opioid prescription.
  3. In 2018, US Attorneys in Massachusetts and Georgia sent warning letters to physicians who had relatively high opioid prescribing histories, or physicians who may have had a patient die from an overdose, or who died for any reason within two-months of being prescribed opioids.
  4. In the letters in Massachusetts, the US Attorney reminded the physicians that prescribing opioids without a legitimate medical purpose or in excessive amounts is illegal. Of course, this begs the question:  for physicians who genuinely care about their patients and are trying to treat real chronic pain, how do they ensure they are prescribing for a legitimate medical purpose or diagnosis where opioid treatment is both indicated and appropriate?  What dosages or number of pills is “an excessive amount” that could put the physician at legal jeopardy?  

What are legislators and regulators doing to address the opioid crisis? 

  1. The crisis has resulted in new laws and regulations addressing hospital staffing, their discharge and treatment processes, limits on the quantity and dosages of opioids that can be prescribed, and mandated use of state Prescription Drug Monitoring Program databases (PDMPs).   
  2. Just this February, CMS issued a letter to all Medicare providers with what they call their “roadmap”, focusing on “preventing new cases of opioid-ise disorder,” “treating patients with opioid use disorders,” and “using data to target prevention and treatment activities.” 
  3. As a result of this evolving legal environment, individual physicians and physician extenders, group practices, hospitals, and even insurance companies who are increasingly employing physicians, face significant regulatory and liability risks if they are engaging in inappropriate and dangerous opioid prescribing practices, or not complying with the increasingly complex prescribing laws and regulations. 

What is the legal and regulatory framework impacting opioid prescribing?

  1. There are a number of federal and state laws impacting opioid prescribing practices. Some of the more recent and significant developments include state laws limiting the quantity and dosage of opioids that can be prescribed and requiring providers to use and check PDMP databases before prescribing certain drugs to a patient.  There are also more sophisticated guidelines for practitioners, including CDC Guidelines, for prescribing opioids, which are becoming the standard of care for prescribers. 
  2. For example, just about every state has a PDMP, which is a database that tracks a patient’s history of opioid prescriptions.Increasingly, states require providers to check the PDMP before prescribing opioids.  By checking the PDMP the physician can be informed whether the patient appears to have an addiction problem, may be doctor-shopping for opioid prescriptions, may be diverting drugs, or might be at risk for dangerous drug interactions. 
  3. More and more states are passing laws limiting the quantity or dosage of opioids prescribed. For example, Massachusetts, the first state to pass such a law in 2016, set a seven-day limit on initial opioid prescriptions. 
  4. The CDC’s Guidelines are targeted to primary care physicians treating adult patients for chronic pain and are designed to improve communications between providers and patients about the benefits and risks of using opioids, and ultimately to reduce opioid addiction and overdoses.  According to the CDC, the three main principles behind the Guidelines are:
  5. Non-opioid therapy is preferred for chronic pain in most circumstances;
  6. The lowest possible effective dosage should be prescribed; and
  7. Clinicians should always exercise caution when prescribing opioids and should closely monitor their patients who have been prescribed opioids.
  8. The CDC then offers 12 separate recommendations addressing each of these principles.

What should be the primary compliance concerns for healthcare organizations in connection with the opioid crisis?

  1. The big questions for healthcare organizations are:
  2. Do you have policies and procedures in place to ensure that your staff, and particularly your physicians, are aware of all the new requirements for opioid prescribing?
  3. Have your providers and staff been educated in those policies and procedures?
  4. And are they actually following appropriate opioid prescribing practices, and all relevant laws and regulations, including the organization’s own prescribing polices? 

Join us for Episode 2, where we discuss how healthcare organizations can identify and mitigate the risks from opioid prescribing.
For more information on Affiliated Monitors, check out their website here.