Categories
Blog

Modern Philosophers and Compliance: Part 2 – Simone de Beauvoir and the Conditions for Ethical Action

This week we will conclude our lengthy exploration of the philosophical underpinnings of the modern corporate compliance program. We have looked at Hannah Arendt and her concepts around personal responsibility and how they relate to the modern compliance program. We will look at John Rawls and institutional justice and fairness in a corporate compliance program; Jürgen Habermas and the governance of speaking up and Hans Jonas and the responsibility for the future of corporate compliance. Today we continue by looking at Simone de Beauvoir and the conditions for ethical action in a corporation.

A company that asks employees to act ethically must examine the conditions under which they make decisions. An employee may understand the code of conduct, recognize a problem, and know how to report it, yet reasonably fear that speaking up will jeopardize a livelihood. That fear is a governance issue. Simone de Beauvoir helps compliance professionals understand why.

In Part 1, Hannah Arendt brought personal responsibility into the corporate approval process. We examined whether individuals exercise judgment when organizational routines encourage deference. Beauvoir takes the discussion further by asking how circumstances affect the ability to act on that judgment. Responsibility matters, and so does the distribution of power around the person expected to exercise it.

For the chief compliance officer, this means examining the distance between what a policy permits and what employees believe they can safely do. A reporting mechanism becomes credible when the company understands that distance and takes concrete steps to reduce it.

Freedom Exists Within Real Circumstances

Beauvoir was a French philosopher whose work explored freedom, responsibility, and oppression. In The Ethics of Ambiguity, published in 1947, she examined human beings as both capable of choosing and constrained by circumstances they did not choose. We pursue our own projects while depending on a world shared with other people. Ethical responsibility includes concern for their freedom as well as our own.

Ambiguity, in this sense, does not make every choice equally acceptable. It describes a condition of human life: we act with limited knowledge and within circumstances we cannot fully control, yet our decisions affect others. We must take responsibility without assuming that a simple formula will resolve every conflict.

In The Second Sex, published in 1949, Beauvoir examined how women had been defined in relation to men and constrained through social expectations, institutions, and material dependence. Her analysis of women as the Other challenged the treatment of one group’s experience as the norm against which everyone else was measured.

The compliance application is an interpretation of these ideas. Beauvoir did not prescribe hotline procedures or investigation protocols. Her work asks us to attend to people’s actual circumstances. Inside a corporation, that means considering who controls pay, work assignments, advancement, and access to decision-makers. Those relationships can shape whether an employee sees an ethical option as practically available.

The Employee Who Knows How to Report

Consider this hypothetical. A junior procurement analyst discovers that a supplier has submitted invoices for services that lack supporting documentation. Her manager directs her to process them before the reporting period closes. He says the supplier is important and that asking further questions will make the department look uncooperative.

The analyst has completed compliance training. She knows the hotline number. She also knows that the manager controls desirable assignments and will soon recommend whether her temporary position becomes permanent. A colleague who challenged him previously lost important responsibilities. She does not know whether that change was retaliatory, but she understands its warning value.

From headquarters, the reporting system appears accessible. From her position, the choice carries immediate economic consequences. The uncertainty about those consequences affects her decision even before anyone makes an explicit threat.

Beauvoir helps us examine that difference. The analyst retains responsibility for her conduct, while management remains responsible for the conditions it creates. Telling her to demonstrate courage leaves the governance problem unresolved. The company must examine how managerial discretion, employment insecurity, and prior experience influence the use of its controls.

For the CCO, this requires asking whose perspective informed the policy. A senior employee with financial security and direct access to legal may experience the same reporting procedure very differently from someone whose continued employment depends on the person named in the concern.

The DOJ Connection Through Trusted Reporting

The Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) examines whether reporting mechanisms are trusted and whether employees feel comfortable using them. It also asks whether organizational practices discourage reporting and whether the company assesses employees’ willingness to raise concerns.

These inquiries create a substantive connection to Beauvoir’s emphasis on circumstances. Publishing a telephone number establishes an available channel. Understanding whether employees can use it requires evidence about their experience. The ECCP’s attention to proactive retaliation prevention reinforces that distinction.

In our hypothetical, the CCO should examine whether the analyst can reach someone outside the manager’s reporting line, whether temporary employees understand the available protections, and how concerns involving powerful managers are routed. The company should also explain the limits of confidentiality. In a small team, the facts themselves may reveal who reported.

An effective response could include an independent contact, a documented protection plan proportionate to the circumstances, and follow-up with the analyst. Those are practical design choices flowing from the identified risk. The organization should explain what it can do and who will act, rather than offer assurances that nobody can reliably deliver.

Whose Experience Shapes the Compliance Program

Beauvoir’s analysis of the Other offers another lesson for policy design. Organizations can mistake the experience of their most influential employees for the experience of the workforce. A policy written around headquarters staff may overlook workers who lack private computer access, work overnight, or depend on a supervisor to interpret company communications.

The ECCP asks about language and other barriers to accessing policies, as well as how the company confirms that employees know where to find them. Compliance professionals can use those questions to investigate whether the program works across different employment conditions.

Review a reporting process with employees who actually use it. Can a warehouse worker obtain guidance without leaving a visible record on a shared terminal? Can an employee working through a staffing agency identify the correct reporting route? Does the policy clearly explain where a concern about a supervisor should go? Answers should inform the design of the process.

This work requires listening without assuming that a category determines someone’s experience. Employees facing similar constraints may make different choices. The objective is to identify specific barriers and address them. Participation in policy testing gives the company evidence that a headquarters review cannot supply.

Protection Must Extend Beyond the Initial Report

A report begins a period of heightened responsibility for the organization. Once the analyst raises her concern, management decisions about her assignments, evaluation, and employment status may require additional scrutiny. The practical risk extends beyond formal dismissal.

Retaliation can take forms that appear routine when viewed separately: exclusion from meetings, reduced access to training, undesirable shifts, or a sudden change in performance assessments. Such actions require fact-specific investigation. Their occurrence after a report does not automatically establish retaliation, but it can justify closer review.

The ECCP examines retaliation policies, training, complaint handling, and follow-up. It also asks whether investigations are independent, objective, appropriately conducted, and documented.[3] A company should translate those expectations into assigned responsibilities for protecting reporters and assessing concerns about adverse treatment.

In our hypothetical, compliance and human resources could arrange an independent review of material employment decisions concerning the analyst during an appropriate monitoring period. The review should consider existing performance evidence and legitimate business reasons. Protection should preserve fair management processes while reducing the risk that discretionary decisions become instruments of punishment.

The analyst should also have a named contact and a realistic explanation of what follow-up to expect. A company can communicate that it has addressed a concern without disclosing confidential personnel information. Silence after intake can leave a reporter uncertain about both the investigation and personal safety within the organization.

Power Must Be Part of the Investigation

Beauvoir’s perspective also changes the questions investigators ask. If the analyst processed unsupported invoices before reporting, the investigation should establish the instructions she received, her understanding of them, the authority she possessed, and the options she believed were available. Pressure is relevant evidence. It does not predetermine the outcome.

Investigators should examine the manager’s conduct with the same care. Did he discourage inquiry? Had employees raised similar concerns? Did commercial targets reward the removal of inconvenient checks? Were previous complaints dismissed because his department delivered strong results?

The ECCP examines whether managers encouraged unethical conduct or tolerated greater compliance risk in pursuit of business objectives. It also addresses consistent discipline and accountability for supervisory failures. These expectations support an investigation that follows power and responsibility through the organization.

A Board should receive enough information to assess whether influential managers are obstructing the program. Relevant reporting might identify repeated concerns within a business unit, unresolved retaliation allegations, or exceptions involving senior personnel. Aggregate results should be interpreted carefully. Few reports can reflect confidence in local management, fear of reporting, or other conditions requiring inquiry.

A useful governance discussion therefore asks what the company knows about the employees least able to challenge authority. The answer should connect employee experience with management action, including who owns unresolved issues and when the board will receive an update.

Five Key Beauvoir Takeaways for the Compliance Professional

  1. Assess the conditions surrounding ethical choices. Examine who controls an employee’s income, assignments, evaluation, and future opportunities. Use that understanding to identify situations where dependence may discourage questions or reporting.
  2. Test policies with employees in different circumstances. Include workers with limited access to technology, language barriers, insecure employment, or little access to senior leaders. Ask them to demonstrate how they would obtain guidance or report a concern.
  3. Treat reporter protection as an assigned responsibility. Establish independent contacts, appropriate follow-up, and proportionate review of potentially adverse treatment. Explain confidentiality limits and avoid promises the organization cannot keep.
  4. Investigate power alongside individual conduct. Determine what instructions, pressures, and authority shaped decisions. Preserve fair accountability for employees while examining the actions and supervisory responsibilities of managers.
  5. Give the board evidence about barriers to ethical action. Report material retaliation risks, repeated concerns involving influential leaders, and progress on corrective action. Explain what remains uncertain and how the company will investigate it.

Beauvoir’s contribution to compliance is practical: ethical expectations must be considered alongside the conditions in which people are asked to fulfill them. The CCO should ask which employees face the greatest personal cost when they follow the code. The board should ask what management has done to reduce that cost.

In Part 3, we turn to John Rawls and the twin concepts of institutional justice and institutional fairness. Having considered responsibility with Arendt and the conditions for ethical action with Beauvoir, Rawls shows a compliance professional how a company can design policies, investigations, and discipline that employees can regard as fair regardless of their position or influence.
Categories
Blog

Modern Philosophers and Compliance: Part 1 – Hannah Arendt and Personal Responsibility in Corporate Compliance

This week we will conclude our lengthy exploration of the philosophical underpinnings of the modern corporate compliance program. We will examine Simone de Beauvoir and the conditions for ethical action in a corporation; John Rawls and institutional justice and fairness in a corporate compliance program; Jürgen Habermas and the governance of speaking up; and Hans Jonas and responsibility for the future of corporate compliance. Today we begin with Hannah Arendt and her concepts of personal responsibility and how they relate to the modern compliance program.

Every approval in a compliance process represents a decision. Someone accepts an explanation, authorizes a payment, resolves a concern, or allows business to proceed. The central question is whether that person understands and takes responsibility for the decision. Hannah Arendt gives compliance professionals a powerful way to examine what happens when organizational routines weaken that connection.

Our examination of ancient and Enlightenment thinkers established the importance of inquiry, ethical habits, institutional order, and evidence. We now turn to twentieth-century philosophy, beginning with responsibility inside complex organizations. Arendt asks us to consider the individual who operates within the system. What happens when that person stops examining the meaning and consequences of the work?

For a Chief Compliance Officer, this question reaches directly into third-party approvals, internal investigations, management conduct, and board oversight. A company can assign responsibilities in a policy while its employees learn to defer judgment to someone else. An effective compliance program must address that gap.

Thinking and Judgment as Compliance Responsibilities

Arendt was a German-born Jewish political thinker who fled Nazi Germany and eventually settled in the United States. Her experiences of persecution and displacement informed her examination of totalitarianism, political life, and personal responsibility. In essays including “Personal Responsibility Under Dictatorship” and “Thinking and Moral Considerations,” she explored the relationship between independent thought, moral judgment, and conduct.

Her account of Adolf Eichmann and the phrase “banality of evil” remain controversial, if not one of the most well-known phrases to describe Nazi Germany. The phrase did not mean that the crimes were ordinary or insignificant. Her interpretation emphasized his failure to think critically about what he was doing, although scholars have challenged her assessment of his motivations. The historical crimes she examined must retain their specificity and gravity.

The compliance application is narrower: institutional roles do not eliminate the need for personal judgment. Arendt was not writing a corporate governance manual. Her work nevertheless provides a basis for asking whether employees examine what their actions enable, particularly when organizational language makes questionable conduct appear routine.

That question builds on Socrates. Socratic inquiry tests assumptions through questioning. Arendt directs our attention to the person who must decide whether to accept the answer and participate in the conduct. For compliance professionals, that is where inquiry becomes responsibility.

When Approvals Divide Responsibility

Consider this hypothetical. A multinational manufacturer proposes hiring an intermediary to help secure business with a state-owned customer. The commission is unusually high. The service description is vague, and the intermediary requests payment to an account outside its home jurisdiction.

Sales confirms the commercial opportunity. Procurement verifies that the vendor record is complete. Legal reviews contractual provisions. Finance checks that the required approvals appear in the payment system. Compliance previously reviewed the intermediary, but the proposed payment arrangement has changed since that review. Each function assumes another has addressed the remaining concern—the payment proceeds.

No single feature establishes bribery. Together, these facts warrant further inquiry. The governance failure is that nobody takes responsibility for obtaining a satisfactory explanation before payment. Each participant can describe a completed task. The organization cannot explain who assessed the unresolved risk.

This is where Arendt becomes useful to the CCO. Division of labor is necessary in a large company. It must be accompanied by clear obligations to recognize concerns, communicate them, and seek an appropriate decision. Otherwise, specialization can allow important facts to disappear between functions.

The practical response is to specify what each approval means. Does the approver confirm budget availability, verify services, resolve due diligence findings, or authorize an exception? What changes require renewed review? Who owns the decision when concerns remain? These questions turn personal responsibility into an operating requirement.

The DOJ Connection Through Gatekeepers and Escalation

The Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) addresses this issue directly. Under policies and procedures, the ECCP asks about guidance and training for gatekeepers with approval or certification responsibilities. It examines whether they recognize misconduct and understand when and how to escalate concerns.

This is a substantive connection to Arendt’s work, rather than a claim of philosophical influence on DOJ. The compliance question concerns whether an employee’s assigned role includes meaningful judgment. An approval control weakens when its operator understands the mechanics but cannot identify the circumstances that require further review.

Return to our hypothetical. The finance employee should understand whether the changed bank account requires renewed diligence. The business sponsor should explain the services and commercial rationale. Compliance should receive material changes to the information on which its earlier review depended. The final decision should record how identified concerns were resolved.

The CCO can test this through a sample of actual transactions. Interview the approvers. Ask what they believed their approval represented, what information they reviewed, and what would have caused them to stop. Compare those answers with the procedure. The gap between intended and understood responsibility is a control issue that requires attention.

Training Employees to Recognize the Decision

Arendt’s emphasis on thinking also offers a practical lesson for training. Employees need opportunities to examine a situation before organizational habit supplies the answer. A course can explain a prohibition accurately while leaving participants uncertain about how to respond when a manager presents a questionable request as urgent and routine.

The ECCP examines whether training is tailored to relevant employees and risks, whether employees can ask questions, and how the company evaluates learning and training’s effect on behavior or operations.[4] Those inquiries support training that develops judgment within defined responsibilities.

Use the hypothetical intermediary payment as an exercise. Give participants the initial facts, then introduce the changed bank account after approval. Ask them to identify what requires renewed attention, which function should act, and what must happen before payment. Require an explanation for the proposed response.

Include the manager who says the transaction has already been approved. That intervention tests whether employees understand the limits of an earlier decision. The training should leave them with a usable escalation route and a clear account of their authority. Asking people to exercise judgment carries a corresponding obligation to equip them to act.

Leadership Determines Whether Judgment Is Welcome

Employees learn what management expects by watching what happens when someone raises a concern. A company may encourage questions in training while a business leader treats delay as disloyalty. Over time, employees may conclude that completing the transaction is safer than examining it.

The ECCP assesses how senior and middle management demonstrate commitment to compliance. It also examines whether employees feel comfortable reporting concerns and whether the company maintains an effective approach to preventing retaliation.[5] These are relevant tests of the environment in which personal judgment operates.

For the CCO, the practical inquiry should include decisions under pressure. When did a manager support an employee who paused a transaction? What happened to an unresolved concern near quarter-end? Did a policy exception receive appropriate scrutiny when the business sponsor was influential? Such examples help explain whether the stated expectations survive commercial pressure.

Boards also have a role here. The ECCP examines compliance access to governing authorities and opportunities for private discussions. It also cites the Sentencing Guidelines’ expectations concerning governing authority knowledge and oversight.[5] Directors should use that access to ask where management pressure is weakening escalation and whether the compliance function can obtain timely decisions on unresolved concerns.

Investigations Must Examine the Approval Chain

When misconduct emerges, Arendt’s focus on personal responsibility should sharpen the investigation without prejudging anyone’s culpability. The inquiry must establish what individuals knew, what their roles required, what authority they possessed, and how they responded. Participation in a process alone does not establish intentional wrongdoing.

In our hypothetical, investigators should trace the changed payment instructions through the approval chain. Who received them? Did the system alert compliance? Did anyone ask for an explanation? Was a concern overridden, misunderstood, or never transmitted? Those facts distinguish deliberate avoidance from inadequate training, poor system design, or reasonable reliance on incomplete information.

The ECCP asks whether investigations identify system vulnerabilities and accountability failures, including those involving supervisory managers and senior executives. Its remediation questions address failed controls, missed opportunities, and accountability for supervisory failures.[6] An investigation that stops at the person who released the payment may leave the conditions that enabled the problem intact.

Fair accountability therefore requires attention to both conduct and context. Discipline should reflect facts and relevant responsibilities. Remediation should repair the information flows, authority gaps, and incentives that shaped the decision. The organization must be able to explain what it learned and how that learning changes future approvals.

Five Key Arendt Takeaways for the Compliance Professional

  1. Define the responsibility within each approval. Identify what the approver must assess, the evidence required, and the conditions that trigger escalation. Test whether employees understand these obligations in actual transactions.
  2. Train for judgment under realistic pressure. Use scenarios involving changed facts, urgent requests, and influential sponsors. Assess whether employees can explain a concern and identify the appropriate response.
  3. Make challenge operationally possible. Give employees clear escalation routes and appropriate authority to pause decisions. Examine how managers respond when employees use those mechanisms, including whether adverse consequences follow.
  4. Follow accountability through the management chain. Investigate who knew what, who exercised authority, and where supervision failed. Apply fair standards to senior leaders and high performers as well as frontline employees.
  5. Give the board evidence of independent judgment. Report material overrides, unresolved concerns, and lessons from investigations. Explain where employee challenge changed a decision and where management action is still required.

Arendt helps us see that personal responsibility must remain visible inside institutional processes. The CCO’s task includes designing controls that preserve that responsibility and creating conditions in which employees can exercise it. A useful board question follows: Where could our processes allow every participant to believe that someone else was responsible for examining the risk?

Join us tomorrow in Part 2, as we turn to Simone de Beauvoir and discuss the conditions that make ethical action possible. If Arendt asks individuals to exercise judgment, Beauvoir helps us examine how unequal power, dependence, and vulnerability affect their ability to act on it. That inquiry leads directly to reporting culture, retaliation prevention, and the lived experience of corporate compliance.

Categories
Blog

Southern Glazer’s Compliance Roadmap: How the ECCP Helped Turn Serious Misconduct into an NPA

For years, compliance professionals have turned to the Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) to answer a fundamental question: What does an effective compliance program actually look like? Unfortunately, given statements from the early Trump Administration, many compliance professionals feared the Administration would withdraw or otherwise eviscerate the ECCP.

Southern Glazer’s resolution gives us one of the clearest answers in recent memory. The answer is a resounding no: the ECCP is alive and well, even under this DOJ.

Southern Glazer’s entered into a two-year Non-Prosecution Agreement (NPA) with the U.S. Attorney’s Office for the Northern District of California and agreed to pay $12.5 million to resolve a federal criminal investigation involving improper payments, gifts, travel, gift cards, and other benefits. Some of those benefits were facilitated through third-party vendors and concealed through false invoices.

The underlying conduct was serious. Five former Southern Glazer’s employees were indicted in March 2026 for an alleged conspiracy involving commercial bribery and obstruction. Prosecutors alleged that approved vendors and suppliers were used to disguise payments for prepaid gift cards, luxury items, and other benefits through false invoices. Yet Southern Glazer’s itself received an NPA.

For compliance professionals, the most important part of this resolution may be why. The government expressly credited Southern Glazer’s with making significant enhancements to its compliance program beginning in 2023 and, remarkably, specifically noted that the company had aligned those improvements with the factors contained in the ECCP. That makes Southern Glazer’s much more than another bribery enforcement action. It provides a roadmap for remediation.

The ECCP Is Not Sitting on the Shelf

There has been plenty of discussion about what role the ECCP would play in the current enforcement environment. Southern Glazer’s provides a concrete answer. DOJ didn’t merely mention that the company improved compliance. The NPA expressly credited Southern Glazer’s for its “significant efforts to enhance its Compliance Program” and to align that program with DOJ’s evaluation guidance.

That is important. The ECCP should not be treated as an academic document or something pulled from the shelf only after the government arrives. It is a blueprint for building, assessing, and improving a compliance program. Southern Glazer’s demonstrates the potential value of using that blueprint during remediation.

The company did not start from zero. DOJ acknowledged that during the relevant period Southern Glazer’s had compliance policies, a Code of Conduct and employee handbook, trade-practice training, and mechanisms for reporting, investigating, and remediating misconduct. In 2019, the company also notified certain third-party marketing companies that it would no longer process incentives through them and terminated their ability to handle incentives and gift cards. Yet the Statement of Facts makes clear that problems persisted. Employees continued using outside mechanisms for gift cards, travel funds, and other benefits after the 2019 intervention.

This case offers an important compliance lesson. Remediation cannot stop at closing the door through which misconduct previously traveled. Compliance must determine whether employees simply found another door.

Put Resources Behind Compliance

Southern Glazer’s response beginning in 2023 was substantial. Between 2022 and 2024, the company increased compliance headcount by 85 percent and compliance funding by more than 65 percent. It also retained outside compliance experts to advise on program enhancements and best practices. Those numbers matter.

DOJ has repeatedly focused through the ECCP on whether compliance has sufficient resources and authority. Southern Glazer’s provides a practical example of what investment can look like when an organization concludes that its existing compliance infrastructure does not adequately address its risks. This was not simply hiring more investigators after misconduct occurred. Southern Glazer strengthened its compliance architecture.

The General Counsel was promoted to Executive Vice President, Chief Legal and Compliance Officer, reporting directly to the CEO. The company created and filled a Senior Vice President of Compliance & Ethics position. It hired a Vice President and Associate General Counsel for the West region and remapped compliance around five business regions. That is a significant point for boards. If management says compliance is important, look at the organization chart and the budget. Resources are evidence of priorities.

Accountability Had to Follow Misconduct

Southern Glazer’s also addressed individual accountability. The NPA credits the company with removing certain vice presidents and managers for violations of company policy, disciplining additional employees, and replacing senior leadership for California and the West Region. That matters because compliance programs lose credibility quickly when discipline stops at organizational rank.

The Corporate Compliance Agreement takes this concept further. It requires applying disciplinary procedures consistently and fairly, regardless of an employee’s position or perceived importance. When misconduct is discovered, the company must also remediate the resulting harm and assess whether the compliance program itself requires modification. That is precisely the right question after misconduct:

Not simply, Who violated the policy?

But also, What allowed them to do it?

An effective investigation should therefore generate two workstreams. One addresses individual accountability. The other addresses program failure.

Follow the Money

The Southern Glazer’s case is also a powerful internal-controls case. The alleged misconduct involved gift cards, travel, luxury goods, entertainment, marketing expenditures, supplier funds, bill-backs, expense reimbursements, and third-party vendors. According to the Statement of Facts, employees sometimes used altered invoices purporting to reflect legitimate business purposes to circumvent company accounting controls.

Southern Glazer’s responded by moving compliance closer to those transactions. The company imposed a Trade Practice Compliance Audit Program and implemented its “iShop” platform for marketing and promotional spending. It also added mandatory ethics and compliance training and additional compliance resources. That is another important lesson from the ECCP.

Training and policies matter, but compliance effectiveness ultimately has to reach the business process. If bribery risk resides in marketing spend, test marketing spend. If risk resides in bill-backs, audit bill-backs. If employees can manipulate expense descriptions, analyze expense data. If misconduct travels through Accounts Payable, build controls into Accounts Payable. The goal is not simply to tell employees not to engage in misconduct. It is to make misconduct harder to execute and easier to detect.

Rebuild Third-Party Risk Around Payment Controls

The third-party remediation may be the most instructive aspect of the Southern Glazer’s resolution. Third parties were not peripheral to the alleged misconduct. They were part of the mechanism through which value could be transferred and transactions disguised.

Southern Glazer’s responded with a Third-Party Management Program requiring vendors to agree to the company’s compliance and audit standards. Vendors became subject to enhanced due diligence and documentation requirements. The company obtained audit rights. Most importantly, vendors had to be approved before the company could issue payment. Southern Glazer’s also offboarded vendors because of the new requirements. That last point deserves attention.

Third-party compliance frequently becomes an onboarding exercise. Conduct diligence. Assign a risk rating. Obtain contractual language. Approve the vendor. Done. Southern Glazer’s demonstrates why that was insufficient. The control environment must connect onboarding to payment. Accounts Payable should not merely assume that a vendor appearing in the system has passed appropriate compliance controls. The process should prevent payment when required approvals have not occurred. That is compliance embedded into operations.

Compliance Has to Reach the Field

Southern Glazer’s also created a network of state-level “Compliance Champions” responsible for promoting awareness locally and providing additional compliance support. That is particularly relevant for geographically dispersed organizations. Corporate compliance can design excellent policies from headquarters. Risk occurs where employees interact with customers, suppliers, distributors, government officials, and other third parties.

Compliance therefore needs mechanisms to reach those employees and understand what is actually happening locally. The ECCP’s focus on whether a compliance program works in practice is important here. A policy residing on an intranet is not embedded compliance. Employees must know whom to call, understand the rules, and believe compliance understands their business.

Tone at the Top Still Matters

Southern Glazer’s also strengthened senior leadership messaging. The NPA specifically cites communications from the President and CEO reinforcing the importance of ethics and compliance. The company also updated its corporate values around “HEART”: Honesty, Excellence, Agility, Respect, and Teamwork.

Tone at the top is sometimes dismissed as soft compliance. It should not be. But tone only matters when behavior follows the message. Here, leadership messaging was backed by increased resources, management changes, discipline, audit mechanisms, training, third-party controls, and structural changes. That combination is important.

A CEO email saying compliance matters is communication. A CEO message backed by budget, personnel, discipline and controls is governance.

Test Whether the Remediation Actually Works

The final lesson is perhaps the most important. Southern Glazer’s did not simply promise that its enhanced program would work. The Corporate Compliance Agreement requires periodic risk assessments, annual review of policies and procedures, appropriate compliance independence and resources, training, confidential reporting mechanisms, adequately resourced investigations, discipline, M&A procedures, and periodic testing designed to evaluate and improve program effectiveness.

The company must also report annually to the USAO and TTB regarding remediation and implementation of its compliance measures during the NPA. At the end of the term, the CEO, Executive Vice President, and Chief Legal and Compliance Officer must certify that the company has implemented a compliance program that meets the agreement’s requirements and is reasonably designed to detect and prevent trade-practice violations throughout its operations.

That puts real accountability behind remediation.

The Southern Glazer’s Roadmap

Every CCO facing a significant compliance failure should study Southern Glazer’s. The lesson is not that remediation guarantees an NPA. The agreement expressly states that the government reached its decision based on the individual facts and circumstances of this case.

The lesson is that remediation matters, and DOJ has given compliance professionals an unusually detailed picture of what meaningful remediation can look like. Southern Glazer’s strengthened leadership. It increased resources. It brought in outside expertise. It disciplined employees and changed management. It strengthened tone at the top. It pushed compliance into the field. It created new audit mechanisms. It improved training. It rebuilt third-party controls. It connected vendor approval to payment. And it committed to continued risk assessment, monitoring, and testing.

Most significantly, it did these things by expressly aligning its compliance program with the ECCP. For CCOs, that may be the most important takeaway from this entire resolution. Do not wait for prosecutors to use the ECCP to evaluate your compliance program. Use it yourself.

Ask whether your program is well designed. Ask whether it is adequately resourced and empowered to function effectively. Ask whether it works in practice. Then test the answers against your actual risks, transactions, third parties, investigations, and control environment.

Southern Glazer’s demonstrates that the ECCP is more than DOJ guidance. Used properly, it can be a roadmap for remediation, a framework for explaining compliance investment to senior management and the board, and, when misconduct occurs, evidence that the company understood the failure and built a stronger program in response.

That is the compliance lesson from Southern Glazer’s. The best time to align your program with the ECCP is before misconduct occurs. The second-best time is when you discover your existing controls weren’t enough.

Other Resources

Tom and Matt Kelly took a deep dive into the Southern Glazer NPA on this episode of Compliance into the Weeds.

Matt Kelly looked at it on Radical Compliance.

Categories
Compliance Into the Weeds

Compliance into the Weeds: Southern Glazer’s NPA: How Remediation and ECCP Alignment Drove a Favorable Settlement

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into compliance-related topics, literally going into the weeds to explore a subject in greater depth. Looking for hard-hitting compliance insights? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss the Southern Glazer NPA.

The Southern Glazer Wine and Spirits’ non-prosecution agreement is a rare example where prosecutors credited compliance program remediation, rather than self-disclosure or extensive cooperation, as central to a favorable outcome. Southern Glazer, the largest US liquor distributor, faced a major California kickback and bribery scheme involving five former employees, fabricated records, sham agreements, and luxury benefits to retailers and others, along with alleged tax impacts. The company resolved the matter with a $12.5 million payment and a two-year NPA requiring the CEO and CCO to certify program effectiveness. Tom and Matt review how the NPA affirms DOJ’s Evaluation of Corporate Compliance Programs as still relevant and detail remediation steps: major headcount and budget increases, upgraded compliance leadership, audits of marketing spend, enhanced training, strengthened third-party controls and AP payment blocks, outside reviews, and tone-at-the-top messaging.

Key highlights:

  • Southern Glazer Case Setup
  • Industry Risks and Scheme
  • ECCP Guidance Still Matters
  • Program Overhaul Timeline
  • Concrete Remediation Metrics
  • DOJ Signals Under Trump Era

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds was most recently honored as one of the Top 25 Regulatory Compliance Podcasts, a Top 10 Business Law Podcast, and a Top 12 Risk Management Podcast. Compliance into the Weeds has received Davey, Communicator, and W3 Awards, all for podcast excellence.

Categories
FCPA Compliance Report

FCPA Compliance Report: From Prosecutor to White Collar Lawyer to CCO and Back: Mike Koenig

In this episode, Tom Fox welcomes Mike Koenig to talk about his career and his recent move back to private practice after a 5-year stint at JBS. Mike is one of the few folks to move from private practice to an in-house CCO role, then back to private practice.

Mike began by reviewing his career, from 25 years in private practice and a 2003 DOJ Fraud Section stint prosecuting corporate fraud to becoming chief compliance officer at JBS in August 2021 amid DOJ and SEC settlement agreements requiring an effective compliance program. He describes learning to operate within business-driven priorities by building relationships, learning the business and culture, “educating not dictating,” and securing C-suite, board, and audit committee buy-in, including CEO-driven training completion. He explains that he uses trusted outside experts and focuses on the specific problem to solve rather than “boiling the ocean.” After JBS completed the settlements and listed on the NYSE in June 2025, he returned to private practice at Friedman Kaplan to advise on investigations and compliance, emphasizing concise, solution-oriented counsel. He warns against de-prioritizing compliance despite reduced enforcement, urges risk assessments (tariffs, export controls, and human rights), and recommends using DOJ compliance guidance to review programs.

Key highlights:

  • Career Journey Recap
  • Joining JBS In-House
  • Building Compliance Fast
  • Relationships Not Dictates
  • Leadership Buy-In
  • FCPA Pause or a Wake-Up Call
  • Compliance Through 2030

Resources:

Mike Koenig on LinkedIn

Mike Koenig at Friedman Kaplan

Friedman Kaplan

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

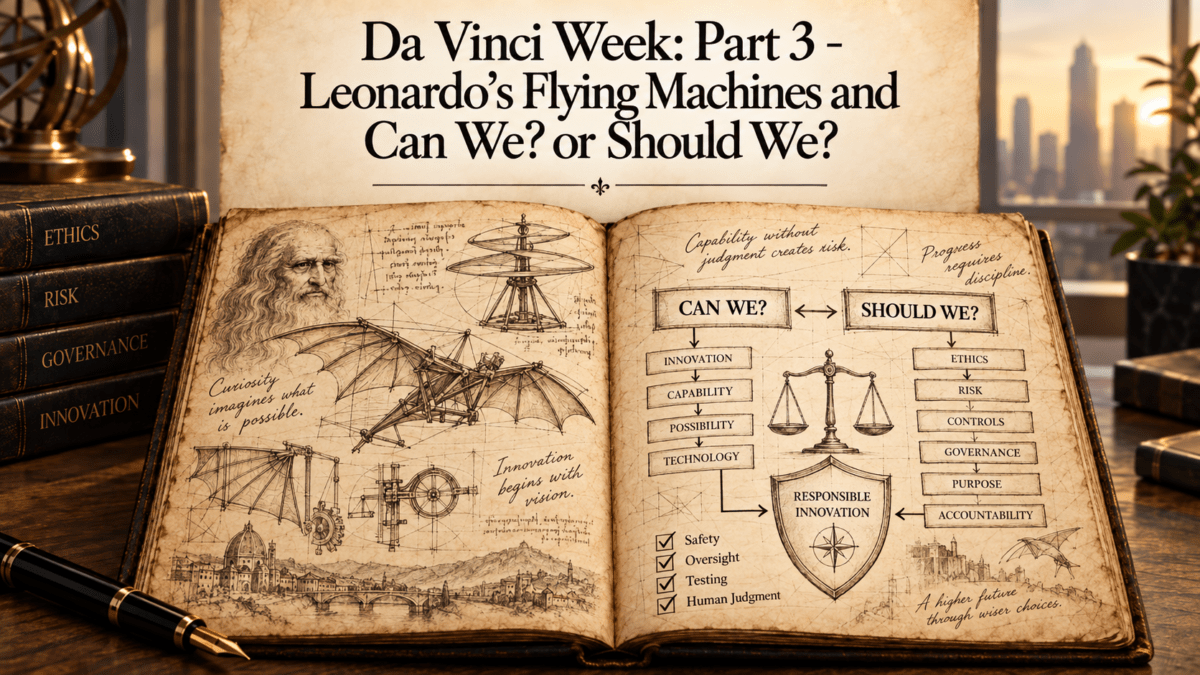
Da Vinci Week: Part 3 – Leonardo’s Flying Machines and “Can We?” or “Should We?”

In the first two posts in the Leonardo Compliance Framework, the Mona Lisa gave us Refine, the principle that an effective compliance program improves as the organization learns from experience. Leonardo’s anatomical studies gave us Investigate, the discipline of looking beneath misconduct to understand root causes, control failures, incentives, management decisions, and the organizational systems that produced the outcome. The third principle is Innovate.

For that lesson, we turn to Leonardo’s studies of flight and his designs for flying machines. Leonardo examined birds, air movement, wings, and mechanical systems as he considered whether technology could allow human beings to fly. Many of his concepts were far beyond the practical capabilities of his time, but they demonstrate an important characteristic of Leonardo’s work: he imagined capabilities that did not yet exist and then studied the systems necessary to make them possible.

For corporate compliance professionals in 2026, the analogy to artificial intelligence is particularly useful. AI is expanding what companies can automate, analyze, predict, generate, and increasingly act upon. Organizations are moving beyond using generative AI to draft documents and summarize information. AI systems are becoming embedded in business processes, interacting with corporate data, supporting consequential decisions, communicating with customers, evaluating third parties, and, through increasingly agentic capabilities, taking actions that previously required human intervention.

The compliance challenge is not whether companies should innovate. They will. The challenge is establishing governance that lets innovation create business value without creating unmanaged legal, ethical, operational, or compliance risk.

AI Governance Is Enterprise Governance

Compliance professionals have sometimes approached emerging technology as primarily the responsibility of IT, Cybersecurity, Data Privacy, or Legal. That division becomes increasingly difficult with AI because these systems can influence many of the activities a corporate compliance team already oversees. Indeed, the Evaluation of Corporate Compliance Programs (ECCP) anticipates these very concepts in its 2024 edition.

AI may assist with third-party due diligence, contract review, procurement, transaction analysis, hiring, customer communications, investigations, fraud detection, marketing, or pricing. Each application creates a different risk profile. A due diligence system may generate inaccurate information about a business partner. An investigation tool may expose privileged or confidential information. A sales application may generate communications inconsistent with company policies. An agent connected to corporate systems may take actions that historically required human approval.

The ECCP asks the following:

  • How does the company assess the potential impact of new technologies, such as artificial intelligence (AI), on its ability to comply with criminal laws?
  • Is management of risks related to the use of AI and other new technologies integrated into broader enterprise risk management (ERM) strategies?
  • What is the company’s approach to governance regarding the use of new technologies such as AI in its commercial business and in its compliance program?
  • How is the company curbing any potential negative or unintended consequences resulting from the use of technologies, both in its commercial business and in its compliance program? 

Visibility and Risk Should Drive the Control Environment

By 2026, asking whether a company uses AI provides little useful information. Management needs to understand how AI is being used and what authority particular systems possess. A tool that summarizes a public document presents a very different risk profile from a system that influences hiring, approves a third party, communicates with customers, accesses confidential information, initiates a transaction, changes corporate records, or takes actions across interconnected systems.

An AI inventory should therefore identify meaningful use cases, including the business owner, intended purpose, relevant data, third parties involved, decisions influenced by the technology, degree of autonomy, and applicable controls. The objective is not simply to count tools. It is to give management sufficient visibility to identify where material risk exists.

That visibility should support risk classification. Not every AI application requires the same level of governance. Classification should consider the system’s purpose, data sensitivity, potential consequences of error, degree of autonomy, affected populations, ability to review or reverse decisions, and applicable legal or regulatory requirements.

This is familiar territory for compliance professionals. Risk-based programs have long applied different levels of scrutiny to third parties, transactions, investigations, and markets. AI should follow the same principle. Higher-risk systems should receive greater review, stronger controls, and more rigorous monitoring.

Human Oversight Must Preserve Accountability

“Human in the loop” has become common language in AI governance, but a human’s presence alone does not create an effective control. Meaningful oversight requires defined responsibilities, appropriate expertise, sufficient capacity to review relevant outputs, and authority to challenge or override the system.

If one employee is nominally responsible for reviewing thousands of AI-generated recommendations each day, human oversight may exist on paper but not function in practice. The same problem arises when employees routinely accept recommendations because they assume the technology is more reliable than their own judgment.

The control should therefore define the reviewer’s responsibilities, the circumstances requiring additional scrutiny, the authority to reject recommendations, and how to handle material overrides or recurring disagreements between the system and human decision-makers. Most importantly, technology should not create an accountability vacuum. If an AI system contributes to a compliance failure, the organization should still be able to identify the business process owner, who approved the use case, who monitored it, and who had authority to intervene.

This becomes increasingly important with agentic systems. Traditional corporate controls generally assume identifiable human actors approve payments, create vendors, review contracts, or authorize higher-risk third parties. When technology performs some of those activities, the organization has effectively delegated authority to a system. The control environment must reflect that delegation while retaining human and organizational accountability for the outcome.

Third-Party AI and Data Risk

Many companies will obtain significant AI capabilities from external vendors rather than develop them internally. Using a vendor does not transfer accountability for the resulting compliance risk. Traditional third-party risk management principles remain relevant. The company should understand the service provided, the information the vendor receives, how data are used and retained, which subcontractors are involved, how incidents are managed, and what contractual rights the company has to obtain information, require remediation, audit, or terminate the relationship.

AI adds a dynamic element because models, features, and business uses can change after initial approval. Monitoring should therefore identify material changes in functionality, data use, vendor practices, or business application that could alter the original risk assessment.

Data governance is equally important. Companies need clear rules regarding which AI systems may access confidential business information, personal data, investigation materials, privileged communications, customer information, trade secrets, source code, and other sensitive information. As enterprise AI systems increasingly operate on internal data, blanket prohibitions will often give way to more precise governance defining approved systems, permissible data, access controls, retention, deletion, and accountability.

These issues require coordination across Compliance, Legal, Privacy, Cybersecurity, IT, Records Management, and the business. Effective governance depends upon clear responsibilities rather than overlapping or fragmented ownership.

Test Before Deployment and Monitor Afterward

Leonardo’s flying machines provide another useful innovation lesson. Test a design before you trust it with a critical task. AI testing should match the risk. Before deployment, the company should understand whether the system performs as intended, where its limitations lie, how it responds to unusual circumstances, whether users can manipulate it, and whether inaccurate or inconsistent outputs could create material consequences. Testing at implementation is not enough. Business conditions change, vendors update models, employees develop new uses, and system capabilities expand. An application that operated within acceptable parameters when approved may later present a different risk profile.

Higher-risk systems therefore require post-deployment monitoring that can identify performance issues, material changes, incidents, and circumstances requiring reassessment. Management should also establish when a system should be modified, restricted, or suspended.

This lifecycle approach connects Innovate to the next Leonardo principle, Monitor. Responsible innovation is not a one-time approval. Governance should continue throughout the period the organization relies on the technology.

Using NIST and ISO as Governance Architecture

Compliance professionals do not need to invent an AI governance structure from scratch. The NIST AI Risk Management Framework provides a useful approach to governance, mapping, measuring, and managing AI risk, while ISO/IEC 42001 offers a management-system perspective built around responsibilities, processes, documentation, monitoring, and continuous improvement.

For the CCO, the value lies in providing governance architecture, not another checklist. The relevant measure is not whether a company can say it follows NIST or ISO. It is whether its governance system addresses the actual risks created by its AI applications and whether the resulting controls work in practice. Frameworks provide structure. Management remains responsible for operating the system.

Compliance Should Enable Responsible Innovation

The CCO should avoid two extremes: allowing enthusiasm for AI to outrun governance or creating an approval structure so burdensome that employees circumvent it. A better model is responsible innovation. Compliance can help create clear pathways for lower-risk experimentation while ensuring that higher-risk applications receive appropriate scrutiny. Employees should understand what uses are permitted, which require approval, what categories of information may be used, and when escalation is necessary.

This approach also creates opportunities for a corporate compliance program. AI may improve due diligence, transaction monitoring, investigations, risk assessment, training, and data analysis. The compliance function should be willing to explore those capabilities under the same risk-based governance it expects the business to follow.

A CCO’s contribution should not be measured by how much innovation Compliance prevents. It should be measured in part by whether Compliance helps the enterprise capture value while maintaining appropriate accountability and control.

Before Leaving the Ground

Leonardo’s flying-machine studies represent the willingness to imagine possibilities beyond current practice. The modern compliance lesson is to combine that willingness with disciplined governance. For the CCO, Innovate means helping the enterprise pursue new capabilities through a risk-based system that provides visibility, assigns ownership, preserves meaningful human accountability, tests higher-risk applications, and monitors them as technology and business use evolve. The objective is neither unrestricted adoption nor blanket prohibition. It is responsible innovation that can produce sustainable business value.

From Innovation to Monitoring

Responsible innovation does not end when technology is approved and deployed. The organization must determine whether systems continue to operate as intended as data, users, vendors, business conditions, and risks change. That brings us to the fourth Leonardo principle: Monitor.

In Blog Post Four, The Last Supper and the Danger of Deterioration, we will use Leonardo’s experimental masterpiece to examine the difference between implementing a control and demonstrating that it remains effective. The discussion will focus on control testing, continuous monitoring, compliance analytics, ownership, remediation, AI monitoring, and the board’s role in evaluating evidence of continuing program effectiveness.

Categories
Blog

Da Vinci Week: Part 2 – Leonardo’s Anatomical Studies and Getting Beneath the Surface

In the first post in our Leonardo Compliance Framework, the Mona Lisa introduced Refine: the discipline of continuous improvement. An effective compliance program should learn from investigations, monitoring, risk assessments, employee feedback, control failures, and business changes. The program should evolve because the organization knows more today than it knew yesterday. That brings us to the second principle: investigate.

Leonardo was not satisfied with observing the human body from the outside. His anatomical studies examined muscles, bones, organs, movement, and the relationships among different parts of the body because he wanted to understand how the entire system worked. That provides a useful model for the modern Chief Compliance Officer because an effective corporate investigation should accomplish more than determine whether an employee violated a policy. It should help the organization understand why the conduct occurred, which controls failed, what incentives influenced behavior, whether management contributed to the problem, whether similar conditions exist elsewhere, and what should change as a result.

The compliance lesson from Leonardo is to look beneath the visible misconduct and understand the system that produced it.

An Investigation Is More Than a Search for Misconduct

Consider a familiar scenario. An investigation establishes that a sales employee used a consultant to make an improper payment to secure business. The company confirms the misconduct, terminates the employee and consultant, documents the findings, and closes the matter.

That process may answer the immediate legal and disciplinary questions, but it does not necessarily answer the larger compliance question. The company should also understand why it hired the consultant, how it approved the relationship, what due diligence it performed, whether it identified red flags, how it compensated the consultant, and how the resulting invoices and payments moved through the organization. Management should consider whether commercial incentives contributed to the conduct, whether supervisors encountered warning signs, and whether similar consultants are being used elsewhere.

If the company concludes only that one employee violated the anti-corruption policy, it may remove the individual while leaving intact the conditions that allowed the misconduct to occur. The investigation has then addressed the actor without addressing the vulnerability. That is why investigations should be viewed as a source of organizational intelligence.

Root Cause Should Drive Remediation

Root-cause analysis is where Leonardo’s anatomical method becomes particularly relevant. The objective is to move from the visible event to the systems underneath it. The Evaluation of Corporate Compliance Program (ECCP) states, “Finally, a hallmark of a compliance program that is working effectively in practice is the extent to which a company can conduct a thoughtful root.” It asks: What is the company’s root cause analysis of the misconduct at issue? Were any systemic issues identified? Who in the company was involved in making the analysis?

Root-cause analysis helps the company distinguish symptoms from causes, and that distinction should determine remediation. A response directed only at the visible misconduct may create the appearance of action without materially reducing the underlying risk.

This is also why significant investigations should test assumptions about the compliance program. If an intermediary engages in misconduct despite passing third-party due diligence, the company should examine whether the process missed information it reasonably could have identified. If an employee disguises improper payments, Compliance and Finance should understand how the relevant financial controls were circumvented. If retaliation occurs after an employee raises a concern, the organization should determine whether its anti-retaliation controls function in practice.

A well-designed compliance program can still experience misconduct. No reasonable system eliminates all risk. Effectiveness is measured by how the organization detects misconduct, responds, learns from failures, and strengthens the program when it identifies weaknesses.

Follow the Decision Trail

Investigators naturally follow evidence by reviewing documents, interviewing witnesses, analyzing transactions, and reconstructing events. Compliance investigations should also follow the decision trail because misconduct frequently passes through business processes designed to create accountability.

The investigation should identify who selected and approved a problematic third party, who authorized exceptions or unusual compensation, who approved payments, who received warnings, and who decided whether concerns warranted escalation. This becomes especially important when misconduct involves senior personnel, high performers, or commercially significant relationships.

The purpose is not to assign blame indiscriminately across every function connected to an incident. It is to understand where accountability actually resided and whether the people responsible for operating or supervising controls fulfilled those responsibilities.

A decision trail can reveal that misconduct was not simply the act of one individual. Other employees may have facilitated the conduct, ignored warning signs, approved questionable transactions, or failed to escalate information. Conversely, the evidence may demonstrate that established controls operated appropriately and that the individual deliberately circumvented them.

Organizational Justice Requires Consistency

Investigations also play a central role in corporate culture. Employees watch how organizations respond to allegations, particularly when cases involve senior executives or high-performing employees. They notice whether powerful people receive different treatment and whether employees who raise concerns suffer professional consequences. This makes consistency an important component of organizational justice, which the ECCP identifies as a part of every compliance program.

Consistency does not require identical outcomes. Facts, intent, responsibilities, prior conduct, cooperation, supervisory duties, and other legitimate considerations can justify different consequences. What matters is that the organization uses a credible process and applies its standards without creating privileged classes of employees.

Investigation governance is therefore important. The company should establish clear decision rights concerning whether allegations require investigation, who determines scope, who approves closure, how disciplinary decisions are made, when conflicts of interest require independent handling, and when matters involving senior executives should be escalated to the Audit Committee or board. These governance arrangements should be in place before a sensitive case arises.

Accountability should also extend beyond the individual who directly engaged in misconduct. Management behavior matters. A supervisor who ignored repeated warning signs, encouraged excessive risk-taking, approved unjustified exceptions, or created incentives that contributed to misconduct may raise separate accountability issues.

If employees see junior personnel disciplined while supervisors face no consequences for meaningful oversight failures, the company may signal that accountability flows only downward. Credible organizational justice requires a more consistent approach.

Investigation Data Is Enterprise Risk Intelligence

Individual investigations explain specific events. Aggregated investigation data can reveal enterprise-wide patterns, making it an important compliance asset. A CCO must understand which allegations recur, whether particular business units or managers appear repeatedly, where investigations are delayed, what root causes occur most often, whether similar control failures appear across jurisdictions, and whether employees who raise concerns subsequently experience unusual turnover or other adverse outcomes.

Those patterns can identify emerging risks that individual case files may not reveal. The data must be interpreted carefully. A business unit with a high number of hotline reports may have significant cultural problems, or it may have a healthy speak-up environment in which employees trust the reporting system. A location with few reports may have an excellent culture, or employees may fear retaliation.

Investigation data works best when combined with other information, including hotline trends, employee surveys, HR data, audit findings, transaction monitoring, exit interviews, and business knowledge. The objective is not simply to count cases but to use investigative information to understand the organization more effectively. This is the Leonardo approach in practice: observation combined with inquiry.

AI Changes the Investigation Function

Artificial intelligence is also changing corporate investigations. AI tools may assist with document review, chronology development, translation, pattern identification, data analysis, and summarization. Used appropriately, these capabilities may allow investigation teams to analyze larger volumes of information and identify relationships more efficiently.

They also create significant governance issues because investigations frequently involve some of the company’s most sensitive information. Before using AI, the organization should understand what data it will provide to the system, whether the material includes privileged, confidential, personal, or commercially sensitive information, where the data will be processed and retained, and what contractual and technical protections apply. Once again, the ECCP puts this onus on your compliance function.

Reliability is equally important. Investigators need a process to validate AI-assisted analysis and identify inaccurate or unsupported outputs. AI use should not obscure how a significant investigative conclusion was reached or prevent the company from explaining the evidence supporting its decision.

Human accountability should remain clear. AI can assist investigators, but it should not replace professional judgment concerning scope, credibility, findings, discipline, or remediation. The broader governance principles reflected in the NIST AI Risk Management Framework and ISO/IEC 42001 can help organizations think about risk management, human oversight, documentation, and monitoring. Still, the fundamental investigation requirements remain confidentiality, accuracy, fairness, privilege, and defensibility.

Connect Investigations to Remediation and Lessons Learned

Companies sometimes separate investigations and remediation too sharply. Legitimate reasons exist to maintain appropriate independence between fact-finding and certain management decisions, but the compliance program still needs a clear mechanism to convert investigative findings into corrective action.

For significant matters, management should understand what failed, why it failed, whether the weakness could exist elsewhere, what corrective action is required, who owns that action, and how the company will determine whether remediation worked. This turns an investigation from a historical examination into a forward-looking compliance tool. Without that connection, an organization can become highly proficient at investigating the same problem repeatedly without becoming better at preventing it.

Lessons learned should also travel beyond the specific business unit or jurisdiction involved. If an investigation in one market identifies improper distributor discounts caused partly by weak approval controls, the company should consider whether comparable controls exist elsewhere. If employees use personal messaging applications to circumvent company systems, management should assess whether the practice extends beyond the employees involved in the investigation. If an AI incident reveals that employees can deploy unapproved tools without effective technical restrictions, the organization should consider the broader governance implications.

This does not require distributing confidential investigative details throughout the company. It means converting case-specific findings into enterprise risk intelligence. Depending on the issue, the lesson may lead to changes in controls, risk assessments, monitoring, training, policies, management communications, or incentive structures. That is how Investigate feeds Refine.

What the Board Should Understand About Investigations

Boards and Audit Committees should resist evaluating the investigation function primarily through case counts. Knowing how many matters were opened and closed provides useful operational information, but it offers limited insight into program effectiveness.

Directors should understand what the company is learning from investigations. Significant themes, recurring root causes, internal control weaknesses, unusual patterns across business units, retaliation concerns, and the status and effectiveness of remediation all provide more meaningful information about compliance risk.

The board should also understand whether investigative resources match the company’s risk profile. Significant cases should not remain unresolved because the organization lacks appropriate staffing, cross-border expertise, data capabilities, employment-law support, or access to information. Matters involving senior personnel should be handled through processes designed to preserve independence and avoid conflicts.

The board does not need to manage individual investigations. Its role is to understand whether the investigation system provides reliable information about significant compliance risks and whether management responds appropriately to what that system reveals.

Getting Beneath the Surface

Leonardo’s anatomical studies give compliance professionals a useful model for investigations because the visible event may be only the first indication of a larger systemic issue. An improper payment may reveal a third-party weakness that exposes deficiencies in due diligence, technology, ownership, incentives, or management oversight.

The investigator’s task is to understand those connections without allowing every matter to become an unlimited enterprise-wide inquiry. Scope should remain proportionate to the seriousness, complexity, and potential reach of the issue. The objective is disciplined curiosity: understanding whether the evidence points to an isolated act or a broader weakness in the compliance system.

For the CCO, the practical lesson is that investigations should do more than establish whether a rule was violated. Significant matters should help the organization understand the controls, incentives, management decisions, and business conditions that contributed to the conduct. Root-cause analysis should drive remediation, investigation findings should test assumptions about program effectiveness, aggregated case data should inform enterprise risk assessment, and lessons learned should improve controls beyond the immediate matter.

That is Investigate, the second principle of the Leonardo Compliance Framework. Finding misconduct matters, but the greater compliance value comes from understanding the system that produced it and using that knowledge to reduce the likelihood of recurrence.

From Investigation to Innovation

Investigation helps the compliance professional understand how existing systems work and why they sometimes fail. Leonardo, however, was equally interested in systems that did not yet exist, which takes us to the third principle in the Leonardo Compliance Framework: Innovate.

In Blog Post Three, Leonardo’s Flying Machines and AI Governance, we will use Leonardo’s studies of flight to examine responsible innovation in 2026. Artificial intelligence and increasingly agentic technologies are moving from generating information to taking action within business processes, raising new questions about risk classification, human accountability, third-party AI, data governance, testing, monitoring, NIST AI RMF, and ISO/IEC 42001.

Leonardo’s willingness to imagine flight provides the innovation lesson. For the modern CCO, the corresponding governance task is ensuring the enterprise understands the risks, controls, and accountability needed before giving new technology meaningful authority inside the business.

Categories
Blog

The Clippers Investigation: Part 4 – Consequence Management at the Top

The Clippers penalties demonstrate that discipline is not the end of a compliance process. They are a public test of whether rules apply to powerful people. The Clippers investigation demonstrates why conflict controls must follow influence, economic benefit, and interconnected transactions, not merely financial ownership. In this Part 4 of a five-part series, we consider the consequences of cheating and not following the rules and regulations your organization agrees to comply with going forward. Every organization claims that no one is above the rules. Consequence management determines whether that statement is true.

The test does not come when a junior employee commits an obvious policy violation. It comes when the conduct involves a founder, controlling owner, senior executive, star performer, or other person viewed as essential to the business. The investigation into the LA Clippers and Kawhi Leonard presents that test in unusually clear terms. The independent investigators’ report of the Clippers’ NBA salary cap circumvention (Wachtell Report) attributed primary responsibility to Clippers owner Steve Ballmer, President of Business Operations Gillian Zucker, and President of Basketball Operations Lawrence Frank. It also found violations by Leonard through the conduct of his uncle and then-business manager, Dennis Robertson (Uncle Dennis).

The NBA responded with organizational, financial, individual, competitive, and monitoring consequences. For compliance professionals, the case provides a framework for considering who should be held accountable, for what conduct, and through what mechanism.

From Punishment to Consequence Management

Punishment looks backward. It asks what sanction should follow a violation. Consequence management is broader. It identifies misconduct, investigates responsibility, calibrates discipline, addresses supervisory failures, remediates control weaknesses, and communicates the organization’s expectations. All of this brings me to one of my favorite compliance phrases: consequence management.

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) introduces consequence management procedures as procedures to identify, investigate, discipline, and remediate violations of law, regulation, or policy. It goes on to state that every organization must enforce them consistently across the organization and ensure the procedures are commensurate with the violations. It concludes: Prosecutors should also assess the extent to which the company’s communications convey to its employees that unethical conduct will not be tolerated and will bring swift consequences, regardless of the employee’s position or title. 

Consequence Calibration

The report provides several categories for assessing responsibility.

  1. Direct participation. Investigators concluded that Zucker initiated, facilitated, and induced endorsement agreements involving Leonard and four Clippers business partners. They found that Ballmer knowingly sought to help Leonard obtain outside income and approved the Forum agreement after learning that Aspiration had tied it to Leonard’s endorsement arrangement. Frank conveyed Robertson’s demands and approved impermissible personal expenses.
  2. Supervisory responsibility. The report concluded that Ballmer failed to supervise the organization’s most senior business executive and failed to create conditions supporting compliance with the circumvention rules.
  3. Reporting responsibility. Investigators found that Ballmer, Zucker, and Frank did not report Robertson’s improper demands, despite an NBA rule requiring those reports even when the solicitation was rejected.
  4. Personal or represented conduct. The report concluded that Leonard, through Robertson, pressured the team to help obtain outside income and failed to reimburse certain personal expenses. Robertson allegedly made the demands and applied the pressure.

A defensible consequence decision should map each individual to the conduct, knowledge, authority, benefit, supervisory obligation, and missed opportunity to intervene. Titles alone should neither establish nor eliminate responsibility.

Credibility and Cooperation Matter

The report did something particularly useful for compliance officers: it distinguished among witness behavior. Investigators wrote that Zucker made statements inconsistent with contemporaneous documents and other witnesses, professed limited recollection on significant issues, placed responsibility on subordinates, and provided inconsistent versions of events.

By contrast, they reported that Frank discussed his conduct openly, recalled important details, accepted responsibility for subordinates, and remained generally consistent across interviews. The investigators stated that cooperation and credibility, or their absence, should factor into determining consequences.

Cooperation does not erase underlying conduct. It should, however, affect how consequences are calibrated. An employee who preserves documents, provides candid information, accepts responsibility, and assists remediation presents a different risk from one who misleads investigators or shifts blame.

The organization should define cooperation before an investigation begins. Employees should understand that cooperation requires truthful, complete, and timely responses; preserving relevant information; correcting prior inaccuracies; and no retaliation or interference. It does not require surrendering legitimate legal rights.

Prior Misconduct Changes the Analysis

The Clippers had previously been penalized for a salary-cap circumvention violation involving an endorsement opportunity. The NBA had also investigated demands made during Leonard’s 2019 free agency and provided specific training to Clippers leaders.

Prior history matters because it changes what the organization and its leaders reasonably should have done. A first incident may reveal an unrecognized risk. A repeated incident following investigation, rule clarification, and training raises questions about culture, supervision, remediation, and willingness to comply.

The Sentencing Guidelines identify prior organizational history as relevant to culpability and direct organizations to consider similar misconduct when designing an effective program. DOJ likewise asks whether policies, training, controls, and risk assessments incorporate lessons from prior incidents.

Remediation that ends with training is incomplete. The organization must test whether behavior, decision rights, escalation pathways, and controls changed.

The NBA’s Consequence Framework

The NBA’s official action included multiple forms of individual accountability. The box score of individual consequences reads as follows:

Person Relationship Consequence
Steve Ballmer Owner: LA Clippers Fine and one-year ban
Gillian Zucker Clippers President of Business Operations One-year unpaid suspension
Lawrence Frank Clippers President of Basketball Operations 6-month Unpaid Suspension
Kawhi Leonard Clipper Player $700K fine
Uncle Dennis Leonard Representative 5-Year Ban from NBA

These measures address different risks. For corporate compliance programs, the equivalent toolkit may include termination, suspension, bonus reduction, clawbacks where legally available, promotion restrictions, written warnings, removal of approval authority, enhanced supervision, vendor termination, and mandatory remediation. Consequences need not be identical, but the process must be consistent. Consistency means applying the same decision factors to similarly situated people. It does not mean imposing the same outcome regardless of role, intent, cooperation, history, or responsibility.

Practical Takeaways

CCOs, human resources leaders, and boards should consider the following:

  • Adopt written consequence-management procedures before a significant investigation occurs.
  • Use a consistent decision matrix covering conduct, intent, seniority, authority, benefit, cooperation, prior history, and supervisory responsibility.
  • Separate factual findings from disciplinary decisions, and ensure decision-makers understand the evidentiary record.
  • Document why similarly situated individuals received similar or different outcomes.
  • Apply financial consequences where permitted and align future compensation with compliance performance.
  • Communicate substantiated outcomes internally with enough detail to reinforce expectations while respecting legal and privacy constraints.
  • Track disciplinary data by level, function, geography, and type of misconduct to identify inconsistency.
  • Require independent board oversight when senior management is implicated.

Consequence management is where culture becomes measurable. If the organization protects its most powerful people, employees will understand that performance outranks integrity. If it applies a fair, independent, and proportionate process, employees will understand that compliance is part of how the business operates.

In our final blog post, we will bring the series together and develop a practical framework for CCOs, boards, and risk leaders seeking to build a compliance program that can say no to the star.

Categories
Daily Compliance News

Daily Compliance News: September 8, 2026, The Big 10 Refs Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • Did the Big 10 refs cheat to give UM a win over WMU? (Yahoo!Sports)
  • Iran vows to strike US energy facilities. (Reuters)
  • DOJ ‘pauses’ work with Canada on antitrust. (WSJ)
  • Deutsche Bank settles with employees it falsely accused of corruption. (FT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

Odyssey Week: Leadership: Penelope’s Loom: Integrity Under Pressure

Ed. Note: I was finally able to see the movie The Odyssey. To say it blew me away was an understatement. Even though it didn’t follow Homer’s work precisely or use ancient Greek, I still thought it was great cinema. Anytime you get people talking about the Greek classics, that is a win in my book. So check out the movie and enjoy it. Anne Hathaway was great as Penelope.

Penelope does not get enough credit. Odysseus gets the monsters, the storms, the speeches, the disguises, and the dramatic return. He gets the action scenes. Penelope gets the waiting. If the movie version made one thing clear, such an interpretation sells her short—very short.

Penelope is not simply waiting. She is governing under pressure. Opportunists surround her. The suitors have occupied her home, consumed her resources, pressured her to choose one of them, and treated uncertainty as an invitation to abuse. Odysseus is gone. Authority is contested. Telemachus is young. The house is under stress.

So Penelope does something quietly brilliant. She promises to choose a suitor after she finishes weaving a burial shroud for Laertes. By day, she weaves. By night, she unweaves. She buys time without surrendering the core issue. It is not flashy. It is not a thunderbolt. It is not a sword fight in the hall. It is disciplined patience under pressure.

That is why Penelope belongs in the leadership section of a compliance odyssey. She reminds us that integrity is not always dramatic. Sometimes it looks like refusing to sign the certification, approve the vendor, bless the transaction, release the report, close the investigation, or accept the explanation simply because everyone is tired of waiting.

The Corporate Translation

Penelope is the leader who understands that time pressure is not the same as good governance. Every organization has Penelope moments. The quarter is closing, and someone wants revenue recognized now. A third party has not cleared diligence, but the business sponsor says the relationship is too important to delay. A certification is due, but the control owner is not comfortable with the evidence. A board report needs to go out, but the investigation findings are still incomplete. A product launch is scheduled, but privacy, security, or regulatory concerns remain unresolved. A customer is demanding speed. A senior executive wants closure. The team is exhausted.

And then someone says the magic words: “Can we just move forward?” That is the sound of the loom beginning to tighten. Penelope’s lesson is not that delay is always virtuous. It is not. Delay can be passive, political, cowardly, or evasive. But some delay is not avoidance. It is governance. The question is whether the organization can tell the difference.

Defensible Delay Is Not Obstruction

In compliance, delay has a bad reputation. That is why compliance is known as The Land of No, populated by Dr. No. Sometimes it is the Department of Business (Non)Development. Whatever the moniker is, this is why business leaders often hear “we need more time” as “compliance is blocking the business.” Sometimes that criticism is fair. Compliance functions can be too slow, too opaque, too academic, or too disconnected from commercial reality. A policy review that disappears into a black hole is not governance. It is bureaucracy with a ticket number.

But there is another kind of delay: defensible delay. Defensible delay has a reason. It has an owner. It has a process. It has a timeline. It identifies the unresolved risk and the information needed to make a decision. It is communicated clearly. It is proportionate to the issue. It protects the company from making a false, rushed, or poorly documented commitment.

Penelope’s loom was not random. It had a purpose. It created time when the available choices were bad. That matters in corporate life. A leader who refuses to approve a questionable vendor is not “being difficult” if the due diligence is incomplete and red flags remain unresolved. A CFO who refuses to sign a certification without adequate support is not “overly cautious.” A compliance officer who asks for more facts before closing an investigation is not “dragging things out.” A privacy officer who pauses a product launch because sensitive data controls are not ready is not “anti-innovation.” Sometimes the most ethical sentence in business is “Not yet.”

Culture Is Built in the Waiting

Corporate culture is often revealed by what happens during delay. When a leader says, “We need more information,” does the organization respect the concern? Or does it start applying pressure?

Does the business provide the missing evidence, or does it complain that Legal is slowing things down? Does management support the control owner, or quietly ask for a more “practical” answer? Does the board ask why the delay is necessary or simply demand that the issue be resolved before the next meeting? Does compliance explain the path forward or hide behind process? These moments shape culture.

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks whether a compliance program works in practice, whether senior and middle management have encouraged or discouraged compliance through their words and actions, and whether compliance personnel have sufficient authority, resources, and access to function effectively. It also asks whether employees have practical guidance and know when to seek advice.

That is Penelope’s world. Culture is not only what the company says about integrity. It is whether the company protects people who slow down a decision for the right reasons. If every delay is treated as disloyalty, employees learn to approve first and worry later. That is not agility. That is ethical surrender in business casual.

Ethical Resilience Under Pressure

Penelope is not powerful in the obvious way. She does not command an army. She does not remove the suitors by force. Her resilience is quieter. She endures pressure without surrendering judgment. That kind of resilience is essential in compliance.

Ethical resilience is the capacity to hold the line when the organization is tired, when the facts are inconvenient, when the deadline is real, and when compromise would be easier. It is the controller who insists on evidence. The manager who escalates a concern before approving the payment. The compliance officer who says the investigation is not complete. The board member who asks whether management’s optimism is supported by testing. The executive who tells the team, “We will not do this the wrong way just because the right way takes longer.”

The DOJ Justice Manual states that prosecutors should evaluate a company’s commitment to fostering a strong culture of compliance at all levels, including how the company incentivizes employee, executive, and director behavior through discipline, complaint handling, and compensation plans. That means ethical resilience cannot depend on heroic individuals. The system must support it.

People must know they will not be punished for raising legitimate concerns. Performance goals must not make ethical delay impossible. Leaders must model patience when facts matter. Governance bodies must ask for evidence, not just reassurance. Compliance must help the business move responsibly, not merely tell it to wait. Penelope’s loom works because she has discipline. A company’s compliance program works because discipline is built into the system.

What a Better Compliance Program Does

A better compliance program helps the organization make disciplined decisions under pressure. It defines which approvals require evidence. It gives control owners authority to withhold certifications when support is inadequate. It builds escalation paths for unresolved risk. It documents exceptions and unresolved issues. It trains leaders on how to respond when employees raise concerns. It tracks aging remediation items. It distinguishes between acceptable risk, unresolved risk, and ignored risk. It also makes delay visible.

If a vendor approval is paused, document the reason. If leadership cannot sign a certification, they should know what evidence is missing. If an investigation remains open, there should be a plan. If a product launch is delayed, stakeholders should understand which control or risk issue must be resolved. That is not bureaucracy. That is governance with receipts.

The Compliance Takeaway

Penelope’s loom is a lesson in ethical leadership. She shows that integrity is not always a grand public stand. Sometimes it is a disciplined refusal to be rushed into a bad decision. Sometimes it is the courage to say, “The facts are not ready.” Sometimes it is the wisdom to buy time without losing the trust of those who are waiting.

For compliance officers and business leaders, the challenge is to build organizations where prudent delay is respected and avoidance is exposed. Do not approve the questionable vendor because everyone is tired. Do not sign the certification because the calendar is unforgiving. Do not close the investigation because the subject is influential. Do not bless the transaction because the business has already promised the outcome.

Weave if you must. Unweave if you must. But know why you are doing it, tell the truth about the risk, and make sure the delay serves integrity rather than fear. That is Penelope’s gift to corporate compliance. She reminds us that sometimes the strongest leader in the room is the one patient enough not to make the wrong decision.

Final Thoughts

Taken together, the leadership lessons from The Odyssey show that corporate compliance is not sustained by slogans, heroes, or good intentions alone. The Trojan Horse reminds us that cleverness without discipline can become a control failure; Athena shows that wise counsel must have real authority, resources, and access to challenge power; and Odysseus demonstrates that even brilliant, high-performing leaders can become compliance risks when success becomes a shield from scrutiny.

Telemachus then carries the lesson into succession, showing that governance must survive the absence of the indispensable leader, with authority, control, ownership, and escalation clearly embedded into the business. Penelope completes the leadership arc by reminding us that integrity under pressure is often quiet, patient, and disciplined: the willingness to say “not yet” when facts are incomplete, risks are unresolved, and everyone else wants to move forward. Together, these stories teach that ethical leadership is not simply about winning the battle or reaching Ithaca; it is about building a compliance culture strong enough to resist shortcuts, challenge heroes, survive transitions, and hold the line when pressure is highest.