Categories
Blog

Da Vinci Week: Part 4 – The Last Supper and the Danger of Deterioration

In the previous post in the Leonardo Compliance Framework, Leonardo’s flying machines gave us Innovate, the principle that Compliance should help organizations capture the benefits of emerging technology while establishing governance appropriate to the risks. Yet approving and deploying a new technology, control, or compliance process does not demonstrate that it will remain effective over time. The organization must continue to evaluate whether the system operates as intended as the business and its risk environment change. That brings us to the fourth principle in the Leonardo Compliance Framework: Monitor.

For this lesson, we turn to Leonardo’s The Last Supper. Leonardo experimented with a painting technique that provided greater artistic flexibility than conventional fresco methods. The result was extraordinary, but the physical work proved vulnerable to deterioration, and environmental conditions and later damage compounded those problems.

For compliance professionals, the lesson is not that experimentation was a mistake. It is that implementation marks the beginning of the control lifecycle, not its end. A system that operates effectively when introduced may weaken as people, processes, technology, incentives, and business conditions change. Modern compliance program effectiveness therefore requires more than evidence that a control exists. Management needs evidence that the control continues to work.

Implementation Is Not Effectiveness

Companies appropriately recognize major implementation milestones. A new third-party platform goes live, an updated Code of Conduct is launched, an investigation protocol is approved, or a sanctions-screening system is installed. These accomplishments demonstrate that the organization has taken action, but they do not establish that the underlying risk is being managed effectively.

Consider a third-party due diligence system implemented across a global enterprise. At launch, the workflow operates as designed. Business sponsors submit required information, higher-risk third parties receive enhanced review, approvals are documented, and Compliance can monitor the process. Two years later, an acquisition may have added thousands of vendors, employees may have developed workarounds because they consider the process too slow, regional teams may interpret risk classifications differently, and data feeds may no longer operate consistently. The system still exists, and the policy remains in force, but the control environment has changed.

This is the central monitoring challenge. Controls operate inside dynamic organizations. A gifts and entertainment process may become inadequate when the company enters markets involving greater interaction with government officials. Sanctions controls may require adjustment following significant geopolitical developments. A conflict-of-interest process may become less effective after an acquisition substantially expands the workforce. Controls designed for one business model may no longer fit another.

Effective monitoring should therefore connect directly to risk assessment. When the company’s risk environment changes, management should evaluate whether the controls designed for the previous environment remain appropriate. Successful implementation at one point in time cannot establish continuing effectiveness.

Monitoring and Testing Provide Different Evidence

Compliance professionals should distinguish between monitoring and testing because each provides different information about the control environment. Monitoring is generally continuous or recurring. It observes transactions, trends, exceptions, employee behavior, third-party activity, hotline information, investigation patterns, and other indicators that may reveal changes in risk or control performance. Testing is more focused and determines whether a particular control is appropriately designed and operating as intended.

Consider a control requiring enhanced approval for high-risk third parties. Monitoring may reveal how many high-risk relationships are approved, how long reviews take, which business units generate the most exceptions, and whether particular patterns are developing. Testing may examine a sample of approved relationships to determine whether required due diligence was performed, red flags were resolved appropriately, approvals occurred at the correct level, and documentation supports the final decision.

Monitoring provides signals about what may be changing. Testing provides evidence about whether specific controls perform as expected. Together, they allow the CCO to move beyond control existence and assess effectiveness.

That distinction matters most when presenting compliance information to senior management and the board. Activity metrics may demonstrate that processes are operating, but control testing provides a stronger basis for determining whether those processes are managing the intended risk.

Ownership Turns Monitoring Into Accountability

Monitoring becomes considerably less effective when control ownership is unclear. This is a recurring compliance problem because responsibilities often cross functional boundaries. Compliance may own the policy, Procurement may operate the process, IT may own the technology, Finance may process the payment, and the business may own the commercial relationship. When the control fails, each function may reasonably believe another function was responsible.

Effective control design should therefore identify an accountable owner responsible for ensuring that the control operates as intended. Compliance may provide oversight and challenge, and Internal Audit may provide independent assurance, but first-line functions should understand their responsibility for managing the underlying business risk.

Ownership should extend to the results of monitoring and testing. If testing identifies repeated exceptions, someone must determine whether the process requires modification. If a data feed fails, someone must restore it. If employees routinely circumvent a control, management must address the underlying behavior or process weakness. Monitoring without ownership produces information without accountability. The objective is not simply to identify control deficiencies but to drive a management response.

Use Data to Identify Deterioration Earlier

Data analytics has significantly expanded compliance functions’ ability to identify changes in risk and control performance. Traditional monitoring often depended on periodic reviews of relatively small samples. Modern analytics can help organizations identify patterns across larger populations and, in some circumstances, detect changes earlier.

Payment data may reveal unusual transaction patterns, while procurement information can identify repeated overrides or vendor concentrations. Third-party data may identify expired due diligence or changes in risk characteristics. Hotline and investigation data can reveal shifts in allegations and recurring root causes, while HR information may signal retaliation or cultural issues.

The objective is not to collect the greatest possible volume of information or create the most sophisticated dashboard. The purpose is to identify data that help management determine whether risks are changing or controls are weakening. Exceptions are particularly valuable in this respect. An individual exception is not necessarily evidence of misconduct because legitimate business circumstances may justify deviation from a standard process. Patterns of exceptions, however, can reveal important information about the control environment.

If one business unit generates substantially more third-party exceptions than comparable operations, Compliance should understand the reason. Repeated overrides near quarter-end may indicate commercial pressure. Due diligence consistently completed after engagement may indicate that the formal process no longer reflects how the business actually operates.

A mature program should therefore examine the frequency, rationale, approving authority, concentration, and recurrence of significant exceptions. When exceptions become routine, they can create an unofficial alternative process that exists alongside the formal control environment. Data become valuable when they reveal that divergence early enough for management to respond.

Investigations, Monitoring, and Remediation Should Form a Feedback Loop

Investigations provide some of the strongest evidence about how controls operate under actual business conditions. Their findings should therefore influence what a compliance program monitors. If an investigation discovers that employees circumvented third-party controls by classifying consultants as ordinary vendors, remediation should address the immediate classification weakness, while monitoring should examine whether comparable patterns exist elsewhere. If an investigation identifies improper discounts used to create funds for inappropriate payments, transaction monitoring can be adjusted to identify similar discount patterns. If a retaliation investigation reveals adverse employment consequences shortly after an employee raised a concern, a compliance professional could consider whether HR data can identify comparable patterns.

This creates a feedback loop. Investigations explain how a control failed in a particular case, monitoring helps determine whether the same weakness exists elsewhere or is recurring, and remediation addresses the underlying problem. Monitoring has limited value if the organization does not act on what it learns. When testing identifies a significant deficiency, management should understand why it occurred, whether it is systemic, what risk it creates, what corrective action is required, and who owns that remediation. The organization should then validate that the corrective action addressed the weakness.

This last step is important because remediation completion and remediation effectiveness are different concepts. Issuing a revised procedure or completing additional training may satisfy a project milestone without solving the underlying problem. Follow-up testing provides evidence that the remediation worked.

The compliance learning cycle should therefore move from investigation to monitoring, from monitoring to remediation, and from remediation to validation.

AI Requires Continuing Monitoring

AI provides a particularly clear example of why approval and implementation cannot end the governance process. A company may conduct extensive review before deploying an AI application by assessing the vendor, testing the system, evaluating data use, classifying risk, and establishing human oversight. Those steps are important, but the system and its operating environment can change after deployment.

Vendors may update models, employees may develop new uses, data may change, integrations may expand access, and capabilities may increase. For higher-risk applications, monitoring should therefore match the potential consequences. It may include performance testing, incident monitoring, reviewing material overrides, validating outputs, and reassessing after significant changes in functionality or use.

Agentic systems deserve particular attention because monitoring may need to address not only output quality but also the actions a system performs, the permissions it exercises, and whether it remains within its approved authority. The broader principle is the same as for any other compliance control. Governance should continue for as long as the organization relies upon the system.

Culture Also Requires Monitoring

Corporate culture presents a different monitoring challenge because no single metric establishes whether an organization has a strong ethical culture. Hotline reporting rates provide useful information but require interpretation. High reporting may indicate significant problems or employee confidence in the reporting system. Low reporting may reflect a healthy environment or fear of speaking up. Employee surveys provide additional information but capture sentiment at a particular moment, while investigation data reflect only matters that become known.

Compliance should therefore build a broader picture using multiple indicators, including reporting trends, employee surveys, exit interviews, focus groups, disciplinary information, HR data, investigation findings, and management assessments. Changes across these indicators may reveal emerging issues in particular business units, management teams, or employee populations.

Culture monitoring is especially important after leadership changes, acquisitions, restructurings, layoffs, or significant incentive changes because these events can quickly alter employee perceptions and behavior. Formal policies may remain unchanged while the operating culture deteriorates. As with other compliance risks, the objective is not perfect measurement. It is obtaining enough reliable information to identify material changes and respond appropriately.

The Danger of Deterioration

The Last Supper reminds us that implementation captures a moment in time while organizations continue to evolve. Personnel, technology, incentives, business models, markets, and risks change, and controls that once worked can weaken in response. An effective compliance program therefore needs monitoring, testing, clear ownership, useful data, and validated remediation. These disciplines allow the organization to identify deterioration before a control weakness becomes a larger compliance failure.

The practical lesson for the CCO is that implementation should never be confused with effectiveness. Monitoring and testing should provide different but complementary evidence about control performance. Ownership should ensure findings produce action, analytics should identify meaningful changes rather than simply populate dashboards, and remediation should be validated before the organization concludes the underlying problem is solved. That is Monitor, the fourth principle of the Leonardo Compliance Framework. A control deserves continuing confidence only when the organization has continuing evidence that it works.

From Monitoring to Documentation

Monitoring tells the organization what is happening, but institutional learning depends upon preserving what the organization learns. A company may conduct an effective investigation, identify a root cause, redesign a control, test the remediation, and reach a thoughtful risk decision. Yet, much of that value can disappear if the reasoning exists only in the memories of the people involved.

That brings us to the fifth and final Leonardo principle: Document. In Blog Post Five, Leonardo’s Notebooks: Documentation the Defensible Compliance Program, we will use Leonardo’s extraordinary record of observations, drawings, experiments, and ideas to examine documentation as a governance discipline. The discussion will focus on preserving significant compliance reasoning, establishing accountability, creating institutional memory, documenting remediation and AI governance decisions, and ensuring that what the organization learns today remains available to the people responsible for managing its risks tomorrow.
Categories
Blog

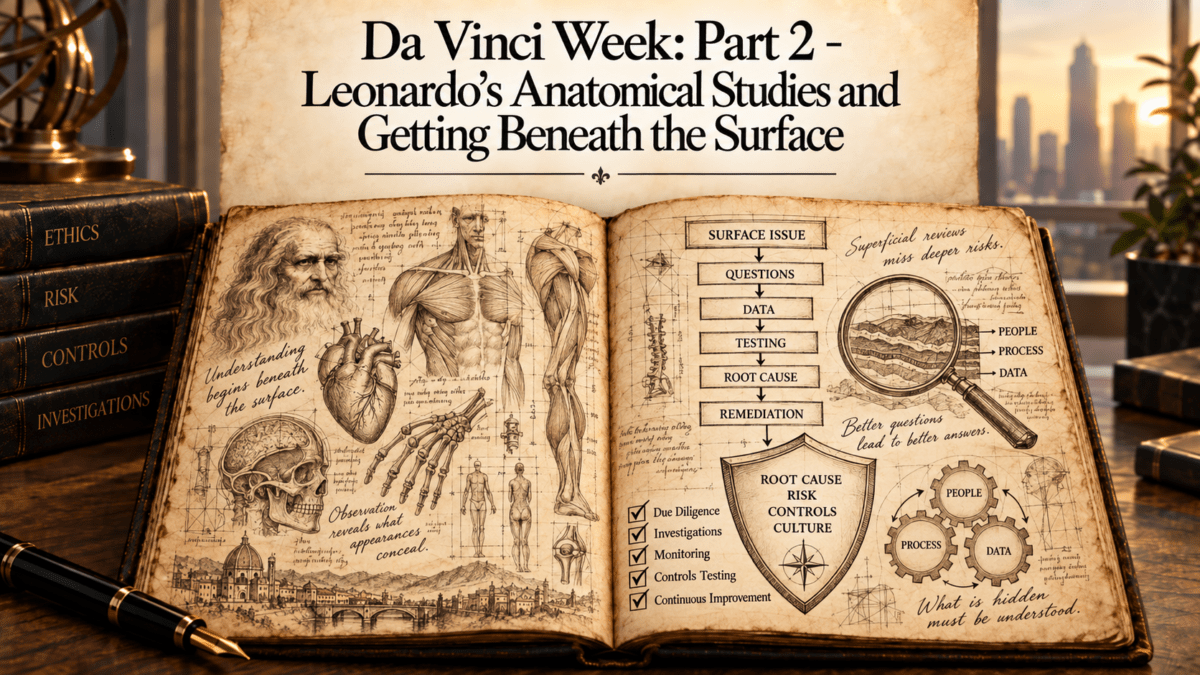
Da Vinci Week: Part 2 – Leonardo’s Anatomical Studies and Getting Beneath the Surface

In the first post in our Leonardo Compliance Framework, the Mona Lisa introduced Refine: the discipline of continuous improvement. An effective compliance program should learn from investigations, monitoring, risk assessments, employee feedback, control failures, and business changes. The program should evolve because the organization knows more today than it knew yesterday. That brings us to the second principle: investigate.

Leonardo was not satisfied with observing the human body from the outside. His anatomical studies examined muscles, bones, organs, movement, and the relationships among different parts of the body because he wanted to understand how the entire system worked. That provides a useful model for the modern Chief Compliance Officer because an effective corporate investigation should accomplish more than determine whether an employee violated a policy. It should help the organization understand why the conduct occurred, which controls failed, what incentives influenced behavior, whether management contributed to the problem, whether similar conditions exist elsewhere, and what should change as a result.

The compliance lesson from Leonardo is to look beneath the visible misconduct and understand the system that produced it.

An Investigation Is More Than a Search for Misconduct

Consider a familiar scenario. An investigation establishes that a sales employee used a consultant to make an improper payment to secure business. The company confirms the misconduct, terminates the employee and consultant, documents the findings, and closes the matter.

That process may answer the immediate legal and disciplinary questions, but it does not necessarily answer the larger compliance question. The company should also understand why it hired the consultant, how it approved the relationship, what due diligence it performed, whether it identified red flags, how it compensated the consultant, and how the resulting invoices and payments moved through the organization. Management should consider whether commercial incentives contributed to the conduct, whether supervisors encountered warning signs, and whether similar consultants are being used elsewhere.

If the company concludes only that one employee violated the anti-corruption policy, it may remove the individual while leaving intact the conditions that allowed the misconduct to occur. The investigation has then addressed the actor without addressing the vulnerability. That is why investigations should be viewed as a source of organizational intelligence.

Root Cause Should Drive Remediation

Root-cause analysis is where Leonardo’s anatomical method becomes particularly relevant. The objective is to move from the visible event to the systems underneath it. The Evaluation of Corporate Compliance Program (ECCP) states, “Finally, a hallmark of a compliance program that is working effectively in practice is the extent to which a company can conduct a thoughtful root.” It asks: What is the company’s root cause analysis of the misconduct at issue? Were any systemic issues identified? Who in the company was involved in making the analysis?

Root-cause analysis helps the company distinguish symptoms from causes, and that distinction should determine remediation. A response directed only at the visible misconduct may create the appearance of action without materially reducing the underlying risk.

This is also why significant investigations should test assumptions about the compliance program. If an intermediary engages in misconduct despite passing third-party due diligence, the company should examine whether the process missed information it reasonably could have identified. If an employee disguises improper payments, Compliance and Finance should understand how the relevant financial controls were circumvented. If retaliation occurs after an employee raises a concern, the organization should determine whether its anti-retaliation controls function in practice.

A well-designed compliance program can still experience misconduct. No reasonable system eliminates all risk. Effectiveness is measured by how the organization detects misconduct, responds, learns from failures, and strengthens the program when it identifies weaknesses.

Follow the Decision Trail

Investigators naturally follow evidence by reviewing documents, interviewing witnesses, analyzing transactions, and reconstructing events. Compliance investigations should also follow the decision trail because misconduct frequently passes through business processes designed to create accountability.

The investigation should identify who selected and approved a problematic third party, who authorized exceptions or unusual compensation, who approved payments, who received warnings, and who decided whether concerns warranted escalation. This becomes especially important when misconduct involves senior personnel, high performers, or commercially significant relationships.

The purpose is not to assign blame indiscriminately across every function connected to an incident. It is to understand where accountability actually resided and whether the people responsible for operating or supervising controls fulfilled those responsibilities.

A decision trail can reveal that misconduct was not simply the act of one individual. Other employees may have facilitated the conduct, ignored warning signs, approved questionable transactions, or failed to escalate information. Conversely, the evidence may demonstrate that established controls operated appropriately and that the individual deliberately circumvented them.

Organizational Justice Requires Consistency

Investigations also play a central role in corporate culture. Employees watch how organizations respond to allegations, particularly when cases involve senior executives or high-performing employees. They notice whether powerful people receive different treatment and whether employees who raise concerns suffer professional consequences. This makes consistency an important component of organizational justice, which the ECCP identifies as a part of every compliance program.

Consistency does not require identical outcomes. Facts, intent, responsibilities, prior conduct, cooperation, supervisory duties, and other legitimate considerations can justify different consequences. What matters is that the organization uses a credible process and applies its standards without creating privileged classes of employees.

Investigation governance is therefore important. The company should establish clear decision rights concerning whether allegations require investigation, who determines scope, who approves closure, how disciplinary decisions are made, when conflicts of interest require independent handling, and when matters involving senior executives should be escalated to the Audit Committee or board. These governance arrangements should be in place before a sensitive case arises.

Accountability should also extend beyond the individual who directly engaged in misconduct. Management behavior matters. A supervisor who ignored repeated warning signs, encouraged excessive risk-taking, approved unjustified exceptions, or created incentives that contributed to misconduct may raise separate accountability issues.

If employees see junior personnel disciplined while supervisors face no consequences for meaningful oversight failures, the company may signal that accountability flows only downward. Credible organizational justice requires a more consistent approach.

Investigation Data Is Enterprise Risk Intelligence

Individual investigations explain specific events. Aggregated investigation data can reveal enterprise-wide patterns, making it an important compliance asset. A CCO must understand which allegations recur, whether particular business units or managers appear repeatedly, where investigations are delayed, what root causes occur most often, whether similar control failures appear across jurisdictions, and whether employees who raise concerns subsequently experience unusual turnover or other adverse outcomes.

Those patterns can identify emerging risks that individual case files may not reveal. The data must be interpreted carefully. A business unit with a high number of hotline reports may have significant cultural problems, or it may have a healthy speak-up environment in which employees trust the reporting system. A location with few reports may have an excellent culture, or employees may fear retaliation.

Investigation data works best when combined with other information, including hotline trends, employee surveys, HR data, audit findings, transaction monitoring, exit interviews, and business knowledge. The objective is not simply to count cases but to use investigative information to understand the organization more effectively. This is the Leonardo approach in practice: observation combined with inquiry.

AI Changes the Investigation Function

Artificial intelligence is also changing corporate investigations. AI tools may assist with document review, chronology development, translation, pattern identification, data analysis, and summarization. Used appropriately, these capabilities may allow investigation teams to analyze larger volumes of information and identify relationships more efficiently.

They also create significant governance issues because investigations frequently involve some of the company’s most sensitive information. Before using AI, the organization should understand what data it will provide to the system, whether the material includes privileged, confidential, personal, or commercially sensitive information, where the data will be processed and retained, and what contractual and technical protections apply. Once again, the ECCP puts this onus on your compliance function.

Reliability is equally important. Investigators need a process to validate AI-assisted analysis and identify inaccurate or unsupported outputs. AI use should not obscure how a significant investigative conclusion was reached or prevent the company from explaining the evidence supporting its decision.

Human accountability should remain clear. AI can assist investigators, but it should not replace professional judgment concerning scope, credibility, findings, discipline, or remediation. The broader governance principles reflected in the NIST AI Risk Management Framework and ISO/IEC 42001 can help organizations think about risk management, human oversight, documentation, and monitoring. Still, the fundamental investigation requirements remain confidentiality, accuracy, fairness, privilege, and defensibility.

Connect Investigations to Remediation and Lessons Learned

Companies sometimes separate investigations and remediation too sharply. Legitimate reasons exist to maintain appropriate independence between fact-finding and certain management decisions, but the compliance program still needs a clear mechanism to convert investigative findings into corrective action.

For significant matters, management should understand what failed, why it failed, whether the weakness could exist elsewhere, what corrective action is required, who owns that action, and how the company will determine whether remediation worked. This turns an investigation from a historical examination into a forward-looking compliance tool. Without that connection, an organization can become highly proficient at investigating the same problem repeatedly without becoming better at preventing it.

Lessons learned should also travel beyond the specific business unit or jurisdiction involved. If an investigation in one market identifies improper distributor discounts caused partly by weak approval controls, the company should consider whether comparable controls exist elsewhere. If employees use personal messaging applications to circumvent company systems, management should assess whether the practice extends beyond the employees involved in the investigation. If an AI incident reveals that employees can deploy unapproved tools without effective technical restrictions, the organization should consider the broader governance implications.

This does not require distributing confidential investigative details throughout the company. It means converting case-specific findings into enterprise risk intelligence. Depending on the issue, the lesson may lead to changes in controls, risk assessments, monitoring, training, policies, management communications, or incentive structures. That is how Investigate feeds Refine.

What the Board Should Understand About Investigations

Boards and Audit Committees should resist evaluating the investigation function primarily through case counts. Knowing how many matters were opened and closed provides useful operational information, but it offers limited insight into program effectiveness.

Directors should understand what the company is learning from investigations. Significant themes, recurring root causes, internal control weaknesses, unusual patterns across business units, retaliation concerns, and the status and effectiveness of remediation all provide more meaningful information about compliance risk.

The board should also understand whether investigative resources match the company’s risk profile. Significant cases should not remain unresolved because the organization lacks appropriate staffing, cross-border expertise, data capabilities, employment-law support, or access to information. Matters involving senior personnel should be handled through processes designed to preserve independence and avoid conflicts.

The board does not need to manage individual investigations. Its role is to understand whether the investigation system provides reliable information about significant compliance risks and whether management responds appropriately to what that system reveals.

Getting Beneath the Surface

Leonardo’s anatomical studies give compliance professionals a useful model for investigations because the visible event may be only the first indication of a larger systemic issue. An improper payment may reveal a third-party weakness that exposes deficiencies in due diligence, technology, ownership, incentives, or management oversight.

The investigator’s task is to understand those connections without allowing every matter to become an unlimited enterprise-wide inquiry. Scope should remain proportionate to the seriousness, complexity, and potential reach of the issue. The objective is disciplined curiosity: understanding whether the evidence points to an isolated act or a broader weakness in the compliance system.

For the CCO, the practical lesson is that investigations should do more than establish whether a rule was violated. Significant matters should help the organization understand the controls, incentives, management decisions, and business conditions that contributed to the conduct. Root-cause analysis should drive remediation, investigation findings should test assumptions about program effectiveness, aggregated case data should inform enterprise risk assessment, and lessons learned should improve controls beyond the immediate matter.

That is Investigate, the second principle of the Leonardo Compliance Framework. Finding misconduct matters, but the greater compliance value comes from understanding the system that produced it and using that knowledge to reduce the likelihood of recurrence.

From Investigation to Innovation

Investigation helps the compliance professional understand how existing systems work and why they sometimes fail. Leonardo, however, was equally interested in systems that did not yet exist, which takes us to the third principle in the Leonardo Compliance Framework: Innovate.

In Blog Post Three, Leonardo’s Flying Machines and AI Governance, we will use Leonardo’s studies of flight to examine responsible innovation in 2026. Artificial intelligence and increasingly agentic technologies are moving from generating information to taking action within business processes, raising new questions about risk classification, human accountability, third-party AI, data governance, testing, monitoring, NIST AI RMF, and ISO/IEC 42001.

Leonardo’s willingness to imagine flight provides the innovation lesson. For the modern CCO, the corresponding governance task is ensuring the enterprise understands the risks, controls, and accountability needed before giving new technology meaningful authority inside the business.

Categories
Blog

The Scoular DPA: Part 2 – A Journey Through Non-Disclosure

The Scoular Company Deferred Prosecution Agreement (DPA) presents a difficult but essential lesson for every Chief Compliance Officer and board: stopping misconduct is not the same as voluntarily disclosing it. This might seem as self-evident as anything in compliance, but it is a critical component of this case.

The Statement of Facts says that internal reports alleging improper business practices connected to the Mexican inspection fees arose in 2019. Scoular then changed its grain-shipment practices and terminated its direct engagement with the customs brokers involved. Those steps addressed the immediate conduct. They did not produce voluntary self-disclosure credit. That misstep cost Scoular Company millions, potentially leading to a full declination.

The DPA states that Scoular did not receive credit under the DOJ Corporate Enforcement and Voluntary Self-Disclosure Policy (VSP) because it did not “voluntarily and timely disclose” the conduct to the Fraud Section. That single sentence creates the central governance question in Blog Post Part 2: What must happen after a credible internal report reaches the company? An internal allegation starts an investigative clock. The company must preserve evidence, protect against retaliation, assess immediate risk, and establish enough facts to make responsible decisions. It also starts a disclosure clock.

The VSP encourages companies to report potential wrongdoing at the earliest possible time, even before an internal investigation is complete. To qualify as a voluntary self-disclosure, a report must be made in good faith to the appropriate DOJ component, concern misconduct not already known to the Department, occur without a preexisting disclosure obligation, precede an imminent threat of disclosure or government investigation, and be made within a reasonably prompt time after the company becomes aware of the misconduct.

The burden of demonstrating timeliness rests with the company. This does not mean a company must call the DOJ the moment an untested allegation enters the hotline. It does mean disclosure cannot wait until every interview, legal conclusion, and remediation project is complete. The investigation and disclosure analyses must proceed together.

The DPA Tells Us the Result, Not the Internal Debate

The agreement does not explain who received the 2019 reports, how the allegations were investigated, when senior management or the board learned of them, or why Scoular did not make a qualifying disclosure. It does not tell us whether the company made a deliberate decision not to report. What the DPA does establish is the outcome. Internal reports arose. The company changed its practices and terminated direct broker relationships. The company did not voluntarily and timely disclose the conduct to the Fraud Section and therefore received no voluntary disclosure credit.

That sequence is enough to demonstrate a control lesson. A company can remediate an operational problem and still leave the enforcement decision unresolved. The response requires four distinct workstreams:

  • Stopping the conduct prevents additional harm.
  • Investigating the conduct determines what happened and which controls failed.
  • Remediating the controls reduces recurrence risk.
  • Evaluating disclosure determines whether, when, where, and how the company should approach enforcement authorities. This fourth step is arguably the most important and must be reached with great speed, perhaps as little as two weeks after initial determination.

A Disclosure Needs a Decision Process

Disclosure decisions should not depend on one executive’s instinct or on the hope that remediation will close the matter. The company needs a defined escalation structure involving legal, compliance, internal audit, finance, and appropriate senior management. Depending on the seriousness of the facts, the audit committee or another independent board committee may need to oversee the decision.

For an FCPA matter involving customs brokers, repeated payments, government officials, inaccurate invoice descriptions, senior personnel, and multiple years of conduct, the disclosure analysis should address:

  • What credible facts are known now?
  • Is the misconduct continuing?
  • Which individuals and third parties may be involved?
  • Are the books and records inaccurate?
  • Is there evidence of management participation, approval, condonation, or willful ignorance?
  • Has a whistleblower, auditor, regulator, bank, business partner, or foreign authority already received the same information?
  • Is there an imminent threat that the DOJ will learn of the conduct?
  • What additional facts are necessary to make a disclosure decision?
  • When will the decision be revisited?
  • Who has authority to decide, and how will the reasoning be documented?

The objective is not to create a paper defense for a predetermined result. It is to establish a disciplined process that forces the company to confront timing, uncertainty, accountability, and enforcement exposure.

Disclosure Does Not Require a Finished Investigation

One reason companies may delay is the understandable fear of reporting facts that are incomplete or later prove wrong. The DOJ policy addresses that concern directly. It encourages early disclosure even when the company has not completed its internal investigation. The company can report the misconduct known at that stage, identify the limits of its current knowledge, preserve credibility by avoiding unsupported conclusions, and provide rolling updates as the investigation develops.

That approach requires discipline. The initial disclosure should distinguish facts from allegations, describe preservation and remediation steps, and explain the investigative plan. Later presentations should attribute facts to specific sources and identify individuals regardless of seniority.

Waiting for certainty can eliminate the benefit the company hoped to secure. A whistleblower may contact the government, a third party may cooperate, or the payment may surface in another investigation. Once the DOJ already knows or disclosure is imminent, the analysis changes. The business lesson is straightforward. Uncertainty calls for a staged disclosure strategy, not an indefinite pause.

Cooperation Still Mattered

Scoular Company lost the disclosure benefit, but the DPA demonstrates that the company could still earn meaningful credit. The DOJ credited Scoular with conducting an internal investigation, making detailed factual presentations, identifying individuals involved, producing and organizing requested materials, securing counsel for current employees, and providing all relevant facts known to it.

Voluntary self-disclosure, cooperation, and remediation are separate pillars. A company that misses the first can still create value through the other two. The DPA also notes “certain deficiencies in the early part of the investigation.” It does not identify those deficiencies, and they should not be guessed. Their inclusion nevertheless sends a message: cooperation is judged across the life of the investigation, not merely by the quality of the final presentation.

The current DOJ policy makes the standard explicit. A company starts at zero cooperation credit and earns credit through specific actions: scope, quality, impact, and timing matter. A failure to cooperate fully at the earliest opportunity may reduce the credit available later. For CCOs and boards, the lesson is that recovery remains possible, but delay has a price.

Remediation Changed How the Business Operated

Scoular also received credit for substantial remediation. The company increased compliance engagement with the business, used external compliance maturity and anti-corruption risk assessments, restructured the compliance function, and incorporated senior leadership oversight. It eliminated customs brokers associated with reinspection fees, strengthened risk-based review and monitoring with software tools, revised policies, enhanced third-party screening and approvals, added anti-corruption and audit-right provisions to contracts, improved financial controls for high-risk transactions, and delivered general and targeted training.

These measures went beyond terminating vendors. They addressed governance, third-party management, payment controls, monitoring, technology, policies, and training. That breadth matters because remediation must be tied to root cause. If the misconduct was enabled by commercial pressure, broker dependence, misleading invoices, weak transaction validation, and fragmented data, another annual training course will not solve the problem.

The Economic Difference Was Significant

Scoular entered into a three-year DPA and agreed to pay a $9,769,521 criminal penalty and $414,351 in forfeiture. The DPA states that the penalty reflected a 25 percent reduction from the applicable low-end amount. A footnote explains that the statutory alternative-fine cap, based on twice the approximately $6.513 million gross gain, constrained the otherwise higher Guidelines minimum.

The DPA does not say what disposition Scoular would have received after a qualifying disclosure. It would be improper to rewrite the resolution with hypothetical facts.

The current department-wide CEP nevertheless shows why the distinction matters. A company that voluntarily self-discloses, fully cooperates, timely remediates, and has no disqualifying aggravating circumstances is placed on a declination path. A good-faith self-report that narrowly misses the policy’s technical requirements can still lead to an NPA, a term shorter than three years, no monitor, and a reduction of 50 to 75 percent from the low end. Companies outside those paths remain subject to prosecutorial discretion, with a reduction capped at 50 percent.

Scoular received a DPA, a three-year term, and a 25 percent reduction. The numbers turn disclosure governance into a business issue. The decision affects resolution form, penalty exposure, duration, oversight, reputation, management time, and the company’s ability to move beyond the misconduct.

Questions for CCOs

CCOs should ask:

  • Does every credible allegation involving government payments trigger a documented disclosure analysis?
  • Who owns the disclosure clock while the investigation proceeds?
  • Can legal and compliance make an early report without waiting for a completed investigation?
  • Are facts, assumptions, open questions, and decision deadlines documented separately?
  • Have we tested the process through a tabletop exercise involving a whistleblower, a third party, and an imminent government inquiry?

The Scoular DPA does not establish why the company missed voluntary disclosure credit. It does establish that internal reporting, operational remediation, and voluntary disclosure are not interchangeable. When a credible allegation arrives, the company must stop the conduct, investigate the facts, remediate the controls, and make a timely, documented disclosure decision. Doing three of those four things can still leave substantial value on the table.

Join us tomorrow for Part 3, where we will examine how a robust internal control system paired with a robust data analytics overview can help a company avoid a Scoular Company-type series of failures.

Categories
Compliance Into the Weeds

Compliance into the Weeds: Balt and TradeStation: Lessons for the Compliance Professional

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into a compliance-related topic, literally going into the weeds to explore it more fully. Looking for some hard-hitting insights on compliance? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly look at the Declination awarded to Balt SAS and the OFAC enforcement action involving TradeStation. 

First, they review a Corporate Enforcement Policy declination for French medical-equipment company BAL SAS and the company’s U.S. subsidiary after self-disclosing, cooperating and remediating misconduct involving a U.S. subsidiary executive and a Belgian consultant allegedly funneling about $600,000 in bribes to a French public hospital official using sham consulting agreements, invoices, and poor documentation; BAL disgorged about $1.21 million in profit on roughly $1.68 million in revenue and disclosed while its internal investigation was still ongoing, raising timing and high-margin red-flag issues.

Second, they cover OFAC’s $1.1 million settlement with TradeStation for accidentally disabling sanctions-screening controls for nearly a year, enabling hundreds of transactions from Iran, Syria, and Crimea; despite having layered tools on paper, IT changes and lapsed subscriptions undermined those controls, underscoring the need for ongoing monitoring, testing, and auditing.

 Key highlights:

  • Balt FCPA Case
  • Disclosure Timing
  • Profit Margin Red Flags
  • Controls and France Angle
  • TradeStation Overview
  • How Screening Failed
  • Monitoring and Accountability
  • Costs and OFAC Lessons

Resources:

Matt in ⁠Radical Compliance⁠

Tom in the ⁠FCPA Compliance Report⁠

Tom  

⁠Instagram⁠

⁠Facebook⁠

⁠YouTube⁠

⁠Twitter⁠

⁠LinkedIn⁠

A multi-award-winning podcast, Compliance into the Weeds was most recently honored as one of the Top 25 Regulatory Compliance Podcasts, a Top 10 Business Law Podcast, and a Top 12 Risk Management Podcast. Compliance into the Weeds has been conferred a Davey, a Communicator Award, and a W3 Award, all for podcast excellence.

Categories
Blog

The Updated CEP: Is Real Credit Finally Here?

Matthew R. Galeotti, Head of the Criminal Division at the U.S. Department of Justice (DOJ), recently delivered a speech at SIFMA’s Anti-Money Laundering and Financial Crimes Conference. Contemporaneously, the DOJ issued a Memo (the Galeotti Memo) entitled Focus, Fairness, and Efficiency in the Fight Against White-Collar Crime. I have explored both in previous blog posts. Today, I want to review the Corporate Enforcement and Voluntary Self-Disclosure Policy (CEP) updates. It provides a roadmap for how companies can earn leniency when they self-report wrongdoing. And in an increasingly unforgiving regulatory landscape, that roadmap is worth its weight in gold.

Under the CEP, a company that voluntarily self-discloses, fully cooperates, and timely remediates can qualify for a declination of prosecution, provided there are no aggravating circumstances. This is the reaffirmation of a multi-year DOJ effort to garner more self-disclosures. It gives compliance professionals something real to bring to the C-suite: if we invest in robust compliance and proactively address issues, we can avoid criminal prosecution altogether.

What if aggravating factors exist, such as senior-level involvement or prior misconduct? If the company cooperates and remediates in good faith, the policy still provides for reduced penalties, non-prosecution agreements, and shorter resolution terms. In other words, the DOJ offers a “near miss” safety net for companies that fall short of full eligibility but act responsibly.

The takeaway is clear: Compliance is not just a cost center but a value driver. The CEP recognizes that companies should be rewarded for coming forward, cooperating, and fixing problems. That means compliance professionals must build systems that detect misconduct early, encourage internal reporting, and enable swift action. When a crisis hits, your response will not just shape your company’s future; it may be the difference between a decline and a prosecution.

Voluntary Self-Disclosure

The DOJ’s Criminal Division strongly encourages companies to voluntarily self-disclose potential misconduct as early as possible, even before completing an internal investigation. To qualify under the CEP, a disclosure must meet several key criteria: it must be made to the Criminal Division (or in good faith to another DOJ component involved in the resolution), concern previously unknown misconduct, not be required by any existing legal obligation, and occur before any imminent threat of disclosure or government investigation arises. Additionally, the disclosure must be made within a “reasonably prompt” timeframe, with the company bearing the burden of proving timeliness.

The DOJ proposes a limited exception for the new Corporate Whistleblower Awards Pilot Program. Suppose a whistleblower reports misconduct internally and to the DOJ. In that case, a company may still qualify for the presumption of declination, but only if it self-discloses to the DOJ within 120 days of the internal report and meets all other voluntary disclosure conditions.

This guidance underscores the urgency and importance of real-time reporting mechanisms, strong internal controls, and rapid compliance response protocols. Timely self-disclosure is not just encouraged; it is now a strategic imperative in mitigating enforcement risk.

What is Full Cooperation?

To earn full cooperation credit under the CEP, a company must go beyond the general requirements of the Principles of Federal Prosecution of Business Organizations (Justice Manual 9-28.000) and meet six key obligations:

  1. Disclosure of All Relevant Facts: A company must share all non-privileged, relevant facts it knows, including facts about individuals responsible for the misconduct, regardless of their rank, whether internal or external to the company.
  2. Timely and Specific Information Sharing: This includes facts obtained through any internal investigation, updates during that investigation, and specific attributions of facts to sources. The company must also clearly identify all involved parties.
  3. Proactive Cooperation: Companies must voluntarily disclose relevant facts, even if prosecutors do not specifically request them. They are also expected to alert the DOJ to any avenues of obtaining evidence not in the company’s possession but known to them.
  4. Preservation and Disclosure of Documents: Relevant documents, including overseas ones, must be preserved, collected, and produced. Companies must detail such documents’ origin, custodians, and locations; facilitate third-party productions; and provide necessary translations. The company must prove the restriction if foreign law prevents disclosure and suggest viable alternatives.
  5. De-confliction: Companies must avoid actions that might interfere with DOJ investigations. If requested, they must delay certain investigative steps, such as employee interviews, for a narrowly tailored period to protect DOJ priorities.
  6. Availability of Individuals for Interviews: Subject to constitutional protections, companies must make current and former employees (including those overseas) available for DOJ interviews and facilitate third-party interviews where possible.

These standards ensure that cooperation is meaningful, timely, and valuable to the DOJ’s efforts, rewarding companies that truly support investigations with favorable outcomes under the CEP.

Timely and Appropriate Remediation

Under the CEP, timely and appropriate remediation is a non-negotiable component of earning cooperation credit and potentially avoiding prosecution. And for compliance professionals, it is a clarion call to action. First, the company must conduct a root cause analysis, a genuine examination of what went wrong, why, and how to prevent it from happening again. It’s not about blaming a few bad apples but addressing systemic issues that allowed the misconduct to take root. Did a cultural blind spot develop in a high-risk market? Was there a breakdown in oversight or a failure to escalate red flags? The DOJ expects thoughtful answers and corrective action.

Second, the company must demonstrate an effective compliance and ethics program tailored to its risk profile, business model, and resources. That means more than having policies on the books. DOJ evaluators are looking at leadership’s commitment, compliance’s access to the board, compensation tied to ethical performance, and real-time testing of program effectiveness. Box-checking won’t cut it.

Third, accountability is key. Companies must appropriately discipline wrongdoers, including those who failed in their supervisory duties, and ensure they retain and safeguard business records, including communications on personal devices and ephemeral apps.

Finally, remediation includes showing that the company understands the seriousness of the misconduct and is proactively reducing future risk. This is about culture, not cosmetics.

In short, remediation is proof of your values in action. It is the difference between performative compliance and real commitment. Suppose you’re building a credible compliance program in today’s enforcement environment. In that case, remediation must be embedded in your DNA because the DOJ is watching, and your organization’s future may depend on how you respond.

Providing Cooperation Credit

Finally, there is the cooperation credit. Hopefully, we have finally moved past the Kenneth Polite formulation of super, double-secret, undefined “we know it when we see it” cooperation. Cooperation credit here will be earned through demonstrable, high-quality, timely actions. Cooperation is assessed on a sliding scale based on how extensively and effectively a company supports the government’s investigation. Once a company meets the minimum threshold for cooperation, prosecutors evaluate factors such as scope, quantity, quality, timing, and the overall impact of the cooperation provided.

Importantly, cooperation credit starts at zero and increases only with meaningful contributions, and there is no presumption of full credit. The DOJ now distinguishes between cooperation levels by varying the starting point within the U.S. Sentencing Guidelines fine range, and the percentage of fine reduction awarded. Companies that delay cooperation may significantly reduce their potential credit.

Waiver of attorney-client privilege or work product protections is not required to receive cooperation credit. If a company claims its financial condition limits its ability to cooperate, it must provide supporting documentation. The DOJ will carefully evaluate any such claims. Ultimately, the message is clear: to earn meaningful credit, cooperation must be real, proactive, and sustained. But at least it is now defined and not “We know it when we see it.”

Resources:

CRM White Collar Enforcement Plan

Revised CEP

CRM Monitor Memo

Categories
Blog

TD Bank: Part 5 – The Reckoning

Today, I want to review the OCC Consent Order to see the bank’s requirements. This is separate from the DOJ requirements under the Bank’s Plea Agreement(s) and the FinCEN Consent. Further, the DOJ and OCC have mandated separate monitors under their attendant settlement agreements. FinCEN’s Order imposes a four-year independent monitorship, and the DOJ Plea Agreement a 3-year Monitorship. As Matt Kelly noted in Radical Compliance, the remediation steps include:

  • Establishing a dedicated compliance committee at the board level;
  • Drafting a plan within 120 days to overhaul its AML compliance program;
  • Hiring an independent compliance consultant within 60 days to conduct their review of TD’s compliance program;
  • Hiring a senior-level AML compliance officer;
  • Staffing up a more robust AML compliance function; and
  • Implementing new policies, procedures, training, and all the other usual requirements we’ve seen from similar banking settlements.

In this blog post, we will consider some of the highlights above and beyond these remediation steps that the Bank must perform.

The Action Plan

The enforcement order mandates that within 120 days, TDBNA must submit a comprehensive BSA/AML Action Plan to the Examiner-in-Charge for approval. This plan must address the bank’s deficiencies in adhering to the Bank Secrecy Act (BSA) and Anti-Money Laundering (AML) regulations. The action plan must include detailed corrective actions, reasonable timelines for implementation, and clear accountability for executing these measures. The board of directors is responsible for overseeing the implementation, ensuring adherence, and monitoring progress, with formal reviews required at least annually.

The Action Plan must be subject to continuous updates and modifications as necessary, particularly if directed by the Examiner-in-Charge or if the bank identifies further areas of improvement. The Examiner-in-Charge must approve any significant deviations or material changes to the plan. TDBNA must also submit quarterly progress reports detailing corrective actions, outstanding issues, and timelines for resolving compliance deficiencies, ensuring transparency in the bank’s efforts to remediate its AML program.

In the event of ongoing issues or independent assessments highlighting further weaknesses, the bank must provide written documentation to the Examiner-in-Charge. The board’s review and response to these assessments will drive accountability and ensure the continuous improvement of TDBNA’s BSA/AML compliance program.

AML Program Assessment and Remediation

TDBNA’s response to its enforcement action underlines the critical role of independent third-party assessments in fortifying a bank’s BSA/AML program. The bank must engage an independent consultant, approved by the OCC, to conduct an exhaustive end-to-end review of its entire BSA/AML framework. This process begins within 60 days of the enforcement order, where TDBNA must submit the proposed consultant’s qualifications, along with a detailed scope of work and timeline, for the OCC’s review. The consultant’s expertise in BSA/AML compliance is a key requirement to ensure the assessment is thorough and capable of addressing the bank’s regulatory obligations.

The independent consultant’s primary objective is to assess the bank’s BSA/AML program against its risk profile, identifying any gaps or weaknesses in its structure and operations. This review will examine whether the bank’s transaction monitoring, suspicious activity reporting, and overall governance are robust enough to meet the demands of U.S. regulatory requirements and the bank’s evolving risk landscape. The consultant’s findings will be critical in determining how effectively TDBNA’s AML framework functions and where improvements are necessary.

Upon completing the review, the consultant will deliver a comprehensive report to TDBNA’s board of directors detailing any deficiencies in the bank’s BSA/AML program. The report will also include recommendations for remediation, ensuring the bank addresses areas of concern in a structured and strategic manner. To ensure transparency and accountability, the board will document its review of the report in official meeting minutes, which must be submitted to the OCC. Additionally, the independent consultant will provide a copy of the report directly to the Examiner-in-Charge, ensuring that regulators have a clear view of the findings and the bank’s planned corrective actions.

Beyond simply identifying deficiencies, the bank must ensure it takes prompt and effective action to remediate the issues raised by the independent consultant. TDBNA must incorporate the necessary remediation efforts into its existing BSA/AML Action Plan, ensuring that all gaps are addressed promptly and comprehensively. This integration is crucial, as failure to properly implement corrective measures could lead to further regulatory actions and potentially severe penalties. The OCC will continue to monitor the bank’s progress by submitting updated action plans and progress reports.

Ultimately, this process highlights the importance of maintaining a dynamic and adaptable BSA/AML program that can respond to emerging risks and regulatory expectations. TDBNA’s engagement with an independent consultant reminds all financial institutions that complacency in AML compliance is not an option. By continually assessing and improving their compliance frameworks, banks can better mitigate risk, avoid regulatory scrutiny, and ensure their AML programs remain strong, effective, and compliant with the law.

Three is Not Always a Crowd

Are you beginning to see a pattern here? The Bank engaged third-party consultants who identified significant weaknesses in its AML program and reported these issues to the Bank’s AML leadership. In 2018, one consultant noted that increasing regulatory requirements and transaction volumes would pressure AML operations, making it difficult to meet demands and deadlines. Additionally, the consultant found that The Bank’s testing of its transaction monitoring scenarios took less than the industry average, highlighting inefficiencies in its ability to assess and capture suspicious activity.

In 2019, another consultant flagged sub-optimal transaction monitoring scenarios based on outdated parameters. These outdated scenarios generated many alerts, overwhelming the AML team and limiting their ability to focus on truly high-risk customers and transactions. This finding pointed to a broader issue in the bank’s ability to adapt its monitoring systems to changing regulatory and risk environments, significantly undermining the effectiveness of its AML compliance efforts.

In 2021, a third consultant identified additional limitations within the Bank’s transaction monitoring program, particularly its technology infrastructure. The consultant found that the bank faced technological barriers that restricted its ability to develop new scenarios or adjust existing parameters, further hampering its AML efforts. These ongoing challenges reflect a broader need for the Bank to modernize its systems and ensure its AML program is agile enough to meet regulatory expectations and address emerging risks effectively.

Restriction on Growth

The Consent Order also required the Bank to maintain its total consolidated assets at or below the level reported on September 30, 2024. This mandate prevents the banks from increasing their average total consolidated assets beyond this threshold until they achieve compliance with all actionable articles of the order. The total consolidated assets will be measured using the banks’ respective Consolidated Reports of Condition and Income.

The asset restrictions will remain in place until the banks meet all compliance obligations outlined in the order. However, the Deputy Comptroller can temporarily suspend the asset cap in unusual circumstances. If the banks fail to meet compliance deadlines, the Deputy Comptroller may require a reduction of up to 7% of their total consolidated assets, as reported in the most recent calendar quarter.

If the Bank is notified that a reduction is necessary, it must submit a plan within 30 days for the Comptroller’s approval and have 60 days to implement the asset reduction. If non-compliance continues beyond the first year, the Deputy Comptroller may impose an additional reduction of up to 7% annually, with the same plan submission and implementation requirements applying each successive year until full compliance is achieved.

Jon Hill wrote in Law360 that this is only the second time “that a federal banking agency has slapped such handcuffs on a financial institution’s overall growth.” The first was Wells Fargo, slapped for its fraudulent accounts scandal. Moreover, while the Wells Fargo “cap has remained in place much longer than many observers originally expected, the OCC has designed its cap for TD Bank with more of a need for remedial speed in mind. In particular, the OCC order establishing the cap includes express provisions that allow the agency to reduce the size limit — that is, tighten the cuffs — by up to 7% annually if the bank does not meet certain deadlines for strengthening its U.S. anti-money laundering compliance.” The article quoted Julie A. Hill, a banking law professor and dean at the University of Wyoming College of Law, for the following, “where the asset cap has gone on for years and years as the bank has tried to get compliant.”

Put Money Where Their Mouth Is

Even more than the commitment to do business ethically and in compliance with its AML/BSA requirements, the Bank must also financially commit to compliance. The Order requires that before the Bank can declare or pay dividends, engage in share repurchases, or make any other capital distributions, the Board of Directors must certify in writing to the Examiner-in-Charge that adequate resources and staffing have been allocated to the remediation efforts required by the OCC’s order. This certification must be submitted at least 30 days before any proposed capital action. It must include a detailed description of the Bank’s current allocation of compliance resources, its progress in remediation, any anticipated changes in resource allocation, and the funding source for the proposed payment or distribution. The goal is to ensure that remediation efforts take priority over capital distributions.

Join us next time, where I will consider TD Bank and the Caremark Doctrine.

Resources

OCC

OCC Press Release

Consent Order 

Civil Money Penalty 

DOJ

TD Bank US Holding Company Information

TD Bank N.A. Information

TD Bank US Holding Company Plea Agreement and Attachments

TD Bank N.A. Plea Agreement and Attachments

Merrick Garland Remarks

Nicole Argentieri Remarks

FinCEN

Press Release

Consent Order

Categories
Blog

The Trafigura FCPA Enforcement Action – Part 4 – Lessons Learned

We conclude our exploration of the resolution of the FCPA enforcement action involving the Swiss trading firm G Trafigura Beheer B.V. (Trafigura), an international commodity trading company with its primary operations in Switzerland. The company pleaded guilty and will pay over $126 million to resolve an investigation stemming from the company’s corrupt scheme to pay bribes to Brazilian government officials to secure business with Brazil’s state-owned and state-controlled oil company, Petróleo Brasileiro S.A. – Petrobras (Petrobras). The matter was resolved via a Plea Agreement. Information detailing the company’s conduct was also issued.

Despite substantial violations of the FCPA and its extension into the corporate offices, Trafigura received the 10% discount noted above. The message from this enforcement action is the cost of failing to self-disclose, creating liability under the FCPA and creating jurisdiction for the DOJ to bring an enforcement action, denial that you have done anything wrong, failure to cooperate (at least initially), and not sanctioning any of the culpable company actors. In other words, there is a bit of reverse logic and analysis in this case. However, as noted several times, the DOJ rewarded Trafigura with some credit and gave them a discount. Most importantly, and perhaps inexorably, Trafigura was not required to retain a monitor.

Remediation 

While most of the remediation is reported as standard, the one item that every compliance professional should consider is that the company proactively discontinued using third-party agents for business origination. This point is perhaps the most significant, as we have now seen the DOJ call out Albemarle and SAP for discontinuing their use of third-party agents.

As Matt Kelly noted in Radical Compliance, in his discussion of Guvnor FCPA enforcement action, “This is the latest in a string of FCPA enforcement cases where we’ve seen a big, structural change to the sale function. Albemarle eliminated its use of third-party sales agents as part of its FCPA settlement last year; SAP eliminated its third-party sales commission model globally as part of its own FCPA settlement announced in January. Now we have a third global enterprise going that same route, reducing its FCPA risk in a deep, permanent way by restructuring its sales operations.” With Trafigura, we now have a fourth.”

As I noted in my review of the Albemarle and SAP enforcement actions, SAP eliminated its third-party sales commission model globally, prohibited all sales commissions for public sector contracts in high-risk markets, and enhanced compliance monitoring and audit programs, including the creation of a well-resourced team devoted to audits of third-party partners and suppliers. Albemarle changed its approach to sales and its sales teams. Guvnor also moved from being a third-party agent to a direct sales force.

Moving to a direct sales force does have its risks, which must be managed, but those risks can certainly be managed with an appropriate risk management strategy, monitoring of the strategy, and improvement; those risks can be managed. Yet there is another reason, and more importantly, a significant business reason, to move towards a direct sales business model. Whenever you have a third-party agent or anyone else between you and your customer, you risk losing that customer because your organization does not have a direct relationship with the customer. A direct sales business model will give your organization more direct access to your customers.

Another exciting aspect of this approach used by Albemarle, SAP, and Trafigura is that it is not an approach laid out in either the 2020 FCPA Resource Guide, 2nd edition, or the 2023 Evaluation of Corporate Compliance Programs. The companies developed all of these strategies based on their own analysis and risk models. It may have come from a realization that the risk involved with 3rd party sales models was too great, that the companies wanted more control over their sales, or another reason. Whatever the reason for the change, the DOJ clearly noted each organization and viewed it affirmatively.

Bribery Schemes

This area is essential for all compliance professionals to take note of. The bribes were initially funded with a $ 0.20 surcharge or uplift for every barrel of oil traded. With the price of oil fluctuating wildly at the time in question, between $60 to $100 per barrel, I am not sure such a small amount would even seem anomalous. It would not rise to a rounding error but generate $19 million in bribes. While I am not sure that the bribery scheme was designed to be so hard to detect, the reality is that no compliance professional could look at the trades and determine if a bribe was baked into the pricing.

Yet there was even a deeper part of the bribery scheme. Executives at Trafigura and corrupt traders at Petrobras prearranged the oil trading prices rather than letting the market determine them. The information noted, “The Trafigura Executive 2 and Brazilian Official 1 agreed to prices for trades of oil products and bribe amounts for each trade. After determining the price, Trafigura Executive 2 instructed Trafigura traders to negotiate with Petrobras, which Trafigura Executive 2 knew to be a sham, to arrive at the pre-agreed price.” [emphasis supplied]

Finally, another set of bribes was funded through an unrelated business unit. This occurred when one of the two corrupt Trafigura executives involved in the bribery scheme was transferred to run the company’s Singapore business unit. From there, this corrupt executive had a corrupt third party in Hong Kong bill the Singapore business unit for non-existent consulting services related to the Chinese market for $500,000. This money funded additional bribes to corrupt Petrobras employees. This extra step would require someone in compliance to connect the dots between a corrupt third-party bribery scheme in Singapore and China and the corruption at Petrobras in Brazil.

Lack of a Monitor

The following DOJ Memo governs the decision of whether a company needs a monitor: Revised Memorandum on Selection of Monitors in Criminal Division Matters, released in March 2023. The memo has 10 factors a prosecutor must consider.

  1. Did the corporation voluntarily self-disclose?
  2. At the time of the resolution and after a thorough risk assessment, has the company implemented an effective compliance program and sufficient internal controls to detect and prevent similar misconduct in the future?
  3. At the time of the resolution, the company had adequately tested its compliance program and internal controls to demonstrate that they would likely detect and prevent similar misconduct.
  4. Whether the underlying criminal conduct was long-lasting or pervasive across the business organization or was approved, facilitated, or ignored by senior management, executives, or directors (including through a corporate culture that tolerated risky behavior or misconduct or did not encourage open discussion and reporting of possible risks and concerns),.
  5. Whether the underlying criminal conduct involved exploiting an inadequate compliance program or system of internal controls.
  6. Did the conduct involve the active participation of compliance personnel?
  7. Did the company take adequate investigative or remedial measures to address the underlying criminal conduct, including terminating business relationships and practices that contributed to it?
  1. At the time of the resolution, the company’s risk profile had substantially changed.
  2. Whether the corporation faces any unique risks or compliance challenges.
  3. Is the company subject to other oversight?

A review of the Information and Plea Agreement reveals no self-disclosure. Equally significantly, there is no information about whether the company has implemented an effective compliance program or sufficient controls, let alone tested them. According to the data, the conduct was long-lasting across multiple business units. If there were internal controls in place, they were undoubtedly inadequate. There does not appear to be involvement in the compliance function. The only positive factor from the resolution documents is that Trafigura did terminate its use of third parties to initiate and foster business development, but that appears to be the only factor they have met.

Writing again in Radical Compliance, Matt Kelly said, “Either way, these cases send mixed messages to the compliance community. It looks like you can get away with not self-disclosing misconduct and perhaps even slow-rolling your cooperation if you’re prepared to invest lots in a newly invigorated compliance program and tolerate the Fraud Section as your new BFFs for the next three years of a settlement agreement.”

If the DOJ has discontinued its monitoring program or changed the requirements, it is undoubtedly its prerogative to do so. It would be helpful if they communicated that change to the compliance community.

Categories
Compliance Tip of the Day

Compliance Tip of the Day: How an Investigation Informs Remediation

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements.

Whether you’re a seasoned compliance professional or just starting your journey, our aim is to provide you with bite-sized, actionable tips to help you stay on top of your compliance game.

Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law.

Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

In this episode, we consider why and how an investigation can be a key to your remediation after an incident occurs.

For more information on the Ethico ROI Calculator and a free White Paper on the ROI of Compliance, click here.

Categories
Blog

Ten Top Lessons from Recent FCPA Settlements – Lesson No. 9, Internal Controls

Over the past 15 months, the Department of Justice (DOJ) and Securities and Exchange Commission (SEC) have made clear, through three Foreign Corrupt Practices Act (FCPA) enforcement actions and speeches, their priorities in investigations, remediations, and best practices compliance programs. Every compliance professional should study these enforcement actions closely for the lessons learned and direct communications from the DOJ. They should guide not simply your actions should you find yourself in an investigation but also how you should think about priorities.

The three FCPA enforcement actions are ABB from December 2022, Albemarle from November 2023, and SAP from January 2024. Taken together, they point out a clear path for the company that finds itself in an investigation, using extensive remediation to avoid monitoring and provide insight for the compliance professional into what the DOJ expects in an ongoing best practices compliance program.

Over a series of blog posts, I will lay out what I believe are the Top Ten lessons from these enforcement actions for compliance professionals who find themselves in an enforcement action. Today, we continue with Number 9, Internal Controls. The DOJ has made it clear that any organization under FCPA scrutiny must use its internal controls to continuously test, monitor, and improve all aspects of its compliance program.

SAP

As a part of its remediation, the company conducted a gap analysis of internal controls. This remediation found those internal controls “lacking.” SAP also undertook a “comprehensive risk assessment focusing on high-risk areas and controls around payment processes and enhancing its regular compliance risk assessment process.” Using this risk assessment as a starting point, the company performed a gap analysis, determined the overall remediation regime needed, and effectuated that remediation. 

ABB

The ABB Plea Agreement reported that ABB “performed a root-cause analysis of the conduct at issue. From there, the company revamped its internal controls, investing significant additional resources in control testing and monitoring throughout the organization. While not often seen as a part of internal controls, the company restructured its reporting by internal project teams to ensure compliance controls oversight.

Additionally, ABB essentially created its monitoring program around controls, testing its compliance program, and reporting to the DOJ. In the “Written Work Plans, Reviews, and Reports” section, ABB agreed to conduct a first review and prepare a report, followed by at least two follow-up reviews and reports. But more than simply reporting on control testing, ABB agreed to create and submit for review a work plan for this ongoing testing of its compliance program, as the program was detailed in the DPA. The DPA specified, “No later than one (I) year from the date this Agreement is executed, the Company shall submit to the Offices a written report setting forth:

  • a complete description of its remediation efforts to date;
  • a complete description of the controls testing conducted to evaluate the effectiveness of the compliance program and the results of that testing; and
  • It proposes to ensure that its compliance program is reasonably designed, implemented, and enforced so that the program is effective in deterring and detecting violations of the FCPA and other applicable anti-corruption laws.”

The bottom line is that all these companies worked very hard to significantly enhance their controls, testing, and monitoring and then improve based on that information. None of the actions taken by these companies were particularly new or even innovative. Indeed, these strategies have been available from the DOJ since at least the first edition of the FCPA Resource Guide in 2012. It was, however, the work by the company to understand the deficiencies in their internal controls regime and their superior efforts to upgrade them.

Albemarle

The Albemarle SEC Order was instructive regarding internal controls for a different reason than we have been considering throughout this series. The Order detailed a series of internal control failures by the company across multiple business units in several other countries. The entire story painted a picture of a company that did not have adequate or easily overridden internal controls.

Vietnam. The Order noted, “Albemarle’s system of internal accounting controls was insufficient to prevent or detect these improper payments, which Albemarle Singapore falsely recorded as legitimate commissions in books and records consolidated into Albemarle’s financial statements.”

India. A backdated agreement increased an India agent’s commission multiple times without compliance oversight or approval. Commissions went from “extremely high” to “far from any possible realistic justification.” Finally, “the agreement called for payment of a three percent commission to India Agent, a rate three times higher than that paid to Albemarle’s existing agent for India.”

Indonesia. Albemarle’s system of internal accounting controls was insufficient to prevent or detect the improper payments made to and through Indonesia Agent, which Albemarle Singapore falsely recorded as legitimate commissions and business expenses in books and records consolidated into Albemarle’s financial statements.”

China.  When an Albemarle business director questioned China Agent’s compensation as “high,” an Albemarle Netherlands business director provided the business justification that he anticipated significant returns on the contract.

UAE.  No due diligence was conducted on an agent until after the agent agreement had been executed. The agent provided no discernible services other than conveying confidential tender evaluations and competitors’ bids obtained from the customer.

Each of these resolutions drives home the importance of internal controls, creation, and remediation as a key part of your overall compliance regime during any investigation. The sooner you can start on your internal controls, the better off you will be in your negotiations with the DOJ and SEC.

Categories
Blog

Ten Top Lessons from Recent FCPA Settlements – Lesson No. 4, Start with a Root Cause Analysis

Over the past 15 months, the Department of Justice (DOJ) and Securities and Exchange Commission (SEC) have made clear, through three Foreign Corrupt Practices Act (FCPA) enforcement actions and speeches, their priorities in investigations, remediations, and best practices compliance programs. Every compliance professional should study these enforcement actions closely for the lessons learned and direct communications from the DOJ. They should guide not simply your actions should you find yourself in an investigation but also how you should think about priorities.

The three FCPA enforcement actions are ABB from December 2022, Albemarle from November 2023, and SAP from January 2024. Taken together, they point out a clear path for the company that finds itself in an investigation, using extensive remediation to avoid monitoring and provide insight for the compliance professional into what the DOJ expects in a best practices compliance program on an ongoing basis.

Over a series of blog posts, I will lay out what I believe are the Top Ten lessons from these enforcement actions for compliance professionals who find themselves in an enforcement action. Today, we continue with Number 4, Root Cause, Risk Assessment, and Gap Analysis. Your remediation should begin with a root cause analysis. From there, move on to a risk assessment and gap analysis, and then you are ready to start your complete remediation.

SAP

The SAP Deferred Prosecution Agreement (DPA) laid out the best example of how this works in practice. The DPA reported extensive remediation by SAP, and the information provided in the DPA is instructive for every compliance professional. SAP engaged in a wide range of remedial actions. It all started with a root cause analysis. Root Cause analysis was enshrined in the FCPA Resource Guide, 2nd edition, as one of the Hallmarks of an Effective Compliance Program. It stated, “The truest measure of an effective compliance program is how it responds to misconduct. Accordingly, for a compliance program to be truly effective, it should have a well-functioning and appropriately funded mechanism for the timely and thorough investigations of any allegations or suspicions of misconduct by the company, its employees, or agents. An effective investigation’s structure will also have an established means of documenting the company’s response, including any disciplinary or remediation measures taken.”

This means a company should respond to the specific incident of misconduct that led to the FCPA violation. This means your organization “should also integrate lessons learned from misconduct into the company’s policies, training, and controls. To do so, a company will need to analyze the root causes of the misconduct to timely and appropriately remediate those causes to prevent future compliance breaches.” The SAP DPA noted that SAP engaged in the following steps based on these factors:

1. Conducted a root cause analysis of the underlying conduct, then remediated those root causes through enhancement of its compliance program;
2. Conducted a gap analysis of internal controls, remediating those found lacking;
3. Undertook a “comprehensive risk assessment focusing on high-risk areas and controls around payment processes and enhancing its regular compliance risk assessment process”;
4. SAP documented using “comprehensive operational and compliance data” in its risk assessments.

In addition to having a mechanism for responding to the specific incident of misconduct, the company’s compliance program should also integrate lessons learned from any misconduct into the company’s policies, training, and controls on a go-forward basis. To do so, a company will need to analyze the root causes of the misconduct and remediate those causes promptly and appropriately to prevent future compliance breaches. This SAP did it during its remediation phase.

Albemarle

Albemarle also received credit “because it engaged in extensive and timely remedial measures.” This remedial action began based on the company’s root cause analysis of its FCPA violations.
This root cause analysis led to a risk assessment, which led to remediation. All of these steps were taken during the pendency of the DOJ investigation so that when the parties were ready to resolve the matter, Albemarle had built out an effective compliance program and had tested it.

ABB

ABB also did an excellent job in its remedial efforts. According to the ABB Plea, ABB “engaged in extensive remedial measures, including hiring experienced compliance personnel and following a root-cause analysis of the conduct,” which led to the FCPA enforcement action. More on the ABB remediation later.

Each entity worked diligently to rebuild its compliance programs from the ground up. Whatever the faults of their prior compliance programs, each company was quite diligent in revamping their compliance regimes. While each company builds out a program based on its own risk, there is quite a bit of guidance you can draw from if your company finds itself in this position.

Here, the DOJ communicates that your remedial measures should start with a root cause analysis of the FCPA violation. From there, move to a risk assessment and internal control gap analysis to create a clear risk management strategy.