Categories
Popcorn and Compliance

Popcorn and Compliance: Frankenstein It’s Alive: Innovation, Governance, and the Responsibility of the Creator

This October we return to one of my all-time favorites, the Universal Picture Classic monsters. Over the years, I have looked at all the classics, Dracula, The Mummy, The Wolfman, The Invisible Man, took detours in the films of Val Lewton and the Hammer Studios. This year, I wanted to return for a deep dive into the first five Frankenstein movies. We will consider the original, the Bride of Frankenstein, Son of Frankenstein, Ghost of Frankenstein and Frankenstein Meets the Wolfman. In this first episode we consider the original and one of the greatest horror movies of all-time, Frankenstein, released in 1931. In this exploration, I have used my AI friends, Timothy and Fiona to provide commentary.

Film Synopsis

James Whale’s Frankenstein remains one of the foundational movies of American horror, with Colin Clive as Henry Frankenstein and Boris Karloff giving us the definitive cinematic image of the Monster. Henry retreats to his laboratory with his assistant Fritz, determined to discover the secret of life. His experiment succeeds, but a crucial mistake has already occurred: Fritz has supplied the brain identified in the film as abnormal rather than the intended brain. Henry brings his creation to life without understanding what he has created, without controls for managing it, and without any real plan for what comes next. The resulting tragedy ultimately sends creator and creation toward their confrontation at the burning windmill.

Key Highlights

  • Innovation without governance is simply uncontrolled risk.
  • The abnormal brain is a third-party and supply-chain failure.
  • Waldman represents credible challenge without sufficient authority.
  • Henry abandons responsibility when responsibility matters most.
  • The catastrophe begins before the Monster escapes.

Popcorn and Compliance takeaway: Do not wait until the Monster is running through the village to conduct the risk assessment.

Timothy and Fiona are AI generated voices courtesy Notebook LM.

Categories
Blog

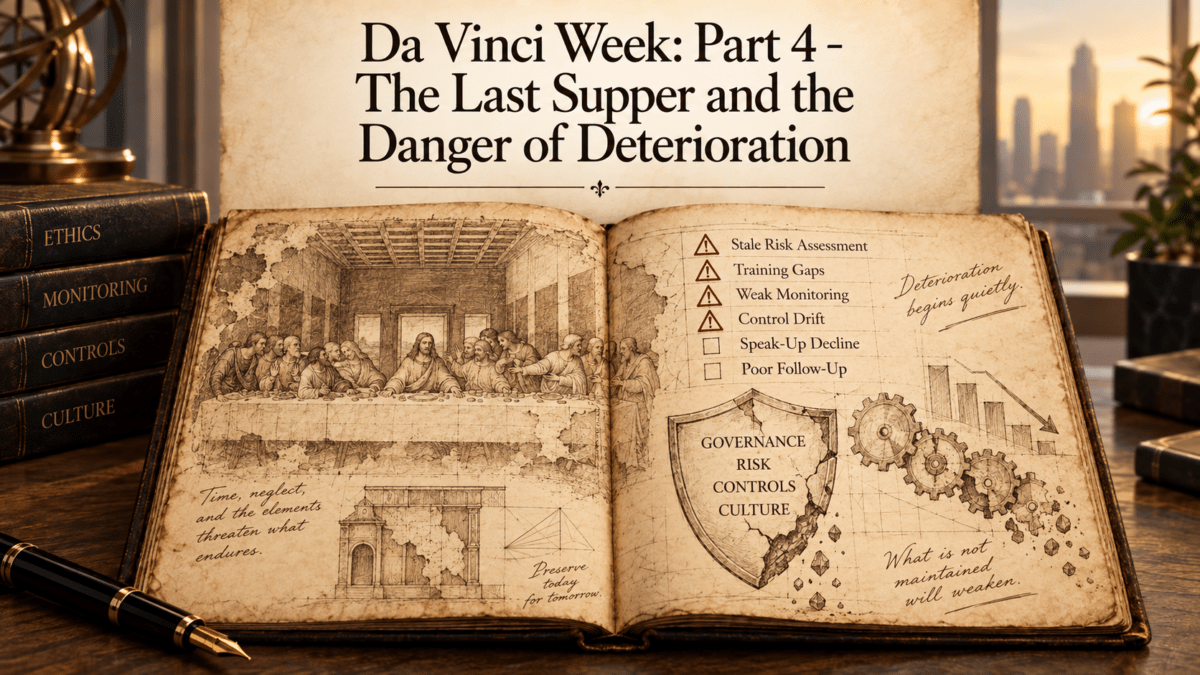
Da Vinci Week: Part 4 – The Last Supper and the Danger of Deterioration

In the previous post in the Leonardo Compliance Framework, Leonardo’s flying machines gave us Innovate, the principle that Compliance should help organizations capture the benefits of emerging technology while establishing governance appropriate to the risks. Yet approving and deploying a new technology, control, or compliance process does not demonstrate that it will remain effective over time. The organization must continue to evaluate whether the system operates as intended as the business and its risk environment change. That brings us to the fourth principle in the Leonardo Compliance Framework: Monitor.

For this lesson, we turn to Leonardo’s The Last Supper. Leonardo experimented with a painting technique that provided greater artistic flexibility than conventional fresco methods. The result was extraordinary, but the physical work proved vulnerable to deterioration, and environmental conditions and later damage compounded those problems.

For compliance professionals, the lesson is not that experimentation was a mistake. It is that implementation marks the beginning of the control lifecycle, not its end. A system that operates effectively when introduced may weaken as people, processes, technology, incentives, and business conditions change. Modern compliance program effectiveness therefore requires more than evidence that a control exists. Management needs evidence that the control continues to work.

Implementation Is Not Effectiveness

Companies appropriately recognize major implementation milestones. A new third-party platform goes live, an updated Code of Conduct is launched, an investigation protocol is approved, or a sanctions-screening system is installed. These accomplishments demonstrate that the organization has taken action, but they do not establish that the underlying risk is being managed effectively.

Consider a third-party due diligence system implemented across a global enterprise. At launch, the workflow operates as designed. Business sponsors submit required information, higher-risk third parties receive enhanced review, approvals are documented, and Compliance can monitor the process. Two years later, an acquisition may have added thousands of vendors, employees may have developed workarounds because they consider the process too slow, regional teams may interpret risk classifications differently, and data feeds may no longer operate consistently. The system still exists, and the policy remains in force, but the control environment has changed.

This is the central monitoring challenge. Controls operate inside dynamic organizations. A gifts and entertainment process may become inadequate when the company enters markets involving greater interaction with government officials. Sanctions controls may require adjustment following significant geopolitical developments. A conflict-of-interest process may become less effective after an acquisition substantially expands the workforce. Controls designed for one business model may no longer fit another.

Effective monitoring should therefore connect directly to risk assessment. When the company’s risk environment changes, management should evaluate whether the controls designed for the previous environment remain appropriate. Successful implementation at one point in time cannot establish continuing effectiveness.

Monitoring and Testing Provide Different Evidence

Compliance professionals should distinguish between monitoring and testing because each provides different information about the control environment. Monitoring is generally continuous or recurring. It observes transactions, trends, exceptions, employee behavior, third-party activity, hotline information, investigation patterns, and other indicators that may reveal changes in risk or control performance. Testing is more focused and determines whether a particular control is appropriately designed and operating as intended.

Consider a control requiring enhanced approval for high-risk third parties. Monitoring may reveal how many high-risk relationships are approved, how long reviews take, which business units generate the most exceptions, and whether particular patterns are developing. Testing may examine a sample of approved relationships to determine whether required due diligence was performed, red flags were resolved appropriately, approvals occurred at the correct level, and documentation supports the final decision.

Monitoring provides signals about what may be changing. Testing provides evidence about whether specific controls perform as expected. Together, they allow the CCO to move beyond control existence and assess effectiveness.

That distinction matters most when presenting compliance information to senior management and the board. Activity metrics may demonstrate that processes are operating, but control testing provides a stronger basis for determining whether those processes are managing the intended risk.

Ownership Turns Monitoring Into Accountability

Monitoring becomes considerably less effective when control ownership is unclear. This is a recurring compliance problem because responsibilities often cross functional boundaries. Compliance may own the policy, Procurement may operate the process, IT may own the technology, Finance may process the payment, and the business may own the commercial relationship. When the control fails, each function may reasonably believe another function was responsible.

Effective control design should therefore identify an accountable owner responsible for ensuring that the control operates as intended. Compliance may provide oversight and challenge, and Internal Audit may provide independent assurance, but first-line functions should understand their responsibility for managing the underlying business risk.

Ownership should extend to the results of monitoring and testing. If testing identifies repeated exceptions, someone must determine whether the process requires modification. If a data feed fails, someone must restore it. If employees routinely circumvent a control, management must address the underlying behavior or process weakness. Monitoring without ownership produces information without accountability. The objective is not simply to identify control deficiencies but to drive a management response.

Use Data to Identify Deterioration Earlier

Data analytics has significantly expanded compliance functions’ ability to identify changes in risk and control performance. Traditional monitoring often depended on periodic reviews of relatively small samples. Modern analytics can help organizations identify patterns across larger populations and, in some circumstances, detect changes earlier.

Payment data may reveal unusual transaction patterns, while procurement information can identify repeated overrides or vendor concentrations. Third-party data may identify expired due diligence or changes in risk characteristics. Hotline and investigation data can reveal shifts in allegations and recurring root causes, while HR information may signal retaliation or cultural issues.

The objective is not to collect the greatest possible volume of information or create the most sophisticated dashboard. The purpose is to identify data that help management determine whether risks are changing or controls are weakening. Exceptions are particularly valuable in this respect. An individual exception is not necessarily evidence of misconduct because legitimate business circumstances may justify deviation from a standard process. Patterns of exceptions, however, can reveal important information about the control environment.

If one business unit generates substantially more third-party exceptions than comparable operations, Compliance should understand the reason. Repeated overrides near quarter-end may indicate commercial pressure. Due diligence consistently completed after engagement may indicate that the formal process no longer reflects how the business actually operates.

A mature program should therefore examine the frequency, rationale, approving authority, concentration, and recurrence of significant exceptions. When exceptions become routine, they can create an unofficial alternative process that exists alongside the formal control environment. Data become valuable when they reveal that divergence early enough for management to respond.

Investigations, Monitoring, and Remediation Should Form a Feedback Loop

Investigations provide some of the strongest evidence about how controls operate under actual business conditions. Their findings should therefore influence what a compliance program monitors. If an investigation discovers that employees circumvented third-party controls by classifying consultants as ordinary vendors, remediation should address the immediate classification weakness, while monitoring should examine whether comparable patterns exist elsewhere. If an investigation identifies improper discounts used to create funds for inappropriate payments, transaction monitoring can be adjusted to identify similar discount patterns. If a retaliation investigation reveals adverse employment consequences shortly after an employee raised a concern, a compliance professional could consider whether HR data can identify comparable patterns.

This creates a feedback loop. Investigations explain how a control failed in a particular case, monitoring helps determine whether the same weakness exists elsewhere or is recurring, and remediation addresses the underlying problem. Monitoring has limited value if the organization does not act on what it learns. When testing identifies a significant deficiency, management should understand why it occurred, whether it is systemic, what risk it creates, what corrective action is required, and who owns that remediation. The organization should then validate that the corrective action addressed the weakness.

This last step is important because remediation completion and remediation effectiveness are different concepts. Issuing a revised procedure or completing additional training may satisfy a project milestone without solving the underlying problem. Follow-up testing provides evidence that the remediation worked.

The compliance learning cycle should therefore move from investigation to monitoring, from monitoring to remediation, and from remediation to validation.

AI Requires Continuing Monitoring

AI provides a particularly clear example of why approval and implementation cannot end the governance process. A company may conduct extensive review before deploying an AI application by assessing the vendor, testing the system, evaluating data use, classifying risk, and establishing human oversight. Those steps are important, but the system and its operating environment can change after deployment.

Vendors may update models, employees may develop new uses, data may change, integrations may expand access, and capabilities may increase. For higher-risk applications, monitoring should therefore match the potential consequences. It may include performance testing, incident monitoring, reviewing material overrides, validating outputs, and reassessing after significant changes in functionality or use.

Agentic systems deserve particular attention because monitoring may need to address not only output quality but also the actions a system performs, the permissions it exercises, and whether it remains within its approved authority. The broader principle is the same as for any other compliance control. Governance should continue for as long as the organization relies upon the system.

Culture Also Requires Monitoring

Corporate culture presents a different monitoring challenge because no single metric establishes whether an organization has a strong ethical culture. Hotline reporting rates provide useful information but require interpretation. High reporting may indicate significant problems or employee confidence in the reporting system. Low reporting may reflect a healthy environment or fear of speaking up. Employee surveys provide additional information but capture sentiment at a particular moment, while investigation data reflect only matters that become known.

Compliance should therefore build a broader picture using multiple indicators, including reporting trends, employee surveys, exit interviews, focus groups, disciplinary information, HR data, investigation findings, and management assessments. Changes across these indicators may reveal emerging issues in particular business units, management teams, or employee populations.

Culture monitoring is especially important after leadership changes, acquisitions, restructurings, layoffs, or significant incentive changes because these events can quickly alter employee perceptions and behavior. Formal policies may remain unchanged while the operating culture deteriorates. As with other compliance risks, the objective is not perfect measurement. It is obtaining enough reliable information to identify material changes and respond appropriately.

The Danger of Deterioration

The Last Supper reminds us that implementation captures a moment in time while organizations continue to evolve. Personnel, technology, incentives, business models, markets, and risks change, and controls that once worked can weaken in response. An effective compliance program therefore needs monitoring, testing, clear ownership, useful data, and validated remediation. These disciplines allow the organization to identify deterioration before a control weakness becomes a larger compliance failure.

The practical lesson for the CCO is that implementation should never be confused with effectiveness. Monitoring and testing should provide different but complementary evidence about control performance. Ownership should ensure findings produce action, analytics should identify meaningful changes rather than simply populate dashboards, and remediation should be validated before the organization concludes the underlying problem is solved. That is Monitor, the fourth principle of the Leonardo Compliance Framework. A control deserves continuing confidence only when the organization has continuing evidence that it works.

From Monitoring to Documentation

Monitoring tells the organization what is happening, but institutional learning depends upon preserving what the organization learns. A company may conduct an effective investigation, identify a root cause, redesign a control, test the remediation, and reach a thoughtful risk decision. Yet, much of that value can disappear if the reasoning exists only in the memories of the people involved.

That brings us to the fifth and final Leonardo principle: Document. In Blog Post Five, Leonardo’s Notebooks: Documentation the Defensible Compliance Program, we will use Leonardo’s extraordinary record of observations, drawings, experiments, and ideas to examine documentation as a governance discipline. The discussion will focus on preserving significant compliance reasoning, establishing accountability, creating institutional memory, documenting remediation and AI governance decisions, and ensuring that what the organization learns today remains available to the people responsible for managing its risks tomorrow.

Categories
Blog

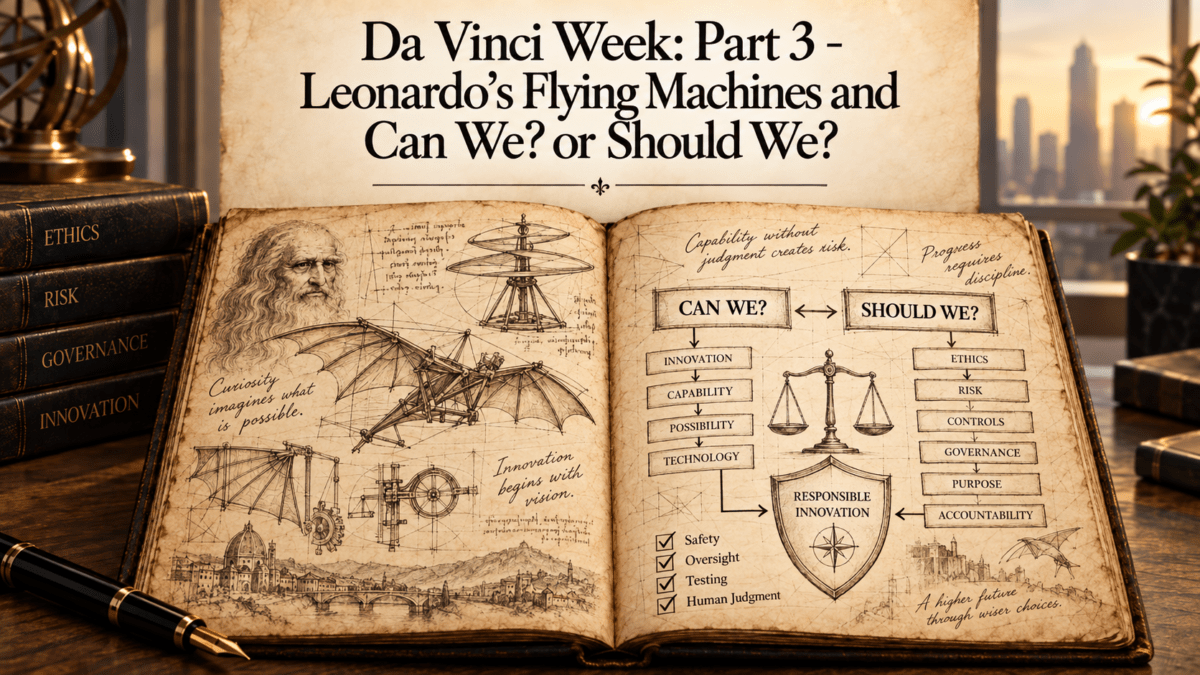
Da Vinci Week: Part 3 – Leonardo’s Flying Machines and “Can We?” or “Should We?”

In the first two posts in the Leonardo Compliance Framework, the Mona Lisa gave us Refine, the principle that an effective compliance program improves as the organization learns from experience. Leonardo’s anatomical studies gave us Investigate, the discipline of looking beneath misconduct to understand root causes, control failures, incentives, management decisions, and the organizational systems that produced the outcome. The third principle is Innovate.

For that lesson, we turn to Leonardo’s studies of flight and his designs for flying machines. Leonardo examined birds, air movement, wings, and mechanical systems as he considered whether technology could allow human beings to fly. Many of his concepts were far beyond the practical capabilities of his time, but they demonstrate an important characteristic of Leonardo’s work: he imagined capabilities that did not yet exist and then studied the systems necessary to make them possible.

For corporate compliance professionals in 2026, the analogy to artificial intelligence is particularly useful. AI is expanding what companies can automate, analyze, predict, generate, and increasingly act upon. Organizations are moving beyond using generative AI to draft documents and summarize information. AI systems are becoming embedded in business processes, interacting with corporate data, supporting consequential decisions, communicating with customers, evaluating third parties, and, through increasingly agentic capabilities, taking actions that previously required human intervention.

The compliance challenge is not whether companies should innovate. They will. The challenge is establishing governance that lets innovation create business value without creating unmanaged legal, ethical, operational, or compliance risk.

AI Governance Is Enterprise Governance

Compliance professionals have sometimes approached emerging technology as primarily the responsibility of IT, Cybersecurity, Data Privacy, or Legal. That division becomes increasingly difficult with AI because these systems can influence many of the activities a corporate compliance team already oversees. Indeed, the Evaluation of Corporate Compliance Programs (ECCP) anticipates these very concepts in its 2024 edition.

AI may assist with third-party due diligence, contract review, procurement, transaction analysis, hiring, customer communications, investigations, fraud detection, marketing, or pricing. Each application creates a different risk profile. A due diligence system may generate inaccurate information about a business partner. An investigation tool may expose privileged or confidential information. A sales application may generate communications inconsistent with company policies. An agent connected to corporate systems may take actions that historically required human approval.

The ECCP asks the following:

  • How does the company assess the potential impact of new technologies, such as artificial intelligence (AI), on its ability to comply with criminal laws?
  • Is management of risks related to the use of AI and other new technologies integrated into broader enterprise risk management (ERM) strategies?
  • What is the company’s approach to governance regarding the use of new technologies such as AI in its commercial business and in its compliance program?
  • How is the company curbing any potential negative or unintended consequences resulting from the use of technologies, both in its commercial business and in its compliance program? 

Visibility and Risk Should Drive the Control Environment

By 2026, asking whether a company uses AI provides little useful information. Management needs to understand how AI is being used and what authority particular systems possess. A tool that summarizes a public document presents a very different risk profile from a system that influences hiring, approves a third party, communicates with customers, accesses confidential information, initiates a transaction, changes corporate records, or takes actions across interconnected systems.

An AI inventory should therefore identify meaningful use cases, including the business owner, intended purpose, relevant data, third parties involved, decisions influenced by the technology, degree of autonomy, and applicable controls. The objective is not simply to count tools. It is to give management sufficient visibility to identify where material risk exists.

That visibility should support risk classification. Not every AI application requires the same level of governance. Classification should consider the system’s purpose, data sensitivity, potential consequences of error, degree of autonomy, affected populations, ability to review or reverse decisions, and applicable legal or regulatory requirements.

This is familiar territory for compliance professionals. Risk-based programs have long applied different levels of scrutiny to third parties, transactions, investigations, and markets. AI should follow the same principle. Higher-risk systems should receive greater review, stronger controls, and more rigorous monitoring.

Human Oversight Must Preserve Accountability

“Human in the loop” has become common language in AI governance, but a human’s presence alone does not create an effective control. Meaningful oversight requires defined responsibilities, appropriate expertise, sufficient capacity to review relevant outputs, and authority to challenge or override the system.

If one employee is nominally responsible for reviewing thousands of AI-generated recommendations each day, human oversight may exist on paper but not function in practice. The same problem arises when employees routinely accept recommendations because they assume the technology is more reliable than their own judgment.

The control should therefore define the reviewer’s responsibilities, the circumstances requiring additional scrutiny, the authority to reject recommendations, and how to handle material overrides or recurring disagreements between the system and human decision-makers. Most importantly, technology should not create an accountability vacuum. If an AI system contributes to a compliance failure, the organization should still be able to identify the business process owner, who approved the use case, who monitored it, and who had authority to intervene.

This becomes increasingly important with agentic systems. Traditional corporate controls generally assume identifiable human actors approve payments, create vendors, review contracts, or authorize higher-risk third parties. When technology performs some of those activities, the organization has effectively delegated authority to a system. The control environment must reflect that delegation while retaining human and organizational accountability for the outcome.

Third-Party AI and Data Risk

Many companies will obtain significant AI capabilities from external vendors rather than develop them internally. Using a vendor does not transfer accountability for the resulting compliance risk. Traditional third-party risk management principles remain relevant. The company should understand the service provided, the information the vendor receives, how data are used and retained, which subcontractors are involved, how incidents are managed, and what contractual rights the company has to obtain information, require remediation, audit, or terminate the relationship.

AI adds a dynamic element because models, features, and business uses can change after initial approval. Monitoring should therefore identify material changes in functionality, data use, vendor practices, or business application that could alter the original risk assessment.

Data governance is equally important. Companies need clear rules regarding which AI systems may access confidential business information, personal data, investigation materials, privileged communications, customer information, trade secrets, source code, and other sensitive information. As enterprise AI systems increasingly operate on internal data, blanket prohibitions will often give way to more precise governance defining approved systems, permissible data, access controls, retention, deletion, and accountability.

These issues require coordination across Compliance, Legal, Privacy, Cybersecurity, IT, Records Management, and the business. Effective governance depends upon clear responsibilities rather than overlapping or fragmented ownership.

Test Before Deployment and Monitor Afterward

Leonardo’s flying machines provide another useful innovation lesson. Test a design before you trust it with a critical task. AI testing should match the risk. Before deployment, the company should understand whether the system performs as intended, where its limitations lie, how it responds to unusual circumstances, whether users can manipulate it, and whether inaccurate or inconsistent outputs could create material consequences. Testing at implementation is not enough. Business conditions change, vendors update models, employees develop new uses, and system capabilities expand. An application that operated within acceptable parameters when approved may later present a different risk profile.

Higher-risk systems therefore require post-deployment monitoring that can identify performance issues, material changes, incidents, and circumstances requiring reassessment. Management should also establish when a system should be modified, restricted, or suspended.

This lifecycle approach connects Innovate to the next Leonardo principle, Monitor. Responsible innovation is not a one-time approval. Governance should continue throughout the period the organization relies on the technology.

Using NIST and ISO as Governance Architecture

Compliance professionals do not need to invent an AI governance structure from scratch. The NIST AI Risk Management Framework provides a useful approach to governance, mapping, measuring, and managing AI risk, while ISO/IEC 42001 offers a management-system perspective built around responsibilities, processes, documentation, monitoring, and continuous improvement.

For the CCO, the value lies in providing governance architecture, not another checklist. The relevant measure is not whether a company can say it follows NIST or ISO. It is whether its governance system addresses the actual risks created by its AI applications and whether the resulting controls work in practice. Frameworks provide structure. Management remains responsible for operating the system.

Compliance Should Enable Responsible Innovation

The CCO should avoid two extremes: allowing enthusiasm for AI to outrun governance or creating an approval structure so burdensome that employees circumvent it. A better model is responsible innovation. Compliance can help create clear pathways for lower-risk experimentation while ensuring that higher-risk applications receive appropriate scrutiny. Employees should understand what uses are permitted, which require approval, what categories of information may be used, and when escalation is necessary.

This approach also creates opportunities for a corporate compliance program. AI may improve due diligence, transaction monitoring, investigations, risk assessment, training, and data analysis. The compliance function should be willing to explore those capabilities under the same risk-based governance it expects the business to follow.

A CCO’s contribution should not be measured by how much innovation Compliance prevents. It should be measured in part by whether Compliance helps the enterprise capture value while maintaining appropriate accountability and control.

Before Leaving the Ground

Leonardo’s flying-machine studies represent the willingness to imagine possibilities beyond current practice. The modern compliance lesson is to combine that willingness with disciplined governance. For the CCO, Innovate means helping the enterprise pursue new capabilities through a risk-based system that provides visibility, assigns ownership, preserves meaningful human accountability, tests higher-risk applications, and monitors them as technology and business use evolve. The objective is neither unrestricted adoption nor blanket prohibition. It is responsible innovation that can produce sustainable business value.

From Innovation to Monitoring

Responsible innovation does not end when technology is approved and deployed. The organization must determine whether systems continue to operate as intended as data, users, vendors, business conditions, and risks change. That brings us to the fourth Leonardo principle: Monitor.

In Blog Post Four, The Last Supper and the Danger of Deterioration, we will use Leonardo’s experimental masterpiece to examine the difference between implementing a control and demonstrating that it remains effective. The discussion will focus on control testing, continuous monitoring, compliance analytics, ownership, remediation, AI monitoring, and the board’s role in evaluating evidence of continuing program effectiveness.

Categories
Innovation in Compliance

Innovation in Compliance: Compliance by Design in iGaming: Engineering, Data, and Release Governance with Mouhcine Jalili

Innovation comes in many areas, and compliance professionals need to not only be ready for it but also embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom visits with Mouhcine Jalili, VP of Growth – iGaming at Software Mind, on reframing iGaming compliance as a design, delivery, and platform challenge rather than an end-stage legal checklist.

Mouhcine argues compliance failures often stem from siloed teams, fragmented legacy platforms, inconsistent vendor integrations (B2B2C), and release management across jurisdictions with differing rules (e.g., spin time, buy-bonus features). He emphasizes strong release governance, modular and configurable architectures, automated controls that cannot be bypassed, and real-time monitoring and alerts to prevent harm, including responsible gambling interventions based on early behavioral signals. Scaling successfully requires standardization and automation while allowing local configuration and avoiding post-acquisition data fragmentation. Over the next 3–5 years, he expects operational compliance to become more engineering- and data-driven, with tighter integration among compliance, product, and engineering teams.

Key highlights:

  • Compliance As Design Platform
  • Breaking Silos With Automation
  • KYC Data And Onboarding Gaps
  • Integrity And Preventive Controls
  • Future Engineering Driven Compliance

Resources:

Connect with Mouhcine Jalili on LinkedIn

Software Mind on Linkedin

Software Mind Website

Innovation in Compliance was recently honored as the Number 4 podcast in Risk Management by 1,000,000 Podcasts.

Categories
Blog

The Muppet C-Suite: A Compliance Professional’s Guide to Culture, Controls, and Chaos Part 3: Gonzo as Chief Innovation Officer: Innovation Without Governance Is Just Operational Risk

This week we are honoring the return of The Muppets for a 2026 Special Edition. I thought it would be fun to look at business leadership teams through the lens of The Muppets. Every compliance professional has worked with a Kermit, managed a Piggy, worried about a Gonzo, or tried to contain an Animal. This series uses the Muppet executive team as a framework to explore leadership, governance, innovation, operational risk, and corporate compliance through the lens of the DOJ’s Evaluation of Corporate Compliance Programs and modern governance expectations.

Every company eventually hires a Gonzo. Not literally, of course. But every organization eventually encounters someone who believes the limits of the possible are merely suggestions waiting to be ignored. That is Gonzo. He is creative, fearless, experimental, unconventional, and absolutely convinced that launching himself out of a cannon remains a reasonable business strategy despite overwhelming evidence to the contrary. Naturally, he becomes the Chief Innovation Officer.

At first glance, Gonzo appears to represent innovation at its most dangerous. He ignores procedure, embraces uncertainty, and treats risk as entertainment. But beneath the chaos sits a lesson that modern compliance professionals urgently need to understand: innovation itself is not the problem. The problem is innovation without governance.

That distinction matters enormously in today’s corporate environment, where organizations face relentless pressure to adopt the following:

  • artificial intelligence,
  • automation,
  • advanced analytics,
  • digital transformation,
  • agentic AI, and
  • and emerging technologies that often evolve faster than governance structures can respond.

In other words, many organizations are currently operating inside a large-scale Gonzo experiment.

Gonzo Represents Innovation Pressure

One overriding instinct: pushing boundaries drives Gonzo. That instinct exists in virtually every modern enterprise. Boards demand innovation. Investors reward disruption. Executives fear being left behind by competitors. Product teams move quickly. Technology leaders promise transformation. Vendors insist their tools are revolutionary. The result is predictable: governance often lags behind implementation.

This is exactly the environment the DOJ’s ECCP increasingly expects organizations to manage. Prosecutors now ask whether compliance programs can identify and respond to evolving risks. They also ask whether organizations adequately understand the technologies they deploy and the risks those technologies create. In practical terms, the government is asking:

“Do you know where your Gonzos are? ”Many organizations do not.

The Problem Is Not Innovation. It Is Uncontrolled Innovation.

Too many compliance discussions frame governance and innovation as opposing forces. That is incorrect. Good governance should enable innovation by allowing organizations to experiment responsibly. The objective is not to stop Gonzo from inventing new things. The objective is preventing Gonzo from accidentally detonating the theater during testing. This distinction becomes critical in AI governance.

Consider what often happens inside organizations:

  • business units adopt generative AI tools without approval,
  • employees upload sensitive data into external systems,
  • procurement bypasses security reviews,
  • automated decision systems are deployed without testing,
  • vendors market “AI-powered” solutions nobody fully understands,
  • and leadership assumes innovation itself justifies the risk.

That is not a transformation. That is unmanaged operational exposure. Gonzo would absolutely deploy experimental AI tools without reading the documentation. He would also enthusiastically demonstrate them during a live performance before anyone completed legal review. Many companies are doing exactly that right now.

Shadow AI Is the Modern Gonzo Problem

One of the most significant emerging governance risks is shadow AI: technology adoption occurring outside formal oversight structures. This happens because innovation pressure rarely waits for policy development. Employees want efficiency. Business units want speed. Executives want results. Vendors promise a competitive advantage. Eventually, someone says:

“We cannot afford to fall behind.”

At that point, governance often becomes reactive rather than proactive. The compliance challenge is not preventing experimentation. It is creating governance structures that enable safe experimentation. This is why mature AI governance programs increasingly rely on:

  • approved use-case inventories,
  • risk-tiering frameworks,
  • data-governance protocols,
  • human oversight requirements,
  • testing standards,
  • escalation procedures,
  • and continuous monitoring.

Or, stated differently:

Someone needs to verify whether Gonzo’s cannon is aimed at the audience.

Innovation Requires Documentation

One of Gonzo’s defining traits is enthusiasm without paperwork. That creates a governance problem. The ECCP repeatedly emphasizes documentation, testing, continuous improvement, and evidence-based compliance. Organizations must demonstrate not merely that policies exist, but that controls operate effectively in practice.

Innovation functions often struggle here because innovation culture tends to prioritize speed over documentation. This creates dangerous blind spots:

  • unclear accountability,
  • undocumented approvals,
  • undefined ownership,
  • missing testing records,
  • inconsistent monitoring,
  • and inadequate escalation procedures.

If the organization cannot explain:

  • why a technology was adopted,
  • who approved it,
  • how risks were assessed,
  • what controls exist,
  • and how effectiveness is monitored,

Then the organisation does not truly govern the technology. It merely hopes for the best. Hope is not a control.

Gonzo and the Myth of the Brilliant Exception

Another important compliance lesson emerges from Gonzo’s personality itself. Organizations often tolerate elevated risk from highly creative or high-performing individuals because leadership perceives them as uniquely valuable. This is a dangerous governance instinct.

Every major corporate failure eventually contains some version of:

  • “We assumed he knew what he was doing.”
  • “Nobody wanted to challenge the innovation team.”
  • “They moved too fast for the controls.”
  • “The business results were too good to slow down.”

In many organizations, innovation teams become culturally insulated from oversight because questioning them appears anti-progress or anti-growth. That is precisely when governance becomes most necessary. The role of compliance is not to suppress innovation. It is to ensure innovation remains accountable to the enterprise.

Gonzo should absolutely continue inventing things. But somebody must still ask:

  • Was the system tested?
  • Is the data reliable?
  • Who owns the risk?
  • What happens if the model fails?
  • Is there human oversight?
  • Can we explain the outcome?

Those questions are not barriers to innovation. They are what keep innovation from becoming litigation.

Continuous Monitoring: The “Day Two” Problem

One of the most overlooked governance failures occurs after deployment. Organizations frequently focus intensely on implementation but pay far less attention to ongoing monitoring. Yet most technology risks emerge over time through:

  • model drift,
  • scope expansion,
  • vendor changes,
  • data degradation,
  • user workarounds,
  • and control fatigue.

Gonzo perfectly represents this problem because he rarely revisits prior experiments. Once the cannon fires, he is already planning the next stunt. Modern compliance programs cannot operate that way. AI governance, digital governance, and innovation oversight require “Day Two” discipline:

  • continuous testing,
  • ongoing review,
  • updated risk assessments,
  • incident reporting,
  • and remediation protocols.

The question is not merely: “Did the innovation work? ”The real question is:

“Does the control environment still work six months later? ”That is where mature governance separates itself from performative governance.

The Board’s Role in Innovation Governance

Boards increasingly face direct oversight expectations regarding technology and innovation risk. That means directors should ask:

  • Do we have formal AI governance?
  • Who owns innovation risk?
  • How are emerging technologies reviewed?
  • What testing standards exist?
  • How do we monitor ongoing performance?
  • What happens when innovation conflicts with compliance requirements?
  • How quickly can issues be escalated?

These questions are no longer theoretical. Regulators increasingly expect boards and senior leadership to demonstrate understanding of operational technology risk, especially where AI, automation, or sensitive data are involved. In governance terms, the age of “let the technology team handle it” is over.

5 Key Takeaways for the Compliance Professional

1. Innovation is not the enemy of compliance.

The real risk is innovation that operates outside governance structures, documentation, and accountability.

2. Shadow AI creates significant operational exposure.

Organizations must identify and govern unauthorized or poorly supervised technology adoption.

3. Documentation is a governance control.

If an organization cannot explain how a technology was approved, tested, monitored, and governed, it does not truly control the risk.

4. High-performing innovators still require oversight.

Organizations should not exempt innovation teams from compliance expectations because they generate results or move quickly.

5. Governance continues after deployment.

Continuous monitoring, testing, escalation, and remediation are essential to managing evolving technology and innovation risk.

From Gonzo to Animal

Gonzo teaches compliance professionals that innovation creates risk when governance cannot keep pace with experimentation. But there is another danger waiting behind the pressure to innovate: the normalisation of unmanaged operational chaos. That is where Animal enters the story.

Because eventually every organization encounters a moment when high-energy operational risk stops being an exception and starts becoming part of the culture itself. In Part 4, we will examine Animal as Chief Operating Risk Officer and what he teaches compliance professionals about operational volatility, escalation failures, crisis management, and the dangers of unmanaged high performers.

Categories
Innovation in Compliance

Innovation in Compliance: Dr. Rohan Lall: Innovation, Clinical Evidence, and Compliance in Electrifying Spine Surgery

Innovation occurs across many areas, and compliance professionals need not only to be ready for it but also to embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom Fox visits with Dr. Rohan Lall, a clinically trained Neurological Surgeon and Chief Medical Officer of SynerFuse, about innovation in spine surgery and the compliance infrastructure needed to support it.

Dr. Lall Law explains TLIF (transforaminal lumbar interbody fusion) and ETLIF, which integrates direct nerve root stimulation into reconstructive spine surgery to address persistent pain from chronically injured nerves even after decompression and fusion. Dr. Lall describes the innovation as team-driven, highlighting collaboration and detailing the regulatory path for a novel Class III device, including a feasibility proof-of-concept study, third-party data management, and an independent data and safety monitoring board. Dr. Lall outlines how compliance leaders should align with business speed while managing FDA requirements, data integrity, ethics, and risk, and he notes future impacts from neuromodulation, robotics, and image guidance.

Key highlights:

  • Back Surgery Basics and Electrified TLIF Explained
  • Innovation Origin Story
  • Regulatory and Collaboration Hurdles
  • Clinical Trials and Data Integrity
  • How Compliance Can Help Innovators

Resources:

Dr. Rohan Lall on LinkedIn

Synerfuse Company Website

Innovation in Compliance is a multi-award-winning podcast that was recently ranked Number 4 in Risk Management by 1,000,000 Podcasts.

Categories
Innovation in Compliance

Innovation in Compliance: Navigating AI: Governance, Risk with some Culture Thrown in with Matt Kunkel

Innovation spans many areas, and compliance professionals need not only to be ready for it but also to embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode,  host Tom Fox interviews Matt Kunkel, CEO and Co-Founder at LogicGate, about the company’s governance, risk, and compliance (GRC) platform and current market trends.

Matt recounts his path into regulatory risk and compliance work that led to founding LogicGate and launching its Risk Cloud platform in 2015. A major focus is AI governance. Tom and Matt explore how and why senior management is asking compliance teams to provide governance frameworks despite the absence of a single standard (e.g., NIST/ISO/SOC). Matt explains organizations need scalable processes to triage and route large volumes of AI usage requests, apply guardrails based on data sensitivity and criticality, and avoid becoming a bottleneck to innovation. He emphasizes training and culture to address employee misuse, highlighting risks of exposing proprietary data and the need to define what information is acceptable to input into AI models.

The discussion turns to LogicGate’s culture and how it has been sustained during rapid, organic growth (no acquisitions). Matt outlines LogicGate’s six values: Be as One, Embrace Your Curiosity, Empower Customers, Raise the Bar, Own It, and Do the Right Thing. For evaluating AI and modernizing compliance programs, he frames value in three outcomes: making money, reducing costs, or reducing risk, and describes LogicGate’s value realization framework that translates efficiency and ROI into business terms. He also describes Risk Cloud as an orchestration layer for compliance programs and anticipates more “intentional AI” and selective use of agentic capabilities rather than fully autonomous end-to-end program execution.


Key highlights:

  • From Consulting to GRC: Coding, Madoff Investigation, and Founding LogicGate
  • Why AI Is Supercharging the “G” in GRC
  • LogicGate’s Culture Playbook: Values That Scale with Hypergrowth
  • How to Evaluate AI Tools in Compliance: Proving Value, ROI, and “Intentional AI”
  • Cybersecurity in 2026: AI-Powered Social Engineering, Deepfakes, and Risk Mapping
  • What’s Next for GRC by 2030: Agents, Responsible AI, and Tech as the Glue

Resources:

Matt Kunkel on LinkedIn

LogicGate

Innovation in Compliance was recently ranked Number 4 in Risk Management by 1,000,000 Podcasts.

Categories
Sunday Book Review

Sunday Book Review: January 18, 2026, The Top Books on Innovation ’26 Edition

In the Sunday Book Review, Tom Fox considers books that would interest compliance professionals, business executives, or anyone curious. It could be books about business, compliance, history, leadership, current events, or anything else that might interest Tom. In this episode, we look at some of the top books on innovation, both those already published and those scheduled for 2026.

  1. Twin Transformation: A Gripping Tale of How AI and Sustainability Converge, and the Race to Get It Right by Michael Wade & Konstantinos Trantopoulos 
  2. The Innovation Approach: Overcoming the Limitations of Design Thinking and the Lean Startup by David C. Roach
  3. The Shortest History of AI: The Six Essential Ideas That Animate It by Toby Walsh
  4. The Coming Wave: AI, Power, and Our Future by Mustafa Suleyman & Michael Bhaskar
Categories
AI Today in 5

AI Today in 5: December 4, 2025, The Microsoft Blips Edition

Welcome to AI Today in 5, the newest edition of the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today In 5. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest about AI.

Top AI stories include:

  1. Does AI portend the end of the law/consulting firm pyramid? (FT)
  2. Strengthening AI strategies with proactive compliance. (WSJ)
  3. Microsoft stock dips on the news. (CNBC)
  4. Salesforce touts AI adoption. (Bloomberg)
  5. Strong AI governance can foster innovation. (Bloomberg)

For more information on the use of AI in Compliance programs, my new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

Categories
AI Today in 5

AI Today in 5: December 3, 2025, The Code Red Edition

Welcome to AI Today in 5, the newest edition of the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today In 5. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest about AI.

Top AI stories include:

  1. OpenAI declares Code Red. (WSJ)
  2. How compliance can drive AI innovation. (AboveTheLaw)
  3. How Amazon is embracing the AI chaos. (Bloomberg)
  4. AI and the economic singularity. (FT)
  5. Major banks are incorporating AI into their operations. (FinTechMagazine)

For more information on the use of AI in Compliance programs, my new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.