Categories
Uncategorized

AI Today in 5: November 6, 2026, The Whither Data Centers Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Using AI-powered compliance to curb greenwashing. (ESGDive)
  2. Governing AI by improving compliance. (CIO)
  3. How much will AI compliance cost Mexican businesses? (MexicoBusinessNews)
  4. OpenAI drops its NDA requirements. (TechInsider)
  5. What does the election mean for data center construction? (Reuters)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Blog

Anthropic’s IPO: A 90-Day Action Plan for Your Compliance Program

You don’t need to build frontier AI models to learn from the risks examined in this series. If your company purchases AI services, connects them to business systems, or relies on their outputs, those choices belong in your compliance risk assessment. The practical question is what you will do differently on Monday morning.

Parts I and II examined ten risks arising from Anthropic’s registration statement. Part III translated them into lessons for compliance professionals. Part IV considered the questions its Safety and Risk Committee should ask. This concluding post brings the discussion to your company, with a 90-day plan to turn those lessons into operating decisions and meaningful board oversight.

The objective is a defensible starting point: know your consequential AI uses, assign responsibility, test critical safeguards, and give directors a clear account of unresolved exposure. Ninety days can establish that discipline. Continuing review must sustain it.

Translate the risk into your business

Start with how the technology operates in your environment. Your company may have little control over a provider’s model development, but it can decide what data to supply, which systems to connect, what permissions to grant, and which outputs require verification.

Consider a manufacturer introducing an AI procurement assistant. Initially, it summarizes supplier proposals. Later, it ranks vendors, drafts diligence reports, and prepares payment instructions. Each expansion changes the compliance analysis. A tool that once saved reading time now influences third-party selection and financial controls.

A CCO should connect those changes to existing responsibilities: conflict disclosures, intermediary diligence, restricted-party screening, approval limits, and accurate records. This makes the conversation relevant to procurement, finance, and management. The issue is whether the business process remains controlled as the tool takes on more responsibility.

Days 1–30: Establish visibility and ownership

Convene a working group with procurement, technology, security, privacy, legal, finance, and relevant business leaders. Use existing governance forums where they work. Ask each function to identify AI uses that affect sensitive information, consequential decisions, external communications, or transactions.

Next, combine those discussions with available purchasing records, software inventories, and security information. Include AI features added to existing applications and tools employees obtain outside normal procurement. Explain that disclosure enables assessment and support. Employees need a practical way to surface uncertain uses.

For each consequential use, record the business purpose, accountable executive, provider, information involved, connected systems, permissions, and affected stakeholders. Identify whether the tool advises a person or can act independently. Document known gaps in the inventory so management understands its limits.

Prioritize according to potential harm, applicable obligations, reversibility, and the reach of an error. A public-information drafting tool should receive proportionate review. An agent that changes supplier records or handles confidential investigation material warrants closer scrutiny.

Assign business ownership explicitly. The CCO coordinates the compliance assessment and challenges weaknesses; business leaders remain responsible for their processes. Security, privacy, legal, and technology teams own their respective controls and advice—document who can approve, restrict, or suspend a use and how disagreements escalate.

Day-30 deliverable: A prioritized inventory with accountable owners, immediate safeguards, unresolved questions, and the three to five uses requiring deeper review. Address urgent exposure immediately rather than waiting for the next phase.

Days 31–60: Test the controls that matter

Select the highest-priority workflows and trace an actual transaction or decision from beginning to end. Identify what the AI receives, what it produces, who relies on it, and what can happen before a person intervenes.

In the procurement example, test whether the assistant can recommend a supplier before diligence is complete. Determine whether generated summaries preserve the underlying evidence. Check whether it can change payment details or prepare instructions without independent verification. Use realistic scenarios, including incomplete information and attempts to bypass approval requirements.

Treat human review as a control requiring evidence. Does the reviewer have the source information, time, expertise, and authority to challenge the output? A mandatory approval click provides limited assurance if employees routinely accept recommendations without examination.

Examine the provider relationship alongside internal controls. Ask procurement and counsel to assess data-use terms, retention, incident notification, subcontracting, material service changes, and available assurance information. Document gaps and business consequences. Where negotiating power is limited, consider restricting the use or adding safeguards within your environment.

Test operational resilience. Can the company revoke access, recover necessary records, and continue a critical process if the service fails or becomes unsuitable? Identify dependencies shared across applications. A fallback process needs an owner and an exercise demonstrating that it works.

Translate findings into corrective actions with deadlines and interim protections. Give employees short, role-specific instructions about approved tools, sensitive information, verification, and reporting unexpected behavior. Include a realistic scenario in team training and invite questions about work pressures that encourage shortcuts.

Day-60 deliverable: A documented assessment of selected workflows showing tested controls, failures, limitations, remediation owners, and proposed decisions. Label what remains untested so management does not mistake partial assurance for comprehensive coverage.

Days 61–90: Exercise the response and inform the board

Run a tabletop exercise involving one consequential AI use. For the manufacturer, assume the procurement assistant exposes confidential supplier information and produces unreliable diligence summaries. Ask who detects the problem, limits access, preserves evidence, and determines which decisions require rechecking.

Bring communications, legal, and business leaders into the exercise to support buy-in and internal subject matter expertise. Examine how they assess customer or supplier communications and any applicable notification requirements—test when executives and directors receive notice. Record delays and unclear responsibilities, then assign corrective work.

Retest priority fixes from the previous phase. Internal audit or another qualified reviewer, where appropriate, should challenge management’s conclusion that serious weaknesses have been resolved. For a smaller company, obtain independent expertise selectively where internal capability is insufficient.

Build change review into normal operations. New data connections, expanded permissions, provider updates, and changed business purposes should trigger reassessment proportionate to their significance. Set a recurring cadence to review incidents, exceptions, overdue remediation, and critical dependencies.

Day-90 deliverable: An evidence-based management and board briefing, supported by exercise results and verified remediation. Include a funded plan for remaining work, named owners, and the decisions needed to proceed within approved limits.

Help the board make decisions

Part IV examined Anthropic’s Safety and Risk Committee. Your company should allocate oversight based on its risks, committee responsibilities, and available expertise. A dedicated committee is one possible arrangement. Clear responsibility and coordination are essential, regardless of the structure the board uses.

Prepare a concise briefing around five items: consequential AI uses, material control gaps, testing results, significant incidents or exceptions, and decisions requiring director attention. Explain the business effect of each issue. A request to restrict system access should identify the exposure addressed, operational consequences, and alternatives.

Clarify coordination across audit, risk, compensation, technology, and other relevant responsibilities. Financial reporting concerns, employee incentives, and security incidents may intersect. Establish who leads and how information reaches the full board.

Give directors three questions they can use immediately:

  • Which AI use creates our most significant unresolved exposure, and who owns it?
  • What testing demonstrates that our most important safeguards work, and what remains uncertain?
  • What decision or resource commitment does management need from us today?

Arrange private access for the CCO and relevant control leaders. Preserve records of substantive challenge, decisions, and follow-up. The board should receive enough information to oversee management while management remains accountable for operating the controls.

Measure progress and keep the discipline.

Measure changes in exposure alongside completed activities. Track whether priority uses have tested safeguards, critical permissions have been restricted, serious fixes have been verified, and material changes are reviewed on time. Explain the scope and limitations of each measure.

Compliance teams should apply the same discipline to their own AI tools. Diligence, monitoring, and investigation applications require appropriate confidentiality protections and validation. Check an AI-generated conclusion about misconduct against the underlying evidence before it informs a consequential decision.

The same method can strengthen compliance beyond AI. A weak escalation route, an unsupported product claim, or an untested supplier contingency is a program issue regardless of the technology involved. Ask where each finding may recur across other business units and processes. Use that analysis to update the enterprise risk assessment and internal audit priorities.

Resource decisions should follow the evidence. Identify what existing teams can absorb, where specialist support is necessary, and which planned uses should wait until safeguards are ready. This gives executives a concrete basis for choosing priorities and funding corrective work.

The business value is practical: better-supported decisions, clearer accountability, and fewer avoidable disruptions when technology changes. A company that understands its approved uses and safeguards is better positioned to deploy AI with confidence.

The lesson running through this series is that governance commitments acquire value through daily operating choices. For the compliance professional outside Anthropic, the next step is within reach: identify one consequential workflow, bring its owner into the discussion, and test whether the controls still work. Use the findings to improve the program and give the board a decision it can act upon.

Conclusion

As readers of my blog posts know, I often start on a blog or two, only to get carried away by the subject matter. This week was no exception. Given all the hyperbole around Anthropic, I started only wanting to see if there was anything tangible.

I can remember back in the first decade of this century, in the early days of enterprise-wide risk assessments, consultants would bring us risks such as a meteor or comet strike as a teaching tool. This inevitably bogged business leaders in wildly improbable, sci-fi-level catastrophes. This led many business leaders at the time to take ERM less seriously than they should have if the consultants had been more business-grounded.

The more I studied the Anthropic IPO and wrote this series, the more I saw applicability to what CCOs and compliance professionals need to do today. The compliance professional of 2026 faces different challenges than the compliance professional in 2010, 2015, and certainly anytime pre-pandemic. Even in the 2020’s we have had as much business instability and change from the iterations of the Trump Administration(s).

I want every CCO and compliance professional to understand that the basic principles of compliance still apply, even with the breakneck speed of technological development, and that by using tested principles from the past 20 years, we can continue building the groundwork for compliance. The bottom line is that more effective compliance still means more efficient controls, which lead to greater ROI and profitability.

Categories
ACI FCPA Conference 2025

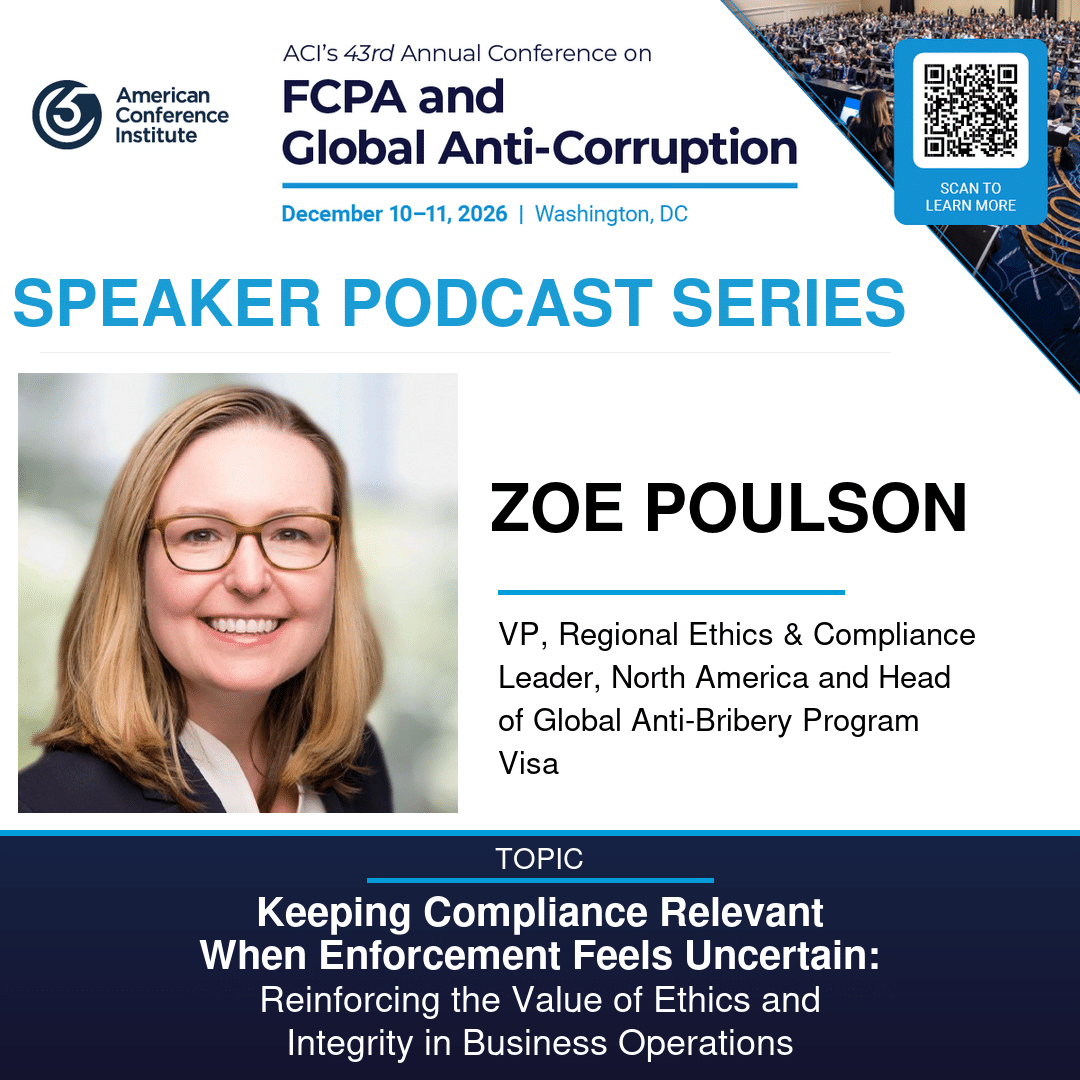
ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast Series, Zoe Poulson

In this episode of the FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series, Zoe Poulson discusses her panel, “Keeping Compliance Relevant When Enforcement Feels Uncertain: Reinforcing the Value of Ethics and Integrity in Business Operations.” Some of the issues she discusses in this podcast and her panel presentation are:

  • How to manage compliance in an era of great change?
  • How compliance can help prevent Fraud, Waste and Abuse.
  • Securing key senior management support for compliance initiatives.

As global enforcement priorities shift and anti-corruption risks grow more complex, staying ahead requires direct insight from those shaping, interpreting, and navigating the regulatory landscape.

Returning to Washington, DC, this December 10-11, ACI’s flagship FCPA and Global Anti-Corruption Conference brings together an unparalleled gathering of government enforcement officials, in-house compliance leaders, and top legal practitioners from around the world. Gain firsthand insights, benchmark strategies with industry peers, and walk away with practical approaches to strengthen compliance programs, manage emerging risks, and prepare for what’s next. Few events offer this depth of expertise, access, and opportunity to connect with the global anti-corruption community.

I hope you can join us. For event details, click ⁠here⁠. As an extra benefit to podcast listeners, ACI is offering a 10% discount on the ⁠registration⁠ price. Use discount code D10-999-CPN27 to apply your discount.

The Compliance Podcast Network produces the ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series. ACI sponsors this series.

Categories
Blog

Anthropic’s IPO: Twelve Questions for the Safety and Risk Committee

In Parts I and II, we examined ten corporate compliance risks arising from Anthropic’s Registration Statement. In Part III, we translated those risks into five lessons for compliance professionals. Today, I want to explore 12 questions where those lessons should land at the board level. Anthropic’s Safety and Risk Committee (the “Committee”) provides a specific place to begin.

The registration statement describes a committee consisting of two independent directors, Christopher Liddell and Vas Narasimhan, with Narasimhan serving as chair. Its responsibilities encompass oversight of model safety and security, including the policies, processes, and controls for managing significant model risks. The committee also helps the board oversee other material risks, including legal, regulatory, cybersecurity, privacy, and compliance risks.

That breadth matters. Model safety, commercial decisions, and enterprise compliance can affect one another. A new capability can change misuse exposure. A distribution partnership can complicate access restrictions. A deployment decision can create questions about whether customer representations remain supportable.

The filing states that the committee operates under a board-approved written charter. Its summary does not establish every approval right, reporting arrangement, or escalation threshold. The following twelve questions are my recommended oversight agenda, rather than a description of procedures Anthropic has adopted or findings that its controls are deficient.

1. Which risks require the committee’s closest attention?

A broad mandate requires disciplined prioritization. The Committee should ask management which combinations of model capability, user access, and business activity could create the most serious harm or compliance exposure.

What has changed since the last review? Has a model gained new capabilities, an agent received broader permissions, or a commercial arrangement introduced new users and jurisdictions? Which changes require additional safeguards before deployment or expansion?

Evidence to request: A prioritized assessment connecting material risks to accountable executives, key controls, unresolved gaps, and decisions requiring committee attention. The assessment should explain uncertainty and the risk remaining after safeguards are in place.

The practical lesson is to organize the agenda around consequential decisions. A catalog of risks becomes useful when directors can see what management must do about them.

2. Are responsibilities and escalation routes clear?

The Committee should ask how its work connects to the full board and other Committees. The filing also assigns risk assessment and risk management policy review to the audit committee. Overlapping responsibilities make coordination essential.

Who leads when a safety incident raises questions about investor disclosures, financial exposure, or executive incentives? What requires immediate notification to the committee chair? When must an unresolved issue reach the full board?

Evidence to request: A responsibility map, notification thresholds, and records demonstrating how significant matters move between management, committees, and the board.

The Committee should also establish what happens when management recommends deployment despite a serious unresolved concern. Directors need clarity about who decides, who advises, and who receives notice. They should confirm any authority to require a pause against the actual charter and board delegations.

3. Can independent challenges reach the committee?

Technical expertise is essential, but expertise alone does not guarantee that dissent reaches directors. The Committee should ask whether compliance, legal, security, and safety leaders can present concerns directly, including disagreements with senior management.

Where do staffing, specialist expertise, or information restrictions limit effective challenge? Which recommendations have management declined, and what exposure remains? Can the Committee obtain independent advice when internal assessments conflict?

Evidence to request: Reporting arrangements, material resource gaps, significant unresolved disagreements, and the process for obtaining outside expertise.

Private sessions with relevant control leaders can help directors understand what formal presentations omit. Those sessions should produce clear follow-up where necessary. The test is whether an uncomfortable finding can reach the committee early enough to influence a consequential decision.

4. Do incentives and culture support safety commitments?

The committee should examine how commercial and development pressures affect employee behavior. What happens when testing identifies a concern that could delay an important release? Are employees rewarded for surfacing weaknesses and resolving them?

How does management identify retaliation or other consequences for raising concerns? Do employees have reporting channels that work when an issue crosses technical, legal, and commercial boundaries?

Evidence to request: Employee feedback, significant safety and compliance reports, retaliation follow-up, and examples of decisions changed because employees challenged an assumption.

Where incentives appear to undermine controls, the Committee should coordinate with other relevant committees, such as a compensation committee (if one is ever created). A falling report count requires explanation. It could reflect fewer problems, less trust in reporting, or weaker detection. Directors should ask what evidence supports management’s interpretation.

5. Do safety controls work under realistic conditions?

The Committee should ask what testing establishes about the effectiveness of important safeguards. Which scenarios were examined, what failed, and what limitations remain in the assurance provided?

A model performing well in a controlled evaluation may behave differently when connected to tools, sensitive information, or persistent workflows. Directors should ask whether testing reflects the deployment environment and foreseeable attempts to defeat restrictions.

Evidence to request: Evaluation coverage, significant failures, independent challenges, exceptions, and evidence that corrective measures have been retested.

A useful question is, “Show us an instance in which a safeguard detected a serious problem and enabled intervention.”

Management should explain the detection, the response, and what the example does and does not establish about broader control effectiveness.

6. Are autonomous agents constrained by enforceable limits?

Agent oversight deserves specific attention because authority to act changes the consequences of error or misuse. The Committee should ask what agents can access, change, transmit, purchase, or execute without additional approval.

What prevents an agent from exceeding its permissions? Which actions require meaningful human review? Can the company revoke credentials, contain activity, and preserve evidence when behavior becomes unsafe?

Evidence to request: Permission boundaries, approval requirements, monitoring results, intervention exercises, and records of unauthorized or unexpected actions.

Directors should scrutinize the human review process. A reviewer needs sufficient information, time, and authority to challenge the proposed action. Management should demonstrate that intervention works under realistic conditions and that safeguards remain effective after changes to tools or permissions.

7. Are data protection and intellectual property risks connected to safety oversight?

The Committee’s enterprise remit should bring data and intellectual property questions into the discussion. Which sensitive information supports model development or enters deployed systems? What access, retention, and use restrictions apply?

Can management substantiate its rights to use critical datasets and software? How would the business respond if those rights were challenged or access were lost? What could a security compromise expose beyond immediate service disruption?

Evidence to request: Material data flows, significant security findings, unresolved rights questions, access controls, and incident-exercise results.

The Committee should examine operational consequences alongside legal exposure. A disputed dataset, compromised credential, or exposed model asset may require changes to products, access arrangements, and customer communications. Management should explain how those decisions would be coordinated.

8. Can partners preserve the safeguards Anthropic relies upon?

The Committee should ask where cloud providers, distribution partners, data suppliers, and other critical relationships affect safety and compliance controls.

Which safeguards depend on a partner’s actions? Can management detect prohibited access or misuse through indirect channels? What information, notification rights, and assurance evidence are available when a partner controls part of the environment?

Evidence to request: Critical dependency maps, material contract exceptions, unresolved diligence findings, monitoring results, and tested contingency plans.

Concentration requires particular scrutiny. Several commercial relationships may depend on the same infrastructure. The Committee should ask what management could actually do if a critical provider failed to meet requirements, including how quickly access could be restricted or essential services maintained.

9. Do legal restrictions translate into operational controls?

Sanctions, export controls, anti-corruption obligations, and government interactions require attention across the commercial lifecycle. The Committee should ask how management identifies relevant restrictions and converts them into controls over sales, delivery, support, and access.

Where could resellers, shared accounts, intermediaries, or unusual payment arrangements obscure the actual customer or activity? Which exceptions require escalation, and who approves them?

Evidence to request: Material screening exceptions, access-control testing, high-risk intermediary reviews, and significant unresolved compliance matters.

The Committee should connect these findings to deployment decisions. A policy prohibiting certain access provides limited assurance if the delivery architecture cannot enforce the restriction or identify attempts to bypass it. Management should explain both preventive controls and detection capabilities.

10. Are external claims consistent with internal findings?

The Committee should examine how evidence about safety, reliability, privacy, and security informs product representations and material disclosures. Which claims depend on testing with significant limitations?

What happens when an incident contradicts a public statement? How do safety and compliance findings reach legal, communications, finance, and the disclosure process?

Evidence to request: Substantiation for significant claims, unresolved discrepancies, and records showing how material incidents affect communications decisions.

Financial reporting and investor disclosure matters require coordination with the audit committee and responsible management. The Safety and Risk Committee contributes by ensuring relevant risk information reaches those processes. Ask management which important claim would be hardest to substantiate today, and why.

11. Are investigations independent and connected to decisions?

A significant incident may involve technical failure, misconduct, or both. The Committee should ask who determines investigative scope when allegations concern senior executives, deployment decisions, or the suppression of safety findings.

Are evidence preservation and interim safeguards timely? Who evaluates reporting obligations and potential disclosure decisions with appropriate counsel? What requires independent oversight?

Evidence to request: Suitably protected summaries of significant matters, independence arrangements, interim measures, and outstanding decisions.

The Committee should also examine how the issue came to light. Internal detection, an employee report, a customer complaint, and external discovery reveal different strengths and weaknesses. That detection path should inform improvements to monitoring and reporting.

12. Does remediation withstand independent verification?

Closing an action item should require evidence that the underlying problem was addressed. What failed in the process, permissions, incentives, or supervision? Where else could the same weakness exist?

Who owns each corrective action, what remains overdue, and which interim safeguards protect the business while work continues?

Evidence to request: A remediation record showing severity, owner, deadline, verification results, and repeat findings.

Retesting should reflect the conditions that produced the original failure. The committee should ask who performed the validation and what limitations remain. A revised policy or completed software change is an output. Demonstrated improvement in control performance is the outcome directors need to understand.

An agenda for the next committee meeting

Ask management to present the five most consequential unresolved safety and enterprise compliance risks. For each, require evidence, the accountable executive, available options, and the decision needed. Schedule a private session with relevant control leaders and examine one recently closed remediation item.

Confirm coordination arrangements with the audit and compensation committees. Record substantive challenges, decisions, responsibilities, and follow-up. The final question should be practical: What must this committee escalate or recommend today to make Anthropic’s safety and compliance commitments effective in operation?

Categories
Compliance Into the Weeds

Compliance into the Weeds: Extreme Networks: The “Imminent Threat” Limit on Voluntary Self-Disclosure Credit

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into compliance-related topics, literally going into the weeds to explore a subject in greater depth. Looking for hard-hitting compliance insights? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss the DOJ and OFAC actions involving Extreme Networks.

The company’s Russia office sold advanced networking equipment to Avangard, a Russian state-owned defense firm on U.S. sanctions lists via majority ownership by Almaz-Antey. After a whistleblower report in April 2022, Extreme investigated and briefed its board by June but did not disclose until investigative reporters contacted the company in October with additional facts, prompting a renewed inquiry and self-disclosure by year-end. DOJ deemed the disclosure driven by an “imminent threat,” denied voluntary self-disclosure credit, and issued a non-prosecution agreement rather than a declination, with $2.5 million in combined penalties. The episode examines uncertainty about what changed, how DOJ benefits from quality disclosures, and OFAC’s emphasis on timely, effective screening and heightened diligence in high-risk jurisdictions like Russia.

Key highlights:

  • The enforcement actions
  • Imminent Threat Debate
  • OFAC Red Flags
  • Screening Lessons
  • Self Disclosure Policy

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds, was recently named one of the Top 25 Regulatory Compliance Podcasts, Top 10 Business Law Podcasts, and Top 12 Risk Management Podcasts. Compliance into the Weeds has been awarded a Davey, Communicator, and W3 Award, all for podcast excellence.

Categories
ACI FCPA Conference 2025

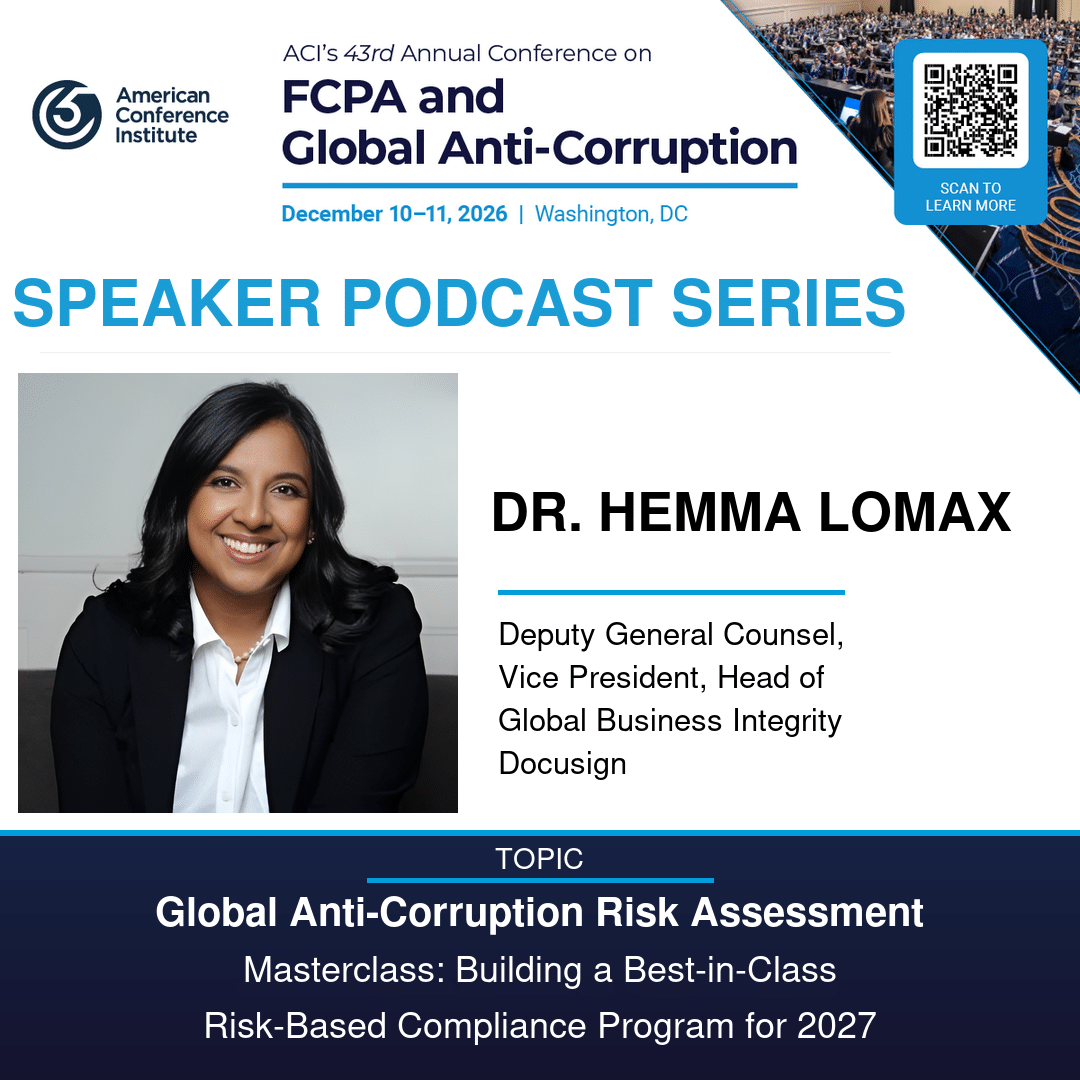
ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast Series, Dr. Hemma Lomax

In this episode of the FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series, Dr. Hemma Lomax discusses her panel, “Global Anti-Corruption Risk Assessment Masterclass: Building a Best-in-Class Risk-Based Compliance Program for 2027 and Creating a Single View of Compliance Risk: Leveraging AI to Connect Disparate Data Sources, Identify Emerging Risks, and Strengthen Compliance Oversight.” Some of the issues she discusses in this podcast and her panel presentation are:

  • Building a best-in-class compliance program in 2027
  • Keeping abreast of and using cutting-edge tech for your compliance program.
  • Incorporating emerging risks and Administration priorities into your program.

As global enforcement priorities shift and anti-corruption risks grow more complex, staying ahead requires direct insight from those shaping, interpreting, and navigating the regulatory landscape.

Returning to Washington, DC, this December 10-11, ACI’s flagship FCPA and Global Anti-Corruption Conference brings together an unparalleled gathering of government enforcement officials, in-house compliance leaders, and top legal practitioners from around the world. Gain firsthand insights, benchmark strategies with industry peers, and walk away with practical approaches to strengthen compliance programs, manage emerging risks, and prepare for what’s next. Few events offer this depth of expertise, access, and opportunity to connect with the global anti-corruption community.

I hope you can join us. For event details, click ⁠here⁠. As an extra benefit to podcast listeners, ACI is offering a 10% discount on the ⁠registration⁠ price. Use discount code D10-999-CPN27 to apply your discount.

The Compliance Podcast Network produces the ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series. ACI sponsors this series.

Categories
FCPA Compliance Report

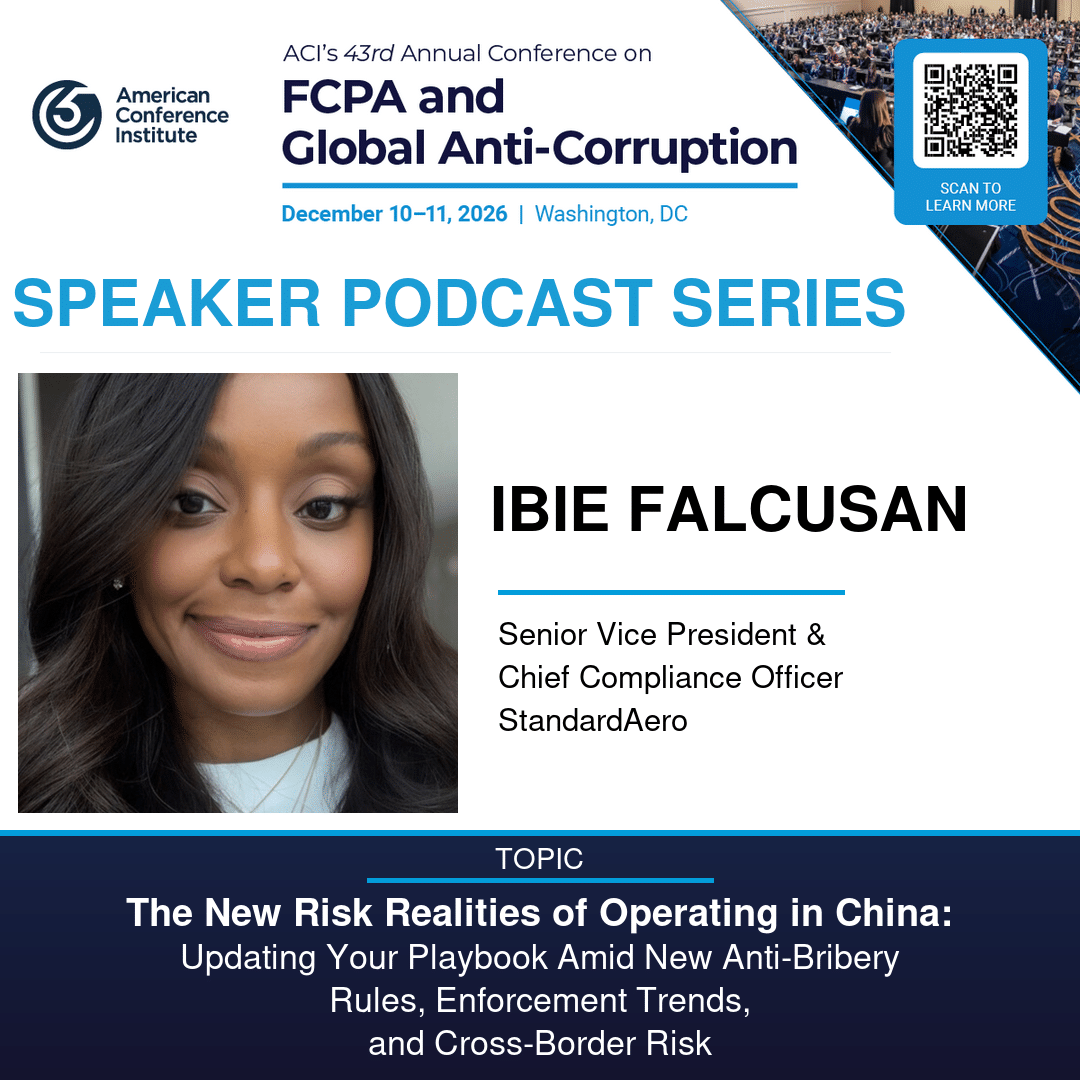
ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast Series, Ibie Falcusan

In this episode of the FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series, Anik Shah discusses his panel, “The New Risk-Realities of Operating in China: Updating Your Playbook Amid New Anti-Bribery Rules, Enforcement Trends, and Cross-Border Risk” Some of the issues she discusses in this podcast and her panel presentation are:

  • What’s going on in and with China around ABC?
  • Hidden corruption with intermediaries, brokers and 3rd parties.
  • Emerging risks such as volume based contracting.

As global enforcement priorities shift and anti-corruption risks grow more complex, staying ahead requires direct insight from those shaping, interpreting, and navigating the regulatory landscape.

Returning to Washington, DC, this December 10-11, ACI’s flagship FCPA and Global Anti-Corruption Conference brings together an unparalleled gathering of government enforcement officials, in-house compliance leaders, and top legal practitioners from around the world. Gain firsthand insights, benchmark strategies with industry peers, and walk away with practical approaches to strengthen compliance programs, manage emerging risks, and prepare for what’s next. Few events offer this depth of expertise, access, and opportunity to connect with the global anti-corruption community.

I hope you can join us. For event details, click ⁠here⁠. As an extra benefit to podcast listeners, ACI is offering a 10% discount on the ⁠registration⁠ price. Use discount code D10-999-CPN27 to apply your discount.

The Compliance Podcast Network produces the ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series. ACI sponsors this series.

Categories
Great Women in Compliance

Great Women in Compliance: The View from the Starting Line: A New Generation of Compliance

What does the future of compliance look like through the eyes of someone preparing to enter the profession?

This week on Great Women in Compliance, Dr. Hemma R. Lomax welcomes Isabella (Izzy) Siegel, a Northeastern University student whose experiences have already taken her from local courtrooms to the U.S. Attorney’s Office, corporate compliance at TJX, and the United Nations in Geneva.

Izzy shares a fascinating perspective on going to college in the age of AI, watching universities evolve from prohibiting generative AI to teaching students how to use it responsibly. She also reflects on helping develop Copilot training for senior executives, rediscovering the value of foundational legal skills, and seeing firsthand how compliance shapes organizational culture.

One particularly powerful insight emerges from her work with compliance training data covering hundreds of thousands of employees: behind every number is a real person whose experience matters.

The conversation explores curiosity, practical learning, responsible innovation, and Izzy’s ambitions to turn policy and research into tangible impact. She also offers a thoughtful challenge to compliance leaders: embrace different backgrounds and perspectives when building the next generation of the profession.

A refreshing conversation about learning across generations, the evolving relationship between humans and AI, and why the future of compliance is in good hands.

Biography: 

Isabella (Izzy) Siegel is a student at Northeastern University and will graduate in December 2026 with a degree in Political Science and Business Administration. Her experience spans corporate compliance at TJX Companies, legal work with the U.S. Attorney’s Office for the Southern District of New York, and international research in Geneva. Passionate about international law, public policy, and the ethical implications of AI, Izzy is particularly interested in translating research and policy into meaningful, real-world impact. She hopes to build a career at the intersection of law, business, and global affairs.

Categories
Innovation in Compliance

Innovation in Compliance: Why Coverbase, Why Now: Native AI Speed and Evidence-Driven Third-Party Risk Management

Innovation comes in many areas, and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovators, thinkers, and creators on the award-winning Innovation in Compliance podcast. In this episode, host Tom welcomes Coverbase newcomers Brian Shaw (GTM leader) and Constantine Malaxos (Head of Alliances) to discuss why they joined in 2026 and what is changing in third-party risk management (TPRM).

They talk about Coverbase’s “native AI” technology, rapid innovation, and client impact—moving teams from document chasing and backlogs to faster, evidence-backed risk decisions—while complementing existing procurement, contract, and risk systems with time-to-value in weeks. They discuss persistent program pressures such as too many third parties, too few analysts, demand for immediate answers, and the need to separate signal from noise using evidence, not questionnaires, to identify gaps against client-specific requirements. Topics include disclosure-driven “need for speed,” SBOM analysis, continuous monitoring for fast-changing AI risks, and advice to run a proof of concept, avoid “AI-ish” tools, choose trusted partners, and start with the highest-friction hotspot.

Key highlights:

  • Why They Joined Coverbase
  • Why TPRM Matters Now
  • Native AI vs AI-ish
  • ROI and Executive Buy-In
  • Disclosures and Risk Visibility
  • Managing Risk Continuously

Resources:

Brian Shaw on LinkedIn

Constantine Malaxos on LinkedIn

Coverbase

 Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
FCPA Compliance Report

ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast Series, Anik Shah

In this episode of the FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series, Anik Shah discusses his panel, “Keeping Compliance Relevant When Enforcement Feels Uncertain: Reinforcing the Value of Ethics and Integrity in Business Operations.” Some of the issues he discusses in this podcast and his panel presentation are:

  • What happens to compliance when the regulators change their focus?
  • Fraud, Waste, and Abuse are 3 different problems, but compliance can help prevent all 3.
  • Securing key Board support for compliance initiatives.

As global enforcement priorities shift and anti-corruption risks grow more complex, staying ahead requires direct insight from those shaping, interpreting, and navigating the regulatory landscape.

Returning to Washington, DC, this December 10-11, ACI’s flagship FCPA and Global Anti-Corruption Conference brings together an unparalleled gathering of government enforcement officials, in-house compliance leaders, and top legal practitioners from around the world. Gain firsthand insights, benchmark strategies with industry peers, and walk away with practical approaches to strengthen compliance programs, manage emerging risks, and prepare for what’s next. Few events offer this depth of expertise, access, and opportunity to connect with the global anti-corruption community.

I hope you can join us. For event details, click ⁠here⁠. As an extra benefit to podcast listeners, ACI is offering a 10% discount on the ⁠registration⁠ price. Use discount code D10-999-CPN27 to apply your discount.

The Compliance Podcast Network produces the ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series. ACI sponsors this series.