Categories
Blog

De-Risking AI Adoption Through Accountability and Effective Governance

A company can publish thoughtful AI principles, appoint a governance committee, and still struggle to answer a basic question: who can stop an AI system when its behavior creates unacceptable business risk? For chief compliance officers and boards, that question reaches the heart of program effectiveness. Policies establish expectations. The real test comes when someone must decide, enforce a boundary, and show what happened.

Pamela Gupta addresses that challenge in De-Risking AI Adoption: The AI Trust Layer: An AI Governance Playbook. Her central argument is that trustworthy AI requires an operating model connecting ownership, controls, deployment decisions, monitoring, and evidence. The book provides a structure for translating responsible AI commitments into repeatable business practices. For compliance professionals, its value lies in explaining how governance can support adoption while keeping accountability attached to the people making consequential decisions.

Making Trust Operational

Gupta defines trustworthy AI through three practical capabilities: people can understand the behavior to expect and its limits, verify what actually occurred, and identify an accountable person when something goes wrong. This moves the discussion toward demonstrable performance.

That approach should resonate with any CCO who has examined the distance between a written procedure and actual business conduct. An AI policy may require human oversight. Whether that oversight works depends on the reviewer’s information, competence, time, and authority to intervene. A human approval step has limited value if the organization rewards automatic acceptance or discourages challenges.

The compliance application is straightforward. For each significant AI use case, identify the business purpose, potential harm, responsible owner, operating limits, and evidence needed to evaluate performance. These questions belong at the beginning of development and procurement, when the answers can still shape the system.

Eight Pillars of AI Governance

The book organizes its methodology around AI TIPS™, Gupta’s framework of eight interconnected pillars: cybersecurity, privacy, ethics and bias, transparency, explainability, regulations, audit, and accountability. Together, they address the different ways AI can create enterprise exposure.

The connections matter. Security controls may protect information against unauthorized access while leaving questions about discriminatory outcomes unresolved. Transparency can establish which data and processes a system uses, while explainability addresses whether people can understand and challenge a particular decision. Independent assurance requires evidence from across these activities.

Gupta also presents mappings to established frameworks and standards, including the NIST AI Risk Management Framework and ISO/IEC 42001. Her purpose is to connect enterprise controls and evidence across multiple governance expectations.

For a compliance team, the practical lesson is to coordinate existing expertise. Privacy, security, legal, risk, audit, and business leaders each hold part of the answer. The CCO can help connect their work through common requirements, escalation procedures, and documented decisions. Business owners must remain answerable for the systems they deploy.

Accountability Must Carry Authority

Accountability receives special treatment throughout the book. Under Gupta’s methodology, a critical accountability failure blocks deployment regardless of the aggregate governance score. A system needs a named owner with authority to accept risk and stop its operation. Consequential uses also require appropriate human override and redress mechanisms.

This is a useful challenge to governance committees that distribute responsibility so broadly that no individual can decide. Participation in a committee does not automatically establish authority over a business process.

CCOs should translate this principle into explicit decision rights. Who approves the use case? Who accepts the remaining risk? Who authorizes exceptions? Who can suspend operation? Who addresses harm to an affected customer or employee? Document and understand those answers before an incident forces the organization to discover whether its governance arrangements work.

Governance Throughout the Lifecycle

Gupta’s gated lifecycle makes these responsibilities actionable. It follows AI from concept and planning through data preparation, development, independent validation, deployment, continuing monitoring, and retirement. Decision gates establish criteria for moving forward and identify the people authorized to approve or refuse progression.

Independent validation is particularly important. The team building a system should face review capable of challenging its assumptions and testing whether performance meets the intended use. Deployment readiness also includes monitoring, incident response, rollback capability, and operational procedures.

For compliance professionals, the lesson extends beyond initial approval. A system’s exposure can change when it receives new data, serves a different population, gains additional permissions, or undergoes a material modification. Gupta calls for defined triggers that return systems to validation.

Apply the same discipline to exceptions. Record the rationale, compensating controls, approver, remediation owner, and expiration date. An exception should remain visible until it is resolved. Retirement deserves similar attention, including appropriate data disposition and preservation of evidence needed to explain earlier decisions.

Measuring Whether Controls Work

The Trust Index gives Gupta’s framework a common measurement approach. It combines control implementation, control effectiveness, residual risk exposure, and compliance status into pillar scores and an overall assessment. The methodology assigns the greatest combined emphasis to whether controls exist and whether they work.

For boards, this creates a way to discuss changes in governance performance and direct attention toward unresolved weaknesses. Gupta also distinguishes inherent risk from current risk after controls. An inherently consequential use case does not become inconsequential because its controls improve.

The compliance implication is to examine the evidence supporting the number. Directors should understand significant weaknesses, testing results, exceptions, and corrective actions. A dashboard becomes useful when it supports decisions about resources, restrictions, and remediation. The underlying assessment must remain open to challenge, especially where a favorable aggregate score could obscure a serious problem in one area.

Governing AI That Takes Action

The book’s treatment of agentic AI deserves senior executives’ attention. An AI system that can invoke tools, modify records, send communications, or initiate transactions introduces questions about delegated business authority. Evaluating the model’s outputs covers only part of that exposure.

Gupta describes an agentic control plane that governs identity, permissions, tools, memory, delegation, observation, and intervention. A central principle is that consequential boundaries must operate outside the agent’s own reasoning. Written instructions alone cannot reliably limit what credentials and connected tools permit.

Consider a compliance application: an agent assisting with third-party onboarding. Management should distinguish permission to summarize diligence materials from permission to approve a supplier, alter payment information, or release a blocked transaction. Each capability requires deliberate authorization and appropriate controls.

Internal controls professionals know this lesson. Delegated authority needs defined limits, traceable actions, and effective intervention. Automation increases the importance of those disciplines because actions can occur faster than a person can review them.

Data and Third Parties Remain Central

Gupta also emphasizes the information an AI system uses when it acts. Policies, customer records, retrieved documents, and stored memory shape its behavior. Even a system operating within its permissions can make a harmful decision when its information is outdated or inappropriate.

For compliance teams, this means governing the sources behind AI advice. An assistant answering employee questions should use approved, current policies with identifiable owners and version histories. Access restrictions should continue to apply when information enters a retrieval system.

Third-party oversight must also reach beyond the primary model provider. Gupta examines tools, connectors, and packaged agent capabilities as supply-chain dependencies. She adds a business continuity question: what happens if a critical model becomes unavailable? Organizations should identify affected processes, evaluate alternatives, and test fallback arrangements before disruption forces an improvised response.

Evidence the Board Can Use

Gupta’s evidence-by-design approach connects the entire operating model. Significant decisions and actions should generate records as work occurs: approvals, validation results, system versions, permissions, relevant context, interventions, and monitoring outcomes. Those records should support reconstruction of a consequential action.

For boards, reporting should connect this evidence to oversight. Which systems carry the greatest exposure? Which controls have failed testing? Which exceptions remain unresolved? What has management restricted, delayed, or rejected? What decisions require board attention?

The CCO’s contribution is to make this reporting actionable and consistent with operational reality. Evidence should reveal where management needs to intervene and whether previous corrective actions achieved their intended result.

A useful starting exercise is to select one consequential AI decision and trace it from initial authorization to its outcome. Ask the owner to produce the supporting evidence. Any missing link identifies a concrete improvement for the governance program to address.

Practical Steps for CCOs and Boards

Gupta recommends starting with an honest readiness assessment and a manageable set of high-impact use cases, then expanding proven governance practices. Apply that approach through five actions:

  1. Inventory consequential AI systems, their owners, permissions, and dependencies.
  2. Establish authority for approval, exceptions, escalation, and suspension.
  3. Test controls against actual business risks and affected populations.
  4. Capture decision evidence during ordinary operations.
  5. Give the board visibility into unresolved exposure and remediation.

The business lesson from De-Risking AI Adoption is that effective governance makes responsible adoption repeatable. For CCOs and boards, the immediate task is to make accountability observable in how AI is approved, operated, challenged, and improved.
Categories
AI in Financial Services in 5 Stories

AI in Financial Services in 5 Stories – Week Ending September 25, 2026

Welcome to AI in Financial Services in 5 Stories. A practical weekly roundup of the five most important AI developments affecting banking, insurance, payments, asset management, and fintech. Each Friday, Tom Fox will break down the top stories that matter most through the lenses of compliance, risk management, governance, and business strategy. Designed for compliance professionals, executives, legal teams, and financial services leaders, it goes beyond headlines to explain why each development matters in a highly regulated industry. The result is a concise weekly briefing that helps listeners stay current on AI innovation while asking sharper questions about oversight, accountability, and trust.

This week’s stories include the following:

  1. Trust and AI in the financial sector.  (FinTech Global)
  2. AI recordkeeping hurdles for financial services firms. (ACA)
  3. Can financial services overcome barriers to AI adoption?  (FinTech Global)
  4. Finance leaders want more proof of and control over AI. (Business Insider)
  5. Banks warn on AI shopping. (Reuters)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
AI Today in 5

AI Today in 5: September 22, 2026, The Kill Switch Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Newsom wants an AI kill switch. (Bloomberg)
  2. Policing AI in finance. (FT)
  3. What’s advancing AI in healthcare? (Distilled Post)
  4. Trust and AI in the financial sector. (FinTech Global)
  5. AI co-agents in drug development. (NYT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Compliance and AI

Compliance and AI: The Psychology of AI Adoption at Work: Overcoming Fear, Identity Threat, and Shadow AI

What is the intersection of AI and compliance? What about machine learning? Are you using ChatGPT? These questions are just three of the many we will explore in this cutting-edge podcast series, Compliance and AI, hosted by Tom Fox, the award-winning Voice of Compliance. Today, Tom visits with Dr. Gleb Tsipursky about his book, The Psychology of AI Adoption at Work: From Resistance to Results (Georgetown University Press), arguing that AI adoption fails mainly due to human factors, not tool complexity.

Citing Pew research showing widespread anxiety about AI and an MIT finding that 95% of AI pilots fail to scale, Dr. Tsipursky describes three emotional blockers: fear of job loss (“AI alarmists”), identity threat when AI automates work people take pride in (“pragmatic resisters”), and shame-driven “reluctant adopters” who use AI secretly, fueling shadow AI risk and limiting ROI. He advises leaders to commit to growth over layoffs, automate disliked tasks first, model AI use, and create sharing channels and meetings to normalize safe adoption. He also emphasizes governance with clear ethical guardrails and individual accountability, replacing approval bottlenecks that drive shadow use.

Key highlights:

  • Why AI Adoption Fails
  • Three Emotional Blockers
  • Trust and Social Stigma
  • AI Versus Calculators
  • Creating Psychological Safety
  • Tactics for Identity Threat
  • Ending Shadow AI Usage
  • Ethical Guardrails and Governance
  • What Success Looks Like

Resources:

Follow Dr. Gleb Tsipursky on:

LinkedIn

YouTube

Facebook

Instagram

X (formerly Twitter)

Book: The Psychology of AI Adoption at Work on Amazon

Website: Disaster Avoidance Experts, LLC

Categories
Blog

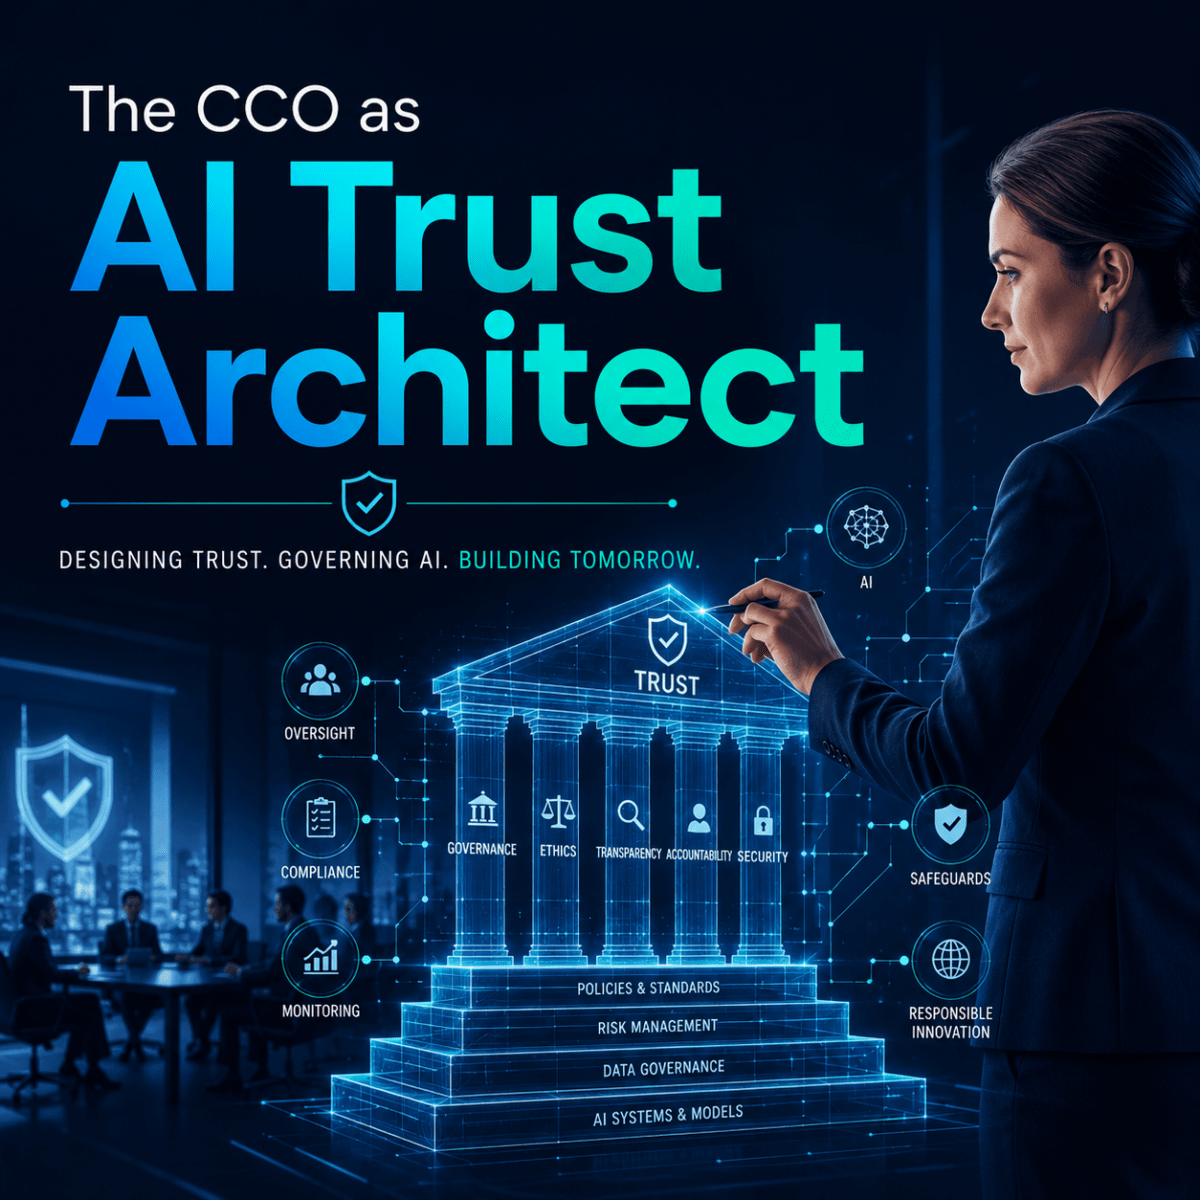
The CCO as AI Trust Architect

The most important AI risk inside many companies may not be that employees are using AI. It may be that employees are using AI and hiding what they are learning. That is the central compliance lesson from Eric Anicich and Jeslyn Brouwers’ HBR article, Why Employees Aren’t Transparent About Their AI Usage. The authors open with a physician who had built a highly effective prompting template inside an approved, HIPAA-compliant AI tool. His colleagues were struggling with the same tool. He believed his template could help them. Yet he did not share it.

The article reports that a study by KPMG and the University of Melbourne, involving more than 48,000 respondents, found that 57% of employees admitted to hiding their AI use at work. More importantly, the authors argue that concealed use is only part of the issue. What employees are learning privately through prompt sequences, chained tools, and successful workflows may matter even more. AI introduces what the authors call the suppression of solutions: employees may be withholding productivity breakthroughs that could help the entire organization.

For the CCO, this creates a new mandate. The compliance function must help bring AI use into the open without becoming the AI police. The CCO must build a governance system that encourages employees to disclose, share, and improve AI-enabled work while still protecting the company from real risks around confidentiality, privacy, IP, bias, inaccurate outputs, cybersecurity, records retention, regulatory representations, and misuse. That is the function the CCO can fulfill: the AI trust function.

Why Hidden AI Use Is a Compliance Problem

Most compliance professionals instinctively focus on the obvious AI risks. Employees may paste confidential data into public tools. They may use AI to draft customer-facing claims without verification. They may generate code, contracts, marketing copy, investigation summaries, due diligence reports, or regulatory submissions without appropriate review. They may rely on AI outputs that are inaccurate, biased, incomplete, or unsupported. Those risks are real.

But the authors point to a second problem: the company may also be losing the benefits of compliant AI experimentation. Productivity gains are once scaled through shared systems and standardized processes. With AI, many gains begin as individual discoveries: a better prompt, a workflow shortcut, a way to summarize information, a way to identify anomalies, or a method that reduces a multi-hour task to minutes. That knowledge is portable, private, and easy to conceal.

This means the CCO must avoid a one-dimensional response. A punitive AI governance program may reduce some visible misuse, but it may also drive experimentation underground. Employees who fear being judged, punished, overworked, or replaced will not share what they are doing. They will protect themselves. That creates the worst of both worlds: risk remains hidden, and useful innovation remains trapped inside individual workflows.

The CCO’s New Role: Govern for Trust, Not Just Control

The author’s core finding is highly relevant to compliance. They surveyed 604 U.S.-based employees who used AI at work daily or multiple times per day. Nearly one in three said they had intentionally withheld AI-related knowledge, workflows, or techniques. Employees in the lowest quartile of organizational trust were nearly four times as likely to withhold AI knowledge as those in the highest quartile (47% versus 14%). A similar pattern appeared for psychological safety, 45% versus 17%.

That finding should feel familiar to compliance professionals. Speak-up culture works the same way. Employees report misconduct when they believe the company will listen, protect them, and act fairly. Employees hide misconduct when they believe the company will punish the messenger, ignore the issue, or retaliate indirectly. AI transparency is now a speak-up issue.

The CCO should therefore treat AI disclosure as part of the company’s broader culture of integrity. The question is not merely, “Are employees using approved AI tools? ”The better question is, ‘Do employees trust us enough to tell us how they are using AI, what they have learned, where they are uncertain, and what risks they see? ”

That is where the compliance function can add unique value. Compliance already understands reporting channels, non-retaliation, policy clarity, training, investigation triage, escalation, monitoring, remediation, third-party risk, and board reporting. Those capabilities can be applied to AI governance if the CCO frames the issue correctly.

Distinguish Experimentation from Misconduct

A major insight in the article is that companies often confuse two very different categories of behavior. One is blameworthy deviance: ignoring rules or cutting corners in ways that harm the organization. The other is exploratory testing: experimenting at the edge of what is known in ways that can generate valuable learning. When companies confuse the second with the first, they punish the behavior they need to encourage. This is directly applicable to the CCO.

An employee who uploads customer personal data into an unapproved public AI tool may have created a serious compliance issue. An employee who uses an approved internal AI tool to create a better first draft of a due diligence memo may have created a learning opportunity. An employee who uses AI to fabricate supporting documentation has engaged in misconduct. An employee who uses AI to test a workflow and then asks compliance whether the use is permissible has done exactly what the company should want. The CCO’s job is to build a framework that makes those distinctions clear.

That means creating red lines, green lanes, and gray zones. Red lines are prohibited uses: confidential data in unapproved tools, AI-generated false records, unreviewed regulatory filings, discriminatory automated decision-making, or any use that circumvents required approvals. Green lanes are encouraged for use: approved tools for summarization, first drafts, brainstorming, translation support, policy search, training development, or internal productivity tasks, where appropriate safeguards are in place. Gray zones are uses that require consultation: HR decisions, customer communications, legal analysis, investigation outputs, high-risk third-party reviews, or regulated submissions.

A compliance program that treats every use of AI as suspicious will teach employees to hide. A compliance program that treats every use of AI as harmless will fail in its duty. The CCO must create the middle path: clear, risk-based, practical, and trusted.

Earn the Disclosure You Want

The article advises leaders to “earn the disclosure” they want. Employees need clear guidance on what AI use is encouraged, what is off-limits, and how to handle gray areas. The authors also warn that companies should not force employees to convert a useful prompt into a long process memo. Lightweight templates, short demos, and practical “show me how you built this” sessions are better ways to turn private methods into reusable knowledge.

That is a practical blueprint for the CCO. A CCO should create an AI disclosure process that is easy to use. It should not feel like an investigation request. It should not require a ten-page form. It should not punish employees for asking questions. The goal is to make disclosure normal.

That is enough to begin. The CCO can then partner with IT, Legal, Privacy, Cybersecurity, HR, Internal Audit, and business leaders to determine whether the workflow should be approved, modified, shared, restricted, or escalated. The key is tone. The message should be: “Show us what you are learning so we can help you use AI safely and scale what works.”

Reward Multiplier Behavior

The article warns against rewarding only individual AI productivity. If employees believe that sharing makes them less distinctive while others benefit, they will hide. Instead, companies should reward reusable workflows, peer adoption, quality improvements, and contributions that help others. The authors recommend giving credit in performance reviews, protecting time for continued experimentation, and closing the loop by telling employees where their contribution was used and what improved. This is where a CCO can help turn AI transparency into culture.

Compliance should not run a generic AI leaderboard that encourages unhealthy competition. Instead, the CCO should help build recognition for responsible AI multipliers: employees who find a better way to do their work, disclose it, help validate it, and enable the company to scale it safely. This turns AI governance from a prohibition system into an integrity system. Employees are not just being told what not to do. They are being recognized for helping the company do better.

In compliance terms, that means rewarding employees who:

  • Identify a safe AI workflow that improves the effectiveness of control.
  • Flag a risky AI use before harm occurs.
  • Develop a prompt that improves due diligence quality.
  • Create a monitoring workflow that identifies anomalies faster.
  • Help colleagues use approved tools properly.
  • Document limitations and human review requirements.
  • Share lessons learned from AI experimentation.

Treat Disclosure as a Contribution

One of the article’s most powerful points is that the manager’s reaction in the first thirty seconds after an employee discloses an AI workflow may be the decisive trust signal. If the employee is treated as though they cut corners, they learn to hide. If the disclosure is treated as something worth understanding, they learn that disclosure pays. The authors also warn that disclosure should not amount to unpaid labor; the employee should demonstrate the method once, and the company should then own the documentation, distribution, and support, while the discoverer keeps the credit. This is a direct instruction to compliance professionals.

A CCO should train managers to respond the same way. Most AI disclosures will not go to compliance first. They will happen in team meetings, performance conversations, project reviews, and manager check-ins. If local managers shame employees for using AI, employees will hide. If local managers automatically add more work to anyone who discloses a productivity gain, employees will hide. If local managers give credit and bring compliance in as a partner, employees will share.

The CCO’s AI Trust Playbook

A CCO who wants to fulfill this function should take five practical steps.

  1. Create a risk-based AI use framework. Define prohibited uses, encouraged uses, and uses requiring consultation. Make the guidance short, practical, and example-driven.
  2. Build a safe AI disclosure channel. This should be separate from the hotline in tone, even if connected administratively. Employees need a place to ask, “Can I use AI this way? ”without feeling as if they are self-reporting misconduct.
  3. Launch structured AI learning sessions. Invite employees to demonstrate useful workflows created with approved tools. Keep documentation light. Capture the use case, data inputs, review controls, risks, and adoption potential.
  4. Partner with HR on incentives. Ensure responsible AI sharing is recognized in performance reviews, promotion discussions, and leadership communications. Reward employees who become AI multipliers, not only those who quietly produce more.
  5. Report AI transparency metrics to leadership and the board. Do not only report policy completion or tool adoption. Report the number of disclosed workflows, number approved for broader use, number modified for risk reasons, number rejected, key risk themes, training gaps, and examples where disclosure improved both productivity and control.

Conclusion

The CCO should not try to own every aspect of AI. IT must own infrastructure. Cybersecurity must own security controls. Legal must advise on legal risks.  Privacy must address data protection. HR must address workforce impacts. Business leaders must own operational use cases. Internal audit must test the program. But the CCO can own the trust architecture.

The bottom line is straightforward. AI governance cannot be built only on restriction, monitoring, and fear. That approach may make the company look controlled while driving the most important AI activity underground.

The CCO has a different opportunity: to build an AI trust function that brings use cases, risks, questions, and innovations into the open. The compliance function should not be the department that says, “Do not use AI.” It should be the function that says, “Use it responsibly, show us what you are learning, and let us help the company scale it safely.” That is how compliance fulfills this function. It turns hidden AI use into visible learning, visible learning into governed practice, and governed practice into ethical business value.

Categories
Blog

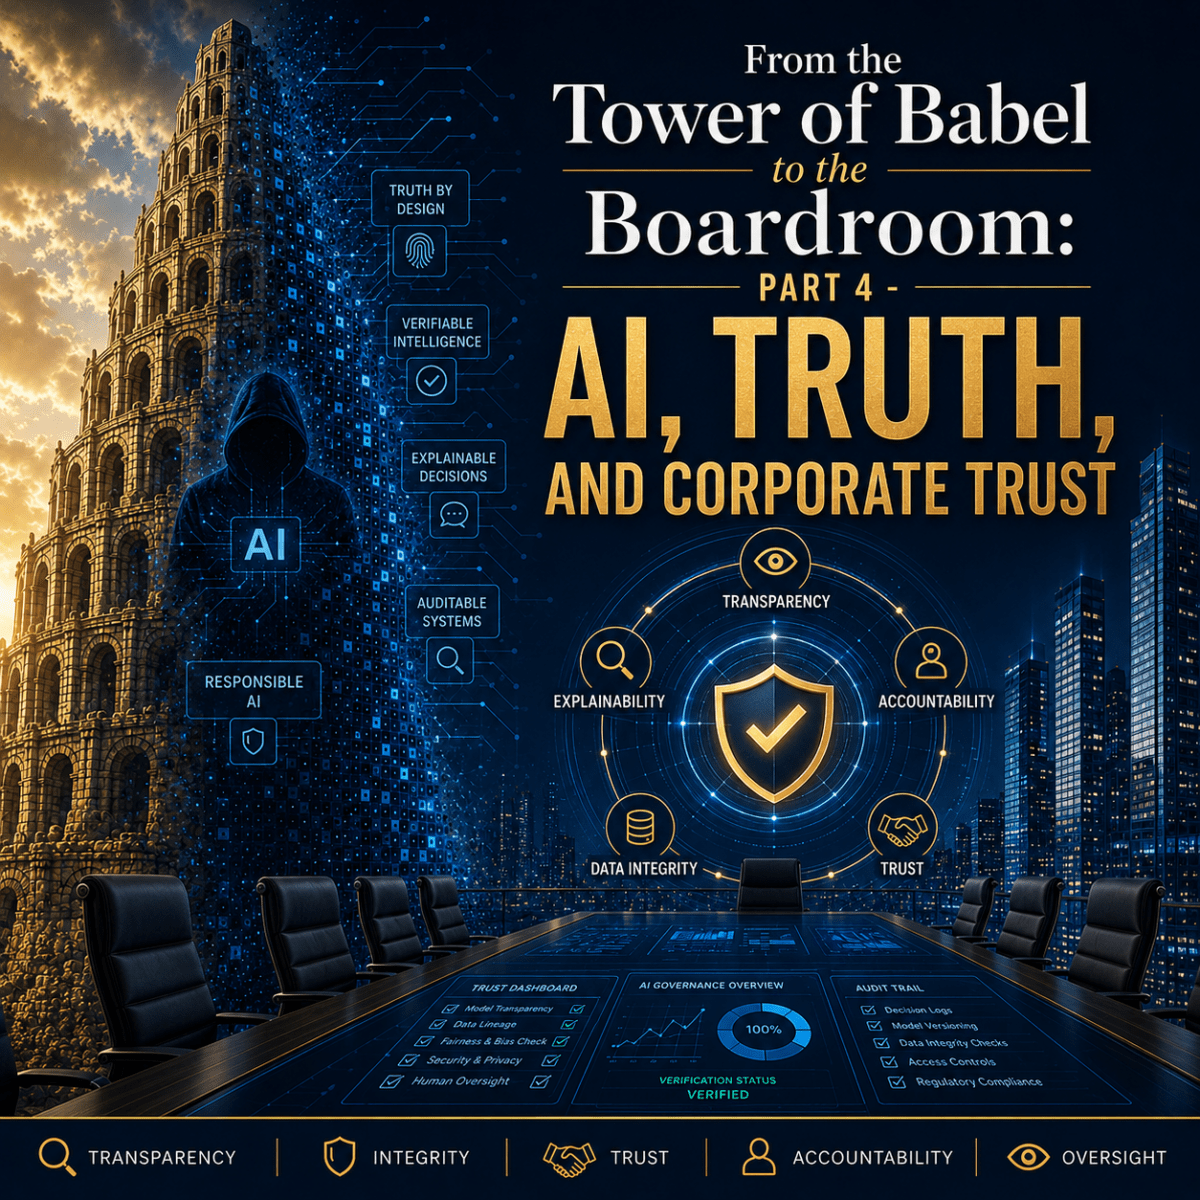
From the Tower of Babel to the Boardroom: Part 4 – AI, Truth, and Corporate Trust

Employees trust that leadership will tell them the truth. Investors trust that disclosures are accurate. Customers trust that representations are reliable. Boards trust that management reporting is complete. Compliance officers trust that records, interviews, hotline reports, emails, chats, invoices, certifications, and audit findings reflect reality.

Artificial intelligence now challenges that foundation. AI can generate text, audio, images, video, records, summaries, identities, and narratives at speed and scale. It can help a compliance function become more effective. It can also make falsehood more convincing, fraud more sophisticated, and manipulation harder to detect.

In the first three posts in this series, we used Magnifica Humanitas to move from governance principle to compliance program design and then to internal controls for shadow AI. In this fourth post, we turn to one of the most important themes in the Encyclical Letter: truth. Pope Leo XIV says the digital transformation requires us to rediscover truth as a common good, protect the dignity of work, and safeguard freedom against dependence and commercialization (Magnifica Humanitas, ¶131). For boards and compliance leaders, that is a powerful governance lesson. Without truth, there is no trust. Without trust, there is no culture. Without culture, no compliance program can be effective.

Truth as a Common Good

Magnifica Humanitas warns that digital platforms and AI systems are transforming public and institutional communication. The Encyclical identifies a core risk: AI can construct distorted narratives, blur the boundary between truth and falsehood, mix facts with opinions, and manipulate content, images, and video (Magnifica Humanitas, ¶132). It also reminds us that truthful information requires verification, cross-checking of sources, responsible argument, and shared practices of trust (Magnifica Humanitas, ¶132).

For the compliance professional, this is not abstract philosophy. It is an operational reality. A corporation is built on records and representations. A company’s compliance program depends on accurate policies, reliable data, trustworthy reporting, credible investigations, authentic communications, and truthful escalation to leadership and the board. If AI weakens the company’s ability to know what is real, AI becomes a compliance risk.

The issue is not only misinformation in public discourse. It is misinformation inside the enterprise. AI-generated falsehood can appear in emails, invoices, employee complaints, due diligence materials, contracts, investigation files, synthetic images, training materials, board reports, and financial documentation. Truth is no longer only an ethical value. It is a control objective.

From Encyclical Principle to Corporate Trust Requirement

The corporate translation is direct. If truth is a common good, information integrity is a governance requirement. If AI can distort narratives and manipulate content, companies need verification controls. If truthful information depends on cross-checking and responsible argument, compliance cannot treat AI outputs as self-authenticating. If communication creates culture, as Magnifica Humanitas teaches, then AI-generated communications must be governed because they shape how employees, customers, investors, and directors understand the company (Magnifica Humanitas, ¶135).

The Encyclical also calls for an ecology of communication grounded in transparency, personal data protection, rigorous verification, and the proper use of digital tools (Magnifica Humanitas, ¶137). In corporate terms, that means controls over high-risk communications, rules for AI-generated content, validation of AI-assisted summaries, protection of the integrity of investigations, and reporting systems that enable the board to trust what it receives.

Synthetic Reality and Corporate Risk

We are entering the age of synthetic reality. Companies must assume that audio may be cloned, video may be fabricated, documents may be AI-generated, and digital identities may be false. This does not mean every communication is suspect. It means the company must build verification protocols for high-risk decisions.

The Arup deepfake fraud demonstrates the corporate risk. The Guardian reported that in 2024, public reporting stated that engineering firm Arup was victimized in a deepfake scam involving its Hong Kong office, where fraudsters reportedly used AI-generated video impersonations in a call that led to the transfer of approximately $25 million. That incident should be understood as more than a cyber story. It is a governance story, a finance controls story, a human factors story, and a compliance story.

A traditional approval process may fail when a trusted executive appears to be present on a video call. A fraud-prevention control may fail when an employee believes their identity has already been verified. A payment control may fail when urgency, authority, secrecy, and synthetic trust converge. The compliance lesson is clear: in an AI-enabled environment, trust must be verified when the risk is high.

AI and the Integrity of Corporate Information

Boards and CCOs should treat the integrity of corporate information as part of AI governance. This includes information created by AI, information summarized by AI, and information used to make AI-supported decisions.

Consider internal investigations. AI can help summarize documents, cluster communications, identify patterns, and organize timelines. But Magnifica Humanitas reminds us that AI lacks moral conscience, does not understand what it produces, and does not bear responsibility for its consequences (Magnifica Humanitas, ¶99). A compliance investigator cannot delegate credibility findings to a machine. AI can support the investigation record. It cannot become the investigation record.

Consider hotline reporting. AI may help triage allegations, identify themes, translate complaints, and route issues. But if the system misclassifies a serious allegation as low risk, strips away nuance, or fails to identify indicators of retaliation, the company may miss a critical signal. Consider board reporting. A polished AI-generated report may look authoritative while masking weak data, incomplete controls, or unsupported conclusions. In compliance, elegance is not evidence.

The DOJ ECCP and Trustworthy AI

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) now asks how companies identify and manage emerging technology risks, including AI. It asks how companies govern AI in commercial operations and in their compliance programs; whether controls monitor trustworthiness and reliability; whether AI is limited to intended uses; what human decision-making baseline is used; how accountability is enforced; and how employees are trained.

This is where the Encyclical’s moral mandate and the DOJ’s compliance test meet. Magnifica Humanitas says responsibility must be clearly defined at every stage and that accountability requires identifying who must account for decisions, justify them, monitor them, challenge them, and remedy harm (Magnifica Humanitas, ¶105). The ECCP asks whether a company has converted that accountability into governance, controls, training, monitoring, and evidence. For CCOs, the question is not whether AI can help compliance. It can. The question is whether compliance can explain how AI-supported information is validated, reviewed, escalated, corrected, and documented.

NIST, COSO, and the Control Language of Trust

NIST provides a practical vocabulary for this discussion. The NIST AI Risk Management Framework identifies trustworthy AI characteristics, including validity and reliability; safety, security, and resilience; accountability and transparency; explainability and interpretability; privacy enhancement; and fairness, with harmful bias managed. For this post, reliability and transparency matter most. Reliability asks whether an output can be trusted for the intended purpose. Transparency asks whether the company can understand, explain, and govern the system.

COSO also matters here. COSO’s internal control framework is designed to help organizations achieve operations, reporting, and compliance objectives, and COSO’s GenAI guidance translates that internal-control discipline into AI governance. In the AI context, companies need controls over the creation, use, review, approval, and communication of AI-generated or AI-assisted information. This is where CCOs, internal audit, finance, legal, and IT must work together. The company should identify where authenticity matters most and design controls accordingly.

Practical Controls for AI, Truth, and Trust

A practical compliance program should include controls for AI-enabled truth risk.

First, companies should adopt verification protocols for high-risk communications. Payment instructions, executive requests, wire transfers, confidential transactions, changes to vendor banking information, M&A activity, crisis communications, and sensitive employment decisions should require independent verification outside the original communication channel.

Second, companies should require labeling or disclosure where AI-generated content is used in official corporate communications and authenticity matters. Third, companies should protect investigations from unverified AI outputs. AI-generated summaries should be treated as work aids, not evidence. Investigators should validate source documents, preserve original records, and document human review.

Fourth, companies should train employees on synthetic fraud. Magnifica Humanitas warns that AI-enabled manipulation of images and videos can make exploitation and deception more insidious (Magnifica Humanitas, ¶141). Employees should learn the red flags: urgency, secrecy, unusual payment instructions, refusal to use normal channels, unexpected video calls, requests to bypass controls, and pressure from apparent senior leaders.

Fifth, companies should create an incident response process for AI-enabled deception. A deepfake attempt, a synthetic invoice, a cloned executive voice, a fake employee profile, or an AI-generated document should be reportable, investigated, tracked, and remediated.

Board Oversight and Corporate Trust

For boards, AI and truth raise a serious oversight issue. Directors rely on management reporting to fulfill their duties. If AI affects the integrity of that reporting, boards need to understand the control environment.

The Caremark lesson is not that directors must become forensic AI experts. Directors must make a good-faith effort to ensure that reasonable information and reporting systems are in place for central compliance risks. In Marchand v. Barnhill (Bluebell Ice Cream), the Delaware Supreme Court emphasized the importance of board-level monitoring and reporting systems for mission-critical compliance risks.

Magnifica Humanitas gives this oversight obligation a deeper accountability mandate. It says AI governance requires defined responsibility, justification of decisions, monitoring, challenge, and remediation (Magnifica Humanitas, ¶105). The board’s obligation is not technical mastery. It is a reporting and monitoring system that shows management can authenticate what matters, identify AI-enabled truth risks, escalate concerns, and remediate failures.

5 Lessons for the CCO
  1. Treat truth as a compliance control. Accurate records, authentic communications, validated reports, and reliable investigation files are essential to the effectiveness of compliance programs. Truth must be designed into the control environment.
  2. Build verification into high-risk processes. Payment approvals, executive instructions, vendor bank changes, crisis communications, and sensitive decisions should require independent verification.
  3. Govern AI-assisted evidence. AI can support investigations and reporting, but human review, source validation, preservation of original records, and documentation must remain mandatory.
  4. Train employees to challenge synthetic reality. Deepfakes, cloned voices, fake identities, and AI-generated documents should be part of fraud, cyber, finance, and compliance training.
  5. Report information integrity risk to the board. Boards need evidence that management has identified AI-enabled truth risks and designed controls to prevent, detect, respond to, and remediate them.
Conclusion: Corporate Trust Must Be Protected

Magnifica Humanitas reminds us that truth is a common good. That is a moral principle, but it is also a compliance principle. A company cannot govern itself if it cannot trust its information. A board cannot oversee what management cannot verify. A CCO cannot certify program effectiveness if the underlying records, reports, and communications are unreliable.

Compliance professionals should embrace AI. It can improve risk detection, strengthen monitoring, support investigations, and expand analytical capacity. But AI also requires vigilance, responsibility, transparency, governance, and human primacy. In the age of synthetic reality, compliance must help the company protect truth as part of the control environment.

In the next and final post in this five-part series, we will broaden the lens again. We will examine the Human Supply Chain of AI: Workforce Transformation, Third-Party Risk, and Modern Slavery. That post will tie together the human impact of AI, the dignity of work, vendor risk, data governance, and the compliance responsibility to look beyond the visible interface to the people, suppliers, and systems that make AI possible.

Categories
AI in Healthcare

AI in Healthcare: Five Healthcare AI Stories You Need to Know This Week – May 15, 2026

Welcome to AI in Healthcare in 5 Stories. This podcast is a Weekly Briefing of the five most important AI developments shaping healthcare, medicine, and life sciences. Each week, Tom Fox breaks down the latest stories on clinical innovation, regulation, privacy, compliance, patient safety, and operational transformation through a practical, business-focused lens. Designed for healthcare compliance professionals, executives, legal teams, clinicians, and industry leaders, the podcast moves beyond headlines to explain what each development means in the real world.

The top five stories for the week ending May 15, 2026, include:

  1. Acceptance of AI in healthcare is governed by trust. (American Medical Journal)
  2. The Trump Administration wants to cut back AI protections in healthcare. (KFF Health News)
  3. Where AI is making a difference in healthcare. (Medical Economics)
  4. Using AI in pharma development. (WSJ)
  5. Using AI in hospital systems. (American Hospital Association)

For more information on the use of AI in Compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.

Categories
All Things Investigations

ATI In-House Insights: Navigating Internal Investigations: A Conversation with Mike Gill

Welcome to the Hughes Hubbard Anti-Corruption & Internal Investigations Practice Group’s podcast, All Things Investigation. This is a special series featuring sights from in-house practitioners, hosted by Mike DeBernardis. In this podcast, Mike D visits with Mike Gill, Assistant GC and Director of Investigations at HII, on conducting internal investigations from an in-house perspective in a defense shipbuilding environment.

Gill says the first concern when allegations arise is immediate safety risk to employees and the integrity of work affecting Navy and other military customers, followed by designing an investigation that will be viewed as timely, accurate, and credible. He emphasizes scoping, planning, selecting the right team (including technical experts and, sometimes, outside counsel), and establishing disciplined communication and reporting lines to management and customers while protecting privilege. Gill highlights building employee trust through fair processes, enforcement of anti-retaliation policies, and appropriate follow-up, and notes common mistakes: jumping to conclusions, failing to bound scope, and inadequate planning.

Key highlights:

  • Safety First Priorities
  • Architecting the Investigation
  • Scope Planning and Team
  • Protecting Privilege
  • Culture and Fairness
  • Anti-Retaliation Trust
  • Top Mistakes to Avoid

Resources:

Hughes Hubbard & Reed website

Mike DeBernardis

Mike Gill on LinkedIn

Categories
Great Women in Compliance

Great Women in Compliance: Why Decision Rubrics Matter in the Age of AI with Hemma Lomax and Shalini Rajoo

In this conversation, GWIC host Dr. Hemma R. Lomax and Shalini Rajoo explore the critical role of decision rubrics in governance, accountability, and trust, especially in the context of AI. Shalini shares her journey from law to compliance, emphasizing the importance of understanding systems and the impact of leadership on decision-making processes. They discuss how transparency and clarity in decision-making can build trust within organizations and the necessity of responsible AI governance. Practical tips for improving decision quality are also provided, highlighting the importance of self-awareness and critical thinking in leadership.

Takeaways:

  • The biggest risk in governance is unclear decisions.
  • AI amplifies existing clarity or confusion in decision-making.
  • Systems and rules reflect the identities of their architects.
  • Everyone has an impact on those around them every day.
  • Leadership is about improving the people around you.
  • It’s not just about rules; it’s about how people behave.
  • Decision rubrics provide consistency and predictability in outcomes.
  • Transparency in decision-making processes builds trust.
  • Slowing down to ask questions can lead to better decision-making.
  • Writing down the reasons for decisions brings clarity and accountability.

Sound bites:

“Systems and rules are not inherently neutral.”

“Transparency in decision making builds trust.”

“Slow is smooth, and smooth is fast.”

Chapters:

00:00 Introduction to Decision Rubrics and Governance

02:55 Shalini’s Journey: From Law to Governance

06:09 The Impact of Systems on Leadership and Accountability

09:09 Transitioning to Compliance and Ethics

11:49 Understanding Decision Rubrics in Compliance

15:06 The Role of Leadership in Decision Making

18:03 Designing Conditions for Effective Decision Making

20:47 The Importance of Transparency in Decision Processes

24:09 Decision Rubrics: Building Trust in Organizations

26:49 AI and Governance: Leadership Infrastructure Failures

29:47 Responsible AI: The Role of Ethics and Compliance

32:55 Practical Tips for Improving Decision Quality

36:00 Conclusion: The Future of Decision Making in AI

Guest Biography:

Shalini Rajoo is the Founder and Principal Consultant of Shalini Rajoo Advisory, LLC, where she partners with organizations to design governance, compliance, and decision-making systems that are resilient, trustworthy, and aligned to real operational pressures. Across more than two decades in law, compliance, HR, and organizational leadership, Shalini has helped companies and leaders move beyond check-the-box frameworks to build structures that embed accountability, clarity, and performance into everyday decisions.

She began her career in South Africa, first as a public prosecutor and then leading regulatory work with the Department of Trade and Industry, collaborating with legislative and executive stakeholders on corporate, competition, and consumer law. After relocating to the U.S., Shalini practiced commercial litigation. She later served as Director of Global Business Conduct for a Fortune 500 company, where she redesigned ethics and compliance systems, led global risk assessments, and championed psychological safety and integrity-based practices.

Today, Shalini’s work centers on helping leaders clarify decision rights, governance architectures, and accountability pathways — especially as organizations adopt AI and automation. She recently spoke at the Opal Group’s Corporate Governance & Ethics in the Age of AI conference, where she reframed AI governance as a leadership-infrastructure challenge rather than a purely technical or compliance one.

Categories
From the Editor's Desk

From the Editor’s Desk – Aaron Nicodemus on the CW AI Conference Insights: Navigating the Practical Use of AI in Compliance

In this episode of ‘From the Editor’s Desk,’ Tom Fox visits with Aaron Nicodemus to discuss highlights from the recent Compliance Week AI Conference. Key takeaways include the importance of understanding the purpose and practical use of AI tools before implementation, the pressures from C-suite and boards to adopt AI, and the necessity of a human-in-the-loop approach. The conversation also touches on integrating trust and integrity into AI adoption, the evolving role of compliance as a trusted partner in AI initiatives, and the collective willingness to learn and apply AI across compliance operations.

Key highlights:

  • Importance of Understanding AI Implementation
  • Pressure from the Top: Compliance and AI
  • Human Oversight in AI Processes
  • Trust and Integrity in AI
  • Compliance as a Competitive Advantage
  • Real-World Examples: Robinhood and DocuSign
  • The Evolving Role of Compliance in AI
  • Conference Vibes and Final Thoughts

Resources:

Aaron Nicodemus on LinkedIn

Compliance Week