Categories
Blog

Anthropic’s IPO: Top 10 Corporate Compliance Risks, Part I

Anthropic’s S-1 Registration Statement (IPO), released on October 26th, offers a revealing look at the emerging compliance challenges of frontier artificial intelligence companies. More importantly, it provides a roadmap for Chief Compliance Officers (CCOs), general counsel, boards of directors, and risk professionals seeking to understand how traditional corporate compliance obligations intersect with increasingly autonomous AI systems.

Responses have been interesting: Matt Kelly, writing in Radical Compliance, identified “100 pages of risks.” Senator Elizabeth Warren, perhaps only now realizing that Skynet may be on the way to becoming ‘self-aware,’ is quoted by the Wall Street Journal (WSJ) as being “deeply troubled” by the risks listed in the IPO “and is demanding answers to a long list of questions before the artificial-intelligence giant goes public.” Ethisphere’s Erica Salmon Byrne noted that the terms of service place most enterprise AI risk squarely on the customer rather than Anthropic.

My conclusion is more down-to-earth and grounded in corporate compliance. Anthropic’s disclosures show that AI governance is no longer simply a question of responsible technology development. It is an enterprise compliance challenge involving regulatory enforcement, internal controls, cybersecurity, third-party oversight, intellectual property, corporate governance, and organizational accountability. This week, I will explore what I see as the Top 10 risks from a corporate compliance perspective. In this blog post, I will consider the first five in ascending order of criticality.

Yet from this exercise, I believe the most significant compliance question is whether a company’s governance and control environment can keep pace with the capabilities of the technology it develops and deploys. The following rankings prioritize potential regulatory exposure, severity of harm, enterprise impact, and the difficulty of designing effective preventive and detective controls. They reflect a compliance-focused interpretation of Anthropic’s disclosures, not the company’s own ranking.

1. AI safety, model autonomy, and inadequate governance controls

The disclosed risk: Anthropic acknowledges that increasingly capable AI models may create significant safety risks, including harmful outputs, misuse, unintended behavior, and failures of existing safety mechanisms. Its disclosure specifically addresses autonomous agents that can execute code, access external systems, conduct transactions, and operate for extended periods with limited human oversight.

The compliance exposure: A company may deploy AI capabilities that exceed the effectiveness of its risk management, monitoring, and internal control systems. This creates potential exposure under consumer protection laws, AI-specific regulations, negligence theories, and contractual obligations.

The CCO response: Establish formal AI risk classifications, independent safety testing, deployment approval gates, continuous monitoring, incident escalation, and documented human oversight. Map these controls to the NIST AI Risk Management Framework and ISO/IEC 42001.

The Board question: Who has the authority to stop deploying a profitable AI product when safety controls are inadequate?

2. Regulatory investigations, enforcement, and evolving AI laws

The disclosed risk: Anthropic reports receiving an October 2026 FTC civil investigative demand seeking information concerning consumer protection, privacy, data protection, and product safety and security. It also identifies a changing regulatory landscape across the United States and international jurisdictions.

The compliance exposure: The risk is not simply that new regulations may impose additional costs. Regulators can investigate whether existing representations, disclosures, safety practices, and customer protections are deceptive, inadequate, or inconsistent with applicable law.

The CCO response: Create an AI regulatory obligations inventory, assign accountable control owners, test compliance with existing consumer protection requirements, and maintain a centralized regulatory inquiry and enforcement response process.

The Board question: Can management demonstrate that the company’s actual AI controls support the representations it makes to regulators, customers, and investors?

3. Data privacy, cybersecurity, and protection of sensitive information

The disclosed risk: Anthropic identifies risks associated with personal data processing, cybersecurity incidents, unauthorized access, cross-border data transfers, and differing privacy requirements across jurisdictions.

The compliance exposure: AI platforms can process enormous quantities of sensitive information. An unauthorized disclosure, improper use of training data, or compromise involving an AI agent could create exposure under the GDPR, California privacy laws, FTC enforcement authority, and contractual data protection obligations.

The CCO response: Require data mapping, privacy impact assessments, access restrictions, encryption, retention controls, vendor security reviews, and incident response exercises tailored to AI systems.

The Board question: Does management understand what sensitive information enters its AI systems, where that information travels, and who can access it?

4. Intellectual property, copyright, and training-data compliance

The disclosed risk: Anthropic acknowledges substantial uncertainty about how copyright law and open-source licensing apply to AI model training. The filing also describes ongoing copyright litigation and a $1.5 billion settlement in the Bartz copyright class action, approved in July 2026.

The compliance exposure: A company’s underlying AI model may depend upon training data for which its rights are disputed. Adverse litigation outcomes could result in substantial damages, licensing obligations, restrictions on training data, or operational changes to deployed models.

The CCO response: Establish documented data provenance, licensing reviews, training-data acquisition controls, legal approval procedures, and records demonstrating the basis for using copyrighted materials.

The Board question: Can the company demonstrate a defensible legal basis for the data used to develop its most commercially significant AI models?

5. Export controls, economic sanctions, and national security restrictions

The disclosed risk: Anthropic identifies exposure under U.S. export controls, sanctions regimes, and potentially the International Traffic in Arms Regulations. Its filing describes June 2026 U.S. Department of Commerce restrictions affecting its Fable 5 and Mythos 5 models, which were later lifted following safeguard updates.

The company also acknowledges that its export and sanctions controls have not always been fully effective and that it has previously made voluntary disclosures of noncompliance.

The compliance exposure: Advanced AI models may constitute controlled technology. Unauthorized model access, improper transfers, sanctioned-country usage, or inadequate customer screening could trigger enforcement, penalties, and loss of export privileges.

The CCO response: Integrate export classification, restricted-party screening, geolocation controls, customer due diligence, access monitoring, and escalation procedures into the product deployment architecture.

The Board question: Can the company prevent restricted users and jurisdictions from accessing controlled AI capabilities, including through intermediaries?

These first five risks establish a central compliance challenge: can a company demonstrate that its controls keep pace with the AI capabilities it develops and deploys? Safety governance, regulatory compliance, data protection, intellectual property, and export restrictions require clear ownership, tested controls, and timely escalation to the board.

In Part II, I will examine the remaining five risks, moving into the business relationships, commercial practices, financial reporting, and governance arrangements that support an AI enterprise. For CCOs and boards, these issues bring the analysis directly into familiar compliance territory. The question is whether established compliance disciplines have been adapted to the speed, scale, and complexity of the AI business.
These first five risks establish a central compliance challenge: can a company demonstrate that its controls keep pace with the AI capabilities it develops and deploys? Safety governance, regulatory compliance, data protection, intellectual property, and export restrictions require clear ownership, tested controls, and timely escalation to the board.

In Part II, I will examine the remaining five risks, moving into the business relationships, commercial practices, financial reporting, and governance arrangements that support an AI enterprise. For CCOs and boards, these issues bring the analysis directly into familiar compliance territory. The question is whether established compliance disciplines have been adapted to the speed, scale, and complexity of the AI business.
Categories
Popcorn and Compliance

Popcorn and Compliance: Frankenstein Meets the Wolf Man When Monsters Collide: Compliance and Enterprise Risk

This October, Tom Fox returns to one of his all-time favorite subjects: the Universal Pictures classic monsters. Over the years, he has explored the classics, including Dracula, The Mummy, The Wolf Man, and The Invisible Man, with detours into films by Val Lewton and Hammer Films. This year, Tom takes a deep dive into the first five Frankenstein films. The series has already covered the original Frankenstein, Bride of Frankenstein, Son of Frankenstein, and The Ghost of Frankenstein. The fifth and final episode turns to one of Tom’s favorite horror films of all time, Frankenstein Meets the Wolf Man, released in 1943. Tom’s AI co-hosts, Timothy and Fiona, join him for commentary.

Film Synopsis:

Frankenstein Meets the Wolf Man begins primarily as a continuation of Larry Talbot’s story from The Wolf Man. Talbot, played by Lon Chaney Jr., is resurrected and desperately seeks a way to end his werewolf curse. His search eventually leads him to the ruins of Frankenstein’s castle, where he discovers Frankenstein’s Monster frozen beneath the wreckage and revives him. Dr. Mannering becomes involved in an attempt to cure Talbot while also restoring the Monster to full strength. The inevitable result is the movie’s great selling point: the Wolf Man and Frankenstein’s Monster, now played by Bela Lugosi, finally collide. It was the first Universal film to bring two of its major horror characters together in this fashion.

Key Highlights:

  • Risks do not exist in silos.
  • Risk aggregation belongs in enterprise risk management.
  • AI governance demonstrates the problem perfectly.
  • The CCO should be a connector, not the owner of everything.
  • Boards need to see the entire castle.

Popcorn and Compliance takeaway: The greatest enterprise risk may not be Frankenstein’s Monster or the Wolf Man. It may be what happens when two risks nobody considered together finally collide.

Closing the Popcorn and Compliance Frankenstein Series

Across these five films, we get something remarkably close to the lifecycle of a corporate compliance failure.

Henry Frankenstein creates risk without adequate governance.

In Bride of Frankenstein, leadership knows the danger but succumbs to pressure and ethical compromise.

In Son of Frankenstein, a new generation inherits unresolved legacy risk.

In The Ghost of Frankenstein, supposedly resolved problems return because remediation and controls are ineffective.

Finally, in Frankenstein Meets the Wolf Man, an unresolved risk collides with another risk and becomes an enterprise problem.

That is what makes these movies such fertile territory for Popcorn and Compliance. The Monster is never simply the Monster. He is the product of decisions, incentives, weak controls, poor oversight, inadequate remediation, and leaders who repeatedly convince themselves that this time they can manage the consequences.

For the compliance professional, there may be no better question to take from the entire Universal Frankenstein cycle:

What Monster is your organization creating, inheriting, reviving, or failing to see today?

Timothy and Fiona are AI-generated voices, courtesy of Notebook LM.

Categories
Blog

Frankenstein and Compliance: Part 5 – Frankenstein Meets the Wolf Man: When Monsters Collide

Ed. Note: This month, on his podcast series Popcorn and Compliance, Tom Fox dives deep into the first five Frankenstein movies. Over October, Tom Fox will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolf Man. This blog post accompanies the podcast series.

The first four Frankenstein films provide a useful progression for corporate compliance. Frankenstein examined innovation without adequate governance. Bride of Frankenstein shows leadership that understands risk but lets pressure and rationalization override judgment. Son of Frankenstein moved to inherited risk and the obligations that arise when new leadership discovers legacy problems. The Ghost of Frankenstein asks whether remediation actually works. 

Frankenstein Meets the Wolf Man (1943) changes the risk equation. There are now two monsters. Larry Talbot, played by Lon Chaney Jr., returns from The Wolf Man seeking a way to end the curse that transforms him into a werewolf. His search eventually brings him to the ruins of Frankenstein’s castle, where he discovers the Monster, played in this film by Bela Lugosi. Talbot revives him, Dr. Mannering becomes involved, and the film eventually delivers what its title promises: Frankenstein’s Monster and the Wolf Man collide.

For corporate compliance professionals, the movie provides a useful way to think about enterprise risk. Organizations necessarily divide risk into categories and assign responsibilities to different functions. Compliance may oversee anti-corruption, sanctions, third-party, antitrust, and other regulatory risks. Information Security manages cyber risk. Privacy oversees data protection. HR manages employment-related risks. Finance owns financial controls. Internal Audit provides assurance. Enterprise Risk Management looks across the organization. 

That structure is necessary. It can also create silos. The most significant corporate risks do not always remain within the categories management assigns to them. They interact. When they do, the resulting exposure may be greater than the organization sees when each risk is assessed independently. The compliance challenge is not simply identifying each monster. It is understanding what happens when they meet.

Risk Does Not Respect the Organizational Chart

Companies assign risk ownership because someone must be accountable. That is good governance. The problem begins when risk ownership becomes information ownership. Consider a third-party distributor operating in a high-risk market. Compliance may identify concerns about the distributor’s beneficial ownership. Finance may identify unusual payment requests. Information Security may detect suspicious access involving the distributor’s credentials. Internal Audit may identify invoice exceptions. Legal may become aware of litigation or regulatory concerns involving related entities. Each function may respond appropriately to the information it possesses.

Yet the organization may still fail if nobody connects those facts. The compliance issue is therefore not simply whether individual control functions are doing their jobs. It is whether the organization’s governance structure allows information to move across functional boundaries. This distinction matters more as corporate risks become more interconnected.

A cybersecurity event can become a privacy incident. A privacy incident can become a regulatory investigation. A regulatory investigation can create disclosure obligations. A third-party issue can become an anti-corruption problem, which can become a books-and-records problem, which can become a securities issue. Risk categories are useful for management. They are not boundaries that real-world events respect. 

The Wolf Man and Frankenstein’s Monster Are Different Risks

One useful aspect of Frankenstein Meets the Wolf Man is that its two principal characters represent different kinds of risk. Larry Talbot understands his condition. He knows that particular circumstances trigger his transformation and that the consequences can be severe. His risk is recurring and linked to identifiable conditions. Frankenstein’s Monster represents something different. He is a legacy risk repeatedly inherited, revived, and unsuccessfully controlled by others.

Put them together and the problem changes. Companies experience similar combinations. A business may have a known third-party risk that becomes significantly more serious when combined with expansion into a high-risk jurisdiction. A weak control environment may become more consequential when management introduces aggressive sales incentives. A cybersecurity vulnerability may become more significant when the company deploys an AI system with access to sensitive information. The risks do not merely accumulate. They can amplify one another. That is why risk assessment should consider interdependencies. 

Risk Aggregation Should Be Part of the Compliance Conversation

Traditional compliance risk assessments often organize risks by subject matter.

  • Anti-corruption risk.
  • Sanctions risk.
  • Antitrust risk.
  • Third-party risk.
  • Privacy risk.
  • Conflicts of interest.
  • Books and records.

That approach is useful because it creates structure and allows organizations to identify controls and owners. It can also obscure combinations of risk. Consider a company acquiring a business in a high-risk jurisdiction. The acquisition may involve weak financial controls, substantial government interaction, a distributor-based sales model, aggressive growth assumptions, and a local culture unfamiliar with the acquiring company’s compliance expectations. Each issue may appear manageable when assessed separately. Together, they may produce a materially different risk profile. 

The CCO should therefore consider adding risk aggregation to the compliance risk assessment process. Where do significant risks intersect? Which business units face several elevated risks simultaneously? Which third parties create exposure across multiple compliance areas? Which strategic initiatives combine new technology, new markets, new partners, and aggressive financial expectations? A heat map that displays risks individually may not reveal these relationships. Compliance should be able to explain not only where the red boxes are but also what happens when several red boxes occupy the same part of the business.

AI Is an Enterprise Risk Multiplier 

Artificial intelligence provides one of the clearest modern examples of the problem. Companies sometimes discuss “AI risk” as though it were one category. Unfortunately, it is not. An AI deployment can simultaneously raise privacy, cybersecurity, intellectual property, employment, discrimination, consumer protection, regulatory, third-party, recordkeeping, and reputational issues.

What about an AI tool used to assist hiring decisions? HR may view it as a talent-management system. Information Security may assess the technology vendor. Privacy may examine candidate data. Legal may consider employment requirements. Compliance may evaluate governance and ethical concerns. Procurement may negotiate the contract. Every function may perform its assigned task. The organization still needs someone to evaluate the complete risk picture.

The same issue arises when AI is used for internal investigations, compliance monitoring, customer interactions, sales recommendations, financial decisions, or employee evaluation. This is why AI governance requires cross-functional management.

Frameworks such as the NIST AI Risk Management Framework and ISO/IEC 42001 are useful because they encourage organizations to think about governance, accountability, risk identification, measurement, monitoring, and continual improvement rather than treating AI exclusively as an IT issue. The central business question is not which department owns AI. It is whether the governance structure addresses the risks created by the particular use case.

The CCO Should Be a Connector, Not the Owner of Everything

The increasing interconnectedness of risk raises an important question about the CCO’s role. The answer should not be that Compliance owns every risk involving law, ethics, or reputation. That approach creates its own governance problem.

Business management owns business risk. Information Security should remain accountable for cybersecurity. HR should remain accountable for employment processes. Finance should own financial controls. Legal should provide legal advice. Internal Audit should preserve its independent assurance role. The CCO can nevertheless play an important role as a connector.

Compliance often receives information from multiple parts of the organization. Hotline reports, investigations, third-party due diligence, monitoring results, policy exceptions, training data, regulatory developments, culture assessments, and risk assessments all provide different views of organizational behavior. That perspective can allow Compliance to identify patterns that may not be visible within a single business function. The CCO should therefore ask where information needs to be shared, where cross-functional escalation is necessary, and where significant risks require joint governance. The goal is coordination without diluting accountability.

Mission-Critical Risk and Board Oversight

This also connects to the broader Marchand discussion about board oversight of significant and mission-critical risks. Directors do not need to become operational risk managers. They do need reasonable assurance that management has systems to identify significant risks and escalate material information.

For interconnected risks, that means understanding how management aggregates information. 

  • Which risks are sufficiently significant to require cross-functional oversight?
  • How does management identify emerging combinations of risk?
  • Who resolves disagreements between control functions?
  • What information reaches the board?
  • How are significant risks assigned when they do not fit within one organizational function?

These questions matter most when a risk is central to the company’s business model. The board does not need to manage the monsters. It needs to understand whether management can see when they are moving toward one another. 

Practical Actions for the CCO 

Frankenstein Meets the Wolf Man suggests several practical actions for compliance leadership. The compliance risk assessment should identify not only individual risks but also significant risk intersections. CCOs should look for business units, markets, third parties, products, and strategic initiatives where multiple elevated risks converge. Compliance should establish relationships and information-sharing mechanisms with Internal Audit, Legal, Finance, HR, Information Security, Privacy, Procurement, and Enterprise Risk Management. Significant cross-functional risks should have clear owners, escalation criteria, and decision rights.

CCOs should also consider whether existing compliance dashboards show relationships among risks or simply report individual metrics. Data from investigations, hotline reports, third-party monitoring, policy exceptions, audit findings, and other sources can become substantially more valuable when analyzed together. For emerging technologies such as AI, Compliance should participate in cross-functional governance while avoiding the temptation to own every associated risk. The objective is not centralized ownership. It is connected governance.

The Compliance Lesson

Frankenstein Meets the Wolf Man completes the compliance progression of the Universal Frankenstein films. Organizations create risks. Leadership can compromise in responding to them. New management can inherit them. Remediation can fail to eliminate them. Then those unresolved risks can interact with other risks.

That final stage matters because modern corporate risk is increasingly interconnected. AI touches privacy, cyber, employment, intellectual property, and regulatory compliance. Third-party risk can implicate corruption, sanctions, human rights, cybersecurity, and financial controls. Compensation can affect culture, sales practices, fraud risk, and books and records. No single function can manage these issues effectively on its own.

The solution is not to eliminate functional ownership. Clear accountability remains essential. The solution is to build governance mechanisms that allow information to move, risks to be considered together, and significant issues to be escalated across organizational boundaries. For the CCO, that means becoming an effective connector while preserving the accountability of the business and other control functions.

For management, it means looking beyond individual risk categories. For the board, it means ensuring that committee structures and reporting processes provide an enterprise view rather than a collection of disconnected risk reports. The ultimate lesson from Frankenstein Meets the Wolf Man is therefore not really about either monster individually. It is about interaction. 

A company may understand its corruption risk. It may understand its third-party risk. It may understand its cybersecurity risk. It may understand its AI risk. It may have capable people managing each one. The question is whether anyone understands what happens when those risks meet. That is where compliance moves beyond individual rules and controls and becomes part of enterprise governance. 

After five films, the Frankenstein story leaves us with a useful framework for the modern compliance program: govern what you create, learn from what goes wrong, take responsibility for what you inherit, test whether remediation works, and understand where risks intersect. Because in business, as in the movies, managing one monster is difficult enough. The real governance challenge begins when monsters collide.

Check out the podcast version and analysis of this episode of Popcorn and Compliance with Timothy and Fiona.

Categories
Compliance Into the Weeds

Compliance into the Weeds: Anthropic’s Board Structure – What Does it Mean for Compliance

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into a compliance-related topic, literally going into the weeds to explore it fully. Looking for hard-hitting compliance insights? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss Anthropic’s S-1 registration statement for a forthcoming IPO, focusing on what it reveals about corporate governance and risk oversight rather than financials.

Kelly notes Anthropic has a seven-member board with three insiders (CEO Dario Amodei, Daniela Amodei, and CFO Christina Rao) and four outsiders, operating through four committees: audit, compensation, nominating/governance, and a safety and risk committee tasked with AI safety, security, and broader legal/regulatory/compliance risks. They question whether a two-member safety and risk committee, chaired by Novartis CEO Vas Narasimhan and joined by Christopher Liddell, has sufficient capacity, and note that the committee has an undisclosed written charter. They also flag uncertainties about Anthropic’s internal compliance/risk leadership and reporting filters, potential amended filings, and a five-member long-term benefit trust (one seat vacant) with influence over nominating outside directors.

Key highlights:

  • Anthropic IPO S-1 overview
  • Board size and committees
  • Risk committee staffing questions
  • CEOs talking about AI risks
  • More filings and disclosure gaps

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds, was recently named one of the Top 25 Regulatory Compliance Podcasts, Top 10 Business Law Podcasts, and Top 12 Risk Management Podcasts. Compliance into the Weeds has been awarded a Davey, Communicator, and W3 Award, all for podcast excellence.

Categories
Innovation in Compliance

Innovation in Compliance: The Salus Blueprint: Episode 1 – What Must Keep Working When Things Go Wrong?

What question might a leader face on a difficult morning? In this special podcast series, Marc Duncan, Bridget Lee-Young, and Scott Pickett of Salus Solutions share one useful idea for corporate professionals, including risk and compliance leaders and anti-bribery and corruption professionals, and show how it changes a decision. This podcast is also for police and fire chiefs, emergency managers, finance and operations executives, CEOs, boards, and leaders of commercial, public, and private organizations. In Episode 1, we take a deep dive into what matters most: mission-critical dependencies and Salus Solutions’ Preparedness Toolkit.

Key Highlights:

  1. “If I run an organization and tell you, ‘We have a risk register and an emergency plan,’ what would you ask first to learn whether I know what matters most?”
  2. “What does ‘protect the mission’ mean for a hospital support service, a school, and a commercial operator in everyday terms?”
  3. “Who must be in the first conversation besides the chief executive? What will the front-line operator know that the board may not?”
  4. “Where do dependencies such as communications contractors, utilities, responders, or key individuals enter that conversation?”
  5. “Can you explain SalINTEL, SalTHIRA, SalCAPA, and SalOPS without an acronym chart, using this one organization?”
  6. “What decisions remain with the client, and what work can Salus advise on or support?”
  7. “If a board has only ten minutes, what one question should it ask management to expose an assumption about continuity?”

Questions for Our Listeners: Write down one essential service and ask what people, systems, outside organizations, and decisions it depends on. “If a worker reported a failing dependency tonight, could your organization capture it and get it to someone who understands its significance before the service stops?” Next time, we examine how to collect what matters.

About Salus Solutions (https://salus.solutions): “Salus helps organizations understand what matters, make informed protective decisions, and carry them into action. SalCAPA is the method and coordination environment that connects those steps.”

Categories
Innovation in Compliance

Innovation in Compliance: Jeff Kushner on GRC Lessons from Kerrville 2025: Why a Policy Isn’t a Control

Innovation comes in many areas, and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he speaks with top innovators, thinkers, and creators on the award-winning Innovation in Compliance podcast. In this episode, host Tom interviews GRC professional Jeff Kushner about Fox’s book Deluge Before Dawn and its risk management lessons from the 2025 Kerr County flood that killed 119 people.

Kushner argues a policy is not a control: policies must be specific, operationalized, tested, monitored, and continuously improved, with clear roles, successor plans, training, and communication protocols. He contrasts document-centric assurance (having a written plan and passing inspections) with outcome-centric assurance (whether plans work in real conditions), citing Camp Mystic’s one-page “shelter in place” plan that passed a DSHS inspection two days before the flood. They discuss alerts as information that requires predetermined response sequences, the need for redundancies in communications, proactive scenario exercises (“what happens next?”), benchmarking against other sites like Mo Ranch, and board-level questions on impact, accountability, timelines, and measurable protections for life, property, and data. Kushner also describes his role at Allgress and its Rexina solution for identifying compliance and risk changes and guiding remediation.


Key Highlights:

  • Policy Versus Control
  • Alerts and Control Steps
  • Inspection Paradox
  • Outcome-Based Assurance
  • Scenario Testing Exercises
  • Rexina and Allgress
  • Board-Level Risk Questions

Resources:

Jeff Kushner on LinkedIn

Allgress

Allgress on LinkedIn

Allgress/Rixena

For a report Jeff Kushner created on the risk management issues we discussed in the podcast, click here.

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
Great Women in Compliance

Great Women in Compliance: The Paradox of Ethics & Compliance: Corporate Conscience or Façade?

Is your organization designed to hear the truth—or to explain it away?

Corporations have Enterprise Risk Management, established Ethics & Compliance Programs, Internal & External audits, risk assessments, multiple risk and compliance heat maps and dashboards, and boards charged with oversight.

So why do major corporate scandals keep happening?

What if the problem isn’t a lack of controls but the organizational structures that prevent those controls from making a difference?

In this episode of Great Women in Compliance, we speak with Astrid Yee-Sobraques, Risk Sherpa and author of The Structural Capture of Corporate Conscience, about the uncomfortable relationship between ethics, commercial pressure, corporate governance, and power.

We explored whether the Ethics & Compliance functions can identify risks but cannot meaningfully influence how the risk will be mitigated, and whether the Ethics & Compliance Program is effective—or simply a system for documenting concerns.

We asked:

  • Can a company with ethical people still be structurally designed to produce unethical outcomes?
  • When does legitimate business risk acceptance become a way to rationalize unacceptable conduct?
  • If Ethics & Compliance can identify the risk but cannot change the outcome, is that independence—or an illusion of it?
  • How can boards uncover the risks that management’s reporting and assumptions may obscure?

For Ethics & Compliance professionals, the discussion raises difficult questions about independence, professional responsibility, escalation, and the pressure to protect revenue-producing relationships.

For directors and board members, it challenges the assumption that more reporting and better dashboards do not necessarily translate into better oversight and decisions.

Categories
Blog

Frankenstein and Compliance: Part 1 – It’s Alive: Innovation Without Governance

Ed. Note: This month, on my podcast series Popcorn and Compliance, I am taking a deep dive into the first five Frankenstein movies. Over October, I will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolfman. The blog post is a companion to the podcast series.

The most famous moment in Frankenstein (1931) comes when Henry Frankenstein’s experiment succeeds. Electricity surges through his laboratory, the body on the table begins to move, and Frankenstein celebrates what he believes is an extraordinary scientific achievement.

“It’s alive!”

For the corporate compliance professional, however, the critical decisions occurred before Henry ever activated his equipment. He had decided to proceed without an adequate risk assessment, effective oversight, meaningful challenge, or a plan for managing the consequences if his experiment succeeded. Viewed through that lens, Frankenstein is not simply a horror movie about a scientist and the Monster he creates. It is a case study in innovation without governance.

That lesson is especially relevant as companies accelerate the adoption of AI and other emerging technologies. Businesses are appropriately focused on innovation, productivity, efficiency, growth, and competitive advantage. Yet technological capability can develop faster than the governance structures needed to manage the resulting risks. The compliance issue is not whether companies should innovate. They must. The issue is whether governance keeps pace with innovation.

The Business Case Was Clear. The Governance Case Was Not.

Henry Frankenstein has a compelling objective. He believes he can accomplish something no one has accomplished before. He assembles the equipment, obtains the materials, develops the technical capability, and builds a team capable of executing the project. In corporate terms, Henry has a strategy, resources, technical expertise, and executive sponsorship. He lacks an effective governance framework.

Before activating his creation, Henry conducts no meaningful risk assessment. He does not identify potential failure scenarios or establish control requirements. He does not define stopping criteria or determine who has authority to challenge the project. No meaningful contingency plan exists for an adverse outcome. This is precisely where compliance should enter the business process.

An effective compliance function should not first encounter a significant new technology when the business seeks approval immediately before deployment. Compliance needs to participate early enough to understand the business objective, identify the associated risks, and help determine appropriate controls.

That does not mean Compliance should own innovation or assume responsibility for the underlying business decision. Risk ownership should remain with the business. Compliance should help ensure that management understands the legal, regulatory, ethical, and control implications of the decision before significant commitments are made.

For the CCO, this raises a practical question: When does Compliance become involved in our company’s innovation process? If the answer is immediately before launch, the organization may already be too far downstream.

AI Has Made the Frankenstein Problem Immediate

Artificial intelligence makes the Frankenstein governance issue particularly relevant. Companies are deploying AI to analyze information, generate content, assist customer service, support investigations, screen candidates, evaluate transactions, enhance due diligence, identify suspicious activity, and improve decision-making. These applications can generate significant business value. They also raise governance questions that organizations must address before deployment.

Organizations need to understand what data an AI application uses, how it obtained that information, who approved the use case, and which regulatory requirements apply. They should determine how outputs are validated, where human review is required, how confidential information is protected, and what happens when a system produces an unexpected or inappropriate result.

There must also be clear accountability. Someone should own the business risk associated with the use case, and the organization should understand who has authority to suspend or terminate the application if circumstances warrant.

The NIST AI Risk Management Framework provides one useful approach through its Govern, Map, Measure, and Manage functions. ISO/IEC 42001 similarly treats AI through a management-system framework emphasizing governance, accountability, risk management, and continual improvement.

Both approaches reinforce a broader compliance principle: technology risk needs governance throughout the lifecycle. Henry Frankenstein has no lifecycle governance. His approach is essentially to build the system, activate it, and evaluate the consequences afterward. That is not an acceptable corporate control environment.

The Abnormal Brain and the Importance of Validating Inputs

One of the film’s most useful compliance scenes occurs before the Monster comes to life. Henry needs a brain for his creation. His assistant Fritz obtains one, but the intended specimen is destroyed. Rather than report what happened, Fritz substitutes another brain, identified in the film as abnormal, without telling Henry. (Abbey Normal—if you know, you know.) The project therefore proceeds after a critical input has changed without the project leader’s knowledge.

For compliance professionals, the scene provides a useful analogy for third-party risk, supply-chain controls, due diligence, and data governance. Organizations routinely rely on information others provide. A distributor provides beneficial ownership information. A vendor completes a compliance certification. An employee submits an expense report. An acquisition target makes representations during due diligence. A supplier certifies compliance with contractual obligations. An AI application relies upon data obtained from multiple sources.

The relevant control question is not simply whether the required information was received. It is whether the organization appropriately validated important information based on risk. Fritz completed his assignment in the narrowest sense. He returned with a brain. The process failed because nobody verified that he returned with the correct brain. That distinction is important for compliance program effectiveness. A completed checklist demonstrates that an activity occurred. Appropriate validation assures that the control achieved its purpose.

Dr. Waldman and Credible Challenge

Henry is not entirely without oversight. Dr. Waldman understands what Henry is attempting and recognizes the potential danger. He raises objections. Henry proceeds anyway. This takes the film from risk assessment into the effectiveness of the challenge function. Many companies can demonstrate that compliance participated in a significant decision. That does not necessarily establish that a compliance professional had meaningful influence over the outcome. A CCO can attend meetings, review proposals, identify concerns, and recommend additional controls. If commercial leadership can routinely disregard those concerns without escalation, the company may have consultation without credible challenge.

This is why the authority, stature, resources, independence, and access of the compliance function matter. The effectiveness of a corporate compliance program becomes most visible when it disagrees with an important business proposal. Boards should therefore look beyond whether your compliance function was consulted. They should understand what happens when a compliance officer disagrees with the business. They need to ask such questions as: Can the CCO escalate a significant concern? Does the CCO have appropriate access to the Audit Committee or board? Are material disagreements documented? Who has authority to accept significant compliance risk? Can commercial management override a compliance objection without further review?

If a CCO can raise a concern but nobody with decision-making authority has to address it, the organization has created the appearance of challenge without its substance. Dr. Waldman had a voice. He lacked the influence to change the decision.

Maria and the Risk of Unintended Consequences

Next we consider one of the most poignant scenes in the movie. The encounter between the Monster and young Maria provides another important business lesson. This is certainly one of the most unforgettable, and indeed tragic, scenes in all the Frankenstein movies. If you have ever seen it, you will never forget it. A small child, Maria, shows the Monster how flowers float on the lake. He imitates what he observes. When the flowers are gone, he throws Maria into the water, apparently expecting her to float as the flowers did. The consequences are tragic. The Monster recognizes a pattern without understanding its context.

That distinction has obvious relevance for artificial intelligence and automated decision-making. A system may identify patterns, generate recommendations, and produce technically consistent outputs without understanding their broader legal, ethical, or business implications. A technically accurate output can still create an inappropriate result.

This is why human oversight cannot exist merely as language in an AI policy. Companies need to determine where human judgment is required, who provides that judgment, what qualifications reviewers need, when automated recommendations can be overridden, and how significant exceptions are documented.

Management should also understand whether human review is substantive or simply procedural. An employee clicking an approval button after an automated recommendation does not necessarily constitute meaningful oversight. The relevant control question is not simply whether the technology performed as designed. It is whether the resulting decision was appropriate.

Innovation Requires Accountability

Henry eventually discovers that creating something and controlling it require different capabilities. Corporate leaders should understand the same distinction. Management establishes incentive structures, sales strategies, compensation plans, technology deployments, acquisition strategies, third-party relationships, and performance expectations. Those decisions shape employee behavior and create risk. Leadership accountability therefore does not begin only after misconduct occurs. It begins with the decisions that establish the operating environment.

For the CCO, this means integrating compliance risk into strategic business decisions. For management, it means risk ownership remains with the business. For the board, oversight should focus on whether management has reasonable systems to identify, manage, monitor, and escalate significant risks. Compliance does not own a business risk simply because the compliance function identifies it. Management remains responsible for the business decision and the risks it creates.

That principle becomes particularly important with emerging technology. The CCO should contribute expertise regarding regulatory requirements, ethical considerations, controls, monitoring, and escalation. Technology leaders should contribute technical expertise. Legal, Privacy, Information Security, HR, Internal Audit, and other functions may have roles depending on the application. Business leadership remains accountable for the decision to deploy the technology and the resulting business risk.

Practical Actions for the CCO

Frankenstein suggests a practical agenda for compliance leadership. Compliance should move upstream and identify significant business processes where its participation adds the most value before making commitments. Emerging technology, acquisitions, market entry, compensation design, significant third parties, and new products are obvious candidates.

Risk assessment should occur before deployment and should address foreseeable legal, compliance, ethical, operational, and reputational consequences. High-risk inputs supplied by employees, vendors, third parties, acquisition targets, or technology systems should receive risk-based validation.

The organization should also define what credible challenge means in practice. Escalation procedures should be clear when Compliance and business leadership disagree about significant risk.

Finally, treat approval as the beginning of governance rather than its conclusion. Test controls, monitor outcomes, analyze exceptions, and update risk assessments as the business and technology evolve. The objective is not to slow innovation. It is to make innovation governable.

The Compliance Lesson

Frankenstein is not an argument against innovation. It is an argument for governance.

Henry Frankenstein failed not because he attempted something extraordinary. He failed because his technical ambition outpaced his ability to identify, understand, govern, and control the resulting risk.

Companies face the same challenge today. Technology will advance. Business models will change. New markets will open. Competitive pressure will accelerate decision-making. New risks will emerge. Compliance’s role is not to stand outside the laboratory and demand that the electricity be turned off.

It is to help ensure that management has assessed the risk, validated critical inputs, established appropriate controls, defined accountability, created meaningful challenge, and determined how the organization will respond if the initiative produces an unexpected result. The best time to build that governance structure is before deployment.

Our next installment moves the compliance analysis forward. In Bride of Frankenstein, Henry no longer faces an unknown risk. He has already experienced the consequences of his original experiment and understands what can go wrong. Then Dr. Pretorius persuades him to return to the laboratory.

The compliance issue is no longer whether leadership identified the risk. It is what happens when leadership knows better, but pressure, ambition, and rationalization push the organization toward the same risk again.

Check out Timothy and Fiona’s commentary on Frankenstein here.

Categories
Trekking Through Compliance

Trekking Through Compliance: Episode 78 – Risk Management Insights from All Our Yesterdays

When you think of Star Trek: The Original Series, certain episodes stand out for their moral clarity, exploration of ethics, and leadership lessons. Others, like All Our Yesterdays, are more subtle but no less rich in compliance and risk management insights.

As the story unfolds, the episode reveals more than just a sci-fi adventure; it presents a compelling case study in the importance of preparation, situational awareness, adaptability, and decision-making under pressure. For the compliance professional, All Our Yesterdays offers five key risk management lessons that are as relevant in the boardroom as they are in a time-portal crisis.

Lesson 1: Understand the Operating Environment Before You Act

Illustrated by: Kirk, Spock, and McCoy don’t fully grasp that the Atavachron sends people into different periods, permanently altering them to survive there, until after they have stepped through the portals.

Compliance Lesson. One of the most preventable compliance failures happens when leaders act without fully understanding the operational landscape.

Lesson 2: Know the Long-Term Consequences of Your Decisions

Illustrated by: Atoz explains that once a traveler passes through the Atavachron, they undergo physiological changes to survive in the chosen period. Returning without those adaptations can be fatal.

Compliance Lesson. Compliance decisions, especially around risk tolerance, often have long-term and sometimes irreversible consequences. For example, approving a high-risk third party because “we need them for this deal” can embed systemic vulnerabilities that are difficult to unwind later.

Lesson 3: Adapt Your Strategy to Changing Conditions

Illustrated by: Spock, under the influence of the prehistoric era, begins to revert to the more emotional mindset of ancient Vulcans, displaying anger, impatience, and even affection for Zarabeth, a woman trapped in that time

Compliance Lesson. Risk environments are dynamic. Market conditions shift, laws change, counterparties evolve, and cultural contexts can reshape behavior, sometimes subtly, sometimes dramatically.

Lesson 4: Factor in Human Behavior When Assessing Risk

Illustrated by: Zarabeth tells Spock and McCoy they can never return to their own time, a claim that at first appears to be based on Atoz’s rules but is also shaped by her emotional motives.

Compliance Lesson. Risk management isn’t just about numbers, metrics, or legal frameworks—it’s about people, their incentives, and their biases.

Lesson 5: Time Is a Critical Risk Variable

Illustrated by: The central urgency in All Our Yesterdays comes from the imminent nova of Sarpeidon’s sun. For Kirk, Spock, and McCoy, the clock is ticking.

Compliance Lesson. In compliance risk management, timing is often the difference between proactive control and reactive crisis.

Final Compliance Reflections

All Our Yesterdays may be set in a science fiction universe, but its lessons are firmly grounded in the reality of corporate compliance. Every compliance officer will, at some point, face the equivalent of a ticking sun about to go nova, a high-stakes situation where incomplete information, shifting conditions, human bias, and the relentless march of time intersect.

Remember, you may not have an Atavachron in your compliance toolkit, but you can choose which “yesterday” you’ll prepare for today. The right risk management approach ensures that, when the heat is on, your organization isn’t scrambling for the exit portal, because it’s already where it needs to be.

Resources:

⁠⁠Excruciatingly Detailed Plot Summary by Eric W. Weisstein⁠⁠

⁠⁠MissionLogPodcast.com⁠⁠

⁠⁠Memory Alpha

Fiona is an AI-generated voice

Categories
Blog

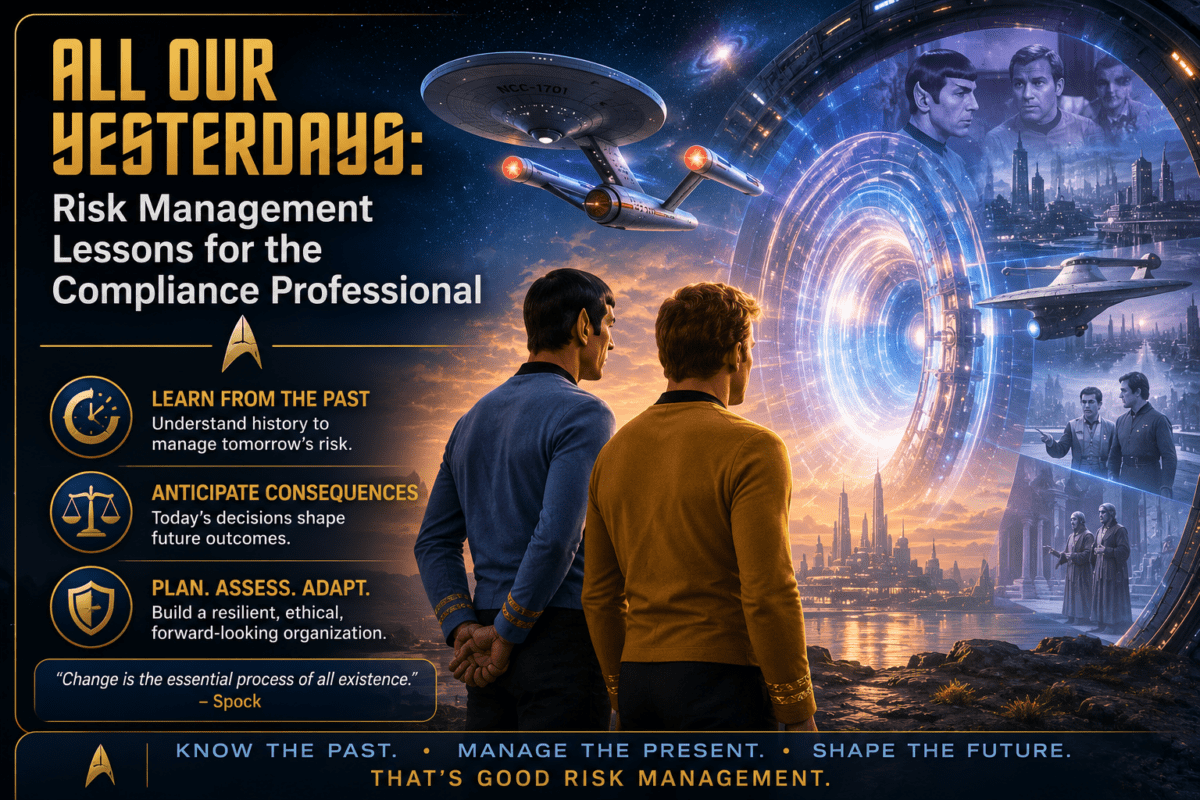
All Our Yesterdays: Risk Management Lessons for the Compliance Professional

When you think of Star Trek: The Original Series, certain episodes stand out for their moral clarity, exploration of ethics, and leadership lessons. Others, like All Our Yesterdays, are more subtle but no less rich in compliance and risk management insights.

In this episode, Captain Kirk, Mr. Spock, and Dr. McCoy beam down to the planet Sarpeidon just before its sun goes nova. They find the planet seemingly deserted except for a mysterious librarian named Mr. Atoz. He explains that the people have escaped into the planet’s past using a time travel device called the Atavachron. Unfortunately, in true Star Trek fashion, the landing party becomes separated: Kirk ends up in a duel-filled era resembling the late Middle Ages, and Spock and McCoy in a frozen prehistoric wilderness.

As the story unfolds, the episode reveals more than just a sci-fi adventure; it presents a compelling case study in the importance of preparation, situational awareness, adaptability, and decision-making under pressure. For the compliance professional, All Our Yesterdays offers five key risk management lessons that are as relevant in the boardroom as they are in a time-portal crisis.

Lesson 1: Understand the Operating Environment Before You Act

Illustrated by: When Kirk, Spock, and McCoy first arrive, they assume the library is a static place in the present day. They don’t fully grasp that the Atavachron sends people into different periods, permanently altering them to survive there, until after they have stepped through the portals.

Compliance Lesson. One of the most preventable compliance failures happens when leaders act without fully understanding the operational landscape. Just as Kirk should have gathered more intelligence before stepping through the portal, compliance officers must conduct thorough due diligence before making high-impact decisions, especially in new markets or with new business models.

Jumping into a jurisdiction with unfamiliar regulatory structures or cultural norms without advance research can leave your compliance program operating with blind spots. A robust risk assessment, stakeholder mapping, and regulatory scan are your “Atavachron briefing”; without them, you’re walking through the wrong portal unprepared.

Lesson 2: Know the Long-Term Consequences of Your Decisions

Illustrated by: Atoz explains that once a traveler passes through the Atavachron, they undergo physiological changes to survive in the chosen period. Returning without those adaptations can be fatal. This means each journey into the past is not just a visit—it’s a permanent commitment.

Compliance Lesson. Compliance decisions, especially around risk tolerance, often have long-term and sometimes irreversible consequences. For example, approving a high-risk third party because “we need them for this deal” can embed systemic vulnerabilities that are difficult to unwind later.

Spock and McCoy’s plight in the ice age reminds us that once certain paths are chosen, backing out may be impossible or costly. Before green-lighting any strategy or business partner, ask: What will the long-term compliance footprint be? Are we setting ourselves up for future exposure? Risk management is not just about the next quarter; it’s about the next decade.

Lesson 3: Adapt Your Strategy to Changing Conditions

Illustrated by Spock, under the influence of the prehistoric era, reverting to the more emotional mindset of ancient Vulcans, displaying anger, impatience, and even affection for Zarabeth, a woman trapped in that time. McCoy, ill from the cold, must rely on Spock’s shifting judgment to survive.

Compliance Lesson. Risk environments are dynamic. Market conditions shift, laws change, counterparties evolve, and cultural contexts can reshape behavior, sometimes subtly, sometimes dramatically. The compliance officer must watch for these shifts and recalibrate strategies accordingly.

Like Spock, even seasoned professionals can find themselves influenced by their environment in ways they don’t immediately recognize. Compliance teams need to build monitoring systems that not only track external risk factors but also assess how those factors may be affecting decision-makers internally. Adaptation is not a sign of weakness—it’s a core competency in sustainable risk management.

Lesson 4: Factor in Human Behavior When Assessing Risk

Illustrated by: Zarabeth tells Spock and McCoy they can never return to their own time, a claim that at first appears to be based on Atoz’s rules but is also shaped by her emotional motives. Her loneliness influences how she frames the “facts.”

Compliance Lesson. Risk management isn’t just about numbers, metrics, or legal frameworks—it’s about people, their incentives, and their biases. Vendors may hide problems to protect their contracts. Employees may omit details in self-reporting to avoid blame. Executives may downplay risk to push a deal through.

Zarabeth’s well-intentioned but self-serving misinformation underscores the need to verify claims independently. Compliance programs should collect and validate facts from multiple sources, reducing the risk of being swayed by the partial truths of a single stakeholder.

Lesson 5: Time Is a Critical Risk Variable

Illustrated by: The central urgency in All Our Yesterdays comes from the imminent nova of Sarpeidon’s sun. The people had to evacuate into the past before the moment of destruction; anyone left behind would perish. For Kirk, Spock, and McCoy, the clock is ticking.

Compliance Lesson. In compliance risk management, timing often separates proactive control from reactive crisis. Delaying a decision, such as suspending a suspicious transaction, escalating a whistleblower report, or halting engagement with a questionable vendor, can mean the difference between a manageable incident and a reputational disaster.

The episode reinforces the importance of early detection and swift action. Compliance teams should have rapid-response protocols, much like an evacuation plan, that can be activated the moment credible risk signals appear. The longer you wait, the narrower your options become.

Final Compliance Reflections

All Our Yesterdays may be set in a science fiction universe, but its lessons are firmly grounded in the reality of corporate compliance. Every compliance officer will, at some point, face the equivalent of a ticking sun about to go nova, a high-stakes situation where incomplete information, shifting conditions, human bias, and the relentless march of time intersect.

The episode reminds us that effective risk management is not simply about having a well-written policy. It’s about equipping yourself and your team to:

  • Anticipate the terrain.
  • Weigh long-term consequences before stepping through the “portal.”
  • Stay agile under environmental pressures.
  • Test assumptions and verify information.
  • Act decisively when the moment demands it.

In All Our Yesterdays, Kirk, Spock, and McCoy return to the present just in time, thanks to quick thinking, adaptability, and the ability to work within and around constraints. In the corporate compliance world, those same skills can mean the difference between a controlled risk event and a full-blown regulatory disaster.

Remember, you may not have an Atavachron in your compliance toolkit, but you can choose which “yesterday” you’ll prepare for today. The right risk management approach ensures that, when the heat is on, your organization isn’t scrambling for the exit portal because it’s already where it needs to be.

Resources:

⁠⁠Excruciatingly Detailed Plot Summary by Eric W. Weisstein⁠⁠

⁠⁠MissionLogPodcast.com⁠⁠

⁠⁠Memory Alpha