Categories
Blog

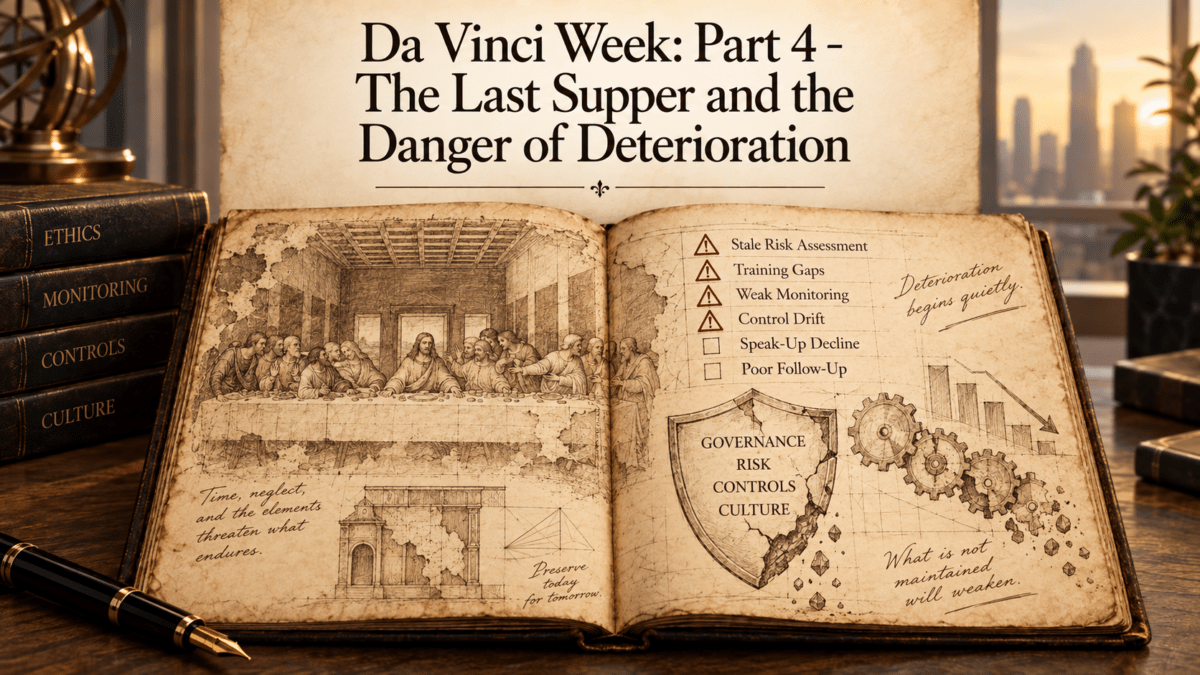
Da Vinci Week: Part 4 – The Last Supper and the Danger of Deterioration

In the previous post in the Leonardo Compliance Framework, Leonardo’s flying machines gave us Innovate, the principle that Compliance should help organizations capture the benefits of emerging technology while establishing governance appropriate to the risks. Yet approving and deploying a new technology, control, or compliance process does not demonstrate that it will remain effective over time. The organization must continue to evaluate whether the system operates as intended as the business and its risk environment change. That brings us to the fourth principle in the Leonardo Compliance Framework: Monitor.

For this lesson, we turn to Leonardo’s The Last Supper. Leonardo experimented with a painting technique that provided greater artistic flexibility than conventional fresco methods. The result was extraordinary, but the physical work proved vulnerable to deterioration, and environmental conditions and later damage compounded those problems.

For compliance professionals, the lesson is not that experimentation was a mistake. It is that implementation marks the beginning of the control lifecycle, not its end. A system that operates effectively when introduced may weaken as people, processes, technology, incentives, and business conditions change. Modern compliance program effectiveness therefore requires more than evidence that a control exists. Management needs evidence that the control continues to work.

Implementation Is Not Effectiveness

Companies appropriately recognize major implementation milestones. A new third-party platform goes live, an updated Code of Conduct is launched, an investigation protocol is approved, or a sanctions-screening system is installed. These accomplishments demonstrate that the organization has taken action, but they do not establish that the underlying risk is being managed effectively.

Consider a third-party due diligence system implemented across a global enterprise. At launch, the workflow operates as designed. Business sponsors submit required information, higher-risk third parties receive enhanced review, approvals are documented, and Compliance can monitor the process. Two years later, an acquisition may have added thousands of vendors, employees may have developed workarounds because they consider the process too slow, regional teams may interpret risk classifications differently, and data feeds may no longer operate consistently. The system still exists, and the policy remains in force, but the control environment has changed.

This is the central monitoring challenge. Controls operate inside dynamic organizations. A gifts and entertainment process may become inadequate when the company enters markets involving greater interaction with government officials. Sanctions controls may require adjustment following significant geopolitical developments. A conflict-of-interest process may become less effective after an acquisition substantially expands the workforce. Controls designed for one business model may no longer fit another.

Effective monitoring should therefore connect directly to risk assessment. When the company’s risk environment changes, management should evaluate whether the controls designed for the previous environment remain appropriate. Successful implementation at one point in time cannot establish continuing effectiveness.

Monitoring and Testing Provide Different Evidence

Compliance professionals should distinguish between monitoring and testing because each provides different information about the control environment. Monitoring is generally continuous or recurring. It observes transactions, trends, exceptions, employee behavior, third-party activity, hotline information, investigation patterns, and other indicators that may reveal changes in risk or control performance. Testing is more focused and determines whether a particular control is appropriately designed and operating as intended.

Consider a control requiring enhanced approval for high-risk third parties. Monitoring may reveal how many high-risk relationships are approved, how long reviews take, which business units generate the most exceptions, and whether particular patterns are developing. Testing may examine a sample of approved relationships to determine whether required due diligence was performed, red flags were resolved appropriately, approvals occurred at the correct level, and documentation supports the final decision.

Monitoring provides signals about what may be changing. Testing provides evidence about whether specific controls perform as expected. Together, they allow the CCO to move beyond control existence and assess effectiveness.

That distinction matters most when presenting compliance information to senior management and the board. Activity metrics may demonstrate that processes are operating, but control testing provides a stronger basis for determining whether those processes are managing the intended risk.

Ownership Turns Monitoring Into Accountability

Monitoring becomes considerably less effective when control ownership is unclear. This is a recurring compliance problem because responsibilities often cross functional boundaries. Compliance may own the policy, Procurement may operate the process, IT may own the technology, Finance may process the payment, and the business may own the commercial relationship. When the control fails, each function may reasonably believe another function was responsible.

Effective control design should therefore identify an accountable owner responsible for ensuring that the control operates as intended. Compliance may provide oversight and challenge, and Internal Audit may provide independent assurance, but first-line functions should understand their responsibility for managing the underlying business risk.

Ownership should extend to the results of monitoring and testing. If testing identifies repeated exceptions, someone must determine whether the process requires modification. If a data feed fails, someone must restore it. If employees routinely circumvent a control, management must address the underlying behavior or process weakness. Monitoring without ownership produces information without accountability. The objective is not simply to identify control deficiencies but to drive a management response.

Use Data to Identify Deterioration Earlier

Data analytics has significantly expanded compliance functions’ ability to identify changes in risk and control performance. Traditional monitoring often depended on periodic reviews of relatively small samples. Modern analytics can help organizations identify patterns across larger populations and, in some circumstances, detect changes earlier.

Payment data may reveal unusual transaction patterns, while procurement information can identify repeated overrides or vendor concentrations. Third-party data may identify expired due diligence or changes in risk characteristics. Hotline and investigation data can reveal shifts in allegations and recurring root causes, while HR information may signal retaliation or cultural issues.

The objective is not to collect the greatest possible volume of information or create the most sophisticated dashboard. The purpose is to identify data that help management determine whether risks are changing or controls are weakening. Exceptions are particularly valuable in this respect. An individual exception is not necessarily evidence of misconduct because legitimate business circumstances may justify deviation from a standard process. Patterns of exceptions, however, can reveal important information about the control environment.

If one business unit generates substantially more third-party exceptions than comparable operations, Compliance should understand the reason. Repeated overrides near quarter-end may indicate commercial pressure. Due diligence consistently completed after engagement may indicate that the formal process no longer reflects how the business actually operates.

A mature program should therefore examine the frequency, rationale, approving authority, concentration, and recurrence of significant exceptions. When exceptions become routine, they can create an unofficial alternative process that exists alongside the formal control environment. Data become valuable when they reveal that divergence early enough for management to respond.

Investigations, Monitoring, and Remediation Should Form a Feedback Loop

Investigations provide some of the strongest evidence about how controls operate under actual business conditions. Their findings should therefore influence what a compliance program monitors. If an investigation discovers that employees circumvented third-party controls by classifying consultants as ordinary vendors, remediation should address the immediate classification weakness, while monitoring should examine whether comparable patterns exist elsewhere. If an investigation identifies improper discounts used to create funds for inappropriate payments, transaction monitoring can be adjusted to identify similar discount patterns. If a retaliation investigation reveals adverse employment consequences shortly after an employee raised a concern, a compliance professional could consider whether HR data can identify comparable patterns.

This creates a feedback loop. Investigations explain how a control failed in a particular case, monitoring helps determine whether the same weakness exists elsewhere or is recurring, and remediation addresses the underlying problem. Monitoring has limited value if the organization does not act on what it learns. When testing identifies a significant deficiency, management should understand why it occurred, whether it is systemic, what risk it creates, what corrective action is required, and who owns that remediation. The organization should then validate that the corrective action addressed the weakness.

This last step is important because remediation completion and remediation effectiveness are different concepts. Issuing a revised procedure or completing additional training may satisfy a project milestone without solving the underlying problem. Follow-up testing provides evidence that the remediation worked.

The compliance learning cycle should therefore move from investigation to monitoring, from monitoring to remediation, and from remediation to validation.

AI Requires Continuing Monitoring

AI provides a particularly clear example of why approval and implementation cannot end the governance process. A company may conduct extensive review before deploying an AI application by assessing the vendor, testing the system, evaluating data use, classifying risk, and establishing human oversight. Those steps are important, but the system and its operating environment can change after deployment.

Vendors may update models, employees may develop new uses, data may change, integrations may expand access, and capabilities may increase. For higher-risk applications, monitoring should therefore match the potential consequences. It may include performance testing, incident monitoring, reviewing material overrides, validating outputs, and reassessing after significant changes in functionality or use.

Agentic systems deserve particular attention because monitoring may need to address not only output quality but also the actions a system performs, the permissions it exercises, and whether it remains within its approved authority. The broader principle is the same as for any other compliance control. Governance should continue for as long as the organization relies upon the system.

Culture Also Requires Monitoring

Corporate culture presents a different monitoring challenge because no single metric establishes whether an organization has a strong ethical culture. Hotline reporting rates provide useful information but require interpretation. High reporting may indicate significant problems or employee confidence in the reporting system. Low reporting may reflect a healthy environment or fear of speaking up. Employee surveys provide additional information but capture sentiment at a particular moment, while investigation data reflect only matters that become known.

Compliance should therefore build a broader picture using multiple indicators, including reporting trends, employee surveys, exit interviews, focus groups, disciplinary information, HR data, investigation findings, and management assessments. Changes across these indicators may reveal emerging issues in particular business units, management teams, or employee populations.

Culture monitoring is especially important after leadership changes, acquisitions, restructurings, layoffs, or significant incentive changes because these events can quickly alter employee perceptions and behavior. Formal policies may remain unchanged while the operating culture deteriorates. As with other compliance risks, the objective is not perfect measurement. It is obtaining enough reliable information to identify material changes and respond appropriately.

The Danger of Deterioration

The Last Supper reminds us that implementation captures a moment in time while organizations continue to evolve. Personnel, technology, incentives, business models, markets, and risks change, and controls that once worked can weaken in response. An effective compliance program therefore needs monitoring, testing, clear ownership, useful data, and validated remediation. These disciplines allow the organization to identify deterioration before a control weakness becomes a larger compliance failure.

The practical lesson for the CCO is that implementation should never be confused with effectiveness. Monitoring and testing should provide different but complementary evidence about control performance. Ownership should ensure findings produce action, analytics should identify meaningful changes rather than simply populate dashboards, and remediation should be validated before the organization concludes the underlying problem is solved. That is Monitor, the fourth principle of the Leonardo Compliance Framework. A control deserves continuing confidence only when the organization has continuing evidence that it works.

From Monitoring to Documentation

Monitoring tells the organization what is happening, but institutional learning depends upon preserving what the organization learns. A company may conduct an effective investigation, identify a root cause, redesign a control, test the remediation, and reach a thoughtful risk decision. Yet, much of that value can disappear if the reasoning exists only in the memories of the people involved.

That brings us to the fifth and final Leonardo principle: Document. In Blog Post Five, Leonardo’s Notebooks: Documentation the Defensible Compliance Program, we will use Leonardo’s extraordinary record of observations, drawings, experiments, and ideas to examine documentation as a governance discipline. The discussion will focus on preserving significant compliance reasoning, establishing accountability, creating institutional memory, documenting remediation and AI governance decisions, and ensuring that what the organization learns today remains available to the people responsible for managing its risks tomorrow.
Categories
Blog

Connected Compliance: Part 1 – Communication as the Operating System of Compliance

An effective compliance program is not a collection of disconnected policies, training modules, hotline reports, and investigation files. It is an operating system. Culture determines whether employees will use it. Risk assessment tells the organization where it must adapt. Investigations test whether the system responds credibly. Whistleblower programs reveal whether employees trust it enough to speak. Over this four-part blog post series, we will examine those connections, beginning with the discipline that makes every other element work: communication.

Compliance professionals often describe communication as one element of a program. That description is too narrow. Communication is the operating system through which employees learn expectations, seek advice, identify risk, report concerns, and judge whether management means what it says. If that system is slow, generic, inaccessible, or untrusted, even well-designed controls can fail in practice.

This matters because a compliance program does not become effective when a policy is published or training is completed. It becomes effective when an employee facing pressure knows what to do, understands where to go, and believes that asking for help will not create a career problem. Communication is therefore not simply messaging. It is a preventive control, a detection mechanism, and a source of management information.

Communication Is a Control, Not a Campaign

Many organizations still approach compliance communication as a calendar exercise. They send a Code of Conduct message, deliver annual training, publish a hotline reminder, and count distribution. Those activities may be necessary, but they do not establish whether the message reached the employee at the moment of risk.

An effective communication control has four characteristics.

  1. It is accessible, so employees can find guidance without having to navigate a maze.
  2. It is relevant, so examples reflect the decisions employees actually face.
  3. It is interactive so that employees can ask questions and test judgment.
  4. It is responsive, so the organization uses employee feedback to improve policies, training, and controls.

These distinctions are important. A campaign pushes information out. A control creates a reliable exchange of information. That exchange gives compliance an early view of confusion, pressure, process weakness, and emerging misconduct. It also gives employees a practical path to lawful and ethical decisions.

What the DOJ Is Really Asking

The Department of Justice has moved the compliance discussion away from paper design and toward operational effectiveness. The three fundamental questions in the 2024 Evaluation of Corporate Compliance Programs (ECCP) examine the program’s design, empowerment, and whether it works in practice.

For culture, the DOJ asks, “Does the company seek input from all levels of employees?” It then asks, “What steps has the company taken in response to its measurement of the compliance culture?” Those questions place two obligations on compliance. First, the company must listen across levels, functions, and locations. Second, it must demonstrate that listening changed something. Data without response is observation, not effectiveness.

The ECCP also directs prosecutors to examine policy accessibility, training effectiveness, the availability of guidance, and whether employees know when to seek advice. Taken together, these questions make communication evidence. A company should be able to show not only what it said but also who could access it, whether employees understood it, how they used it, and what management learned from it.

Build Channels Around Employee Behavior

Employees do not experience the company through a single channel. They communicate through managers, messaging platforms, internal websites, employee groups, town halls, mobile devices, and informal workplace networks. A compliance program that relies on one formal channel will miss important signals.

The practical response is a channel portfolio. Policies should be searchable and written in language employees can use. Guidance should be available through live compliance contacts and appropriate digital tools. Reporting options should include the hotline, web intake, direct contact with compliance or human resources, and management escalation. Communications should reach operational employees who may not sit at a computer, as well as global employees who may face language or cultural barriers.

Compliance also needs to listen where employees are already speaking. That may include internal collaboration channels, employee surveys, focus groups, office visits, and patterns in questions received by the compliance team. Any monitoring must be consistent with law, privacy expectations, company policy, and records-management requirements. The goal is not surveillance. The goal is to understand the employee experience before a cultural weakness becomes a control failure.

Face-to-face contact remains especially valuable. A visit to a business unit can reveal whether employees understand a policy, whether managers create pressure, and whether the local process matches the written procedure. It also changes how employees see compliance. A familiar adviser is easier to contact than a distant function that appears only during training or an investigation.

Replace Training Completion With Decision Readiness

Completion rates answer whether an employee opened a course. They do not answer whether the employee can recognize a conflict, challenge a questionable payment, escalate an export-control concern, or pause the use of an unapproved AI tool. As Hui Chen continually reminds us, it is about results, not inputs.

Training should therefore be built around decision readiness. Scenario-based sessions allow employees to work through realistic gray areas and explain why one course of action is safer than another. Shorter, targeted modules can address risk by role. Experienced employees may be able to demonstrate proficiency through testing, while supervisors may require additional training because they receive concerns and translate policy into daily conduct.

Relevance is a control feature. Employees are more likely to retain training that reflects their workplace, business model, and actual risk. A procurement team needs different scenarios from a sales team. A manager needs to understand retaliation and escalation. An engineer needs clear boundaries around data, cybersecurity, and AI. Localization must also address more than translation. Examples, delivery methods, and escalation paths should make sense in the local operating environment. The measurement should move beyond completion. Useful indicators include questions asked after training, repeat areas of confusion, scenario performance, requests for advice, policy-page use, control exceptions, and whether similar misconduct declines over time.

Make Leadership Visible and Consistent

Tone at the top loses force when it sounds scripted or appears only once a year. Employees judge leadership commitment through repeated choices: which risks receive attention, whether high performers are disciplined, whether managers welcome questions, and whether business pressure routinely overrides control requirements.

Compliance communication is stronger when leaders explain expectations in their own voices and connect them to business responsibilities. The chief executive can frame integrity as part of strategy. Finance can address books and records. Human resources can speak to respect, retaliation, and accountability. Business leaders can explain why escalation protects customers and sustainable growth.

Middle management is equally important. Most employees experience culture through their direct supervisor. Managers should be trained to receive concerns, avoid promises they cannot keep, protect confidentiality, escalate promptly, and prevent retaliation. If employees hear an ethical message from senior leadership but experience dismissal from a supervisor, the local message will win. Consistency completes the control. The organization must apply standards across rank, geography, and commercial importance. Unequal treatment communicates more powerfully than any policy statement.

Use Data Without Losing the Human Signal

Technology can help compliance measure reach and engagement. Policy-page analytics can show whether employees use key resources. Digital guidance tools can identify common questions. Investigation and reporting data can reveal trends by issue, region, or function. Training results can show where judgment remains weak.

These data points should be treated as signals, not verdicts. High question volume may indicate confusion, but it may also show that employees trust compliance. An increase in reports may reflect more misconduct, a successful awareness campaign, or greater confidence in the reporting process. Low reporting may indicate a healthy environment, or it may be a warning that employees believe speaking up is futile.

The best analysis combines quantitative and qualitative evidence. Compliance should compare usage data with employee interviews, survey responses, investigation themes, audit findings, exit information, and observations from business partners. It should protect privacy, limit access, and avoid metrics that encourage the wrong behavior. A target that simply seeks fewer reports can suppress the very information the company needs.

Convert Listening Into Action

The strongest evidence of culture is not the survey itself. It is what the company does next. If employees cannot find a policy, redesign access. If repeated questions reveal ambiguity, rewrite the guidance. If a region reports little despite known risk, test for fear or channel barriers. If investigations identify manager misconduct, adjust training, incentives, supervision, and discipline.

This requires a closed-loop process. Gather information. Analyze it for themes and root causes. Assign ownership for action. Document the decision. Communicate appropriate changes. Then measure whether the change worked. That process turns communication into continuous improvement and creates a defensible record of program evolution.

It also connects this first installment to the rest of the series. Employee questions and reporting patterns are early risk indicators. Investigation quality tells employees whether the company acts on what it hears. Whistleblower-program credibility determines whether critical information enters the system at all. Each element depends on the others.

From Culture to a Shifting Risk Environment

Communication gives compliance something more valuable than reach. It provides intelligence. Questions about a new market, an AI application, a third party, a customer demand, or a supply-chain disruption may be the first evidence that the risk environment has changed.

Join us tomorrow for our next installment, where we will examine how compliance can convert those signals into dynamic risk assessment, clear ownership, and adaptive controls. A shifting risk environment cannot be managed by an annual exercise alone. It requires the listening discipline established here.

Bonus Questions for Compliance Professionals

  1. Can employees find practical guidance at the moment they face a risky decision?
  2. Which groups, locations, or shifts are least engaged with compliance resources, and why?
  3. What evidence shows that employee feedback has changed the program?
  4. Are managers prepared to receive concerns, escalate them, protect confidentiality, and prevent retaliation?
  5. Do current metrics reward learning and trust, or do they unintentionally reward silence?
  6. What recent employee question should be treated as an emerging-risk signal?
Categories
31 Days to More Effective Compliance Programs

31 Days to a More Effective Compliance Program: Day 12 – The Importance and Construction of a Corporate Code of Conduct

Welcome to 31 Days to a More Effective Compliance Program. Over this 31-day series in January 2026, Tom Fox will post a key component of a best-practice compliance program each day. By the end of January, you will have enough information to create, design, or enhance a compliance program. Each podcast will be short, at 6-8 minutes, with three key takeaways that you can implement at little or no cost to help update your compliance program. I hope you will join each day in January for this exploration of best practices in compliance. This Day 12 episode explores the critical value and construction of a corporate Code of Conduct, explaining its evolution from a legalistic document to a cornerstone of compliance programs.

Key highlights:

  • Introduction to Code of Conduct
  • Regulatory Expectations and Guidelines
  • Crafting an Effective Code of Conduct

Resources:

Listeners to this podcast can receive a 20% discount on The Compliance Handbook, 6th edition, by clicking here.

Categories
Compliance Into the Weeds

Compliance into the Weeds: Checking in on Codes of Conduct

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into a compliance-related topic, literally going into the weeds to explore a subject more fully. Looking for some hard-hitting insights on compliance? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly review a recent report from LRN on the state of Codes of Conduct.

This episode explores the multifaceted use of a corporate code of conduct, discussing its role as both a defensive and offensive tool. Tom and Matt emphasize the importance of managers talking about the code and view it as a substantive part of senior management’s dialogue on corporate culture. The conversation underscores the code’s utility in various contexts and advocates for its broader adoption within the organization.

Key highlights:

  • Code as a Tool
  • The Role of Managers in Code Discussion
  • Senior Managers and Corporate Culture
  • Versatility of the Code

Resources:

Matt on Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds was most recently honored as one of the Top 25 Regulatory Compliance Podcasts, a Top 10 Business Law Podcast, and a Top 12 Risk Management Podcast. Compliance into the Weeds has been conferred the Davey, Communicator, and W3 Awards for podcast excellence.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Code of Conduct as an Internal Control

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our goal is to provide you with bite-sized, actionable tips to help you stay ahead in your compliance efforts. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

How does your Code of Conduct act as an internal control?

For more information on this topic, refer to The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, 6th edition, recently released by LexisNexis. It is available here.

Categories
31 Days to More Effective Compliance Programs

31 Days to a More Effective Compliance Program: Day 12 – The Importance and Construction of a Corporate Code of Conduct

Welcome to a special podcast series on the Compliance Podcast Network, 31 Days to a More Effective Compliance Program. Over these 31 days of the series in January 2025, Tom Fox will post a key part of a best practices compliance program daily. By the end of January, you will have enough information to create, design, or enhance a compliance program. Each podcast will be short, at 6-8 minutes, and will include three key takeaways you can implement at little or no cost to help update your compliance program. I hope you will join us each day in January for this exploration of best practices in compliance.

This episode explores the critical value and construction of a corporate Code of Conduct, explaining its evolution from a legalistic document to a cornerstone of compliance programs. The discussion includes an analysis of the 2016 SEC Enforcement Action against United Airlines, highlighting how violations of the Code of Conduct can lead to severe consequences, including substantial penalties and executive resignations. Key takeaways emphasize that a Code of Conduct should be tailored to a company’s specific culture and industry, must be accessible to all employees, and needs to be regularly updated and documented to ensure its effectiveness. Tune in to learn why a robust Code of Conduct is foundational for any compliance program.

Key highlights:

  • Introduction to Code of Conduct
  • Regulatory Expectations and Guidelines
  • Crafting an Effective Code of Conduct

Resources:

Listeners to this podcast can receive a 20% discount on The Compliance Handbook, 5th edition, by clicking here.

Categories
31 Days to More Effective Compliance Programs

31 Days to a More Effective Compliance Program: Day 12 – Your Code of Conduct

What is the value of having a Code of Conduct? In its early days, a Code of Conduct tended to be lawyer-written and lawyer-driven to wave in a regulator’s face during an enforcement action as proof of ethical overall behavior. Is such a legalistic code effective? Is a Code of Conduct more than simply your company’s internal law? What should be the goal of the creation of your company’s Code of Conduct?

How important is the Code of Conduct? Consider the 2016 SEC enforcement action involving United Airlines, Inc., which turned on a violation of the company’s Code of Conduct. The breach of the Code of Conduct was determined to be an FCPA internal control violation. It involved a clear quid pro quo benefit paid out by United to David Samson, the former Chairman of the Board of Directors of the Port Authority of New York and New Jersey, the public government entity that has authority over, among other things, United’s operations at the company’s huge east coast hub in Newark, NJ.

Three key takeaways:

1. A Code of Conduct is a foundational document in any compliance regime.

2. The substance of your Code of Conduct should be tailored to the company’s culture, to its industry, and to its corporate identity.

3. “Document, Document, and Document” your training and communication efforts regarding your Code of Conduct.

Categories
Blog

Your Code of Conduct

What is the value of having a Code of Conduct? In its early days, a Code of Conduct tended to be lawyer-written and lawyer-driven to wave in regulator’s face during an enforcement action as proof of ethical overall behavior. Is such a legalistic code effective? Is a Code of Conduct more than simply your company’s internal law? What should be the goal in the creation of your company’s Code of Conduct?

How important is the Code of Conduct? Consider the 2016 SEC enforcement action involving United Airlines, Inc., which turned on violation of the company’s Code of Conduct. The breach of the Code of Conduct was determined to be a FCPA internal controls violation. It involved a clear quid pro quo benefit paid out by United to David Samson, the former Chairman of the Board of Directors of the Port Authority of New York and New Jersey, the public government entity which has authority over, among other things, United’s operations at the company’s huge east coast hub at Newark, NJ.

The actions of United’s former CEO, Jeff Smisek, in personally approving the benefit granted to favor Samson violated the company’s internal controls around gifts to government officials by failing to not only follow the United Code of Conduct but also violating it. The $2.4 million civil penalty levied on United was in addition to its 2016 Non-Prosecution Agreement (NPA) settlement with the DOJ, which resulted in a penalty of $2.25 million. The scandal also cost the resignation of Smisek and two high-level executives from United.

In the 2020 FCPA Resource Guide, 2nd edition, the DOJ and SEC stated:

A company’s Code of Conduct is often the foundation upon which an effective compliance program is built. As DOJ has repeatedly noted the most effective codes are clear, concise, and accessible to all employees and to those conducting business on the company’s behalf.

The 2023 ECCP specified “As a threshold matter, prosecutors should examine whether the company has a code of conduct that sets forth, among other things, the company’s commitment to full compliance with relevant Federal laws that is accessible and applicable to all company employees.” The Antitrust Guidance also specified “If the company has a Code of Conduct, are antitrust policies and principles included in the document?”

The 2020 FCPA Resource Guide, 2nd edition, the 2023 ECCP and Antitrust Guidance go on to make it clear that it is difficult to effectively implement a compliance program if it was not available in the local language so that employees in foreign subsidiaries can access and understand it. When assessing a compliance program, DOJ and SEC will review whether the company has taken steps to make certain that the Code of Conduct remains current and effective and whether a company has periodically reviewed and updated its code.

There are several purposes which should be communicated in your Code of Conduct. The overriding goal is for all employees to follow what is required of them under the Code of Conduct. You can do this by communicating those requirements, to providing a process for proper decision-making and then requiring that all persons subject to the Code of Conduct put these standards into everyday business practice. Such actions are some of your best evidence that your company upholds and supports proper compliance.

The substance of your Code of Conduct should be tailored to your company’s culture, and to its industry and corporate identity. It should provide a mechanism by which employees who are trying to do the right thing in the compliance and business ethics arena can do so. The Code of Conduct can be used as a basis for employee review and evaluation. It should certainly be invoked if there is a violation. Your company’s disciplinary procedures must be stated in the Code. These would include all forms of disciplines, up to and including dismissal, for serious violations of the Code. Further, your company’s Code should emphasize it will comply with all applicable laws and regulations, wherever it does business. The code needs to be written in plain English and translated into other languages as necessary so that all applicable persons can understand it.

The three most important things about your compliance program are “Document, Document, and Document.” The same is true in communicating your company’s Code of Conduct. You need to do more than simply put it on your website and tell folks it is there, available and that they should read it. You need to document that all employees, or anyone else that your Code of Conduct is applicable to, has received, read, and understands it. The DOJ expects each company to begin its compliance program with a very publicly announced, very robust Code of Conduct. If your company does not have one, you need to implement one forthwith.

However, your Code of Conduct is not a static document to be put on a shelf and never reviewed again. For just as your compliance program is a living entity; it should be constantly evolving, the same is true for your Code of Conduct. If your company has not reviewed or assessed your Code of Conduct for five years, do so in short order, as much has changed in the compliance world. Some of the questions you should begin with include:

• When was the last time your Code of Conduct was revised?

• Have there been changes to your company’s business model since the last revision to the Code of Conduct?

• Have there been changes to relevant laws relating to a topic covered in your company’s Code of Conduct?

• Are any provisions of the Code of Conduct outdated?

• What is the budget to revise your Code of Conduct?

After revision of your Code of Conduct, you should develop a plan to communicate the revised document. A rollout is always critical because it is important that revisions are communicated in a manner that encourages employees to review and use the Code of Conduct on an ongoing basis. Your company should use the full panoply of tools available to it to publicize the revised Code of Conduct. This can include a multi-media approach or physically handing out a copy to all employees at a designated time. You might consider having a company-wide compliance Code of Conduct roll out meeting where the revised Code is announced with great fanfare out across the company all in one day. Also remember, with all things compliance; the three most important aspects are “Document, Document, and Document”. However, for each delivery of revised Code of Conduct, you must document that each employee received it.

These points are a useful guide to not only thinking through how to determine if your Code of Conduct need updating, but also practical steps on how to tackle the problem. It is far better to review and update your Code of Conduct, than wait for a massive FCPA investigation to go through the process.

Categories
FCPA Compliance Report

FCPA Compliance Report – Jim Walton on LRN’s 2023 Code of Conduct Report

Welcome to the award-winning FCPA Compliance Report, the longest-running podcast in compliance. In this episode, Tom Fox welcomes Jim Walton to discuss LRN’s always great annual Code of Conduct Report.

Jim Walton is a well-known compliance professional with a background in engineering and a passion for assessing and improving corporate codes of conduct effectiveness. His perspective on this topic is shaped by his extensive experience, including his current role as a Director on LRN’s Advisory Services team, where he leads their code of conduct practice. Jim believes a company’s code of conduct should reflect its character, culture, and values, serving as a foundation for its ethical culture. He emphasizes the importance of the code being a useful resource for employees, providing guidance on ethical decision-making and access to detailed information and resources. Jim also acknowledges that there is always room for improvement in corporate codes of conduct, even among some of the largest companies in the world. Join Tom Fox and Jim Walton on this FCPA Compliance Report podcast episode to dive deeply into Codes of Conduct.

Key Highlights:

  • Evaluating the Effectiveness of Company Codes of Conduct
  • Codes of Conduct Evaluation and Best Practices
  • Comprehensive and User-Friendly Code of Conduct
  • Eight Dimensions for an Effective Code of Conduct

Resources:

Jim Walton on LinkedIn

LRN

LRN 2023 Code of Conduct Report

Tom Fox

Thread

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
31 Days to More Effective Compliance Programs

One Month to More Effective Written Standards: Day 6 – Operationalization of your Code of Conduct

How can you work to operationalize your Code of Conduct as articulated in the DOJ 2023 Evaluation of Corporate Compliance Programs (ECCP)? The 2023 ECCP focuses not on whether a company has a paper compliance program but whether a company is actually doing compliance. A company does compliance by moving it into the functional business units as a part of an overall business process. That is what makes a compliance program effective at the business level. There are several different parts of the 2023 ECCP that touch upon your Code of Conduct.
The Code of Conduct design and implementation process enshrine your company’s values. Those are set by senior management and their input and support for any code project, whether initial draft or update, is critical. This gets to the heart of operationalization and demonstrates how a Code of Conduct can work to meet the DOJ requirements. As an early part of your design and drafting process, you should assemble a cross-functional team. This is important for several reasons. First, diversity in your team will help produce a more well-rounded final product. But having such team diversity will also assist in your benchmarking effort, coupled with those who are going to help you out looking at designs and maybe helping forge the design of the code. Finally, you can use a group to help in the drafting, redrafting and editing process. This diversity will help you to answer all of the DOJ questions from the 2019 Guidance in a manner consistent to support operationalization.
All of these requirements point to getting out and making your Code of Conduct a part of the very fabric of your organization. By using some or all of these strategies, you will have a good starting point. But it is more than simply rollout and training. There must be ongoing communications as well.

Three key takeaways:

  1. What has been the role of senior management in the creation or update of your Code of Conduct?
  2. How have you worked with employees outside the compliance function to lay the groundwork for fully operationalizing your Code of Conduct?
  3. How have you measured the effectiveness of your Code of Conduct training?

For more information, check out The Compliance Handbook, 4th edition, here.