Categories
Blog

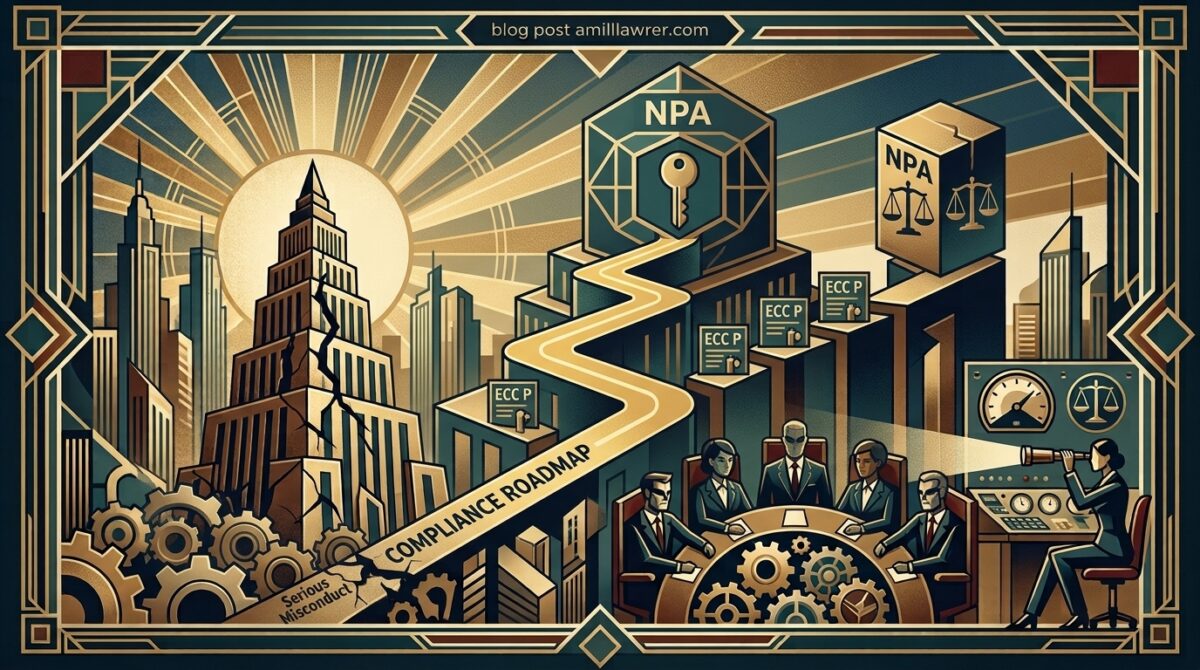
Southern Glazer’s Compliance Roadmap: How the ECCP Helped Turn Serious Misconduct into an NPA

For years, compliance professionals have turned to the Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) to answer a fundamental question: What does an effective compliance program actually look like? Unfortunately, given statements from the early Trump Administration, many compliance professionals feared the Administration would withdraw or otherwise eviscerate the ECCP.

Southern Glazer’s resolution gives us one of the clearest answers in recent memory. The answer is a resounding no: the ECCP is alive and well, even under this DOJ.

Southern Glazer’s entered into a two-year Non-Prosecution Agreement (NPA) with the U.S. Attorney’s Office for the Northern District of California and agreed to pay $12.5 million to resolve a federal criminal investigation involving improper payments, gifts, travel, gift cards, and other benefits. Some of those benefits were facilitated through third-party vendors and concealed through false invoices.

The underlying conduct was serious. Five former Southern Glazer’s employees were indicted in March 2026 for an alleged conspiracy involving commercial bribery and obstruction. Prosecutors alleged that approved vendors and suppliers were used to disguise payments for prepaid gift cards, luxury items, and other benefits through false invoices. Yet Southern Glazer’s itself received an NPA.

For compliance professionals, the most important part of this resolution may be why. The government expressly credited Southern Glazer’s with making significant enhancements to its compliance program beginning in 2023 and, remarkably, specifically noted that the company had aligned those improvements with the factors contained in the ECCP. That makes Southern Glazer’s much more than another bribery enforcement action. It provides a roadmap for remediation.

The ECCP Is Not Sitting on the Shelf

There has been plenty of discussion about what role the ECCP would play in the current enforcement environment. Southern Glazer’s provides a concrete answer. DOJ didn’t merely mention that the company improved compliance. The NPA expressly credited Southern Glazer’s for its “significant efforts to enhance its Compliance Program” and to align that program with DOJ’s evaluation guidance.

That is important. The ECCP should not be treated as an academic document or something pulled from the shelf only after the government arrives. It is a blueprint for building, assessing, and improving a compliance program. Southern Glazer’s demonstrates the potential value of using that blueprint during remediation.

The company did not start from zero. DOJ acknowledged that during the relevant period Southern Glazer’s had compliance policies, a Code of Conduct and employee handbook, trade-practice training, and mechanisms for reporting, investigating, and remediating misconduct. In 2019, the company also notified certain third-party marketing companies that it would no longer process incentives through them and terminated their ability to handle incentives and gift cards. Yet the Statement of Facts makes clear that problems persisted. Employees continued using outside mechanisms for gift cards, travel funds, and other benefits after the 2019 intervention.

This case offers an important compliance lesson. Remediation cannot stop at closing the door through which misconduct previously traveled. Compliance must determine whether employees simply found another door.

Put Resources Behind Compliance

Southern Glazer’s response beginning in 2023 was substantial. Between 2022 and 2024, the company increased compliance headcount by 85 percent and compliance funding by more than 65 percent. It also retained outside compliance experts to advise on program enhancements and best practices. Those numbers matter.

DOJ has repeatedly focused through the ECCP on whether compliance has sufficient resources and authority. Southern Glazer’s provides a practical example of what investment can look like when an organization concludes that its existing compliance infrastructure does not adequately address its risks. This was not simply hiring more investigators after misconduct occurred. Southern Glazer strengthened its compliance architecture.

The General Counsel was promoted to Executive Vice President, Chief Legal and Compliance Officer, reporting directly to the CEO. The company created and filled a Senior Vice President of Compliance & Ethics position. It hired a Vice President and Associate General Counsel for the West region and remapped compliance around five business regions. That is a significant point for boards. If management says compliance is important, look at the organization chart and the budget. Resources are evidence of priorities.

Accountability Had to Follow Misconduct

Southern Glazer’s also addressed individual accountability. The NPA credits the company with removing certain vice presidents and managers for violations of company policy, disciplining additional employees, and replacing senior leadership for California and the West Region. That matters because compliance programs lose credibility quickly when discipline stops at organizational rank.

The Corporate Compliance Agreement takes this concept further. It requires applying disciplinary procedures consistently and fairly, regardless of an employee’s position or perceived importance. When misconduct is discovered, the company must also remediate the resulting harm and assess whether the compliance program itself requires modification. That is precisely the right question after misconduct:

Not simply, Who violated the policy?

But also, What allowed them to do it?

An effective investigation should therefore generate two workstreams. One addresses individual accountability. The other addresses program failure.

Follow the Money

The Southern Glazer’s case is also a powerful internal-controls case. The alleged misconduct involved gift cards, travel, luxury goods, entertainment, marketing expenditures, supplier funds, bill-backs, expense reimbursements, and third-party vendors. According to the Statement of Facts, employees sometimes used altered invoices purporting to reflect legitimate business purposes to circumvent company accounting controls.

Southern Glazer’s responded by moving compliance closer to those transactions. The company imposed a Trade Practice Compliance Audit Program and implemented its “iShop” platform for marketing and promotional spending. It also added mandatory ethics and compliance training and additional compliance resources. That is another important lesson from the ECCP.

Training and policies matter, but compliance effectiveness ultimately has to reach the business process. If bribery risk resides in marketing spend, test marketing spend. If risk resides in bill-backs, audit bill-backs. If employees can manipulate expense descriptions, analyze expense data. If misconduct travels through Accounts Payable, build controls into Accounts Payable. The goal is not simply to tell employees not to engage in misconduct. It is to make misconduct harder to execute and easier to detect.

Rebuild Third-Party Risk Around Payment Controls

The third-party remediation may be the most instructive aspect of the Southern Glazer’s resolution. Third parties were not peripheral to the alleged misconduct. They were part of the mechanism through which value could be transferred and transactions disguised.

Southern Glazer’s responded with a Third-Party Management Program requiring vendors to agree to the company’s compliance and audit standards. Vendors became subject to enhanced due diligence and documentation requirements. The company obtained audit rights. Most importantly, vendors had to be approved before the company could issue payment. Southern Glazer’s also offboarded vendors because of the new requirements. That last point deserves attention.

Third-party compliance frequently becomes an onboarding exercise. Conduct diligence. Assign a risk rating. Obtain contractual language. Approve the vendor. Done. Southern Glazer’s demonstrates why that was insufficient. The control environment must connect onboarding to payment. Accounts Payable should not merely assume that a vendor appearing in the system has passed appropriate compliance controls. The process should prevent payment when required approvals have not occurred. That is compliance embedded into operations.

Compliance Has to Reach the Field

Southern Glazer’s also created a network of state-level “Compliance Champions” responsible for promoting awareness locally and providing additional compliance support. That is particularly relevant for geographically dispersed organizations. Corporate compliance can design excellent policies from headquarters. Risk occurs where employees interact with customers, suppliers, distributors, government officials, and other third parties.

Compliance therefore needs mechanisms to reach those employees and understand what is actually happening locally. The ECCP’s focus on whether a compliance program works in practice is important here. A policy residing on an intranet is not embedded compliance. Employees must know whom to call, understand the rules, and believe compliance understands their business.

Tone at the Top Still Matters

Southern Glazer’s also strengthened senior leadership messaging. The NPA specifically cites communications from the President and CEO reinforcing the importance of ethics and compliance. The company also updated its corporate values around “HEART”: Honesty, Excellence, Agility, Respect, and Teamwork.

Tone at the top is sometimes dismissed as soft compliance. It should not be. But tone only matters when behavior follows the message. Here, leadership messaging was backed by increased resources, management changes, discipline, audit mechanisms, training, third-party controls, and structural changes. That combination is important.

A CEO email saying compliance matters is communication. A CEO message backed by budget, personnel, discipline and controls is governance.

Test Whether the Remediation Actually Works

The final lesson is perhaps the most important. Southern Glazer’s did not simply promise that its enhanced program would work. The Corporate Compliance Agreement requires periodic risk assessments, annual review of policies and procedures, appropriate compliance independence and resources, training, confidential reporting mechanisms, adequately resourced investigations, discipline, M&A procedures, and periodic testing designed to evaluate and improve program effectiveness.

The company must also report annually to the USAO and TTB regarding remediation and implementation of its compliance measures during the NPA. At the end of the term, the CEO, Executive Vice President, and Chief Legal and Compliance Officer must certify that the company has implemented a compliance program that meets the agreement’s requirements and is reasonably designed to detect and prevent trade-practice violations throughout its operations.

That puts real accountability behind remediation.

The Southern Glazer’s Roadmap

Every CCO facing a significant compliance failure should study Southern Glazer’s. The lesson is not that remediation guarantees an NPA. The agreement expressly states that the government reached its decision based on the individual facts and circumstances of this case.

The lesson is that remediation matters, and DOJ has given compliance professionals an unusually detailed picture of what meaningful remediation can look like. Southern Glazer’s strengthened leadership. It increased resources. It brought in outside expertise. It disciplined employees and changed management. It strengthened tone at the top. It pushed compliance into the field. It created new audit mechanisms. It improved training. It rebuilt third-party controls. It connected vendor approval to payment. And it committed to continued risk assessment, monitoring, and testing.

Most significantly, it did these things by expressly aligning its compliance program with the ECCP. For CCOs, that may be the most important takeaway from this entire resolution. Do not wait for prosecutors to use the ECCP to evaluate your compliance program. Use it yourself.

Ask whether your program is well designed. Ask whether it is adequately resourced and empowered to function effectively. Ask whether it works in practice. Then test the answers against your actual risks, transactions, third parties, investigations, and control environment.

Southern Glazer’s demonstrates that the ECCP is more than DOJ guidance. Used properly, it can be a roadmap for remediation, a framework for explaining compliance investment to senior management and the board, and, when misconduct occurs, evidence that the company understood the failure and built a stronger program in response.

That is the compliance lesson from Southern Glazer’s. The best time to align your program with the ECCP is before misconduct occurs. The second-best time is when you discover your existing controls weren’t enough.

Other Resources

Tom and Matt Kelly took a deep dive into the Southern Glazer NPA on this episode of Compliance into the Weeds.

Matt Kelly looked at it on Radical Compliance.
Categories
Compliance Into the Weeds

Compliance into the Weeds: Southern Glazer’s NPA: How Remediation and ECCP Alignment Drove a Favorable Settlement

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into compliance-related topics, literally going into the weeds to explore a subject in greater depth. Looking for hard-hitting compliance insights? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss the Southern Glazer NPA.

The Southern Glazer Wine and Spirits’ non-prosecution agreement is a rare example where prosecutors credited compliance program remediation, rather than self-disclosure or extensive cooperation, as central to a favorable outcome. Southern Glazer, the largest US liquor distributor, faced a major California kickback and bribery scheme involving five former employees, fabricated records, sham agreements, and luxury benefits to retailers and others, along with alleged tax impacts. The company resolved the matter with a $12.5 million payment and a two-year NPA requiring the CEO and CCO to certify program effectiveness. Tom and Matt review how the NPA affirms DOJ’s Evaluation of Corporate Compliance Programs as still relevant and detail remediation steps: major headcount and budget increases, upgraded compliance leadership, audits of marketing spend, enhanced training, strengthened third-party controls and AP payment blocks, outside reviews, and tone-at-the-top messaging.

Key highlights:

  • Southern Glazer Case Setup
  • Industry Risks and Scheme
  • ECCP Guidance Still Matters
  • Program Overhaul Timeline
  • Concrete Remediation Metrics
  • DOJ Signals Under Trump Era

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds was most recently honored as one of the Top 25 Regulatory Compliance Podcasts, a Top 10 Business Law Podcast, and a Top 12 Risk Management Podcast. Compliance into the Weeds has received Davey, Communicator, and W3 Awards, all for podcast excellence.

Categories
Blog

Da Vinci Week: Part 3 – Leonardo’s Flying Machines and “Can We?” or “Should We?”

In the first two posts in the Leonardo Compliance Framework, the Mona Lisa gave us Refine, the principle that an effective compliance program improves as the organization learns from experience. Leonardo’s anatomical studies gave us Investigate, the discipline of looking beneath misconduct to understand root causes, control failures, incentives, management decisions, and the organizational systems that produced the outcome. The third principle is Innovate.

For that lesson, we turn to Leonardo’s studies of flight and his designs for flying machines. Leonardo examined birds, air movement, wings, and mechanical systems as he considered whether technology could allow human beings to fly. Many of his concepts were far beyond the practical capabilities of his time, but they demonstrate an important characteristic of Leonardo’s work: he imagined capabilities that did not yet exist and then studied the systems necessary to make them possible.

For corporate compliance professionals in 2026, the analogy to artificial intelligence is particularly useful. AI is expanding what companies can automate, analyze, predict, generate, and increasingly act upon. Organizations are moving beyond using generative AI to draft documents and summarize information. AI systems are becoming embedded in business processes, interacting with corporate data, supporting consequential decisions, communicating with customers, evaluating third parties, and, through increasingly agentic capabilities, taking actions that previously required human intervention.

The compliance challenge is not whether companies should innovate. They will. The challenge is establishing governance that lets innovation create business value without creating unmanaged legal, ethical, operational, or compliance risk.

AI Governance Is Enterprise Governance

Compliance professionals have sometimes approached emerging technology as primarily the responsibility of IT, Cybersecurity, Data Privacy, or Legal. That division becomes increasingly difficult with AI because these systems can influence many of the activities a corporate compliance team already oversees. Indeed, the Evaluation of Corporate Compliance Programs (ECCP) anticipates these very concepts in its 2024 edition.

AI may assist with third-party due diligence, contract review, procurement, transaction analysis, hiring, customer communications, investigations, fraud detection, marketing, or pricing. Each application creates a different risk profile. A due diligence system may generate inaccurate information about a business partner. An investigation tool may expose privileged or confidential information. A sales application may generate communications inconsistent with company policies. An agent connected to corporate systems may take actions that historically required human approval.

The ECCP asks the following:

  • How does the company assess the potential impact of new technologies, such as artificial intelligence (AI), on its ability to comply with criminal laws?
  • Is management of risks related to the use of AI and other new technologies integrated into broader enterprise risk management (ERM) strategies?
  • What is the company’s approach to governance regarding the use of new technologies such as AI in its commercial business and in its compliance program?
  • How is the company curbing any potential negative or unintended consequences resulting from the use of technologies, both in its commercial business and in its compliance program? 

Visibility and Risk Should Drive the Control Environment

By 2026, asking whether a company uses AI provides little useful information. Management needs to understand how AI is being used and what authority particular systems possess. A tool that summarizes a public document presents a very different risk profile from a system that influences hiring, approves a third party, communicates with customers, accesses confidential information, initiates a transaction, changes corporate records, or takes actions across interconnected systems.

An AI inventory should therefore identify meaningful use cases, including the business owner, intended purpose, relevant data, third parties involved, decisions influenced by the technology, degree of autonomy, and applicable controls. The objective is not simply to count tools. It is to give management sufficient visibility to identify where material risk exists.

That visibility should support risk classification. Not every AI application requires the same level of governance. Classification should consider the system’s purpose, data sensitivity, potential consequences of error, degree of autonomy, affected populations, ability to review or reverse decisions, and applicable legal or regulatory requirements.

This is familiar territory for compliance professionals. Risk-based programs have long applied different levels of scrutiny to third parties, transactions, investigations, and markets. AI should follow the same principle. Higher-risk systems should receive greater review, stronger controls, and more rigorous monitoring.

Human Oversight Must Preserve Accountability

“Human in the loop” has become common language in AI governance, but a human’s presence alone does not create an effective control. Meaningful oversight requires defined responsibilities, appropriate expertise, sufficient capacity to review relevant outputs, and authority to challenge or override the system.

If one employee is nominally responsible for reviewing thousands of AI-generated recommendations each day, human oversight may exist on paper but not function in practice. The same problem arises when employees routinely accept recommendations because they assume the technology is more reliable than their own judgment.

The control should therefore define the reviewer’s responsibilities, the circumstances requiring additional scrutiny, the authority to reject recommendations, and how to handle material overrides or recurring disagreements between the system and human decision-makers. Most importantly, technology should not create an accountability vacuum. If an AI system contributes to a compliance failure, the organization should still be able to identify the business process owner, who approved the use case, who monitored it, and who had authority to intervene.

This becomes increasingly important with agentic systems. Traditional corporate controls generally assume identifiable human actors approve payments, create vendors, review contracts, or authorize higher-risk third parties. When technology performs some of those activities, the organization has effectively delegated authority to a system. The control environment must reflect that delegation while retaining human and organizational accountability for the outcome.

Third-Party AI and Data Risk

Many companies will obtain significant AI capabilities from external vendors rather than develop them internally. Using a vendor does not transfer accountability for the resulting compliance risk. Traditional third-party risk management principles remain relevant. The company should understand the service provided, the information the vendor receives, how data are used and retained, which subcontractors are involved, how incidents are managed, and what contractual rights the company has to obtain information, require remediation, audit, or terminate the relationship.

AI adds a dynamic element because models, features, and business uses can change after initial approval. Monitoring should therefore identify material changes in functionality, data use, vendor practices, or business application that could alter the original risk assessment.

Data governance is equally important. Companies need clear rules regarding which AI systems may access confidential business information, personal data, investigation materials, privileged communications, customer information, trade secrets, source code, and other sensitive information. As enterprise AI systems increasingly operate on internal data, blanket prohibitions will often give way to more precise governance defining approved systems, permissible data, access controls, retention, deletion, and accountability.

These issues require coordination across Compliance, Legal, Privacy, Cybersecurity, IT, Records Management, and the business. Effective governance depends upon clear responsibilities rather than overlapping or fragmented ownership.

Test Before Deployment and Monitor Afterward

Leonardo’s flying machines provide another useful innovation lesson. Test a design before you trust it with a critical task. AI testing should match the risk. Before deployment, the company should understand whether the system performs as intended, where its limitations lie, how it responds to unusual circumstances, whether users can manipulate it, and whether inaccurate or inconsistent outputs could create material consequences. Testing at implementation is not enough. Business conditions change, vendors update models, employees develop new uses, and system capabilities expand. An application that operated within acceptable parameters when approved may later present a different risk profile.

Higher-risk systems therefore require post-deployment monitoring that can identify performance issues, material changes, incidents, and circumstances requiring reassessment. Management should also establish when a system should be modified, restricted, or suspended.

This lifecycle approach connects Innovate to the next Leonardo principle, Monitor. Responsible innovation is not a one-time approval. Governance should continue throughout the period the organization relies on the technology.

Using NIST and ISO as Governance Architecture

Compliance professionals do not need to invent an AI governance structure from scratch. The NIST AI Risk Management Framework provides a useful approach to governance, mapping, measuring, and managing AI risk, while ISO/IEC 42001 offers a management-system perspective built around responsibilities, processes, documentation, monitoring, and continuous improvement.

For the CCO, the value lies in providing governance architecture, not another checklist. The relevant measure is not whether a company can say it follows NIST or ISO. It is whether its governance system addresses the actual risks created by its AI applications and whether the resulting controls work in practice. Frameworks provide structure. Management remains responsible for operating the system.

Compliance Should Enable Responsible Innovation

The CCO should avoid two extremes: allowing enthusiasm for AI to outrun governance or creating an approval structure so burdensome that employees circumvent it. A better model is responsible innovation. Compliance can help create clear pathways for lower-risk experimentation while ensuring that higher-risk applications receive appropriate scrutiny. Employees should understand what uses are permitted, which require approval, what categories of information may be used, and when escalation is necessary.

This approach also creates opportunities for a corporate compliance program. AI may improve due diligence, transaction monitoring, investigations, risk assessment, training, and data analysis. The compliance function should be willing to explore those capabilities under the same risk-based governance it expects the business to follow.

A CCO’s contribution should not be measured by how much innovation Compliance prevents. It should be measured in part by whether Compliance helps the enterprise capture value while maintaining appropriate accountability and control.

Before Leaving the Ground

Leonardo’s flying-machine studies represent the willingness to imagine possibilities beyond current practice. The modern compliance lesson is to combine that willingness with disciplined governance. For the CCO, Innovate means helping the enterprise pursue new capabilities through a risk-based system that provides visibility, assigns ownership, preserves meaningful human accountability, tests higher-risk applications, and monitors them as technology and business use evolve. The objective is neither unrestricted adoption nor blanket prohibition. It is responsible innovation that can produce sustainable business value.

From Innovation to Monitoring

Responsible innovation does not end when technology is approved and deployed. The organization must determine whether systems continue to operate as intended as data, users, vendors, business conditions, and risks change. That brings us to the fourth Leonardo principle: Monitor.

In Blog Post Four, The Last Supper and the Danger of Deterioration, we will use Leonardo’s experimental masterpiece to examine the difference between implementing a control and demonstrating that it remains effective. The discussion will focus on control testing, continuous monitoring, compliance analytics, ownership, remediation, AI monitoring, and the board’s role in evaluating evidence of continuing program effectiveness.

Categories
Blog

Da Vinci Week: Part 2 – Leonardo’s Anatomical Studies and Getting Beneath the Surface

In the first post in our Leonardo Compliance Framework, the Mona Lisa introduced Refine: the discipline of continuous improvement. An effective compliance program should learn from investigations, monitoring, risk assessments, employee feedback, control failures, and business changes. The program should evolve because the organization knows more today than it knew yesterday. That brings us to the second principle: investigate.

Leonardo was not satisfied with observing the human body from the outside. His anatomical studies examined muscles, bones, organs, movement, and the relationships among different parts of the body because he wanted to understand how the entire system worked. That provides a useful model for the modern Chief Compliance Officer because an effective corporate investigation should accomplish more than determine whether an employee violated a policy. It should help the organization understand why the conduct occurred, which controls failed, what incentives influenced behavior, whether management contributed to the problem, whether similar conditions exist elsewhere, and what should change as a result.

The compliance lesson from Leonardo is to look beneath the visible misconduct and understand the system that produced it.

An Investigation Is More Than a Search for Misconduct

Consider a familiar scenario. An investigation establishes that a sales employee used a consultant to make an improper payment to secure business. The company confirms the misconduct, terminates the employee and consultant, documents the findings, and closes the matter.

That process may answer the immediate legal and disciplinary questions, but it does not necessarily answer the larger compliance question. The company should also understand why it hired the consultant, how it approved the relationship, what due diligence it performed, whether it identified red flags, how it compensated the consultant, and how the resulting invoices and payments moved through the organization. Management should consider whether commercial incentives contributed to the conduct, whether supervisors encountered warning signs, and whether similar consultants are being used elsewhere.

If the company concludes only that one employee violated the anti-corruption policy, it may remove the individual while leaving intact the conditions that allowed the misconduct to occur. The investigation has then addressed the actor without addressing the vulnerability. That is why investigations should be viewed as a source of organizational intelligence.

Root Cause Should Drive Remediation

Root-cause analysis is where Leonardo’s anatomical method becomes particularly relevant. The objective is to move from the visible event to the systems underneath it. The Evaluation of Corporate Compliance Program (ECCP) states, “Finally, a hallmark of a compliance program that is working effectively in practice is the extent to which a company can conduct a thoughtful root.” It asks: What is the company’s root cause analysis of the misconduct at issue? Were any systemic issues identified? Who in the company was involved in making the analysis?

Root-cause analysis helps the company distinguish symptoms from causes, and that distinction should determine remediation. A response directed only at the visible misconduct may create the appearance of action without materially reducing the underlying risk.

This is also why significant investigations should test assumptions about the compliance program. If an intermediary engages in misconduct despite passing third-party due diligence, the company should examine whether the process missed information it reasonably could have identified. If an employee disguises improper payments, Compliance and Finance should understand how the relevant financial controls were circumvented. If retaliation occurs after an employee raises a concern, the organization should determine whether its anti-retaliation controls function in practice.

A well-designed compliance program can still experience misconduct. No reasonable system eliminates all risk. Effectiveness is measured by how the organization detects misconduct, responds, learns from failures, and strengthens the program when it identifies weaknesses.

Follow the Decision Trail

Investigators naturally follow evidence by reviewing documents, interviewing witnesses, analyzing transactions, and reconstructing events. Compliance investigations should also follow the decision trail because misconduct frequently passes through business processes designed to create accountability.

The investigation should identify who selected and approved a problematic third party, who authorized exceptions or unusual compensation, who approved payments, who received warnings, and who decided whether concerns warranted escalation. This becomes especially important when misconduct involves senior personnel, high performers, or commercially significant relationships.

The purpose is not to assign blame indiscriminately across every function connected to an incident. It is to understand where accountability actually resided and whether the people responsible for operating or supervising controls fulfilled those responsibilities.

A decision trail can reveal that misconduct was not simply the act of one individual. Other employees may have facilitated the conduct, ignored warning signs, approved questionable transactions, or failed to escalate information. Conversely, the evidence may demonstrate that established controls operated appropriately and that the individual deliberately circumvented them.

Organizational Justice Requires Consistency

Investigations also play a central role in corporate culture. Employees watch how organizations respond to allegations, particularly when cases involve senior executives or high-performing employees. They notice whether powerful people receive different treatment and whether employees who raise concerns suffer professional consequences. This makes consistency an important component of organizational justice, which the ECCP identifies as a part of every compliance program.

Consistency does not require identical outcomes. Facts, intent, responsibilities, prior conduct, cooperation, supervisory duties, and other legitimate considerations can justify different consequences. What matters is that the organization uses a credible process and applies its standards without creating privileged classes of employees.

Investigation governance is therefore important. The company should establish clear decision rights concerning whether allegations require investigation, who determines scope, who approves closure, how disciplinary decisions are made, when conflicts of interest require independent handling, and when matters involving senior executives should be escalated to the Audit Committee or board. These governance arrangements should be in place before a sensitive case arises.

Accountability should also extend beyond the individual who directly engaged in misconduct. Management behavior matters. A supervisor who ignored repeated warning signs, encouraged excessive risk-taking, approved unjustified exceptions, or created incentives that contributed to misconduct may raise separate accountability issues.

If employees see junior personnel disciplined while supervisors face no consequences for meaningful oversight failures, the company may signal that accountability flows only downward. Credible organizational justice requires a more consistent approach.

Investigation Data Is Enterprise Risk Intelligence

Individual investigations explain specific events. Aggregated investigation data can reveal enterprise-wide patterns, making it an important compliance asset. A CCO must understand which allegations recur, whether particular business units or managers appear repeatedly, where investigations are delayed, what root causes occur most often, whether similar control failures appear across jurisdictions, and whether employees who raise concerns subsequently experience unusual turnover or other adverse outcomes.

Those patterns can identify emerging risks that individual case files may not reveal. The data must be interpreted carefully. A business unit with a high number of hotline reports may have significant cultural problems, or it may have a healthy speak-up environment in which employees trust the reporting system. A location with few reports may have an excellent culture, or employees may fear retaliation.

Investigation data works best when combined with other information, including hotline trends, employee surveys, HR data, audit findings, transaction monitoring, exit interviews, and business knowledge. The objective is not simply to count cases but to use investigative information to understand the organization more effectively. This is the Leonardo approach in practice: observation combined with inquiry.

AI Changes the Investigation Function

Artificial intelligence is also changing corporate investigations. AI tools may assist with document review, chronology development, translation, pattern identification, data analysis, and summarization. Used appropriately, these capabilities may allow investigation teams to analyze larger volumes of information and identify relationships more efficiently.

They also create significant governance issues because investigations frequently involve some of the company’s most sensitive information. Before using AI, the organization should understand what data it will provide to the system, whether the material includes privileged, confidential, personal, or commercially sensitive information, where the data will be processed and retained, and what contractual and technical protections apply. Once again, the ECCP puts this onus on your compliance function.

Reliability is equally important. Investigators need a process to validate AI-assisted analysis and identify inaccurate or unsupported outputs. AI use should not obscure how a significant investigative conclusion was reached or prevent the company from explaining the evidence supporting its decision.

Human accountability should remain clear. AI can assist investigators, but it should not replace professional judgment concerning scope, credibility, findings, discipline, or remediation. The broader governance principles reflected in the NIST AI Risk Management Framework and ISO/IEC 42001 can help organizations think about risk management, human oversight, documentation, and monitoring. Still, the fundamental investigation requirements remain confidentiality, accuracy, fairness, privilege, and defensibility.

Connect Investigations to Remediation and Lessons Learned

Companies sometimes separate investigations and remediation too sharply. Legitimate reasons exist to maintain appropriate independence between fact-finding and certain management decisions, but the compliance program still needs a clear mechanism to convert investigative findings into corrective action.

For significant matters, management should understand what failed, why it failed, whether the weakness could exist elsewhere, what corrective action is required, who owns that action, and how the company will determine whether remediation worked. This turns an investigation from a historical examination into a forward-looking compliance tool. Without that connection, an organization can become highly proficient at investigating the same problem repeatedly without becoming better at preventing it.

Lessons learned should also travel beyond the specific business unit or jurisdiction involved. If an investigation in one market identifies improper distributor discounts caused partly by weak approval controls, the company should consider whether comparable controls exist elsewhere. If employees use personal messaging applications to circumvent company systems, management should assess whether the practice extends beyond the employees involved in the investigation. If an AI incident reveals that employees can deploy unapproved tools without effective technical restrictions, the organization should consider the broader governance implications.

This does not require distributing confidential investigative details throughout the company. It means converting case-specific findings into enterprise risk intelligence. Depending on the issue, the lesson may lead to changes in controls, risk assessments, monitoring, training, policies, management communications, or incentive structures. That is how Investigate feeds Refine.

What the Board Should Understand About Investigations

Boards and Audit Committees should resist evaluating the investigation function primarily through case counts. Knowing how many matters were opened and closed provides useful operational information, but it offers limited insight into program effectiveness.

Directors should understand what the company is learning from investigations. Significant themes, recurring root causes, internal control weaknesses, unusual patterns across business units, retaliation concerns, and the status and effectiveness of remediation all provide more meaningful information about compliance risk.

The board should also understand whether investigative resources match the company’s risk profile. Significant cases should not remain unresolved because the organization lacks appropriate staffing, cross-border expertise, data capabilities, employment-law support, or access to information. Matters involving senior personnel should be handled through processes designed to preserve independence and avoid conflicts.

The board does not need to manage individual investigations. Its role is to understand whether the investigation system provides reliable information about significant compliance risks and whether management responds appropriately to what that system reveals.

Getting Beneath the Surface

Leonardo’s anatomical studies give compliance professionals a useful model for investigations because the visible event may be only the first indication of a larger systemic issue. An improper payment may reveal a third-party weakness that exposes deficiencies in due diligence, technology, ownership, incentives, or management oversight.

The investigator’s task is to understand those connections without allowing every matter to become an unlimited enterprise-wide inquiry. Scope should remain proportionate to the seriousness, complexity, and potential reach of the issue. The objective is disciplined curiosity: understanding whether the evidence points to an isolated act or a broader weakness in the compliance system.

For the CCO, the practical lesson is that investigations should do more than establish whether a rule was violated. Significant matters should help the organization understand the controls, incentives, management decisions, and business conditions that contributed to the conduct. Root-cause analysis should drive remediation, investigation findings should test assumptions about program effectiveness, aggregated case data should inform enterprise risk assessment, and lessons learned should improve controls beyond the immediate matter.

That is Investigate, the second principle of the Leonardo Compliance Framework. Finding misconduct matters, but the greater compliance value comes from understanding the system that produced it and using that knowledge to reduce the likelihood of recurrence.

From Investigation to Innovation

Investigation helps the compliance professional understand how existing systems work and why they sometimes fail. Leonardo, however, was equally interested in systems that did not yet exist, which takes us to the third principle in the Leonardo Compliance Framework: Innovate.

In Blog Post Three, Leonardo’s Flying Machines and AI Governance, we will use Leonardo’s studies of flight to examine responsible innovation in 2026. Artificial intelligence and increasingly agentic technologies are moving from generating information to taking action within business processes, raising new questions about risk classification, human accountability, third-party AI, data governance, testing, monitoring, NIST AI RMF, and ISO/IEC 42001.

Leonardo’s willingness to imagine flight provides the innovation lesson. For the modern CCO, the corresponding governance task is ensuring the enterprise understands the risks, controls, and accountability needed before giving new technology meaningful authority inside the business.

Categories
Blog

Da Vinci Week: Part 1 – The Mona Lisa and Continuous Improvement

I recently wrote a five-part blog series on compliance through Michelangelo’s lens. In our Michelangelo Compliance Framework, we used five extraordinary projects to explore five disciplines of the modern compliance function: Challenge, Execute, Defend, Build, and Govern. Michelangelo gave us a model of the compliance professional as a builder. His work showed the importance of structure, execution, resilience, accountability, and the ability to turn an ambitious vision into something enduring.

This week, I want to do the same through the lens of Leonardo da Vinci, who gives us a different model. Leonardo was an observer, investigator, experimenter, engineer, anatomist, artist, and relentless student of how things worked. Where Michelangelo offers lessons about building, Leonardo offers lessons about learning. That distinction underpins our five-part Leonardo Compliance Framework: Refine, Investigate, Innovate, Monitor, and Document. In this blog post 1, we begin with Refine and Leonardo’s most famous painting, the Mona Lisa.

The compliance lesson is continuous improvement. An effective compliance program is never truly finished because the business it supports is never truly static. Markets change. Employees change. Third parties change. Regulations change. Technology changes. Criminal methodologies change. Artificial intelligence is accelerating many of those changes simultaneously. For the Chief Compliance Officer (CCO) or compliance professional in 2026, the question is therefore not simply whether the company has a compliance program. The better question is whether the program is materially better today because of what the organization learned yesterday.

The Compliance Program Is Never Finished

One fascinating aspect of the Mona Lisa is Leonardo’s extended relationship with the work. He kept refining it as he developed his understanding of light, anatomy, optics, and human perception. That provides a useful metaphor for compliance because companies often approach compliance initiatives through the language of completion. Policies are issued, training is delivered, third-party systems are implemented, investigations are closed, remediation projects are completed, and risk assessments are presented to the board.

A policy issued three years ago may no longer address how the business operates. A successful third-party implementation may not account for changes in the company’s distribution model. A 100 percent training completion rate does not demonstrate that employees can apply the training when confronting an ethical problem. Closing a remediation item does not establish that the revised control reduced the underlying risk.

Leonardo offers a different approach. Completion should create an opportunity for observation and learning. Management should understand what worked, what did not work as expected, what changed in the business, and whether those lessons justify refinement of the program. That is continuous improvement.

Turn Compliance Failures Into Organizational Knowledge

The DOJ has made clear in the most recent iteration of the Evaluation of Corporate Compliance Programs (ECCP) that continuous improvement sits at the heart of modern expectations for compliance program effectiveness. A risk-based program should evolve as the company’s risks evolve, using risk assessments, investigations, audits, monitoring, employee feedback, transaction data, and lessons learned to inform changes. A company that identifies the same weakness year after year without changing its response has not created an effective learning system.

Leonardo’s approach to understanding the natural world was to look beneath the visible surface. Compliance professionals should apply the same discipline. Misconduct often signals a deeper weakness in the system, and root-cause analysis helps identify it and use the lesson to improve the program.

Risk Assessment Should Produce Management Action

The compliance risk assessment provides another important opportunity for refinement. Companies frequently devote substantial resources to identifying and ranking risks, producing a heat map, presenting the findings to management and the board, and repeating the process the following year.

Here the ECCP asks, “Is the risk assessment current and subject to periodic review?” Is the periodic review limited to a “snapshot” in time or based upon continuous access to operational data and information across functions? Has the periodic review led to updates in policies, procedures, and controls? Do these updates account for risks discovered through misconduct or other compliance program issues?

The principle applies to artificial intelligence. If AI adoption changes the company’s risk profile, the risk assessment should lead to governance action through measures such as an AI inventory, risk classification, approval processes, human oversight, monitoring, or technical controls.

A mature compliance program should be able to draw a line from an identified risk to a management decision. If the risk profile changes while resources, controls, monitoring, and governance remain unchanged, the risk assessment has generated information without generating action.

Use Data to Refine the Program

Leonardo was a relentless observer who recorded what he saw and used those observations to develop new ideas. Modern compliance functions possess an advantage he could scarcely have imagined: enormous quantities of organizational data.

Hotline information can reveal cultural patterns. Investigation data can identify recurring allegations and root causes. HR data may indicate retaliation. Transaction information can identify unusual payments. Third-party data can reveal concentrations of risk, while audit findings can identify recurring control weaknesses.

But these insights are not enough. Are these insights put into practice? The ECCP inquires: Does the company have a process for tracking and incorporating into its periodic risk assessment lessons learned either from the company’s own prior issues or from those of other companies operating in the same industry and/or geographical region?

Compliance analytics should not become a competition to create the most sophisticated dashboard. The objective is better decision-making. A business unit with very few hotline reports, for example, could have an excellent culture or an environment in which employees are reluctant to speak. The number alone does not tell the whole story.

Compliance should therefore combine quantitative information with qualitative evidence, including employee surveys, focus groups, exit interviews, investigations, management discussions, and audit findings. The objective is to understand what the data mean in the business context.

AI Accelerates the Need for Refinement

Artificial intelligence makes continuous improvement increasingly important because AI systems and their uses can change faster than traditional corporate governance cycles.

The ECCP asks companies to consider how emerging technologies such as AI affect their ability to comply with criminal laws, how related risks are incorporated into enterprise risk management, and how organizations mitigate unintended consequences and potential misuse. The ECCP asks some pointed questions: How does the company assess the potential impact of new technologies, such as artificial intelligence (AI), on its ability to comply with criminal laws? Is management of risks related to the use of AI and other new technologies integrated into broader enterprise risk management (ERM) strategies? What is the company’s governance approach to using new technologies such as AI in its commercial business and compliance program? The implication for the CCO is significant: AI risk cannot be treated as a once-a-year compliance exercise.

NIST’s AI Risk Management Framework and ISO/IEC 42001 provide useful approaches to this challenge because both emphasize governance and ongoing risk management. For the CCO, the broader lesson is that AI governance should operate as a management system rather than a policy-writing project. The organization needs to learn from incidents, testing, employee behavior, technological changes, and evolving business use, then adjust governance accordingly. The principle is the same as the Mona Lisa: refinement should follow learning.

Move the Board Conversation From Activity to Learning

Boards and Audit Committees can reinforce this discipline by shifting the compliance conversation. Compliance presentations frequently focus on activity metrics: employees trained, investigations closed, third parties reviewed, policies updated, and remediation items completed. These measures provide useful information about program operations, but they do not necessarily demonstrate effectiveness.

Directors should also understand what the organization learned during the reporting period, what investigations revealed about controls, what monitoring identified that management did not previously know, how the risk profile changed, and what the compliance function changed as a result.

The board should also understand whether those changes worked. This moves oversight from compliance activity to compliance effectiveness. It allows the CCO to present Compliance not simply as a collection of programs and controls but as a management system that identifies risk, learns from experience, and improves organizational decision-making.

The Mona Lisa Principle: Disciplined Refinement

Leonardo’s Mona Lisa gives the modern compliance professional a straightforward lesson about continuous improvement. An effective compliance program should develop through observation, evidence, learning, and a willingness to reconsider earlier decisions when circumstances justify change. The objective is not perpetual revision. It is disciplined refinement.

That distinction matters because continuous improvement can become counterproductive if it produces continuous disruption. Employees need stability, controls need sufficient time to operate, and management needs enough information to distinguish a meaningful trend from temporary noise. A compliance function that repeatedly changes policies, procedures, training, and controls without a clear risk-based rationale can create confusion rather than effectiveness.

Program refinement should therefore follow evidence. An investigation may reveal a systemic control weakness. Employee feedback may demonstrate that a policy is difficult to understand or apply. Monitoring may show that a control generates excessive false positives or is routinely circumvented. A regulatory development may require a different process, while an acquisition, new market, or technological change may materially alter the company’s risk profile. Artificial intelligence may introduce capabilities and risks that did not exist when the original governance structure was designed.

The CCO should have a disciplined process for converting those developments into program changes. Management should understand what triggered the proposed change, what risk it addresses, who owns implementation, and how the organization will determine whether the change produced the intended result. In this sense, continuous improvement should itself be governed.

A mature CCO should also be able to explain why today’s compliance program differs from the one the company operated two or three years ago. The answer should not simply be that policies were updated or new technology was purchased. The program should have changed because the organization learned something about its risks, controls, employees, third parties, culture, or business model and acted on that knowledge.

That is the central lesson of Refine, the first principle of the Leonardo Compliance Framework. Completion should not be confused with effectiveness. Root-cause analysis should produce program improvement, risk assessments should lead to management action, and data should help the organization understand what is happening rather than simply populate dashboards. When the evidence demonstrates that change is necessary, the organization should refine the program and then determine whether the refinement worked.

Leonardo models the compliance professional as a student of the organization. The CCO observes how the business operates, learns from failures and successes, and uses that knowledge to improve the compliance system. The measure of continuous improvement, therefore, is not how often the program changes. It is whether the program becomes more effective because the organization has learned.

From Refinement to Investigation

Continuous improvement depends upon understanding why problems occur. A company cannot meaningfully refine its compliance program if it treats each incident as an isolated act of employee misconduct. It must examine the systems, incentives, controls, management decisions, and behaviors that produced the outcome. That takes us to the second Leonardo principle: Investigate.

In Blog Post Two, we will consider Leonardo’s Anatomical Studies and will use Leonardo’s study of the human body as a framework for corporate investigations. Just as Leonardo looked beneath the surface to understand how interconnected systems functioned, modern compliance investigations should move beyond identifying misconduct to understanding its causes. We will examine how root-cause analysis connects investigations to remediation, why organizational justice matters, how investigation data can reveal systemic weaknesses, and what boards should understand when management reports that an investigation has been closed.

Categories
Blog

The NBA/Clippers Investigation: Part 5 – Lessons for CCOs and Boards

The ultimate measure of a compliance program is whether it can constrain the people the organization believes it cannot afford to disappoint. Most compliance programs are designed for ordinary decisions made by ordinary employees. The real danger lies in extraordinary decisions involving people with unusual economic power. Today we conclude with lessons learned.

They may be founders, controlling owners, senior executives, rainmakers, celebrity endorsers, critical customers, or star performers. Their value to the organization can become a reason to bypass controls, reinterpret rules, or treat prohibited requests as business problems requiring creative solutions.

The investigation into the LA Clippers and Kawhi Leonard demonstrates what happens when that pressure enters the commercial ecosystem. The independent investigators’ report (Wachtell Report) concluded that Clippers leaders helped create outside-income opportunities for Leonard through companies doing business with the team, linked vendor business to endorsement arrangements, paid impermissible personal expenses, and failed to report prohibited demands.

The lessons reach well beyond professional sports. They reach into all businesses. Finally, they apply wherever commercial urgency can overwhelm governance.

Lesson One: Power Is a Compliance Risk Factor

Traditional risk assessments organize risk by geography, business unit, transaction type, or regulatory subject. They often overlook individual power.

Organizations should identify people whose economic importance, ownership position, revenue contribution, reputation, or personal relationship with leadership could weaken ordinary controls. This is not an accusation against those individuals. It is recognition that employees may respond differently when a request comes from someone perceived as indispensable.

The DOJ’s Evaluation of Corporate Compliance Programs asks whether risk management is proactive, whether resources follow risk, and whether senior leaders persist in their commitment to compliance when facing competing business objectives. A power-risk assessment helps answer those questions.

Lesson Two: Prior Misconduct Must Change the System

The Clippers had a prior circumvention violation. The NBA later investigated improper demands associated with Leonard’s 2019 free agency, established a reporting requirement, and trained the team’s senior leadership. Yet the Wachtell Report concluded that similar risks materialized again.

Training is not remediation unless the organization can demonstrate changed behavior. After an incident, compliance should identify the root cause, assign control owners, establish deadlines, test effectiveness, and report results to the board. The inquiry should continue until the organization can show it has materially reduced the opportunity for recurrence. DOJ expressly asks whether companies incorporate lessons from their own misconduct and from similar problems at peer organizations. The Organizational Sentencing Guidelines likewise make prior history relevant to risk assessment, program design, and organizational culpability.

Lesson Three: Compliance Must Have Independent Authority

The question is not whether the organization employs compliance professionals. It is whether those professionals can challenge a powerful executive, suspend a transaction, obtain complete information, and reach an independent board committee without management permission.

The DOJ evaluates whether compliance has adequate qualifications, seniority, stature, resources, autonomy, and direct board access. These are operational requirements, not organizational-chart preferences. A CCO who can advise but cannot stop or escalate is not empowered. A compliance committee dominated by the executives sponsoring the transaction is not independent. A board that receives only management-filtered information is not exercising informed oversight.

Lesson Four: Follow the Entire Commercial Relationship

The Clippers investigation involved sponsorships, consulting agreements, sustainability services, an owner’s investment, player endorsements, vendor payments, and personal expenses. Reviewing each transaction separately could obscure the common purpose. Compliance needs a consolidated view of the relationship. That requires common identifiers across procurement, contracts, accounts payable, expenses, conflict disclosures, gifts, sponsorships, and third-party systems.

The most useful question may be simple: What other business do we have with this person or entity? Make that question mandatory when a transaction involves a significant vendor, executive relationship, personal investment, public official, customer representative, agent, or other high-risk beneficiary.

Lesson Five: Test Economic Substance

According to the Wachtell Report, several endorsement arrangements had unusual economics, limited performance obligations, little public activation, and compressed negotiation timelines. Consulting agreements involved substantial advance payments. Separate agreements contained matching or closely connected amounts. The COSO Internal Control–Integrated Framework reminds organizations that controls support compliance and operational objectives, not simply accurate accounting. A payment can be correctly recorded and still serve an improper purpose.

Controls should test business rationale, market value, deliverables, proof of performance, payment timing, ultimate beneficiary, and connections to other transactions. Internal audit should be authorized to ask whether a contract makes commercial sense, not merely whether an authorized person signed it.

Lesson Six: Mandatory Reporting Requires a Closed Loop

The Wachtell Report found that Clippers leaders did not report improper solicitations made on Leonard’s behalf, despite a rule requiring reporting even if a request was rejected. A mandatory reporting policy needs more than a sentence in the code of conduct. It requires defined triggers, responsible owners, escalation deadlines, documentation, non-retaliation protection, and verification that the report reached the required recipient.

Organizations should test the reporting control. Present leaders with realistic scenarios and ask what they would do, whom they would contact, and how quickly. If answers vary, the control is not operating reliably.

Lesson Seven: Red Flags Must Reach Someone Who Can Act

The Wachtell Report described unusual payment structures, internal concern about the Forum transaction, resistance from Aspiration executives, and explicit communications linking Clippers business to Leonard’s endorsement agreement. Red flags do not protect an organization merely because they exist in an email archive. They must reach a person with authority, independence, and responsibility to act.

Boards should identify mission-critical compliance risks and establish reporting systems that deliver meaningful information. The Delaware Supreme Court’s decision in Marchand v. Barnhill emphasizes the board’s obligation to make a good-faith effort to establish and monitor reporting systems for central compliance risks. That does not make every control failure a Caremark violation. It does mean that silence at the board level is not a defensible oversight model.

Lesson Eight: Investigation Conduct Is Compliance Conduct

Investigators assessed not only the underlying transactions but also witness credibility and cooperation. They distinguished between witnesses who accepted responsibility and those whose accounts conflicted with documents or changed over time.

Organizations should prepare for investigations before a crisis. Document preservation, witness instructions, privilege protocols, anti-retaliation protections, escalation duties, and cooperation standards should already be in place. Outside counsel should defend legitimate interests without impairing the organization’s ability to learn the truth. An investigation is not solely a litigation event. It tests culture and governance.

Lesson Nine: Accountability Must Reach Supervisors

The NBA’s penalties included a $30 million organizational fine, forfeiture of five first-round draft picks, individual suspensions, a payment by Leonard, a five-year restriction on Robertson, and a five-year compliance and monitoring program.

The sanctions reached individuals based on different forms of responsibility, including direct conduct, approval, supervision, and organizational leadership. Corporate consequence management should do the same. Employees who participate directly should be accountable, but so should managers who ignore red flags, approve unsupported exceptions, or fail to supervise. Enforce compliance consistently, regardless of commercial value or title.

Lesson Ten: The Board Must Oversee the Pressure Points

Boards do not need to approve every sponsorship, vendor agreement, or expense report. They do need visibility into the areas where incentives, power, and mission-critical compliance risks intersect.

The board should receive reporting on high-risk transactions, control overrides, related-party relationships, significant investigations, repeated policy violations, executive discipline, and remediation testing. It should meet privately with the CCO and internal audit leader and confirm both functions have the information and resources they need. Board oversight is not passive dashboard receipt. It is an informed challenge followed by documented action.

Practical Takeaways: A 90-Day Agenda

CCOs and risk leaders can translate these lessons into action:

  • Identify the organization’s most powerful internal and external stakeholders and assess where their requests could bypass controls.
  • Review prior investigations, violations, and audit findings to confirm that remediation was implemented and tested.
  • Map all relationships involving high-risk vendors, personal investments, sponsorships, consulting arrangements, and individual beneficiaries.
  • Establish independent review for transactions involving controlling owners, senior executives, or conflicts of interest.
  • Test procurement, payment, expense, and reporting controls using real transaction data.
  • Give compliance documented stop-work and escalation authority.
  • Define investigation cooperation and consequence-management standards before the next allegation.
  • Provide the board with targeted reporting on control overrides, repeat issues, and high-risk relationships.

The final lesson from the Clippers investigation is straightforward. Compliance fails when the organization treats the rule as an obstacle and the desired outcome as nonnegotiable. An effective program reverses that order. The rule defines the boundary, and the business must operate within it. The true measure of compliance is whether the organization can say no when yes would be more profitable, more convenient, or more popular. That is where governance becomes real.

Categories
Blog

The Clippers Investigation: Part 4 – Consequence Management at the Top

The Clippers penalties demonstrate that discipline is not the end of a compliance process. They are a public test of whether rules apply to powerful people. The Clippers investigation demonstrates why conflict controls must follow influence, economic benefit, and interconnected transactions, not merely financial ownership. In this Part 4 of a five-part series, we consider the consequences of cheating and not following the rules and regulations your organization agrees to comply with going forward. Every organization claims that no one is above the rules. Consequence management determines whether that statement is true.

The test does not come when a junior employee commits an obvious policy violation. It comes when the conduct involves a founder, controlling owner, senior executive, star performer, or other person viewed as essential to the business. The investigation into the LA Clippers and Kawhi Leonard presents that test in unusually clear terms. The independent investigators’ report of the Clippers’ NBA salary cap circumvention (Wachtell Report) attributed primary responsibility to Clippers owner Steve Ballmer, President of Business Operations Gillian Zucker, and President of Basketball Operations Lawrence Frank. It also found violations by Leonard through the conduct of his uncle and then-business manager, Dennis Robertson (Uncle Dennis).

The NBA responded with organizational, financial, individual, competitive, and monitoring consequences. For compliance professionals, the case provides a framework for considering who should be held accountable, for what conduct, and through what mechanism.

From Punishment to Consequence Management

Punishment looks backward. It asks what sanction should follow a violation. Consequence management is broader. It identifies misconduct, investigates responsibility, calibrates discipline, addresses supervisory failures, remediates control weaknesses, and communicates the organization’s expectations. All of this brings me to one of my favorite compliance phrases: consequence management.

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) introduces consequence management procedures as procedures to identify, investigate, discipline, and remediate violations of law, regulation, or policy. It goes on to state that every organization must enforce them consistently across the organization and ensure the procedures are commensurate with the violations. It concludes: Prosecutors should also assess the extent to which the company’s communications convey to its employees that unethical conduct will not be tolerated and will bring swift consequences, regardless of the employee’s position or title. 

Consequence Calibration

The report provides several categories for assessing responsibility.

  1. Direct participation. Investigators concluded that Zucker initiated, facilitated, and induced endorsement agreements involving Leonard and four Clippers business partners. They found that Ballmer knowingly sought to help Leonard obtain outside income and approved the Forum agreement after learning that Aspiration had tied it to Leonard’s endorsement arrangement. Frank conveyed Robertson’s demands and approved impermissible personal expenses.
  2. Supervisory responsibility. The report concluded that Ballmer failed to supervise the organization’s most senior business executive and failed to create conditions supporting compliance with the circumvention rules.
  3. Reporting responsibility. Investigators found that Ballmer, Zucker, and Frank did not report Robertson’s improper demands, despite an NBA rule requiring those reports even when the solicitation was rejected.
  4. Personal or represented conduct. The report concluded that Leonard, through Robertson, pressured the team to help obtain outside income and failed to reimburse certain personal expenses. Robertson allegedly made the demands and applied the pressure.

A defensible consequence decision should map each individual to the conduct, knowledge, authority, benefit, supervisory obligation, and missed opportunity to intervene. Titles alone should neither establish nor eliminate responsibility.

Credibility and Cooperation Matter

The report did something particularly useful for compliance officers: it distinguished among witness behavior. Investigators wrote that Zucker made statements inconsistent with contemporaneous documents and other witnesses, professed limited recollection on significant issues, placed responsibility on subordinates, and provided inconsistent versions of events.

By contrast, they reported that Frank discussed his conduct openly, recalled important details, accepted responsibility for subordinates, and remained generally consistent across interviews. The investigators stated that cooperation and credibility, or their absence, should factor into determining consequences.

Cooperation does not erase underlying conduct. It should, however, affect how consequences are calibrated. An employee who preserves documents, provides candid information, accepts responsibility, and assists remediation presents a different risk from one who misleads investigators or shifts blame.

The organization should define cooperation before an investigation begins. Employees should understand that cooperation requires truthful, complete, and timely responses; preserving relevant information; correcting prior inaccuracies; and no retaliation or interference. It does not require surrendering legitimate legal rights.

Prior Misconduct Changes the Analysis

The Clippers had previously been penalized for a salary-cap circumvention violation involving an endorsement opportunity. The NBA had also investigated demands made during Leonard’s 2019 free agency and provided specific training to Clippers leaders.

Prior history matters because it changes what the organization and its leaders reasonably should have done. A first incident may reveal an unrecognized risk. A repeated incident following investigation, rule clarification, and training raises questions about culture, supervision, remediation, and willingness to comply.

The Sentencing Guidelines identify prior organizational history as relevant to culpability and direct organizations to consider similar misconduct when designing an effective program. DOJ likewise asks whether policies, training, controls, and risk assessments incorporate lessons from prior incidents.

Remediation that ends with training is incomplete. The organization must test whether behavior, decision rights, escalation pathways, and controls changed.

The NBA’s Consequence Framework

The NBA’s official action included multiple forms of individual accountability. The box score of individual consequences reads as follows:

Person Relationship Consequence
Steve Ballmer Owner: LA Clippers Fine and one-year ban
Gillian Zucker Clippers President of Business Operations One-year unpaid suspension
Lawrence Frank Clippers President of Basketball Operations 6-month Unpaid Suspension
Kawhi Leonard Clipper Player $700K fine
Uncle Dennis Leonard Representative 5-Year Ban from NBA

These measures address different risks. For corporate compliance programs, the equivalent toolkit may include termination, suspension, bonus reduction, clawbacks where legally available, promotion restrictions, written warnings, removal of approval authority, enhanced supervision, vendor termination, and mandatory remediation. Consequences need not be identical, but the process must be consistent. Consistency means applying the same decision factors to similarly situated people. It does not mean imposing the same outcome regardless of role, intent, cooperation, history, or responsibility.

Practical Takeaways

CCOs, human resources leaders, and boards should consider the following:

  • Adopt written consequence-management procedures before a significant investigation occurs.
  • Use a consistent decision matrix covering conduct, intent, seniority, authority, benefit, cooperation, prior history, and supervisory responsibility.
  • Separate factual findings from disciplinary decisions, and ensure decision-makers understand the evidentiary record.
  • Document why similarly situated individuals received similar or different outcomes.
  • Apply financial consequences where permitted and align future compensation with compliance performance.
  • Communicate substantiated outcomes internally with enough detail to reinforce expectations while respecting legal and privacy constraints.
  • Track disciplinary data by level, function, geography, and type of misconduct to identify inconsistency.
  • Require independent board oversight when senior management is implicated.

Consequence management is where culture becomes measurable. If the organization protects its most powerful people, employees will understand that performance outranks integrity. If it applies a fair, independent, and proportionate process, employees will understand that compliance is part of how the business operates.

In our final blog post, we will bring the series together and develop a practical framework for CCOs, boards, and risk leaders seeking to build a compliance program that can say no to the star.

Categories
Blog

The NBA/Clippers Investigation: Part 3 – Paper Compliance Is Not an Internal Control: Substance, Procurement, and the Audit Trail

The Clippers investigation shows why contracts, approvals, and carefully drafted emails cannot substitute for controls that test economic reality. In Part 3 of a five-part series, we explore why and how a transaction can have a contract, an approval, an invoice, and an email trail and still pose a serious compliance problem. Documentation proves that a process occurred. It does not prove that the process was legitimate.

That distinction sits at the center of the investigation into the LA Clippers and Kawhi Leonard. The independent investigators’ report (Wachtell Report) concluded that the Clippers initiated and facilitated endorsement arrangements between Leonard and four companies doing business with the team, induced those arrangements by offering business to the companies, paid impermissible personal expenses, and failed to meet improper demands made on Leonard’s behalf.

The alleged conduct crossed organizational boundaries. It touched business operations, basketball operations, procurement, sponsorships, consulting arrangements, accounts payable, expenses, legal review, and executive management. That makes this an internal controls case.

The Difference Between Evidence and Control

One of the report’s most important findings concerned introduction emails sent by Clippers President of Business Operations Gillian Zucker. The emails were written as if Boingo, Daktronics, Lockton, and later Aspiration had requested introductions to Leonard’s representatives. NBA rules permitted a narrow response when a commercial partner initiated such a request. They did not permit the team to create the opportunity for the player. The investigators concluded that the emails did not reflect the true sequence of events and, in Aspiration’s case, were created after deal development was already underway.

This is a classic paper-compliance problem. The communication used the language of the rule without satisfying its substance. A control cannot merely ask whether an introduction email contains the approved wording. It must test who initiated the contact, what discussions preceded the email, who proposed the economics, and whether team personnel remained involved afterward. Checklists confirm the form. Effective controls challenge reality.

Fragmented Transactions Hid a Common Purpose

The Wachtell Report described multiple agreements that could have appeared unrelated in separate systems. Vendors entered consulting or services agreements with the Clippers while also entering endorsement agreements with Leonard. Aspiration had sponsorship, sustainability, investment, forum, and player-endorsement relationships involving overlapping parties.

Investigators connected those transactions through timing, matching amounts, communications, and business leverage. Two companies reportedly received $10 million in consulting payments before entering endorsement agreements with Leonard. A third received a $2 million consulting payment one day after making its first payment to him.

The Forum agreement initially contemplated $7 million in annual business for Aspiration. That figure matched the annual cash component of Leonard’s endorsement agreement. Investigators further reported that the underlying carbon analysis did not generate the $28 million budget. Instead, the consultant said the Clippers supplied that budget.

The control failure was fragmentation. Procurement reviewed one agreement, marketing another, finance a payment, and business leaders the broader relationship. No control appears to have aggregated the transactions and asked whether one funded, induced, or conditioned another.

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) tells prosecutors to examine how misconduct was funded, including purchase orders and reimbursements (How was the misconduct in question funded (e.g., purchase orders, employee reimbursements, discounts, petty cash?); what controls could have prevented access to those funds (What controls failed?); whether vendor-selection procedures were followed (If vendors were involved in the misconduct, what was the process for vendor selection and did the vendor undergo that process?); and whether contract terms, payment terms, performance, and compensation were appropriate. Those are precisely the questions an organization should ask before enforcement authorities arrive.

Control Environment

The control environment begins with leadership and accountability. According to the report, the most senior business and basketball executives participated in or knew about key parts of the conduct. Investigators concluded that Ballmer failed to create conditions in which the organization followed rules it had previously violated. When senior leaders create the risk, lower-level approvals are unlikely to function as meaningful controls. Employees may view an executive request as authorization to proceed, even when the transaction presents obvious concerns.

Risk Assessment

The Clippers had a prior circumvention violation and were investigated over Leonard’s free-agency negotiations. The NBA had then provided specific training and imposed a mandatory reporting obligation. That history should have produced a targeted risk assessment covering player representatives, sponsor introductions, endorsement arrangements, personal expenses, vendor spend-back programs, and benefits flowing through third parties. Prior misconduct is not simply history. It is risk data.

Here, the ECCP asked some direct questions, including, “Were there prior opportunities to detect the misconduct in question, such as audit reports identifying relevant control failures or allegations, complaints, or investigations?” Additionally, it notes that critical factors in evaluating any program include whether the program is adequately designed to maximize effectiveness in preventing and detecting employee wrongdoing and whether corporate management enforces the program or tacitly encourages or permits employees to engage in misconduct.

Control Activities

The Wachtell Report suggests potential gaps in segregation of duties, conflict review, procurement approval, contract benchmarking, expense reimbursement, and related-transaction analysis. High-risk transactions should require independent approval outside the requesting executive’s chain of command. Controls should compare compensation with deliverables, confirm actual performance, flag advance payments, and identify common counterparties across procurement and non-procurement systems.

Information and Communication

The organization reportedly had information that should have triggered escalation: demands for $10 million in annual off-court income, unusual endorsement economics, concerns from Aspiration executives, internal descriptions of a Forum deal as “shady,” and explicit threats connecting the Forum and Leonard agreements. Indeed, Uncle Dennis’s presence alone was enough of a red flag based on his prior conduct. The issue was not the absence of information. It was the failure to move that information to a function with the independence and authority to act.

Monitoring

Hundreds of personal expenses were reportedly paid without the required deduction or reimbursement. Multiple vendors signed unusual endorsement arrangements, with minimal public activation or performance. These were recurring patterns, not one-time exceptions. Monitoring should identify patterns across time. If a control repeatedly approves exceptions without examining their cumulative effect, it is not monitoring risk. It is normalizing it.

Designing Controls for Substance

An effective control architecture should include three layers. Preventive controls should require documented business rationale, competitive sourcing, conflict disclosures, independent approval, clear deliverables, market benchmarking, and legal and compliance review before committing funds.

Detective controls should compare related transactions, test payment timing, examine overrides, confirm performance, and monitor expense exceptions. They should search for patterns across legal entities and business functions. Responsive controls should define who receives red flags, when compliance can stop payment, when issues reach the audit committee, and how remediation is tracked to completion. The most important design principle is independence. The DOJ asks whether compliance has adequate authority, stature, resources, and direct access to the board. (Where within the company is the compliance function housed (e.g., within the legal department, under a business function, or as an independent function reporting to the CEO and/or board?)

If executives can bypass or overrule the control function without documented challenge, the program is not empowered.

Practical Takeaways

Compliance, audit, and risk leaders should take the following actions:

  • Inventory all systems containing vendor, contract, payment, expense, sponsorship, and conflict information.
  • Build monitoring systems that identify common parties and beneficiaries across those systems.
  • Require proof of services and measurable deliverables before releasing significant payments.
  • Review advance payments, matching amounts, compressed timelines, and executive overrides as elevated-risk indicators.
  • Treat prior violations and mandatory reporting duties as subjects for recurring control testing.
  • Give internal audit authority to examine commercial substance, not merely procedural completion.
  • Report control failures involving senior management directly to an independent board committee.

The Clippers salary cap circumvention demonstrates that an audit trail can document a failure as easily as it documents compliance. The question is whether the organization has controls that can interpret what the records mean.

In tomorrow’s blog post, we will turn from detection to accountability and examine how cooperation, credibility, seniority, prior misconduct, and supervisory failure should shape consequence management.

Categories
Blog

The NBA/Clippers Investigation: Part 1 – A Compliance Failure in Five Acts

Over the next five blog posts, we will consider how commercial pressure, weak controls, and leadership decisions turned a salary-cap rule into an enterprise-wide governance failure. Today in Part 1, we summarize those compliance failures.

The most dangerous compliance failure is not ignorance of the rules. It is knowing the rules, receiving targeted training, having a history of prior violations, and then creating a process that appears compliant while delivering a prohibited result. That is the central compliance lesson from the investigation into the LA Clippers and Kawhi Leonard.

The independent investigators’ report, prepared by the law firm Wachtell, Lipton, Rosen & Katz, concluded that the Clippers violated the NBA’s salary-cap circumvention rules through a pattern of transactions involving Leonard, his representatives, team executives, and four companies doing business with the organization. This is a sports story, but it is also much more. It is a case study in executive accountability, third-party risk, conflicts of interest, internal controls, reporting failures, organizational culture, and board oversight.

The Investigation

The matter began after the September 2025 podcast Pablo Torre Finds Out reported allegations involving a four-year endorsement agreement between Leonard and Aspiration Partners, a sustainability services company that later entered bankruptcy. Torre won a Pulitzer Prize for his podcast reporting. Thereafter, the NBA retained Wachtell Lipton to investigate. The inquiry eventually expanded beyond Aspiration to include endorsement agreements involving Boingo Wireless, Daktronics, and Lockton Insurance.

Investigators conducted 73 interviews of 60 people and reviewed more than 200,000 pages of documents. They interviewed Clippers owner Steve Ballmer; President of Business Operations Gillian Zucker; President of Basketball Operations Lawrence Frank; Leonard; and Leonard’s uncle and then-business manager, Dennis Robertson (Uncle Dennis). Third-party cooperation varied. Aspiration’s bankruptcy trustee and Daktronics provided substantial assistance, while other parties reportedly limited or refused cooperation.

The resulting 36-page report is a summary, not a complete presentation of the evidence. Nevertheless, the investigators concluded that the record was sufficient to establish multiple violations. The misconduct unfolded in five acts.

Act One: A Known Rule and a Known Risk

The NBA’s circumvention rules broadly prohibit teams from providing players with compensation, business opportunities, or anything else of value outside their authorized player contracts. The rules also prohibit attempts, solicitations, inducements, and informal understandings intended to produce such benefits. The rule has a simple underlying principle: to prevent salary cap circumvention.

The NBA provided teams with practical examples. A team representative could not recommend a player to a sponsor for an endorsement arrangement or initiate and facilitate that relationship. If a sponsor independently asked about a player, the team’s permissible response was generally limited to supplying the player’s or agent’s contact information.

The Clippers were not operating in unfamiliar territory. In 2015, the NBA fined the team $250,000 for conduct involving a potential endorsement opportunity for DeAndre Jordan. In 2019, the NBA investigated demands reportedly made by Uncle Dennis during Leonard’s free agency. The League subsequently required teams to report improper solicitations for benefits, even when the team rejected the request.

In December 2019, the NBA provided circumvention training to the Clippers’ senior leadership, including Ballmer, Zucker, and Frank. Investigators reported that all three understood the rule. This is the first compliance lesson: knowledge is not a control. Training can establish awareness, but only governance, monitoring, escalation, and accountability can translate awareness into compliant conduct.

Act Two: Pressure From a Powerful Stakeholder

According to the report, Uncle Dennis pressed the Clippers to help Leonard obtain approximately $10 million per year in off-court income. He communicated his demands to Frank, Ballmer, and Zucker. The report found no evidence that these demands were reported to the NBA, even though the reporting rule had been created in response to earlier concerns involving Robertson. Investigators also found no evidence that senior leaders clearly instructed him to stop making the requests.

Instead, contemporaneous notes reflected assurances that Clippers’ personnel would help Leonard achieve his financial goals. Uncle Dennis requested a plan, a pipeline of potential companies, and more frequent communication. This was a decisive moment. The organization had received a red flag from the highest-risk source, involving one of its most commercially valuable stakeholders. The control that mattered was not another training presentation. It was the ability to say no, document the response, escalate the demand, and make the required report.

Act Three: The Commercial Ecosystem Becomes the Delivery Mechanism

During six days in June 2020, Zucker sent introduction emails connecting Uncle Dennis with Boingo, Daktronics, and Lockton. Each email was written as if the company had requested the introduction. Investigators did not credit that explanation. They concluded that the Clippers initiated the introductions in response to Uncle Dennis’ demands.

Leonard subsequently entered into endorsement agreements with all three companies. The agreements provided for $18 million in total compensation, all of which was paid by August 2021. Investigators identified several unusual characteristics: the agreements were negotiated rapidly during the COVID-19 shutdown, imposed minimal performance obligations, were not publicly announced, and produced little evidence of meaningful activation.

At the same time, each company was pursuing lucrative business with the Clippers or the team’s arena. The report described consulting agreements, substantial advance payments, and perceived links between vendor business and payments to Leonard. The investigators found the Daktronics arrangement particularly direct. They concluded that Clippers personnel proposed using an endorsement agreement with Leonard as part of a “spend back” arrangement connected to Daktronics’ pursuit of the Intuit Dome scoreboard contract.

Here, third-party risk and procurement risk converged. The vendors were not merely outside parties. They allegedly became the mechanism through which the prohibited benefit was delivered.

Act Four: Aspiration and the Appearance of Legitimacy

Aspiration’s relationship with the Clippers was substantial. It included a long-term sponsorship agreement, sustainability services for the Intuit Dome, and a $50 million personal investment by Ballmer. The report concluded that Zucker raised the possibility of an Aspiration endorsement agreement with Leonard, recruited a business agent to help structure it, communicated proposed financial terms, provided input on the term sheet, and remained involved after the formal introduction.

The final agreement called for $48 million in cash and equity over four years. Investigators described the compensation as extraordinarily high in relation to Leonard’s obligations and endorsement profile. The most significant issue involved a separate agreement under which the Clippers would purchase sustainability services for the Forum. Early documents contemplated $7 million in annual business for Aspiration, matching the annual cash component of Leonard’s endorsement agreement. When Aspiration’s co-founder threatened to abandon the Leonard agreement unless the Forum transaction was completed, internal Clippers’ communications reportedly reflected awareness of that linkage. Ballmer nevertheless approved the Forum agreement.

The compliance lesson is substance over form. A formal contract, documented introduction, consultant analysis, or stated business purpose does not end the inquiry. Compliance must ask who initiated the transaction, who benefits, whether the economics make sense, and whether supposedly independent agreements are actually connected.

Act Five: Expenses, Reporting, and the Control Environment

Investigators also identified hundreds of instances in which the Clippers paid personal travel, accommodations, gifts, and ticket expenses for Leonard, his family, or Uncle Dennis without making the deductions required by NBA rules. Frank authorized the payments.

The report further concluded that Ballmer, Zucker, and Frank failed to report Uncle Dennis’ improper solicitations. These findings move the case beyond isolated dealmaking. They suggest failures in expense management, accounts payable, executive approvals, legal review, reporting, and compliance escalation. Under the COSO Internal Control–Integrated Framework, internal controls support operational, reporting, and compliance objectives. They must operate across the enterprise, particularly where multiple transactions point toward the same underlying risk.

The Compliance Program Test

The DOJ’s Evaluation of Corporate Compliance Programs organizes its analysis around three fundamental questions:

  1. Is the compliance program well designed?
  2. Is it adequately resourced and empowered to function effectively?
  3. Does it work in practice?

The Clippers matter raises all three. The DOJ Organizational Sentencing Guidelines similarly require risk assessment, appropriate authority for compliance personnel, monitoring and auditing, confidential reporting mechanisms, consistent enforcement, and remediation. Prior misconduct must inform future risk assessment and control design.

The Caremark Doctrine provides the board-level perspective. The Delaware Supreme Court’s decision in Marchand v. Barnhill emphasizes that directors must make a good-faith effort to establish and monitor reporting systems addressing mission-critical compliance risks. The relevant point here is not that Caremark liability has been established. It is that known, central risks require reliable information to reach governing authorities, followed by documented oversight and action.

The Consequences

Following the report, the NBA imposed significant penalties. According to The Athletic the penalties are:

  • The forfeiture of five first-round picks by the Clippers;
  • A $30 million team fine for the Clippers;
  • A one-year suspension for Clippers owner Steve Ballmer
  • Suspensions without pay for two of the top Clippers executives, Gillian Zucker (president of business operations; one year) and Lawrence Frank (president of basketball operations; six months);
  • Placement in the NBA-controlled compliance and monitoring program for five years;
  • Leonard was required to forfeit $700,000; and
  • Uncle Dennis was banned and is prohibited from conducting business with NBA teams for five years.

These penalties demonstrate that governance failures can create consequences far beyond the value of the underlying transactions.

These penalties demonstrate that governance failures can create consequences far beyond the value of the underlying transactions.

Compliance Takeaways

Compliance professionals should take five immediate lessons from this matter:

  • Treat prior violations as mandates for verified remediation, not completed training exercises.
  • Map interconnected relationships among vendors, executives, customers, agents, and other powerful stakeholders.
  • Require independent review when multiple agreements may benefit the same individual.
  • Test the economic substance of transactions, including pricing, deliverables, advance payments, and ultimate beneficiaries.
  • Give compliance the authority to escalate and stop transactions involving senior executives or strategically important individuals.

The question is not whether an organization has rules. The question is whether its compliance system can withstand pressure from the people the business most wants to satisfy. In Part 2 (after Labor Day), we will examine the conflicts of interest embedded in the Clippers’ commercial ecosystem and consider how organizations should govern transactions where sponsors, vendors, executives, personal relationships, and individual benefits intersect.

Categories
Blog

Odyssey Week: Leadership: Penelope’s Loom: Integrity Under Pressure

Ed. Note: I was finally able to see the movie The Odyssey. To say it blew me away was an understatement. Even though it didn’t follow Homer’s work precisely or use ancient Greek, I still thought it was great cinema. Anytime you get people talking about the Greek classics, that is a win in my book. So check out the movie and enjoy it. Anne Hathaway was great as Penelope.

Penelope does not get enough credit. Odysseus gets the monsters, the storms, the speeches, the disguises, and the dramatic return. He gets the action scenes. Penelope gets the waiting. If the movie version made one thing clear, such an interpretation sells her short—very short.

Penelope is not simply waiting. She is governing under pressure. Opportunists surround her. The suitors have occupied her home, consumed her resources, pressured her to choose one of them, and treated uncertainty as an invitation to abuse. Odysseus is gone. Authority is contested. Telemachus is young. The house is under stress.

So Penelope does something quietly brilliant. She promises to choose a suitor after she finishes weaving a burial shroud for Laertes. By day, she weaves. By night, she unweaves. She buys time without surrendering the core issue. It is not flashy. It is not a thunderbolt. It is not a sword fight in the hall. It is disciplined patience under pressure.

That is why Penelope belongs in the leadership section of a compliance odyssey. She reminds us that integrity is not always dramatic. Sometimes it looks like refusing to sign the certification, approve the vendor, bless the transaction, release the report, close the investigation, or accept the explanation simply because everyone is tired of waiting.

The Corporate Translation

Penelope is the leader who understands that time pressure is not the same as good governance. Every organization has Penelope moments. The quarter is closing, and someone wants revenue recognized now. A third party has not cleared diligence, but the business sponsor says the relationship is too important to delay. A certification is due, but the control owner is not comfortable with the evidence. A board report needs to go out, but the investigation findings are still incomplete. A product launch is scheduled, but privacy, security, or regulatory concerns remain unresolved. A customer is demanding speed. A senior executive wants closure. The team is exhausted.

And then someone says the magic words: “Can we just move forward?” That is the sound of the loom beginning to tighten. Penelope’s lesson is not that delay is always virtuous. It is not. Delay can be passive, political, cowardly, or evasive. But some delay is not avoidance. It is governance. The question is whether the organization can tell the difference.

Defensible Delay Is Not Obstruction

In compliance, delay has a bad reputation. That is why compliance is known as The Land of No, populated by Dr. No. Sometimes it is the Department of Business (Non)Development. Whatever the moniker is, this is why business leaders often hear “we need more time” as “compliance is blocking the business.” Sometimes that criticism is fair. Compliance functions can be too slow, too opaque, too academic, or too disconnected from commercial reality. A policy review that disappears into a black hole is not governance. It is bureaucracy with a ticket number.

But there is another kind of delay: defensible delay. Defensible delay has a reason. It has an owner. It has a process. It has a timeline. It identifies the unresolved risk and the information needed to make a decision. It is communicated clearly. It is proportionate to the issue. It protects the company from making a false, rushed, or poorly documented commitment.

Penelope’s loom was not random. It had a purpose. It created time when the available choices were bad. That matters in corporate life. A leader who refuses to approve a questionable vendor is not “being difficult” if the due diligence is incomplete and red flags remain unresolved. A CFO who refuses to sign a certification without adequate support is not “overly cautious.” A compliance officer who asks for more facts before closing an investigation is not “dragging things out.” A privacy officer who pauses a product launch because sensitive data controls are not ready is not “anti-innovation.” Sometimes the most ethical sentence in business is “Not yet.”

Culture Is Built in the Waiting

Corporate culture is often revealed by what happens during delay. When a leader says, “We need more information,” does the organization respect the concern? Or does it start applying pressure?

Does the business provide the missing evidence, or does it complain that Legal is slowing things down? Does management support the control owner, or quietly ask for a more “practical” answer? Does the board ask why the delay is necessary or simply demand that the issue be resolved before the next meeting? Does compliance explain the path forward or hide behind process? These moments shape culture.

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks whether a compliance program works in practice, whether senior and middle management have encouraged or discouraged compliance through their words and actions, and whether compliance personnel have sufficient authority, resources, and access to function effectively. It also asks whether employees have practical guidance and know when to seek advice.

That is Penelope’s world. Culture is not only what the company says about integrity. It is whether the company protects people who slow down a decision for the right reasons. If every delay is treated as disloyalty, employees learn to approve first and worry later. That is not agility. That is ethical surrender in business casual.

Ethical Resilience Under Pressure

Penelope is not powerful in the obvious way. She does not command an army. She does not remove the suitors by force. Her resilience is quieter. She endures pressure without surrendering judgment. That kind of resilience is essential in compliance.

Ethical resilience is the capacity to hold the line when the organization is tired, when the facts are inconvenient, when the deadline is real, and when compromise would be easier. It is the controller who insists on evidence. The manager who escalates a concern before approving the payment. The compliance officer who says the investigation is not complete. The board member who asks whether management’s optimism is supported by testing. The executive who tells the team, “We will not do this the wrong way just because the right way takes longer.”

The DOJ Justice Manual states that prosecutors should evaluate a company’s commitment to fostering a strong culture of compliance at all levels, including how the company incentivizes employee, executive, and director behavior through discipline, complaint handling, and compensation plans. That means ethical resilience cannot depend on heroic individuals. The system must support it.

People must know they will not be punished for raising legitimate concerns. Performance goals must not make ethical delay impossible. Leaders must model patience when facts matter. Governance bodies must ask for evidence, not just reassurance. Compliance must help the business move responsibly, not merely tell it to wait. Penelope’s loom works because she has discipline. A company’s compliance program works because discipline is built into the system.

What a Better Compliance Program Does

A better compliance program helps the organization make disciplined decisions under pressure. It defines which approvals require evidence. It gives control owners authority to withhold certifications when support is inadequate. It builds escalation paths for unresolved risk. It documents exceptions and unresolved issues. It trains leaders on how to respond when employees raise concerns. It tracks aging remediation items. It distinguishes between acceptable risk, unresolved risk, and ignored risk. It also makes delay visible.

If a vendor approval is paused, document the reason. If leadership cannot sign a certification, they should know what evidence is missing. If an investigation remains open, there should be a plan. If a product launch is delayed, stakeholders should understand which control or risk issue must be resolved. That is not bureaucracy. That is governance with receipts.

The Compliance Takeaway

Penelope’s loom is a lesson in ethical leadership. She shows that integrity is not always a grand public stand. Sometimes it is a disciplined refusal to be rushed into a bad decision. Sometimes it is the courage to say, “The facts are not ready.” Sometimes it is the wisdom to buy time without losing the trust of those who are waiting.

For compliance officers and business leaders, the challenge is to build organizations where prudent delay is respected and avoidance is exposed. Do not approve the questionable vendor because everyone is tired. Do not sign the certification because the calendar is unforgiving. Do not close the investigation because the subject is influential. Do not bless the transaction because the business has already promised the outcome.

Weave if you must. Unweave if you must. But know why you are doing it, tell the truth about the risk, and make sure the delay serves integrity rather than fear. That is Penelope’s gift to corporate compliance. She reminds us that sometimes the strongest leader in the room is the one patient enough not to make the wrong decision.

Final Thoughts

Taken together, the leadership lessons from The Odyssey show that corporate compliance is not sustained by slogans, heroes, or good intentions alone. The Trojan Horse reminds us that cleverness without discipline can become a control failure; Athena shows that wise counsel must have real authority, resources, and access to challenge power; and Odysseus demonstrates that even brilliant, high-performing leaders can become compliance risks when success becomes a shield from scrutiny.

Telemachus then carries the lesson into succession, showing that governance must survive the absence of the indispensable leader, with authority, control, ownership, and escalation clearly embedded into the business. Penelope completes the leadership arc by reminding us that integrity under pressure is often quiet, patient, and disciplined: the willingness to say “not yet” when facts are incomplete, risks are unresolved, and everyone else wants to move forward. Together, these stories teach that ethical leadership is not simply about winning the battle or reaching Ithaca; it is about building a compliance culture strong enough to resist shortcuts, challenge heroes, survive transitions, and hold the line when pressure is highest.