Categories
Blog

UM Cheating Scandal Part 1: The Background Facts Underlying the NCAA Violations

In August 2025, the NCAA released its long-awaited Report on infractions committed by and for the University of Michigan football program. For compliance professionals, this case should be viewed not merely as a college sports story but as a case study in organizational misconduct, leadership failure, and cultural breakdown. Just as an FCPA enforcement action lays bare how companies slip into non-compliance, this NCAA decision reveals how one of the country’s premier football programs allowed systemic misconduct to flourish.

This week, in a five-part series, I will explore the case in detail. Today, in Part 1, we will review the background facts: what happened, who was involved, and how the NCAA investigation unfolded. In Part 2, we will move beyond the facts to examine the lack of a culture of compliance inside Michigan football. In Part 3, we’ll discuss the violations, penalties, and key lessons for compliance professionals. In Part 4, we will explore the consequences when regulators, such as the NCAA, become ineffective. In Part 5, we will explore lessons learned for the corporate compliance professional.

The Scheme’s Architect: Connor Stalions

Every corruption case has its “architect,” and here that title belongs to Connor Stalions. A former U.S. Naval Academy graduate and Marine, Stalions became obsessed with signal decoding, the football equivalent of corporate espionage. What began as a volunteer role with Michigan evolved into a full-time staff position, with his primary job being not recruiting, as his title suggested, but intelligence gathering.

Between 2021 and 2023, Stalions organized an extensive off-campus, in-person scouting operation. Using a network of acquaintances, interns, and even players’ friends, he orchestrated the purchase of tickets to opponents’ games, positioned people in prime seats to film sidelines, and then used that footage to decipher signals.

The scale was stunning. Across three seasons, there were 56 instances of scouting across 52 contests involving 13 opponents. Stalions even disguised himself on the sideline of a Central Michigan game in full coaching gear. He spent upwards of $35,000 on tickets in a single year, often buying burner phones and paying for travel for his “KGB” network of helpers.

He maintained elaborate records, including a “Master Chart” of games, a Google calendar of assignments, and “game day sheets” cataloging thousands of opponent signals. This was not a one-off corner-cutting; it was a fully designed intelligence apparatus.

For compliance officers, this resonates with what we see in corporate scandals: low-level staffers who are empowered and even celebrated for gaming the system, building shadow operations, and producing results that leadership quietly benefits until the scheme explodes into public view.

Beyond Scouting: Recruiting Inducements and Communications

The NCAA’s investigation did not stop at the scouting scheme. It also uncovered impermissible recruiting inducements and contacts. Assistant Coach Steve Clinkscale drove a recruit and his parents to dinner and paid for their meals, provided gear, and even tried to secure “blue check” Instagram verification for another recruit. Denard Robinson, a Michigan football legend turned staffer, also handed out bags of gear. Other inducements included charitable donations to the family of a recruit.

In another violation, Assistant Coaches Jesse Minter and Chris Partridge exchanged nearly 100 impermissible text messages with a prospect before the allowable date. The rules here are clear: no electronic communication until a prospect’s junior year. Yet the coaches went forward anyway, later excusing themselves as “confused about the player’s age”.

Again, this will sound familiar to compliance officers. How many corporate bribery cases involve “hospitality” that turns into improper meals or “business development” that is, in fact, disguised inducement? How many sales managers try to explain away improper payments by claiming they misunderstood the rules?

Leadership Failures: Jim Harbaugh’s Responsibility

The NCAA placed significant responsibility on then-Head Coach (and now San Diego Charger Head Coach) Jim Harbaugh. Under NCAA rules, the head coach is presumed responsible for creating a culture of compliance and monitoring staff. Harbaugh failed in both respects. The decision was blunt: “Harbaugh did not embrace that responsibility. Harbaugh and his program had a contentious relationship with Michigan’s compliance office, leading coaches and staff members to act, at times, with disregard for the rules”.

In practice, this meant Harbaugh either knew and ignored, or intentionally avoided knowing, what his staff was doing. As the record showed, staff referred to compliance as “true scum of the earth,” while Harbaugh awarded Stalions a game ball for his signal-stealing efforts. Whether or not he knew the full scope, the culture was one of indifference, if not hostility, to rules.

For corporate leaders, this is a textbook “tone at the top” failure. Regulators have made clear that leaders are responsible not only for their own conduct but for the culture they set. Harbaugh’s failure mirrors what the DOJ calls “failure to promote a culture of compliance.”

Failures to Cooperate and Obstruction

The misconduct did not stop when the NCAA came knocking. In fact, some of the most damning behavior occurred after the investigation began.

  • Connor Stalions destroyed his phone and hard drives, bragging they were at the bottom of a pond. He instructed interns to delete texts, and even urged a student-athlete to “lie your ass off” to investigators.
  • Jim Harbaugh refused to turn over phone records or sit for interviews once he left for the NFL.
  • Sherrone Moore, then an assistant, deleted 52 text messages with Stalions the day the news broke. He later admitted it was an “emotional reaction”.
  • Denard Robinson gave false or misleading answers about whether he handed out gear.

The NCAA viewed these failures to cooperate as Level I violations, some of the most serious possible. For compliance officers, the parallel is unmistakable. In corporate investigations, obstruction , destroying documents, deleting emails, misleading investigators,  is often what turns a bad case into a catastrophic one.

Repeat Violator Status

Perhaps the most damning aspect of this case was Michigan’s history. The 2025 case overlapped with a 2024 infractions decision, also involving the football program, where violations occurred during the COVID dead period. That case resulted in probation, recruiting restrictions, and suspensions. Now, less than a year later, Michigan was back before the Committee on Infractions. As a result, both the university and Harbaugh were deemed repeat violators (recidivists in the compliance world), triggering higher penalties.

For compliance professionals, this is the equivalent of a company that resolves an FCPA matter, pledges reform, and then shows up again within five years. Regulators view such behavior harshly. Once you’ve been given a chance to reform, repeated violations suggest systemic problems and leadership indifference.

The NCAA’s Case Summary

To summarize the background facts:

  • Impermissible scouting: 56 instances of in-person, off-campus scouting across three seasons.
  • Recruiting inducements: meals, gear, transportation, and social media favors for prospects.
  • Improper communications resulted in nearly 100 premature text messages.
  • Leadership failures: Harbaugh’s lack of responsibility and tone at the top.
  • Failures to cooperate: destruction of evidence, deletions, and false statements.
  • Repeat violator status: back-to-back major infractions cases within two years.

As with an SEC or DOJ enforcement action, the facts reveal a program where non-compliance was not incidental but systemic, and where leadership did little to prevent or even detect misconduct.

Why Compliance Professionals Should Care

At first glance, one might dismiss this as a sports story. But for compliance officers, this case is highly instructive. It demonstrates:

  • How schemes are often run by ambitious “low-level” staff but tolerated at higher levels.
  • How small inducements such as meals, gear, favors can constitute serious violations.
  • How leadership failures define culture.
  • How obstruction magnifies penalties.
  • How repeat violations eliminate credibility with regulators.

These are not just lessons for athletics; they are lessons for corporate compliance across industries. The University of Michigan football infractions case offers a rich factual record, but facts alone do not explain why violations occurred. For that, we must examine the culture.

In Part 2 of this series, I will explore how the Michigan football program created an environment where compliance was unwelcome, resisted, and actively undermined. As the NCAA decision made clear, the Chief Compliance Officer did everything she could — but the culture of football won the day. For compliance professionals, that is the heart of the story: the facts expose the violations, but the culture explains them.

Ed. Note: As most of my readers know, I am a UM Law graduate. Now we have UM winning a National Championship, the same year they were cheating in college football games. Did its cheating help win games? About as much as the Houston Astros’ trash can beating, sign-stealing did to help them win the AL Pennant back in 2017. I went to the University of Texas for my undergraduate degree, and now all I need for UT to become embroiled in a cheating scandal the first year they will win the National Championship since Vince Young and the win over USC in 2006, and I will have the trifecta of my teams cheating to win ‘the Big One’. (I am also a huge Dallas Cowboys fan, but there is no chance the Cowboys will ever win a championship as long as Jerry Jones runs the club, so no worries, Cowboy cheating and about moving to a Quad.)
Categories
Sunday Book Review

Sunday Book Review: August 24, 2025, The More Books from the Ethicsverse Library Edition

In the Sunday Book Review, Tom Fox considers books that would interest the compliance professional, the business executive, or anyone who might be curious. It could be books about business, compliance, history, leadership, current events, or anything else that might interest Tom. Today, we continue our August exploration of four books from the Ethicsverse Library, all curated by Ethico.

Resources:

The Ethicsverse Library

The Sunday Book Review was recently honored as one of the Top 100 Book Podcasts.

Categories
10 For 10

10 For 10: Top Compliance Stories For the Week Ending August 23, 2025

Welcome to 10 For 10, the podcast that brings you the week’s Top 10 compliance stories in one podcast each week. Tom Fox, the Voice of Compliance, brings to you, the compliance professional, the compliance stories you need to be aware of to end your busy week. Sit back, and in 10 minutes, hear about the stories every compliance professional should be aware of from the prior week. Every Saturday, 10 For 10 highlights the most important news, insights, and analysis for the compliance professional, all curated by the Voice of Compliance, Tom Fox. Get your weekly filling of compliance stories with 10 for 10, a podcast produced by the Compliance Podcast Network.

Top stories include:

  • WADA punches its weight, says Sri Lanka is not compliant. (WADA website)
  • Is audio quality a compliance issue? (CX Today)
  • Air cargo compliance challenges. (Cargo Facts)
  • Citibank investigates the Chief Wealth Officer. (Bloomberg)
  • More NYC Mayor associates to face corruption charges. (NYT)
  • CVS ordered to pay $290MM in whistleblower suit. (Reuters)
  • Advice of counsel without the advice. (Reuters)
  • No More Mr. Nice Guy-The boss is back. (FT)
  • New Orleans Mayor and lover charged with corruption. (NYT)
  • Senegal’s President exempts himself from ABC laws. (Africa News)

You can check out the Daily Compliance News for four curated compliance and ethics-related stories each day, here.

Connect with Tom 

Instagram

Facebook

YouTube

Twitter

LinkedIn

You can purchase a copy of my new book, Upping Your Game, on Amazon.com

Categories
Regulatory Ramblings

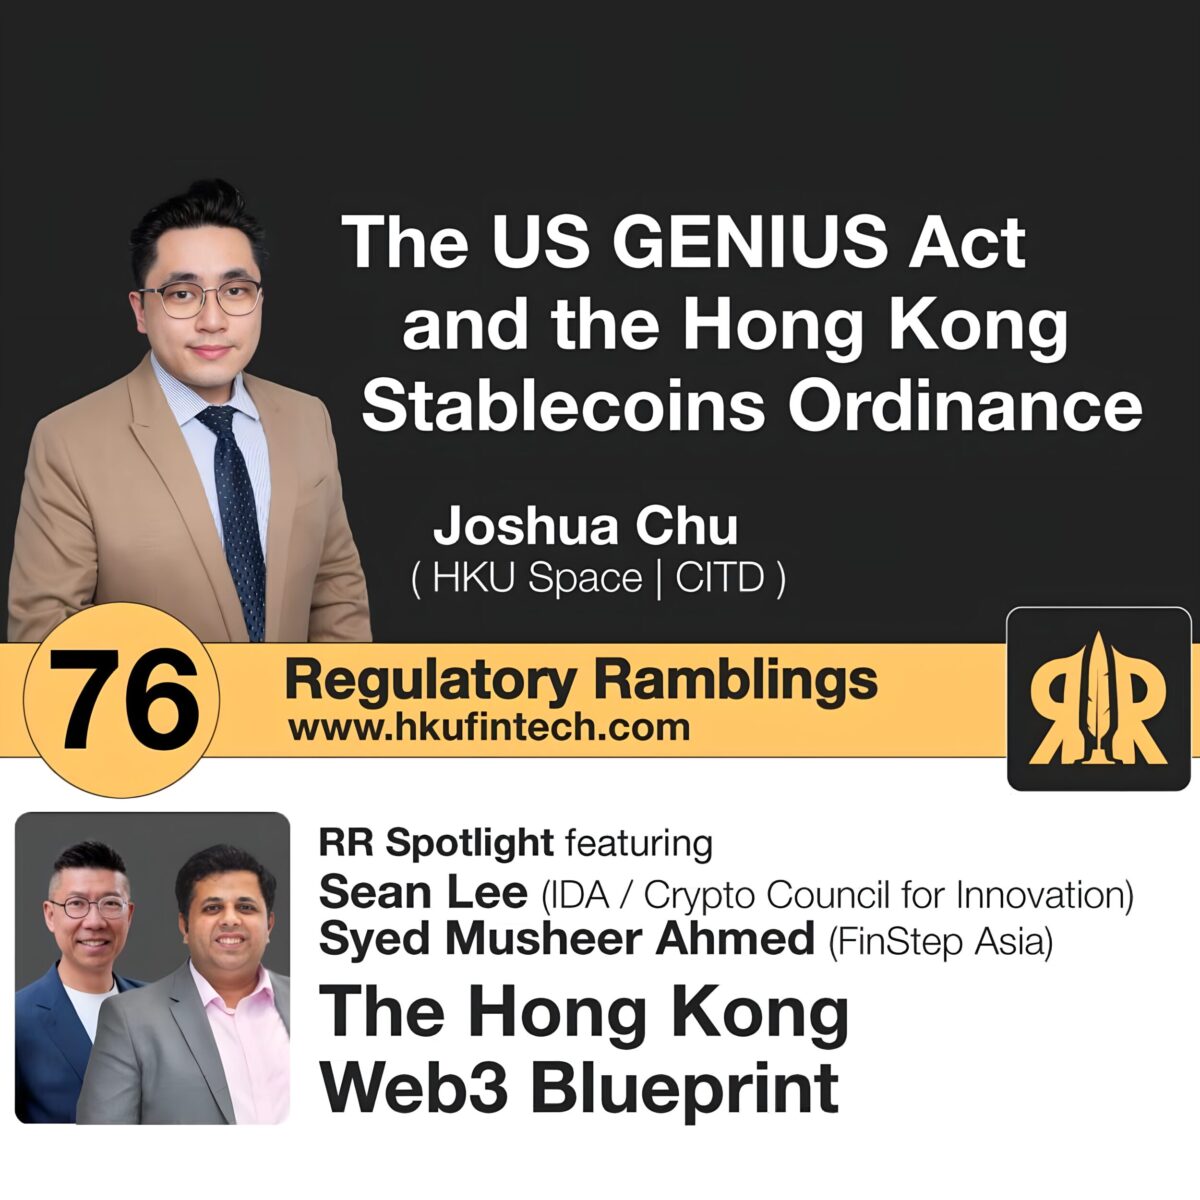
Regulatory Ramblings: Episode 76 – The Digital Future: The US GENIUS Act and Hong Kong Stablecoins Ordinance // The Hong Kong Web3 Blueprint: Building a Web 3 International Financial Hub Report

The common theme for this episode is FinTech and Web3 writ large – with an eye towards digital assets and virtual currency.

In today’s spotlight segment, we’ll be speaking with a returning guest and a dear friend of the program – Syed Musheer Ahmed of Hong Kong-based FinStep Asia on the recently disseminated “Hong Kong Web3 Blueprint: Building a Web 3 International Financial Hub” report. Joining Musheer is Sean Lee, co-lead of Web3 Harbour’s Policy Committee and one of the key leaders of the Blueprint task force.

Following that, we’ll be chatting with local lawyer Joshua Chu on the recently passed US GENIUS Act and what it means for making the US a stablecoin hub.

Joshua Chu

Joshua Chu is a prominent Hong Kong lawyer in all matters fintech and crypto, and a prolific writer. His opinion and insights are much sought after by the local press and correspondents of major foreign news organizations operating in the city. You can often hear him at his most candid on the radio at RTHK. He is also co-chair of the Hong Kong Web 3 Association and legal advisor to the Hong Kong Blockchain Association.


Syed Musheer Ahmed

Syed Musheer Ahmed is managing director of FinStep Asia – a firm he founded six years ago. With over 18 years of extensive experience as an ecosystem builder in the realms of capital markets, fintech, and virtual assets, including a decade as a global markets trader, he came to Hong Kong to attain his MBA from the University of Hong Kong and London Business School’s joint program.
A self-described “fintech ballerina,” since 2016, Musheer has contributed extensively to building the region’s fintech and virtual assets ecosystem, particularly as the co-founder and concurrent board member and the inaugural general manager of the Fintech Association of Hong Kong (FTAHK).

He has also done a stint as a regulator. Beyond his many contributions to the territory’s fintech regulatory policy during his tenure with the FTAHK, from October 2022 to January 2024, he served as a financial markets risk assurance lead with the Virtual Assets Regulatory Authority in Dubai.

Sean Lee

Sean Lee, Co-founder of IDA, a digital asset technology company, aims to lead the widespread adoption of blockchain finance and empower Belt and Road businesses to integrate seamlessly between Web2 and Web3.  Previously, Sean was the CEO of the Algorand Foundation, where he led the layer-1 protocol to achieve a top-10 network valuation of over $10 billion under his leadership.

Sean has active engagements with global regulators and policymakers as a Senior Advisor for the Crypto Council for Innovation in regulatory advocacy and advancing the transformative potential of digital assets, and APAC policy advisor for the Stablecoin Standard.  Sean is also an elected member of the Hong Kong Government’s Cyberport Entrepreneurship Committee Advisory Group and a Forbes Digital Asset contributor.


Discussion:

The conversation starts with a discussion of the Hong Kong Web3 Blueprint Report. Musheer and Sean share with Regulatory Ramblings host Ajay Shamdasani that the document should be seen as a roadmap for hastening blockchain development in the territory. For that purpose, Web3 Harbour joined forces with PwC Hong Kong to launch five action groups this August on stablecoins, funds, and other critical segments.

Ultimately, it is a call for more action across various aspects, from investment to talent, policy, infrastructure, and standards,  to accelerate the development of Web 3.0 in the SAR.

The report highlights the “transparency, security, and user empowerment” of decentralization.

As the SCMP put it: “The blueprint seeks to leverage what it calls ‘Web3 superpowers’ through the development of ‘five key enablers’: talent, market infrastructure, standards, regulation, and funding and economic contribution. It calls on participants to focus on open finance, trade finance, capital markets, asset management, and carbon markets.

The report was compiled with input from Web3 Harbour members and other industry stakeholders.

Web3 Harbour chairman Gary Liu, formerly CEO of the Post, said greater private-public collaboration was among its goals, but it was primarily a guide for where the private sector should focus its efforts.

To that end, the report should not be seen as just a document- it is a blueprint for transformation, the guests say. From regulation and standards to infrastructure and talent, the Hong Kong Web3 Blueprint identifies the key enablers that will shape Hong Kong’s position as a global Web3 finance hub.

Hong Kong has distinct advantages to capture a significant part of the global Web3 opportunity, but the question is, how do we get there? asks Musheer and Sean. They also share what prompted them to write the report now, their key observations and conclusions, and what policy outcomes they advocate.

Ultimately, talent, infrastructure, standards, regulation, and funding are the critical enablers identified in the Web3 Blueprint that are crucial to positioning Hong Kong as a Web3-enabled international financial centre. The document outlines how Web3 technologies can drive sustainable innovation, create economic growth, and raise the territory’s digital finance leadership on the world stage.

Following that, we discussed the enactment of the new GENIUS Act in the US in late July with Joshua. In what was labelled “Crypto Day” during that country’s recent “Crypto Week,” the U.S. House of Representatives first passed the CLARITY market structure bill and then the GENIUS Act on July 18 – the latter of which was signed by President Trump. These moves by Congress were seen as historic steps forward in the regulation of virtual assets in the United States – or as one pundit put it: “Crypto’s time has come.”

The US legislation is the first standalone bill aimed at providing clarity for the growing cryptocurrency ecosystem – particularly the regulation of stablecoins.

According to TRM Labs, stablecoins now represent over 60% of all crypto transaction volume – up from just 35% two years ago. More than 90% of fiat-backed stablecoins in circulation are pegged to the US dollar. Although TRM estimates that 99% of stablecoin activity is licit, their speed, scale, and liquidity have made them appealing for illicit uses, including ransomware payments, fraud, and terrorist financing.​

The GENIUS Act (Guiding and Establishing National Innovation for U.S. Stablecoins) establishes reserve requirements for stablecoin issuers, alongside consumer protection measures and anti-money laundering (AML) provisions.

These provisions aim to provide greater stability and security for stablecoin markets, ensuring they are better integrated into the U.S. financial system. This marks a key moment for the regulatory framework governing digital assets, as the U.S. works to balance innovation with risk management.

As for the CLARITY Act, it addresses broader market structure issues within the cryptocurrency space. The Senate is working on its market structure bill. After both chambers have acted, they will conference to reconcile their differences and finalize a version of the CLARITY bill that will move forward – likely this fall.​

The passage of both bills reflects a significant effort to provide clear regulatory guidance for the crypto market, helping to address the growing need for oversight as the industry continues to expand.

At the same time, half a world away in Hong Kong, the city’s Stablecoins Ordinance (Cap. 656) (Stablecoins Ordinance) and related implementation guidelines issued by the Hong Kong Monetary Authority commenced operation on 1 August 2025 – with a transitional period granted solely for issuance purposes.​

This new regime is touted as a significant milestone for Hong Kong’s growing digital assets market. According to King & Wood Mallesons: “It is relevant to institutions that wish to engage in the primary market issuance of fiat-referenced stablecoins, as well as other secondary market transactions in or involving Hong Kong. Even if you are outside Hong Kong, you should pay attention to the restrictions imposed under the Stablecoins Ordinance for any stablecoin-related activities with a Hong Kong nexus.”

At a glance, the Hong Kong Stablecoins Ordinance regulates:​

– Issuers of stablecoins and the structure of a stablecoin itself.

– Offers of stablecoins.

– Related market integrity and conduct matters.

The regime took effect on 1 August 2025, with a transitional period for issuance only.

The Stablecoins Ordinance regulates “specified stablecoins,” which are stablecoins (ie, a cryptographically secured digital representation of value) that purport to maintain a stable value with reference wholly to one or more official currencies or other HKMA-specified units of account or stores of economic value (see section 4 of the Stablecoins Ordinance).

While this is a rather technical definition, it essentially captures:

– a stablecoin linked to an “official currency”; and

– a stablecoin linked to other “units of account” or “stores of economic value”, in each case, as designated by the HKMA (by notice published in the Gazette).

To date, the HKMA has not specified any such units of account or stores of economic value, but we expect they may include commodities such as gold.

Joshua delineates the longer-term implications for our region and the world as a result of the above regulatory developments in Hong Kong and the US.

Regulatory Ramblings podcasts is brought to you by The University of Hong Kong – Reg/Tech Lab, HKU-SCF Fintech Academy, Asia Global Institute, and HKU-edX Professional Certificate in Fintech, with support from the HKU Faculty of Law.

Useful links in this episode:

You might also be interested in:

Connect with RR Podcast at:

LinkedIn: https://hk.linkedin.com/company/hkufintech 
Facebook: https://www.facebook.com/hkufintech.fb/
Instagram: https://www.instagram.com/hkufintech/ 
Twitter: https://twitter.com/HKUFinTech 
Threads: https://www.threads.net/@hkufintech
Website: https://www.hkufintech.com/regulatoryramblings 

Connect with the Compliance Podcast Network at:

LinkedIn: https://www.linkedin.com/company/compliance-podcast-network/
Facebook: https://www.facebook.com/compliancepodcastnetwork/
YouTube: https://www.youtube.com/@CompliancePodcastNetwork
Twitter: https://twitter.com/tfoxlaw
Instagram: https://www.instagram.com/voiceofcompliance/
Website: https://compliancepodcastnetwork.net

Categories
Data Driven Compliance

Data Driven Compliance – The Failure to Prevent Fraud Offense: Insights for US General Counsels with Mike DeBernardis

Welcome to Season 2 of the award-winning Data Driven Compliance. In this new season, we will look at the new Failure to Prevent Fraud offense. Join host Tom Fox as we explore this new law and how to comply with it through the lens of data-driven compliance. konaAI sponsors this podcast. In this episode of Season 2, Tom Fox is joined by Mike DeBernardis, Partner at Hughes Hubbard & Reed.

In this episode, Tom and Mike look at the specific offenses listed in the Failure to Prevent Fraud Offense and translate them into US-legalese. They discuss common misunderstandings among US lawyers, the broad jurisdictional scope, and specific fraud types under UK law, such as fraud by false representation, failure to disclose information, and abuse of position. They also emphasize the importance of risk assessments for US companies with UK operations to ensure compliance and avoid legal repercussions, and also touch on the potential geopolitical implications and the necessity of having robust policies and procedures to prevent fraud. 

Key highlights:

  • Fraud by False Representation
  • Fraud by Failing to Disclose Information
  • Fraud by Abuse of Position and Obtaining Services Dishonestly
  • Corporate Fraud: Participation, Accounting, and Trading
  • Risk Mapping and Compliance Strategies

Resources:

⁠Hughes, Hubbard & Reed⁠

Mike DeBernardis on ⁠LinkedIn⁠

⁠New Considerations for Companies with U.K. Ties: Home Office Issues Guidance to Organisations on the Offence of Failure to Prevent Fraud⁠

⁠konaAI⁠, a Covasant company

Click here for konaAI White Paper Rethinking Compliance: Practical Steps for Adapting to the UK’s New Fraud Legislation

Connect with Tom Fox on ⁠LinkedIn

Categories
12 O’Clock High-a podcast on business leadership

12 O’Clock High: Navigating Life’s Challenges: A Journey from Military Service to Mental Health Advocacy with Nick Padlo

12 O’Clock High, an award-winning podcast on business leadership, brings together stories from history, the arts, sports, movies, research, and current events to consider leadership lessons. In this episode, Tom Fox speaks with Nick Padlo, a mental health advocate and Founder and CEO of Sophros Recovery, about his diverse professional journey.

Growing up in Jacksonville, Florida, Padlo attended West Point and served in the U.S. Army, during which he witnessed significant combat. Post-military, he attended business school at Stanford and founded a pet cremation business. He also shares his struggles with alcohol and substance abuse and his path to recovery, touching on the leadership lessons he learned from the military, the importance of asking for help, and how he integrates his experiences to aid others through ROS Recovery. The discussion includes building resilience, empathy, and trust within a team, family involvement in recovery, and advice for business leaders facing personal and professional challenges.

Key highlights:

  • Nick Padlo’s Military Background
  • Transition to Civilian Life and Business Ventures
  • Personal Struggles and Path to Recovery
  • Leadership Lessons from the Military
  • Hitting Rock Bottom and Seeking Help
  • Incorporating Experiences into ROS Recovery
  • Building Resilience, Trust, and Empathy
  • Family’s Role in Recovery
  • Advice for Business Leaders

Resources:

Follow Nick Padlo on LinkedIn

Check out Sophros Recovery Website

Visit and follow Sophros Recovery on:

Facebook

LinkedIn

Instagram 

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
AI Today in 5

AI Today in 5: August 22, 2025 The Angst Episode

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the AI Today In 5. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest about AI.

Top AI stories include:

  • Responsible AI in action. (PeopleMatters)
  • State AI regulatory initiatives drive SB angst. (CFO Dive)
  • Balancing complexity and technology. (Financial IT)
  • AI and predictive Analytics are top compliance concerns for investment advisors. (IAA Today)
  • Is ChatGPT 5’s reception worrying? (Bloomberg)
Categories
Compliance Tip of the Day

Compliance Tip of the Day – Using AI to Embed Your Compliance Program

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide you with bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today, we conclude our 5-part series on using compliance in a best practices compliance program by considering how to embed compliance into your business operations with the help of AI.

For more on this topic, check out The Compliance Handbook, a Guide to Operationalizing your Compliance Program, 6th edition, which LexisNexis recently released. It is available here.

Categories
Daily Compliance News

Daily Compliance News: August 22, 2025, The WADA Returns Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

  • WADA punches its weight, says Sri Lanka is not compliant. (WADA)
  • Is audio quality a compliance issue? (CXToday)
  • Air cargo compliance challenges. (Cargo Facts)
  • Citibank investigates the Chief Wealth Officer. (Bloomberg)

You can donate to flood relief for victims of the Kerr County flooding by going to the Hill Country Flood Relief here.

Categories
Blog

Using AI to Embed Compliance into Business Operations

Ed. Note: This week, we present a week-long series on the use of GenAI in a best practices compliance program. Additionally, for each blog post, I have created a one-page checklist for each article that you can use in presentations or for easier reference. Email my EA Jaja at jaja@compliancepodcastnetwork.net for a complimentary copy.

Compliance programs have long wrestled with a central challenge: how to move from “bolt-on” to “built-in.” Too often, compliance has been perceived as an overlay, a set of policies and reviews that operate parallel to business activity. The Department of Justice has repeatedly emphasized that compliance should be integrated directly into operations, not treated as an afterthought.

Generative AI offers compliance professionals a new tool to achieve this, as Elisa Farri and Gabriele Rosani argue in an HBR article How AI Can Help Managers Think Through Problems, that AI is not just a productivity enhancer but a thought partner. Instead, it is capable of helping leaders frame problems, test assumptions, and engage in structured dialogues that improve decision-making.

I aim to utilize their article to support compliance officers in leveraging AI to enhance our ability to embed compliance into business processes more effectively. Today, I conclude my five-part blog post series on using GenAI in compliance to explore how AI can assist in building compliance into the business and what it means for the future of compliance programs. I also provide five key takeaways for compliance professionals on how to do so.

1. AI as a Co-Thinking Partner for Embedding Compliance into Workflows

One of the article’s most powerful insights is the concept of “co-thinking”; AI as a partner in structured dialogue rather than just a tool for quick answers. For compliance, this is transformative. Imagine using AI not simply to draft a policy, but to help you think through how that policy should be embedded in day-to-day operations.

For instance, when designing a gifts-and-entertainment approval process, AI can walk compliance through stakeholder perspectives: What does sales need? What would regulators expect? What friction will finance raise? By simulating these perspectives, AI helps compliance professionals design workflows that are practical and embedded, rather than abstract and detached.

This approach also makes compliance more proactive. Instead of reacting to risks after violations occur, AI-enabled co-thinking allows compliance to anticipate where policies may clash with business objectives and design operational solutions upfront. The compliance lesson is to treat AI as a structured dialogue partner to design compliance that lives inside the workflow, policies, and processes that are not just documented but operationalized.

2. Enhancing Stakeholder Engagement Through AI Simulations

Embedding compliance into business operations requires more than rules; it requires buy-in. The article highlights how AI can role-play different stakeholders, challenging managers to anticipate reactions. Compliance can use this capability to stress-test initiatives before rollout.

Suppose compliance is introducing a new due diligence system for third-party onboarding. AI can simulate how procurement might respond (“slows down vendor onboarding”), how business development might object (“hurts competitiveness”), and how regulators might evaluate (“strong demonstration of risk-based management”). This multi-stakeholder dialogue allows compliance teams to refine both process design and messaging before rollout.

The implication for compliance programs is clear: embedding compliance requires deep cultural alignment. AI makes it possible to test and rehearse that alignment at scale, reducing resistance and building smoother adoption. The compliance lesson is to use AI simulations to bring stakeholder voices into the design process, ensuring compliance is not bolted on but built with empathy for business realities.

3. AI-Assisted Root Cause Analysis Strengthens Business Integration

Compliance programs are expected to conduct root cause analysis after misconduct, but too often these reviews remain siloed. AI-enabled co-thinking helps expand root cause analysis into an exercise that strengthens business operations.

For example, when analyzing repeated travel and expense violations, AI can guide compliance through structured questions: Were training gaps to blame? Were approval workflows too weak? Were sales incentives misaligned? Then, critically, AI can help map remediation back into operations—tightening finance approvals, adjusting incentive structures, and embedding compliance flags directly into expense systems.

This is not about AI making the decision. It is about AI helping compliance think through operational integration of lessons learned. Instead of merely complying with regulations by writing a report that sits on a shelf, the outcome becomes operational adjustments inside business processes. The compliance lesson (or rather, perhaps implication) is that the DOJ expects compliance programs to prevent recurrence through systemic fixes. AI co-thinking can ensure those fixes are operational, not theoretical.

4. Scaling Compliance Culture and Mindset Shifts Across the Organization

The article notes how AI can be used to coach managers through mindset shifts, helping them reflect on new behaviors and practices. Compliance can use the same approach to embed cultural expectations directly into business teams. For example, AI can be configured as a compliance coach embedded in daily tools, guiding managers through ethical dilemmas, prompting reflection during approval requests, or reinforcing company values during project planning. Instead of compliance being external and episodic, it becomes internal and continuous.

This democratizes compliance development. A frontline manager in Asia can interact with AI that reinforces compliance culture in real time, rather than waiting for annual training or sporadic compliance visits. It also gives compliance leaders data on where employees are struggling, revealing cultural gaps that can be addressed systemically.

The implication is that embedding compliance is not just about systems but about mindset. AI can make culture-building a daily, distributed activity rather than a centralized, one-time effort.

5. Ensuring Human Judgment Remains Central in AI-Enabled Compliance

Finally, while AI can enhance problem-solving and integration, the article underscores that co-thinking only works when humans stay actively engaged. Compliance cannot abdicate responsibility to machines. This has profound implications for compliance programs. AI can help frame problems, simulate stakeholders, and propose operational fixes, but it cannot weigh reputational risk, interpret regulatory expectations, or balance competing global obligations. Those decisions require human judgment.

The key is balance: AI accelerates and deepens thinking, but compliance leaders must build governance frameworks to ensure outputs are reviewed, validated, and contextualized. Embedding compliance into business operations does not mean letting AI run the show; it means letting AI augment human reasoning so that compliance becomes more practical, strategic, and defensible.

The compliance lesson, based on both the DOJ’s FCPA Resource Guide and the 2024 ECCP, is clear that compliance must be risk-based, well-resourced, and continuously improved. AI helps compliance think through integration, but humans remain accountable for ensuring it meets regulatory standards and ethical expectations.

AI as a Pathway to Embedded Compliance

The future of compliance is embedded, not bolted on. DOJ expects it. Boards demand it. Employees need it. The challenge is figuring out how to make it real. AI offers compliance professionals a powerful new tool: not as an oracle, but as a co-thinker. By helping compliance frame problems, simulate stakeholders, strengthen root cause analysis, scale cultural coaching, and reinforce human judgment, AI can accelerate the shift from compliance as oversight to compliance as an integrated business practice.

The call to action is simple: use AI not just to make compliance faster, but to make compliance inseparable from business. That is how compliance earns trust, drives culture, and meets regulatory expectations in the age of AI.