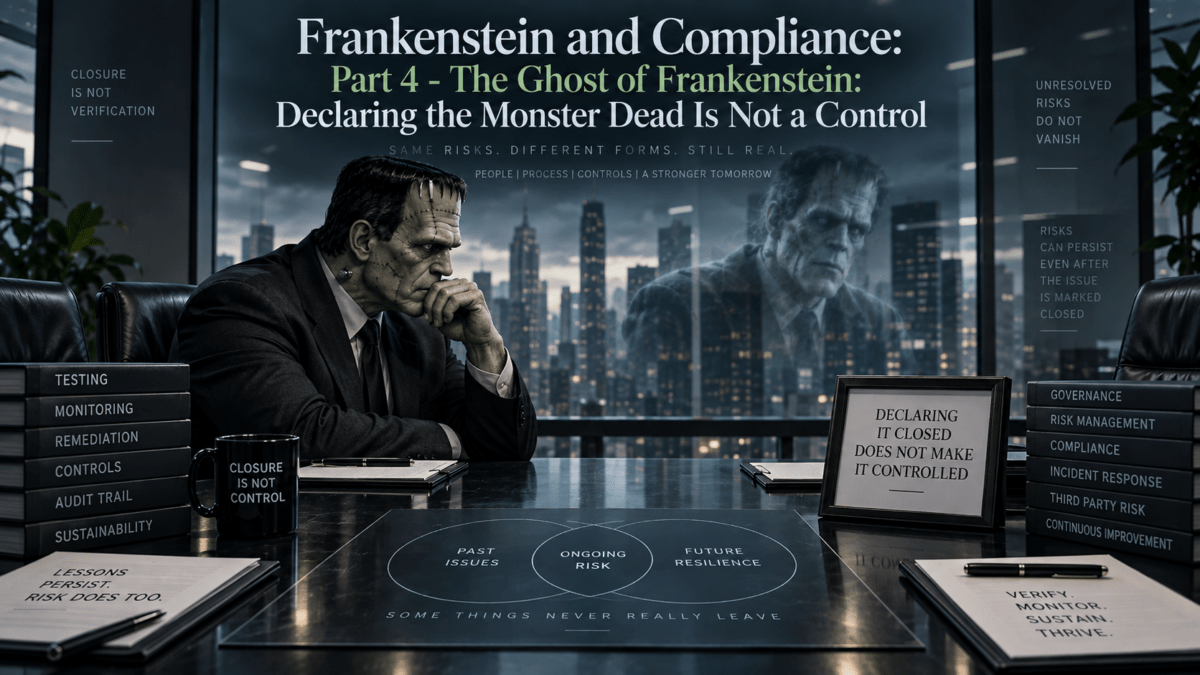
Ed. Note: This month, on his podcast series Popcorn and Compliance, Tom Fox dives deep into the first five Frankenstein movies. Over October, Tom Fox will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolf Man. This blog post accompanies the podcast series.
The first three Frankenstein films trace a recognizable progression in compliance. Frankenstein examined innovation without adequate governance. Bride of Frankenstein explored what happens when leadership recognizes a risk but lets pressure and rationalization override judgment. Son of Frankenstein shifts to inherited risk and the responsibility of new leadership to address problems its predecessors created. The Ghost of Frankenstein (1942) raises the next question. What happens when the organization believes the problem has already been addressed?
By the fourth film, no credible argument suggests that Frankenstein’s Monster represents an unknown risk. Communities have confronted him. Members of the Frankenstein family have attempted to control him. The consequences are well established. Yet the Monster remains. This time, Ygor, again played by Bela Lugosi, brings the Monster, now played by Lon Chaney Jr., to Ludwig Frankenstein, Henry Frankenstein’s other son. Ludwig initially wants nothing to do with his family’s legacy. He eventually concludes that he can solve the problem through a brain transplant. The proposed solution appears technically sophisticated. It is also compromised when Ygor and Ludwig’s colleague Bohmer secretly substitute Ygor’s brain for the intended brain.
For corporate compliance professionals, The Ghost of Frankenstein is a case study in remediation and control effectiveness. Companies routinely investigate misconduct, revise policies, conduct training, implement corrective actions, and close audit findings. Those activities matter, but they don’t prove the underlying risk has been reduced. The relevant compliance question is not whether management completed the remediation plan. It is whether the remediation worked.
Closure Is an Administrative Status
Compliance, Internal Audit, Legal, Finance, and business management are familiar with corrective-action plans. An issue is identified. Management develops remediation. Actions are assigned. Deadlines are established. Policies may be revised, systems changed, training delivered, or controls added. Eventually, the required actions are completed, and the finding is marked closed. That process is not inherently wrong. Organizations need a disciplined method for tracking remediation. The risk comes when administrative closure becomes confused with risk reduction.
Suppose an investigation finds that employees circumvented a third-party approval requirement. Management revises the policy and retrains the business. Both actions may be appropriate. They also may have little effect if the original problem arose because sales targets encouraged employees to bypass the process and local managers routinely approved exceptions. The policy was not necessarily the root cause. Training was not necessarily the solution. A closed action item therefore tells management that a required activity occurred. It does not automatically establish that the control environment changed. That distinction is central to compliance program effectiveness.
Start With Root Cause
Ludwig Frankenstein approaches the Monster as a technical problem. Replace the brain, and the problem is solved. Compliance can fall into the same trap with remediation. Organizations sometimes start corrective action before they have adequately identified why the failure occurred. Effective remediation should begin with root-cause analysis.
Suppose a salesperson makes an improper payment through a third-party distributor. The immediate facts may be straightforward. The employee violated policy, the payment was inappropriate, and the third party was involved. A root-cause analysis goes further.
Why was the third party selected? Was due diligence adequate? Were red flags identified? Did anyone override the process? Was the compensation structure unusually aggressive? Did management communicate unrealistic sales expectations? Were invoices sufficiently detailed? Did Finance question the payments? Had similar issues occurred previously? Did employees believe management would support them if they delayed the transaction? These questions shift the analysis from the individual event to the system that allowed it to happen.
Individual accountability remains important. A company should not use systemic explanations to excuse deliberate misconduct. But disciplining an employee does not repair a control environment. A strong remediation plan addresses both.
Repeat Findings Are Information
Recurring compliance issues should receive particular attention.
- If Internal Audit repeatedly identifies the same control weakness, that is information.
- If multiple investigations identify similar conduct in the same business unit, that is information.
- If hotline reports repeatedly raise concerns about the same management behavior, that is information.
- If third-party monitoring continually identifies the same documentation gaps, that is information.
Repeat issues may indicate that previous remediation addressed symptoms rather than causes. They may also indicate weak implementation, insufficient resources, inadequate supervision, or management resistance. The CCO should therefore have a mechanism to identify recurrence across data sources.
An audit finding may appear unrelated to a hotline complaint. A hotline complaint may appear unrelated to a third-party exception. A third-party exception may appear unrelated to an investigation. Viewed together, they may demonstrate a common control problem. This is where compliance data becomes more valuable than compliance statistics. The objective is not simply to count investigations, audit findings, policy exceptions, or hotline reports. The goal is to identify patterns that tell management how the organization operates.
Bohmer and Management Override
The brain-transplant sequence provides the film’s strongest internal-control lesson. Ludwig develops a plan to replace the Monster’s brain. Whatever one thinks of the underlying objective, the process is defined, and the outcome is intended. Then Bohmer and Ygor subvert it.
Control isn’t defeated because nobody designed a process. It fails because individuals with access and opportunity manipulate the process. That is management override. Corporate controls often assume authorized individuals will use their authority as intended. That assumption requires testing.
- A manager can approve an expense.
- A finance executive can authorize a journal entry.
- A procurement leader can approve a vendor.
- A senior executive can authorize a policy exception.
- An administrator can change system permissions.
- A business leader can influence a third-party decision.
Those authorities are necessary for business operations. They can also create risk when one individual possesses excessive discretion or when oversight is weak. Segregation of duties, approval thresholds, access controls, audit trails, independent review, exception reporting, and transaction monitoring exist partly to address this problem. For the CCO, the question is not simply whether a control exists. It is whether someone can circumvent it and whether the organization would know.
COSO and the Broader Control Environment
The Ghost of Frankenstein also provides an opportunity to consider the COSO Internal Control Integrated Framework. Controls do not operate in isolation. The control environment establishes expectations, authority, accountability, and standards of conduct. Risk assessment identifies threats to organizational objectives. Control activities translate those risks into specific preventive or detective measures. Information and communication ensure the right people receive relevant information. Monitoring determines whether the system continues to operate effectively.
Compliance failures often occur when organizations focus too narrowly on a single control activity. A company identifies misconduct involving gifts and entertainment, so it lowers approval thresholds. That may be useful.
- But what if managers continue encouraging employees to find ways around the limits?
- What if expense descriptions are vague?
- What if Finance does not review unusual patterns?
- What if senior executives routinely receive exceptions?
- What if employees believe questioning an expense submitted by a powerful executive will damage their careers?
The approval threshold may be well designed. The broader control environment remains weak. This is why compliance should work closely with Internal Audit, Finance, HR, Legal, and business management. Compliance risk rarely fits neatly within one control owner.
Design Effectiveness and Operating Effectiveness
One of the most useful distinctions in controls work is between design effectiveness and operating effectiveness. A control may be well designed. That does not mean it operates effectively. Consider third-party due diligence. The company may have a strong written process requiring risk classification, beneficial ownership review, screening, business justification, approval, contractual protections, and periodic monitoring. On paper, the control appears robust. Then testing reveals that business sponsors routinely submit incomplete information, reviewers approve files without resolving red flags, contracts are signed before diligence is complete, and periodic reviews are months overdue. The control design is not necessarily the problem. It is execution.
Conversely, employees may execute a poorly designed control exactly as instructed, even as it fails to address the relevant risk. Compliance needs to understand both. This matters especially when validating remediation. Management should not simply confirm that a new control was implemented. Someone should determine whether the control is appropriately designed and whether it operates consistently in practice. That is how an organization moves from remediation activity to evidence of effectiveness.
Investigations Should Improve the Program
Investigations represent one of the richest sources of compliance intelligence available to a company. They show where actual conduct differs from expected conduct. Yet organizations sometimes treat investigations primarily as case-management exercises. An allegation arrives, the company investigates, decides whether to substantiate it, takes disciplinary action where appropriate, and closes the matter. That process resolves the case. It does not necessarily improve the compliance program.
For significant matters, a compliance professional should ask what the investigation teaches the organization.
- Did a control fail?
- Was a policy unclear?
- Was supervision inadequate?
- Were incentives relevant?
- Did the reporting system work?
- Was retaliation alleged?
- Were similar concerns raised previously?
- Did management respond appropriately when warning signs appeared?
- Should monitoring change?
- Should the risk assessment change?
The investigation should feed the compliance program. Otherwise, the organization may become very efficient at investigating the same problem repeatedly.
Test the Remediation
Perhaps the most important lesson from The Ghost of Frankenstein is that remediation requires validation. Management implements a corrective action. Someone should return later and determine whether it worked. The timing and depth of testing should depend on risk. A significant control failure may require independent validation by Internal Audit, Compliance testing, or another qualified function. Lower-risk matters may be validated through management review or monitoring. The important point is that the organization should define what success looks like before declaring the remediation effective.
The Compliance Lessons
The Ghost of Frankenstein demonstrates a basic principle of compliance program effectiveness. Activity is not the same as effectiveness. A company can revise a policy, deliver training, add an approval, complete a corrective-action plan, and close an audit finding. Each action may be appropriate. The compliance question is whether those actions changed the risk.
That requires root-cause analysis, well-designed controls, disciplined implementation, monitoring, testing, and accountability. It also requires management to recognize that some failures are not caused by employees misunderstanding the rules. They may result from incentives, authority structures, management override, weak supervision, or a control environment that rewards the wrong behavior.
The goal of remediation is not to demonstrate that the organization did something. It is to demonstrate that the organization learned something and changed accordingly. That is why declaring the Monster dead is not a control. The evidence comes from whether he stays dead.
Our final installment of my Universal Classic Monster Movie Month for 2026 takes the Frankenstein compliance story in a different direction. After four films dealing largely with one persistent risk, Universal brings another major risk into the picture. In Frankenstein Meets the Wolf Man, the issue is no longer simply whether an organization can identify, govern, inherit, or remediate a single compliance problem. It is what happens when independently managed risks begin to interact. For modern companies confronting AI, cybersecurity, privacy, third-party, sanctions, anti-corruption, financial, and operational risks, that may be the most important governance question of all: What happens when the risks we manage separately collide?
For a review of the movie and audio analysis, check out Timothy and Fiona’s take on it in Popcorn and Compliance.