Categories
10 For 10

10 For 10: Top Compliance Stories For the Week Ending December 6, 2025

Welcome to 10 For 10, the podcast that brings you the week’s Top 10 compliance stories in one podcast each week. Tom Fox, the Voice of Compliance, brings you the compliance stories you need to know to end your busy week. Sit back, and in 10 minutes, hear about the stories every compliance professional should be aware of from the prior week. Every Saturday, 10 For 10 highlights the most important news, insights, and analysis for the compliance professional, all curated by the Voice of Compliance, Tom Fox. Get your weekly filling of compliance stories with 10 for 10, a podcast produced by the Compliance Podcast Network. 

This week’s stories include:

  • The US lost over $29bn to fraud, waste, and abuse in Afghanistan. ⁠(USA Today⁠)
  • Does AI portend the end of the law/consulting firm pyramid? ⁠(FT⁠)
  • Will a Civility Oath make lawyers more civil?  ⁠(Reuters)⁠
  • What is the environmental cost of corruption? ⁠(BBC)⁠
  • Lane Kiffin should be nowhere near Ole Miss football. ⁠(WSJ⁠)
  • Police detain former EU top diplomat. ⁠(FT)⁠
  • Massive fraud in aircraft parts uncovered in the UK. ⁠(The Times⁠)
  • Switzerland charges Credit Suisse over Tuna Bond fraud. ⁠(ACAMS)⁠
  • Corruption scandals impact the Chinese Army.  ⁠(Reuters)⁠
  • Former Labour PM convicted of corruption in Bangladesh. ⁠(Independent)⁠

You can check out the Daily Compliance News for four curated compliance and ethics-related stories each day, ⁠here⁠.

Connect with Tom 

⁠Instagram⁠

⁠Facebook⁠

⁠YouTube⁠

⁠Twitter⁠

⁠LinkedIn⁠

You can purchase a copy of my new book, Upping Your Game, on ⁠Amazon.com.⁠

Categories
Compliance Tip of the Day

Compliance Tip of the Day – M&A-Pre-Acquisition: Final Lessons

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice for navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide you with bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

This week, we looked at the role of compliance in the pre-acquisition phase of a merger and acquisition. We wrap it all up for you.

For more on this topic, check out The Compliance Handbook: A Guide to Operationalizing your Compliance Program, 6th edition, which LexisNexis recently released. It is available here.

Categories
Compliance and AI

Compliance and AI: Navigating the Challenges and Opportunities of Agentic AI in Compliance

What is the intersection of AI and compliance? What about Machine Learning? Are you using ChatGPT? These questions are just three of the many we will explore in this cutting-edge podcast series, Compliance and AI, hosted by Tom Fox, the award-winning Voice of Compliance. Today, the Everything Compliance gang, led by Dr. Hemma Lomax, is considering how to navigate the challenges and opportunities of agentic AI in compliance.

In this episode, we explore the rapidly evolving landscape of Agentic AI and its implications for compliance professionals. Agentic AI, defined as AI that acts autonomously rather than just responding to prompts, presents both significant opportunities and challenges. The technology can optimize risk management and compliance workflows, but it also introduces complexities around accountability, transparency, and oversight. We discuss recent real-world examples of Agentic AI in use, such as in banks and tax agencies, and highlight potential risks, including autonomous collusion and AI agents making unethical decisions. The episode emphasizes the need for compliance teams to shift from monitoring human activities to overseeing intelligent systems, ensuring the establishment of proper guardrails. We also delve into new roles emerging in this landscape, such as AI ethics coaches and agent supervisors, and the importance of human intervention to verify AI decisions. Join the discussion to understand how to navigate this transformative technology responsibly and effectively.

Key highlights:

  • Defining Agent AI
  • Implications for Compliance and Ethics
  • Challenges and Risks of Agent AI
  • Real-Time Compliance and Risk Management
  • Human Oversight and AI Governance

Resources:

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
Compliance Tip of the Day

Compliance Tip of the Day – M&A-Pre-Acquisition: Reviewing Financial and Operational Data

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice for navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide you with bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

We continue our look at the role of compliance in the pre-acquisition phase of a merger and acquisition. Today, we consider how to look for red flags in financial and operational data.

For more on this topic, check out The Compliance Handbook: A Guide to Operationalizing your Compliance Program, 6th edition, which LexisNexis recently released. It is available here.

Categories
Blog

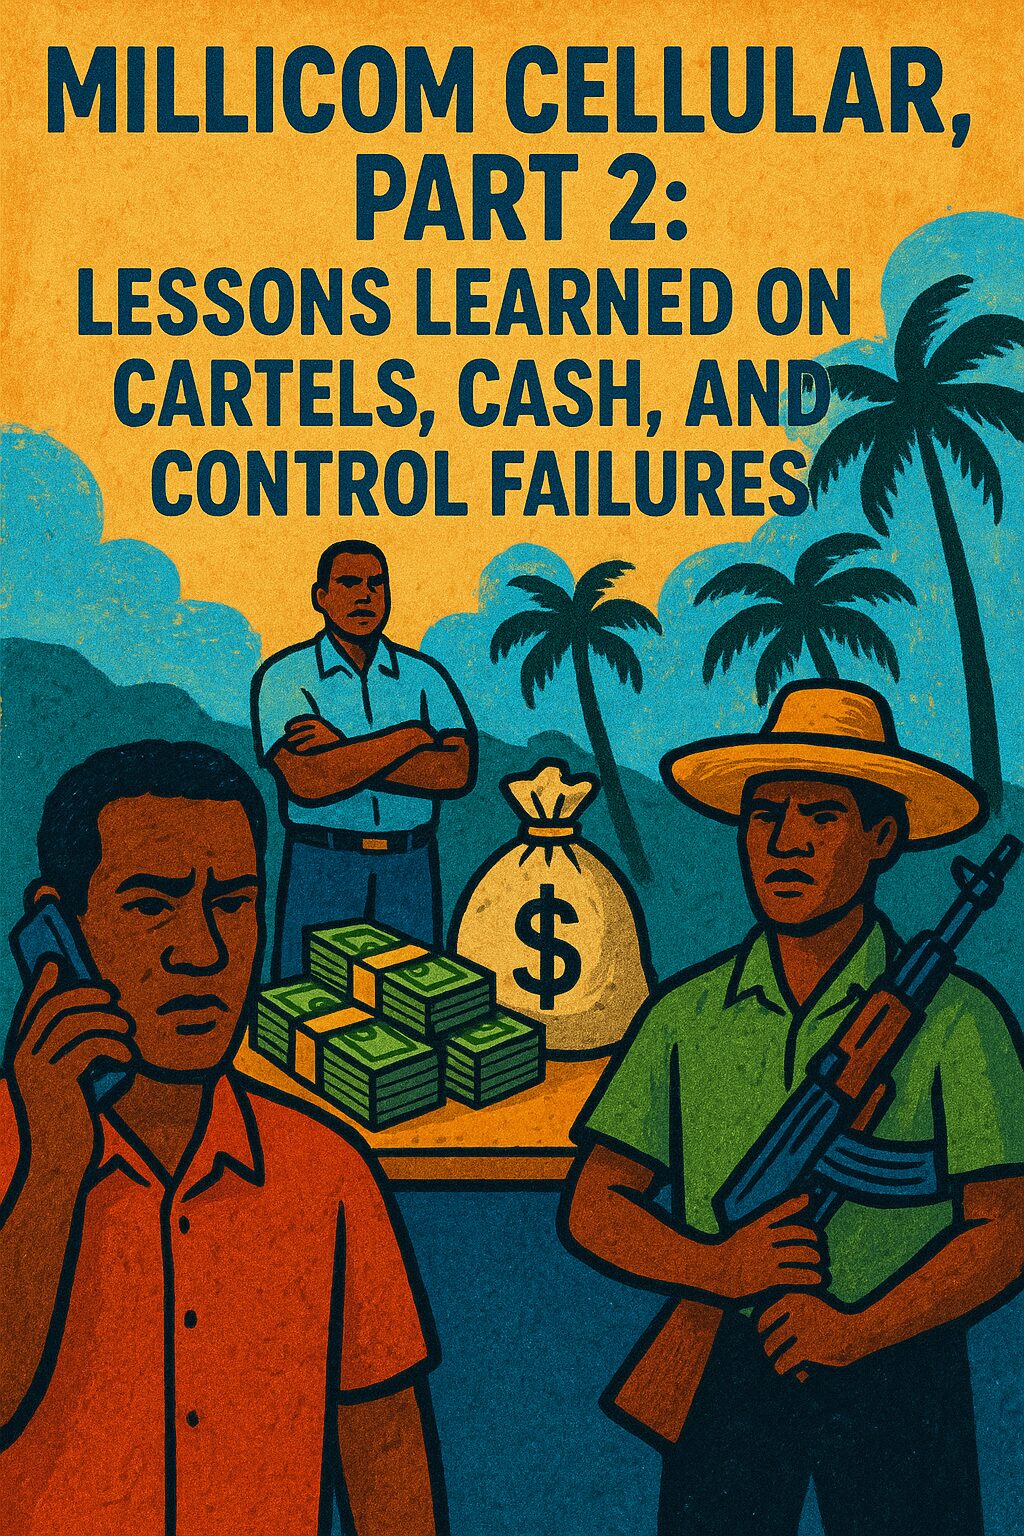
Millicom Cellular, Part 2: Lessons Learned on Cartels, Cash, and Control Failures

The Millicom Cellular FCPA enforcement action is not just another FCPA case. It is a case that signals a new frontier for compliance risk. It blends classic corrupt-payment schemes with organized crime, narcotrafficking proceeds, obstructed governance, and aggressive legislative capture. It is a wake-up call for compliance officers that the threat landscape is expanding in ways that require deeper operational controls, broader due diligence frameworks, and more sophisticated cross-functional collaboration.

In Part 1, we considered the underlying facts and FCPA violations of this matter. In Part 2, we examine what compliance professionals must take away from the case.

Lesson 1: Joint-Venture Governance Failures Are Not a Defense

Millicom Cellular held a 55 percent ownership stake in TIGO Guatemala, but the local partner exercised operational control and blocked Millicom Cellular from information and cooperation. The DOJ notes that Millicom Cellular voluntarily disclosed early concerns in 2015 but was unable to compel cooperation from local executives or obtain complete data. The result is a clear message:

Ownership without operational control equals enormous FCPA exposure.

Compliance professionals must:

  • Implement JV governance protocols that require access rights, audit rights, and cooperation language in shareholder agreements. Try to place your company’s representative as the CFO of the joint venture.
  • Establish escalation pathways if a partner obstructs investigations.
  • Treat “majority ownership without control” as a high-risk structure in compliance risk assessments.

Yet notwithstanding the foregoing, DOJ has made clear it will not accept a lack of control as an excuse for failing to detect corruption, especially when red flags are visible.

Lesson 2: Cash-Based Bribery Ecosystems Require a Different Kind of Monitoring

The bribery scheme ran almost entirely on cash: cash in duffel bags delivered by helicopter, cash laundered through drug traffickers, cash moved through shell companies, and cash withdrawn from banks in plastic bags. Traditional financial controls are almost useless in the face of an off-books cash economy. Compliance must be enhanced:

  • Controls around cash withdrawals
  • Monitoring of cash-intensive vendors
  • Patterns of invoicing irregularities
  • Real-time analytics on deviations in expense and procurement behavior

This is not a theoretical exercise. It is an operational reality for companies in high-risk jurisdictions.

Lesson 3: Cartel Exposure Is Emerging as a Corporate Compliance Obligation

This case represents one of the most explicit linkages between FCPA violations and narco-trafficking cash flows. The scheme not only involved bribes; it also involved bribes financed by organized crime. Compliance officers must now assume that criminal networks may view legitimate multinationals as conduits for illicit financial flows. This demands:

  • Enhanced beneficial-ownership checks
  • Screening for cartel-linked financial intermediaries
  • Deeper diligence on bankers, lawyers, and consultants
  • Country-level threat mapping that includes cartel and organized crime indicators

The DOJ has increasingly emphasized convergence risk between corruption, money laundering, and organized crime. The Millicom Cellular enforcement action is a prime example.

Lesson 4: “Influencing Legislation” Is a Red Flag, Not a Business Strategy

TIGO Guatemala sought legislative outcomes that would alter the national telecom law. That in itself is not illegal. What is unlawful is tying legislative outcomes to cash bribes, helicopter deliveries, and cartel-funded transactions. Compliance teams must scrutinize:

  • Payments to lobbyists, political consultants, and intermediaries
  • Relationships with legislators and political parties
  • Sponsorships, charitable donations, and community programs with political beneficiaries

Any effort to “shape legislation” must come with strict controls.

Lesson 5: Data Gaps Are Compliance Gaps

Millicom’s inability to obtain information access within its own joint venture delayed detection and undermined the credibility of its initial self-disclosure. Compliance professionals must demand:

  • Rights to data
  • Rights to conduct investigations
  • Rights to interview employees
  • The right to require cooperation from partners

A partner who denies access creates liability.

Lesson 6: Remediation Must Be Conducted Like a Corporate Transformation

Millicom’s remediation was extensive. It included:

  • Replacing senior personnel
  • Centralizing compliance oversight
  • Enhancing third-party onboarding and continuous monitoring
  • Adding data analytics
  • Conducting control testing across more than 250 transactions
  • Creating an ephemeral-messaging retention policy
  • Increasing compliance headcount by 800 percent (pages 5–6)

The DOJ’s description reads less like remediation and more like organizational reinvention. That is the expectation now. Compliance must treat remediation as a fully integrated operational overhaul.

Lesson 7: The DOJ Will Reopen Cases When New Evidence Emerges

The DOJ initially closed the investigation in 2018. It reopened the case in 2020 after uncovering new evidence from outside sources, including cartel-linked transactions. The message is clear:

  • Self-disclosure is not a shield when the company lacks visibility into misconduct.
  • Failure to detect ongoing wrongdoing can undermine trust and credit for cooperation.
  • Compliance must ensure continuous monitoring even after perceived risk has been reduced.

Conclusion: The New Compliance Mandate

The Millicom Cellular enforcement action demonstrates that compliance risk is no longer confined to corrupt payments. It now involves organized crime, cash-based bribery systems, cross-border laundering, political capture, and governance obstructions. Compliance professionals must operate with a broader risk lens, encompassing cartel risk, cash-economy vulnerabilities, high-risk political interactions, and joint-venture control structures. This is a key enforcement effort of the Trump Administration.

The future of compliance is not about preventing bribery alone. It is about defending the corporation from becoming an unwitting partner in a criminal enterprise.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – M&A-Pre-Acquisition: Evaluating Compliance Program and Culture

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice for navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide you with bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

We continue our look at the role of compliance in the pre-acquisition phase of a merger and acquisition. Today, we consider why and how to evaluate a target’s program and culture.

For more on this topic, check out The Compliance Handbook: A Guide to Operationalizing your Compliance Program, 6th edition, which LexisNexis recently released. It is available here.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – M&A-Pre-Acquisition: Conducting a Corruption Risk Assessment

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice for navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide you with bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

We continue our look at the role of compliance in the pre-acquisition phase of a merger and acquisition. Today, we consider the need for a corruption risk assessment.

For more on this topic, check out The Compliance Handbook: A Guide to Operationalizing your Compliance Program, 6th edition, which LexisNexis recently released. It is available here.

Categories
Innovation in Compliance

Innovation in Compliance – Steph Holmes on Blending AI and Human Oversight for Effective Compliance

Innovation spans many areas, and compliance professionals need not only to be ready for it but also to embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom welcomes Steph Holmes, long-time friend and Director of Ethics and Compliance Strategy at the EQS Group, who looks at the current Intersection of AI and compliance.

Steph Holmes and EQS are both at the forefront of integrating artificial intelligence (AI) into compliance programs to enhance their efficiency and effectiveness. With a focus on practical applications, Holmes views AI as a crucial tool for expanding resources, especially as organizations face increasing regulatory changes and economic pressures. She advocates for the responsible, sustainable, and explainable adoption of AI, emphasizing that compliance professionals should embrace it rather than fear it. Holmes discusses the importance of blending AI capabilities with human oversight to ensure compliance tasks are managed accurately and risks are mitigated effectively.

Key highlights:

  • Digitizing Compliance: AI Tools and Programs
  • Navigating Compliance Challenges with Human Judgment
  • Enhancing AI Reliability Through Human Oversight
  • Enhancing Compliance through Responsible AI Implementation
  • Implementing AI Pilot Programs in Compliance Workflows

Resources:

Steph Holmes on LinkedIn

EQS Group LinkedIn

Where in the Loop: Corporate Compliance Insights

EQS Website

EQS Benchmark Report: AI Performance in Compliance & Ethics

Innovation in Compliance was recently ranked 4th among Risk Management podcasts by 1,000,000 Podcasts.

Categories
Blog

Why AI Demands a New Breed of Leaders: A Compliance Perspective

Artificial intelligence is no longer a distant future state for compliance teams. It is here, operating inside financial crime platforms, powering third-party due diligence tools, driving monitoring engines, and influencing the everyday judgments that regulators scrutinize. Yet too many companies still approach AI as if it were simply another IT project. In a recent Sloan Management Review article, “Why AI Demands a New Breed of Leader,” the authors, Faisal Hoque, Thomas H. Davenport, and Erik Nelson, argue that successful AI transformation is far more about people, culture, and leadership than about code.

For compliance professionals, that should sound familiar. Every major enforcement action of the last decade has shown that failure rarely begins with a faulty system. Failure begins with leadership that misunderstands risk, a culture that resists change, and governance frameworks that cannot keep pace with new technologies.

The authors argue that modern organizations require a new category of leader to guide AI adoption, a role that blends technical capability with cultural stewardship, ethical understanding, and organizational change management. They call this the Chief Innovation and Transformation Officer (CITO) or an equivalent title. Whether companies formally adopt the title or not, the message is unmistakable: AI changes the leadership equation, and compliance has a front-row seat.

Why Traditional Technology Leadership Is No Longer Enough

While CIOs are increasingly viewed as changemakers, they often lack the time and mandate to address the organizational disruption AI brings. Compliance officers understand this problem intuitively. You can have the most sophisticated tools in the world, but if the culture is not ready for them, the result will be chaos or even misconduct. The authors cite survey data showing that 91 percent of large-company data leaders believe cultural issues, not technical ones, are blocking progress. That finding mirrors what compliance sees in every DOJ corporate enforcement action. Misconduct thrives not because technology fails, but because people and processes fail.

The article also includes examples of organizations that stumbled by treating AI as a purely technical deployment. The Zillow pricing model collapsed. The swift employee backlash at California State University. The Air Canada chatbot that mishandled bereavement fare guidance. Each case reveals the same lesson: AI without governance becomes a liability. For compliance professionals evaluating AI adoption, these examples should resonate. AI raises questions about transparency, fairness, documentation, accountability, and the human impact of automation. Those are governance issues, not engineering puzzles.

The New Leadership Model AI Demands

The authors describe several competencies required for effective AI leadership, all of which map directly into compliance priorities:

Navigating ethical considerations.

AI introduces bias, harm, and fairness risks, all of which are central concerns for regulators. Leaders must weigh efficiency gains against ethical boundaries.

Driving cultural transformation.

AI adoption changes workflows, reporting lines, incentives, and human-machine collaboration. Leadership must prepare the workforce for new models of decision-making.

Managing human-AI partnerships.

The near-future compliance program will rely on co-decision systems that combine algorithmic outputs with human judgment. Leaders must understand how to balance the two.

Breaking down silos.

AI implementation touches HR, legal, IT, operations, procurement, and compliance. Leadership must connect these functions rather than allow fragmented approaches.

Overseeing citizen development.

Employees across the business can now build AI models without IT involvement. That democratization requires governance and guardrails.

These competencies go far beyond traditional CIO responsibilities. They lean toward behavior, judgment, and organizational change, the same strengths compliance brings to the table.

Emerging Executive Roles Around AI

The article documents the rapid rise of AI-focused executive roles such as Chief Innovation Officer, Chief AI Officer, and Chief Transformation Officer. Compensation is rising, hiring is accelerating, and responsibilities increasingly blend technology, ethics, culture, and strategy.

The authors highlight examples:

  • PepsiCo’s Chief Strategy and Transformation Officer is overseeing enterprise-wide digitization.
  • Standard Chartered’s Chief Transformation, Technology, and Operations Officer.
  • JPMorgan Chase’s governance model for IndexGPT and AI-driven investment analysis.

These roles share a common trait: they embed ethics, cultural change, and strategic alignment directly into AI governance. This direction should reassure compliance officers. Regulators have signaled that they expect AI oversight to be integrated, accountable, and verifiable. A dedicated AI leadership role can help unify these obligations.

AI Persona Management: The Next Frontier of Governance

One of the most intriguing sections of the article describes “AI persona management,” the oversight of digital agents with defined personalities, roles, and decision-making authority. As AI becomes more autonomous, these personas may behave like digital employees. That raises profound governance questions.

Compliance professionals should begin considering:

  • What decision rights will AI personas have?
  • How will we document their logic?
  • How will we audit their behavior?
  • How will we ensure ethical consistency across different personas?

The authors note that Salesforce already uses AI personas internally to guide product decisions. That should serve as a signal: AI agents are not a theoretical concept; they are entering the enterprise now. A compliance professional will need to treat AI personas with the same seriousness as human employees, subject to monitoring, training, policies, escalation channels, and accountability structures.

What This Means for Corporate Compliance Leaders

The article argues that companies must rethink how they manage technology change. AI’s impact is too broad to remain confined to the IT organization. Talent, culture, ethics, governance, and risk management all intersect. The authors present the CITO role as the logical solution for a leader who integrates technical fluency with organizational psychology and ethical judgment.

From a compliance standpoint, this represents both an opportunity and a responsibility. The opportunity is clear: compliance brings exactly the kind of cross-functional, ethics-driven perspective AI leadership requires. The compliance function knows how to document decisions, manage cultural change, develop defensible processes, and build controls around complex risks.

The responsibility is equally clear: AI will soon permeate every corner of the enterprise. If compliance does not assert its role in governance, the organization will drift toward risk. This article provides a roadmap for what strong governance must look like. It tells companies that AI success demands a leader capable of bridging technical, ethical, and cultural domains, the very domains compliance has long mastered.

Now is the moment for compliance to claim its seat at the AI leadership table, helping shape the systems that will define operational and ethical performance for years to come.
Categories
ACI FCPA Conference 2025

ACI-FCPA Conference Speaker Preview Series – Doing Business (and Compliance) in India with Joseph Azam

In this episode of the ACI-FCPA and Global Anti-Corruption Conference Speaker Podcasts series, Joseph Azam discusses the panel at the event. Their presentation is entitled “On the Ground in India: Special Considerations for Compliance, Risk Management, and Third-Party Oversight—Practical Takeaways from Real-World Experiences.”

Some of the issues the panel will discuss are:

  • Corruption risk specific to India.
  • Long-term strategies for effective due diligence in India and
  • Aligning global expectations with local realities.

I hope you can join me at the ACI–FCPA Conference. This year’s event will take place on December 3-4 at the Gaylord National Resort & Convention Center in National Harbor, Maryland, near Washington, D.C. The lineup of this year’s event is simply first-rate, featuring some of the top FCPA professionals, white-collar attorneys, and compliance practitioners in the field.

The 2025 program is being completely redesigned to help your organization stay agile, responsive, and ahead of the curve. Expect a dynamic agenda shaped by real-world priorities, practical takeaways, and the most cutting-edge thinking in compliance—led by a faculty of global practitioners with boots-on-the-ground experience encountering the high risks that come across your desk.

Please join me at the event. For information on the event, click here. Listeners of this podcast will receive a discount by using the code D10-999-CPN26.