Categories
Blog

Is FCPA Enforcement Back? Part 1 – What Compliance Professionals Need to Know

After months of speculation and a noticeable lull in FCPA enforcement, the U.S. Department of Justice (DOJ) has made a significant announcement with a new policy statement. In a recently released memorandum titled “Guidelines for Investigations and Enforcement of the FCPA” (FCPA Memo), the Deputy Attorney General (DAG), Todd Blanche, has sent a clear message that FCPA enforcement remains alive under the Trump Administration. However, it will now focus on new areas, including cartel disruption, national security, US business development, and leveling the global playing field for U.S. companies.

This two-part blog post series breaks down, in Part 1, the key compliance takeaways from this important policy pivot, and in Part 2, offers practical insights on how you, the compliance professional, should respond.

1. Cartels, Corruption, and Competitive Disadvantage: The New Enforcement Trifecta

The Trump Administration has refocused DOJ enforcement on cartels and transnational criminal organizations. This FCPA memo formalizes that commitment by tying cartel activity directly to FCPA enforcement. If a foreign company bribes officials in a jurisdiction where cartels thrive, think Mexico or Colombia, this administration sees a compelling hook for the DOJ to act. It is not just about corruption in isolation; it is about rooting out the business practices that enable criminal ecosystems.

More provocatively, the FCPA Memo explicitly prioritizes cases where corruption places U.S. companies at a competitive disadvantage in the business world. That is undoubtedly a reframing of the FCPA’s historical mission. Historically, the US and other uneducated critics have claimed that the FCPA penalizes US companies more harshly than their foreign counterparts. That has never been true, as even in 2025, more than half of the top ten largest FCPA enforcement actions of all time have been against foreign-based companies. However, the DOJ’s message now is that if your foreign competitor is winning contracts by bribing officials, the US government may well be interested in investigating them, not just because it is illegal, but also because it harms American businesses.

Compliance Takeaway: If your company is aware of unfair practices by foreign competitors, this may be the ideal time to take action. The door is open for whistleblower complaints even against non-U.S. entities, primarily where jurisdictional hooks exist. Expect more aggressive cross-border enforcement. Consider strengthening your third-party due diligence in regions where cartels or known corruption are prevalent.

2. Expedited Investigations: A Welcome Burden or a New Headache?

The FCPA Memo calls on prosecutors to “proceed as expeditiously as possible” in investigating and resolving FCPA cases. On its face, this sounds like good news—long, open-ended probes can paralyze business operations and drain resources. But what does this mean? More pressure on prosecutors? More pressure on internal investigations? More pressure on internal reporting and triage? More pressure on getting it right? (Hint: It’s all of the above.)

FCPA investigations are complex. They require cross-border data collection, permissions from foreign authorities, and interviews with key personnel who often have full business calendars. Now, there is added pressure to accelerate timelines, which may involve compressing review cycles, reducing interview preparation time, and making quicker judgment calls.

Compliance Takeaway: Compliance teams should rehearse their internal investigation protocols. Do you have the right tech stack for document review? Can you mobilize your legal team quickly? Is your board informed about high-risk regions and prepared to respond quickly? If not, now’s the time to prepare.

3. Collateral Consequences and Business Disruption: A Balancing Act

The memo notably instructs prosecutors to consider “collateral consequences,” the potential disruption to lawful business operations, and the impact on innocent employees. This language expands the typical resolution-phase considerations into the investigative phase itself.

This could play out in several ways. Investigations may be more narrowly scoped, targeting business units directly implicated in misconduct rather than company-wide fishing expeditions. It may also lead to greater leniency in imposing fines or monitorships where such measures would significantly impair innocent stakeholders. It certainly provides defense counsel with more arguments to present to the DOJ to limit or narrow the scope of any investigations.

Compliance Takeaway: If your organization finds itself under DOJ scrutiny, be prepared to advocate for the operational integrity of your business early and often. Document how cooperation, remediation, and disruption mitigation are being handled throughout the investigation. Use this framework as a proactive tool in early dialogue with prosecutors.

4. National Security Interests Continue to Take Center Stage

Building on the Biden Administration’s policy on Anti-Corruption, the Trump Administration has woven national security into FCPA enforcement priorities, highlighting sectors such as defense, software, artificial intelligence, critical minerals, and deepwater infrastructure. This means more cases involving cobalt mining, chip manufacturing, satellite communications, and cyber tools will fall within the DOJ’s line of sight. In essence, the DOJ is saying, “If your business, or your competitor’s business, touches sensitive sectors with national implications, we care.”

Compliance Takeaway: Compliance professionals in industries even tangentially connected to national security should conduct fresh risk assessments. Are you sourcing from high-risk jurisdictions? Using agents in resource-rich areas? Working with state-owned entities abroad? If so, those red flags now carry more weight.

5. Corporate Structures vs. Individual Misconduct: Back to Basics

One curious phrase in the memo warns against attributing “non-specific malfeasance to corporate structures.” At first glance, it’s a head-scratcher. However, upon closer inspection, it reinforces a longstanding principle: corporations are liable when individuals commit crimes, not due to vague failures in internal controls. This is essentially a reaffirmation of the longstanding DOJ position that it will not prosecute internal control violations absent extraordinary circumstances. (This has been left to the SEC.) This prosecutorial philosophy has defined the DOJ’s FCPA enforcement over the last decade. It is not enough for the DOJ to find a company that had weak controls; you need to show that someone crossed the line.

Compliance Takeaway: This is good news for companies with mature compliance programs. But it also raises the stakes for effective training, monitoring, and investigations. Your internal audit function must be able to identify and document actual misconduct, not just control failures. The DOJ stated that it will focus on crimes rather than paperwork errors.

6. The Focus on Serious Misconduct: Clearing the Docket

The DOJ has also clarified that it will deprioritize routine or “de minimis” FCPA violations, such as small gifts, modest travel perks, or isolated hospitality expenses. These will no longer be the centerpiece of enforcement actions unless they are accompanied by more serious wrongdoing. Although prominently stated in the FCPA Memo, the prosecutorial reality is once again that such violations have never been part of DOJ FCPA enforcement actions.

That does not mean your corporate compliance program should collectively fail to meet expectations. Excessive gifts or travel can still be part of the fact pattern in larger bribery schemes and may be cited in SEC books-and-records charges, even if the DOJ declines to pursue criminal prosecution.

Compliance Takeaway: Your policies on gifts, travel, and entertainment remain relevant, but you should right-size your compliance efforts. Focus your highest controls and resources on areas where real business decisions are being made, such as third-party relationships, government tenders, and public-private partnerships.

7. Foreign Prosecutions and Global Coordination: Sharing the Stage

The memo closes with an acknowledgment that foreign enforcement matters. Prosecutors are instructed to weigh whether other jurisdictions may prosecute before launching their actions. This appears to affirm the DOJ’s commitment to international collaboration rather than signaling retreat. Expect more joint settlements, coordinated raids, and synchronized prosecutions. But do not count on the DOJ stepping aside, especially in high-stakes cases.

Compliance Takeaway: If your company is under investigation abroad, don’t assume you’re out of the DOJ’s reach. Transparency and cooperation with global authorities will still be key. And make sure your disclosures in one country don’t conflict with your representations in another.

Join us tomorrow for Part 2, where we consider some responses you should take now.
Categories
Blog

Investigative Lessons from Sherlock Holmes: The Sign of Four

Corporate compliance and Sherlock Holmes may seem worlds apart, but compliance professionals and Sir Arthur Conan Doyle’s legendary detective share a core responsibility: uncovering truths hidden behind complex webs of evidence. “The Sign of Four,” one of Doyle’s most gripping Sherlock Holmes tales, offers powerful investigative insights directly applicable to the realm of compliance. Here are five key lessons compliance professionals can draw from Holmes’s investigative methods in this classic novel.

1. Precise Documentation: “Methodical Observation”

In The Sign of Four, Sherlock Holmes emphasizes the importance of methodical and precise documentation as crucial to solving complex mysteries. Early in the narrative, Holmes carefully examines a mysterious note received by Miss Mary Morstan. His meticulous observation of handwriting, paper quality, and ink composition enables him to deduce the note’s origin and purpose, thereby setting the course of the investigation.

Compliance professionals should emulate Holmes by rigorously documenting every aspect of an investigation to ensure thoroughness and accuracy. Precise records of evidence, witness statements, and procedures ensure accuracy, accountability, and transparency, significantly reducing risks of oversight or misinterpretation. Proper documentation also strengthens the organization’s ability to respond effectively during audits or regulatory inquiries.

2. Logical Analysis: “Eliminating the Impossible”

Holmes famously asserts in The Sign of Four, “When you have eliminated the impossible, whatever remains, however improbable, must be the truth.” This principle guides his pursuit of justice throughout the novel. Holmes methodically rules out improbable scenarios in investigating the disappearance of Captain Morstan and the subsequent quest for hidden treasure, ultimately unveiling Jonathan Small’s elaborate revenge-driven plot.

Compliance officers should similarly use structured analytical frameworks to eliminate false assumptions and unsubstantiated theories during investigations. Adopting logical, disciplined analysis reduces biases, prevents costly mistakes, and fosters more accurate and actionable outcomes. Holmes’s deductive approach encourages compliance professionals to remain vigilant against assumptions that may cloud judgment.

3. Embrace Collaboration: “Leveraging Complementary Strengths”

In The Sign of Four, Sherlock Holmes frequently relies on Dr. Watson’s support and complementary skills. Watson’s medical knowledge and practical insights greatly assisted Holmes during the investigation, notably during examinations of crime scenes and understanding the emotional motivations of suspects and victims.

For compliance professionals, this illustrates the importance of multidisciplinary collaboration. Effective compliance investigations often require collaboration with professionals from diverse specialties, including auditors, forensic accountants, legal advisors, human resources specialists, and IT experts. Embracing a collaborative approach ensures a comprehensive investigation, as each discipline brings unique insights that enhance the overall effectiveness and credibility of the compliance function.

4. Attention to Subtle Indicators: “Noticing Small Clues”

Holmes’s brilliance often lies in noticing seemingly insignificant details overlooked by others. In The Sign of Four, Holmes carefully notes tiny footprints, peculiar scents, and minor discrepancies in testimonies, each subtly directing the investigation toward its resolution. For instance, Holmes’s keen attention to Toby, the trained bloodhound, and his reaction to specific scents help locate key evidence pivotal to unraveling the mystery.

Compliance professionals must likewise sharpen their observational skills to detect subtle indicators of wrongdoing, such as minor financial discrepancies, slight variations in employee behaviors, or seemingly inconsequential procedural anomalies. Often, the most significant compliance breaches initially manifest as minor irregularities. Developing Holmes-like attentiveness can significantly enhance the detection and early resolution of compliance issues.

5. Managing Bias and Assumptions: “Maintaining Objective Judgment”

Throughout, Holmes maintains rigorous objectivity, avoiding emotional biases or ungrounded assumptions. Even when emotionally involved characters, including Watson and Miss Mary Morstan, draw emotional or intuitive conclusions, Holmes insists on relying exclusively on factual evidence and logic. His disciplined approach ensures accuracy and fairness in the investigation’s outcome.

Compliance officers frequently confront emotionally charged scenarios or influential stakeholders, which can pressure outcomes. Maintaining an objective and unbiased judgment is crucial to upholding fairness and integrity during compliance investigations. Holmes’s unwavering dedication to evidence-based analysis exemplifies the importance of unbiased fact-finding in safeguarding organizational ethics and compliance integrity.

Final Thoughts: Integrating Sherlock Holmes’s Methods into Compliance

The Sign of Four offers rich investigative wisdom that is directly applicable to corporate compliance. Sherlock Holmes’s meticulous documentation, disciplined logical reasoning, strategic collaboration, precise attention to detail, and uncompromising objectivity represent invaluable investigative methodologies for today’s compliance professionals.

As compliance continues evolving in complexity and significance, adopting Holmesian investigative rigor enhances our ability to protect organizational integrity, mitigate risks, and ensure regulatory compliance. Compliance professionals who master these investigative practices not only improve their effectiveness but also significantly contribute to their organization’s overall resilience and ethical standing.

In the dynamic landscape of corporate compliance, Sherlock Holmes’s timeless investigative lessons remain as relevant today as in Victorian London, reminding us that excellence in investigation demands continual refinement, unwavering diligence, and precise analytical clarity.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – New FCPA Enforcement Memo-What Does it Say?

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our goal is to provide you with concise, actionable tips to help you stay ahead in your compliance efforts. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.


Today, we begin a two-part look at the recently released FCPA Enforcement Memo. Today, in Part 1, we consider what it says. 

For more information on this topic, refer to The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, 6th edition, recently released by LexisNexis. It is available ⁠here⁠. 

Categories
Compliance Tip of the Day

Compliance Tip of the Day – COSO Framework

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our goal is to provide you with bite-sized, actionable tips to help you stay ahead in your compliance efforts. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

What is the COSO 2013 Internal Controls Framework?

For more information on this topic, refer to The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, 6th edition, recently released by LexisNexis. It is available here.

Categories
FCPA Compliance Report

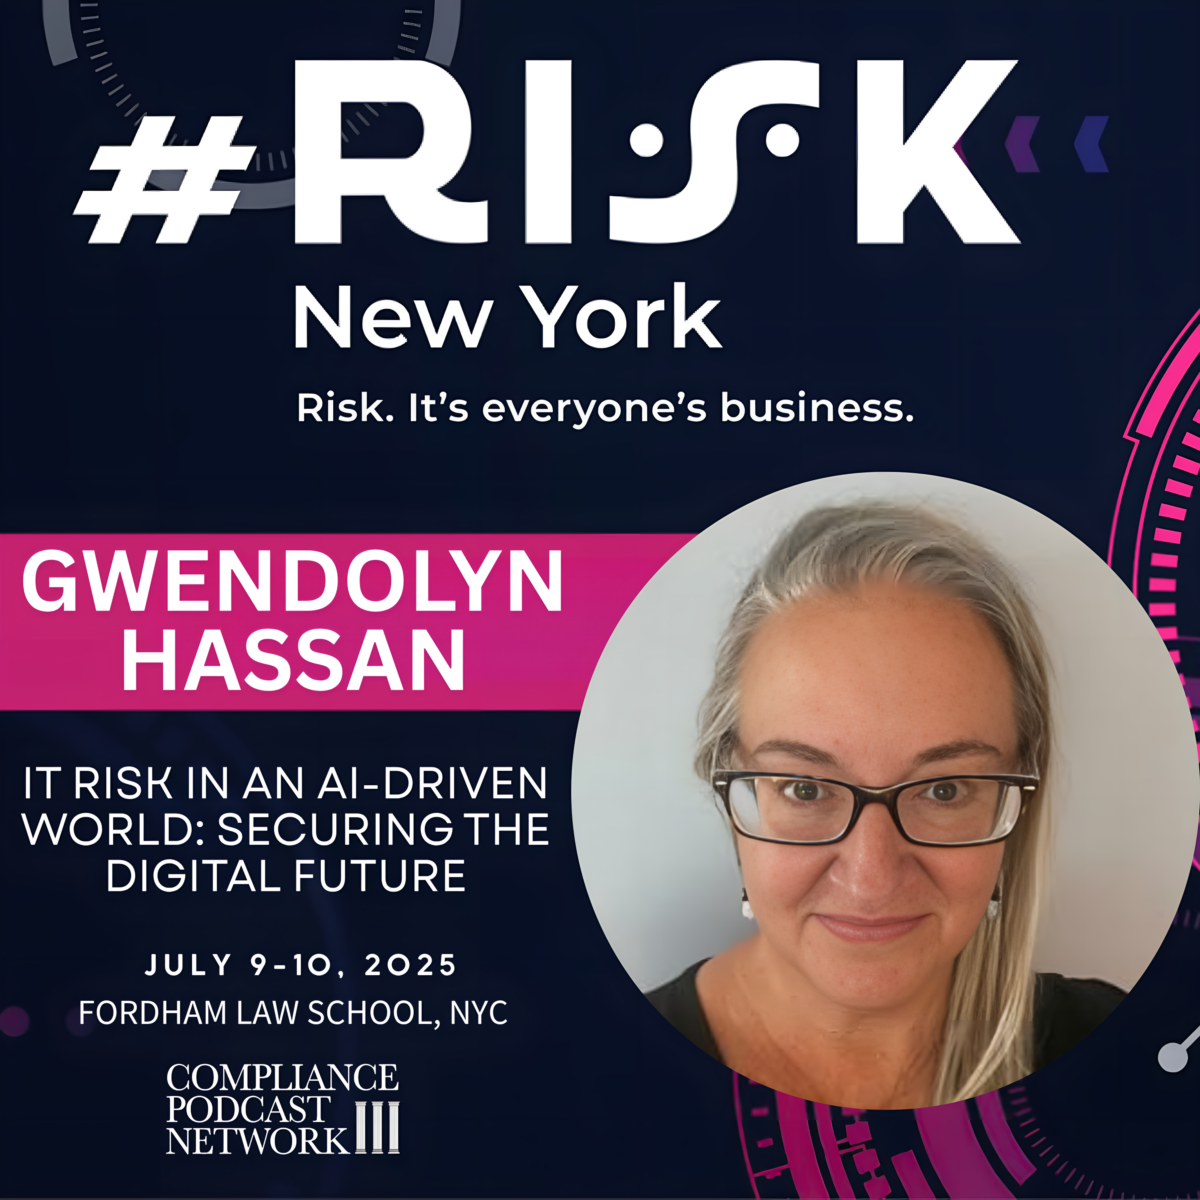
#Risk New York Speaker Series – Exploring AI Risks in Compliance with Gwen Hassan

Join Tom Fox and hundreds of other GRC professionals in the city that never sleeps, New York City, on July 9 & 10 for one of the top conferences around, #Risk New York. The current US landscape, shaped by evolving policies, rapid advancements in AI, and shifting global dynamics, demands adaptive strategies and cross-functional collaboration.

At #RISK New York, you will master the New Regulatory Reality by getting ahead of US regulatory shifts and their impact. Conquer AI and Tech Risk by Safeguarding Your Organization in an AI-Driven World and Understanding the Implications of Major Tech Investments. Navigate Financial and Crypto Volatility by Protecting Your Assets and Exploring Solutions in a Dynamic Market. Strengthen Your GRC Framework by Leveraging Governance, Risk, and Compliance for Strategic Advantage. Protect Digital Trust by addressing challenges in cybersecurity and data privacy, and combating misinformation. All while meeting with the country’s top #Risk management professionals.

In this episode, Tom Fox talks with Gwen Hassan, the Chief Compliance Officer for Unisys Corporation, about her role and the upcoming #RiskNYC conference. Gwen shares insights into Unisys’ operations, including the various technologies and services they provide, and highlights her responsibilities in managing global ethics, compliance, and trade compliance risks. She also gives a teaser about her panel presentation on the compliance and ethics risks associated with artificial intelligence, stressing the importance of understanding AI’s impact on company culture and regulatory compliance. Gwen expresses her excitement about the conference, emphasizing the value of engaging with fellow risk management experts.

Resources:

#Risk Conference Series

#RiskNYC—Tickets and Information

Gwen Hassan on LinkedIn

Categories
Regulatory Ramblings

Regulatory Ramblings: Episode 71 – Crypto Fault Lines: Stablecoins, Meme Coins & the Fight for Clarity PLUS: Sanctions, Shell Companies & Fragmented Global Trade

This episode begins with a brief spotlight chat with Lucas Har from Dow Jones in Singapore, discussing trade compliance, sanctions, dual-use goods, and supply chain risk, particularly in the context of the currently strained US-China trade relationship following the recent increase in US tariffs on China and Hong Kong.

We then proceed to a discussion with Hong Kong-based Joshua Chu and Melizza Anievas to explore Hong Kong’s recently enacted Stablecoin Ordinance, including the distinction between meme coins and stablecoins, as well as the ever-evolving global landscape for virtual assets in light of recent regulatory developments in the US.

On May 21, 2025, the Hong Kong Legislative Council passed the Stablecoins Ordinance, creating a formal licensing regime for fiat-referenced stablecoin (FRS) issuers. While local in implementation, the regulatory milestone decisively places Hong Kong at the forefront of a broader Asian effort to shape the future of legitimate, rules-based decentralized finance (DeFi) and tokenized financial infrastructure.

The move came just one day after the US Senate passed the GENIUS Act. Against this backdrop, Hong Kong’s move added momentum to global harmonization efforts on stablecoin regulation, directing the policy debate more towards developing trustworthy digital asset ecosystems with practical, real-world utility and functionality.

The territory’s new framework requires all issuers promoting fiat-backed stablecoins to the general public locally to be licensed by the Hong Kong Monetary Authority (HKMA)—the city’s banking regulator and de facto central bank.

Additionally, issuers must hold reserves in either cash or high-quality, highly liquid assets, such as short-term government securities. Stablecoins must be redeemable at par value at any time. Issuers must regularly disclose their reserve holdings and undergo audits. AML/CFT compliance and risk controls are also required.

This regulatory clarity is paired with active development. For example, Hong Kong’s Stablecoin Sandbox, launched last year, has enabled companies such as Standard Chartered, Animoca Brands, and JD Coinlink to test real-world use cases across payments, capital markets, and trade finance. Ultimately, it reflects a coordinated effort to turn policy into practical rails for tokenized activity.

Joshua Chu

Joshua Chu is a prominent Hong Kong lawyer specializing in fintech and crypto matters, as well as a prolific writer. His opinion and insights are much sought after by the local press and correspondents of major foreign news organizations operating in the city. You can often hear him at his most candid on the radio at RTHK.

Joshua is also co-chair of the Hong Kong Web 3 Association and legal advisor to the Hong Kong Blockchain Association.


Melizza Anievas

Melizza Anievas is a co-founder and executive director of Women in Web3 Hong Kong. Under her leadership, Women in Web3 Hong Kong has grown to over 1,500 members and secured over HK$300,000 in sponsorships within a year, establishing working relationships with notable partners such as Google Cloud Hong Kong, The Sandbox, and Animoca Brands. A Web3 veteran since 2019, Melizza excels at devising growth-driven strategies and operating hyper-growth businesses.


Lucas Har

Lucas Har is based in Singapore and has been with Dow Jones Risk & Compliance for nearly a decade. He began his career with a focus on Anti-Money Laundering (AML) and Counter-Terrorism Financing (CTF) research across a diverse portfolio of Asia-Pacific jurisdictions.
​
Later, Lucas took on a leadership role overseeing the company’s content curation team, where he was responsible for news curation and monitoring adverse media.
​
In his current position, he manages the firm’s global trade compliance product suite, spearheading innovation and strategic growth.

He has also extensively engaged with financial institutions, corporations, and regulators across multiple regional jurisdictions, fostering discussions on export control compliance and further strengthening Dow Jones’s expertise in such an increasingly vital and complex area.

Discussion:

As our guests flesh out, several common threads emerge linking the two segments of today’s episode. The first is that of regulatory fragmentation across jurisdictions such as the US, mainland China, Hong Kong, and the EU.

There is also the issue of extraterritorial overreach and competition, particularly between China’s export rules and US crypto laws, as well as a global push for clarity in fast-moving, high-risk sectors, including the international trade of goods and virtual assets more broadly. Simply put, the heavy geopolitical undertones in both export control and digital asset regulation cannot be avoided, as they cast a shadow on the role of trust and credibility, or the lack thereof, in navigating both trade and cryptocurrency systems.

With that in mind, the podcast begins with Regulatory Ramblings host Ajay Shamdasani asking Lucas about the evolving regulatory landscape shaping international trade and its implications for Hong Kong businesses, as well as the impact of mainland China’s new export control regulations on dual-use goods.

Lucas shares what legal and compliance specialists need to know about the regulatory hurdles the firms they serve must adhere to, including sanctions and export control regulations, as well as best practices for enhancing due diligence procedures to mitigate trade-related risks.

Following that, Joshua and Melizza share their thoughts on what the new stablecoin ordinance will mean for Hong Kong, as well as the importance of recent US regulations. Securities and Exchange Commission clarifications on meme coins and their potential impact on legal, risk, and compliance strategies for developers and investors.

The three of them go on to discuss the key operational and regulatory challenges stablecoin issuers face under Hong Kong’s new licensing regime and how the US GENIUS and STABLE Acts might reshape the US stablecoin market and influence global regulatory approaches.

Indeed, something worth asking—and which Joshua and Melizza do not shy away from commenting on⁠ — is whether the relatively ‘light touch’ regulation of meme coins encourages innovation or exposes investors to undue risk.

The conversation concludes with a chat about how projects can effectively balance innovation with regulatory compliance amid differing US and APAC frameworks. Most memorable is how Melizza distinguishes between Web 3.0 and Web3.

Useful links in this episode:

You might also be interested in:

Connect with RR Podcast at:

LinkedIn: https://hk.linkedin.com/company/hkufintech 
Facebook: https://www.facebook.com/hkufintech.fb/
Instagram: https://www.instagram.com/hkufintech/ 
Twitter: https://twitter.com/HKUFinTech 
Threads: https://www.threads.net/@hkufintech
Website: https://www.hkufintech.com/regulatoryramblings 

Connect with the Compliance Podcast Network at:

LinkedIn: https://www.linkedin.com/company/compliance-podcast-network/
Facebook: https://www.facebook.com/compliancepodcastnetwork/
YouTube: https://www.youtube.com/@CompliancePodcastNetwork
Twitter: https://twitter.com/tfoxlaw
Instagram: https://www.instagram.com/voiceofcompliance/
Website: https://compliancepodcastnetwork.net

Categories
Blog

Wells Fargo, Risk Management and Reputational Recovery: Part 2 – Lessons Learned

On June 3, 2025, the Federal Reserve lifted its unprecedented $2 trillion asset cap on Wells Fargo, marking the symbolic end to one of the most consequential compliance enforcement actions in modern U.S. banking history. For the compliance and risk management community, this moment is not a victory lap; it is a case study of how compliance failures cascade, reputational risk becomes operationally tangible, and regulatory patience has its limits.

Over these two blog posts, I have explored what happened, why it mattered, and what lessons every compliance professional should carry forward. Yesterday, we examined the unique penalty imposed on Wells Fargo. Today, we reflect on the lessons learned by compliance professionals.

1. Sales Incentives Must Be Auditable and Aligned with Ethics

Incentive structures sit at the very core of behavioral risk. At Wells Fargo, the sales-driven “Gr-eight” initiative, designed to sell eight products per customer, transformed from a marketing aspiration into an existential risk. The program rewarded aggressive cross-selling, but without effective compliance oversight, it became a toxic engine of misconduct. Employees, facing immense pressure to meet unrealistic sales goals, began opening unauthorized accounts and manipulating customer data, led by the very highest levels of the company. This was not isolated behavior; it was systemic fraud incentivized by misaligned performance metrics.

For compliance professionals, the lesson is straightforward: incentive programs must be co-designed with risk and compliance in the room. It is not enough to reward growth; companies must also reward growth achieved in an ethical manner. This means conducting behavioral audits of how incentive programs are experienced in practice, not just how they appear on paper. Are salespeople bending the rules to meet targets? Are managers discouraging whistleblowing to protect metrics?

Moreover, all incentive plans should undergo compliance risk assessments. This includes mapping the downstream effects of reward systems, integrating compliance KPIs, and instituting real-time monitoring mechanisms. Transparency is key; employees must understand that ethical behavior is not just expected but tracked and rewarded.

Wells Fargo’s downfall was a direct result of a cultural failure to align incentives with values. When success is measured solely by numbers, ethics become expendable. Compliance leaders must ensure that incentive systems pass both the audit test and the mirror test: can they be audited for integrity, and can you look in the mirror knowing they support the organization’s stated values?

In the modern regulatory environment, misaligned incentives are no longer just a business risk—they are a regulatory and reputational time bomb waiting to detonate.

2. Regulatory Fatigue Is Not an Excuse

One of the most sobering realities of the Wells Fargo asset cap was its duration: seven years. That’s nearly a decade of constrained growth, investor frustration, and board-level scrutiny. Some might assume that regulatory attention naturally fades over time, but the Wells Fargo case proves otherwise. Regulators did not relent. They did not forget. And they did not lift the restrictions until the institution proved it had earned back the trust lost through systemic misconduct.

For compliance professionals, this underscores a critical truth: regulatory fatigue is no excuse for underperformance or delay. Treating compliance obligations as a burdensome box-checking exercise is what led Wells Fargo into this mess in the first place. Real remediation requires patience, perseverance, and, above all, a cultural shift in how the organization views compliance.

This shift is not cosmetic. Instead, it is strategic. It means compliance is embedded in daily operations rather than being relegated to periodic reports. It means senior leadership engages deeply in control redesigns, audits, and training rather than just approving them. It means boards of directors receive regular updates that go beyond dashboards to include narrative risk insights, root cause analyses, and forward-looking risk indicators.

Wells Fargo’s journey illustrates the high cost of superficial remediation. CEO Charlie Scharf’s arrival in 2019 marked a turning point because he treated compliance not as an obstacle but as a foundation. His willingness to restructure the operating model around risk oversight demonstrated that regulatory trust must be rebuilt brick by brick, meeting by meeting, order by order.

There are no shortcuts. Compliance professionals must prepare their organizations for the long haul. When the pressure to “move on” arises, as it inevitably will, it is the CCO’s duty to say: not yet. True cultural transformation takes time, and regulators will accept nothing less.

3. Asset Caps and Structural Penalties Are the New Frontier

The $2 trillion asset cap imposed on Wells Fargo was unprecedented, but it may not be the last of its kind. It has become a powerful precedent for how regulators can discipline systemically critical financial institutions that fail to meet compliance and ethical standards. Unlike traditional fines, which can be absorbed as the cost of doing business, the asset cap was a structural constraint on the company’s operations. It limited the bank’s ability to grow, serve customers, issue loans, and participate in high-margin Wall Street business lines. It was a living penalty, a regulatory scarlet letter that reshaped how Wells Fargo operated at every level.

For the compliance and risk community, this evolution is of profound significance. It suggests that enforcement tools are expanding beyond punitive monetary settlements to include operational restrictions that fundamentally alter business strategy. This signals a clear shift in regulatory philosophy: punishment should not only be proportional to misconduct. Still, it should also force organizations to re-engineer the systems that enabled that misconduct in the first place.

Compliance leaders must now broaden their risk lens. A mature compliance risk assessment framework must consider not only reputational and financial risks but also operational penalties that can hinder competitiveness. Could your business withstand a regulator-imposed halt to product launches? A limitation on asset growth? A prohibition on acquisitions? These are no longer hypothetical concerns; they are real enforcement options, as Wells Fargo learned.

Moreover, structural penalties create long-term internal pressure. Wells Fargo invested heavily, incurring more than $2.5 billion in extra costs and hiring 10,000 additional compliance personnel to satisfy the consent orders. That level of expenditure may not be feasible for smaller institutions, making early detection and proactive compliance investment even more critical.

The future of enforcement is structural. Innovative compliance programs must prepare for this new reality before regulators force the issue.

4. Invest in the Right People

Wells Fargo’s long road to regulatory redemption was not paved by technology alone or process overhauls, and people drove it. After years of reputational damage, CEO turnover, and regulatory gridlock, the appointment of Charlie Scharf in 2019 signaled a fundamental shift. Scharf understood what prior leadership had not: you cannot reform risk culture without reforming the people responsible for it. He replaced key executives, restructured risk and compliance teams, and built a leadership bench equipped to navigate the demands of a post-scandal environment.

For compliance professionals, the takeaway is clear: people are the heart of your program. You can build a library of policies and procure the most advanced analytics platforms, but without qualified, empowered, and appropriately incentivized professionals, those systems will fail. Effective compliance begins with hiring not just for expertise but also for integrity and courage. Your CCO must have access to the board, independence from business pressures, and the authority to challenge decisions without fear of reprisal.

At Wells Fargo, the turnaround required hiring an “army” of more than 10,000 new risk and compliance professionals. While most companies will not need to scale at that level, the principle remains: a token compliance function cannot defend against systemic risk. The right people in the right roles with clear mandates and sufficient resourcing are the first line of defense.

Equally important is leadership. Scharf’s experience leading Visa and BNY Mellon gave him a strategic understanding of regulatory expectations. He began each executive meeting with a regulatory update, not as a formality but as a signal. This was not compliance theater. This was operational DNA.

In today’s risk environment, talent is your most significant differentiator. Invest in leaders who understand governance, not just growth. Because when crisis strikes, the question isn’t what systems are in place. It’s who is leading them.

What’s Next for Wells Fargo—and You

Now that the cap is lifted, Wells Fargo is poised to grow again. It can expand lending, scale its wealth management services, and bolster its Wall Street business. But as Scharf and analysts have noted, this is “still a journey.”

Even without the cap, consent orders remain in effect. More critically, public trust is still under repair.

For the rest of the financial sector and, frankly, any large organization, the lesson is this: enforcement is not just about punishment. It’s about operational reform. The Wells Fargo story serves as a blueprint for how misconduct can metastasize when culture, incentives, and oversight fail to align and how painfully slow and expensive the path back to credibility can be.

Compliance Is Not a Department—It’s a Discipline

The Wells Fargo saga is not merely a tale of scandal and sanction. It is a real-world case study of how compliance failures metastasize when unchecked and how painful, expensive, and prolonged the road to recovery becomes when structural change is delayed. For seven years, Wells Fargo was held in regulatory purgatory not because of a single incident but because its culture, controls, and leadership failed to recognize that ethics and governance are non-negotiable pillars of business continuity.

Each of the four lessons discussed ethical incentive alignment, stamina in regulatory remediation, preparing for structural penalties, and investing in the right people—reinforces a central truth: compliance is not episodic. It is continuous, cultural, and deeply tied to leadership.

When incentives ignore integrity, misconduct becomes inevitable. When organizations view compliance obligations as burdens rather than opportunities for reform, they erode trust. When regulators respond with operational penalties as they now can and will, compliance becomes not just a cost center but a barrier to growth. And when companies finally decide to rebuild, it is the strength and credibility of their people that determines whether that effort will succeed.

Wells Fargo survived its reckoning. But survival came at a steep price: lost market share, damaged reputation, investor doubt, and a compliance bill in the billions. For the rest of us, the goal is not to weather such a storm but to avoid it entirely. That means taking compliance seriously before the headlines, before the enforcement actions, and before the crisis.

In the post-Wells era, corporate compliance is no longer optional or siloed; it is a fundamental aspect of business operations. It is embedded, empowered, and expected to lead. As compliance professionals, our charge is clear: build systems that promote integrity, protect the enterprise, and earn the trust that regulators can’t mandate but can take away.

Resources:

  1. Wells Fargo Is Allowed to Grow Again After 7 Years Under Asset-Cap Penalty, by Gina Heeb in the Wall Street Journal.
  2. Wells Fargo Asset Cap Lifted by Fed, Paving Way for Growth by Yizou Wang in Bloomberg.
  3. Wells Fargo’s Asset Cap Has Been a Good Punishment in Bloomberg by Paul Davies.
Categories
Everything Compliance

Everything Compliance: Episode 155, To Tesla and Beyond Edition

Welcome to this edition of the award-winning Everything Compliance. In this episode, we have the quartet of Matt Kelly, Jonathan Marks, Jonathan Armstrong, and special guest panelist Hemma Lomax, all hosted by Tom Fox, the Compliance Evangelist.

  1. Hemma Lomax examines the customers of a compliance program and introduces us to the terms EX and CX. She shouts out to AI for podcasters.
  2. Matt Kelly delves into Google’s compliance spending announcement and asks why the company does not have a Chief Compliance Officer. He both shouts out and rants about Marjorie Taylor Greene and her reading list.
  3. Jonathan Marks gives us a primer on corporate governance. He shouts out the quiet compliance professionals who do the day-to-day spadework of compliance.
  4. Jonathan Armstrong takes a deep dive into the finances of Tesla and its profitability. He shouts out to Operation Spider’s Web.
  5. Tom Fox highlights Wells Fargo’s compliance remediation, the Fed’s asset cap placed on Wells Fargo, and its subsequent removal.

The members of Everything Compliance are:

Tom Fox, the Voice of Compliance, is the host, producer, and sometimes panelist of Everything Compliance. He can be reached at tfox@tfoxlaw.com. The award-winning Everything Compliance is part of the Compliance Podcast Network.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Code of Conduct as an Internal Control

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our goal is to provide you with bite-sized, actionable tips to help you stay ahead in your compliance efforts. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

How does your Code of Conduct act as an internal control?

For more information on this topic, refer to The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, 6th edition, recently released by LexisNexis. It is available here.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Board Oversight on Internal Controls

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our goal is to provide you with bite-sized, actionable tips to help you stay ahead in your compliance efforts. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

How can your board fulfill its role in oversight of your internal controls

For more information on this topic, refer to The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, 6th edition, recently released by LexisNexis. It is available here.