Categories
Blog

Compliance by Design: Future-Proofing Your Product Oversight and Governance

The US and the world financial services sector have entered a race of disruption and evolution unlike any other. While companies scramble to launch innovative solutions, be it instant payment technologies, crypto offerings, or AI-driven platforms, compliance professionals must ensure that regulatory rigor and consumer protection never become afterthoughts. Enter “Compliance by Design,” a proactive methodology that integrates compliance principles right into the DNA of product creation and governance.

As noted in a KPMG white paper entitled Compliance by Design, authors Gillian Kelly, Shane Garahy, and Donata Halpin explain that these strategies are not abstract considerations; they represent your daily battlefront. More importantly, these same challenges provide valuable compliance lessons. As compliance professionals, our responsibility lies in managing the fallout from regulatory lapses and actively preventing them. It is about embedding good governance into every aspect of product design and operational lifecycle. I have used the KPMG article as a starting point to review Compliance by Design for Compliance Professionals.

A Shift from Reactive to Proactive Compliance

The authors highlight a crucial compliance lesson: Moving from a reactive to a proactive approach significantly enhances consumer outcomes. (As Carsten Tams continually reminds us, it’s all about the UX.) Companies often adopt reactionary compliance strategies, acting primarily after issues surface. However, Compliance by Design necessitates embedding consumer protection requirements and regulatory oversight from the very beginning.

For compliance officers, the core takeaway is clear: You must anticipate and integrate. Proactivity in compliance is not simply a nice-to-have; rather, it is now a must-have. By defining positive user outcomes upfront and aligning them with clear product performance metrics, firms create built-in guardrails that help identify and mitigate risks from day one. Such an approach fosters not only stronger compliance but also greater consumer trust.

Addressing the Digital Transformation Risks

One significant issue identified by KPMG is the rapidity of innovation and its attendant risks. Product oversight frequently suffers when speed-to-market becomes the overriding priority. Compliance professionals must recognize that innovation, while exciting and essential, can inadvertently introduce new categories of consumer harm and regulatory exposure.

For example, artificial intelligence (AI) brings significant benefits and new risks, such as algorithmic bias, lack of transparency, and unanticipated operational vulnerabilities. Compliance by Design underscores the importance of integrating robust governance, rigorous testing, and continuous monitoring into the product development lifecycle, particularly when new technologies like AI and algorithmic trading are concerned.

Managing Regulatory Expectations

The regulatory landscape, especially in the financial services sector, is in constant flux, as the post-pandemic world has clarified. Whether adapting to the European Banking Authority’s guidelines or navigating the complexities introduced by the Senior Executive Accountability Regime (SEAR), compliance officers are increasingly called upon to demonstrate agility and clarity. For compliance, the arena is currently in a state of extreme flux as well.

By implementing automated compliance checks at early stages and continuously throughout a product’s lifecycle, compliance teams create a strong narrative of responsibility and preparedness, which is precisely what regulators demand. Such preemptive compliance strategies resonate positively during regulatory reviews and audits, making Compliance by Design a strategic advantage for any organization.

Enhancing Consumer Protection through Automation

Manual assurance approaches often falter due to limitations in scope and visibility, potentially allowing consumer detriment to go undetected. Compliance by Design advocates embedding automated testing into the product design, thereby vastly increasing detection capabilities across a consumer population rather than merely targeted subsets.

Automating compliance monitoring enhances consumer protection and significantly boosts operational efficiency. It reduces the manual labor burden on compliance teams and allows compliance officers to refocus their valuable time and expertise away from repetitive tasks towards more strategic compliance initiatives.

Leveraging Data for Compliance Effectiveness

Data collection and analytics remain underutilized resources in compliance circles. According to KPMG, integrating automation and harnessing data insights throughout the product lifecycle enable compliance professionals to establish early-warning systems based on accurate Key Performance Indicators (KPIs) and Key Risk Indicators (KRIs). These data-driven indicators facilitate proactive rather than reactive measures, preventing compliance issues before they escalate.

Compliance professionals must champion analytics integration within their governance frameworks, ensuring data accuracy and completeness. Organizations willing to invest in robust data strategies will find themselves more agile and responsive to regulatory shifts and better positioned to demonstrate robust oversight and accountability.

Tackling Legacy Systems and Knowledge Gaps

The authors identified one significant obstacle for compliance departments as legacy systems and inadequate documentation. Aging IT systems, compounded by incomplete data and inconsistent documentation, create significant barriers to effective compliance monitoring.

Compliance by Design calls for comprehensive understanding and documentation of products from inception, tackling potential legacy problems head-on. Regression testing and systematic IT reviews are crucial steps compliance officers can adopt to prevent future operational fallout from legacy system constraints. Addressing these problems upfront streamlines compliance oversight and mitigates the risk of hidden vulnerabilities resurfacing later in product lifecycles.

Establishing Clear Accountability Structures

An integral part of Compliance by Design is clarifying and enforcing accountability lines within organizations. The Senior Executive Accountability Regime (SEAR) emphasizes this principle, requiring senior leaders to have clear oversight and accountability for consumer outcomes and regulatory adherence. Compliance officers must seize this opportunity to embed accountability into their compliance culture.

This does not merely entail assigning responsibility; it is about fostering a corporate environment where compliance responsibilities are understood, embraced, and enforced at all organizational levels. A strong accountability framework helps organizations swiftly address emerging risks and assures senior executives and regulatory bodies that the firm is proactively managing its compliance obligations.

The Compliance Professional’s Call to Action

Compliance professionals occupy a unique position as custodians of regulatory integrity and consumer trust. By championing the Compliance by Design approach, compliance officers are empowered to transition their organizations from reactionary and issue-prone to proactive and resilient compliance frameworks.

Embracing the principles outlined by the authors means compliance officers can confidently navigate the complexities of regulatory landscapes, rapidly evolving technologies, and consumer-centric expectations. Such an approach will position organizations for immediate compliance successes and sustainable long-term integrity and operational excellence.

The path forward for compliance is clear. You should integrate compliance rigorously into product design from the outset, automate your oversight, harness your data, address legacy challenges proactively, and establish clear accountability. Compliance by Design is an essential business imperative for our digital age. It offers not only a road map but an opportunity. You can build stronger, fairer, and more resilient companies prepared to face any future challenge.
Categories
Blog

Compliance Lessons from Uber’s AI Playbook

Uber is no stranger to innovation. The ride-sharing giant has consistently embraced artificial intelligence (AI) to streamline operations, enhance customer satisfaction, and mitigate risks. An article in Digitalefynd discussed these strategies. The article explored how Uber employs AI, not simply transportation or tech. I have adapted the insights for the compliance professional by reviewing five ways Uber leverages AI. I also discuss how compliance practitioners can adapt these strategies to progress their compliance programs.

1. Efficient Matching and Allocation: Enhancing Your Resource Deployment

Uber uses advanced AI algorithms to match drivers to passengers rapidly. The system integrates data points such as rider location, traffic conditions, and driver availability to minimize wait times and maximize efficiency.

Compliance professionals face similar challenges, allocating compliance resources where they’re needed most precisely and promptly. By adopting data-driven AI models, compliance teams can better assess risks, prioritize actions, and assign resources efficiently. AI analytics can synthesize multiple data streams, like whistleblower reports, audit findings, or third-party due diligence information, ensuring that the compliance team’s attention and resources are allocated effectively. The result is reduced compliance risk, more responsive interventions, and ultimately, a more robust compliance posture

2. Dynamic Pricing: Adaptive Risk Assessment and Prioritization

Uber’s dynamic pricing model, known widely as surge pricing, uses AI to adjust prices in real-time to balance supply and demand. By analyzing historical data, real-time demand, and external factors like local events, Uber ensures availability and responsiveness during peak times.

A dynamic, AI-powered approach to risk assessment in corporate compliance can significantly enhance effectiveness. Compliance risk is dynamic. It fluctuates with new markets, regulatory changes, and emerging threats. Leveraging AI to adjust your risk scoring or prioritize compliance initiatives dynamically can enable teams to proactively respond to evolving circumstances, such as emerging sanctions, regulatory updates, or market-specific risks. Like Uber’s model, compliance functions could employ AI algorithms to identify heightened compliance risk periods and adapt their monitoring, investigations, and training accordingly. This ensures that your organization is always ready to respond to changing risk environments.

3. Route Optimization: Streamlining Investigations and Responses

Route optimization allows Uber to identify the most efficient routes in real time, considering factors such as traffic congestion and road closures. This proactive approach reduces delays and increases reliability.

Applying this calculus, compliance professionals can benefit from AI-driven optimization of investigations, audits, and compliance activities. AI can predict potential compliance bottlenecks and inefficiencies by analyzing historical compliance data and integrating real-time signals from various parts of the organization. Such intelligent route mapping ensures compliance investigations follow the most efficient path, avoiding unnecessary delays, repetition, or resources wasted on low-risk issues. As Uber guides drivers through traffic, AI can navigate compliance teams through complex data, reducing response times and enhancing investigative quality.

4. Fraud Detection: Proactive Risk Mitigation and Ethical Safeguarding

Uber deploys AI to detect and prevent fraud by analyzing transactional patterns, user behaviors, and anomalies, addressing threats before significant harm occurs.

Fraud detection parallels one of the core missions of any corporate compliance professional: proactively preventing misconduct. By adopting similar AI-powered detection mechanisms, compliance departments can enhance their ability to spot anomalies and unethical behavior within the enterprise, such as improper transactions, conflicts of interest, or insider threats. Machine learning models trained on historical compliance incidents can flag unusual activities early, allowing compliance officers to intervene before issues escalate. Enhanced fraud detection capabilities strengthen organizational integrity and build stakeholder confidence in your compliance ecosystem.

5. Predictive Maintenance: Shifting from Reactive to Predictive Compliance

Uber’s predictive maintenance strategy uses AI to forecast vehicle issues before they occur, scheduling maintenance proactively. This approach reduces downtime and improves reliability.

Compliance professionals can mirror this predictive mindset, moving from reactive firefighting to proactive risk management. AI can analyze extensive compliance datasets, like training completions, past violations, regulatory changes, employee feedback, and market trends, to anticipate compliance failures or lapses before they materialize. Predictive compliance modeling enables your team to schedule targeted interventions, training, or policy updates strategically and proactively, significantly reducing the likelihood of compliance breaches. Proactive maintenance of compliance systems enhances organizational resilience, reduces overall compliance costs, and bolsters stakeholder trust.

Uber’s commitment to artificial intelligence has gone beyond simply revolutionizing urban mobility. Its development offers a powerful example of how AI-driven techniques can transform compliance functions. AI empowers compliance teams to anticipate problems, streamline processes, optimize resource allocation, dynamically adapt to risks, and detect misconduct proactively. These approaches shift compliance from a cost center reacting to issues to a strategic asset proactively safeguarding organizational integrity.

As Uber continues to set new industry standards with AI, compliance professionals should admire these innovations and actively embrace their applications. Adopting an AI-enabled compliance approach positions your organization ahead of emerging risks and regulatory expectations, proving once again that compliance is not simply about responding to problems but anticipating and outpacing them.

After all, the road ahead for compliance is paved not just with good intentions but with strategic foresight, precise execution, and the intelligent use of technology. Uber’s journey underscores the power of AI to redefine operational excellence, and for compliance professionals, this is one ride worth taking.

Categories
Great Women in Compliance

Great Women in Compliance – Hearing the Unheard: Leading with Courage When the News Isn’t Good

There is a lot to unpack in this roundtable episode hosted by Sarah Hadden and Ellen Hunt. Listen as they flip the script on delivering bad news to explore how to educate our leaders to hear and act on bad news. Our experts Elaine Lin Hering and Deb Hennelly share and explore strategies on how to:

  • Build a trusting relationship before the crisis;
  • Incorporate role play as an anchor for the desired behavior when bad news needs action;
  • Understand that emotions are data that you need to leverage.
  • Address the “silence” that hinders ethical behavior, and
    Create real psychological safety.

🎧 Listen now on your favorite platforms, the Compliance Podcast Network and Corporate Compliance Insights

♥️ Thanks as always to our wonderful #GWIC community for your support. Have an idea or suggestion? Drop a note to Lisa Fine or Hemma Lomax.

Categories
Compliance Into the Weeds

Compliance into the Weeds: A Deep Dive into Employee Leaks and Corporate Culture

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into a compliance-related topic, literally going into the weeds to explore a subject more fully. Are you looking for some hard-hitting insights on compliance? Look no further than Compliance into the Weeds! In this episode, Tom Fox and Matt Kelly discuss the issues surrounding employee leaks of confidential information, drawing on insights from a recent SCCE Europe event.

They also consider the motivations behind such leaks, including dissatisfaction with corporate culture and ineffective internal reporting channels, exemplified by the recent leaks at Facebook. The episode reviews measures compliance officers can take to prevent leaks, such as implementing tight access controls, encryption, and improving communication during investigations. Practical tips for reducing leaks and the importance of trust in internal reporting are also highlighted.

Key highlights:

  • Discussion on Employee Leaks
  • Facebook’s Toxic Culture (or not) and Leaks
  • Addressing Internal Speak-Up Culture
  • Practical Tips to Prevent Leaks
  • Modern Communication Challenges

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

Compliance into the Weeds was recently honored as one of the Top 25 Regulatory Compliance Podcast.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Corporate Leaks and Compliance

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide you with bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today, we look at the implications of corporate leaks for a company’s culture and the role of a compliance function if they occur.

Categories
Blog

Compliance Leadership: The Art of Adaptation and Style Selection

Leadership in compliance isn’t merely about having expertise in regulatory frameworks or policies. It’s about effectively guiding a team through complex challenges, continuously evolving regulatory landscapes, and an ever-shifting corporate environment. Effective compliance leadership demands a nuanced understanding of leadership styles and the agility to adapt these styles to the demands of specific situations. Today, I dive into six distinct leadership styles first identified by Daniel Goleman and then written about by Rebecca Knight in her HBR article, “6 Common Leadership Styles — and How to Decide Which to Use When,” I use Knight’s article to explore how compliance professionals can integrate these styles to strengthen compliance cultures and organizational resilience.

Understanding Leadership Through a Compliance Lens

Goleman’s seminal research presented six leadership styles: coercive, authoritative, pacesetting, affiliative, democratic, and coaching​. While some of these styles naturally align with compliance efforts, others may initially seem counterintuitive or even detrimental. However, compliance professionals must appreciate and strategically deploy each style to address varying compliance scenarios effectively.

The Coercive Style: Compliance’s Necessary Evil?

Coercive leadership, characterized by a top-down, directive approach, demands immediate compliance. On its surface, this style seems antithetical to the principles of modern compliance, which emphasize collaboration, open dialogue, and transparency. Yet, consider a scenario such as managing an immediate compliance crisis—a data breach, sanctions violation, or serious misconduct allegation. In such instances, swift, decisive action with clear directions can be invaluable to mitigate harm and establish immediate corrective measures.

However, compliance leaders must exercise caution; coercive leadership has significant drawbacks, notably diminished morale, reduced engagement, and potential loss of trust. As Knight rightly notes, frequent reliance on coercive leadership can create a corrosive environment, undermining long-term compliance program effectiveness​. Hence, it’s crucial to limit this approach strictly to emergencies.

The Authoritative Style: Compliance Visionaries at Work

Contrasting starkly with coercive leadership, authoritative leadership excels in mobilizing individuals toward a shared compliance vision. Compliance leaders adopting this style clearly articulate how compliance contributes to overall organizational integrity, sustainability, and success. Whether introducing new compliance technologies, policies, or procedural adjustments, an authoritative leader demonstrates how each action aligns with the broader organizational objectives and regulatory requirements.

This approach helps embed compliance into the fabric of corporate culture by clearly demonstrating compliance’s strategic value. It fosters employee engagement and makes compliance not just a set of rules but a meaningful part of everyday operations.

The Pace-setting Style: High Standards, High Risks

Pace-setting leadership involves establishing and maintaining high standards of performance. Compliance professionals are typically meticulous, driven, and committed to excellence, making the pace-setting style a natural fit. Nonetheless, Rebecca Knight provides an essential cautionary note: the relentless pursuit of perfection, characteristic of this style, can lead to employee burnout and disengagement​.

Compliance officers must carefully manage their use of pace-setting leadership. It’s particularly effective in specialized compliance tasks where precision is paramount, such as preparing for external audits or implementing new regulatory protocols. However, balancing this intensity with other leadership styles can safeguard employee well-being and maintain sustainable compliance standards.

The Affiliative Style: Building the Compliance Community

The affiliative leader prioritizes relationship-building, emotional connections, and fostering a supportive compliance environment. In today’s corporate climate, where teams increasingly grapple with remote work or hybrid arrangements, affiliative leadership offers an essential anchor. It helps compliance professionals feel valued, connected, and integral to the team, significantly enhancing morale and commitment to compliance initiatives.

However, relying solely on affiliative leadership can leave critical feedback unaddressed. Therefore, Knight recommends coupling affiliative strategies with more directive styles, ensuring a healthy balance of encouragement and accountability in compliance teams​.

Democratic Leadership: Harnessing Collective Wisdom

The democratic leader believes in shared decision-making and soliciting diverse viewpoints. This inclusive approach can yield innovative compliance solutions, particularly beneficial when compliance teams confront unprecedented challenges or must develop novel strategies to meet new regulatory demands.

Yet democratic leadership requires time and extensive dialogue. This style may falter during a compliance emergency or when swift decision-making is critical. Thus, compliance professionals must discern wisely when inclusive discussions enhance compliance efforts or when they may lead to paralysis by analysis.

Coaching Leadership: The Long Game of Compliance

Finally, coaching leadership prioritizes team members’ personal and professional growth. This style aligns seamlessly with compliance’s foundational continuous improvement and training objectives. Coaching leaders consistently ask their teams how they can support them in achieving their compliance goals, fostering a culture of learning and development.

Compliance officers employing this style nurture a proactive, engaged compliance team eager to enhance their knowledge, skills, and abilities. The long-term payoff is substantial: sustained compliance effectiveness and a robust compliance culture resilient to ethical and regulatory challenges.

Adaptive Leadership in Compliance: The Ultimate Strategic Advantage

Goleman’s most critical insight is that effective leadership is not rigidly adhering to a single style but fluidly adapting based on circumstances. Compliance leadership, therefore, is inherently situational. Effective compliance officers deftly transition between leadership styles—authoritative when clarifying a compliance vision, democratic when developing new procedures collaboratively, coercive when addressing urgent compliance crises, affiliative when morale is flagging, pace-setting when precision is crucial, and coaching when fostering team growth.

Achieving this level of leadership agility requires developing emotional intelligence—understanding your team’s dynamics, motivations, and emotional states and adapting your leadership accordingly. Leaders can enhance emotional intelligence through self-reflection, feedback, coaching, and practice.

Compliance Leadership as a Dynamic Practice

Compliance leadership cannot afford stagnation. As compliance professionals, we operate in an ever-evolving regulatory and business landscape that continually challenges our assumptions and demands our adaptability. Mastering and appropriately deploying these six leadership styles—coercive, authoritative, pace-setting, affiliative, democratic, and coaching—positions compliance leaders to meet these challenges proactively.

By honing our adaptive leadership skills and embracing the full spectrum of leadership styles detailed by Knight, we strengthen our compliance programs and foster healthier organizational cultures. As compliance professionals, we can turn regulatory compliance from a perceived burdensome obligation into an integral, vibrant component of organizational success.

The call to compliance leadership is clear—let’s embrace its complexities, adapt effectively, and lead purposefully, understanding that flexibility is our greatest strength in the nuanced world of compliance.

Categories
Innovation in Compliance

Innovation in Compliance – Nikki Rausch on Harnessing Relationships for Sales and Effective Compliance

Innovation comes in many areas, and compliance professionals need to be ready for it and embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode,  host Tom Fox welcomes Nikki Rausch, the Sales Maven, to visit her unique journey and expertise in neuro-linguistic programming (NLP) and sales coaching.

Nikki shares her professional background and foray into NLP and how it transformed her communication skills, leading her to start her own business, Sales Maven. We cover key insights on simplifying the sales process using strategic conversations and frameworks like the ‘Selling Staircase’ and debunking common misconceptions about sales. Nikki emphasizes the importance of building rapport and permission-based selling, making the process more collaborative and less daunting for sellers and buyers.

Tom and Nikki also touch upon the importance of storytelling in making content memorable and techniques for scaling businesses by training teams to recognize buying signals and create curiosity. Whether in the corporate world of compliance or an entrepreneur looking to scale your business, this episode offers valuable strategies that can be applied across various fields. Don’t miss Nikki’s gift—a free training course on asking the right questions in sales calls, available through her website.

Highlights include:

  • Exploring NLP and Sales Techniques
  • The Selling Staircase Framework
  • Building Relationships in Sales
  • Positioning Yourself as a Solution Provider

Resources:

Nikkie Rausch on LinkedIn

Your Sales Maven

Free Training called Seal The Deal

Your Sales Maven Podcast

The Selling Staircase: Mastering the Art of Relationship Selling

Your Sales Maven Facebook & Instagram

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Use of Blockchain in Compliance

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today, we examine how blockchain can revolutionize compliance in various ways, from payments to third parties to contracts.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Superforecasting

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today, we look at how a compliance professional can use Superforecasting to improve your overall risk forecasting ability.

Categories
Blog

Creating a Compliance Monitoring Plan

Compliance professionals recognize that robust compliance programs do not simply happen; they require meticulous planning, thoughtful execution, and continual enhancement. Central to any thriving compliance framework is a solid compliance monitoring plan. Even seasoned compliance practitioners occasionally encounter challenges when constructing a monitoring strategy capable of effectively identifying, assessing, and mitigating compliance risks. In this guide explicitly tailored for corporate compliance professionals, we will explore key steps toward creating an effective compliance monitoring plan, drawing on the foundational principles outlined in the Hallmarks of an Effective Compliance Program from the FCPA Resource Guide, 2nd edition.

Compliance monitoring is the ongoing process of assessing and verifying a company’s adherence to applicable laws, regulations, and internal policies. Unlike reactive investigations, compliance monitoring proactively identifies potential issues before they evolve into significant problems or compliance violations.

Step 1: Define Objectives and Scope

Once you have identified your organization’s primary compliance risks through a comprehensive risk assessment, you must define clear and measurable objectives for your compliance monitoring activities. These objectives align directly with your broader compliance strategy, corporate mission, and risk appetite. Begin by establishing what success looks like for your compliance monitoring initiative. Is your primary goal to prevent regulatory breaches, detect internal misconduct promptly, or validate the effectiveness of internal controls? Articulated objectives enable your compliance function to measure progress accurately and demonstrate accountability to stakeholders.

Objectives should be SMART, specific, measurable, achievable, relevant, and time-bound to facilitate clear monitoring and reporting. Next, explicitly outline the scope of your monitoring activities. Determine whether you will monitor all compliance areas equally or strategically prioritize areas of heightened risk, such as international operations, third-party relationships, or high-risk transactions. Defining scope effectively helps allocate your finite compliance resources to the highest impact areas, thus maximizing your monitoring effectiveness. Incorporate feedback from cross-functional teams and relevant business units to ensure your defined scope aligns closely with organizational realities and practical constraints. Regularly revisiting and refining these objectives and scope based on evolving risks and business circumstances keeps your compliance monitoring plan relevant, flexible, and responsive. According to the Hallmarks, clear policies, procedures, and thorough risk assessment underpin a successful compliance program. Thus, ensure your objectives remain tightly integrated with identified risks and documented compliance standards.

Step 2: Develop Monitoring Procedures

With objectives and scope set, the next step is crafting detailed compliance monitoring procedures. Effective procedures must specify the methods, frequency, and tools you’ll use to assess compliance adherence systematically. Procedures should integrate various manual and automated methods to create comprehensive oversight. Regular audits, randomized sampling, targeted employee interviews, and comprehensive documentation reviews form the procedural baseline. It is crucial to identify precisely how each monitoring activity will be executed, who will perform these tasks, and how frequently they will occur. Additionally, incorporating continuous monitoring technologies provides proactive, real-time insights, enhancing the immediacy of your responses to potential compliance breaches.

Documenting these monitoring procedures meticulously ensures consistency, transparency, and accountability, aligning directly with the emphasis on rigorous oversight and robust internal controls. Incorporating clear documentation standards into these procedures provides evidence of compliance activity during internal and external reviews, establishing credibility and trust with stakeholders and regulators. Regularly review and update your monitoring procedures to reflect evolving regulatory requirements, emerging risks, and insights gained from previous monitoring activities. Such periodic reassessments are vital to maintaining effective monitoring practices that meet industry best practices and regulatory expectations, preparing your organization to respond confidently to regulatory scrutiny and internal audits.

Step 3: Assign Roles and Responsibilities

Clearly defining roles and responsibilities within your compliance monitoring plan is fundamental for seamless execution. Compliance team members must understand their duties, expectations, and associated deadlines. Designate who will conduct monitoring activities, evaluate monitoring results, and initiate necessary corrective actions. Assigning these roles based on individual expertise, experience, and authority helps ensure tasks are completed effectively and efficiently. Explicitly document these roles within your compliance governance framework, ensuring clarity and transparency.

The FCPA Resource Guide underscores the importance of adequate autonomy, authority, and resources allocated to compliance functions. Ensuring compliance personnel have delineated responsibilities enhances accountability, promotes clear communication, and supports rapid decision-making. Regular training and communication sessions reinforce these responsibilities, helping compliance team members remain informed and prepared to execute their roles effectively. Furthermore, clearly defined roles and responsibilities empower compliance personnel to act decisively, enhancing responsiveness and ensuring effective intervention when issues arise. Continually reassess and refine these roles as your compliance program evolves, ensuring they remain relevant, efficient, and aligned with organizational goals and regulatory requirements.

Step 4: Implement Continuous Monitoring and Reporting

Effective compliance monitoring must be continuous rather than episodic. Continuous monitoring provides regular, real-time insights into compliance performance, significantly improving your ability to identify and address issues promptly. Implementing technological tools such as data analytics software, automated alerts, and compliance dashboards can greatly enhance continuous monitoring efforts. These technologies provide real-time data, facilitating immediate recognition of compliance deviations and swift corrective action. Establish clear, comprehensive reporting frameworks to communicate monitoring results effectively across all organizational levels, from operational managers to senior executives and board members.

Reporting frameworks must include clearly defined frequency, format, and content, ensuring consistent and relevant information distribution. Transparent reporting aligns directly with the FCPA Resource Guide’s emphasis on adequate internal controls, fostering organizational transparency and accountability. Effective reporting frameworks facilitate informed decision-making, enable quick interventions, and promote organizational trust. Regularly revising reporting protocols based on feedback and evolving compliance needs ensures ongoing effectiveness and relevance.

Step 5: Follow-Up and Remediation

The final crucial step in your compliance monitoring plan involves structured processes for follow-up and remediation. When non-compliance is identified through monitoring efforts, promptly implement a clearly defined process for addressing such issues. The first action is to perform a thorough root cause analysis to comprehend the underlying factors contributing to the compliance violation fully. This analytical step is vital because addressing only superficial symptoms may allow systemic issues to persist, increasing the likelihood of recurrence. After identifying the root cause, develop targeted remediation plans to rectify these foundational weaknesses. These plans should detail precise actions, timelines, responsible parties, and required resources. Communicate these remediation actions throughout the organization, ensuring transparency and clarity among all stakeholders.

Verification processes must be robust and systematic, designed to rigorously assess the effectiveness of implemented remedial actions. Monitoring the outcomes of remediation activities is essential in demonstrating that the organization takes compliance failures seriously and is committed to continuous improvement. Regularly scheduled follow-up evaluations should be conducted, and the results communicated to compliance and senior management. Transparency during this phase is critical, as it builds credibility with regulators and stakeholders by clearly demonstrating that the organization learns from its mistakes and proactively takes corrective action.

Additionally, documenting every step of the follow-up and remediation process provides valuable evidence during external audits and reviews, showcasing organizational accountability. Adopting a disciplined approach to follow-up and remediation aligns directly with the FCPA Resource Guide’s emphasis on ensuring effective responses to compliance risks and issues. This structured approach mitigates risks and cultivates a culture of integrity, accountability, and continuous improvement within your organization, significantly enhancing the resilience and credibility of your compliance program.

Lessons for Compliance Professionals

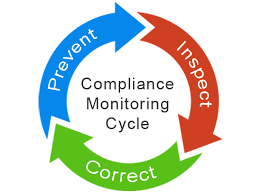
If all of this sounds like a continuous improvement loop, there is a reason. Developing a comprehensive compliance monitoring plan is foundational in cultivating and sustaining an effective compliance program. Compliance professionals must ensure monitoring is proactive, continuous, and aligned with broader organizational objectives and compliance strategies. Documented procedures, defined roles, continuous monitoring technology, transparent reporting, and rigorous follow-up constitute essential pillars supporting ongoing compliance effectiveness. Aligning these strategies with the Hallmarks of an Effective Compliance Program from the FCPA Resource Guide further solidifies your compliance initiatives, positioning your organization for long-term success, resilience, and integrity.