I recently wrote a five-part blog series on compliance through Michelangelo’s lens. In our Michelangelo Compliance Framework, we used five extraordinary projects to explore five disciplines of the modern compliance function: Challenge, Execute, Defend, Build, and Govern. Michelangelo gave us a model of the compliance professional as a builder. His work showed the importance of structure, execution, resilience, accountability, and the ability to turn an ambitious vision into something enduring.
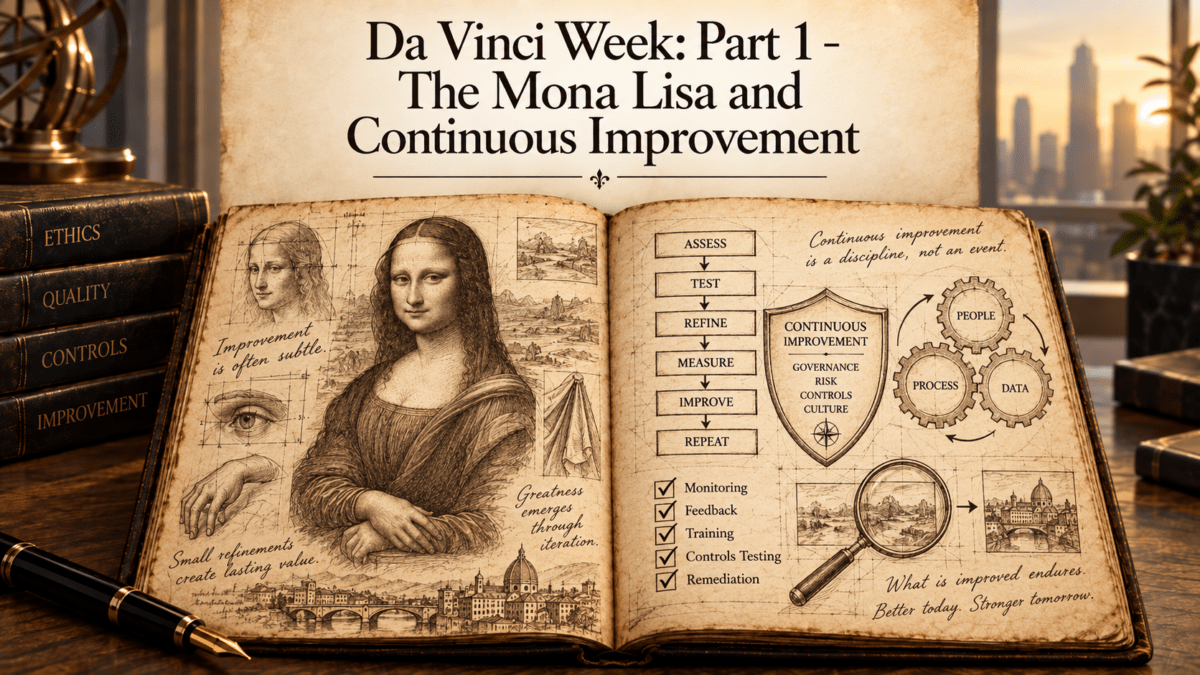
This week, I want to do the same through the lens of Leonardo da Vinci, who gives us a different model. Leonardo was an observer, investigator, experimenter, engineer, anatomist, artist, and relentless student of how things worked. Where Michelangelo offers lessons about building, Leonardo offers lessons about learning. That distinction underpins our five-part Leonardo Compliance Framework: Refine, Investigate, Innovate, Monitor, and Document. In this blog post 1, we begin with Refine and Leonardo’s most famous painting, the Mona Lisa.
The compliance lesson is continuous improvement. An effective compliance program is never truly finished because the business it supports is never truly static. Markets change. Employees change. Third parties change. Regulations change. Technology changes. Criminal methodologies change. Artificial intelligence is accelerating many of those changes simultaneously. For the Chief Compliance Officer (CCO) or compliance professional in 2026, the question is therefore not simply whether the company has a compliance program. The better question is whether the program is materially better today because of what the organization learned yesterday.
The Compliance Program Is Never Finished
One fascinating aspect of the Mona Lisa is Leonardo’s extended relationship with the work. He kept refining it as he developed his understanding of light, anatomy, optics, and human perception. That provides a useful metaphor for compliance because companies often approach compliance initiatives through the language of completion. Policies are issued, training is delivered, third-party systems are implemented, investigations are closed, remediation projects are completed, and risk assessments are presented to the board.
A policy issued three years ago may no longer address how the business operates. A successful third-party implementation may not account for changes in the company’s distribution model. A 100 percent training completion rate does not demonstrate that employees can apply the training when confronting an ethical problem. Closing a remediation item does not establish that the revised control reduced the underlying risk.
Leonardo offers a different approach. Completion should create an opportunity for observation and learning. Management should understand what worked, what did not work as expected, what changed in the business, and whether those lessons justify refinement of the program. That is continuous improvement.
Turn Compliance Failures Into Organizational Knowledge
The DOJ has made clear in the most recent iteration of the Evaluation of Corporate Compliance Programs (ECCP) that continuous improvement sits at the heart of modern expectations for compliance program effectiveness. A risk-based program should evolve as the company’s risks evolve, using risk assessments, investigations, audits, monitoring, employee feedback, transaction data, and lessons learned to inform changes. A company that identifies the same weakness year after year without changing its response has not created an effective learning system.
Leonardo’s approach to understanding the natural world was to look beneath the visible surface. Compliance professionals should apply the same discipline. Misconduct often signals a deeper weakness in the system, and root-cause analysis helps identify it and use the lesson to improve the program.
Risk Assessment Should Produce Management Action
The compliance risk assessment provides another important opportunity for refinement. Companies frequently devote substantial resources to identifying and ranking risks, producing a heat map, presenting the findings to management and the board, and repeating the process the following year.
Here the ECCP asks, “Is the risk assessment current and subject to periodic review?” Is the periodic review limited to a “snapshot” in time or based upon continuous access to operational data and information across functions? Has the periodic review led to updates in policies, procedures, and controls? Do these updates account for risks discovered through misconduct or other compliance program issues?
The principle applies to artificial intelligence. If AI adoption changes the company’s risk profile, the risk assessment should lead to governance action through measures such as an AI inventory, risk classification, approval processes, human oversight, monitoring, or technical controls.
A mature compliance program should be able to draw a line from an identified risk to a management decision. If the risk profile changes while resources, controls, monitoring, and governance remain unchanged, the risk assessment has generated information without generating action.
Use Data to Refine the Program
Leonardo was a relentless observer who recorded what he saw and used those observations to develop new ideas. Modern compliance functions possess an advantage he could scarcely have imagined: enormous quantities of organizational data.
Hotline information can reveal cultural patterns. Investigation data can identify recurring allegations and root causes. HR data may indicate retaliation. Transaction information can identify unusual payments. Third-party data can reveal concentrations of risk, while audit findings can identify recurring control weaknesses.
But these insights are not enough. Are these insights put into practice? The ECCP inquires: Does the company have a process for tracking and incorporating into its periodic risk assessment lessons learned either from the company’s own prior issues or from those of other companies operating in the same industry and/or geographical region?
Compliance analytics should not become a competition to create the most sophisticated dashboard. The objective is better decision-making. A business unit with very few hotline reports, for example, could have an excellent culture or an environment in which employees are reluctant to speak. The number alone does not tell the whole story.
Compliance should therefore combine quantitative information with qualitative evidence, including employee surveys, focus groups, exit interviews, investigations, management discussions, and audit findings. The objective is to understand what the data mean in the business context.
AI Accelerates the Need for Refinement
Artificial intelligence makes continuous improvement increasingly important because AI systems and their uses can change faster than traditional corporate governance cycles.
The ECCP asks companies to consider how emerging technologies such as AI affect their ability to comply with criminal laws, how related risks are incorporated into enterprise risk management, and how organizations mitigate unintended consequences and potential misuse. The ECCP asks some pointed questions: How does the company assess the potential impact of new technologies, such as artificial intelligence (AI), on its ability to comply with criminal laws? Is management of risks related to the use of AI and other new technologies integrated into broader enterprise risk management (ERM) strategies? What is the company’s governance approach to using new technologies such as AI in its commercial business and compliance program? The implication for the CCO is significant: AI risk cannot be treated as a once-a-year compliance exercise.
NIST’s AI Risk Management Framework and ISO/IEC 42001 provide useful approaches to this challenge because both emphasize governance and ongoing risk management. For the CCO, the broader lesson is that AI governance should operate as a management system rather than a policy-writing project. The organization needs to learn from incidents, testing, employee behavior, technological changes, and evolving business use, then adjust governance accordingly. The principle is the same as the Mona Lisa: refinement should follow learning.
Move the Board Conversation From Activity to Learning
Boards and Audit Committees can reinforce this discipline by shifting the compliance conversation. Compliance presentations frequently focus on activity metrics: employees trained, investigations closed, third parties reviewed, policies updated, and remediation items completed. These measures provide useful information about program operations, but they do not necessarily demonstrate effectiveness.
Directors should also understand what the organization learned during the reporting period, what investigations revealed about controls, what monitoring identified that management did not previously know, how the risk profile changed, and what the compliance function changed as a result.
The board should also understand whether those changes worked. This moves oversight from compliance activity to compliance effectiveness. It allows the CCO to present Compliance not simply as a collection of programs and controls but as a management system that identifies risk, learns from experience, and improves organizational decision-making.
The Mona Lisa Principle: Disciplined Refinement
Leonardo’s Mona Lisa gives the modern compliance professional a straightforward lesson about continuous improvement. An effective compliance program should develop through observation, evidence, learning, and a willingness to reconsider earlier decisions when circumstances justify change. The objective is not perpetual revision. It is disciplined refinement.
That distinction matters because continuous improvement can become counterproductive if it produces continuous disruption. Employees need stability, controls need sufficient time to operate, and management needs enough information to distinguish a meaningful trend from temporary noise. A compliance function that repeatedly changes policies, procedures, training, and controls without a clear risk-based rationale can create confusion rather than effectiveness.
Program refinement should therefore follow evidence. An investigation may reveal a systemic control weakness. Employee feedback may demonstrate that a policy is difficult to understand or apply. Monitoring may show that a control generates excessive false positives or is routinely circumvented. A regulatory development may require a different process, while an acquisition, new market, or technological change may materially alter the company’s risk profile. Artificial intelligence may introduce capabilities and risks that did not exist when the original governance structure was designed.
The CCO should have a disciplined process for converting those developments into program changes. Management should understand what triggered the proposed change, what risk it addresses, who owns implementation, and how the organization will determine whether the change produced the intended result. In this sense, continuous improvement should itself be governed.
A mature CCO should also be able to explain why today’s compliance program differs from the one the company operated two or three years ago. The answer should not simply be that policies were updated or new technology was purchased. The program should have changed because the organization learned something about its risks, controls, employees, third parties, culture, or business model and acted on that knowledge.
That is the central lesson of Refine, the first principle of the Leonardo Compliance Framework. Completion should not be confused with effectiveness. Root-cause analysis should produce program improvement, risk assessments should lead to management action, and data should help the organization understand what is happening rather than simply populate dashboards. When the evidence demonstrates that change is necessary, the organization should refine the program and then determine whether the refinement worked.
Leonardo models the compliance professional as a student of the organization. The CCO observes how the business operates, learns from failures and successes, and uses that knowledge to improve the compliance system. The measure of continuous improvement, therefore, is not how often the program changes. It is whether the program becomes more effective because the organization has learned.
From Refinement to Investigation
Continuous improvement depends upon understanding why problems occur. A company cannot meaningfully refine its compliance program if it treats each incident as an isolated act of employee misconduct. It must examine the systems, incentives, controls, management decisions, and behaviors that produced the outcome. That takes us to the second Leonardo principle: Investigate.
In Blog Post Two, we will consider Leonardo’s Anatomical Studies and will use Leonardo’s study of the human body as a framework for corporate investigations. Just as Leonardo looked beneath the surface to understand how interconnected systems functioned, modern compliance investigations should move beyond identifying misconduct to understanding its causes. We will examine how root-cause analysis connects investigations to remediation, why organizational justice matters, how investigation data can reveal systemic weaknesses, and what boards should understand when management reports that an investigation has been closed.