Categories
Blog

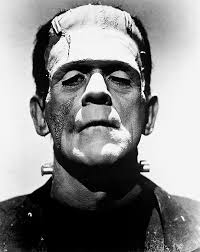
Compliance Lessons from Boris Karloff’s Frankenstein

Ed. Note: This week, leading up to Halloween, I will examine lessons for compliance professionals through the lens of the great Universal Movie Monsters: Frankenstein, Wolfman, Dracula, and The Mummy. First up is Boris Karloff’s film version of Frankenstein. 

============================================================

The 1931 classic Frankenstein, starring Boris Karloff as the iconic monster, offers more than gothic horror. It provides a rich framework for understanding corporate compliance. The film, adapted from Mary Shelley’s novel, tells the story of Dr. Henry Frankenstein, whose ambition to play God results in the creation of a monstrous figure. While focusing on the horror elements is easy and fun, a closer analysis reveals valuable lessons for compliance professionals and business leaders alike.

We will explore how this film version of Frankenstein mirrors real-world compliance challenges and how its themes of ambition, unchecked power, and ethical negligence offer critical insights into today’s corporate environment. We will also consider how Frankenstein offers a range of corporate compliance lessons that resonate with the key points raised by Nicole Argentieri in her recent speech to the Society of Corporate Compliance and Ethics (SCCE) and the 2024 Evaluation of Corporate Compliance Programs (2024 ECCP).

The Perils of Ignoring Ethical Oversight: Frankenstein’s Creation and Corporate Risk

Dr. Frankenstein’s pursuit of creating life was a scientific marvel, but his failure to consider his work’s moral and ethical implications led to his downfall. His ambition closed his eyes to the responsibilities that come with power and innovation. This reflects a critical issue for corporate compliance: the danger of ignoring ethical oversight in the rush to achieve business objectives.

In her SCCE speech, Nicole Argentieri highlighted the importance of ethical decision-making and the need for leadership to embed compliance into every facet of business operations. The 2024 ECCP emphasizes that compliance officers must have the authority and autonomy to act independently and influence decision-making at the highest levels of an organization. Just as Frankenstein lacked the oversight to rein in his dangerous experiment, a lack of oversight in corporate governance can result in catastrophic outcomes.

The clear lesson for compliance professionals is that organizations must prioritize ethical oversight and ensure compliance is involved in strategic decision-making. As the 2024 ECCP advises, having a strong compliance function with direct access to the board of directors can prevent “Frankenstein-like” risks from spiraling out of control. Ethics cannot be an afterthought; just as Frankenstein learned too late that his creation needed more than raw ambition, organizations must recognize the importance of ethical governance before it’s too late.

Risk Management: Expecting the Unexpected

One key reason for Frankenstein’s failure was his inability to anticipate the risks his creation posed. He believed he could control the creature, but without proper planning, things quickly spiraled out of control. This is a critical lesson in risk management for any organization. The creature was the manifestation of uncalculated risk—an outcome born of Dr. Frankenstein’s failure to consider the “what ifs.”

Argentieri’s speech and the 2024 ECCP emphasize the importance of addressing emerging risks and implementing proactive risk management strategies. As business models evolve, new risks emerge, and compliance professionals must be vigilant in identifying and addressing them before they become uncontrollable.

Compliance professionals should continuously evaluate and adjust their risk management strategies. This aligns with Argentieri’s recommendation that compliance programs must be agile and anticipate emerging risks, especially in areas such as new technologies, cybersecurity, and third-party relationships. A comprehensive risk management process that includes scenario planning and stress testing can prevent corporate “creatures” from escaping the lab and causing damage.

Accountability and Governance Failures

Dr. Frankenstein operated without accountability, answerable only to himself. His lack of governance resulted in a situation without checks and balances on his actions, and his poor judgment led to tragic consequences. The creature’s actions, while horrifying, can be traced back to Frankenstein’s governance failures.

Argentieri emphasized in her SCCE speech that the DOJ expects organizations to maintain a strong compliance culture backed by a governance structure that holds individuals accountable for their actions. The 2024 ECCP builds on this expectation, stressing that compliance programs must ensure accountability at all levels—from executives to front-line employees.

Effective compliance programs must have strong governance structures to hold individuals accountable for their decisions. This is more than just ensuring policies are in place; it’s about creating a culture where employees at every level understand their ethical responsibilities. Just as Frankenstein should have been accountable for the consequences of his experiment, corporate leaders must be held accountable for the risks and decisions they make within the company.

The Ethical Consequences of Secrecy

In Frankenstein, secrecy plays a critical role in Dr. Frankenstein’s downfall. He isolates himself from his peers, hiding the details of his experiments out of fear that others will not understand or approve. This secrecy prevents him from receiving the input and guidance that could have prevented disaster.

Similarly, corporate secrecy can breed ethical violations. In her speech, Argentieri discussed the importance of transparency in compliance efforts, particularly when addressing misconduct. The 2024 ECCP emphasizes open communication within organizations, noting that secrecy or a culture of silence can lead to deeper ethical violations, regulatory breaches, and, ultimately, significant legal consequences.

Compliance professionals must constantly work to foster a culture of transparency and open communication within their organizations. Indeed, the DOJ sees compliance professionals as the holders of institutional justice and institutional fairness in their organizations. Employees should feel empowered to raise concerns without fear of retaliation. Compliance professionals should encourage whistleblowers, monitor for red flags, and ensure that no department operates in secrecy. In the same way, that Dr. Frankenstein’s isolation led to his downfall, a corporate culture of secrecy can result in unethical behaviors festering in the shadows.

Remediation and the Need for Swift Action

One of the more tragic elements of Frankenstein is Dr. Frankenstein’s inability—or refusal—to remediate his mistakes. Instead of acknowledging the harm his creation causes and taking steps to stop it, he spends much of the film trying to avoid responsibility. This refusal to act only exacerbates the problem, leading to even more destruction.

In her SCCE speech, Argentieri emphasized the importance of remediation when compliance issues arise. The 2024 ECCP reinforces this point, stating that companies must take swift action when misconduct occurs to address the immediate issue and prevent future violations. A failure to remediate can lead to a loss of trust from regulators, stakeholders, and the public.

Companies must act swiftly to remediate any ethical or compliance violations. This means conducting thorough investigations, holding wrongdoers accountable, and implementing corrective measures to prevent similar issues in the future. Dr. Frankenstein’s inaction led to tragic consequences, and in the corporate world, failure to remediate can result in reputational damage, legal penalties, and a loss of public trust.

Creating a Culture of Compliance and Ethical Awareness

Ultimately, Dr. Frankenstein’s downfall can be traced to his failure to create an environment that valued ethical considerations and accountability. He was driven by ambition without the ethical grounding to manage his creation responsibly.

Argentieri’s speech stressed the importance of building a culture of compliance and ethical awareness within organizations. The 2024 ECCP echoes this, highlighting that culture is the foundation of an effective compliance program. A company’s culture should not only encourage compliance but make it clear that ethical behavior is a core value of the organization.

Compliance professionals should focus on building a strong ethical culture within your organization. Compliance programs are most effective when employees at all levels buy into the company’s ethical mission. Training programs, consistent messaging from leadership, and visible consequences for unethical behavior are all crucial components of creating this culture.

The Boris Karloff version of Frankenstein may be categorized as a horror film, but its compliance lessons are relevant to any organization today. From respecting ethical boundaries to the importance of accountability, risk management, and training, the film underscores the dangers of unchecked ambition and the value of thoughtful, well-designed compliance frameworks. As compliance professionals, we must ensure that our organizations don’t become modern-day Frankenstein’s, creating monsters we cannot control.

Join us tomorrow as we consider the corporate branding lessons for the compliance professional from the Bela Lugosi movie version of Count Dracula.
Categories
Blog

2024 ECCP on Accessing Data

In the recently released 2024 Update to the Evaluation of Corporate Compliance Programs (2024 ECCP), the Department of Justice (DOJ) has brought new challenges and opportunities for compliance professionals. One of the most significant changes revolves around data access and the role data plays in an effective compliance program. In this blog post, we’ll explore the key takeaways from the updated guidance and what compliance professionals must do to meet these new expectations, especially when gaining and maintaining access to the right data. This is no longer just about best practices; it is now table stakes. Matt Kelly and I explored this question in this week’s Compliance into the Weeds edition.

Now More Than Ever

One of the most notable aspects of the DOJ’s 2024 update is its focus on data access for compliance professionals. The DOJ has made it clear that if you do not have sufficient access to data, you cannot adequately monitor compliance, detect issues, or remediate problems. Compliance officers are no longer given a pass when they say, “I didn’t have access to the data.”

How did we get here? Part of this shift can be attributed to companies that have demonstrated excellence in leveraging data to bolster their compliance programs. Through the heat of DOJ investigations, these businesses have proven that with the right data, compliance officers can detect misconduct more quickly and prevent violations altogether. At the same time, the DOJ recognizes that many companies still struggle to provide their compliance teams with the data they need to do their jobs effectively.

Data Access: From Best Practice to Table Stakes

In prior years, having a robust data analytics program for compliance was considered a gold standard. It was an aspirational goal that companies could work toward. However, as the DOJ has seen companies implement highly effective data programs, what was once a best practice is now table stakes. If your compliance program can’t access the right data in real-time or near-real-time, you’re not just behind the curve—you’re putting your organization at risk.

Compliance officers can now point to this updated guidance and tell senior management: “This isn’t optional anymore.” You need the resources, tools, and support to access and analyze data effectively. The DOJ’s guidance clarifies that if your company faces an investigation, the inability to access relevant data won’t just be an inconvenience; it will be seen as a compliance failure.

The Six Key Questions: A Roadmap for Data Access

The 2024 ECCP includes six specific questions related to data access, which serve as a roadmap for what compliance officers need to ask within their organizations. While a DOJ prosecutor may not ask all six in any given case, companies should be prepared to answer them all. We will break down how compliance professionals should approach each of these questions.

Does Compliance Have Sufficient Access to Data?

The first question asks whether compliance and control personnel have direct or indirect access to relevant data sources for timely and effective monitoring or testing. In other words, can the compliance team get the information they need when they need it?

This can be a major hurdle for many companies, especially those with complex IT ecosystems. If you’ve gone through multiple mergers and acquisitions, chances are you’re dealing with a variety of legacy systems that don’t “talk” to each other. Compliance officers might find themselves chasing down data from various silos across different business units, which can delay their ability to spot red flags.

What You Should Do

  • Map out your data sources. Know where all relevant data resides, from ERP systems to HR software and procurement platforms.
  • Identify bottlenecks. If your compliance team encounters roadblocks when accessing data, document those challenges and bring them to senior management.
  • Collaborate with IT. Ensure that IT systems are integrated and compliance has the tools to pull and analyze data without delay.

Are There Impediments to Accessing Data?

The second question focuses on barriers preventing compliance from accessing data. These barriers could be structural, such as outdated or incompatible systems, or they could be cultural, such as senior management not prioritizing compliance’s data needs.

What You Should Do

  • Address structural and cultural issues: If your company uses disparate systems, work with IT to create a data lake or central repository for key compliance data. Culturally, ensure that leadership understands the importance of compliance’s access to data and empowers the team accordingly.

Does Compliance Have the Tools to Analyze Data?

Once you can access the data, do you have the tools to analyze it effectively? This question goes beyond simply having access to the data—it’s about whether you have the analytics capabilities to make sense of it.

What You Should Do

  • Invest in the right tools. Data access means nothing if you can’t analyze the information. Invest in data analytics platforms, allowing your compliance team to automate risk assessments, flag potential issues, and generate real-time reports.
  • Train your team. Ensure that compliance personnel are trained on how to use these tools effectively. Analytics without insight is just noise.

Is Data Maintained Properly?

The fourth question concerns data maintenance. Is data stored securely, and is it accurate and reliable? The DOJ wants to ensure that companies don’t just pull data from disparate sources without validating its accuracy.

What You Should Do

  • Validate your data. Work with IT to ensure that data is accurate and up-to-date. Compliance teams need to know that the information they are using is reliable.
  • Establish data governance protocols. Set clear guidelines for data maintenance, including how data should be stored, accessed, and updated.

Is the Company Leveraging Data Analytics to Improve Compliance?

This question is at the heart of the DOJ’s updated guidance. It asks whether companies are using data analytics to create efficiencies in compliance operations and to measure the effectiveness of their compliance programs.

What You Should Do

  • Integrate data analytics into your compliance program. Use data to identify risk patterns, monitor employee behavior, and assess the effectiveness of your compliance efforts.
  • Review your analytics strategy regularly to ensure that you’re continually improving how you use data analytics to enhance your compliance program.
  1. How Precise is Your Data?

Finally, the DOJ asks about the precision of your data. This question goes beyond accuracy—it’s about whether you’re getting the right data at the right level of detail.

What You Should Do

  • Refine your data collection efforts. Ensure you collect precise, relevant data that aligns with your compliance needs. Broad, imprecise data won’t help you detect or prevent misconduct.

Communicating the Importance of Data Access to Senior Management

One of the most important takeaways from the 2024 ECCP update is that compliance officers now have a concrete basis to advocate for better data access. This is no longer about wish lists or best practices—it’s a regulatory expectation. Compliance officers must have honest conversations with senior management and the board about the company’s current data capabilities and where improvements are needed.

Companies often invest in technology when a problem arises, only to pull back once the issue is resolved. This cycle leaves compliance teams under-resourced and needing help to keep pace with evolving risks. The 2024 ECCP gives compliance officers the leverage to push for sustained investments in data access and analytics.

The DOJ’s 2024 update to the Evaluation of Corporate Compliance Programs underscores the critical importance of data access and analytics for modern compliance programs. It is no longer enough to have policies in place; compliance officers need the right data at the right time and the tools to analyze it effectively. The questions posed by the DOJ should serve as a guide for structuring your data access strategy and ensuring that your compliance program is up to the task.

By taking proactive steps to improve data access and analytics, compliance professionals can meet regulatory expectations and build stronger, more resilient programs that can detect and prevent misconduct before it escalates into a serious issue.

Categories
Innovation in Compliance

Innovation in Compliance: Evie Wentink on Rethinking Compliance

Innovation comes in many areas and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast.

In this episode, Tom welcomes back Evie Wentink to discuss the importance of rethinking ethics and compliance practices.

Evie shares insights from her recent LinkedIn articles on best practices for ethics hotlines and the importance of finding creative ways to engage employees in compliance topics. She reads a whimsical Dr. Seuss-inspired piece on reaching ethics hotlines and emphasizes the need for compliance messaging to be approachable and engaging. Additionally, Evie discusses the challenges compliance professionals face with limited budgets and offers practical solutions such as leveraging LinkedIn for networking and creating low-cost, effective compliance awareness tools.

The conversation also touches on the significance of changing the narrative around ethics and compliance for younger generations. Evie shares her experiences discussing compliance with her children and highlights the need for better education in schools to prepare future employees. She concludes by mentioning her new website, Ethical Edge Experts, and various platforms she’s using to spread compliance awareness. Tom and Evie agree on the necessity of continuous dialogue and innovation in the compliance field.

Key Highlights:

  • Rethinking Compliance Practices
  • Creative Messaging for Ethics Hotlines
  • Leveraging Low-Cost Resources
  • Engaging Managers in Compliance

Resources:
Evie Wentink on LinkedIn

Evie’s Top 10 Compliance Back to Basics

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
Compliance Tip of the Day

Compliance Tip of the Day: Everything Old is New Again: The John Deere FCPA Enforcement Action

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements.

Whether you’re a seasoned compliance professional or just starting your journey, our aim is to provide you with bite-sized, actionable tips to help you stay on top of your compliance game.

Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law.

Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today we review the basics of the John Deere enforcement action and why it is so instructive for compliance professionals.


Categories
Blog

Tone at the Top Week: Part 5 – CCOs Using Town Halls to Build Compliance

This week, we have been exploring how Chief Executive Officers and other senior executives can set an appropriate Tone at the Top by actually walking-the-walk of compliance rather than simply talking-the-talk of compliance. For any corporate compliance program to succeed, the commitment of senior leadership is essential. When establishing and maintaining the right Tone at the Top, few opportunities are as effective and personal as town hall meetings.

Town halls provide CEOs and senior executives with a direct platform to engage with employees across the organization, offering an authentic way to reinforce the importance of compliance. Unlike emails or formal reports, town halls allow real-time interaction, allowing leadership to connect directly with employees and make compliance a part of the company’s culture.

In this concluding blog post from this 5-part series, we will explore how CEOs and other corporate leaders can use town hall meetings to establish and maintain an appropriate tone at the top for a best practices compliance program. From including compliance in every meeting to addressing specific ethical challenges and fostering open dialogue, these strategies will help create a culture where compliance is seen as a shared responsibility and a driver of long-term success.

  • Include Compliance in Every Town Hall

One of the most effective ways to reinforce the importance of compliance is to make it a regular topic of discussion in every town hall meeting. Whether covering updates on regulatory changes, sharing new company policies, or discussing recent compliance issues, consistently integrating compliance into your messaging demonstrates that it is a key part of the company’s business strategy.

The obvious significance is that when compliance is a constant in company communications, employees start to understand that it is not a separate, siloed responsibility but a core element of the business’s operations. Regularly addressing compliance issues signals to employees that ethical behavior is as critical to the company’s success as financial performance or market expansion.

How to Implement

  • Dedicate a section of each town hall to discussing compliance. This could include updates on new business regulations, how the company adapts to changing legal landscapes, or reminders of key compliance policies.
  • Use the platform to highlight how compliance contributes to business objectives. For example, explain how maintaining compliance with environmental regulations helps the company avoid penalties while supporting sustainability goals.
  • Regularly including compliance topics also shows that leadership views compliance as proactive rather than reactive and that ethical behavior is a forward-thinking component of company strategy.

By consistently including compliance in town hall discussions, you reinforce its value and ensure it stays at the top of employees’ minds.

  • Address Specific Ethical Challenges

Town halls are an ideal venue to address specific compliance or ethical challenges the company may be facing. Whether dealing with emerging regulatory risks, handling a recent compliance breach, or navigating ethical dilemmas in high-stakes business decisions, discussing these issues openly with employees helps build trust and foster transparency.

It is not so much that employees need to know that leadership is aware of compliance challenges and actively working to address them. Discussing these challenges openly sends a message that compliance is a shared responsibility across the organization. This approach also helps demystify the compliance process and shows employees that issues are handled systematically and transparently.

How to Implement

  • When a new compliance challenge emerges—whether it’s a change in industry regulations, a data privacy issue, or a new ethical dilemma in business operations—use the town hall to explain the issue clearly. Describe what the company is doing to address it and what is expected of employees to help navigate the challenge.
  • Emphasize that compliance is not just the responsibility of the legal or compliance team but requires every employee’s involvement. This ensures that compliance issues are not seen as external or distant from day-to-day operations.
  • Consider sharing examples of companies or industries where a failure to address ethical challenges led to significant risks or damages. This helps illustrate the real-world consequences of neglecting compliance.

By openly addressing specific ethical challenges, you build a culture of accountability in which employees feel empowered to participate in compliance efforts.

  • Invite Questions About Compliance

One of the most powerful aspects of town hall meetings is their interactive nature. Inviting employees to ask questions about compliance-related topics shows that leadership is open to dialogue and committed to resolving concerns. This openness encourages a culture where employees feel safe raising potential compliance issues and know their voices will be heard.

As I have said many times, the flip side to a culture of speaking up is a culture of listening up. Nothing shows this better than soliciting questions at a town hall, for encouraging questions demonstrates compliance as a collaborative effort. It shows employees that leadership values their input and is willing to engage in a two-way conversation about ethical issues. This is especially important for fostering an environment where employees feel comfortable reporting concerns, knowing that leadership will take them seriously.

How to Implement

  • Set aside time during each town hall for a Q&A session focused on compliance. Let employees know they are welcome to ask about compliance issues related to company policies, regulatory changes, or ethical dilemmas.
  • Ensure that responses to compliance-related questions are thoughtful and demonstrate a commitment to transparency. If an employee raises a concern, provide an actionable response or explain how the company will investigate further.
  • Follow up after the town hall on any unresolved questions. This shows that leadership is committed to addressing compliance concerns beyond the meeting and reinforces trust.

Inviting questions and engaging in meaningful dialogue helps build a culture of openness and encourages employees to take an active role in compliance.

  • Highlight Compliance Success Stories

Town halls also provide an excellent opportunity to celebrate successes. By sharing stories of how compliance actions have helped the company avoid risks or achieve positive outcomes, you reinforce the idea that compliance is a value driver, not a burden. Highlighting these stories shows employees that compliance is not just about avoiding penalties but enabling the company to thrive in a complex regulatory environment.

This is one of the time-honored ways to build incentives in an organization. Sharing success stories helps build employee buy-in and engagement with the compliance program. When employees see the tangible benefits of compliance, they are more likely to view it as a positive and necessary part of their work. This also helps combat the perception that compliance is simply about limiting risk or avoiding punishment.

How to Implement

  • Use town halls to share specific examples of compliance successes. For instance, you might highlight how the company avoided a regulatory fine by proactively addressing a compliance risk or how strong compliance practices helped secure a valuable business partnership.
  • Frame compliance successes in a way that shows how they contribute to broader company goals, such as market expansion, reputation management, or innovation.
  • Recognize the individuals or teams who contributed to these compliance successes. This public recognition reinforces that the organization values and rewards ethical behavior.

You highlight compliance success stories and demonstrate that compliance drives long-term value and growth.

  • Building a Strong Compliance Culture Through Town Halls

Town hall meetings are one of the most powerful tools CEOs and senior executives can use to establish and maintain an appropriate tone at the top for a best practices compliance program. By including compliance in every meeting, addressing specific ethical challenges, inviting questions, and sharing success stories, leaders can foster a culture where compliance is not just a requirement but a shared responsibility and a source of competitive advantage.

When employees hear directly from leadership about the importance of compliance, they are more likely to internalize the message and make ethical behavior part of their daily work. Through regular and open communication in town halls, CEOs can build a strong compliance culture that drives long-term success for the organization.

I hope you have enjoyed and found this five-part series on Tone at the Top. Equally importantly, I hope this more outline format will allow you to cut and paste this information into a Memo you can send to your CEO and other senior executives to give them some concrete steps they can take to improve your organization’s culture so that your organization will do business ethically and in compliance. Additionally, it will give you an audit trail on this issue if a regulator ever comes knocking.

Categories
Innovation in Compliance

Innovation in Compliance: The Evolution of Compliance and Technology: An Interview with Stuart Breslow

Innovation comes in many areas and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast.

In this episode, Tom welcomes Stuart Breslow, a member of the Board of Directors at StarCompliance., who takes a deep dive into the evolution of tech solutions for compliance.

Breslow has had extensive journey in compliance, including professional roles at Morgan Stanley, Credit Suisse, McKinsey, and Google Cloud. He was the CCO at Morgan Stanley. Our conversation takes a deep dive into the transformation of compliance through technological solutions, the evolution of Codes of Conduct, and the impact of digital tools on compliance efficiency.

Breslow advocates for the use of technology to scale compliance efforts, address evolving challenges, and integrate compliance more seamlessly with business operations. Emphasizing data analysis and proactive risk identification, Breslow believes that modern compliance tools not only enhance efficiency and effectiveness but also contribute significantly to business profitability. Breslow also explores the future role of generative AI and how StarCompliance is poised to leverage advanced data management to enhance compliance functions.

Key Highlights:

  • Evolution of Compliance Technology
  • The Role of Codes of Conduct in Compliance
  • Digital Transformation in Compliance
  • Future of Compliance with Generative AI

Resources:
StarCompliance

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
Blog

Bank of America’s Corporate Culture Crisis: Part 3 – The Role of Internal Controls

Compliance professionals constantly seek to understand how systemic issues within corporate hierarchies can lead to severe consequences. The recent revelations about Bank of America’s (BoA) persistent workplace culture problems are a powerful reminder of compliance’s critical role in safeguarding employees and the organization.

This week, I will explore the BoA failure around workplace culture from various perspectives articulated by the Everything Compliance gang, including Karen Woody, Jonathan Armstrong, Matt Kelly, Karen Moore, and Jonathan Marks. This exploration will include the failure of internal controls, failures by the Board and senior management, culture failures around highly driven, self-selecting employees, and the cultural miasma that is BoA from a perspective from across the pond. In Part 3, we will consider the role of internal controls.

Internal controls are often seen as the backbone of an organization’s ability to operate efficiently, ethically, and within the bounds of the law. They serve as the safety net that catches errors deters fraud, and ensures that policies are not just theoretical but are put into practice. However, the recent revelations in the Wall Street Journal (WSJ) surrounding the culture of overwork at a major financial institution, where junior bankers were expected to work excessively long hours, shine a spotlight on a critical failure in internal controls—not in their design, but in their execution and monitoring. This blog post will explore the lessons compliance professionals can learn from this situation, focusing on implementing, actively managing, and enforcing internal controls.

Understanding the Control Environment

The control environment is at the heart of any robust internal control system. This includes the corporate culture, employee attitudes toward internal controls, and the tone set by senior management. It’s the foundation upon which all other aspects of internal control are built. When the control environment is weak or toxic, as in the situation under discussion, the entire control structure can crumble.

In this case, BoA had ostensibly implemented controls to prevent overwork—junior bankers were required to self-report their working hours. If they exceeded a certain threshold, this would trigger a review by HR. However, this control was ineffective because those responsible for enforcing it did not take it seriously. Managers instructed their subordinates not to report excessive hours, bypassing control entirely. Additionally, think about the basic conflict of interest (READ: Absurdity) in having the person the control was supposed to monitor input the information for the control to activate.

For the compliance professional, this emphasizes that your control environment is only as strong as the commitment of those enforcing it. Senior management must set the tone and ensure that it resonates throughout the organization. When internal controls are ignored or undermined, it’s often a sign that the control environment is flawed.

The Role of Monitoring and Remediation

Internal controls are not static; they require ongoing monitoring and, when necessary, fine-tuning or remediation. In the BoA situation, the institution needed to adequately monitor the effectiveness of its controls. Even after the tragic death of a junior banker, which should have been a clear signal that the controls in place were not working, there was no significant overhaul or improvement in the control environment.

Monitoring is a critical component of internal control, as it allows an organization to detect weaknesses and address them before they lead to significant issues. In this case, the failure to monitor and remediate allowed a toxic culture to persist for years, ultimately leading to repeated tragedies.

For the compliance professional, the lesson is clear: regular monitoring of internal controls is essential. When weaknesses are identified, they must be addressed promptly and effectively. A failure to remediate control weaknesses leaves an organization vulnerable to risks and can signal to employees that the controls—and the culture—are not taken seriously.

The Flaws of Self-Reporting as a Control

One of the most striking aspects of this case is the reliance on self-reporting as a key control mechanism. While self-reporting can be helpful, it is far from foolproof, especially in environments with significant pressure to conform to unrealistic expectations. In this instance, the control requiring junior bankers to self-report their hours was ineffective because the reporting was neither enforced nor monitored.

The problem with self-reporting as a control is that it places the onus on the individuals being controlled, which can create a conflict of interest. Employees may feel pressured to underreport or falsify their time to meet expectations or avoid repercussions. With independent verification and oversight, self-reporting is likely to be reliable.

For the compliance professional, the starkness of the lesson could not be more profound. Self-reporting should not be relied upon as the sole or primary control in a high-risk environment. It should be supplemented with independent verification methods, such as automated time tracking, regular audits, or cross-referencing with other data sources. This approach ensures that the data collected is accurate and that controls are truly effective.

Automation and Technology in Internal Controls

Given BoA’s size and sophistication, it is somewhat perplexing that more robust, automated controls were not implemented. In today’s technologically advanced world, numerous tools can automatically track employee hours, monitor for signs of overwork, and flag potential issues for review. These tools can remove the burden of self-reporting and provide more accurate, real-time data.

For example, many organizations use software that tracks employee computer activity, monitors login and logout times, and even tracks time spent on specific tasks. This data can then be used to identify patterns of overwork and take proactive measures to prevent burnout or health issues.

For the compliance professional, it is a direct lesson that leveraging technology can significantly enhance the effectiveness of internal controls. Automated systems can provide continuous monitoring, reduce the risk of human error, and offer objective data that can be used to identify and address potential issues before they escalate.

The Importance of a Holistic Approach

Finally, every compliance professional must recognize that internal controls cannot operate in a vacuum. Internal controls must be part of a broader, holistic approach to risk management and compliance. This includes fostering a strong ethical culture, regularly training employees at all levels, and ensuring transparent, accessible channels for reporting concerns.

With BoA, the failure was not just in the specific control related to work hours—it was a systemic failure across the organization. The culture of overwork was allowed to persist because the control environment was weak, monitoring was inadequate, and there was no serious commitment to remediation.

This final lesson learned for the compliance professional is that internal controls are just one piece of the puzzle. To be truly effective, they must be integrated into a comprehensive risk management framework that includes strong ethical leadership, ongoing education, and a commitment to continuous improvement. 

Internal Controls as a Reflection of Corporate Culture

The tragic situation at BoA is a stark reminder of the critical importance of internal controls in maintaining compliance and a healthy and sustainable corporate culture. Internal controls are more than checkboxes—they reflect an organization’s values and priorities. When controls are ignored or undermined, they send a message that compliance, and by extension, employee well-being, is not a priority.

For compliance professionals, the key takeaway is clear: internal controls must be actively managed, monitored, and enforced. They must be part of a broader effort to create a culture of integrity and accountability. Perhaps most importantly, they must be seen as a dynamic system that requires constant attention and adjustment to remain effective. In a world where pressure on employees is greater than ever, robust internal controls are not just a regulatory requirement but a moral imperative.

Categories
Blog

Bank of America’s Corporate Culture Crisis: Part 2 – Lessons Learned for Compliance

Compliance professionals constantly seek to understand how systemic issues within corporate hierarchies can lead to severe consequences. The recent revelations about Bank of America’s (BoA) persistent workplace culture problems are a powerful reminder of compliance’s critical role in safeguarding employees and the organization.

This week, I will explore the BoA failure around workplace culture from various perspectives articulated by the Everything Compliance gang, including Karen Woody, Jonathan Armstrong, Matt Kelly, Karen Moore, and Jonathan Marks. This exploration will include the failure of internal controls, failures by the Board and senior management, culture failures around highly driven, self-selecting employees, and the cultural miasma that is BoA from a perspective from across the pond. In Part 2, we journey through some key lessons learned for compliance professionals.

In the high-stakes world of investment banking, where deals are won or lost in hours, the pressure to perform can push individuals to the brink. Unfortunately, that brink has meant a premature end to some people’s lives. The recent tragedy at BoA, where a junior banker named Leo Lukenas died after working over 100 hours a week for weeks on end, has cast a harsh light on a decade-long problem. This is not the 2013 scandal revisited; it’s an ongoing crisis, a corporate culture problem that has festered for years. The lessons from this ongoing debacle are critical and chilling for compliance professionals.

Lukenas was not the first casualty of this toxic culture. In 2013, an intern in Bank of America’s London office, Moritz Erhardt, met a similar fate after enduring a grueling workload. Following that incident, the bank promised to implement policies to prevent such tragedies from recurring. Yet, a decade later, Lucas’s death is a stark reminder that those policies have either failed or were never truly enforced.

The investment banking division at Bank of America has been likened to a “white-collar sweatshop,” a description that, sadly, fits too many high-pressure work environments. While the term “sweatshop” might conjure images of factories in developing countries, overwork and exploitation can happen in plush office towers just as easily. Lucas’s death has brought into sharp relief the human cost of such environments, where the relentless pursuit of profit eclipses the well-being of employees.

What is particularly concerning is that this issue is separate from a single office or even a single country. The WSJ’s reporting has revealed that overwork at Bank of America is a pervasive issue, affecting employees in New York, London, Tokyo, and Latin America. Former employees have cited overwork as a primary reason for leaving the bank, underscoring that this is not a localized problem but an enterprise-wide failure of corporate culture.

This brings us to a crucial question: Where was compliance? Why have the policies and controls put in place to prevent overwork ineffective? The answer lies in a deep-seated cultural issue that transcends mere policy implementation. Middle management has tolerated if not outright encouraged, this culture, which senior management has failed to address with the necessary urgency.

Middle management is often described as the “meat grinder” of corporate culture, where good intentions from the top can get mangled into toxic behaviors at the bottom. In the case of Bank of America, middle managers were reportedly telling their subordinates not to report excessive working hours to HR, effectively bypassing the controls that were supposed to prevent overwork.

This is a classic example of what can happen when senior management fails to engage effectively with middle management. Senior executives may have genuinely wanted to prevent overwork, but their message could have been more focused and addressed by those in the middle tasked with enforcing it. This disconnect is where corporate culture often fails. Compliance professionals understand that policies are only as good as their enforcement, and enforcement is only as good as the people who are responsible for it. For the compliance professional, this means you must directly connect what senior management has laid out as policy and not simply put procedures in place to implement the policy but then monitor the implementation to ensure the policy is being followed. Sadly, that was not the case at BoA.

Another critical factor in this crisis is the role of incentive structures. It is no secret that high-stakes deals and intense pressure to produce results drive investment banking. But the stage is set for disaster when bonuses and career advancement are tied to closing deals, even at the cost of employee health.

This misalignment of incentives is a fundamental issue that any compliance officer must address. If the financial rewards for middle managers are tied to delivering results, irrespective of the human cost, then it should be no surprise that overwork becomes a pervasive problem. Incentive structures must be reexamined and realigned with the organization’s ethical and operational goals.

As compliance professionals, it is imperative not just to address the symptoms of such crises but to dig deeper and identify the root causes. This case’s root cause is clear: a toxic corporate culture prioritizes results over people. But beyond that, it is about senior management’s failure to enforce a healthy work culture and the misalignment of incentives that drives middle managers to push employees to the brink.

Organizations need to examine their culture, management practices, and incentive structures to prevent such tragedies in the future. This is not just a problem for Bank of America; it’s an industry-wide issue that requires a collective response. Compliance officers have a crucial role in advocating for stronger controls, better communication, and a culture that truly values employee well-being.

The ongoing crisis at BoA is a sobering reminder of the human cost of a toxic work culture. For compliance professionals, it serves as a call to action. A culture that values employees as people, not just as cogs in a machine, is necessary for enforcing and supporting policies; having them on paper is not sufficient.

As we progress, the lessons from this tragedy should guide our efforts to create healthier, more sustainable work environments. Compliance is not just about ticking boxes; it’s about ensuring our values are reflected in our organizations’ day-to-day operations. Ultimately, it’s about protecting the organization and the people who make it what it is.

Categories
Adventures in Compliance

The Last Bow Stories – Investigative Lessons from The Disappearance of Lady Frances Carfax

Welcome to a review of all the Sherlock Holmes stories that are collected in the work, “The Last Bow.“. It is a collection of eight detective stories written by Sir Arthur Conan Doyle, from 1908 to 1917. The collection spans some of the most intriguing cases and mysteries that Holmes and his loyal friend Dr. John Watson tackle.

Today we take up The Disappearance of Lady Frances Carfax, which appeared in Strand Magazine in December 1911, as we consider investigative lessons for compliance professionals from The Disappearance of Lady Frances Carfax.

This episode considers the investigative methods employed by Holmes and Watson, which offers valuable lessons on investigations for compliance professionals. Key points include thorough information gathering, maintaining confidentiality, attention to detail, critical thinking, collaboration, understanding human behavior, following financial clues, meticulous documentation, and learning from each case. The episode underscores how these investigative principles can be directly applied to the field of compliance.

Key Highlights:

  • Introduction to Lady Frances Carfax
  • The Disappearance and Investigation
  • Holmes’ Discoveries and the Climax
  • Key Investigative Lessons for Compliance
  • Compliance Principles

 Resources:

The New Annotated Sherlock Holmes

Sherlock Holmes FAQ

Connect with Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

For more information on Ethico and a free White Paper on top compliance issues in 2024, click here.

Categories
Compliance Tip of the Day

Compliance Tip of the Day: Persuasion in Compliance

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements.

Whether you’re a seasoned compliance professional or just starting your journey, our aim is to provide you with bite-sized, actionable tips to help you stay on top of your compliance game.

Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law.

Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

At the end of the day, persuasion is a compliance professional’s most powerful tool. Learn how to wield it effectively.

For more information on the Ethico ROI Calculator and a free White Paper on the ROI of Compliance, click here.

To check out The Compliance Handbook, 5th edition, click here.