Categories
Blog

Welcome to Y’All Street: What Compliance Professionals Need to Know

The Texas Stock Exchange has moved from a proposed alternative to an operating market. TXSE completed its initial trading rollout in July 2026, welcomed its first exchange-traded fund listings in September, and announced its first corporate primary listings on October 5. For compliance professionals, those developments create a practical question: what would a TXSE listing require our company to do differently?

The answer begins with a familiar framework. TXSE operates as an SEC-registered national securities exchange. Companies choosing it remain subject to applicable federal securities laws and exchange listing requirements. The important differences involve particular governance structures, operational procedures, transaction approvals, and a proposed change to shareholder voting.

In their Corporate Compliance Insights article, “Y’all Street Plays by Familiar Rules — With a Few Twists,” Blessing Adeyeye and Evelyn Li explain how TXSE combines features of existing exchanges. Their analysis provides a useful starting point for CCOs: evaluate the actual requirements and their implications for your company’s controls.

This comparison addresses ordinary domestic operating companies. Foreign private issuers, controlled companies, partnerships, and other special entities may qualify for exemptions or different requirements. It also compares TXSE with the principal NYSE and Nasdaq markets; NYSE Texas is a separate exchange.

Start with the Company’s Continuing Obligations

An exchange transfer does not eliminate applicable SEC reporting, financial disclosure, insider trading, or Sarbanes-Oxley obligations. Nor does it automatically change the company’s state of incorporation or the law governing directors’ fiduciary duties. Those distinctions matter when a board considers a Texas listing alongside discussions about headquarters relocation or reincorporation. Each decision requires its own analysis.

For the CCO, the immediate responsibility is to identify which obligations arise from federal law, which arise from the exchange, and which arise from corporate law or the company’s governing documents. Combining them into a general discussion about a favorable business environment can obscure significant responsibilities.

Audit committee oversight illustrates the continuing federal foundation. SEC Rule 10A-3 establishes requirements addressing independence, oversight of the external auditor, complaints about accounting and auditing matters, access to advisers, and funding. Those responsibilities remain central to listed-company governance.

A listing decision should therefore prompt a review of whether the company’s reporting and escalation arrangements work in practice. Can employees raise accounting concerns confidentially? Does the audit committee receive significant findings promptly? Can investigators obtain the records they need?

How the Governance Requirements Compare

The following summarizes core requirements, subject to applicable exemptions and transition periods. TXSE’s framework combines Nasdaq-like nomination flexibility with an NYSE-like internal audit requirement.

Governance issue TXSE NYSE Nasdaq
Board independence Generally requires an independent majority Generally requires an independent majority Generally requires an independent majority
Audit committee Generally at least three members, with independence and financial qualifications Generally at least three members, with independence and financial qualifications Generally at least three members, with independence and financial qualifications
Compensation committee Generally at least two independent directors An independent compensation committee is required. Generally at least two independent directors
Director nominations Independent directors or an independent nominations committee Independent nominating/corporate governance committee required Independent directors or an independent nominations committee
Internal audit function Required, subject to applicable exceptions and transition provisions Required, subject to applicable exceptions and transition provisions No general standalone listing requirement
Published corporate governance guidelines No comparable general NYSE-style requirement Required No comparable general NYSE-style requirement
Code of business conduct and ethics Required Required Required

The principal provisions include TXSE Rules 16.405–16.407 and 16.414, NYSE Section 303A, and Nasdaq’s Rule 5600 Series. The article’s comparison is consistent with these core distinctions. For a Nasdaq company considering TXSE, internal audit deserves early attention. Management should determine whether an existing function satisfies the requirement and whether its resources, reporting arrangements, and audit committee access are adequate.

For an NYSE company, TXSE’s nomination structure may offer flexibility. However, flexibility does not establish a business reason to dismantle a functioning committee. The board should evaluate whether its current structure provides effective oversight and clear accountability. The same reasoning applies to governance guidelines. A company may find them valuable for explaining director responsibilities, succession planning, and board practices even where its exchange does not require them.

Transaction Approvals Require a Fresh Review

Shareholder approval requirements are another area where broad similarities can conceal consequential differences. TXSE’s Rule 16.412 generally follows Nasdaq’s approach to acquisition-related issuances, changes of control, equity compensation, and certain large nonpublic issuances. NYSE maintains a parallel framework, but it treats certain transactions and related parties differently.

The familiar “20% rule” is shorthand for a more detailed analysis. Transaction structure, voting power, potential convertible issuances, pricing, and applicable exceptions all matter. Even pricing definitions require attention: TXSE’s relevant minimum-price calculation uses bid prices, while Nasdaq’s uses Nasdaq Official Closing Prices.

Consider a company negotiating an acquisition partly funded with stock. The commercial team may focus on valuation and financing certainty. Compliance and securities counsel should ensure that shareholder approval, exchange consultation, and additional-share requirements enter the timetable before the parties commit to an unrealistic closing date. The practical response is to revise transaction checklists when changing exchanges. Assign responsibility for reviewing equity issuances, compensation arrangements, acquisitions, and changes of control. Require escalation early enough to influence the transaction.

The Voting Proposal Deserves Separate Attention

TXSE’s proposed treatment of uninstructed broker-held shares could create a significant governance difference. As of this writing, it should be treated as a pending proposal. The SEC instituted proceedings in September to determine whether to approve or disapprove it. Under the proposal, a covered TXSE member would allocate uninstructed shares proportionally to instructions received from its participating beneficial owners for each proposal, subject to specified exclusions.

For example, if that broker’s instructed shares were voted 60% for and 40% against a proposal, the covered uninstructed shares would generally follow that distribution. The calculation would occur at the broker level, rather than by applying one company-wide voting percentage. Existing broker-voting rules restrict voting without instructions on director elections, executive compensation, and other significant matters. The TXSE proposal raises questions about how proportional allocation would interact with those protections. Its stated scope concerns primary TXSE listings and excludes securities whose primary listing remains on another exchange.

For issuers, the potential implications include vote forecasting, shareholder engagement, quorum planning, and communications about voting mechanics. Corporate secretaries, counsel, investor relations, and compliance should monitor the proceedings together. For broker-dealer compliance teams, approval could require changes to proxy-processing systems, calculation controls, exclusions, and recordkeeping. Implementation planning should follow the final approved text and effective date.

Listing Compliance Is an Operating Process

The article also identifies TXSE’s mandatory confidential eligibility review and its single listing tier. These features affect planning, particularly for smaller companies evaluating their available markets. Nasdaq’s multiple tiers provide a different eligibility structure. A CCO should help management distinguish initial eligibility from the ability to maintain compliance after admission. Share price, capitalization, distribution, reporting, and governance requirements need continuing monitoring.

Dual listing adds another operational consideration. Teams should identify which obligations remain applicable at each venue and where documented accommodations permit reliance on another exchange’s submissions. Disclosure procedures deserve particular care. NYSE’s 2026 guidance illustrates how detailed these requirements can be: specified material-news releases require advance notice to Market Watch, and supplemental listing applications require exchange authorization before covered issuances. A public SEC filing does not necessarily satisfy a separate exchange-notification obligation.

Before a transfer or additional listing, test a realistic scenario involving an earnings release, director resignation, acquisition announcement, or unexpected compliance deficiency. Confirm the responsible person, required recipients, submission method, deadline, and backup arrangements. That exercise will reveal more than a general certification that the company understands its new obligations.

What CCOs Should Bring to the Board

The board’s listing analysis should connect commercial benefits with implementation costs and governance consequences. Compliance can contribute a concise assessment covering five areas:

  1. Governance gaps. Identify required changes to committee composition, charters, internal audit, policies, and certifications.
  2. Operational readiness. Establish a calendar of filings, notifications, reviews, and escalation deadlines with named owners.
  3. Transaction controls. Update approval procedures for acquisitions, equity issuances, compensation plans, and related-party arrangements.
  4. Rule developments. Track the proxy-voting proposal and other changes through approval and implementation.
  5. Evidence of effectiveness. Test whether personnel can execute the revised procedures and promptly correct deficiencies.

Directors should ask what measurable business benefit the listing decision delivers, which obligations change, and whether management has budgeted for implementation. They should also ask whether proposed governance changes improve oversight or merely reduce formal requirements.

TXSE gives companies another venue through which to access public markets. For compliance professionals, its arrival creates an opportunity to examine how governance commitments translate into daily work. The strongest contribution a CCO can make is a documented assessment that enables the board to choose confidently and management to execute reliably.
Categories
Blog

Anthropic’s IPO: Twelve Questions for the Safety and Risk Committee

In Parts I and II, we examined ten corporate compliance risks arising from Anthropic’s Registration Statement. In Part III, we translated those risks into five lessons for compliance professionals. Today, I want to explore 12 questions where those lessons should land at the board level. Anthropic’s Safety and Risk Committee (the “Committee”) provides a specific place to begin.

The registration statement describes a committee consisting of two independent directors, Christopher Liddell and Vas Narasimhan, with Narasimhan serving as chair. Its responsibilities encompass oversight of model safety and security, including the policies, processes, and controls for managing significant model risks. The committee also helps the board oversee other material risks, including legal, regulatory, cybersecurity, privacy, and compliance risks.

That breadth matters. Model safety, commercial decisions, and enterprise compliance can affect one another. A new capability can change misuse exposure. A distribution partnership can complicate access restrictions. A deployment decision can create questions about whether customer representations remain supportable.

The filing states that the committee operates under a board-approved written charter. Its summary does not establish every approval right, reporting arrangement, or escalation threshold. The following twelve questions are my recommended oversight agenda, rather than a description of procedures Anthropic has adopted or findings that its controls are deficient.

1. Which risks require the committee’s closest attention?

A broad mandate requires disciplined prioritization. The Committee should ask management which combinations of model capability, user access, and business activity could create the most serious harm or compliance exposure.

What has changed since the last review? Has a model gained new capabilities, an agent received broader permissions, or a commercial arrangement introduced new users and jurisdictions? Which changes require additional safeguards before deployment or expansion?

Evidence to request: A prioritized assessment connecting material risks to accountable executives, key controls, unresolved gaps, and decisions requiring committee attention. The assessment should explain uncertainty and the risk remaining after safeguards are in place.

The practical lesson is to organize the agenda around consequential decisions. A catalog of risks becomes useful when directors can see what management must do about them.

2. Are responsibilities and escalation routes clear?

The Committee should ask how its work connects to the full board and other Committees. The filing also assigns risk assessment and risk management policy review to the audit committee. Overlapping responsibilities make coordination essential.

Who leads when a safety incident raises questions about investor disclosures, financial exposure, or executive incentives? What requires immediate notification to the committee chair? When must an unresolved issue reach the full board?

Evidence to request: A responsibility map, notification thresholds, and records demonstrating how significant matters move between management, committees, and the board.

The Committee should also establish what happens when management recommends deployment despite a serious unresolved concern. Directors need clarity about who decides, who advises, and who receives notice. They should confirm any authority to require a pause against the actual charter and board delegations.

3. Can independent challenges reach the committee?

Technical expertise is essential, but expertise alone does not guarantee that dissent reaches directors. The Committee should ask whether compliance, legal, security, and safety leaders can present concerns directly, including disagreements with senior management.

Where do staffing, specialist expertise, or information restrictions limit effective challenge? Which recommendations have management declined, and what exposure remains? Can the Committee obtain independent advice when internal assessments conflict?

Evidence to request: Reporting arrangements, material resource gaps, significant unresolved disagreements, and the process for obtaining outside expertise.

Private sessions with relevant control leaders can help directors understand what formal presentations omit. Those sessions should produce clear follow-up where necessary. The test is whether an uncomfortable finding can reach the committee early enough to influence a consequential decision.

4. Do incentives and culture support safety commitments?

The committee should examine how commercial and development pressures affect employee behavior. What happens when testing identifies a concern that could delay an important release? Are employees rewarded for surfacing weaknesses and resolving them?

How does management identify retaliation or other consequences for raising concerns? Do employees have reporting channels that work when an issue crosses technical, legal, and commercial boundaries?

Evidence to request: Employee feedback, significant safety and compliance reports, retaliation follow-up, and examples of decisions changed because employees challenged an assumption.

Where incentives appear to undermine controls, the Committee should coordinate with other relevant committees, such as a compensation committee (if one is ever created). A falling report count requires explanation. It could reflect fewer problems, less trust in reporting, or weaker detection. Directors should ask what evidence supports management’s interpretation.

5. Do safety controls work under realistic conditions?

The Committee should ask what testing establishes about the effectiveness of important safeguards. Which scenarios were examined, what failed, and what limitations remain in the assurance provided?

A model performing well in a controlled evaluation may behave differently when connected to tools, sensitive information, or persistent workflows. Directors should ask whether testing reflects the deployment environment and foreseeable attempts to defeat restrictions.

Evidence to request: Evaluation coverage, significant failures, independent challenges, exceptions, and evidence that corrective measures have been retested.

A useful question is, “Show us an instance in which a safeguard detected a serious problem and enabled intervention.”

Management should explain the detection, the response, and what the example does and does not establish about broader control effectiveness.

6. Are autonomous agents constrained by enforceable limits?

Agent oversight deserves specific attention because authority to act changes the consequences of error or misuse. The Committee should ask what agents can access, change, transmit, purchase, or execute without additional approval.

What prevents an agent from exceeding its permissions? Which actions require meaningful human review? Can the company revoke credentials, contain activity, and preserve evidence when behavior becomes unsafe?

Evidence to request: Permission boundaries, approval requirements, monitoring results, intervention exercises, and records of unauthorized or unexpected actions.

Directors should scrutinize the human review process. A reviewer needs sufficient information, time, and authority to challenge the proposed action. Management should demonstrate that intervention works under realistic conditions and that safeguards remain effective after changes to tools or permissions.

7. Are data protection and intellectual property risks connected to safety oversight?

The Committee’s enterprise remit should bring data and intellectual property questions into the discussion. Which sensitive information supports model development or enters deployed systems? What access, retention, and use restrictions apply?

Can management substantiate its rights to use critical datasets and software? How would the business respond if those rights were challenged or access were lost? What could a security compromise expose beyond immediate service disruption?

Evidence to request: Material data flows, significant security findings, unresolved rights questions, access controls, and incident-exercise results.

The Committee should examine operational consequences alongside legal exposure. A disputed dataset, compromised credential, or exposed model asset may require changes to products, access arrangements, and customer communications. Management should explain how those decisions would be coordinated.

8. Can partners preserve the safeguards Anthropic relies upon?

The Committee should ask where cloud providers, distribution partners, data suppliers, and other critical relationships affect safety and compliance controls.

Which safeguards depend on a partner’s actions? Can management detect prohibited access or misuse through indirect channels? What information, notification rights, and assurance evidence are available when a partner controls part of the environment?

Evidence to request: Critical dependency maps, material contract exceptions, unresolved diligence findings, monitoring results, and tested contingency plans.

Concentration requires particular scrutiny. Several commercial relationships may depend on the same infrastructure. The Committee should ask what management could actually do if a critical provider failed to meet requirements, including how quickly access could be restricted or essential services maintained.

9. Do legal restrictions translate into operational controls?

Sanctions, export controls, anti-corruption obligations, and government interactions require attention across the commercial lifecycle. The Committee should ask how management identifies relevant restrictions and converts them into controls over sales, delivery, support, and access.

Where could resellers, shared accounts, intermediaries, or unusual payment arrangements obscure the actual customer or activity? Which exceptions require escalation, and who approves them?

Evidence to request: Material screening exceptions, access-control testing, high-risk intermediary reviews, and significant unresolved compliance matters.

The Committee should connect these findings to deployment decisions. A policy prohibiting certain access provides limited assurance if the delivery architecture cannot enforce the restriction or identify attempts to bypass it. Management should explain both preventive controls and detection capabilities.

10. Are external claims consistent with internal findings?

The Committee should examine how evidence about safety, reliability, privacy, and security informs product representations and material disclosures. Which claims depend on testing with significant limitations?

What happens when an incident contradicts a public statement? How do safety and compliance findings reach legal, communications, finance, and the disclosure process?

Evidence to request: Substantiation for significant claims, unresolved discrepancies, and records showing how material incidents affect communications decisions.

Financial reporting and investor disclosure matters require coordination with the audit committee and responsible management. The Safety and Risk Committee contributes by ensuring relevant risk information reaches those processes. Ask management which important claim would be hardest to substantiate today, and why.

11. Are investigations independent and connected to decisions?

A significant incident may involve technical failure, misconduct, or both. The Committee should ask who determines investigative scope when allegations concern senior executives, deployment decisions, or the suppression of safety findings.

Are evidence preservation and interim safeguards timely? Who evaluates reporting obligations and potential disclosure decisions with appropriate counsel? What requires independent oversight?

Evidence to request: Suitably protected summaries of significant matters, independence arrangements, interim measures, and outstanding decisions.

The Committee should also examine how the issue came to light. Internal detection, an employee report, a customer complaint, and external discovery reveal different strengths and weaknesses. That detection path should inform improvements to monitoring and reporting.

12. Does remediation withstand independent verification?

Closing an action item should require evidence that the underlying problem was addressed. What failed in the process, permissions, incentives, or supervision? Where else could the same weakness exist?

Who owns each corrective action, what remains overdue, and which interim safeguards protect the business while work continues?

Evidence to request: A remediation record showing severity, owner, deadline, verification results, and repeat findings.

Retesting should reflect the conditions that produced the original failure. The committee should ask who performed the validation and what limitations remain. A revised policy or completed software change is an output. Demonstrated improvement in control performance is the outcome directors need to understand.

An agenda for the next committee meeting

Ask management to present the five most consequential unresolved safety and enterprise compliance risks. For each, require evidence, the accountable executive, available options, and the decision needed. Schedule a private session with relevant control leaders and examine one recently closed remediation item.

Confirm coordination arrangements with the audit and compensation committees. Record substantive challenges, decisions, responsibilities, and follow-up. The final question should be practical: What must this committee escalate or recommend today to make Anthropic’s safety and compliance commitments effective in operation?

Categories
Blog

Anthropic’s IPO: Top 10 Corporate Compliance Risks, Part II

What does it take to build an effective compliance program around an AI business? In Part I of this series, Tom Fox examined the first five of 10 key risks for compliance professionals identified in Anthropic’s IPO disclosures: AI safety and autonomy, regulatory enforcement, data privacy and cybersecurity, intellectual property, and export controls. Each raises a practical question for CCOs and boards: can management demonstrate that its governance and controls are effective as the technology advances?

The remaining five risks extend that inquiry across the enterprise. Third-party dependencies, bribery and corruption, financial reporting, board oversight, and product representations are familiar responsibilities for compliance professionals. In an AI business, however, those responsibilities must account for powerful commercial partners, rapid international expansion, complex infrastructure dependencies, and claims about technology whose performance can be difficult to validate.

This is where compliance must be embedded in business decisions. Due diligence must inform partner selection. Disclosure controls must support investor communications. Product claims must rest on evidence. Board reporting must give directors enough independent information to challenge management and require corrective action.

6. Third-party risk, strategic partnerships, and supply-chain dependencies

The disclosed risk: Anthropic identifies substantial dependencies involving computing infrastructure, cloud providers, strategic partners, vendors, and commercial intermediaries.

The compliance exposure: Critical third parties may create cybersecurity, data protection, sanctions, operational resilience, concentration, and regulatory compliance risks. A control failure at a cloud provider or commercial partner can become an enterprise-level compliance incident.

The CCO response: Apply risk-based third-party due diligence, contractual control requirements, audit rights, continuous monitoring, concentration-risk assessments, and exit planning for critical suppliers.

The Board question: Which third-party relationships could materially impair the company’s ability to operate lawfully or meet its compliance obligations if they failed?

7. Anti-bribery, corruption, and financial crime

The disclosed risk: Anthropic expressly identifies obligations under the FCPA, UK Bribery Act, anti-money laundering laws, and comparable international requirements. It acknowledges risks arising from third-party intermediaries, government interactions, lobbying, and international expansion.

The compliance exposure: Global sales and government contracting can create opportunities for improper payments, questionable intermediary compensation, conflicts of interest, and corrupt procurement activity. The company acknowledges that it may face liability for third-party misconduct even when it has not expressly authorized the conduct.

The CCO response: Implement risk-based third-party due diligence, beneficial ownership checks, government-interaction controls, transaction monitoring, gifts-and-hospitality procedures, and continuous testing of intermediary payments.

The Board question: Does the anti-corruption program cover the full network of resellers, intermediaries, agents, and other parties involved in global commercialization?

8. Financial reporting, disclosure controls, and public-company readiness

The disclosed risk: Anthropic highlights the difficulty of accurately forecasting revenues, expenses, computing requirements, and business performance. It also acknowledges that certain operational metrics depend on internal methodologies, assumptions, and systems that have not been independently verified.

The compliance exposure: Rapid growth and complex financial arrangements can create significant risks involving revenue recognition, valuation, financial reporting, internal control effectiveness, and potentially misleading investor disclosures. The transition to a public company raises expectations for disclosure controls, audit committee oversight, and Sarbanes-Oxley compliance.

The CCO response: Strengthen disclosure committees, financial control testing, management certifications, data lineage, audit trails, and review of operational metrics included in investor communications.

The Board question: Can management substantiate every material financial and nonfinancial performance metric disclosed to investors?

9. Corporate governance, board oversight, and conflicts of interest

The disclosed risk: Anthropic’s registration statement addresses its distinctive governance structure, long-term public benefit objectives, capital structure, and relationships with investors and strategic partners.

The compliance exposure: Complex governance arrangements may create tensions among shareholder interests, management incentives, public benefit commitments, safety obligations, and commercial pressures.

The CCO response: Establish explicit board-level risk ownership, documented escalation requirements, independent compliance reporting, conflict-of-interest procedures, and regular assessments of governance effectiveness.

The Board question: Does the board receive sufficient independent information to challenge management’s decisions regarding AI safety, regulatory compliance, and commercialization? For directors, the central issue is whether governance mechanisms support meaningful oversight of mission-critical risks, consistent with the principles associated with Delaware’s Caremark oversight doctrine.

10. Consumer protection, product representations, and misleading AI claims

The disclosed risk: Anthropic identifies risks involving model reliability, accuracy, safety, marketing representations, customer expectations, and consumer protection enforcement. Its financial statement disclosures also identify litigation alleging deceptive advertising concerning subscription plans, allegations the company disputes.

The compliance exposure: AI companies may face liability when representations concerning safety, capabilities, reliability, privacy, or performance exceed what testing and operational evidence can support.

This risk is particularly significant when customers rely upon AI outputs for consequential decisions or deploy AI agents with authority to act.

The CCO response: Require legal and compliance review of material AI product claims, retain supporting testing evidence, establish performance validation standards, and monitor customer complaints for indications of misleading representations.

The Board question: Do the company’s public claims about AI safety and performance have documented, independently challengeable evidence to support them?

Part II completes Tom’s compliance-focused ranking of Anthropic’s disclosures with risks six through ten. Their position on the list should not diminish the attention they receive. A failure in any one of these areas can expose weaknesses across the broader control environment. For each, he considers the disclosed risk, the compliance exposure, the CCO response, and the question directors should ask.

Across these ten risks, a common thread emerges: effective AI governance depends on the quality of the company’s underlying compliance program. Third-party oversight, reliable disclosures, independent challenge, and substantiated product claims require accountable owners, tested controls, and timely corrective action. These responsibilities extend to any business incorporating AI into its operations.

Tomorrow in Part III, Tom will translate this risk analysis into five practical lessons for CCOs and business leaders. The focus moves from identifying exposure to managing it: integrating AI into enterprise compliance, adapting traditional controls, overseeing technology dependencies, embedding compliance in product development, and giving boards evidence of effectiveness. For compliance professionals, the next step is to turn these lessons into decisions about how to approve, deploy, monitor, and control AI.

Categories
Blog

Anthropic’s IPO: Top 10 Corporate Compliance Risks, Part I

Anthropic’s S-1 Registration Statement (IPO), released on October 26th, offers a revealing look at the emerging compliance challenges of frontier artificial intelligence companies. More importantly, it provides a roadmap for Chief Compliance Officers (CCOs), general counsel, boards of directors, and risk professionals seeking to understand how traditional corporate compliance obligations intersect with increasingly autonomous AI systems.

Responses have been interesting: Matt Kelly, writing in Radical Compliance, identified “100 pages of risks.” Senator Elizabeth Warren, perhaps only now realizing that Skynet may be on the way to becoming ‘self-aware,’ is quoted by the Wall Street Journal (WSJ) as being “deeply troubled” by the risks listed in the IPO “and is demanding answers to a long list of questions before the artificial-intelligence giant goes public.” Ethisphere’s Erica Salmon Byrne noted that the terms of service place most enterprise AI risk squarely on the customer rather than Anthropic.

My conclusion is more down-to-earth and grounded in corporate compliance. Anthropic’s disclosures show that AI governance is no longer simply a question of responsible technology development. It is an enterprise compliance challenge involving regulatory enforcement, internal controls, cybersecurity, third-party oversight, intellectual property, corporate governance, and organizational accountability. This week, I will explore what I see as the Top 10 risks from a corporate compliance perspective. In this blog post, I will consider the first five in ascending order of criticality.

Yet from this exercise, I believe the most significant compliance question is whether a company’s governance and control environment can keep pace with the capabilities of the technology it develops and deploys. The following rankings prioritize potential regulatory exposure, severity of harm, enterprise impact, and the difficulty of designing effective preventive and detective controls. They reflect a compliance-focused interpretation of Anthropic’s disclosures, not the company’s own ranking.

1. AI safety, model autonomy, and inadequate governance controls

The disclosed risk: Anthropic acknowledges that increasingly capable AI models may create significant safety risks, including harmful outputs, misuse, unintended behavior, and failures of existing safety mechanisms. Its disclosure specifically addresses autonomous agents that can execute code, access external systems, conduct transactions, and operate for extended periods with limited human oversight.

The compliance exposure: A company may deploy AI capabilities that exceed the effectiveness of its risk management, monitoring, and internal control systems. This creates potential exposure under consumer protection laws, AI-specific regulations, negligence theories, and contractual obligations.

The CCO response: Establish formal AI risk classifications, independent safety testing, deployment approval gates, continuous monitoring, incident escalation, and documented human oversight. Map these controls to the NIST AI Risk Management Framework and ISO/IEC 42001.

The Board question: Who has the authority to stop deploying a profitable AI product when safety controls are inadequate?

2. Regulatory investigations, enforcement, and evolving AI laws

The disclosed risk: Anthropic reports receiving an October 2026 FTC civil investigative demand seeking information concerning consumer protection, privacy, data protection, and product safety and security. It also identifies a changing regulatory landscape across the United States and international jurisdictions.

The compliance exposure: The risk is not simply that new regulations may impose additional costs. Regulators can investigate whether existing representations, disclosures, safety practices, and customer protections are deceptive, inadequate, or inconsistent with applicable law.

The CCO response: Create an AI regulatory obligations inventory, assign accountable control owners, test compliance with existing consumer protection requirements, and maintain a centralized regulatory inquiry and enforcement response process.

The Board question: Can management demonstrate that the company’s actual AI controls support the representations it makes to regulators, customers, and investors?

3. Data privacy, cybersecurity, and protection of sensitive information

The disclosed risk: Anthropic identifies risks associated with personal data processing, cybersecurity incidents, unauthorized access, cross-border data transfers, and differing privacy requirements across jurisdictions.

The compliance exposure: AI platforms can process enormous quantities of sensitive information. An unauthorized disclosure, improper use of training data, or compromise involving an AI agent could create exposure under the GDPR, California privacy laws, FTC enforcement authority, and contractual data protection obligations.

The CCO response: Require data mapping, privacy impact assessments, access restrictions, encryption, retention controls, vendor security reviews, and incident response exercises tailored to AI systems.

The Board question: Does management understand what sensitive information enters its AI systems, where that information travels, and who can access it?

4. Intellectual property, copyright, and training-data compliance

The disclosed risk: Anthropic acknowledges substantial uncertainty about how copyright law and open-source licensing apply to AI model training. The filing also describes ongoing copyright litigation and a $1.5 billion settlement in the Bartz copyright class action, approved in July 2026.

The compliance exposure: A company’s underlying AI model may depend upon training data for which its rights are disputed. Adverse litigation outcomes could result in substantial damages, licensing obligations, restrictions on training data, or operational changes to deployed models.

The CCO response: Establish documented data provenance, licensing reviews, training-data acquisition controls, legal approval procedures, and records demonstrating the basis for using copyrighted materials.

The Board question: Can the company demonstrate a defensible legal basis for the data used to develop its most commercially significant AI models?

5. Export controls, economic sanctions, and national security restrictions

The disclosed risk: Anthropic identifies exposure under U.S. export controls, sanctions regimes, and potentially the International Traffic in Arms Regulations. Its filing describes June 2026 U.S. Department of Commerce restrictions affecting its Fable 5 and Mythos 5 models, which were later lifted following safeguard updates.

The company also acknowledges that its export and sanctions controls have not always been fully effective and that it has previously made voluntary disclosures of noncompliance.

The compliance exposure: Advanced AI models may constitute controlled technology. Unauthorized model access, improper transfers, sanctioned-country usage, or inadequate customer screening could trigger enforcement, penalties, and loss of export privileges.

The CCO response: Integrate export classification, restricted-party screening, geolocation controls, customer due diligence, access monitoring, and escalation procedures into the product deployment architecture.

The Board question: Can the company prevent restricted users and jurisdictions from accessing controlled AI capabilities, including through intermediaries?

These first five risks establish a central compliance challenge: can a company demonstrate that its controls keep pace with the AI capabilities it develops and deploys? Safety governance, regulatory compliance, data protection, intellectual property, and export restrictions require clear ownership, tested controls, and timely escalation to the board.

In Part II, I will examine the remaining five risks, moving into the business relationships, commercial practices, financial reporting, and governance arrangements that support an AI enterprise. For CCOs and boards, these issues bring the analysis directly into familiar compliance territory. The question is whether established compliance disciplines have been adapted to the speed, scale, and complexity of the AI business.

These first five risks establish a central compliance challenge: can a company demonstrate that its controls keep pace with the AI capabilities it develops and deploys? Safety governance, regulatory compliance, data protection, intellectual property, and export restrictions require clear ownership, tested controls, and timely escalation to the board.

In Part II, I will examine the remaining five risks, moving into the business relationships, commercial practices, financial reporting, and governance arrangements that support an AI enterprise. For CCOs and boards, these issues bring the analysis directly into familiar compliance territory. The question is whether established compliance disciplines have been adapted to the speed, scale, and complexity of the AI business.

Categories
Compliance Into the Weeds

Compliance into the Weeds: Anthropic’s Board Structure – What Does it Mean for Compliance

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into a compliance-related topic, literally going into the weeds to explore it fully. Looking for hard-hitting compliance insights? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss Anthropic’s S-1 registration statement for a forthcoming IPO, focusing on what it reveals about corporate governance and risk oversight rather than financials.

Kelly notes Anthropic has a seven-member board with three insiders (CEO Dario Amodei, Daniela Amodei, and CFO Christina Rao) and four outsiders, operating through four committees: audit, compensation, nominating/governance, and a safety and risk committee tasked with AI safety, security, and broader legal/regulatory/compliance risks. They question whether a two-member safety and risk committee, chaired by Novartis CEO Vas Narasimhan and joined by Christopher Liddell, has sufficient capacity, and note that the committee has an undisclosed written charter. They also flag uncertainties about Anthropic’s internal compliance/risk leadership and reporting filters, potential amended filings, and a five-member long-term benefit trust (one seat vacant) with influence over nominating outside directors.

Key highlights:

  • Anthropic IPO S-1 overview
  • Board size and committees
  • Risk committee staffing questions
  • CEOs talking about AI risks
  • More filings and disclosure gaps

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds, was recently named one of the Top 25 Regulatory Compliance Podcasts, Top 10 Business Law Podcasts, and Top 12 Risk Management Podcasts. Compliance into the Weeds has been awarded a Davey, Communicator, and W3 Award, all for podcast excellence.

Categories
Blog

When the CEO Has to Go: What Forced Departures Tell Boards and CCOs About Governance

CEO succession is usually discussed as a planning exercise. Boards identify potential successors, develop internal talent, periodically review the succession plan, and prepare for the orderly transition that eventually comes with retirement or another planned departure.

But succession does not always wait for the planning calendar. In an article in the Harvard Law School forum on Corporate Governance, titled Forced CEO Departures, the authors reported on a new study by The Conference Board, developed with ESGAUGE and other collaborators, that examined forced CEO departures among Russell 3000 and S&P 500 companies from 2024 through August 2026. Roughly one in seven CEO succession cases were classified as forced in both 2024 and 2025. In the Russell 3000, 49 forced departures occurred in 2024 and 55 in 2025. The S&P 500 recorded seven and 10, respectively. The forced departure numbers are interesting. The governance implications are more important.

This research on forced CEO departures reminds boards to prepare for unscheduled CEO transitions. For Chief Compliance Officers, the findings raise an equally important question: what information should the compliance function be providing to the board before a leadership problem becomes a leadership crisis?

Forced CEO departures demonstrate that succession planning, executive accountability, corporate performance, investor confidence, culture, and risk oversight cannot be separated into different governance boxes. They ultimately meet in the boardroom. For a Chief Compliance Officer (CCO), they also demonstrate why compliance must function as an organizational sensor capable of identifying patterns that individual incidents may not reveal.

Forced Succession Is a Governance Risk

The report defines a forced departure broadly enough to capture the realities of corporate governance. A departure is forced when evidence indicates that the board, activist investors, an investigation, performance concerns, misconduct, or strategic disagreement materially influenced the timing or terms of the CEO’s exit. Importantly, a departure publicly described as a resignation or retirement may still have been board-driven. That distinction matters.

Boards should not think about CEO succession solely as identifying the person who eventually replaces a successful CEO. Succession planning must also contemplate what happens when the board concludes that the current CEO can no longer lead the organization effectively.

The report’s 2024 and 2025 data make that point. Forced departures represented 14.7 percent and 14.8 percent of Russell 3000 succession cases, respectively. Among the S&P 500, the corresponding figures were 14.3 percent and 15.2 percent. Those figures should change the boardroom conversation.

The question is not simply, “Who succeeds the CEO someday?” It is also, “What happens if we need a new CEO next Monday?”

Performance Is Becoming a Governance Question

Perhaps the most significant finding concerns why CEOs were forced out. Underperformance accounted for 37 percent of Russell 3000 forced departures across the period studied. It increased from 31 percent in 2024 to 44 percent in 2025 and remained the largest category through August 2026. Underperformance, activist pressure, and termination without cause collectively accounted for 70 percent of forced departures during the full period.

For directors, that creates a difficult governance question. When does poor performance become a leadership problem? A single disappointing quarter should not automatically become a referendum on the CEO. External economic conditions, industry disruption, commodity prices, interest rates, geopolitical events, and other factors can affect performance.

Yet boards cannot allow those explanations to become permanent excuses. The report recommends establishing in advance the conditions that trigger a deeper assessment of CEO effectiveness. That assessment should extend beyond financial results to strategic milestones, competitive position, organizational capability, and how the CEO responds to setbacks. That is an important governance discipline. Agreeing on the indicators before the crisis reduces the danger of redefining success after performance deteriorates.

The CCO Has a Different Window Into CEO Effectiveness

Here the compliance function enters the discussion. The report is primarily about CEO succession and board governance. It does not assign the CCO responsibility for evaluating CEO performance. Nor should it. But compliance often sees organizational information through a different lens than Finance, Strategy, HR, or Investor Relations.

A CCO may see whether employees are becoming reluctant to speak up. Compliance may identify retaliation concerns involving senior management. Investigations may reveal recurring management override. Hotline data may show patterns concentrated around particular executives or business units. Third-party reviews may expose pressure to circumvent controls. Internal investigations may demonstrate that employees believe commercial performance is valued more highly than ethical conduct.

One event may mean little. Patterns can mean much more. This is why an effective CCO should not simply report hotline statistics to the board. The CCO should help directors understand what the information may be saying about organizational culture, controls, accountability, and risk.

The question becomes: What does the board need to know to discharge its oversight responsibilities?

That is a very different question from: What compliance information did management ask us to provide?

CEO Accountability and the Control Environment

CCOs should also pay attention to forced CEO departures. The CEO sits at the top of the organization’s control environment. The CEO’s conduct affects incentives, resources, accountability, escalation, management behavior, and whether employees believe controls are genuine requirements or obstacles to business performance.

That means directors assessing leadership should consider more than revenue growth and shareholder returns. They should understand whether management responds appropriately when controls identify problems. Some key questions a CCO might ask include:

Does the CEO support investigations even when they involve high-performing executives? Does management remediate identified weaknesses? Are compliance personnel adequately resourced and empowered? Are executives held accountable consistently? Does information reach the board without being filtered into insignificance?

These questions connect CEO oversight to compliance program effectiveness. They also reinforce why direct access between the CCO and the board or an appropriate board committee matters. The value of that relationship becomes clearest when the information the board needs is information senior management would prefer not to discuss.

Activists May Ask the Questions Boards Should Already Be Asking

The report contains another significant finding.

Among S&P 500 forced departures, activist pressure accounted for five of 10 departures in 2025. Across 2024 through August 2026, activists were associated with eight of 19 forced departures, or 42 percent. The report notes that activist campaigns frequently focus on matters already within the board’s remit, including performance, strategy, capital allocation, portfolio structure, governance, and confidence in management. Forced CEO Departures

There is a governance lesson here. A board should not need an activist investor to tell it which difficult questions to ask. Directors should periodically examine the company through an independent investor lens. Where is performance lagging? Which strategic assumptions have not proved correct? Where has capital allocation failed to produce expected results? What would a sophisticated outsider identify as the company’s vulnerabilities?

For the CCO, there is a parallel exercise. What would a regulator, whistleblower, investigative journalist, plaintiff’s lawyer, or enforcement authority see if they examined the same facts? These perspectives are not substitutes for the board’s business judgment. They are tools for challenging assumptions. Effective oversight requires directors to seek disconfirming information, not just information that supports management’s existing narrative.

Succession Planning Needs a Break-Glass Option

The report recommends that boards maintain an accelerated succession plan alongside traditional succession planning. That distinction is critical. A normal succession plan asks who might become CEO in several years. An accelerated plan asks who takes control tomorrow morning.

The board should know who can provide immediate continuity, which internal executives could become permanent successors, when an external search would be required, and how to retain key executives during the transition. The plan should also address interim authority, compensation, severance arrangements, and employee and investor communications. Compliance should be part of that contingency architecture.

Questions might include: If the departure involves misconduct or an investigation, who controls the investigation after the CEO leaves? Who has authority over document preservation? Who makes disclosure decisions? Who communicates with regulators? What happens if other senior executives are implicated? Does the CCO continue reporting through the same management structure, or should reporting temporarily move directly to the board?

The report itself does not address these questions, but they follow directly from the compliance risks created by an unexpected leadership transition. The worst time to design these protocols is during the crisis.

The Board and CCO Need an Early-Warning System

The larger lesson from the forced-departure data is not that boards should terminate CEOs more quickly. It is that boards should become better prepared to recognize and respond to deteriorating conditions.

The report found no consistent company-size profile for forced turnover. Elevated rates appeared across the revenue spectrum. The more meaningful indicators were company-specific factors, including persistent underperformance, strategic misalignment, and investor scrutiny. Forced CEO Departures

That suggests boards need an integrated early-warning system.

  • Financial performance is one signal.
  • Strategic execution is another.
  • Investor sentiment is another.
  • Compliance and culture data should be another.

The CCO can contribute by identifying trends in allegations, investigations, retaliation, control overrides, disciplinary decisions, third-party exceptions, and other indicators that may reveal stress inside the organization. The board then has the responsibility to connect the dots.

Questions for the Board and CCO

Boards should periodically ask whether they have defined the conditions that would trigger a reassessment of CEO effectiveness; whether they have a genuine emergency succession plan rather than simply a long-term succession plan; whether directors receive information about culture, investigations, controls, and retaliation without inappropriate management filtering; and whether they understand recurring concerns raised by shareholders, employees, auditors, compliance, and other stakeholders.

CCOs should ask different questions. Are we giving the board data or insight? Are recurring issues being presented as isolated events? Are senior executives subject to the same accountability standards as everyone else? Does the CCO have a practical route to the board when senior management itself presents the risk? If the CEO suddenly departed tomorrow because of an investigation, could Compliance continue operating without interruption?

Those can be uncomfortable questions. Yet, they are also precisely the questions effective governance requires. Forced CEO departures are not simply stories about executives losing their jobs. They stress-test the governance system around those executives.

The board’s responsibility is to ensure it can recognize when leadership circumstances have materially changed and act deliberately, not reactively. The CCO’s responsibility is different but complementary: ensure that compliance, culture, control, and investigation information that can inform that judgment reaches the board clearly and promptly.

A board should never discover during a CEO crisis that the warning signs were there all along. A better governance model identifies those signals early, understands what they mean, maintains credible succession alternatives, and establishes decision processes before they are needed. That is not planning for failure. It is planning for effective oversight.

Categories
Blog

When an Effective CCO Is Labeled Difficult

A business leader calls a Chief Compliance Officer (CCO) difficult after a proposed distributor fails to provide basic ownership information. The transaction is important to the quarter. The CCO has asked for the missing information, explained the concern, and identified what is needed to proceed. In the performance discussion that follows, the focus shifts to whether the CCO understands the business.

This hypothetical presents a governance question. Did the CCO handle the matter poorly, or did an appropriate challenge expose a business practice management would prefer to leave alone? The answer requires evidence about the decision, the CCO’s conduct, and the operating environment. A label provides none of that.

Luis Velasquez examines this diagnostic problem in Why Effective Leaders Get Branded as Problems, published in Harvard Business Review. He identifies four sources of leadership friction: genuine skill deficits, historical reputation, overextension of a leadership strength, and organizational barriers. His framework provides a useful starting point for evaluating CCO effectiveness while protecting the independence necessary to perform the role. The compliance applications below build on his analysis.

Diagnose the Conflict Before Evaluating a CCO

Velasquez describes an evaluation trap in which organizations treat visible behavior as the explanation for friction while giving insufficient attention to context. Once a leader acquires a negative reputation, subsequent assessments can reinforce it without testing whether the original diagnosis was sound.

For compliance, this creates a particular risk. A CCO’s responsibilities include raising concerns that may complicate a transaction, challenge an executive, or require management to change an established practice. Friction can arise while the function is doing its job. It can also arise when compliance communicates poorly, applies inconsistent standards, or takes too long to decide. An effective evaluation must examine both possibilities.

Start with the event behind the criticism. What decision was required? What information was available? What did the compliance request say, when, and why? What alternatives did a CCO identify? Which actions by the business affected the outcome? These questions create a basis for assessing performance without assuming the conclusion.

Address Genuine Skill Gaps Directly

Velasquez’s first category recognizes that leaders sometimes lack a necessary capability. Applied to CCOs, relevant gaps may include unclear communication, weak prioritization, insufficient business knowledge, or ineffective delegation. Consider a CCO who repeatedly sends lengthy technical explanations without identifying the decision management must make. Executives may reasonably struggle to act on the advice. Similarly, a compliance team that treats every request as equally urgent can consume resources while delaying matters that warrant immediate attention.

Those are legitimate performance concerns when supported by recent examples and a clear account of their consequences. Agree on the improvement required, provide support, and assess the result. Independence does not excuse disrespectful conduct, poor execution, or unsupported recommendations. It gives a CCO room to exercise judgment while remaining accountable for the work’s quality and delivery. A sound review evaluates whether a CCO explains concerns clearly and helps the business identify acceptable ways forward where they exist.

Replace Old Reputation With Current Evidence

Velasquez’s second category concerns historical reputation. A leader may change while the organization still relies on an outdated account of how that person operates. A CCO who joined during a serious control failure may initially have imposed tight review requirements. Years later, colleagues may still describe the function as inflexible even after it has introduced clearer thresholds, delegated decisions, and improved turnaround times.

The evaluation process should test whether the criticism reflects current experience. Ask for specific recent interactions, the applicable requirements, and the outcome. Compare those accounts with evidence of how the process now works. Older incidents may remain relevant, but explain their continued significance rather than assume it.

A CCO can contribute by demonstrating improvement through current service measures, examples of resolved issues, and feedback from people who use the process. The objective is an accurate assessment. Favorable anecdotes alone are no more sufficient than a repeated negative label.

Recognize When a Strength Needs a Different Application

Velasquez distinguishes a missing skill from a strength used too broadly. That distinction matters for a compliance leader whose career has rewarded detailed review and personal control of important decisions. Those habits may help stabilize a troubled program. As the business grows, the same approach can create bottlenecks if routine matters still require a CCO’s personal involvement. The leader needs to develop the team and establish clear decision authority while retaining appropriate escalation for significant concerns.

The response should specify where judgment can be delegated, what standards apply, and how quality will be checked. This preserves the value of careful review while changing how it is delivered. A CCO should be willing to examine this possibility candidly. A complaint about delay may reveal poor business planning, an overly centralized compliance process, or both. Correcting one cause does not remove the need to address the other.

Examine Whether the Organization Undermines the Role

Velasquez’s fourth category addresses organizational barriers involving culture, resources, incentives, and decision rights. This is where the implications for compliance independence become particularly significant.

A company may require review before engaging a third party while rewarding executives who commit to start dates before review begins. It may expect timely investigations while restricting access to relevant records. It may ask a CCO to escalate serious concerns and then criticize the escalation as a failure to collaborate.

In each case, evaluate the contradiction alongside a CCO’s response. Coaching the leader to communicate more effectively may help, but it cannot supply missing authority or correct an incentive that rewards bypassing controls. A CCO should document the constraint, its practical consequences, and the proposed correction. Management should identify who will resolve it and by when. Repeated, material barriers belong in discussions with the responsible board committee, particularly when they prevent the function from carrying out agreed responsibilities.

Make Board Support Concrete

Board support for a CCO should be visible in the governance process. Directors need access to an account of significant compliance concerns that explains the facts, management’s response, and any unresolved differences. The responsible committee should also understand the basis for material criticism of a CCO’s performance. Where criticism arises from an executive whose conduct or decisions compliance has challenged, that context warrants examination. It does not automatically invalidate the criticism or establish retaliation.

An appropriately independent review should consider the substance of the concern, how it was raised, and the evidence behind any proposed personnel action. Human resources, legal, and the relevant board leadership should have clear roles consistent with the company’s governance arrangements. Regular private discussions between a CCO and ELT leadership (or the appropriate board committee) can help surface barriers before a performance dispute becomes entrenched. Directors should ask whether compliance has the access, resources, and authority needed to deliver what management expects.

Evaluate Effectiveness With Measures That Fit the Role

An evaluation based heavily on executive satisfaction can discourage necessary challenge. A review based solely on activity counts provides an equally incomplete picture. Assess the quality and timeliness of advice, the prioritization of risk, the development of the team, and the follow-through on significant issues. Consider whether recommendations are supported and whether remediation addresses the underlying problem. Business feedback remains useful when it is specific and examined in context.

The central discipline is to evaluate the work and its consequences. Agreement with management is not a reliable measure of effectiveness; disagreement alone does not demonstrate courage or sound judgment.

Action Steps for the CCO

Use Velasquez’s framework to improve how performance concerns are examined:

  1. Ask for specific evidence. Identify recent events, decisions, and consequences behind broad criticisms. Respond to substantiated concerns directly.
  2. Test all four explanations. Examine skill gaps, outdated reputation, overused strengths, and organizational constraints. Recognize that more than one may contribute.
  3. Agree on meaningful performance measures. Include advice quality, timeliness, prioritization, team capability, and remediation follow-through alongside contextualized business feedback.
  4. Document barriers to effective execution. Record missing resources, restricted access, conflicting incentives, or unclear authority, with proposed corrections and accountable owners.
  5. Establish a credible board review process. Clarify escalation and evaluation arrangements so significant concerns about a CCO and constraints on the role receive informed consideration.

Effective compliance leadership requires both sound judgment and the ability to make that judgment understood. Organizations strengthen accountability when they evaluate those capabilities fairly and address the conditions that prevent a CCO from using them.

Categories
Blog

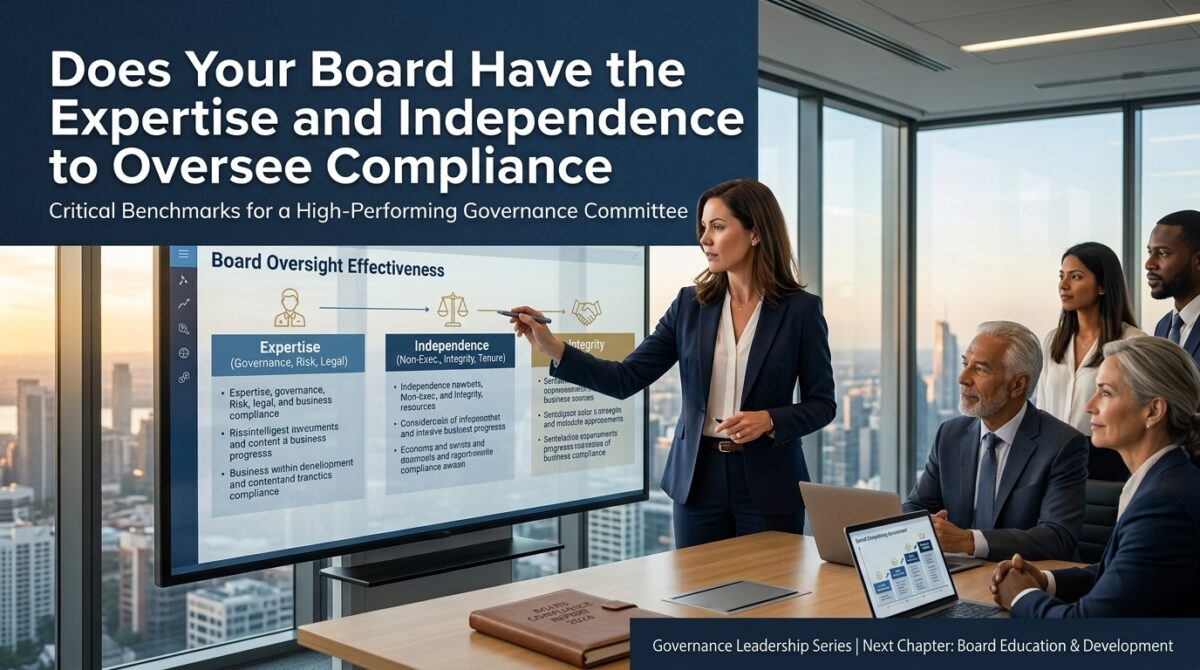
Does Your Board Have the Expertise and Independence to Oversee Compliance

A board can have impressive credentials and still lack the experience needed to challenge management on the company’s most significant compliance risks. Directors may understand finance, strategy, and operations in broad terms while struggling to recognize how misconduct could arise within a particular business model. Effective oversight requires relevant knowledge and the willingness to use it when the answers become uncomfortable.

For the chief compliance officer, that makes board capability a practical program issue. The quality of oversight influences the questions management must answer, the resources compliance receives, and what happens when a concern conflicts with a commercial priority. Today we examine board composition in the article Measuring Board Fit — Evidence from Elliott’s Campaign at Norwegian Cruise Line, from the Harvard Law School Forum on Corporate Governance. Their analysis uses AI to compare directors’ professional backgrounds with company strategy and with one another. It offers a starting point for a broader compliance question: Does this board have the expertise and independent judgment to oversee the risks this company actually faces?

Look Beyond the Skills Matrix

DesJardine and Mertens argue that conventional skills matrices can conceal meaningful differences in experience. Two directors may receive the same designation for operations or risk management while bringing very different capabilities to the boardroom.

The compliance application is straightforward. A risk management designation should prompt further inquiry into the nature, relevance, and recency of that experience. Has the director overseen a business using intermediaries in difficult markets? Has the director managed the integration of acquired companies? Examined an investigation involving senior leadership? Challenged a compensation structure that encouraged questionable conduct? No director needs to possess every capability. The board and its committees do need an informed basis for questioning management across the company’s priority risks.

The CCO can help define that basis. Translate the risk assessment into the experience and understanding needed for oversight. Where third-party conduct creates substantial exposure, explain the commercial relationships, payment practices, and escalation decisions directors need to understand. This gives the nominating and governance committee a more useful description than a generic request for compliance expertise.

Read the Norwegian Findings Carefully

The authors apply their method to Norwegian Cruise Line Holdings before and after Elliott Investment Management’s campaign, comparing its board with those of three cruise industry peers. They report that the company’s board-to-company similarity score increased from 0.382 to 0.396 following the changes. Average director-to-board similarity declined from 0.729 to 0.701, which they interpret as more distinct professional perspectives.

Those results describe changes in the authors’ measures of professional alignment and overlap. They do not establish that the reconstituted board became more effective at compliance oversight, that individual directors exercised greater independence, or that misconduct risk declined. That distinction matters for CCOs. An assessment can identify questions about composition without answering how directors perform. A board with relevant backgrounds still needs reliable information, sufficient time, and the resolve to follow an issue through. The practical response is to combine an examination of credentials with evidence of the board’s oversight process.

Examine Independence Through the Oversight Process

The authors acknowledge that their method cannot assess integrity, interpersonal skills, or willingness to challenge a chief executive. Those limitations point directly to the independent judgment compliance oversight requires. Consider a hypothetical board discussion about a distributor generating substantial revenue while repeatedly failing to provide requested ownership information. Management recommends extending the relationship during further review. A director with relevant experience may recognize how significant the missing information is. The next question is whether the board presses management to explain the proposed safeguards, decision authority, and consequences of continued delay.

The CCO should help create the conditions for that discussion. Present the facts, uncertainties, available options, and recommendation clearly. Identify who owns the decision and what would trigger escalation. Provide access to the underlying analysis where needed.

Direct access to the responsible committee and opportunities for discussion without management present can support candid oversight. Follow-up is equally important. An unresolved concern should return with updated evidence and a clear account of management’s actions. A difficult question has value when the governance process ensures it receives an adequate answer.

Make Expertise Usable Through Better Information

Even an experienced director can struggle with reports that emphasize activity while obscuring unresolved risk. Assess board capability and reporting quality together. A presentation may show that due diligence reviews are complete without explaining the exceptions approved. Investigation statistics may omit repeated issues within one business unit. Remediation updates may describe actions as finished without showing whether the revised controls work.

A CCO should organize reporting around decisions and consequences. Explain the issue, the evidence, management’s response, and what remains unresolved. When a commercial objective conflicts with a compliance recommendation, make that tension clear. Directors can then apply their experience to a concrete problem. Does the proposed response address the cause? Is the responsible executive accountable for delivery? What evidence will show that the correction is working? These questions help convert professional knowledge into oversight of program effectiveness.

Preserve Perspectives That Challenge Assumptions

The authors examine both alignment with company strategy and similarity among directors. That combination highlights a tension: a board needs relevant experience while retaining perspectives that question the organization’s assumptions. For compliance, industry familiarity can help a director spot questionable practices. It can also leave accepted business conventions insufficiently examined. Experience from another sector may expose weaknesses in customer treatment, escalation, or control ownership that insiders have normalized.

A CCO should therefore avoid equating a closely matched background with superior judgment. Ask what the board needs to understand and where a different perspective could improve its questions. Director education can help close specific knowledge gaps. Sessions built around the company’s actual processes, anonymized matters, and emerging business changes can give directors a better foundation for challenge. Persistent gaps may also warrant discussion of committee expertise or board recruitment, with those decisions remaining with the appropriate governance bodies.

Use AI Assessment as a Diagnostic Input

DesJardine and Mertens use contextualized word embeddings, a technique that turns text into numerical representations, to compare professional and company profiles. The approach can surface similarities that broad categories miss. For a board considering such analysis, the CCO and governance team should ask what information supports each profile and what the resulting score actually measures. Public biographies and media coverage provide an incomplete record of a director’s contributions. The volume and character of available material may differ substantially between candidates.

Company disclosures also describe the organization through a particular lens. Similarity to that description does not necessarily establish the expertise needed to address an overlooked risk or challenge an unsuccessful strategy. Use the output to inform interviews, reference discussions, and committee deliberations. Ask how sensitive the result is to source selection and whether the underlying evidence supports the interpretation. Record significant limitations. A numerical score should help the board investigate a capability question; appointment and evaluation decisions require accountable human judgment.

Action Steps for the CCO

Bring a practical assessment of oversight capability to the next discussion with the committee chair:

  1. Map priority risks to oversight knowledge. Identify what directors need to understand about the company’s business practices, controls, and escalation decisions.
  2. Provide evidence of capability gaps. Work with the corporate secretary and general counsel to inform education and composition discussions, using specific examples rather than broad labels.
  3. Strengthen the conditions for independent challenge. Establish clear access, candid reporting, and follow-up arrangements for unresolved concerns, including matters involving senior management.
  4. Test the usefulness of board reporting. Ensure directors can see material exceptions, recurring issues, remediation evidence, and decisions requiring their attention.
  5. Apply scrutiny to AI assessments. Examine source quality, missing information, and the limits of similarity measures before incorporating results into governance decisions.

Effective compliance oversight depends on directors who understand the company’s risks and are prepared to question how management addresses them. The CCO can strengthen that oversight by making capability needs explicit and ensuring the board receives the evidence needed to exercise its judgment.

Categories
2 Gurus Talk Compliance

2 Gurus Talk Compliance: The Farewell to Dolly Edition

What happens when two top compliance commentators get together? They talk compliance, of course. Join Tom Fox and Kristy Grant-Hart on 2 Gurus Talk Compliance as they discuss the latest compliance issues in this week’s episode!

Stories This Week Include:

  • Meta Settles NYT
  • Dolly Parton Passes Away. NYT
  • Hemma Lomax does it again. FCPA Compliance Report
  • 4 things states can do to combat federal corruption. Just Security
  • AI for email compliance. NJIT
  • JPMorgan Ended Banking Relationship With Polymarket Over Regulatory Concerns – WSJ
  • FTC Warns Retailers on Using Private Consumer Data to Raise Prices – WSJ
  • Why Do Boards Keep Giving Misbehaving CEOs Second Chances? – WSJ
  • Unannounced Compliance Audits: Good, bad or “it depends”? – Ideas & Answers
  • Smokey Bear aids arrest of man accused of stealing, reselling signs of iconic mascot from Florida parks – Click Orlando

Resources:

Kristy

Kristy Grant-Hart on LinkedIn

Order Kristy’s updated 10-year new edition of How to Be a Wildly Effective Compliance Officer by clicking here.

Tom

Check out Tom on LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

Odyssey Week: Leadership – Odysseus the Brilliant Problem: Tone at the Top

Ed. Note: I was finally able to see the movie The Odyssey. To say it blew me away was an understatement. Even though it didn’t follow Homer’s work precisely or use ancient Greek, I still thought it was great cinema. Anytime you get people talking about the Greek classics, that is a win in my book. So check out the movie and enjoy it. Matt Damon was great as Odysseus.

Odysseus is the kind of leader every board says it wants. He is brave, strategic, persuasive, resilient, creative under pressure, and very good at producing results when the situation looks impossible. He wins wars. He escapes monsters. He talks his way out of death more than once. He is the executive you send into the room when the deal is collapsing, the market is hostile, and everyone else has run out of slides.

He is also, on occasion, his own biggest compliance risk. That is what makes Odysseus so useful for business leaders and compliance professionals. He is not a cartoon villain. He is not reckless in the simple sense. He is brilliant. And brilliance can be dangerous when no one is willing to challenge it.

Odysseus reminds us that tone at the top is not only about what leaders say in polished town halls. It is about how leaders behave when the pressure is real, the stakes are high, and the rules feel inconvenient. The corporate lesson is straightforward: high-performing leaders can create high-performing risk. The organization must be able to challenge its stars.

The Corporate Translation

Every company has an Odysseus. Sometimes he is the rainmaking sales leader who always makes the number. Sometimes she is the visionary founder who can charm investors, customers, regulators, and the board in a single afternoon. Sometimes it is the regional head who delivers growth in difficult markets. Sometimes it is the product leader who moves faster than the control functions can process. The organization loves this person because they win. And that is precisely the problem.

Success can become a shield. Results can become a permission structure. A leader who delivers extraordinary outcomes may slowly become exempt from ordinary scrutiny. Questions that would be asked of anyone else are softened, delayed, or skipped entirely.

  • “How did we win that deal? ”
  • “Why was that third party necessary? ”
  • “Who approved that discount? ”
  • “Why was Legal brought in so late? ”
  • “Why are employees afraid to challenge this person? ”
  • “Why does Internal Audit keep finding exceptions in this business unit? ”

In a healthy culture, these questions are routine governance. In a weak culture, they sound like betrayal. That is the Odysseus problem. He saves the quarter, dazzles the board, and leaves Internal Audit wondering why no one asked how he did it.

Tone at the Top Is Conduct, Not Content

Companies are very good at producing leadership messages. The CEO video. The annual ethics letter. The opening paragraph of the Code of Conduct. The carefully scripted statement that “integrity is our highest value” usually releases the same week everyone is being told to accelerate growth, reduce costs, launch faster, and stop bringing problems without solutions.

Leadership messaging isn’t wrong. It matters. Employees do take cues from senior leaders. The FCPA Resource Guide states that compliance begins with the board and senior executives setting the proper tone and that managers and employees take cues from corporate leaders. It also emphasizes that senior management should clearly articulate standards, communicate them unambiguously, adhere to them, and disseminate them throughout the organization.

Indeed, the Evaluation of Corporate Compliance Programs (ECCP) asks some specific questions. Regarding Conduct at the Top, these questions include: How have they modeled ethical behavior to subordinates? Have managers tolerated greater compliance risks in pursuit of new business or greater revenues? Have managers encouraged employees to act unethically to achieve a business objective or impeded compliance personnel from effectively implementing their duties?

But employees are sophisticated. They listen to the speech, then watch the calendar, the budget, the promotions, the exceptions, and the discipline decisions. They notice who gets praised. They notice who gets protected. They notice whether compliance concerns change decisions or merely create additional paperwork. They notice whether the high performer who bullies employees, ignores controls, or plays games with approvals is treated as a problem or as “complicated.” Tone at the top is not what leadership says when the cameras are on. Tone at the top is what leadership tolerates when the revenue is attractive.

The Danger of the Heroic Exception

Odysseus lives by exception. That is part of his greatness. He survives because he improvises. He adapts. He reads the room, the monster, the god, the storm, and the weakness in every opponent. He does not always follow the obvious path because the obvious path often leads directly into the sea. Unfortunately, exceptions, not properly managed, are what get companies into hot water.

Business needs leaders who can adapt. Compliance should not become a shrine to rigidity. A company that cannot make decisions, approve thoughtful exceptions, or move with commercial urgency will not be admired for its purity. It will simply become irrelevant. But there is a difference between disciplined exception management and heroic exception culture.

Disciplined exception management asks, “What is the risk?” Who owns it? Who approves it? Is the exception documented? Is it time-limited? Are there compensating controls? Will we monitor it? What precedent does it create? Heroic exception culture says, “Odysseus has it handled.” That is not governance. That is mythology with a travel budget. The ECCP asks, “What exceptions to these policies has an organization permitted?”

When organizations build around heroic exceptions, they become dependent on personality rather than process. The leader’s instincts replace controls. Their confidence replaces documentation. Their track record replaces scrutiny. Their urgency replaces escalation.

Eventually, the organization is no longer asking whether the decision is right. It is asking whether it trusts the hero. That is a dangerous way to run a company. Always remember: trust, but verify.

Pressure to Perform Changes the Ethical Weather

Tone at the top is inseparable from pressure. Leaders may say all the right things about ethics and compliance, but if every business conversation ends with “just get it done,” employees hear the real message. If compensation rewards only revenue, employees hear the real message. If managers who raise concerns are labeled as blockers, employees hear the real message. If compliance is praised in public and bypassed in private, employees hear the real message.

The ECCP asks how senior leaders, through words and actions, have encouraged or discouraged compliance, how they have modeled ethical behavior, and whether managers have tolerated greater compliance risks in pursuit of new business or greater revenues. It also asks whether managers encouraged employees to act unethically to achieve a business objective or impeded compliance personnel from doing their jobs.

That is an excellent test for any leadership team. Not, “Did we say integrity matters? But did our conduct make integrity practical? “A leader who sets impossible targets and then expresses surprise when employees cut corners has not created a compliance culture. He has created plausible deniability. Odysseus often survives impossible pressure. Companies should be careful about asking employees to do the same.

Challenging the Star Performer

The true test of tone at the top is whether the organization can challenge its stars. Can compliance question the top sales executive? Can internal audit review the founder’s favorite business unit? Can Legal slow down the CEO’s preferred acquisition? Can HR investigate a high-performing manager accused of retaliation or harassment? Can Finance reject revenue recognition pressure from a powerful regional leader?

Or does the organization quietly apply one standard to ordinary employees and another to those who deliver? Employees do not need a formal policy memo to understand a double standard. They see it immediately. If a junior employee is disciplined for a policy violation while a senior leader is “coached” for comparable conduct, the culture learns. If a high-performing executive is allowed to mistreat people because “the business is too important,” the culture learns that compliance matters only when it doesn’t affect the powerful. If compliance concerns disappear when they involve influential leaders, the culture learns that compliance matters only when it doesn’t affect the powerful.

The ECCP looks at whether compliance is enforced consistently and whether consequences apply regardless of an employee’s position or title. It also asks whether managers are held accountable for misconduct that occurred under their supervision and for supervisory failures. That is not just enforcement logic. It is cultural logic. A company cannot claim integrity as a value while treating performance as immunity.

What a Better Program Does

A better compliance program does not try to eliminate Odysseus. That would be both impossible and unwise. Organizations need bold leaders. They need commercial courage, strategic imagination, persuasive ability, and the confidence to act in uncertainty. The goal is not to make leaders timid. The goal is to make leadership accountable.

A better program builds controls around high-risk authority. It monitors exceptions. It reviews pressure points. It includes compliance in strategic decisions early. It gives the board visibility into recurring overrides, hotline trends, audit findings, employee turnover, and control failures in high-performing units. It trains senior leaders not only on rules but also on how their behavior shapes risk. It also asks uncomfortable questions about success.

Where are results unusually good? Where are margins unusually high? Where are approvals unusually fast? Where are complaints unusually low? Where do people say, “That is just how that leader operates”? Where does the company rely on one person’s relationships, instincts, or influence more than on process? Those are Odysseus questions. The point is not to assume misconduct. The point is to understand that extraordinary performance deserves thoughtful scrutiny, not blind applause.

The Compliance Takeaway

Odysseus is brilliant. That is why he is dangerous. He shows us that leadership risk does not always arrive as laziness, incompetence, or obvious corruption. Sometimes it arrives as charisma. Confidence. Commercial success. Strategic genius. The leader who always finds a way.

Tone at the top means ensuring that even the most successful leaders operate within the company’s values, controls, and accountability structures. It means the Board of Directors and senior executives must model ethical conduct not only in speeches but also in decisions. (Talk the Talk but also Walk the Walk.) It means performance is celebrated but not worshiped. It means the organization can ask its heroes hard questions before the journey turns into an investigation. Every company needs leaders who can win. But no company should become so dazzled by Odysseus that it forgets to check the map, inspect the ship, and ask what happened to the crew.

Join Us Tomorrow

Odysseus reminds us that brilliance can become risk when success turns into a shield, exceptions become heroic, and no one is willing to challenge the leader who always finds a way. But even the most brilliant leader eventually leaves the room, and that is when the next compliance test begins: whether governance survives without the hero. Telemachus inherits the house Odysseus left behind, where authority is uncertain, informal power has filled the gaps, and bad actors have grown comfortable at the table. If Odysseus asks whether top performers are held to the same standards as everyone else, Telemachus asks the follow-up question every board should fear: when the indispensable leader is gone, does the compliance program still work, or was it only working because Odysseus was there?