Categories
Blog

Modern Philosophers and Compliance: Part 4 – Jürgen Habermas and the Governance of Speaking Up

This week we will continue our lengthy exploration of the philosophical underpinnings of the modern corporate compliance program. We have looked at, or will look at, Hannah Arendt and her concepts around personal responsibility; Simone de Beauvoir and the conditions for ethical action in a corporation; and John Rawls and the twin concepts of institutional justice and fairness in a corporate compliance program. We will review Hans Jonas and the responsibility for the future of corporate compliance. Today we continue with Jürgen Habermas and the governance of speaking up.

A compliance concern has value when it receives a fair hearing and an accountable response. Employees may submit reports, attend risk meetings, and complete surveys while important decisions remain insulated from what they say. Jürgen Habermas gives compliance professionals a way to examine whether internal communication lets evidence and reasons influence the exercise of authority.

For the Chief Compliance Officer, the practical question is what happens next. Who considers the concern? What evidence is examined? Who explains the response? A speak-up culture needs answers to those questions throughout ordinary business operations and within the formal reporting system.

Reasoned Dialogue as an Ethical Discipline

Habermas was a German philosopher and social theorist whose major twentieth-century works include The Theory of Communicative Action and Moral Consciousness and Communicative Action. He distinguished action oriented toward mutual understanding from strategic action aimed at achieving an actor’s purposes. His discourse ethics examines how moral norms are justified through reasoned discussion among those affected.

The conditions of that discussion matter. Participants must be able to question assertions, offer reasons, and express their concerns without coercion preventing participation. Agreement matters differently when it results from examining arguments than when it reflects pressure or exclusion.

Corporate decision-making operates within authority structures, commercial obligations, and legal requirements. Applying Habermas does not turn every management decision into a vote. His ideas offer a demanding test of the process: have relevant claims been open to challenge, and have decision-makers responded to the reasons presented?

That test gives compliance a practical responsibility. The function should help create conditions in which a concern can reach the right decision-maker without losing its substance. Participation must include a meaningful opportunity to affect the analysis. Otherwise, consultation can become a procedure for endorsing a conclusion already reached.

The Meeting Where Agreement Came Too Quickly

Consider the following. A company plans to enter a new market through a local distributor. During a launch meeting, the regional president announces that the agreement must be signed before quarter-end. She then asks whether anyone has compliance concerns.

A diligence analyst explains that the distributor’s ownership information remains incomplete and that a proposed subcontractor has not been reviewed. The sales leader responds that the distributor comes highly recommended. The president asks whether there is evidence of wrongdoing. The analyst says there is not but explains that important questions remain unanswered.

The discussion moves on. The meeting summary records that compliance raised no substantiated misconduct concern and that the team supported proceeding. The analyst’s request for additional review disappears from the decision record.

The facts do not establish that the distributor is improper. They establish a failure to address the question raised. The analyst identified an information gap relevant to approval. Management answered a different question about proven misconduct. The resulting agreement rested on an incomplete description of the discussion.

Habermas helps the CCO identify that failure. The analyst spoke, but the process did not meaningfully engage the claim. A useful response would clarify the missing information, define the approval criteria, and assign responsibility for resolving the issue before an authorized decision.

The DOJ Connection Through Reporting and Response

The Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) examines whether employees are comfortable using reporting mechanisms, whether company practices discourage reporting, and whether compliance has access to reporting and investigative information.

Those inquiries connect employee voice to program effectiveness. A concern cannot inform the company’s response if employees are discouraged from raising it, it is mischaracterized, or it is withheld from the people responsible for assessing it. Habermas supplies a philosophical lens for examining the quality of that communication.

The CCO should extend this inquiry beyond hotline intake. Concerns arise in procurement discussions, contract reviews, operational meetings, and informal requests for guidance. The company needs a proportionate way to capture material unresolved issues from those settings. Employees should know when a conversation must be documented as an escalation.

In our hypothetical, the meeting summary should preserve the substance of the analyst’s concern. It should identify the missing information, the required review, the decision owner, and any conditions on proceeding. If the summary is inaccurate, the analyst should have a practical means to correct it. That mechanism protects the reliability of the decision record.

Management Must Answer the Concern Raised

Reasoned dialogue requires attention to what a person is actually saying. In compliance speak, a speak-up culture must be paired with a listen-up culture. A concern about missing diligence should receive an answer about diligence. A concern about an incentive should receive an examination of how that incentive affects behavior. General assurances about leadership commitment do not resolve either issue.

The CCO can help managers distinguish disagreement about facts, disagreement about applicable standards, and disagreement about available options. Each calls for a different response. Missing facts may require investigation. An unclear standard may require legal or policy interpretation. Competing options may require an authorized decision about a risk that can lawfully be accepted.

Return to the distributor. If the policy requires ownership verification before approval, management should obtain it or follow an authorized exception process where one exists and is permissible. A commercial deadline does not, by itself, satisfy the requirement. If the concern rests on a misunderstanding, the decision-maker should explain the evidence that resolves it.

This approach makes discussion more useful to the business. It identifies what must be resolved and who can resolve it. It also prevents repeated requests for assurance from replacing a decision. An effective compliance professional should state the issue clearly enough that management can respond to its substance.

Hierarchy Can Distort the Conversation

Managers influence discussion through timing, framing, and reaction. Announcing the desired outcome before inviting concerns can make disagreement appear obstructive. Requiring employees to prove misconduct before raising uncertainty can exclude the very questions that preventive controls are intended to address.

The ECCP examines whether senior and middle managers encourage or discourage compliance and whether their commitment persists when commercial interests compete with it. Compliance professionals can translate that inquiry into observation of actual decision processes.

For material risk reviews, circulate relevant information early enough for participants to assess. Invite questions before seeking approval. Ask responsible functions to identify unresolved matters in their own words. Where hierarchy discourages discussion, provide an independent route for concerns and follow up on how employees who challenge decisions are treated.

These measures do not guarantee agreement, nor should agreement be the sole objective. Decision-makers may reasonably reject an objection after reviewing the evidence. The record should explain why. A team can disagree about the preferred option while understanding the basis for the authorized decision and the obligations that follow.

The quality of the discussion also depends on access. An employee working overnight or speaking another language may need a different way to participate. A written question or private conversation can carry the same substantive concern as a confident presentation in a committee meeting. The company should assess the argument without making presentation style a proxy for credibility.

Closing the Loop Requires Evidence

Receiving a concern creates an obligation to route it appropriately and determine what response is warranted. The ECCP addresses timely investigation, follow-up, and accountability for findings and recommendations. The practical challenge is connecting those steps so an issue doesn’t disappear when one function transfers it to another.

For significant concerns, assign an owner, a response date, and a defined basis for closure. Record whether the company obtained additional evidence, changed the decision, introduced a safeguard, or concluded that further action was unnecessary. The explanation should be specific enough for an independent reviewer to follow.

Where appropriate, tell the person who raised the concern that it was considered and describe the process or outcome to the extent permitted. Protect personal information, legitimate confidentiality, and the integrity of the investigation. A useful response acknowledges the issue and explains the next step without disclosing restricted details.

The analyst should learn whether the ownership question was resolved and whether the subcontractor review remains a condition of approval. If the transaction proceeds under an exception, the record should identify the authority, rationale, and monitoring obligations. A concern that changes a control or approval condition provides tangible evidence that speaking up influences business operations.

The Board Must Hear Unresolved Disagreement

Board reporting can lose valuable information when management summarizes a complicated risk discussion as organizational alignment. Directors need visibility into material unresolved concerns within their oversight remit, particularly when compliance and business leadership differ about the adequacy of controls.

The ECCP examines private sessions with compliance and control functions, the information used in board oversight, and compliance autonomy and access to the board. These arrangements can help directors examine concerns that ordinary reporting channels have failed to resolve.

The CCO should present the issue, competing explanations, the evidence, and the required decision. Identify what is known, what remains uncertain, and who has authority to act. Directors should ask whether those closest to the issue find the summary accurate.

Reporting should also show whether the process improves decisions. Useful evidence includes material concerns that led to further diligence, changed approval conditions, or remediation. Volume alone provides an incomplete picture. The board needs to understand whether significant questions receive reasoned responses and whether corrective actions are completed.

Five Key Habermas Takeaways for the Compliance Professional

  1. Preserve the substance of employee concerns. Record the actual question, relevant evidence, and unresolved issue. Give employees a practical way to correct summaries that materially misstate what they raised.
  2. Require a response to the reasons presented. Distinguish factual gaps from policy questions and choices among permissible options. Assign each issue to someone with the competence and authority to address it.
  3. Design discussions that permit meaningful challenge. Share information in time for review, invite concerns before decisions, and provide independent escalation routes. Examine whether hierarchy or managerial reactions discourage participation.
  4. Connect reporting with accountable closure. Assign owners and response dates, document the basis for decisions, and communicate appropriate feedback. Verify that promised safeguards and remediation occur.
  5. Bring material disagreement into board oversight. Explain unresolved concerns accurately, including competing views and missing information. Show directors how employee challenge has changed decisions or exposed work still required.

Habermas offers the CCO a practical measure of speak-up culture: can the company show how it considered and answered a significant concern? The corresponding board question is whether a difficult issue can reach directors without being softened into apparent agreement. The answers reveal how seriously the organization treats reasoned challenge.

In our final installment, Part 5, we close out this series with Hans Jonas and responsibility for future consequences. Having examined how people exercise judgment, act under constraints, receive fair treatment, and challenge decisions, we will consider the people who cannot participate in today’s discussion. Jonas takes us into technology governance, AI, and the long-term effects of corporate power.
Categories
Blog

Modern Philosophers and Compliance: Part 1 – Hannah Arendt and Personal Responsibility in Corporate Compliance

This week we will conclude our lengthy exploration of the philosophical underpinnings of the modern corporate compliance program. We will examine Simone de Beauvoir and the conditions for ethical action in a corporation; John Rawls and institutional justice and fairness in a corporate compliance program; Jürgen Habermas and the governance of speaking up; and Hans Jonas and responsibility for the future of corporate compliance. Today we begin with Hannah Arendt and her concepts of personal responsibility and how they relate to the modern compliance program.

Every approval in a compliance process represents a decision. Someone accepts an explanation, authorizes a payment, resolves a concern, or allows business to proceed. The central question is whether that person understands and takes responsibility for the decision. Hannah Arendt gives compliance professionals a powerful way to examine what happens when organizational routines weaken that connection.

Our examination of ancient and Enlightenment thinkers established the importance of inquiry, ethical habits, institutional order, and evidence. We now turn to twentieth-century philosophy, beginning with responsibility inside complex organizations. Arendt asks us to consider the individual who operates within the system. What happens when that person stops examining the meaning and consequences of the work?

For a Chief Compliance Officer, this question reaches directly into third-party approvals, internal investigations, management conduct, and board oversight. A company can assign responsibilities in a policy while its employees learn to defer judgment to someone else. An effective compliance program must address that gap.

Thinking and Judgment as Compliance Responsibilities

Arendt was a German-born Jewish political thinker who fled Nazi Germany and eventually settled in the United States. Her experiences of persecution and displacement informed her examination of totalitarianism, political life, and personal responsibility. In essays including “Personal Responsibility Under Dictatorship” and “Thinking and Moral Considerations,” she explored the relationship between independent thought, moral judgment, and conduct.

Her account of Adolf Eichmann and the phrase “banality of evil” remain controversial, if not one of the most well-known phrases to describe Nazi Germany. The phrase did not mean that the crimes were ordinary or insignificant. Her interpretation emphasized his failure to think critically about what he was doing, although scholars have challenged her assessment of his motivations. The historical crimes she examined must retain their specificity and gravity.

The compliance application is narrower: institutional roles do not eliminate the need for personal judgment. Arendt was not writing a corporate governance manual. Her work nevertheless provides a basis for asking whether employees examine what their actions enable, particularly when organizational language makes questionable conduct appear routine.

That question builds on Socrates. Socratic inquiry tests assumptions through questioning. Arendt directs our attention to the person who must decide whether to accept the answer and participate in the conduct. For compliance professionals, that is where inquiry becomes responsibility.

When Approvals Divide Responsibility

Consider this hypothetical. A multinational manufacturer proposes hiring an intermediary to help secure business with a state-owned customer. The commission is unusually high. The service description is vague, and the intermediary requests payment to an account outside its home jurisdiction.

Sales confirms the commercial opportunity. Procurement verifies that the vendor record is complete. Legal reviews contractual provisions. Finance checks that the required approvals appear in the payment system. Compliance previously reviewed the intermediary, but the proposed payment arrangement has changed since that review. Each function assumes another has addressed the remaining concern—the payment proceeds.

No single feature establishes bribery. Together, these facts warrant further inquiry. The governance failure is that nobody takes responsibility for obtaining a satisfactory explanation before payment. Each participant can describe a completed task. The organization cannot explain who assessed the unresolved risk.

This is where Arendt becomes useful to the CCO. Division of labor is necessary in a large company. It must be accompanied by clear obligations to recognize concerns, communicate them, and seek an appropriate decision. Otherwise, specialization can allow important facts to disappear between functions.

The practical response is to specify what each approval means. Does the approver confirm budget availability, verify services, resolve due diligence findings, or authorize an exception? What changes require renewed review? Who owns the decision when concerns remain? These questions turn personal responsibility into an operating requirement.

The DOJ Connection Through Gatekeepers and Escalation

The Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) addresses this issue directly. Under policies and procedures, the ECCP asks about guidance and training for gatekeepers with approval or certification responsibilities. It examines whether they recognize misconduct and understand when and how to escalate concerns.

This is a substantive connection to Arendt’s work, rather than a claim of philosophical influence on DOJ. The compliance question concerns whether an employee’s assigned role includes meaningful judgment. An approval control weakens when its operator understands the mechanics but cannot identify the circumstances that require further review.

Return to our hypothetical. The finance employee should understand whether the changed bank account requires renewed diligence. The business sponsor should explain the services and commercial rationale. Compliance should receive material changes to the information on which its earlier review depended. The final decision should record how identified concerns were resolved.

The CCO can test this through a sample of actual transactions. Interview the approvers. Ask what they believed their approval represented, what information they reviewed, and what would have caused them to stop. Compare those answers with the procedure. The gap between intended and understood responsibility is a control issue that requires attention.

Training Employees to Recognize the Decision

Arendt’s emphasis on thinking also offers a practical lesson for training. Employees need opportunities to examine a situation before organizational habit supplies the answer. A course can explain a prohibition accurately while leaving participants uncertain about how to respond when a manager presents a questionable request as urgent and routine.

The ECCP examines whether training is tailored to relevant employees and risks, whether employees can ask questions, and how the company evaluates learning and training’s effect on behavior or operations.[4] Those inquiries support training that develops judgment within defined responsibilities.

Use the hypothetical intermediary payment as an exercise. Give participants the initial facts, then introduce the changed bank account after approval. Ask them to identify what requires renewed attention, which function should act, and what must happen before payment. Require an explanation for the proposed response.

Include the manager who says the transaction has already been approved. That intervention tests whether employees understand the limits of an earlier decision. The training should leave them with a usable escalation route and a clear account of their authority. Asking people to exercise judgment carries a corresponding obligation to equip them to act.

Leadership Determines Whether Judgment Is Welcome

Employees learn what management expects by watching what happens when someone raises a concern. A company may encourage questions in training while a business leader treats delay as disloyalty. Over time, employees may conclude that completing the transaction is safer than examining it.

The ECCP assesses how senior and middle management demonstrate commitment to compliance. It also examines whether employees feel comfortable reporting concerns and whether the company maintains an effective approach to preventing retaliation.[5] These are relevant tests of the environment in which personal judgment operates.

For the CCO, the practical inquiry should include decisions under pressure. When did a manager support an employee who paused a transaction? What happened to an unresolved concern near quarter-end? Did a policy exception receive appropriate scrutiny when the business sponsor was influential? Such examples help explain whether the stated expectations survive commercial pressure.

Boards also have a role here. The ECCP examines compliance access to governing authorities and opportunities for private discussions. It also cites the Sentencing Guidelines’ expectations concerning governing authority knowledge and oversight.[5] Directors should use that access to ask where management pressure is weakening escalation and whether the compliance function can obtain timely decisions on unresolved concerns.

Investigations Must Examine the Approval Chain

When misconduct emerges, Arendt’s focus on personal responsibility should sharpen the investigation without prejudging anyone’s culpability. The inquiry must establish what individuals knew, what their roles required, what authority they possessed, and how they responded. Participation in a process alone does not establish intentional wrongdoing.

In our hypothetical, investigators should trace the changed payment instructions through the approval chain. Who received them? Did the system alert compliance? Did anyone ask for an explanation? Was a concern overridden, misunderstood, or never transmitted? Those facts distinguish deliberate avoidance from inadequate training, poor system design, or reasonable reliance on incomplete information.

The ECCP asks whether investigations identify system vulnerabilities and accountability failures, including those involving supervisory managers and senior executives. Its remediation questions address failed controls, missed opportunities, and accountability for supervisory failures.[6] An investigation that stops at the person who released the payment may leave the conditions that enabled the problem intact.

Fair accountability therefore requires attention to both conduct and context. Discipline should reflect facts and relevant responsibilities. Remediation should repair the information flows, authority gaps, and incentives that shaped the decision. The organization must be able to explain what it learned and how that learning changes future approvals.

Five Key Arendt Takeaways for the Compliance Professional

  1. Define the responsibility within each approval. Identify what the approver must assess, the evidence required, and the conditions that trigger escalation. Test whether employees understand these obligations in actual transactions.
  2. Train for judgment under realistic pressure. Use scenarios involving changed facts, urgent requests, and influential sponsors. Assess whether employees can explain a concern and identify the appropriate response.
  3. Make challenge operationally possible. Give employees clear escalation routes and appropriate authority to pause decisions. Examine how managers respond when employees use those mechanisms, including whether adverse consequences follow.
  4. Follow accountability through the management chain. Investigate who knew what, who exercised authority, and where supervision failed. Apply fair standards to senior leaders and high performers as well as frontline employees.
  5. Give the board evidence of independent judgment. Report material overrides, unresolved concerns, and lessons from investigations. Explain where employee challenge changed a decision and where management action is still required.

Arendt helps us see that personal responsibility must remain visible inside institutional processes. The CCO’s task includes designing controls that preserve that responsibility and creating conditions in which employees can exercise it. A useful board question follows: Where could our processes allow every participant to believe that someone else was responsible for examining the risk?

Join us tomorrow in Part 2, as we turn to Simone de Beauvoir and discuss the conditions that make ethical action possible. If Arendt asks individuals to exercise judgment, Beauvoir helps us examine how unequal power, dependence, and vulnerability affect their ability to act on it. That inquiry leads directly to reporting culture, retaliation prevention, and the lived experience of corporate compliance.

Categories
Blog

The Clippers Investigation: Part 4 – Consequence Management at the Top

The Clippers penalties demonstrate that discipline is not the end of a compliance process. They are a public test of whether rules apply to powerful people. The Clippers investigation demonstrates why conflict controls must follow influence, economic benefit, and interconnected transactions, not merely financial ownership. In this Part 4 of a five-part series, we consider the consequences of cheating and not following the rules and regulations your organization agrees to comply with going forward. Every organization claims that no one is above the rules. Consequence management determines whether that statement is true.

The test does not come when a junior employee commits an obvious policy violation. It comes when the conduct involves a founder, controlling owner, senior executive, star performer, or other person viewed as essential to the business. The investigation into the LA Clippers and Kawhi Leonard presents that test in unusually clear terms. The independent investigators’ report of the Clippers’ NBA salary cap circumvention (Wachtell Report) attributed primary responsibility to Clippers owner Steve Ballmer, President of Business Operations Gillian Zucker, and President of Basketball Operations Lawrence Frank. It also found violations by Leonard through the conduct of his uncle and then-business manager, Dennis Robertson (Uncle Dennis).

The NBA responded with organizational, financial, individual, competitive, and monitoring consequences. For compliance professionals, the case provides a framework for considering who should be held accountable, for what conduct, and through what mechanism.

From Punishment to Consequence Management

Punishment looks backward. It asks what sanction should follow a violation. Consequence management is broader. It identifies misconduct, investigates responsibility, calibrates discipline, addresses supervisory failures, remediates control weaknesses, and communicates the organization’s expectations. All of this brings me to one of my favorite compliance phrases: consequence management.

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) introduces consequence management procedures as procedures to identify, investigate, discipline, and remediate violations of law, regulation, or policy. It goes on to state that every organization must enforce them consistently across the organization and ensure the procedures are commensurate with the violations. It concludes: Prosecutors should also assess the extent to which the company’s communications convey to its employees that unethical conduct will not be tolerated and will bring swift consequences, regardless of the employee’s position or title. 

Consequence Calibration

The report provides several categories for assessing responsibility.

  1. Direct participation. Investigators concluded that Zucker initiated, facilitated, and induced endorsement agreements involving Leonard and four Clippers business partners. They found that Ballmer knowingly sought to help Leonard obtain outside income and approved the Forum agreement after learning that Aspiration had tied it to Leonard’s endorsement arrangement. Frank conveyed Robertson’s demands and approved impermissible personal expenses.
  2. Supervisory responsibility. The report concluded that Ballmer failed to supervise the organization’s most senior business executive and failed to create conditions supporting compliance with the circumvention rules.
  3. Reporting responsibility. Investigators found that Ballmer, Zucker, and Frank did not report Robertson’s improper demands, despite an NBA rule requiring those reports even when the solicitation was rejected.
  4. Personal or represented conduct. The report concluded that Leonard, through Robertson, pressured the team to help obtain outside income and failed to reimburse certain personal expenses. Robertson allegedly made the demands and applied the pressure.

A defensible consequence decision should map each individual to the conduct, knowledge, authority, benefit, supervisory obligation, and missed opportunity to intervene. Titles alone should neither establish nor eliminate responsibility.

Credibility and Cooperation Matter

The report did something particularly useful for compliance officers: it distinguished among witness behavior. Investigators wrote that Zucker made statements inconsistent with contemporaneous documents and other witnesses, professed limited recollection on significant issues, placed responsibility on subordinates, and provided inconsistent versions of events.

By contrast, they reported that Frank discussed his conduct openly, recalled important details, accepted responsibility for subordinates, and remained generally consistent across interviews. The investigators stated that cooperation and credibility, or their absence, should factor into determining consequences.

Cooperation does not erase underlying conduct. It should, however, affect how consequences are calibrated. An employee who preserves documents, provides candid information, accepts responsibility, and assists remediation presents a different risk from one who misleads investigators or shifts blame.

The organization should define cooperation before an investigation begins. Employees should understand that cooperation requires truthful, complete, and timely responses; preserving relevant information; correcting prior inaccuracies; and no retaliation or interference. It does not require surrendering legitimate legal rights.

Prior Misconduct Changes the Analysis

The Clippers had previously been penalized for a salary-cap circumvention violation involving an endorsement opportunity. The NBA had also investigated demands made during Leonard’s 2019 free agency and provided specific training to Clippers leaders.

Prior history matters because it changes what the organization and its leaders reasonably should have done. A first incident may reveal an unrecognized risk. A repeated incident following investigation, rule clarification, and training raises questions about culture, supervision, remediation, and willingness to comply.

The Sentencing Guidelines identify prior organizational history as relevant to culpability and direct organizations to consider similar misconduct when designing an effective program. DOJ likewise asks whether policies, training, controls, and risk assessments incorporate lessons from prior incidents.

Remediation that ends with training is incomplete. The organization must test whether behavior, decision rights, escalation pathways, and controls changed.

The NBA’s Consequence Framework

The NBA’s official action included multiple forms of individual accountability. The box score of individual consequences reads as follows:

Person Relationship Consequence
Steve Ballmer Owner: LA Clippers Fine and one-year ban
Gillian Zucker Clippers President of Business Operations One-year unpaid suspension
Lawrence Frank Clippers President of Basketball Operations 6-month Unpaid Suspension
Kawhi Leonard Clipper Player $700K fine
Uncle Dennis Leonard Representative 5-Year Ban from NBA

These measures address different risks. For corporate compliance programs, the equivalent toolkit may include termination, suspension, bonus reduction, clawbacks where legally available, promotion restrictions, written warnings, removal of approval authority, enhanced supervision, vendor termination, and mandatory remediation. Consequences need not be identical, but the process must be consistent. Consistency means applying the same decision factors to similarly situated people. It does not mean imposing the same outcome regardless of role, intent, cooperation, history, or responsibility.

Practical Takeaways

CCOs, human resources leaders, and boards should consider the following:

  • Adopt written consequence-management procedures before a significant investigation occurs.
  • Use a consistent decision matrix covering conduct, intent, seniority, authority, benefit, cooperation, prior history, and supervisory responsibility.
  • Separate factual findings from disciplinary decisions, and ensure decision-makers understand the evidentiary record.
  • Document why similarly situated individuals received similar or different outcomes.
  • Apply financial consequences where permitted and align future compensation with compliance performance.
  • Communicate substantiated outcomes internally with enough detail to reinforce expectations while respecting legal and privacy constraints.
  • Track disciplinary data by level, function, geography, and type of misconduct to identify inconsistency.
  • Require independent board oversight when senior management is implicated.

Consequence management is where culture becomes measurable. If the organization protects its most powerful people, employees will understand that performance outranks integrity. If it applies a fair, independent, and proportionate process, employees will understand that compliance is part of how the business operates.

In our final blog post, we will bring the series together and develop a practical framework for CCOs, boards, and risk leaders seeking to build a compliance program that can say no to the star.

Categories
Blog

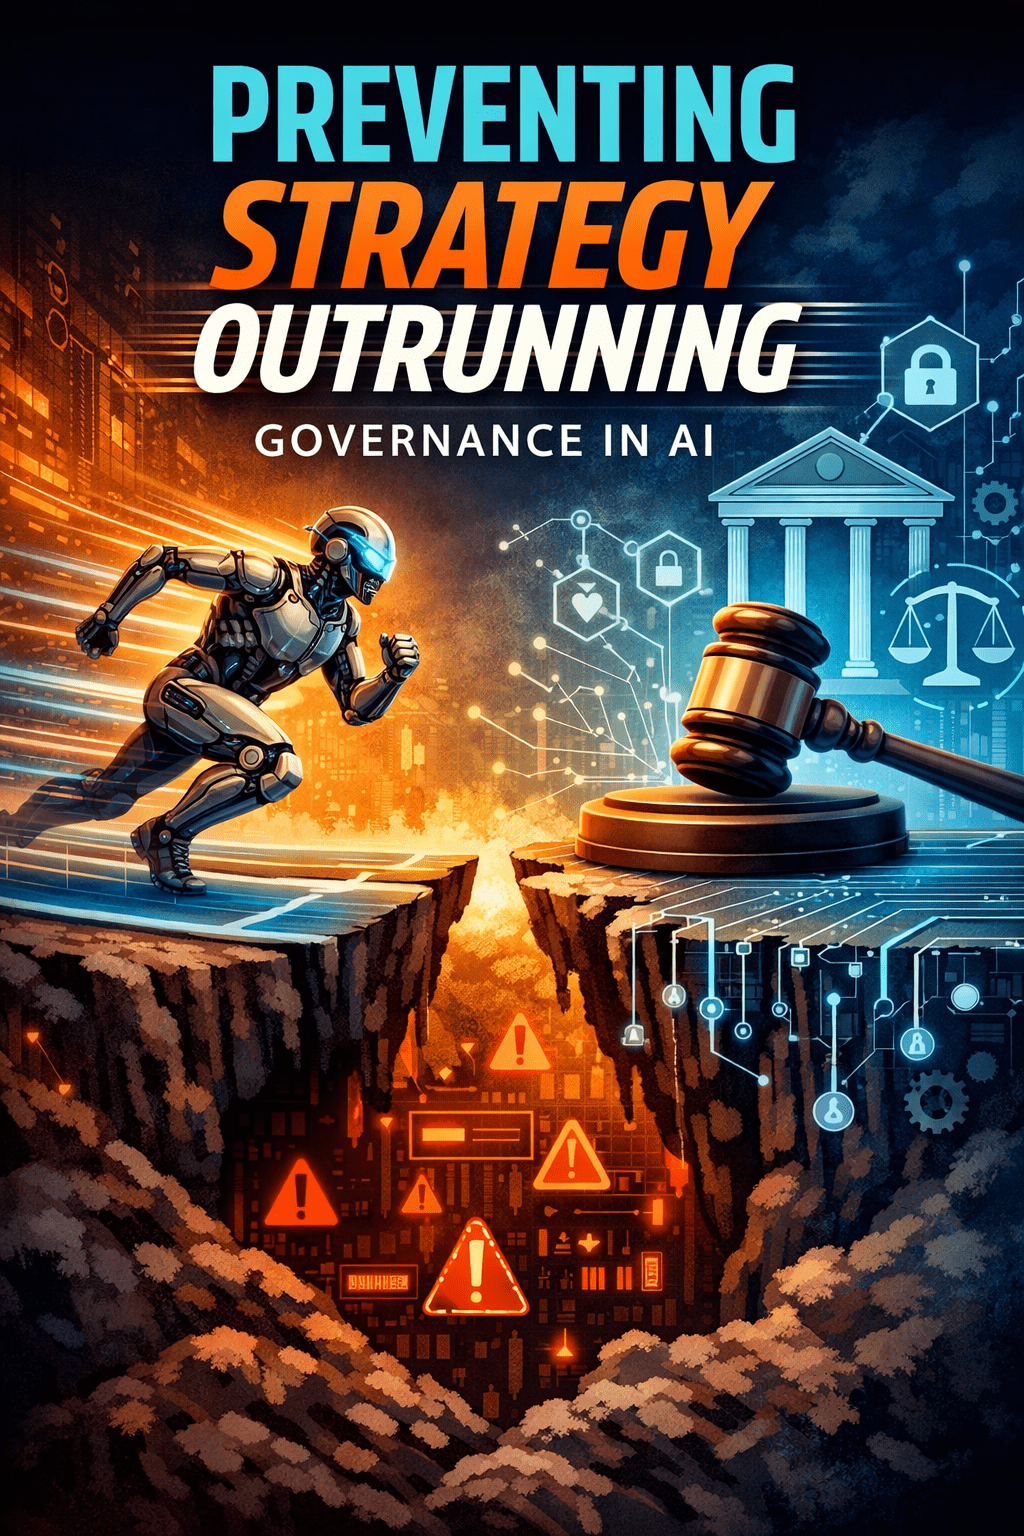
Preventing Strategy Outrunning Governance in AI

One of the clearest AI governance challenges facing companies today is not a failure of ambition. It is a failure of pacing. Put simply, strategy is moving faster than governance. Business teams want results. Senior executives hear daily about efficiency gains, lower costs, faster decision-making, enhanced customer engagement, and competitive advantage. Vendors are more than happy to promise it all. Employees are already experimenting with AI tools on their own. In that environment, the pressure to move quickly is relentless.

That is where the compliance function must step forward. Not to say no. Not to slow innovation for the sake of slowing it. But to ensure that innovation moves with structure, discipline, and accountability. Governance is not the enemy of AI strategy. Governance is what allows an AI strategy to scale without becoming an enterprise risk event.

The Central Question for Boards and CCOs

For boards, Chief Compliance Officers, and business leaders, the central question is straightforward: has the company defined the rules of the road before putting AI into production? If the answer is no, the company is already behind.

This is not a theoretical problem. It is happening every day. A business unit buys an AI-enabled tool before legal, compliance, IT, privacy, and security have reviewed it. A vendor pitches a product as low-risk automation, even though it actually makes consequential recommendations. An employee uploads sensitive data into a generative AI platform for convenience. A use case that began as internal support quietly migrates into customer-facing decision-making. A pilot project becomes business as usual without anyone documenting who approved it, what risks were considered, or what human oversight is supposed to look like.

That is what it means when strategy outruns governance. The business has a faster process for adopting AI than it has for understanding, controlling, and monitoring AI risk.

What the DOJ Expects

The Department of Justice has been telling compliance professionals for years that an effective compliance program must be dynamic, risk-based, and integrated into the business. That lesson applies directly here. Under the ECCP, prosecutors ask whether a company has identified and assessed its risk profile, whether policies and procedures are practical and accessible, whether responsibilities are clearly assigned, whether decisions are documented, and whether the program evolves as risks change. AI governance sits squarely in that framework.

What “Rules of the Road” Means in Practice

What do the “rules of the road” look like in practice?

First, the company must define which AI use cases are permissible. These are lower-risk applications that can be used within established controls. Think internal drafting support, workflow automation for non-sensitive administrative tasks, or summarization tools used on approved data sets. Even here, there should be basic conditions: approved tools only, no confidential data unless authorized, user training, logging, and manager accountability.

Second, the company must identify restricted or high-risk use cases. These are situations where AI may be allowed, but only after enhanced review. This can include uses involving personal data, HR decisions, customer communications, pricing, fraud detection, credit or eligibility decisions, compliance surveillance, or any function where bias, opacity, or error could create legal, regulatory, or reputational harm. These use cases should trigger a more formal process that includes a documented risk assessment, legal and compliance review, data governance checks, testing, defined human oversight, and ongoing monitoring.

Third, the company must be clear about prohibited use cases. If an AI application cannot be used consistently with the company’s values, control environment, legal obligations, or risk appetite, it should be off-limits. That might include tools that process sensitive data in unapproved environments, systems that make fully automated consequential decisions without human review, or applications that cannot be explained, tested, validated, or monitored sufficiently for their intended use.

Fourth, the company must establish escalation thresholds. Not every AI decision belongs at the board level, but some certainly do. Use cases involving strategic transformation, material legal exposure, major customer impact, significant third-party dependency, or high-consequence decision-making may need escalation to senior management, a designated AI or risk committee, or the board itself. If management cannot explain when a matter gets elevated, governance is too vague to be trusted.

Why the NIST AI RMF Matters

This is where the NIST Framework is so useful. NIST does not treat AI governance as a one-time signoff exercise. It organizes governance as an ongoing discipline through four connected functions: Govern, Map, Measure, and Manage. For compliance professionals, that is a practical operating model.

Governance means setting accountability, policies, oversight structures, and risk tolerances. It answers who is responsible, who decides, and what standards apply. A map means understanding the use case, context, stakeholders, data, and risks. It answers what the system is actually doing and where exposure lies. Measure means testing, validating, and assessing performance and controls. It answers whether the system works as intended and whether the company can prove it. Managing means acting on what is learned through oversight, remediation, change management, and continual improvement. It answers whether the company is prepared to respond when reality diverges from the plan.

How ISO 42001 Reinforces Governance Discipline

ISO 42001 reinforces the same message from a management systems perspective. It brings structure, accountability, controls, and continual improvement to AI governance. That matters because many organizations do not fail because of a lack of policy language. They fail because they do not operationalize accountability. ISO 42001 pushes companies to embed AI governance into defined processes, assign responsibilities, document controls, conduct internal reviews, and take corrective action. In other words, it turns aspiration into a management discipline.

What Happens When Strategy Outruns Governance

What happens when none of this is done well?

Shadow AI is usually the first warning sign. Employees use public or lightly reviewed tools because they are easy to use, fast, and readily available. Sensitive data may be entered without approval. Outputs may be used in business decisions without validation. The organization tells itself it is still in the experimentation phase, while the risk has already gone live.

Vendor-driven deployment is another danger. The company relies too heavily on what the vendor says the product can do and not enough on its own evaluation of what the product should do, how it works, what data it uses, and what controls are required. When something goes wrong, accountability becomes murky. Procurement says the business wanted speed. The business says IT approved the integration. IT says legal reviewed the contract. Legal says compliance owns the policy. Compliance says no one submitted the use case for formal review. That is not governance. That is institutional finger-pointing.

Undocumented approvals are equally dangerous. An AI tool is launched because everyone generally agrees it seems useful. But there is no record of the intended purpose, risk rating, required controls, human review standard, or approval rationale. Six months later, the company cannot explain why the system was deployed, what guardrails were put in place, or whether its use has drifted beyond its original scope.

The Compliance Mechanisms Companies Need Now

That is why companies need concrete compliance mechanisms now. They need an intake process for AI use cases to enter a formal review channel before deployment. They need risk tiering so not every use case gets the same treatment, but higher-risk applications receive enhanced scrutiny. They need approval workflows with defined roles for the business, legal, compliance, privacy, security, IT, and, where appropriate, model risk or internal audit. They need board reporting triggers to inform leadership when AI adoption crosses materiality or risk thresholds. They need a current model and use-case inventory so the company knows what is in operation. They need change management, so updates, retraining, vendor changes, and scope shifts are reviewed rather than assumed. And they need periodic review because AI risk does not stand still after launch.

The Special Role of Compliance

The compliance professional has a special role here. Compliance is often the function best positioned to connect governance, process, accountability, documentation, and escalation. That is precisely what the DOJ expects in an effective program. If the company can buy AI faster than it can classify risk, document controls, assign accountability, and test outcomes, the program is not keeping pace with the business. That gap will not stay theoretical for long. It will harden into enterprise risk.

Conclusion: Governance Must Keep Pace With Strategy

The lesson is direct. Strategy and governance must move together. AI governance is not a brake pedal. It is the steering system. A company that wants the benefits of AI must be disciplined enough to define where AI can go, where it cannot go, who decides, what gets documented, and when the business must stop and reassess. If the company can move faster on AI strategy than on AI governance, it is creating risk faster than it can manage. That is not innovation. That is exposure.

Categories
31 Days to More Effective Compliance Programs

31 Days to a More Effective Compliance Program: Day 27 – The Compliance Function in an Organization

Welcome to 31 Days to a More Effective Compliance Program. Over this 31-day series in January 2026, Tom Fox will post a key component of a best-practice compliance program each day. By the end of January, you will have enough information to create, design, or enhance a compliance program. Each podcast will be short, at 6-8 minutes, with three key takeaways that you can implement at little or no cost to help update your compliance program. I hope you will join each day in January for this exploration of best practices in compliance. In today’s Day 27 episode, we explore the growing importance and responsibilities of the compliance function within corporations, emphasizing the need for adequate staffing, resources, and independence.

Key highlights:

  • DOJ’s Expectations for Compliance Programs
  • Funding and Resources for Compliance
  • Compliance Program Structure and Authority

Resources:

Listeners to this podcast can receive a 20% discount on The Compliance Handbook, 6th edition, by clicking here.

Categories
Blog

Greek Philosophers Week: Part 5 – Euclid and Proving Your Program Is Effective

We conclude our exploration of how ancient Greek philosophers influence compliance and ethics in 2026 and beyond. In this series, we have considered Socrates, Plato, Aristotle, and Pythagoras. Today, we conclude with Euclid.

Pythagoras teaches compliance professionals how to measure, analyze, and detect ethical risk through data, proportion, and pattern recognition. But measurement alone never closes the loop. At some point, regulators, boards, and senior leadership ask a harder question: Can you prove your compliance program actually works? That is where Euclid becomes the natural capstone of this philosophical journey.

Euclid was not concerned with numbers in isolation. He was concerned with structure, logic, definition, and proof. His Elements did not merely describe geometry. It demonstrated how a coherent system is built from first principles, how each part follows logically from the last, and how conclusions are proven rather than asserted. That methodology aligns almost perfectly with modern expectations for compliance program effectiveness under the DOJ Evaluation of Corporate Compliance Programs (ECCP).

If Pythagoras gives compliance professionals the tools to see risk, Euclid shows them how to organize those insights into a defensible, durable system. We also circle back to Hui Chen, the original Corporate Compliance Counsel to the DOJ, who would challenge Chief Compliance Officers (CCOs) and their counsel when they came before the DOJ in settlement negotiations, demonstrating the effectiveness of their compliance programs through data rather than anecdote.

First Principles Are the Foundation of Compliance Credibility

Euclid begins with definitions, axioms, and postulates. He does not assume shared understanding. He defines it. Everything that follows depends on clarity at the start. Many compliance programs struggle precisely because they skip this step. Policies proliferate. Controls multiply. Training expands. Yet foundational questions remain vague. What does ethical behavior actually mean in this organization? What risks are intolerable regardless of business pressure? What decisions require escalation without exception?

The ECCP begins with 3 fundamental questions:

  1. Is the corporation’s compliance program well designed?
  2. Is the program being applied earnestly and in good faith? In other words, is the program adequately resourced and empowered to function effectively?
  3. Does the corporation’s compliance program work in practice?

Throughout the ECCP, the DOJ repeatedly asks whether a compliance program is well designed. That evaluation begins with clarity of purpose and scope. A Euclidean compliance program explicitly defines its terms, principles, and boundaries. Without that clarity, enforcement becomes inconsistent, and explanations to regulators become fragile. In daily operations, this means compliance professionals must insist on precision. Ambiguity is not flexibility. It is a risk.

Logical Structure Is a Compliance Control

Euclid’s brilliance lies in sequencing. Each proposition follows logically from what came before. Nothing is random. Nothing is decorative. The system works because it is internally consistent. Compliance programs often fail this test. Risk assessments do not inform training. Training does not influence monitoring. Investigations do not drive remediation. Each function operates competently, but not coherently.

The ECCP explicitly evaluates whether compliance programs operate as integrated systems rather than as disconnected components, stating, “Ensure the compliance program is well-integrated into the company’s operations and workforce.” Prosecutors want to see feedback loops, escalation pathways, and continuous improvement mechanisms. That is Euclidean thinking applied to compliance. In practice, compliance leaders should be able to explain how a risk moves through the system from identification to mitigation. If that explanation requires hand-waving, the system is not structurally sound.

Proof, Not Assertion, Is the Regulatory Standard

Euclid never asks the reader to trust him. He proves every claim. That lesson may be his most important contribution to modern compliance. Companies often assert that their programs are effective because training is delivered, policies are updated, or hotlines exist. Hui Chen led the charge on this concept when she was the DOJ Compliance Counsel. The ECCP has reiterated Chen’s requirement for evidence, as prosecutors now routinely request proof of effectiveness. How quickly are issues identified? How consistently is discipline applied? How does remediation prevent recurrence?

A Euclidean compliance program is designed to generate proof. Controls are documented. Decisions are recorded. Metrics are reviewed and refined. Effectiveness is demonstrated through data and outcomes, not narrative assurances. This is not about bureaucracy. It is about credibility. When regulators ask how you know your program works, Euclid provides the answer: because the proof is built into the structure.

Precision Enables Fairness and Trust

Euclid’s definitions leave little room for interpretation. In compliance, precision serves a similar function. Clear definitions reduce bias, inconsistency, and resentment. Vague policies create uneven enforcement. Uneven enforcement destroys trust. Employees quickly learn whether rules are real or elastic. The ECCP’s emphasis on consistent discipline reflects this reality. The ECCP states, “Have disciplinary actions and incentives been fairly and consistently applied across the organization?”

Daily compliance operations should therefore prioritize clarity. What constitutes a conflict of interest? What thresholds trigger approval? What timelines govern investigations? Who owns decisions at each stage? Precision protects both the organization and the compliance function. It allows fairness to be demonstrated, not merely claimed.

Systems Must Be Built to Endure

Euclid’s work has endured for more than two millennia because it was built as a system, not a response to a crisis. Compliance programs should aspire to similar durability. Programs that rely on personalities, informal influence, or unwritten norms collapse when leadership changes. The ECCP evaluates whether compliance programs are institutionalized, supported by governance structures, and able to withstand turnover. A Euclidean compliance program embeds ethics into processes, charters, reporting lines, and documentation. Knowledge is transferred. Decisions are repeatable. Improvements are systematic. This durability is not accidental. It is designed.

Why Euclid Completes the Series

Socrates teaches compliance professionals to ask uncomfortable questions. Plato teaches them to design ethical governance structures. Aristotle shows how ethics are lived through habit and judgment. Pythagoras introduces measurement, analytics, and AI. Euclid brings all of it together. He shows how inquiry, governance, behavior, and data become a coherent system that can be explained, defended, and proven. In modern compliance, that is the difference between aspiration and effectiveness.

5 Key Takeaways for the Compliance Professional

1. Compliance programs must be grounded in clear first principles.

Euclid reminds us that systems fail when foundations are vague. Compliance programs should clearly define ethical expectations, risk boundaries, and escalation triggers. The ECCP evaluates whether programs are thoughtfully designed, not merely comprehensive. Clear first principles guide daily decisions, reduce ambiguity, and support consistent enforcement. Without them, controls become reactive, and credibility erodes under scrutiny.

2. Logical integration is a core element of effectiveness.

Disconnected compliance components create blind spots. Euclid teaches that a system works when each part follows logically from the previous one. Risk assessments should drive policies. Policies should inform training. Training should influence monitoring. Investigations should lead to remediation. The ECCP rewards programs that demonstrate this internal logic. Integration is not administrative elegance. It is risk management.

3. Proof of effectiveness must be built into the program.

Assertions no longer satisfy regulators. Euclid’s insistence on proof mirrors the ECCP’s demand for evidence. Compliance programs should be designed to generate data demonstrating timely detection, consistent discipline, and meaningful remediation. When proof is embedded in the system, credibility follows naturally.

4. Precision enables fairness and protects trust.

Clear definitions and thresholds reduce inconsistency and perceived bias. Euclid’s precision offers a model for compliance policies and procedures. The ECCP scrutinizes the fairness of disciplinary proceedings and investigations because trust depends on it. Precision protects employees, managers, and the compliance function alike.

5. Durable compliance programs are designed, not improvised.

Euclid’s work endures because it was built as a coherent system. Compliance programs should aim for the same longevity. Institutionalized governance, documented processes, and structured improvement allow programs to survive leadership changes and regulatory shifts. Durability is a marker of maturity and a signal of seriousness to regulators.

Euclid teaches compliance professionals the final lesson in this series: effectiveness is not claimed. It is demonstrated.

Conclusion

The enduring relevance of the ancient Greek philosophers to modern compliance and ethics lies in their not theorizing in the abstract. They were grappling with the same human pressures that drive misconduct today: power, incentives, rationalization, fear, and convenience. Socrates teaches compliance professionals the discipline of ethical inquiry and the courage to ask uncomfortable questions. Plato shows that values without governance structures are fragile, while Aristotle grounds ethics in habit, judgment, and daily behavior rather than aspiration. Together, they mirror the DOJ’s insistence that effective compliance programs begin with understanding risk, designing systems to manage it, and ensuring those systems operate in practice.

What makes these philosophers especially relevant today is how naturally their ideas align with modern regulatory expectations. Pythagoras anticipates the role of data, analytics, and AI in measuring compliance effectiveness, while Euclid provides the blueprint for structure, precision, and proof that regulators now demand. In an era of complex global operations and heightened enforcement scrutiny, compliance programs succeed or fail based on inquiry, governance, behavior, measurement, and demonstrable effectiveness. The ancient Greeks understood those dynamics long before corporate compliance existed, which is why their lessons remain not only relevant but essential for modern compliance and ethics professionals.

Categories
31 Days to More Effective Compliance Programs

31 Days to a More Effective Compliance Program: Day 3 – Key Updates in the ECCP: Messaging Apps, Internal Controls, and Compensation

Welcome to 31 Days to a More Effective Compliance Program. Over this 31-day series in January 2026, Tom Fox will post a key component of a best-practice compliance program each day. By the end of January, you will have enough information to create, design, or enhance a compliance program. Each podcast will be short, at 6-8 minutes, with three key takeaways that you can implement at little or no cost to help update your compliance program. I hope you will join each day in January for this exploration of best practices in compliance. In today’s episode, Day 3, we delve into the significant updates in the evaluation of corporate compliance programs, focusing on messaging apps, internal controls, and adequate compensation.

Key highlights:

  • Messaging Apps and Compliance
  • Internal Controls and Risk Management
  • Adequate Compensation for Compliance Teams

Resources:

Listeners to this podcast can receive a 20% discount on The Compliance Handbook, 6th edition, by clicking here.

Categories
31 Days to More Effective Compliance Programs

31 Days to a More Effective Compliance Program: Day 2 – The ECCP on Incentives, Consequences, and Clawbacks

Welcome to 31 Days to a More Effective Compliance Program. Over this 31-day series in January 2026, Tom Fox will post a key component of a best-practice compliance program each day. By the end of January, you will have enough information to create, design, or enhance a compliance program. Each podcast will be short, at 6-8 minutes, with three key takeaways that you can implement at little or no cost to help update your compliance program. I hope you will join each day in January for this exploration of best practices in compliance. Today, we look at what the ECCP has to say on incentives, consequences, and clawbacks.

Key highlights:

  • Starting with Incentives and Consequences
  • Incentive Program Breakdown
  • Consequence Management Deep Dive

Resources:

Listeners to this podcast can receive a 20% discount on The Compliance Handbook, 6th edition, by clicking here.

Categories
Blog

House of Atreus Week: Part 5 – Orestes and Electra – Breaking the Cycle Through Accountability

Every compliance journey must eventually reach its reckoning —the point at which wrongdoing, however deeply embedded, must give way to accountability. In Greek tragedy, that moment comes with Orestes and Electra, the final heirs of the cursed House of Atreus.

Their story marks a transformation, from vengeance to justice, from chaos to order, from curse to compliance. It’s not just the end of a tragic dynasty; it’s the beginning of governance. And for the modern compliance professional, Orestes’ journey mirrors the evolution every organization must undergo, moving from reactive crisis management to mature, transparent, and accountable systems of justice.

Today, we conclude our look at lessons from the House of Atreus for the 21st-century compliance profession through a review of my personal favorite, the tragedy of Orestes and Electra. Their tale was memorialized as the final play in Aeschylus’s trilogy The Oresteia, written in the 5th century BC. The Oresteia trilogy consists of three plays: Agamemnon, The Libation Bearers, and The Eumenides. They all discuss the murder of Agamemnon by Clytemnestra, the murder of Clytemnestra by Orestes, the trial of Orestes, the end of the curse on the House of Atreus, and the pacification of the Furies.

The tale of Orestes and Electra marks a transformation, from vengeance to justice, from chaos to order, from curse to compliance. It is not just the end of a tragic dynasty; it is the beginning of governance and compliance. And for the modern compliance professional, Orestes’ journey mirrors the evolution every organization must undergo —from reactive crisis management to mature, transparent, and accountable systems of justice.

In today’s Part 5, we discuss what every compliance practitioner and compliance regime must eventually face. Their journey reaches its reckoning,  the point where wrongdoing, however deeply embedded, must give way to accountability.

The Last Act of the Curse

After Clytemnestra murders Agamemnon, she takes power alongside her lover, Aegisthus. Their rule, built on deceit and blood, becomes yet another chapter in the family’s curse. Orestes and his sister Electra, exiled and grieving, grow up in a world where justice has been replaced by fear and silence.

Years later, Orestes returns to Mycenae with Electra’s encouragement. Together, they plot vengeance, the killing of their mother and her consort, to avenge their father’s murder. The act fulfills the family’s grim legacy: the son kills the mother as the mother killed the father. But Orestes doesn’t find peace. Instead, he’s haunted by the Furies, ancient goddesses who punish those who shed family blood. Tormented and desperate, he seeks sanctuary in Athens, where the goddess Athena establishes the first trial by jury. The Furies prosecute, Apollo defends, and Athena casts the deciding vote. The verdict is acquittal, but not because Orestes was blameless, but because justice must evolve from vengeance to law. And just like that, the curse ends,  not through violence, but through accountability.

From Retribution to Governance

What Athena did for Orestes is what modern compliance programs do for organizations: they replace personal retribution with institutional justice and institutional fairness. Before that trial, every wrong in the House of Atreus was met with revenge. Each generation avenged the last until there was no one left to save. Athena’s tribunal introduced a revolutionary idea: that justice must be impartial, procedural, and transparent.

That’s precisely the evolution every organization must undertake when it faces a scandal. At first, the instinct is vengeance: fire the bad actors, issue a statement, move on. But sustainable integrity requires something deeper: process, documentation, fairness, and continuous improvement. Orestes’ trial marks the shift from chaos to compliance.

Accountability: The End of the Curse

The word “accountability” is often misunderstood. It does not mean punishment. It means answerability, the willingness to stand before a system greater than oneself and be judged fairly. That is what Orestes did. He did not flee the Furies forever; he submitted to judgment. He participated in the process. And in doing so, he transformed justice from a personal to an institutional matter. For modern compliance officers, this is a powerful metaphor. Accountability is not about creating fear. It is about building trust. It ensures that wrongdoing is addressed through a fair, transparent process that restores, rather than destroys, culture.

The Furies as Internal Audit

The Furies are terrifying, but in the compliance world, they’re familiar. They represent the internal mechanisms of conscience and oversight, the investigations, audits, and regulators that chase wrongdoing wherever it hides. Like Orestes, many leaders try to outrun them, hoping the past won’t catch up. But true integrity doesn’t come from evasion; it comes from engagement. The companies that emerge strongest from scandal are those that face their Furies head-on, invite scrutiny, and cooperate transparently.

Think of how Siemens rebuilt its compliance function after its massive bribery scandal by embracing rigorous internal controls, external oversight, and a commitment to ethical reform. Indeed, we saw similar results based upon similar actions by both Wells Fargo and ABB. That was Orestes’ trial in corporate form, judgment accepted, redemption earned.

Electra: The Voice of Culture Renewal

Electra plays a quieter but equally vital role. She represents the voice of moral conscience, the employee who still believes in right and wrong even when everyone else has gone silent. She is the whistleblower who says, “This isn’t who we are.” The compliance champion who refuses to normalize misconduct. Without Electra’s courage, Orestes would never have acted.

Modern organizations need their Electras: employees empowered to speak, question, and persist. That’s why building a speak-up culture is the cornerstone of the 2024 DOJ Evaluation of Corporate Compliance Programs (ECCP). A company’s ability to surface issues early depends on whether it protects, informs, and celebrates those who come forward. If Orestes symbolizes accountability, Electra symbolizes cultural integrity, the belief that justice is worth pursuing even when it is dangerous.

The Birth of the Rule of Law

The trial of Orestes is one of the most significant moments in Western moral thought because it replaces vengeance with the rule of law. It is also the mythological birth of compliance, where emotion gives way to ethics, and chaos yields to process. Athena’s message is timeless: “No one person may decide justice alone. We must build systems that outlast individuals.”

That is the essence of compliance governance. Codes of conduct, reporting channels, disciplinary processes, and training all exist for one reason: to ensure that justice does not depend on personalities. Orestes’ acquittal didn’t erase his crime. It institutionalized accountability so the next generation wouldn’t repeat his curse. For corporate culture, that’s exactly what post-crisis reform does: it replaces vengeance with systems and outrage with order.

Compliance as Redemption

Orestes’ story ends not in punishment, but in purification. Athena orders the Furies to become the Eumenides,  “the Kindly Ones.” Their role shifts from persecutors to protectors, guarding the moral order they once avenged. That transformation is the perfect metaphor for what a compliance function can become after a crisis. At first, compliance feels punitive,  investigators, auditors, monitors. But over time, as systems mature and transparency grows, compliance evolves into something restorative: a protector of trust, reputation, and ethical resilience. The same forces that once punished now preserve. That is redemption for organizations and for people.

Lessons in Modern Compliance Transformation

What can compliance professionals learn from Orestes’ journey? The parallels are striking.

  1. Justice Must Be Systemic, Not Personal. Vengeance satisfies emotion but destroys culture. Justice through process restores legitimacy. For the compliance professional, the ECCP demands institutional fairness, which builds procedural fairness into investigations. Transparency and due process protect both the company and its people.
  2. Accountability Ends the Cycle. Denial perpetuates dysfunction. Facing wrongdoing directly, even publicly, is the first step to rebuilding credibility. You should conduct root cause analyses after every violation. Use findings to strengthen systems, not just assign blame.
  3. Protect the Electras. Ethical renewal begins with those who dare to speak truth.
  4. As a compliance professional, you must empower whistleblowers by providing visible protections, feedback loops, and cultural recognition.
  5. Embrace Your Furies. Auditors, regulators, and monitors are not enemies; instead, they should be seen as accountability partners. As counterintuitive as it may seem, you should treat oversight as an opportunity. Transparency with regulators builds long-term trust.
  6. Transform Enforcement into Ethics. The end goal of compliance is not punishment, it is not even detection; it is prevention. Every compliance professional should use disciplinary outcomes as learning opportunities. Celebrate integrity as publicly as you punish misconduct.

From Tragedy to Transformation

The House of Atreus began with arrogance, deception, and retaliation. It ended with something extraordinary, the birth of justice as a system. Each generation’s failure taught a lesson:

  • Tantalus showed that leadership without humility corrupts.
  • Pelops revealed the dangers of winning through corruption.
  • Atreus and Thyestes exposed the poison of internal retaliation.
  • Agamemnon and Clytemnestra warned of power without accountability.
  • Orestes and Electra finally demonstrated how accountability, due process, and transparency can cleanse even the deepest cultural stain.

That arc is the same one every mature compliance program follows from reaction to reflection, from punishment to prevention, from crisis to culture.

From Curse to Compliance

The story of Orestes is not about vengeance; rather, it is about evolution. He did not end the curse by denying it. He ended it by confronting it, submitting to judgment, and accepting that systems, not individuals, define justice. That is the ultimate compliance insight. You can’t train your way out of a cultural problem. You can’t manage ethics through charisma. You must build structures that embed accountability into every decision, every leader, and every process.

Orestes reminds us that compliance is not just about preventing misconduct; it is about healing organizations. It is about helping companies move from the chaos of reaction to the clarity of governance, from fear to fairness, from silence to transparency, from vengeance to virtue. Because in the end, every organization has its own House of Atreus somewhere in its history. The question is not whether the curse exists. The question is whether we, like Orestes, will have the courage to face it and the wisdom to replace it with justice that lasts.

Categories
Blog

House of Atreus Week: Part 4 – Agamemnon and Clytemnestra – When Power Breeds Entitlement

We continue our look at lessons from the House of Atreus for the 21st-century compliance profession, focusing on key stories and mining them for compliance lessons. In today’s Part 4, we take up the Agamemnon Problem: a leader so focused on results, so convinced of their indispensability, that ethics become negotiable. It is the mindset that says, “We’ll fix the compliance later—after we win.”

In Greek tragedy, that rationalization cost Agamemnon his life. In corporate life, it costs organizations their culture, credibility, and sometimes their license to operate. The story of Agamemnon and Clytemnestra is not only one of betrayal and revenge, it is a powerful parable about what happens when leaders mistake power for permission and performance for purpose.

The King’s Fatal Trade-Off

As the legend goes, Agamemnon, king of Mycenae and commander of the Greek forces at Troy, faced a crisis before the war even began. The goddess Artemis, angered by his arrogance, becalmed the winds and trapped his fleet in port. The only way to appease her, a seer declared, was to sacrifice his daughter, Iphigenia.

Agamemnon’s dilemma was stark: abandon his military ambitions or sacrifice his own child. He chose the latter. The winds rose, the ships sailed, and the war began. Years later, when Agamemnon returned triumphant, his wife Clytemnestra murdered him in his bath as revenge for their daughter’s death. This was not just a family tragedy; it was a leadership failure of the highest order. Agamemnon traded ethics for expedience, and the cost was everything he loved.

The Corporate Iphigenia

Every organization has its Iphigenia(s); the values, people, or principles that get sacrificed for “strategic goals.” It may be:

  • Cutting compliance budgets to hit quarterly numbers.
  • Overriding safety protocols to meet production quotas.
  • Ignoring harassment complaints to keep a star performer happy.

Like Agamemnon, leaders rationalize these sacrifices as necessary or temporary. But every compromise chips away at the moral capital that sustains the enterprise. Once the organization learns that “winning” matters more than doing right, the line between ambition and arrogance disappears.

The Entitlement of Success

When Agamemnon returned from Troy, he arrived not as a humbled survivor but as an entitled conqueror. He paraded Cassandra, a captive prophetess, before his wife and walked proudly across a purple carpet, a gesture the Greeks saw as blasphemous arrogance. It’s the same pattern we see in modern compliance disasters: success breeding entitlement. Executives who deliver profits begin to believe they’ve earned the right to bend the rules. Performance metrics replace principles as the measure of worth.

Consider a few familiar examples:

  • The Wells Fargo sales scandal: Pressure to perform led employees to create millions of fake accounts. It also involved senior management lying to its own Board of Directors.
  • Volkswagen’s emissions fraud: Engineers rationalized deception as necessary to stay competitive. But this rationalization went all the way to the CEO.
  • Boeing’s safety crisis: Leadership prioritized schedules and cost over engineering integrity. Then they blamed the airline’s pilots for operational failures.

In each case, strong organizations were undone not by ignorance of ethics but by entitlement —the belief that achievement excused misconduct.

The Compliance Cost of Entitlement

Entitlement corrodes three pillars of compliance: accountability, transparency, and humility.

1. Accountability: When leaders feel untouchable, rules become optional. Internal controls are ignored, and ethical review is seen as bureaucracy rather than protection.

2. Transparency: Entitled leaders hoard information and discourage challenge. “Bad news doesn’t travel up” becomes the cultural norm.

3. Humility: Ethical reflection gives way to moral blindness. If success is proof of righteousness, who needs oversight?

Agamemnon’s decision to sacrifice Iphigenia was not just moral cowardice; it was a governance failure. He believed his power justified his actions, and no one around him could say otherwise. That is precisely how modern compliance collapses begin.

Clytemnestra: The Whistleblower Turned Avenger

Clytemnestra’s revenge may seem extreme, but, symbolically, she represents the voice of accountability that has been ignored for too long. She warned, questioned, and grieved, yet was silenced by hierarchy and hubris. When the system denied her justice, she took justice into her own hands.

Modern organizations often create their own Clytemnestras when they suppress legitimate dissent. Whistleblowers who feel unheard can become external leakers, litigants, or catalysts for regulatory scrutiny. Every retaliation case begins as an unheeded complaint. The DOJ’s 2024 ECCP emphasizes this point. Organizations must protect, inform, and empower those who speak up. When internal channels fail, external consequences follow, just as Clytemnestra’s knife followed Agamemnon’s silence.

Ethical Decision-Making Under Pressure

Agamemnon’s fateful choice came under immense pressure, a condition every executive recognizes. But pressure is where compliance either proves its worth or disappears. Strong organizations prepare for ethical stress tests long before a crisis strikes. They establish frameworks that turn moral instinct into a structured process:

1. Define Core Non-Negotiables – The “values that will not be sacrificed.” If integrity, safety, or human dignity are ever negotiable, they soon become expendable.

2. Create Decision Pathways – Require escalation when choices have ethical or reputational risk. Ethical red flags should automatically trigger review, not after-action regret.

3. Model Accountability at the Top – Leaders must demonstrate that difficult ethical decisions are shared, not borne alone. Agamemnon acted in isolation; modern governance demands collaboration.

The Tyranny of Performance Metrics

Much of Agamemnon’s arrogance stemmed from performance obsession, the need to deliver victory at any cost. That same tyranny drives unethical behavior in today’s boardrooms. Metrics matter, but when they become idols, they demand sacrifices. Compliance programs should therefore measure how results are achieved, not just whether they are achieved.

The 2024 Evaluation of Corporate Compliance Programs (ECCP) specifically instructs prosecutors to ask whether companies’ incentives reward ethical behavior. A compliant organization aligns compensation with conduct; an entitled one rewards outcomes regardless of means. A key question for leaders: Would I still consider this a “win” if it were public tomorrow?

From Power to Stewardship

The entitlement cure is stewardship, the recognition that power is not owned, but entrusted. Great leaders see themselves as guardians of values, not exploiters of privilege. This mindset shift transforms compliance from constraint to compass:

  • Stewards ask how their choices affect stakeholders beyond themselves.
  • Stewards invite transparency because they understand accountability strengthens credibility.
  • Stewards use compliance as a mirror, not a muzzle.

Agamemnon ruled as an owner; a steward would have ruled as a custodian. The difference is the difference between arrogance and integrity.

The Compliance Evangelist’s Reflection: The Scarlet Carpet of Arrogance

When Agamemnon strode across that purple carpet, he symbolically walked across the values he was sworn to protect. Every leader who dismisses compliance as “red tape” does the same. Each step says, “The rules are for others.” But history and enforcement teach a consistent lesson: when leaders trample ethics, the organization soon trips over the fabric they have soiled. Clytemnestra’s dagger was not random vengeance; it was the return of consequence. In today’s language, it was enforcement action, indeed a reckoning deferred until accountability could no longer be ignored.

Breaking the Cycle: From Arrogance to Accountability

The tragedy of Agamemnon and Clytemnestra is that both were right and both were wrong. He betrayed his values for ambition; she destroyed justice in the name of vengeance. Their story ends in blood because neither trusted process, transparency, or accountability. Modern organizations don’t have to share that fate. Compliance offers a third path: structured accountability through systems, not swords. It ensures that no one, no matter how powerful, stands above the moral order that sustains the enterprise.

When companies embrace that mindset, they turn tragedy into transformation. They move from the purple carpet of arrogance to the solid ground of integrity. Because, as every compliance professional knows, the true test of leadership is not what you achieve when you are powerful, it is what you refuse to sacrifice to stay that way.

I hope you will join us for our concluding Part 5 — Orestes and Electra: Breaking the Cycle Through Accountability. This is my favorite story from the House of Atreus. With this myth, we will see how justice, rule of law, and redemption finally end the curse of the House of Atreus and what that means for the modern compliance function striving to build ethical resilience and renewal.