Categories
Blog

House of Atreus Week: Part 3 – Atreus and Thyestes – Internal Rivalry and the Dangers of Retaliation

We continue to look at the lessons from the House of Atreus for the 21st-century compliance profession, focusing on the key stories and mining them for insights. In today’s Part 3, we take up the feud between Atreus and Thyestes, sons of Pelops and heirs to his poisoned legacy. Their myth is not just about murder and betrayal; it is about what happens when leaders weaponize authority for vengeance rather than stewardship.

Every organization eventually faces conflict within its own ranks. Disagreements over power, vision, and credit are inevitable. But when rivalry turns to revenge, governance collapses, trust erodes, and compliance becomes collateral damage. Today, we take a deep dive into this issue from the 21st-century compliance perspective.

The Feast of Vengeance

After Pelops’ death, his sons Atreus and Thyestes fought over the throne of Mycenae. They began like many corporate siblings, ambitious, capable, and determined to lead. But soon ambition turned into envy. Thyestes seduced Atreus’ wife and stole a prized golden lamb that symbolized kingship.

Atreus, humiliated, plotted revenge. Pretending reconciliation, he invited Thyestes and his sons to a grand banquet. During the feast, Atreus served them a meal of Thyestes’s own children. (Shakespeare used this story much later.) When the truth was revealed, horror swept the hall. Thyestes cursed his brother, and the curse carried through the next generation, consuming Atreus’ son Agamemnon and his grandson Orestes. It is a horrifying tale, but beneath the gore lies a familiar truth: internal retaliation destroys organizations from the inside out.

When Leadership Turns on Itself

Atreus’ banquet is not simply a mythic horror story fit for my classic monster movie month; rather, it is a 21st-century metaphor for every leadership team that devours its own. In terms of compliance, Atreus and Thyestes represent toxic internal politics. They illustrate how leadership rivalries, unchecked ego, and personal vendettas can dismantle governance systems faster than any external scandal.

Modern organizations suffer the same fate when:

  • Executives undermine each other publicly.
  • Managers retaliate against whistleblowers or rivals.
  • Compliance officers are punished for doing their jobs.

When leaders use their authority to punish rather than protect, culture collapses into fear. Employees stop reporting misconduct, colleagues turn on one another, and the compliance function becomes an instrument of control instead of accountability. Atreus’ feast might look extreme, but we have all seen versions of it in the workplace.

The Corporate Equivalent of the Cannibal Feast

Let’s translate the myth into modern terms.

  • Atreus’ “banquet” = a retaliatory campaign designed to humiliate a rival or critic.
  • Thyestes’ seduction = internal manipulation, gossip, or theft of credit.
  • The curse = the lingering culture of distrust that infects every successor.

Retaliation rarely ends with the original act. Once one leader weaponizes power, everyone learns the same lesson: “You’re safe only when you’re silent.” That’s how once-strong organizations become silos of fear. Compliance reports decline not because misconduct has ended, but because employees no longer believe reporting is safe. Like the House of Atreus, the company devours itself while pretending to feast.

The Dangers of Internal Retaliation

From the compliance perspective, retaliation is one of the clearest indicators of cultural rot. It’s also one of the DOJ’s most serious red flags. The 2024 Evaluation of Corporate Compliance Programs (ECCP) explicitly asks prosecutors to evaluate:

  • Whether employees are protected from retaliation.
  • Whether complaints lead to timely investigations.
  • Whether leadership promotes a speak-up culture.

If your organization punishes dissent, even quietly, you may well find yourself already on the DOJ’s radar. Atreus’ actions were the ultimate act of retaliation: gruesome, personal, and destructive. But the underlying pattern is timeless, leadership vengeance disguised as discipline. The lesson is as modern as it is mythic: a compliance program without psychological safety is a compliance program in name only.

Case Study Parallels: When Modern Leaders Feast on Their Own

  • Uber (2017): Retaliation against employees who raised harassment claims led to executive resignations and a cultural overhaul.
  • Wells Fargo: Whistleblowers reported retaliation after flagging fraudulent account practices, compounding reputational damage.
  • Boeing (737 MAX): Internal dissent on safety concerns was suppressed, leading to tragedies that reshaped regulatory scrutiny.

Each of these companies faced its own version of Atreus’ banquet, consuming credibility and trust in the process.

The Role of Compliance in Preventing Organizational Cannibalism

The compliance function exists not just to catch misconduct, but to defend integrity against internal retaliation. A strong compliance culture ensures that ethical leadership trumps personal rivalry. Here’s how to do it:

1. Build governance that transcends personalities. Authority should rest on process, not proximity to power.

2. Separate investigative authority from reporting lines. Compliance officers must have autonomy to act without interference.

3. Educate leadership on the cost of retaliation. Retaliation isn’t just a legal risk — it’s a culture killer.

When leaders understand that internal war erodes value faster than external threats, they start behaving more like guardians than gladiators.

Creating a Culture of Trust After Betrayal

Atreus’ kingdom fell because no one could trust anyone. In business terms, that’s what happens when transparency dies. To rebuild trust, companies must do three things:

1. Acknowledge Harm. Pretending internal feuds never happened only deepens cynicism. Compliance leaders must publicly reinforce that retaliation and toxicity are violations of corporate values. Acknowledgment is the first step toward cultural repair.

2. Reinforce Transparency. Regular reporting on investigations, outcomes, and disciplinary measures builds credibility. Employees must see that misconduct is addressed fairly, not selectively.

3. Model Ethical Reconciliation. Where conflict exists, leaders must model resolution through dialogue, not vengeance. A modern compliance culture is one where accountability coexists with forgiveness, where mistakes are corrected, not avenged.

Leadership Ego and the Compliance Cost

The rivalry between Atreus and Thyestes began with ego, the same ego that drives many corporate meltdowns. Ego tells leaders that compliance is optional, that their moral compass is self-calibrated. It convinces them that retaliation is justified, that “he started it,” or that removing a critic will restore order.

But as every compliance professional knows, ego is expensive. It costs credibility, cooperation, and often millions in remediation and fines. The only sustainable leadership model values humility over hubris. In compliance terms: replace ego with ethics, and rivalry with responsibility.

The Compliance Evangelist’s Reflection: The Curse of the Retaliator

Atreus believed vengeance would bring closure. Instead, it ensured endless conflict. In organizations, retaliation operates the same way. It may silence the critic today, but it guarantees more fear and more silence tomorrow.

The DOJ, SEC, and whistleblower programs worldwide have made one thing clear: protecting those who speak up is not just the right thing to do; it is the smart business approach. The companies that thrive in the modern regulatory landscape are those that treat every internal voice as an asset, not a threat. Atreus’ downfall shows what happens when leaders fail to learn that lesson. His house became a case study in the cost of ignoring culture. For compliance professionals, that’s the real moral: you cannot achieve ethical stability through punishment alone.

From Retaliation to Redemption

The saga of Atreus and Thyestes teaches us that retaliation is never a solution; it is a multiplier of risk. The only way to end the cycle is through structural and cultural change: transparency, accountability, and empathy in leadership. For compliance professionals, that means moving from enforcement to enlightenment, helping leaders understand that the true power of compliance is not control, but trust. Because when leaders stop feeding on their own and start feeding their culture with integrity, the curse finally breaks.

I hope you will join me tomorrow for Part 4 — Agamemnon and Clytemnestra: When Power Breeds Entitlement. In it, we will explore how Agamemnon’s moral compromises and Clytemnestra’s revenge illuminate the modern dangers of performance pressure, ethical trade-offs, and the corruption of power at the top.
Categories
Blog

House of Atreus Week: Part 2 – Pelops and Myrtilus – Corruption in the Bidding Process

The curse of the House of Atreus did not begin and end with Tantalus. Like many toxic corporate cultures, it passed from one generation to the next a legacy of moral shortcuts disguised as clever strategy.

We continue our look at lessons from the House of Atreus for the 21st-century compliance profession, focusing on the key stories and mining them for valuable insights. In today’s Part 2, we consider the myth of Pelops and Myrtilus, an ancient fable about corruption, betrayal, and the fatal cost of winning the wrong way. In this story, we look at Pelops, who was Tantalus’s son. Having been literally restored to life by the gods, he had the chance to rebuild his house on a foundation of integrity. Instead, he reached for the easy win, and in doing so, repeated his father’s error: he traded ethics for expedience.

For modern compliance professionals, it is a reminder that bribery and ethical compromise never end where you think they will. They will always come back to haunt you.

The Chariot Race for a Kingdom

According to Greek legend, King Oenomaus of Pisa received a prophecy that he would die at the hands of his son-in-law. To prevent this, he devised a deadly test for any man seeking to marry his daughter, Hippodamia, a chariot race from Pisa to Corinth. If the suitor won, he gained Hippodamia’s hand. If he lost, he died. Pelops, ambitious and determined, entered the race. But he knew Oenomaus’ horses were divine and unbeatable. So he sought an advantage, not through skill or preparation, but through corruption.

He approached the king’s charioteer, Myrtilus, and offered a bribe: riches, favor, and a promise of reward. Myrtilus agreed to sabotage Oenomaus’ chariot by replacing the bronze linchpins with wax. During the race, the wax melted, the chariot crashed, and the king was killed.

But when Myrtilus came to claim his reward, Pelops betrayed him, either pushing him off a cliff or ordering his death. As he fell, Myrtilus cursed Pelops and his descendants, ensuring the family’s cycle of corruption and vengeance would continue.

The First Procurement Fraud

Strip away the mythic trappings, and Pelops’ race looks remarkably modern.

This was a procurement process, a competition for something of value (in this case, marriage and a kingdom), corrupted by bribery and fraud. Pelops did not win on merit; he won by manipulating a key insider in the process.

That’s the same dynamic at play in so many real-world scandals:

  • A contractor bribing a government official for an unfair advantage.
  • A vendor is rigging bids through inside information.
  • A company turning a blind eye to its agents’ actions abroad, so long as they deliver results.

In each case, the underlying temptation is the same as Pelops’: the belief that “winning is what matters.”

The Illusion of a “Victimless” Bribe

Pelops might have rationalized his actions. He could have told himself that everyone cheats in such races or that Oenomaus’ divine horses made the contest unfair to begin with, that the ends justified the means.

Modern compliance officers hear versions of this rationalization every day:

  • “It’s just a facilitation payment.”
  • “That’s how business is done in this region.”
  • “We’re not bribing; we’re just showing appreciation.”

But as Pelops learned, there is no such thing as a victimless bribe. His corruption did not end with a single race; unfortunately, it defined generations. Myrtilus’ curse became symbolic of the reputational and ethical taint that lingers long after the bribe is paid.

Third-Party Risk: Myrtilus as the First “Agent”

In compliance terms, Myrtilus represents the classic third-party intermediary, the local fixer, the consultant, the distributor. He was not a direct employee, but his actions became Pelops’ liability. When Pelops bribed Myrtilus, he created not just moral exposure, but third-party risk. Once you involve a third party in your scheme, you lose control over the outcome. Myrtilus could expose him, blackmail him, or turn witness.

Modern compliance programs have learned this lesson the hard way. Nearly every major FCPA enforcement action, from Siemens to Petrobras to Deere, involves third-party intermediaries. These individuals promise results, grease local wheels, and leave the company holding the bag when the investigation begins. Pelops thought he could control Myrtilus. He could not. No one ever can.

The Cost of Betrayal: When Corruption Destroys Trust

After the race, Pelops killed Myrtilus to eliminate a liability. But in doing so, he destroyed something even more valuable: trust.

Once an organization uses deception as a tool, it cannot sustain authentic relationships with employees, partners, regulators, or the public. Each act of concealment breeds another, until deception becomes standard operating procedure.

We’ve seen this pattern again and again:

  • A company that falsifies quality reports must falsify safety audits next.
  • A firm that manipulates bid data must suppress whistleblowers who question it.
  • A leader who lies externally must eventually lie internally.

In the end, Pelops did not just kill a man; he killed his organization’s capacity for integrity. That’s the same fate that awaits companies that treat compliance as expendable.

Culture Eats Compliance for Breakfast

The myth of Pelops is not about one race or one bribe; it is about the cultural rot that follows. Once Pelops normalized deceit, his descendants followed suit.

In corporate life, this manifests as a culture of winning at any cost, the most dangerous culture there is. It’s what drives salespeople to falsify data, procurement officers to overlook red flags, and executives to manipulate books.

Culture eats compliance for breakfast because if the unspoken rule of your organization is “get the deal,” no policy manual will save you. Pelops’ court would have had a Code of Ethics printed in gold, and it still wouldn’t have mattered. The only antidote is integrity built into incentives, recognition, and leadership behavior.

Lessons for Modern Compliance Professionals

What can we learn from Pelops’ fall? Quite a lot. His story offers five timeless lessons for those charged with safeguarding ethics and integrity in complex organizations.

1. Corruption Always Starts Small

The first step down the wrong path rarely looks like a scandal. It seems like a shortcut. A “favor.” A small gift. Pelops’ race was just one event, yet it came to define an entire dynasty. The concept of broken windows has demonstrated that you should treat every minor ethical compromise as a potential precedent. Small acts of misconduct become cultural habits faster than anyone realizes.

2. Third-Party Due Diligence Is Non-Negotiable

Myrtilus’ betrayal highlights why vetting, monitoring, and auditing third parties is critical. Companies must know who they’re partnering with and what incentives drive their actions. This means that compliance must have a robust third-party risk management process in place. You should require a business justification, a questionnaire, documented due diligence, risk-based screening, compliance terms and conditions in your contract, and ongoing monitoring for all third parties after the contract is signed.  Finally, transparency is not optional; it is mandatory.

3. Ethical Procurement Builds Long-Term Value

In the rush to “win” contracts, companies often forget that ethical procurement protects more than reputation; it protects relationships. A tainted bid can lead to debarment, litigation, and loss of trust from clients and governments alike. For the compliance professional, you must embed integrity in procurement policy. Make ethics a competitive advantage, not a compliance burden.

4. Retaliation Destroys Cultures

Pelops’ murder of Myrtilus was the ancient equivalent of whistleblower retaliation. Myrtilus knew too much, and instead of managing the risk ethically, Pelops eliminated the witness. The result? A curse or, in modern terms, a scandal that never dies. Every compliance professional must work diligently to protect those who speak up. Encourage reporting. Make it clear that retaliation is a firing offense, not a survival tactic.

5. Integrity Outlasts Every Shortcut

Pelops won his race but lost his legacy. The true measure of success for individuals and organizations alike is sustainability. Ethical wins last; corrupt ones collapse. This requires corporate cultures where ethical behavior and business success are aligned. When values drive results, not the other way around, compliance becomes self-sustaining.

The Curse of the Easy Win

Every compliance professional has faced their “Pelops moment”; that pressure to deliver results faster, cheaper, or more impressively than the rules allow. The temptation is powerful because it is wrapped in the language of success. But as Pelops shows, every unethical win carries a hidden invoice. The ancient Greeks would call it nemesis, the inescapable reckoning that follows hubris. We call it enforcement. Whether through regulators, prosecutors, or public outrage, the bill always comes due.

The challenge for modern compliance leaders is to help their organizations see beyond the race. Winning today is not worth cursing tomorrow.

Join us tomorrow for Part 3 — Atreus and Thyestes: Internal Rivalry and the Dangers of Retaliation. We will explore how infighting, revenge, and the weaponization of leadership destroyed the next generation and how modern organizations can prevent internal culture wars from becoming compliance catastrophes.


Categories
Blog

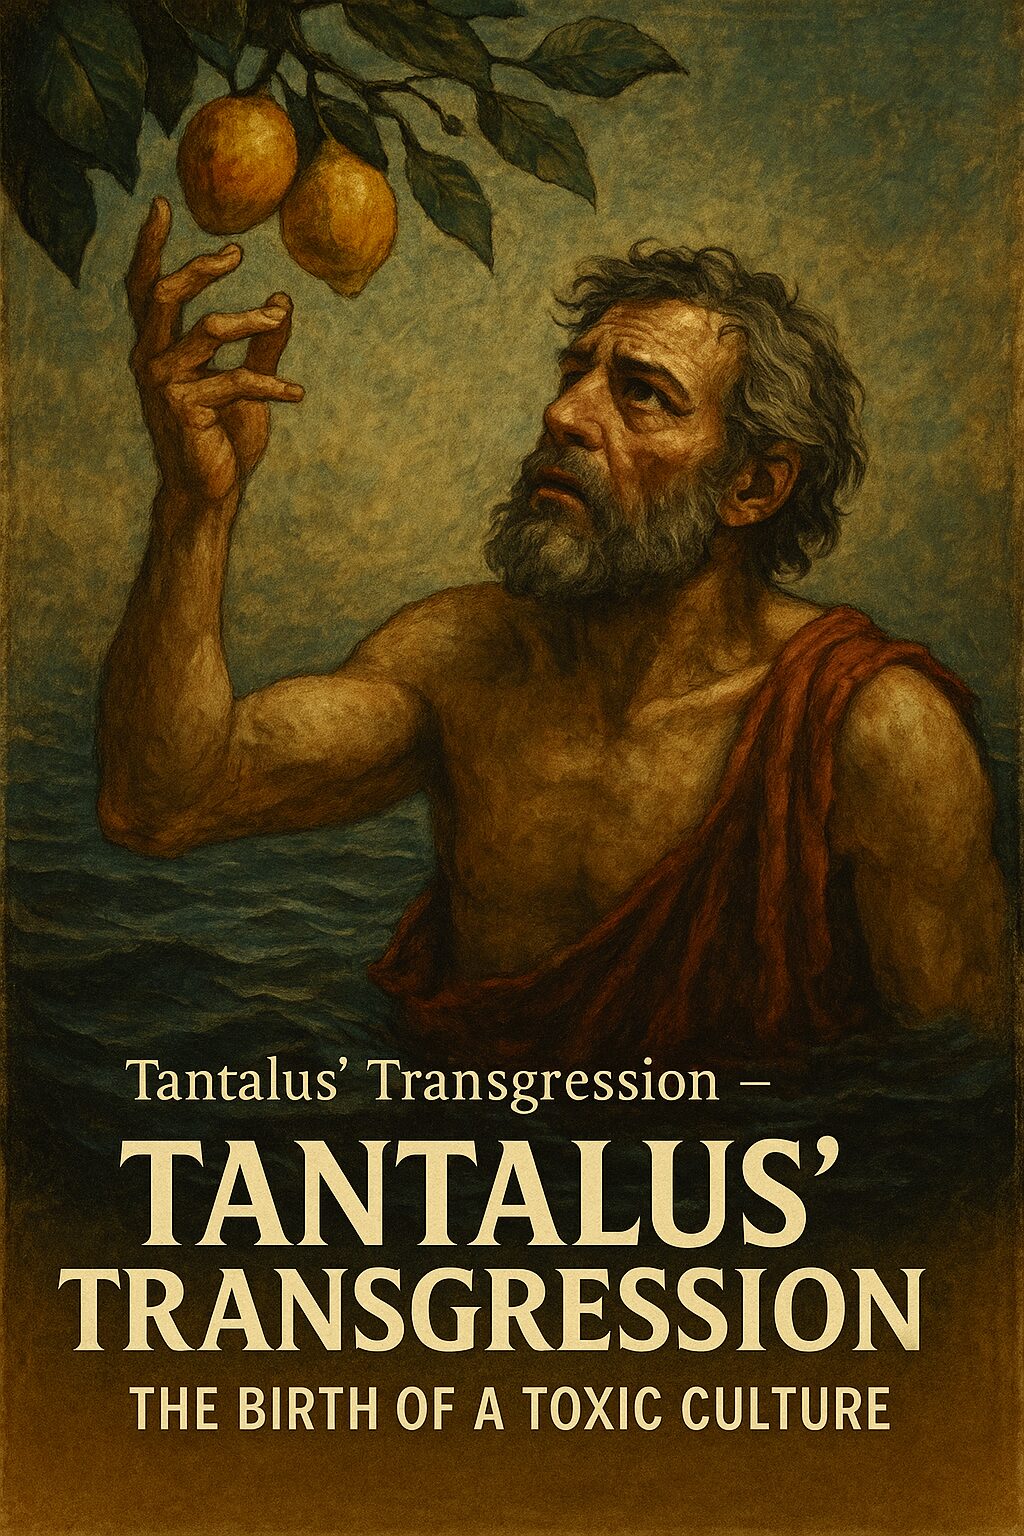
House of Atreus Week: Part 1 – Tantalus’ Transgression – The Birth of a Toxic Culture

I have long been fascinated by the Greek myths around the House of Atreus. It is the most cursed House in all Greek myth. I have also long wanted to blog post series on the compliance lessons for the modern-day compliance professional. This week, I am going to take a deep dive into the most doomed House and explore some of the key stories to mine them for lessons learned for the 21st-century compliance professional. We begin our series with the founder of the House of Atreus, Tantalus, and how one leader’s moral failure can poison the entire culture of an organization. His story is a cautionary tale about hubris, accountability, and the long shadow of tone from the top.

Every great compliance failure begins somewhere. Sometimes it is a single decision, a moment of arrogance, or the quiet belief that the rules apply to everyone else but not to you. In the myths of ancient Greece, that moment came with Tantalus, patriarch of the cursed House of Atreus. His name lives on in infamy, not because of power lost, but because of ethics abandoned.

The Feast of Deception

Tantalus was a favorite of the gods. He dined with them on Mount Olympus, enjoying privileges no mortal ever had. But instead of gratitude, he showed contempt. To test their omniscience, Tantalus served the gods a horrific meal, the cooked flesh of his own son, Pelops. The gods recoiled in horror, restored Pelops to life, and condemned Tantalus to eternal punishment: forever hungry and thirsty, standing in a pool of water beneath fruit-laden branches that receded whenever he reached for them.

This is where we get the word tantalize to tempt with what is always just out of reach. But for compliance professionals, the story isn’t about temptation; it’s about transgression.

Tantalus’ sin was not merely moral or criminal. It was cultural. It revealed a belief that he was above consequence, that his proximity to power made him immune to accountability. Sound familiar? It’s the same psychology that drives corporate misconduct today: the executive who hides risk, manipulates reporting lines, or treats compliance as a box to check rather than a value to live.

Hubris at the Top: When Leaders Believe They Are Untouchable

The core of Tantalus’ failure is hubris, excessive pride that blinds leaders to ethical limits. He thought himself equal to the gods, just as modern executives sometimes see themselves as beyond internal controls, policies, or oversight.

We have seen it in corporate scandals from Enron to Theranos: charismatic leaders who create cultures where questioning authority is punished, transparency is discouraged, and the pursuit of results justifies every means. These leaders often start with good intentions —innovation, performance, growth — but end in disaster because no one dares to tell them “no.” When a CEO, department head, or even a team manager sends the message that rules are flexible for those who produce, that’s the modern equivalent of dining at Olympus. It’s the moment when culture begins to rot from the inside.

Tone from the Top: What Tantalus Forgot

In compliance, we often say “tone from the top” sets the ethical compass of the organization. Tantalus was the top, and his tone was deceitful. Instead of modeling integrity, he modeled arrogance and disrespect. His actions communicated that power excused anything.

Modern organizations are no different. Employees don’t take their ethical cues from the code of conduct on the intranet. They take them from leadership behavior, from what’s rewarded, ignored, or punished.

If Tantalus had shown humility or accountability, his descendants might have inherited a culture of honor. Instead, they inherited corruption, vengeance, and betrayal. It’s no coincidence that every generation of the House of Atreus, including Pelops, Atreus, Thyestes, Agamemnon, Clytemnestra, Orestes, repeats the cycle of wrongdoing and retaliation. The family’s downfall wasn’t fate; it was culture. A toxic tone from the top doesn’t just corrupt a moment; it defines a legacy.

Culture of Consequences: What Happens When Misconduct Goes Unpunished

One of the most striking aspects of the Tantalus myth is how long the effects last. His descendants commit crimes generations later, yet all trace back to his original transgression.

That’s what happens in modern corporations when ethical breaches are not addressed. Once misconduct is tolerated, it becomes precedent. Once precedent hardens, it becomes culture. Think of organizations where sexual harassment was covered up “to protect the company,” or where accounting irregularities were ignored “to meet quarterly targets.” Each decision not to act creates a silent permission structure. And before long, you have what we see in so many enforcement cases: a pattern of misconduct spanning years, sometimes decades.

Tantalus’ punishment, forever reaching but never attaining satisfaction, mirrors what happens in these companies. They chase success endlessly, but integrity is always out of reach because they’ve traded ethics for expedience. A culture of consequences, by contrast, does the opposite. It makes accountability tangible. It shows employees that integrity is the expectation, not the exception.

The Modern Mirror: When Hubris Meets Compliance Failure

The story of Tantalus echoes across modern boardrooms and compliance case studies. Consider:

  • The FCPA case against Siemens (2008): A culture of “business at any cost” led to systematic bribery across divisions, because leadership prioritized results over integrity.
  • The Wells Fargo scandal: Unrealistic sales goals, driven by executives insulated from consequence, encouraged widespread fraud at the branch level.
  • Theranos: A founder’s belief in her infallibility silenced dissent, distorted reporting, and destroyed trust both internally and externally.

Each of these stories began like Tantalus’ dinner with one decision to deceive, rationalized as necessary, even brilliant. Each became a legend of ethical collapse.

The compliance lesson is simple: arrogance without accountability creates catastrophe.

Rebuilding What is Broken: Lessons from Tantalus’ Fall

So how do we avoid the curse of Tantalus in modern organizations? Three principles stand out:

1. Make Ethics the Core of Leadership Identity

Ethical leadership isn’t a function of compliance checklists. It’s the lived demonstration of integrity. Leaders must see compliance not as a constraint but as an enabler of trust and sustainability. When executives model ethical decision-making, it cascades downward.

Compliance Lesson: Integrate ethical leadership into performance reviews and succession planning. Reward transparency as much as performance.

2. Institutionalize Accountability

Accountability must be structured, not situational. That means ensuring robust internal investigations, consistent discipline, and a compliance function with real independence. The moment compliance must “ask permission” to act, the organization has lost its compass.

Compliance Lesson: Empower compliance officers with direct access to the board and audit committee. Build transparency into reporting lines.

3. Preserve Psychological Safety

Tantalus’ court, like many modern workplaces, thrived on fear. When employees can’t question leaders or raise concerns, misconduct flourishes. Psychological safety is the soil in which ethical cultures grow.

Compliance Lesson: Implement anonymous reporting, protect whistleblowers, and make public examples of non-retaliation.

Breaking the Curse: The Compliance Evangelist’s View

The curse of Tantalus was not divine punishment; instead, it was a predictable outcome of leadership failure. Every compliance professional knows that culture is destiny. If leaders are deceitful, employees will be cynical. If leaders are accountable, employees will be engaged.

Tantalus’ name survives as a warning to those who confuse privilege with power, and authority with exemption. His eternal hunger reflects what happens when organizations try to feed success on a diet of deception; they are never satisfied because trust, once lost, cannot nourish growth.

The modern compliance officer stands at the intersection of myth and management, tasked with ensuring that our organizations don’t repeat Tantalus’ mistake. We cannot test the gods of regulation or ethics without consequence. Instead, we must build cultures where doing right isn’t exceptional; it is expected.

Because in the end, every compliance program has a mythic choice: become Olympus or become Tantalus.

Join us tomorrow for Part 2 — Pelops and Myrtilus: Corruption in the Bidding Process. We will explore how bribery, betrayal, and broken promises tainted Pelops’ victory and what it teaches us about third-party risk and ethical procurement.

Categories
Blog

Using AI to Embed Compliance into Business Operations

Ed. Note: This week, we present a week-long series on the use of GenAI in a best practices compliance program. Additionally, for each blog post, I have created a one-page checklist for each article that you can use in presentations or for easier reference. Email my EA Jaja at jaja@compliancepodcastnetwork.net for a complimentary copy.

Compliance programs have long wrestled with a central challenge: how to move from “bolt-on” to “built-in.” Too often, compliance has been perceived as an overlay, a set of policies and reviews that operate parallel to business activity. The Department of Justice has repeatedly emphasized that compliance should be integrated directly into operations, not treated as an afterthought.

Generative AI offers compliance professionals a new tool to achieve this, as Elisa Farri and Gabriele Rosani argue in an HBR article How AI Can Help Managers Think Through Problems, that AI is not just a productivity enhancer but a thought partner. Instead, it is capable of helping leaders frame problems, test assumptions, and engage in structured dialogues that improve decision-making.

I aim to utilize their article to support compliance officers in leveraging AI to enhance our ability to embed compliance into business processes more effectively. Today, I conclude my five-part blog post series on using GenAI in compliance to explore how AI can assist in building compliance into the business and what it means for the future of compliance programs. I also provide five key takeaways for compliance professionals on how to do so.

1. AI as a Co-Thinking Partner for Embedding Compliance into Workflows

One of the article’s most powerful insights is the concept of “co-thinking”; AI as a partner in structured dialogue rather than just a tool for quick answers. For compliance, this is transformative. Imagine using AI not simply to draft a policy, but to help you think through how that policy should be embedded in day-to-day operations.

For instance, when designing a gifts-and-entertainment approval process, AI can walk compliance through stakeholder perspectives: What does sales need? What would regulators expect? What friction will finance raise? By simulating these perspectives, AI helps compliance professionals design workflows that are practical and embedded, rather than abstract and detached.

This approach also makes compliance more proactive. Instead of reacting to risks after violations occur, AI-enabled co-thinking allows compliance to anticipate where policies may clash with business objectives and design operational solutions upfront. The compliance lesson is to treat AI as a structured dialogue partner to design compliance that lives inside the workflow, policies, and processes that are not just documented but operationalized.

2. Enhancing Stakeholder Engagement Through AI Simulations

Embedding compliance into business operations requires more than rules; it requires buy-in. The article highlights how AI can role-play different stakeholders, challenging managers to anticipate reactions. Compliance can use this capability to stress-test initiatives before rollout.

Suppose compliance is introducing a new due diligence system for third-party onboarding. AI can simulate how procurement might respond (“slows down vendor onboarding”), how business development might object (“hurts competitiveness”), and how regulators might evaluate (“strong demonstration of risk-based management”). This multi-stakeholder dialogue allows compliance teams to refine both process design and messaging before rollout.

The implication for compliance programs is clear: embedding compliance requires deep cultural alignment. AI makes it possible to test and rehearse that alignment at scale, reducing resistance and building smoother adoption. The compliance lesson is to use AI simulations to bring stakeholder voices into the design process, ensuring compliance is not bolted on but built with empathy for business realities.

3. AI-Assisted Root Cause Analysis Strengthens Business Integration

Compliance programs are expected to conduct root cause analysis after misconduct, but too often these reviews remain siloed. AI-enabled co-thinking helps expand root cause analysis into an exercise that strengthens business operations.

For example, when analyzing repeated travel and expense violations, AI can guide compliance through structured questions: Were training gaps to blame? Were approval workflows too weak? Were sales incentives misaligned? Then, critically, AI can help map remediation back into operations—tightening finance approvals, adjusting incentive structures, and embedding compliance flags directly into expense systems.

This is not about AI making the decision. It is about AI helping compliance think through operational integration of lessons learned. Instead of merely complying with regulations by writing a report that sits on a shelf, the outcome becomes operational adjustments inside business processes. The compliance lesson (or rather, perhaps implication) is that the DOJ expects compliance programs to prevent recurrence through systemic fixes. AI co-thinking can ensure those fixes are operational, not theoretical.

4. Scaling Compliance Culture and Mindset Shifts Across the Organization

The article notes how AI can be used to coach managers through mindset shifts, helping them reflect on new behaviors and practices. Compliance can use the same approach to embed cultural expectations directly into business teams. For example, AI can be configured as a compliance coach embedded in daily tools, guiding managers through ethical dilemmas, prompting reflection during approval requests, or reinforcing company values during project planning. Instead of compliance being external and episodic, it becomes internal and continuous.

This democratizes compliance development. A frontline manager in Asia can interact with AI that reinforces compliance culture in real time, rather than waiting for annual training or sporadic compliance visits. It also gives compliance leaders data on where employees are struggling, revealing cultural gaps that can be addressed systemically.

The implication is that embedding compliance is not just about systems but about mindset. AI can make culture-building a daily, distributed activity rather than a centralized, one-time effort.

5. Ensuring Human Judgment Remains Central in AI-Enabled Compliance

Finally, while AI can enhance problem-solving and integration, the article underscores that co-thinking only works when humans stay actively engaged. Compliance cannot abdicate responsibility to machines. This has profound implications for compliance programs. AI can help frame problems, simulate stakeholders, and propose operational fixes, but it cannot weigh reputational risk, interpret regulatory expectations, or balance competing global obligations. Those decisions require human judgment.

The key is balance: AI accelerates and deepens thinking, but compliance leaders must build governance frameworks to ensure outputs are reviewed, validated, and contextualized. Embedding compliance into business operations does not mean letting AI run the show; it means letting AI augment human reasoning so that compliance becomes more practical, strategic, and defensible.

The compliance lesson, based on both the DOJ’s FCPA Resource Guide and the 2024 ECCP, is clear that compliance must be risk-based, well-resourced, and continuously improved. AI helps compliance think through integration, but humans remain accountable for ensuring it meets regulatory standards and ethical expectations.

AI as a Pathway to Embedded Compliance

The future of compliance is embedded, not bolted on. DOJ expects it. Boards demand it. Employees need it. The challenge is figuring out how to make it real. AI offers compliance professionals a powerful new tool: not as an oracle, but as a co-thinker. By helping compliance frame problems, simulate stakeholders, strengthen root cause analysis, scale cultural coaching, and reinforce human judgment, AI can accelerate the shift from compliance as oversight to compliance as an integrated business practice.

The call to action is simple: use AI not just to make compliance faster, but to make compliance inseparable from business. That is how compliance earns trust, drives culture, and meets regulatory expectations in the age of AI.

Categories
Blog

Trust and Verify: How Compliance Can Harness AI Agents Safely

Ed. Note: This week, we present a week-long series on the use of GenAI in a best practices compliance program. Additionally, for each blog post, I have created a one-page checklist for each article that you can use in presentations or for easier reference. Email my EA Jaja at jaja@compliancepodcastnetwork.net for a complimentary copy.

When we think of “trust” in compliance, our minds usually go to whistleblowers, employees, or third parties. But increasingly, the question of trust must extend to a new category of actors: AI agents.

As Blair Levin and Larry Downes explain in their provocative Harvard Business Review piece, titled “Can AI Agents Be Trusted?“, AI agents are not just smarter chatbots. They are software systems that can collect data, make decisions, and even act autonomously based on rules and priorities. For compliance professionals, this changes the game. If AI agents can act on our behalf, can they also be trusted to uphold compliance principles?

The answer is yes, but only if we design and monitor them with the same rigor that we apply to employees, third parties, and business partners. Today, we look at five key takeaways from their article to guide compliance professionals in building AI agents into trustworthy components of their programs.

1. Trust Requires Oversight, Just as with Human Agents

The article makes a simple but powerful analogy: think of an AI agent the way you would think of an employee or contractor. Before delegating sensitive responsibilities, you conduct background checks, put controls in place, and possibly even require bonding. The same must hold for AI.

For compliance, this means creating oversight structures before deploying agents into live workflows. If your compliance AI assistant can monitor transactions for red flags, you must ensure that a human compliance officer reviews its outputs. If it can escalate potential whistleblower complaints, you must validate that escalation logic against regulatory requirements.

AI oversight also means testing for vulnerabilities. As Levin and Downes note, AI agents are susceptible to hacking, manipulation, and even misinformation. Compliance should require penetration testing of any agent integrated into company systems, just as IT would test network defenses.

Trust is never blind in compliance. It is built on verification, monitoring, and accountability. AI agents can and should be trusted, but only when they operate within a compliance framework that mirrors the controls we already use for human agents.

2. Recognize and Manage Bias and Conflicts of Interest

One of the major risks highlighted in the article is bias, whether introduced by marketers, advertisers, or flawed training data. Just as a conflicted employee can steer decisions for personal gain, an AI agent can be subtly manipulated to favor sponsors, advertisers, or even certain viewpoints.

For compliance professionals, this should raise alarms. Imagine an AI agent used for third-party due diligence. If biased data shapes its recommendations, you could end up onboarding a high-risk vendor while rejecting a low-risk one. Worse, if regulators discover that your system relied on biased algorithms, you’ll face serious questions about program effectiveness.

The solution is conflict-of-interest monitoring for AI. Just as employees must disclose outside interests, AI agents should be tested and audited for hidden preferences. Compliance should insist on transparency from vendors about training data sources and sponsorship arrangements. In some cases, contracts with AI providers may need explicit clauses guaranteeing independence from commercial influence.

Compliance has always been about spotting and mitigating conflicts. In the age of AI, that vigilance must extend to our digital agents. Only then can we claim that our programs are fair, impartial, and defensible.

3. Treat AI Agents as Fiduciaries of Compliance

Perhaps the most compelling insight from Levin and Downes is that AI agents should be treated as fiduciaries. Just as lawyers, trustees, and board members owe a heightened duty of care to their clients, AI agents entrusted with compliance responsibilities must be designed and governed under similar standards.

For compliance officers, this concept aligns directly with DOJ expectations. The Evaluation of Corporate Compliance Programs (2024 ECCP) emphasizes accountability, transparency, and independence. By treating AI agents as fiduciaries, compliance leaders can extend these principles to technology.

What does fiduciary duty look like in practice?

  • Obedience: AI must follow company policies and regulatory standards.
  • Loyalty: AI must prioritize the company’s compliance objectives over any hidden commercial interests.
  • Confidentiality: AI must protect sensitive compliance data from leaks or misuse.
  • Accountability: AI actions must be traceable, with clear logs and audit trails.

This fiduciary framing provides compliance professionals with a powerful tool. It not only reassures stakeholders that AI can be trusted, but it also sets a benchmark that regulators can understand and evaluate. In short, fiduciary AI is defensible AI.

4. Build Market and Insurance-Based Safeguards

The article notes that beyond regulation, market mechanisms such as insurance and independent oversight will be critical to ensuring AI trustworthiness. For compliance leaders, this presents both a risk management strategy and an opportunity.

Just as identity theft insurance evolved alongside online banking, AI liability insurance will likely become a standard corporate requirement. Compliance officers should begin engaging with insurers to explore coverage for AI-related risks, such as data leaks, wrongful denials of due diligence clearance, or biased decision-making.

Equally important are third-party oversight tools. The article envisions AI “credit bureaus” that could audit agent behavior, set decision thresholds, or freeze activity when risks escalate. For compliance, such independent monitoring could provide an external layer of assurance that your AI systems are behaving as intended.

The takeaway is clear: do not rely solely on internal controls. Pair them with market-based safeguards and external verification. Doing so not only strengthens trust in AI agents but also demonstrates to regulators that your program embraces both proactive and independent oversight.

5. Design for Data Security and Local Control

Finally, Levin and Downes stress the importance of keeping decisions local; that is, ensuring sensitive data stays on company-controlled devices and servers, rather than in external clouds. For compliance professionals, this echoes a familiar principle: control the data, control the risk.

Agentic AI, by definition, processes vast amounts of sensitive information. If compliance agents are reviewing hotline reports, transaction monitoring data, or due diligence files, any data leakage could be catastrophic. That’s why strong encryption, local processing, and secure enclaves are essential.

Compliance officers should demand that AI vendors support:

  • On-device or private cloud processing for sensitive tasks.
  • Encryption of all data in transit and at rest.
  • Independent verification of security claims by external auditors.
  • Full disclosure of sponsorships, promotions, and paid influences.

By designing AI agents with local control and transparency, compliance teams can build systems that are both effective and trustworthy. Data security is not just an IT concern; it is a compliance imperative.

Trust, But Never Blindly

AI agents hold immense potential for compliance programs. They can streamline monitoring, accelerate due diligence, and support real-time risk management. But as Levin and Downes remind us, they must also be carefully governed to prevent bias, manipulation, and misuse.

For compliance leaders, the path forward is to treat AI like any other agent (or channel your inner Ronald Reagan: trust, but verify. With oversight, fiduciary framing, market safeguards, and strong data controls, AI can become a trusted partner in compliance—one that strengthens, rather than weakens, the ethical fabric of the organization.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – AI and Recruiting

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, we aim to provide bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Among the numerous applications of AI, its deployment in recruitment is rapidly becoming one of the most significant and controversial topics compliance professionals need to navigate.

Categories
Blog

AI in Recruitment: Compliance Challenges and Opportunities

Compliance officers increasingly deal with emerging technologies in today’s business environment, and artificial intelligence (AI) is undeniably at the forefront. Among the numerous applications of AI, its deployment in recruitment is rapidly becoming one of the most significant and controversial topics compliance professionals need to navigate. The reason for the spotlight is clear. AI-driven recruitment tools promise substantial efficiency gains, automating tedious processes such as CV screening, initial interviews, and candidate ranking. However, this automation does not come without significant compliance and ethical pitfalls. The implications are vast, involving transparency, fairness, accuracy, and potential biases, each presenting substantial regulatory and reputational risks.

Jonathan Armstrong and I recently explored the issues surrounding the use of AI in corporate recruiting in a recent episode of Life with GDPR. This blog post is based on our discussion. For more information, I invite you to check out the full episode.

The Compliance Landscape: EU, UK, and US Perspectives

The regulatory perspective surrounding AI in recruitment varies significantly, but a general compliance framework exists through the General Data Protection Regulation (GDPR) in Europe. GDPR lays foundational principles such as transparency, fairness, accuracy, and accountability, directly impacting how AI systems must operate in talent acquisition. In the United States, state-level regulations addressing automated recruitment systems are also beginning, reflecting a broader global trend toward stronger regulatory scrutiny of these technologies.

Armstrong highlighted that enforcement is becoming more pronounced. Spain, for example, has seen regulatory actions requiring companies benefiting from AI-driven processes to articulate the basis for automated decisions clearly. The UK’s regulator explicitly notes recruitment as an area under active scrutiny, emphasizing the significance compliance professionals must attach to these practices.

Transparency and Fairness: Essential Compliance Considerations

Transparency in AI systems, particularly in recruitment, is more than a regulatory requirement; it is an ethical imperative. Under GDPR, a candidate who is rejected by an automated system is entitled to understand the basis for that decision. Simply stating “the algorithm decided” will not suffice. Organizations must be prepared to provide candidates with clear, intelligible explanations about how decisions were reached, which inherently involves unpacking the often opaque nature of AI processes.

The challenge is compounded by machine learning technologies, where decision pathways evolve dynamically. Unlike rule-based systems, the internal workings of machine learning-driven AI can be complex, making it difficult, even impossible in some instances, for companies to understand or explain their decision-making criteria fully. This opacity can lead to bias, discrimination, and unfair treatment accusations.

Bias and Discrimination: A Risk Too Real

The specter of bias and discrimination looms large with AI recruitment tools. Systems have been reported to inadvertently penalize candidates for factors unrelated to their competencies or skills, such as internet connection quality during virtual interviews. For instance, a candidate could be unfairly penalized if their internet connectivity is unreliable, leading AI systems to interpret technical delays as hesitancy or lack of confidence wrongly. This subtle discrimination disproportionately affects individuals from lower socioeconomic backgrounds, exacerbating existing inequalities.

Moreover, disturbing parallels can be drawn from AI decision-making in areas such as bail applications in the US, where biases based on ethnicity or racial profiling have resulted in unjust outcomes. The risk of similar biases entering recruitment processes cannot be underestimated, underscoring the need for vigilant compliance oversight.

Proactive Compliance: Essential Steps for Mitigation

Given these concerns, compliance officers cannot afford to adopt a passive stance. The issue of AI in recruitment is far too consequential to be left solely in the hands of HR departments or recruitment agencies. Compliance teams must proactively engage to ensure that all AI applications used in their organizations or by their third-party vendors are compliant, transparent, and fair.

Armstrong proposed the following framework compliance professionals can adopt to manage the risks of using AI in their recruiting process.

  1. Vet AI Providers Rigorously
  2. Not all AI vendors operate equally. Compliance professionals should avoid opaque, “black-box” solutions and favor providers willing and able to demonstrate transparent practices.
  3. Comprehensive Due Diligence
  4. Conduct meticulous due diligence on AI recruitment vendors. This includes verifying their ability to comply with GDPR transparency and fairness principles and their willingness to cooperate fully with subject access requests.
  5. Contractual Protections
  6. Ensure comprehensive contracts with AI recruitment providers that allocate responsibilities clearly and provide sufficient recourse in case of litigation or regulatory action. The provider must be incentivized to maintain stringent compliance standards.
  7. Transparency Obligations
  8. Communicate to candidates how AI systems will process their data. The GDPR demands openness; hence, organizations must disclose the use of AI tools, how decisions are made, and the implications for candidates.
  9. Robust Data Subject Request Procedures
  10. Compliance teams must have effective, responsive mechanisms for handling data subject requests swiftly. Candidates dissatisfied with recruitment decisions frequently resort to GDPR subject access requests, creating significant administrative and compliance burdens.
  11. Regular Auditing and Checks
  12. Establish ongoing monitoring and periodic audits to continually assess AI recruitment tools. This process helps ensure that the systems adhere to compliance principles and remain free from bias or unethical decision-making patterns.
  13. Educate and Engage Internally
  14. Compliance professionals should engage closely with internal stakeholders, educating HR teams and recruiters on the implications of AI and compliance expectations. Internal awareness significantly mitigates the risk of non-compliance and encourages proactive risk management.

Looking Ahead: Staying Vigilant and Informed

The compliance landscape for AI in recruitment is undoubtedly complex, and the stakes are high. As Armstrong emphasizes, regulatory scrutiny is set to intensify, making it imperative for compliance teams to stay ahead of developments. Vigilance, proactive engagement, and informed awareness are key to successfully navigating these challenges.

This field remains ripe for academic and regulatory inquiry. More comprehensive research and analysis into AI’s implications on recruitment fairness, bias, and effectiveness would benefit organizations and compliance practitioners. Compliance professionals should watch developments closely and contribute actively to discussions, research, and policy development in this dynamic area.

AI in recruitment offers immense promise and substantial compliance challenges. Proactively addressing these issues ensures regulatory adherence and upholds corporate ethical standards, which are crucial in maintaining brand integrity and public trust. Compliance officers, thus, play a pivotal role in guiding their organizations through this rapidly evolving technological frontier.

Categories
Compliance Into the Weeds

Compliance into the Weeds: Unsexy Keys to Data Analytics for Compliance Programs

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into a compliance-related topic, literally going into the weeds to explore a subject more fully. Are you looking for some hard-hitting insights on compliance? Look no further than Compliance into the Weeds! In this Compliance into the Weeds episode, Tom Fox and Matt Kelly take a deep dive into the critical yet often overlooked aspects of data analytics.

They discuss Matt’s recent blog post on the ‘Unsexy Keys to Data Analytics,’ emphasizing the importance of foundational infrastructure over flashy visualizations. The conversation covers the need for robust data validation, the cooperation between compliance, business units, and IT departments, and the challenges faced by compliance officers in smaller companies. Highlights include real-world examples, the role of data governance, and how to align compliance risk management with corporate objectives amid ever-changing business landscapes.

Key highlights:

  • The Importance of Data Infrastructure
  • Compliance vs. Enterprise Data Analytics
  • Collaboration Across Departments
  • Data Governance and Change Management
  • Aligning Compliance with Corporate Risk Management

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

Compliance into the Weeds was recently honored as one of the Top 25 Regulatory Compliance Podcast.

Categories
Blog

The Role of Compliance in Auditing AI

As compliance professionals, our roles evolve constantly, shaped by new technologies and emerging risks. One of the most significant developments in recent years has been the rapid growth of artificial intelligence (AI) and machine learning systems in the corporate environment. The 2024 Evaluation of Corporate Compliance Programs (2024 ECCP), under the Management of Emerging Risks to Ensure Compliance with Applicable Law section, asked several key questions.

  • What is the company’s approach to governance regarding the use of new technologies, such as AI, in its commercial business and compliance program?
  • How is the company curbing any potential adverse or unintended consequences resulting from using technologies, both in its commercial business and its compliance program?
  • How is the company mitigating the potential for deliberate or reckless misuse of technologies, including by company insiders?
  • To the extent that the company uses AI and similar technologies in its business or as part of its compliance program, are controls in place to monitor and ensure its trustworthiness, reliability, and use in compliance with applicable law and the company’s code of conduct?
  • Do controls exist to ensure the technology is used only for its intended purposes?
  • What baseline of human decision-making is used to assess AI?
  • How is accountability over the use of AI monitored and enforced?

One key tool for answering many of these questions is auditing. In his recent article in the Harvard Business Review, What Leaders Need to Know About Auditing AI, author Luca Belli outlines crucial insights that business leaders must understand about auditing AI. I have adapted his thoughts for a Chief Compliance Officer and compliance professional.

While audits are becoming a core feature of working with AI, they do not have a predetermined process that follows a straight line; rather, they are a web of different decisions, both from the business and the technical side. Specifically, audits often face four core challenges: 1) they do not follow a straight line, 2) data governance is messy, 3) they require internal trust, and 4) they focus on the past. Leaders can take steps to help audits succeed. Compliance professionals can help instill the right culture and incentives and help design the audit. During the audit, they can shape the process and remove red tape.

AI is no longer confined to back-end analytics. It has stepped confidently into customer-facing roles, making decisions in critical areas such as finance, healthcare, and housing. With such reach and influence, AI poses significant ethical, reputational, and legal risks if left unchecked. Audits of AI systems, therefore, have become a cornerstone of modern compliance frameworks. Policymakers worldwide, including through the EU’s Digital Services Act and New York City’s AI bias law, are mandating external audits of AI systems. Even where not mandated, businesses voluntarily engage in audits to manage risk, mitigate potential crises, and anticipate regulatory developments.

However, auditing of AI is not straightforward. Compliance professionals must understand four fundamental challenges inherent in AI audits.

1. Non-linear Audit Processes

AI audits rarely follow a straight, predictable path. Instead, they often resemble a “random walk,” as auditors must continually adjust their focus based on emerging data and shifting business needs. Consider an audit to detect racial bias in decision-making algorithms where direct data on race is unavailable. Auditors may pivot to proxy measures like zip codes to approximate racial data. This approach, while practical, introduces discrepancies and limitations that must be carefully managed and transparently documented.

2. Complex Data Governance

Effective auditing relies heavily on data governance practices, yet data management often resembles an “old building” layered with historical inefficiencies rather than a clean, structured system. Many organizations struggle to locate and interpret data due to outdated documentation or employee turnover. Compliance teams must actively collaborate with technical teams to ensure data accuracy and completeness. As Belli suggests, robust internal documentation and dedicated data custodians can significantly ease this challenge.

3. Building Internal Trust

Audits can strain internal team dynamics, particularly if audit results lead to perceived criticisms of operational decisions. Compliance professionals must proactively foster a culture of trust, reinforcing that audits are not punitive but integral to operational excellence. As Belli notes, incentives should align accordingly: supporting audits should positively influence personal and professional evaluations, signaling organizational value in transparency and continuous improvement.

4. Historical Focus and Technical Limitations

Most audits evaluate past performance, and evolving AI systems and datasets pose challenges in replicating historical conditions. A user deleting their profile data or changes in system algorithms can complicate audits significantly. Compliance professionals must advocate for real-time monitoring or, at minimum, detailed record-keeping, ensuring auditors have sufficient context to interpret their findings and recommendations accurately.

Given these complexities, how can corporate compliance officers effectively lead their organizations through AI audits? Belli provides several practical steps:

  • Proactive Preparation: Companies should not wait for external mandates to build auditing capabilities. By establishing internal audit teams or clearly defined points of contact within existing teams, organizations can swiftly respond to audit needs while minimizing operational disruption.
  • Cultural Alignment: Corporate culture profoundly impacts audit effectiveness. Compliance professionals must champion transparency and accountability at the highest organizational levels, ensuring that audits are critical to long-term business success rather than occasional inconveniences.
  • Strategic Audit Design: Choosing between external auditors and internal audit teams requires careful consideration of organizational dynamics. Internal teams offer in-depth institutional knowledge, while external auditors provide objective perspectives without internal friction. Belli suggests a hybrid model, often ideal, balancing centralized expertise with distributed operational familiarity.
  • Leadership Engagement: Active, informed involvement by senior leadership during audits can clarify organizational priorities and remove operational roadblocks. Leaders should regularly engage with technical teams to understand key decisions, encourage thorough documentation, and ensure audit findings align clearly with broader business objectives.

The author underscores the CCO’s crucial role in navigating the nuanced landscape of AI auditing. As technology’s reach expands, compliance teams must proactively address these emerging complexities, continually adapting their oversight frameworks to meet the dynamic challenges presented by AI systems. By fostering robust internal collaboration, aligning incentives, and strategically preparing audit infrastructure, compliance professionals not only mitigate risks but also enable their organizations to harness AI’s transformative potential responsibly and ethically.

Categories
Compliance Into the Weeds

Compliance into the Weeds: The DOJ in Crisis

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into a compliance-related topic, literally going into the weeds to explore a subject more fully. Are you looking for some hard-hitting insights on compliance? Look no further than Compliance into the Weeds! In this Compliance into the Weeds episode, Tom Fox and Matt Kelly review the recent astonishing developments at the Justice Department involving the indictment and subsequent attempted dismissal of charges against New York City Mayor Eric Adams.

Tom and Matt explore the implications for corporate compliance professionals and the broader message this dysfunction sends about ethics and the role of compliance programs under the current administration. They consider the possible repercussions for future corporate enforcement, drawing important parallels between the Justice Department’s actions and the expectations for corporate compliance. They emphasize the necessity of disentailing the ethical dysfunction at the department from the practical guidelines for compliance programs. The episode critically analyzes how political maneuvers affect the justice system and corporate compliance standards.

Key highlights:

  • The Eric Adams Indictment
  • Resignations and Internal Conflict
  • Separating DOJ Integrity from Compliance Guidance
  • Tone at the Top vs. Mood at the Middle
  • Future of Compliance Guidelines

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

Compliance into the Weeds was recently honored as one of the Top 25 Regulatory Compliance Podcast.