Categories
Compliance Into the Weeds

Compliance into the Weeds: Mapping and Managing AI Agents’ Compliance Risk

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into compliance-related topics, literally going into the weeds to explore them more fully. Looking for some hard-hitting insights on compliance? Look no further than Compliance into the Weeds! In this special episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss a Darrow AI report on whether leading LLMs can build privacy-sensitive websites while recognizing compliance obligations.

Darrow had seven “frontier” models build three hypothetical sites involving personal data (pediatric lab results, credit scores, and mental health services) and scored them against a privacy/compliance checklist. With no compliance prompting, models averaged about 28/100; with generic privacy prompts, about 63.5; and with extensive documentation and technical specifications, about 88.6 (the top model around 95), with none reaching 100. They highlight “ghost controls,” where front-end compliance features (e.g., opt-out buttons) lack back-end functionality. The conversation stresses that prompting quality, technical specifications, and clear human oversight are essential, especially amid layoffs and “vibe coding,” and warns that GDPR/CCPA risks scale with AI speed. They note insurers requested the research and may push governance requirements.


Key highlights:

  • Darrow Study Setup
  • Workplace Oversight Risks
  • Ghost Controls Explained
  • Governance at Scale
  • Beyond Websites to Projects
  • Insurance Pressure Coming

Resources:

Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds, was recently named one of the Top 25 Regulatory Compliance Podcasts, Top 10 Business Law Podcasts, and Top 12 Risk Management Podcasts. Compliance into the Weeds has been awarded a Davey, Communicator, and W3 Award, all for podcast excellence.

Categories
AI Today in 5

AI Today in 5: November 6, 2026, The Whither Data Centers Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Using AI-powered compliance to curb greenwashing. (ESGDive)
  2. Governing AI by improving compliance. (CIO)
  3. How much will AI compliance cost Mexican businesses? (MexicoBusinessNews)
  4. OpenAI drops its NDA requirements. (TechInsider)
  5. What does the election mean for data center construction? (Reuters)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Blog

Anthropic’s IPO: 5 Lessons for Corporate Compliance Professionals

The most important question arising from Anthropic’s IPO disclosures is what compliance professionals should do with the risks they reveal. Identifying exposure begins the analysis. The business challenge is building a program that can manage that exposure.

In Parts I and II, I examined ten corporate compliance risks, ranging from AI safety and regulatory enforcement to third-party dependencies, financial reporting, and board oversight. In this blog post, I want to turn those risks into five practical lessons CCOs, general counsel, directors, and business leaders can use today to manage AI compliance.

Those lessons extend beyond AI developers. A manufacturer using AI in procurement, a financial services company deploying customer-facing tools, or a professional services firm connecting AI to confidential records must understand how those uses affect its control environment. Purchasing the technology does not eliminate the need to govern its use.

The central issue is accountability. Who owns the risk? Which controls address it? How does management know those controls work? What happens when they fail? These are familiar compliance questions. AI makes the answers more urgent.

1. AI governance must become part of enterprise compliance.

A standalone AI ethics policy cannot carry the weight of an enterprise compliance program. Principles require operational decisions: what uses are permitted, what information systems may access, what actions require approval, and who can suspend deployment. Start with an inventory of AI uses across the business. Include purchased applications, internally developed systems, employee experimentation, and AI features embedded in existing software. For each use, identify the business owner, data involved, decisions supported, and authority granted. A drafting assistant and an agent authorized to initiate payments require different controls.

Then connect the inventory to the enterprise risk assessment. Classify uses according to potential harm, legal exposure, sensitivity of information, and difficulty of reversing an action. Assign control owners and specify when reassessment is required. A new data connection or expanded permission can change the risk without changing the product name. Governance also requires decision rights. Compliance, legal, security, technology, and business teams should understand their respective responsibilities. Disagreements about deployment need a documented escalation route, including authority to delay implementation when critical safeguards remain unresolved.

Frameworks such as the NIST AI Risk Management Framework and ISO/IEC 42001 can help organize this work. Their practical value depends on whether the company translates its chosen approach into operating responsibilities and verifiable controls.

The CCO question: Can we identify the accountable owner and supporting controls for every material AI use?

2. Traditional compliance risks remain fundamental

AI changes how misconduct can occur and how quickly its effects can spread. Established compliance disciplines still provide the starting point for identifying the exposure. Consider a hypothetical procurement agent that recommends vendors and prepares payment instructions. Its technical performance may appear strong while its workflow bypasses conflict disclosures, restricted-party screening, or approval requirements. Faster processing can amplify a weak control environment.

The appropriate response is to examine the underlying business process. Map where an AI system receives information, makes recommendations, changes records, or initiates actions. Identify the approvals, segregation of duties, documentation, and monitoring that must remain effective at each stage. Determine whether automation has created a new route around an existing safeguard. Anti-corruption controls illustrate the point. An intermediary recommended by an AI tool still requires appropriate diligence. A model-generated payment description still requires verification. A confident recommendation cannot substitute for evidence about ownership, services performed, compensation, or government connections.

Training should reflect these practical choices. Employees need examples showing when to question an output, obtain approval, preserve records, or report a concern. Generic instructions to use AI responsibly provide little help when a system recommends a questionable transaction under commercial pressure. The CCO should also examine incentives. Employees measured solely on speed or volume may have little reason to challenge an automated recommendation. Managers must support escalation when verification delays a transaction.

The CCO question: Where could AI bypass, weaken, or obscure a control we already depend upon?

3. Third-party risk management must include technology dependencies

Traditional third-party programs often focus on agents, distributors, consultants, and other commercial intermediaries. AI requires equally careful attention to model providers, cloud infrastructure, data suppliers, integration partners, and subcontractors supporting critical services. The first task is dependency mapping. Determine which providers support essential workflows, what information they receive, and whether multiple applications depend on the same underlying service. Several vendor contracts may conceal a single point of operational failure.

Due diligence should follow the actual use. A tool that processes public information raises different concerns than a service that accesses customer records or executes transactions. Ask how information is retained, whether it may be used for training, how access is controlled, and what changes the provider can make without customer approval. Contracts should support the controls the company needs. Depending on risk, that may include incident notification, restrictions on data use, information about subcontractors, access to assurance evidence, and notice of material service changes. Legal and procurement teams should identify gaps before the business becomes dependent on the service.

Monitoring must continue after onboarding. Provider updates can affect performance, permissions, or data handling. Assign responsibility for reviewing material changes and deciding when testing must be repeated. Finally, test the exit plan. Can the business recover its information, revoke access, and maintain essential operations if the relationship ends? A contractual termination right offers limited protection when no workable alternative exists.

The CCO question: Which technology dependencies could prevent us from meeting critical obligations, and what is our tested response?

4. Compliance must be embedded in product development

Compliance review is most useful while business and technical choices can still be changed. Waiting until launch makes it harder to address weaknesses in data access, system permissions, customer communications, or monitoring. The Evaluation of Corporate Compliance Programs (ECCP) expressly addresses how companies assess and manage risks associated with AI and other emerging technologies. That provides an enforcement-informed reason to integrate AI risk into the broader compliance program.

For the CCO, the practical response is a development process with review points proportionate to risk. Assess the intended use before development, review controls during testing, document approval before deployment, and monitor behavior afterward. Material changes should trigger renewed review. Testing should examine foreseeable misuse and control failure alongside normal performance. Can a user induce unauthorized disclosure? Can an agent exceed its permissions? Does the system preserve records needed to investigate an incident? Can a human reviewer meaningfully intervene?

A nominal human approval step deserves particular scrutiny. If reviewers lack time, information, or authority to challenge recommendations, the safeguard may offer little protection. Test how people actually review realistic workloads. Compliance also needs access to relevant information and sufficient technical support to assess the results. Establish channels for employees to report unexpected behavior without first proving a technical defect. Investigations should connect incidents to root causes and corrective action.

The CCO question: At what development decisions can compliance require changes, and what evidence supports approval?

5. Boards must demand evidence of effectiveness

Board oversight depends on information that enables challenge. Counts of policies issued, training completed, and committee meetings held describe activity. Directors also need evidence about whether material risks are being controlled. Management reporting should identify significant AI uses, unresolved control weaknesses, incidents, overdue remediation, and decisions to accept residual risk. Explain what changed since the previous report and whether the change affects the company’s ability to operate within approved limits.

Metrics need context. An increase in reported incidents may reflect improved detection rather than worsening performance. A low incident count may conceal weak monitoring. Directors should ask how management interprets the numbers and what independent testing supports that interpretation. Reports should also surface disagreements and exceptions. If management approved deployment despite an unresolved compliance concern, the board needs to understand the decision, compensating controls, accountable executive, and deadline for reconsideration. Commercial significance should increase the quality of scrutiny.

Directors do not need to reproduce technical testing. They need reliable reporting, access to appropriate expertise, and a clear process for following material concerns through remediation. Meeting records should capture substantive questions, commitments, and follow-up. The board question: What evidence would cause management to restrict or suspend an AI deployment, and has that response been tested? The larger lesson: turn commitments into operating discipline

Anthropic’s disclosures bring emerging technology risk, traditional compliance obligations, and governance expectations into one discussion. The practical response is an integrated program that connects business decisions to accountable owners, tested controls, and timely escalation.

Begin with three actions: identify the most consequential AI uses, test whether existing controls cover them, and present unresolved gaps to the appropriate decision-makers. Assign deadlines and verify remediation. Give business owners clear responsibility for explaining remaining gaps and reporting progress until corrective work is complete.

For CCOs and boards, measure progress by whether the organization can demonstrate that its controls work as capabilities, permissions, and business uses change. That is how AI governance becomes an effective business discipline. The following is my qualitative assessment, not a quantitative risk score disclosed by Anthropic. The rankings reflect the combined importance of regulatory exposure, potential harm, and control complexity.

Rank Corporate compliance risk Priority Primary accountability
1 AI safety and autonomy Critical Chief AI/Safety Officer, CCO
2 Regulatory enforcement Critical General Counsel, CCO
3 Privacy and cybersecurity Critical CISO, Privacy Officer
4 Intellectual property Critical General Counsel
5 Export controls and sanctions Critical Trade Compliance, CCO
6 Third-party risk High Procurement, CCO
7 Anti-bribery and corruption High CCO
8 Financial reporting and disclosure High CFO, Audit Committee
9 Corporate governance High Board, General Counsel
10 Consumer protection High Legal, Product Compliance

Categories
Innovation in Compliance

Innovation in Compliance: Pamela Gupta on Closing the AI Governance Implementation Gap

Innovation comes in many areas, and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovators, thinkers, and creators on the award-winning Innovation in Compliance podcast. In this episode, host Tom welcomes Pamela Gupta, the author of De-Risking AI Adoption: The AI Trust Layer: An AI Governance Playbook.

Pamela Gupta is the founder of Trusted AI™ and an author. She and Tom discuss closing the AI governance implementation gap between high-level frameworks (e.g., NIST AI RMF, ISO 42001) and use-case execution under rapid AI rollout pressure. Gupta argues organizations struggle to translate principles into actionable, risk-based decisions across many stakeholders (security, privacy, legal, audit, business, IT, and data science), leading to either unmanaged risk or stalled innovation. She emphasizes AI-specific risks such as bias, transparency, explainability, and accountability, citing Humana’s nH Predict claims system (alleged bias; 90% reversals), Amazon’s scrapped hiring model, and Air Canada’s chatbot ruling. Gupta outlines her AI TIPS framework (eight pillars, ~80 controls) and contends AI governance can accelerate adoption by defining intake, evidence, and decision processes, even as agentic AI raises risk and uncertainty.

Key highlights:

  • AI Governance Gap
  • Assessing AI Risk
  • Bias and Ethics Ownership
  • Humana Case Study
  • AI TIPS Framework
  • Governance as Accelerator

Resources:

Pamela Gupta on LinkedIn

De-Risking AI Adoption: The AI Trust Layer: An AI Governance Playbook

Website: TrustedAI.AI

Podcast: Trustworthy AI: De-Risk Business Adoption of AI

Trusted AI Feed: TrustedAI.AI/feed/

X/Twitter: @OutsecureCom

LinkedIn: Trusted AI™

YouTube: @trustedai

 Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Blog

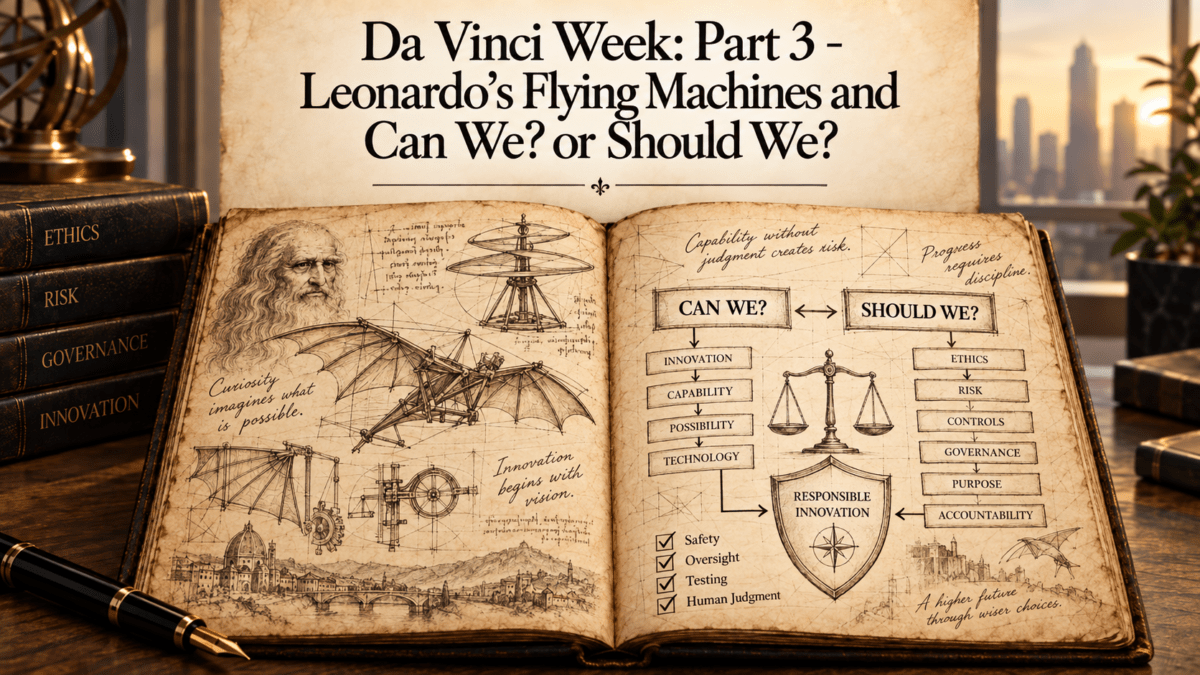
Da Vinci Week: Part 3 – Leonardo’s Flying Machines and “Can We?” or “Should We?”

In the first two posts in the Leonardo Compliance Framework, the Mona Lisa gave us Refine, the principle that an effective compliance program improves as the organization learns from experience. Leonardo’s anatomical studies gave us Investigate, the discipline of looking beneath misconduct to understand root causes, control failures, incentives, management decisions, and the organizational systems that produced the outcome. The third principle is Innovate.

For that lesson, we turn to Leonardo’s studies of flight and his designs for flying machines. Leonardo examined birds, air movement, wings, and mechanical systems as he considered whether technology could allow human beings to fly. Many of his concepts were far beyond the practical capabilities of his time, but they demonstrate an important characteristic of Leonardo’s work: he imagined capabilities that did not yet exist and then studied the systems necessary to make them possible.

For corporate compliance professionals in 2026, the analogy to artificial intelligence is particularly useful. AI is expanding what companies can automate, analyze, predict, generate, and increasingly act upon. Organizations are moving beyond using generative AI to draft documents and summarize information. AI systems are becoming embedded in business processes, interacting with corporate data, supporting consequential decisions, communicating with customers, evaluating third parties, and, through increasingly agentic capabilities, taking actions that previously required human intervention.

The compliance challenge is not whether companies should innovate. They will. The challenge is establishing governance that lets innovation create business value without creating unmanaged legal, ethical, operational, or compliance risk.

AI Governance Is Enterprise Governance

Compliance professionals have sometimes approached emerging technology as primarily the responsibility of IT, Cybersecurity, Data Privacy, or Legal. That division becomes increasingly difficult with AI because these systems can influence many of the activities a corporate compliance team already oversees. Indeed, the Evaluation of Corporate Compliance Programs (ECCP) anticipates these very concepts in its 2024 edition.

AI may assist with third-party due diligence, contract review, procurement, transaction analysis, hiring, customer communications, investigations, fraud detection, marketing, or pricing. Each application creates a different risk profile. A due diligence system may generate inaccurate information about a business partner. An investigation tool may expose privileged or confidential information. A sales application may generate communications inconsistent with company policies. An agent connected to corporate systems may take actions that historically required human approval.

The ECCP asks the following:

  • How does the company assess the potential impact of new technologies, such as artificial intelligence (AI), on its ability to comply with criminal laws?
  • Is management of risks related to the use of AI and other new technologies integrated into broader enterprise risk management (ERM) strategies?
  • What is the company’s approach to governance regarding the use of new technologies such as AI in its commercial business and in its compliance program?
  • How is the company curbing any potential negative or unintended consequences resulting from the use of technologies, both in its commercial business and in its compliance program? 

Visibility and Risk Should Drive the Control Environment

By 2026, asking whether a company uses AI provides little useful information. Management needs to understand how AI is being used and what authority particular systems possess. A tool that summarizes a public document presents a very different risk profile from a system that influences hiring, approves a third party, communicates with customers, accesses confidential information, initiates a transaction, changes corporate records, or takes actions across interconnected systems.

An AI inventory should therefore identify meaningful use cases, including the business owner, intended purpose, relevant data, third parties involved, decisions influenced by the technology, degree of autonomy, and applicable controls. The objective is not simply to count tools. It is to give management sufficient visibility to identify where material risk exists.

That visibility should support risk classification. Not every AI application requires the same level of governance. Classification should consider the system’s purpose, data sensitivity, potential consequences of error, degree of autonomy, affected populations, ability to review or reverse decisions, and applicable legal or regulatory requirements.

This is familiar territory for compliance professionals. Risk-based programs have long applied different levels of scrutiny to third parties, transactions, investigations, and markets. AI should follow the same principle. Higher-risk systems should receive greater review, stronger controls, and more rigorous monitoring.

Human Oversight Must Preserve Accountability

“Human in the loop” has become common language in AI governance, but a human’s presence alone does not create an effective control. Meaningful oversight requires defined responsibilities, appropriate expertise, sufficient capacity to review relevant outputs, and authority to challenge or override the system.

If one employee is nominally responsible for reviewing thousands of AI-generated recommendations each day, human oversight may exist on paper but not function in practice. The same problem arises when employees routinely accept recommendations because they assume the technology is more reliable than their own judgment.

The control should therefore define the reviewer’s responsibilities, the circumstances requiring additional scrutiny, the authority to reject recommendations, and how to handle material overrides or recurring disagreements between the system and human decision-makers. Most importantly, technology should not create an accountability vacuum. If an AI system contributes to a compliance failure, the organization should still be able to identify the business process owner, who approved the use case, who monitored it, and who had authority to intervene.

This becomes increasingly important with agentic systems. Traditional corporate controls generally assume identifiable human actors approve payments, create vendors, review contracts, or authorize higher-risk third parties. When technology performs some of those activities, the organization has effectively delegated authority to a system. The control environment must reflect that delegation while retaining human and organizational accountability for the outcome.

Third-Party AI and Data Risk

Many companies will obtain significant AI capabilities from external vendors rather than develop them internally. Using a vendor does not transfer accountability for the resulting compliance risk. Traditional third-party risk management principles remain relevant. The company should understand the service provided, the information the vendor receives, how data are used and retained, which subcontractors are involved, how incidents are managed, and what contractual rights the company has to obtain information, require remediation, audit, or terminate the relationship.

AI adds a dynamic element because models, features, and business uses can change after initial approval. Monitoring should therefore identify material changes in functionality, data use, vendor practices, or business application that could alter the original risk assessment.

Data governance is equally important. Companies need clear rules regarding which AI systems may access confidential business information, personal data, investigation materials, privileged communications, customer information, trade secrets, source code, and other sensitive information. As enterprise AI systems increasingly operate on internal data, blanket prohibitions will often give way to more precise governance defining approved systems, permissible data, access controls, retention, deletion, and accountability.

These issues require coordination across Compliance, Legal, Privacy, Cybersecurity, IT, Records Management, and the business. Effective governance depends upon clear responsibilities rather than overlapping or fragmented ownership.

Test Before Deployment and Monitor Afterward

Leonardo’s flying machines provide another useful innovation lesson. Test a design before you trust it with a critical task. AI testing should match the risk. Before deployment, the company should understand whether the system performs as intended, where its limitations lie, how it responds to unusual circumstances, whether users can manipulate it, and whether inaccurate or inconsistent outputs could create material consequences. Testing at implementation is not enough. Business conditions change, vendors update models, employees develop new uses, and system capabilities expand. An application that operated within acceptable parameters when approved may later present a different risk profile.

Higher-risk systems therefore require post-deployment monitoring that can identify performance issues, material changes, incidents, and circumstances requiring reassessment. Management should also establish when a system should be modified, restricted, or suspended.

This lifecycle approach connects Innovate to the next Leonardo principle, Monitor. Responsible innovation is not a one-time approval. Governance should continue throughout the period the organization relies on the technology.

Using NIST and ISO as Governance Architecture

Compliance professionals do not need to invent an AI governance structure from scratch. The NIST AI Risk Management Framework provides a useful approach to governance, mapping, measuring, and managing AI risk, while ISO/IEC 42001 offers a management-system perspective built around responsibilities, processes, documentation, monitoring, and continuous improvement.

For the CCO, the value lies in providing governance architecture, not another checklist. The relevant measure is not whether a company can say it follows NIST or ISO. It is whether its governance system addresses the actual risks created by its AI applications and whether the resulting controls work in practice. Frameworks provide structure. Management remains responsible for operating the system.

Compliance Should Enable Responsible Innovation

The CCO should avoid two extremes: allowing enthusiasm for AI to outrun governance or creating an approval structure so burdensome that employees circumvent it. A better model is responsible innovation. Compliance can help create clear pathways for lower-risk experimentation while ensuring that higher-risk applications receive appropriate scrutiny. Employees should understand what uses are permitted, which require approval, what categories of information may be used, and when escalation is necessary.

This approach also creates opportunities for a corporate compliance program. AI may improve due diligence, transaction monitoring, investigations, risk assessment, training, and data analysis. The compliance function should be willing to explore those capabilities under the same risk-based governance it expects the business to follow.

A CCO’s contribution should not be measured by how much innovation Compliance prevents. It should be measured in part by whether Compliance helps the enterprise capture value while maintaining appropriate accountability and control.

Before Leaving the Ground

Leonardo’s flying-machine studies represent the willingness to imagine possibilities beyond current practice. The modern compliance lesson is to combine that willingness with disciplined governance. For the CCO, Innovate means helping the enterprise pursue new capabilities through a risk-based system that provides visibility, assigns ownership, preserves meaningful human accountability, tests higher-risk applications, and monitors them as technology and business use evolve. The objective is neither unrestricted adoption nor blanket prohibition. It is responsible innovation that can produce sustainable business value.

From Innovation to Monitoring

Responsible innovation does not end when technology is approved and deployed. The organization must determine whether systems continue to operate as intended as data, users, vendors, business conditions, and risks change. That brings us to the fourth Leonardo principle: Monitor.

In Blog Post Four, The Last Supper and the Danger of Deterioration, we will use Leonardo’s experimental masterpiece to examine the difference between implementing a control and demonstrating that it remains effective. The discussion will focus on control testing, continuous monitoring, compliance analytics, ownership, remediation, AI monitoring, and the board’s role in evaluating evidence of continuing program effectiveness.

Categories
AI Today in 5

AI Today in 5: September 16, 2026, The False Choice Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. The difference between AI pilots and AI. (Federal News Network)
  2. AI for Supply chain compliance. (ESG News)
  3. AI governance is pressing in healthcare. (Healthcare IT News)
  4. Enterprise AI enters a new era in banking. (FinTech Futures)
  5. Jensen Huang says you can have AI innovation and safety. (FT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
AI Today in 5

AI Today in 5: September 9, 2026, The Wiki Incident Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. AI governance is the real test for compliance. (FinTech Global)
  2. The role of AI in manufacturing. (Deloitte)
  3. AI hacking WeChat. (NYT)
  4. OpenAI has a wiki ‘incident.’ (Reuters)
  5. Is AGI here? (Bloomberg)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
AI Today in 5

AI Today in 5: September 8, 2026, The EU AI Stack Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Can actuaries trust AI? (FinTech Global)
  2. How AI is transforming global trade management. (Thomson Reuters)
  3. Banks are urged to integrate compliance, culture, and AI governance. (CW)
  4. Substantiate your AI claims. (CCI)
  5. What’s in your EU AI stack? (Forkast)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Innovation in Compliance

Innovation in Compliance: Bennett Borden on the AI Driven Law Practices of Clarion AI Partners

Innovation comes in many areas, and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom speaks with Bennett Borden of Clarion AI Partners.

Borden is a lawyer and data scientist whose career has long focused on the intersection of law, data, and technology, including AI governance, compliance, and the legal implications of generative AI. Drawing on experience at the CIA, in big law, and leading AI-focused legal practices, he views generative AI as a disruptive force reshaping both legal services and business models. Borden argues that effective AI governance requires “governance engineering”: translating legal obligations into technical controls and measurable proof of compliance rather than treating compliance as a separate burden. He also encourages lawyers and organizations to embrace AI proactively, using it to build more efficient, future-ready practices while managing risk through practical, system-level safeguards.


Key highlights:

  • AI-Driven Law Practice Beyond the Billable Hour
  • Compliance as guardrails for faster innovation
  • Gift, Travel, and Entertainment Sandbox Projects
  • Trust Built by Enterprise Licenses and Safeguards
  • Microsecond-by-Microsecond Compliance Proof for AI Governance

Resources

Innovation in Compliance was recently honored as the Number 4 podcast in Risk Management by 1,000,000 Podcasts

Categories
AI in Financial Services in 5 Stories

AI in Financial Services in 5 Stories – Week Ending September 4, 2026

Welcome to AI in Financial Services in 5 Stories. A practical weekly roundup of the five most important AI developments affecting banking, insurance, payments, asset management, and fintech. Each Friday, Tom Fox will break down the top stories that matter most through the lenses of compliance, risk management, governance, and business strategy. Designed for compliance professionals, executives, legal teams, and financial services leaders, it goes beyond headlines to explain why each development matters in a highly regulated industry. The result is a concise weekly briefing that helps listeners stay current on AI innovation while asking sharper questions about oversight, accountability, and trust.

This week’s stories include the following:

  1. AI spots gaps in financial firms’ cybersecurity faster than companies can fix them. (FT)
  2. NVB urges AI for transaction monitoring. (AML Intelligence)
  3. AI puts banking governance to the test. (QA Financial)
  4. Does AI threaten the global banking system? (CNBC)
  5. How the Middle East became an AI fintech hub. (Arab News)

For more information on the use of AI in Compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.