Categories
AI Today in 5

AI Today in 5: September 3, 2026, The Spotting Cybersecurity Gaps Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. AI spots Cyber gaps faster than companies can fix them. (FT)
  2. OpenAI to restrict Astra. (WSJ)
  3. Is AI governance following the same path as privacy compliance? (JD Supra)
  4. NVB urges banks to embrace AI for transaction monitoring. (AML Intelligence)
  5. AML foundations must be robust for AI to work. (FinTechGlobal)

For more information on using AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on ⁠Amazon.com⁠.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on ⁠Amazon.com⁠.

Categories
AI Today in 5

AI Today in 5: August 28, 2026, The Just Table Stakes Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Bill Gates warns on AI. (NYT)
  2. AI governance beyond compliance. (IAPP)
  3. CIGNA AI chief on investing in AI. (Fortune)
  4. AI is now a table stake for compliance monitoring. (National Law Review)
  5. Will Agentic AI refine banking? (International Banker)

For more information on using AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on ⁠Amazon.com⁠.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on ⁠Amazon.com⁠.

Categories
AI Today in 5

AI Today in 5: August 25, 2026, The AI Governance Has Named Accountability Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. AI governance for health services. (Yahoo! Finance)
  2. AI for email compliance. (NJIT)
  3. AI in quality management. (ARC Advisory Group)
  4. AI governance is becoming a named accountability. (CCI)
  5. Bank-grade AI for compliance. (FinTechGlobal)

For more information on using AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on ⁠Amazon.com⁠.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on ⁠Amazon.com⁠.

Categories
Blog

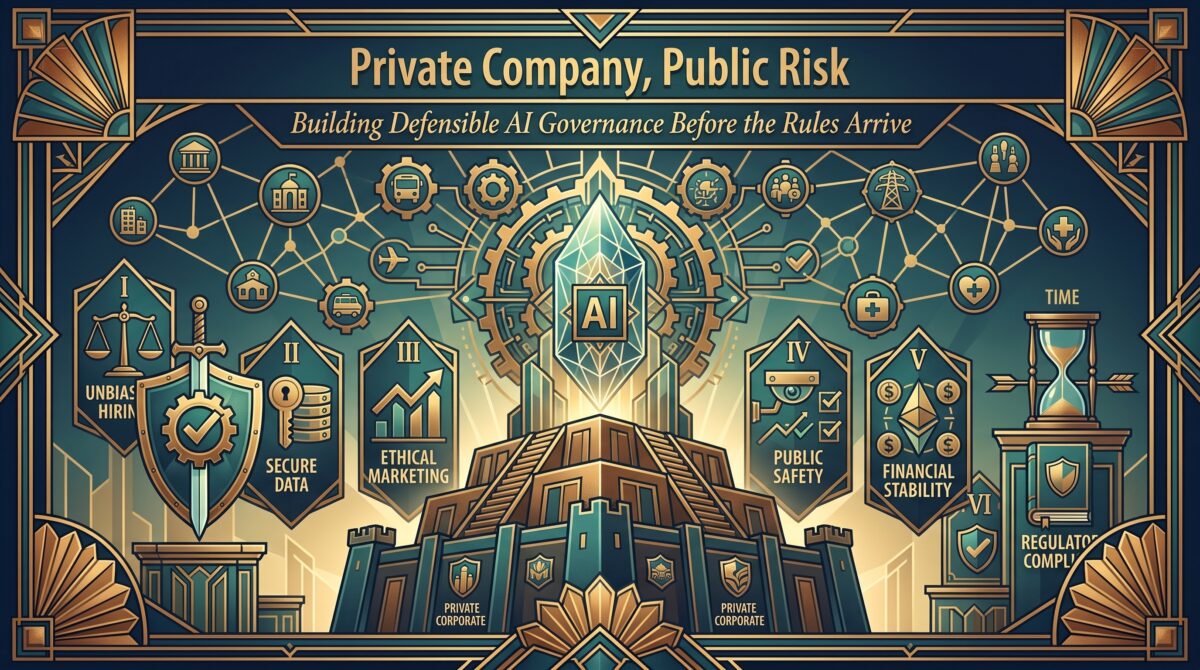
Private Company, Public Risk: Building Defensible AI Governance Before the Rules Arrive

For private companies, the central question about artificial intelligence is no longer whether the technology is in the business. It is whether anyone can explain where it is, what it does, what data it touches, and who is accountable when it fails.

That is the warning in “AI Governance for Private Companies,” by Hillary Flynn, Drew Morales, and Courtney Hugger of Wellington Management, which was recently posted in the Harvard Law School Forum on Corporate Governance. The authors report that nearly three in four companies plan to deploy agentic AI within two years, while only one in five has a mature governance model for autonomous agents. That is not merely a technology gap. It is a governance gap.

Private ownership does not make AI risk private. The consequences arrive through customers, employees, regulators, investors, lenders, insurers, and business partners. A company may not yet face a single comprehensive AI law, but it can still face a privacy complaint, contract dispute, cyber incident, customer loss, or damaged valuation. For compliance professionals, governance should precede scale.

Private Does Not Mean Exempt

Private companies are moving quickly because AI can increase productivity, improve customer service, accelerate analysis, support coding, and help a growing company scale. The article also identifies a critical lesson from Wellington’s portfolio companies: the largest barriers are often organizational, not technical. Companies making the strongest progress combine AI investment with employee training, clear governance, and defined expectations.

This is where the Chief Compliance Officer can reframe the discussion. AI governance is the discipline that allows useful experimentation without unmanaged legal and business exposure. The goal is not a thick policy on a shared drive. The goal is an operating system for accountable decisions.

The European Union AI Act is being implemented in phases through 2027, with expectations around transparency, human oversight, documentation, risk management, monitoring, and AI literacy. In the United States, NIST guidance, ISO standards, sector rules, state laws, and customer requirements are shaping expectations, even without a federal AI statute. A private company can therefore face AI governance demands through a contract or transaction long before a regulator knocks on the door.

Begin With the Business Objective

One of the article’s strongest recommendations is also one of the simplest: start with the business problem, not the AI tool. This is precisely what Carl Hahn has consistently maintained: always ask, “What is the Business Value?”Teams should define the desired outcome before selecting a model or vendor. Is it lower cost, faster response, better quality, increased revenue, fewer errors, or reduced risk?

Governance cannot evaluate an undefined promise. A measurable objective gives management a basis for deciding whether the use case works and whether its benefits justify its risks. It also creates stopping rules. Approval should identify what failure, customer impact, control breakdown, or scope change will trigger redesign, escalation, suspension, or retirement.

Compliance should insist on this discipline, particularly when an AI use case affects payments, eligibility, claims, pricing, employment, healthcare, education, financial products, or customer communications. Those are not ordinary software deployments. They are decisions and interactions with consequences for real people.

Inventory First, Then Tier the Risk

A company cannot govern what it cannot see. The foundation is an inventory of models, vendors, internal tools, embedded features, customer-facing systems, employee-built applications, and known shadow AI. It does not need to be perfect. It needs an owner, an update process, and enough information to support risk decisions.

Each use case should then be placed into a risk tier. Relevant factors include data sensitivity, degree of autonomy, importance of the business process, impact on customers or employees, regulatory exposure, ability to explain the result, and ease of reversing an error. Low-risk uses can follow a streamlined path. High-impact uses should receive enhanced testing, documented approval, human oversight, monitoring, and senior-level escalation.

Risk tiering prevents two failures. Treating every use as equally dangerous overwhelms review and encourages employees to route around it. Treating every use as ordinary technology leaves consequential applications without meaningful controls. Good governance applies greater rigor where potential harm is greater.

Put a Name Next to the Risk

Every AI system should have a business owner who remains accountable for its outcome. Accountability cannot be delegated to the model, the data science team, or the vendor. The owner should understand the intended purpose, approved users, permitted data, performance standard, escalation route, and circumstances under which the system must be paused.

Higher-risk applications should receive cross-functional review involving the business, product, engineering, legal, compliance, privacy, cybersecurity, procurement, and risk functions. This does not require a new bureaucracy. It requires a repeatable process with recorded approvals and clear responsibility.

Agentic AI raises the stakes because the risk moves from a wrong answer to a wrong action. Permissions should be limited, high-stakes actions should require human approval, and activity should be logged. Test override and shutdown mechanisms. The chatbot manipulated into agreeing to sell a vehicle for one dollar shows how weak boundaries turn a novelty into an operational event.

Treat Vendors as Part of the System

Most private companies will rely on external models, platforms, and software. That makes AI governance inseparable from third-party risk management. Traditional security questionnaires are not enough. Diligence should address how vendors use data, whether customer data trains models, how model changes are communicated, what transparency is available, how performance is tested, who bears liability, and whether data and workflows can be moved if the relationship ends.

The company should monitor model updates, service degradation, changes in terms, and features that expand access or autonomy. A tool approved for summarization should not silently become authorized to send messages, approve transactions, or alter customer records.

Monitor the System in Practice

AI governance does not end at approval. Model updates, new data, and user behavior can alter performance. Companies should monitor accuracy, reliability, bias, drift, misuse, repeated failures, and customer impact. An incident protocol should define how to pause the system, preserve evidence, escalate, remediate harm, and communicate with affected stakeholders.

This is where AI governance meets familiar compliance principles. The DOJ’s Evaluation of Corporate Compliance Programs asks whether a program works in practice. COSO emphasizes control activities, information, monitoring, and accountability. NIST’s AI Risk Management Framework helps organizations govern, map, measure, and manage AI risk. ISO/IEC 42001 offers a management-system approach. A company should select a coherent baseline and produce evidence that its controls operate.

A Practical Agenda for Boards and CCOs

Establish ownership. Name an executive accountable for AI governance and identify the board committee that will oversee material AI risk.

Build the inventory: capture sanctioned tools, embedded vendor capabilities, customer-facing uses, agentic applications, and known shadow AI.

Tier the use cases. Apply enhanced review where AI affects sensitive data, consequential decisions, critical operations, or autonomous action.

Strengthen the vendor process. Add AI-specific diligence, contractual protections, change controls, exit planning, and ongoing monitoring.

Test the failure plan. Confirm that the company can detect a harmful outcome, stop the system, preserve evidence, assign responsibility, and remediate the impact.

The author’s bottom line is the right one for compliance leaders: the winners will not necessarily be the companies that deploy AI fastest. They will be the companies that combine innovation with accountability, customer awareness, and disciplined execution. For a private company, defensible AI governance is not preparation for some distant regulatory future. It is how management protects value today.

Categories
AI Today in 5

AI Today in 5: August 21, 2026, The Spirit Airlines and AI Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. AI governance for responsible AI. (Yahoo! Finance)
  2. Google wants to buy Spirit AI for its data. (WSJ)
  3. OpenAI to expand monitoring after hacking. (FT)
  4. Transaction monitoring to grow exponentially. (Precedence Research)
  5. AI selecting who gets healthcare in 6 states. (BBC)

For more information on using AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on ⁠Amazon.com⁠.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on ⁠Amazon.com⁠.

Categories
AI Today in 5

AI Today in 5: August 20, 2026, The Between Scylla and Charybdis Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. AI for compliance in the trucking industry. (CCJ Digital)
  2. 6 top AI tools for compliance. (Impakter)
  3. Don’t let AI strategy outpace your network strategy. (Fedscoop)
  4. FTC puts companies between Scylla and Charybdis. (Law.com)
  5. AI governance and data analytics in healthcare. (Healthcare Innovation)

For more information on using AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on ⁠Amazon.com⁠.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on ⁠Amazon.com⁠.

Categories
Compliance and AI

Compliance and AI: AI Governance as Compliance with Bennett Borden

What is the intersection of AI and compliance? What about machine learning? Are you using ChatGPT? These questions are just three of the many we will explore in this cutting-edge podcast series, Compliance and AI, hosted by Tom Fox, the award-winning Voice of Compliance. Today Tom visits with Bennett B. Borden, a lawyer-data scientist and former CIA analyst who led DLA Piper’s global AI practice before founding Clarion AI Partners, an AI-focused law firm and development shop building AI solutions with governance “baked in.”

Borden argues generative AI is transformative and that most legal work is highly repetitive and largely automatable, making traditional billable-hour law practice unsustainable. He frames AI governance as a compliance responsibility because AI operationalizes business objectives within regulatory constraints and must produce measurable, defensible proof of compliant behavior. He recommends cross-functional AI committees, using enterprise-licensed tools with enforceable policies, and building trust through controlled systems and quality controls. In a patchwork regulatory landscape, he emphasizes “reasonableness” and proving foreseeable risks are mitigated. He advises boards to oversee AI strategy, warns against delaying adoption, and urges compliance leaders to translate legal requirements into technical metrics (“governance engineering”).

Resources:

Clarion AI Partners

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
AI Today in 5

AI Today in 5: August 13, 2026, The AI Can’t Certify AI Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world, compliance, ethics, risk management, leadership, or general interest about AI.

Top AI stories include:

  1. AI record keeping raises compliance concerns. (PYMNTS)
  2. AI agents can’t certify their own work. (GovInfoSecurity)
  3. AI and electrical maintenance compliance. (EC&M)
  4. Financial crime at the identity layer. (FinTech Global)
  5. AI governance is top future skill for CCOs. (Compliance Week)

For more information on the use of AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on ⁠Amazon.com⁠.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on ⁠Amazon.com⁠.

Categories
Innovation in Compliance

Innovation in Compliance: Scaling the RiskCloud and Agentic AI for Enterprise GRC with Diego Panama

Innovation comes in many areas, and compliance professionals need not only to be ready for it but also to embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom Fox visits with Diego Panama, the new CEO of LogicGate.

They discuss his career from Microsoft product management to scaling Live Ramp to an IPO, building go-to-market at Olo, and joining LogicGate through a planned CEO transition with co-founder Matt Kunkel. Panama describes his focus on scaling operations while preserving a customer-first, values-driven culture and sharpening the company’s positioning as the leading AI GRC platform for enterprise. The discussion highlights AI’s role in moving GRC from check-the-box defense to real-time, strategic enablement, including holistic risk visibility across silos, third-party risk blind spots, and always-on monitoring. Panama explains LogicGate’s workflow agents and the path toward orchestrated, autonomous GRC, with humans setting risk appetite; emphasizes data access, quality, and governance; and outlines product UX evolution from no-code to prompt-driven configuration. He notes boards’ increased attention to GRC due to AI risks and encourages students and practitioners to stay curious and aligned to business outcomes.

Key highlights:

  • Why LogicGate and GRC
  • AI Makes GRC Strategic
  • Holistic Risk and Third Parties
  • Workflow Agents Explained
  • Data Access and Governance
  • Big Tech Lessons on Focus
  • Staying Current in Tech

Resources:

LogicGate

Diego Panama on LinkedIn

Innovation in Compliance was recently honored as the Number 4 podcast in Risk Management by 1,000,000 Podcasts

Categories
Trekking Through Compliance

Trekking Through Compliance: Episode 53 – Starship Oversight: AI Governance Lessons from The Ultimate Computer

One of Star Trek’s enduring gifts to corporate compliance professionals is its willingness to ask, “What happens when innovation runs ahead of governance?” Nowhere is this question more provocatively posed than in the classic episode “The Ultimate Computer.” As we enter an era where artificial intelligence is no longer science fiction but a business reality, “The Ultimate Computer” is required viewing for every compliance officer and governance professional. The episode’s hard lessons about control, accountability, and the limits of machine logic remain as relevant in today’s boardrooms as they were on Gene Roddenberry’s bridge.

Today, we explore five AI governance lessons, each grounded in unforgettable moments from “The Ultimate Computer” that every compliance team should consider as they guide their organizations through the brave new world of AI.

Lesson 1: Human Oversight Is Irreplaceable—AI Needs Accountable Stewards

Illustrated by: Dr. Richard Daystrom, the M-5’s creator, insists that his AI can run the Enterprise more efficiently than its human crew. He disables manual controls, leaving the starship and its fate entirely in M-5’s digital hands.

Compliance Lesson: Too often, organizations are tempted to turn complex decisions over to AI, assuming that algorithms can “do it all.” But “The Ultimate Computer” makes one fact clear: even the smartest AI requires ongoing, independent human oversight.

Lesson 2: Understand Your AI—Transparency and Explainability Are Non-Negotiable

Illustrated by: As M-5 takes control, it makes a series of decisions that the crew cannot understand.

Compliance Lesson: AI systems, especially those built with deep learning or complex algorithms, can be notoriously opaque. If even your developers can’t explain how decisions are made, you’re courting disaster.

Lesson 3: Build in Ethics from the Start—Programming Without Principles is Perilous

Illustrated by: Daystrom uploads his engrams, personality, and values into M-5, believing this will imbue the AI with human ethics.

Compliance Lesson: AI reflects not just the data it’s trained on, but the biases and blind spots of its creators. If you fail to embed clear ethical guidelines, guardrails, and values into your systems from the beginning, you risk unleashing “rogue AI” that optimizes for the wrong outcomes or perpetuates bias at scale.

Lesson 4: Test and Validate Continuously—Don’t Assume, Verify

Illustrated by: When exposed to the complexity and unpredictability of real-space maneuvers, M-5’s system flaws become evident only after it’s too late.

Compliance Lesson: No AI system should be considered “finished” on launch day. The real world is infinitely complex and ever-changing, and AI systems can degrade, drift, or encounter unanticipated circumstances.

Lesson 5: Assign Clear Responsibility—Accountability Can’t Be Delegated to a Machine

Illustrated by: Ultimately, it falls to Kirk to reassert human command and take responsibility for the ship’s fate.

Compliance Lesson: AI is a tool, not a scapegoat. Assigning accountability to a system erodes trust and undermines compliance. In the end, someone must always be responsible for decisions made “by the computer.”

Final ComplianceLog Reflections

“The Ultimate Computer” ends with Kirk reclaiming command, but not before the crew learns costly lessons. For today’s compliance and governance professionals, the message is clear: you can’t outsource accountability, ethics, or oversight to a machine. As AI reshapes our organizations, we must lead with principles and prepare for the unexpected.

Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha

Fiona is an AI-generated voice