Categories
Great Women in Compliance

Great Women in Compliance: Wildly Effective, 10 Years Later

Author and compliance professional Kristy Grant-Hart on the 10th anniversary of her book. 

Sarah Hadden sits down with Kristy Grant Hart to discuss the 10th anniversary edition of her influential book, How to Be a Wildly Effective Compliance Officer. They explore how the compliance profession has evolved over the past decade — from a rules-and-regulations mindset toward a more human-centered approach grounded in influence, resilience, storytelling, and leadership.

They also dig into some of the book’s more debated ideas, including personal branding, visibility, networking, and whether being “wildly effective” requires becoming an influencer.

Along the way, they tackle burnout, resilience, AI’s rapidly expanding role and why human judgment remains irreplaceable. This is a candid and energizing conversation about what it really takes to thrive in compliance today — and why the future of the profession is bright.

Categories
Blog

Where No Man Has Gone Before: Power, Ego, and the Ethics of Control

In this episode of Trekking Through Compliance, we consider Where No Man Had Gone Before, which aired on September 22, 1966, Star Date 1312.4. We board the Enterprise as it breaches the edge of the galaxy and the boundaries of ethical power. When a mysterious force transforms navigator Gary Mitchell into a godlike being with unchecked telepathic abilities, his rapid descent into tyranny presents a sobering metaphor for the compliance professional. With rising powers come rising risks, and Kirk must choose between loyalty to a friend and duty to his crew. Today, we explore five key compliance takeaways from Where No Man Has Gone Before, showing how early-stage risk, power imbalances, and ethical hesitation can transform even trusted employees into existential threats for your organization.

Story

This is the first Star Trek episode made (not counting the pilot episode, The Cage), although not the first aired. It differs from subsequent episodes in that there is no “Space, the final frontier” voice-over during the theme song at the beginning.

The Enterprise discovers a 200-year-old ship recorder from the SS Valiant near the galaxy’s edge. Shortly after, the Enterprise passes through an unknown phenomenon that causes major damage and knocks out navigators Gary Mitchell and Dr. Elizabeth Dehner (both of whom have high ESP ratings). When Gary recovers, he begins to acquire telepathic and telekinetic powers. Kirk, alarmed at the prospect of having his ship taken over by an increasingly powerful and tyrannical Mitchell, is convinced by Spock to maroon Mitchell at the lithium cracking plant of Delta Vega. Dr. Piper has no explanation for what is happening. Gary kills Lee Kelso and escapes from his imprisonment. Kirk follows him and can destroy him with the help of Dr. Dehner, who is also beginning to acquire the power but kills herself in the process.

Key highlights:

1. Emerging Risks – Early Signs Should Trigger Action, Not Complacency

🖖 Illustrated by: Gary Mitchell’s glowing eyes and ESP abilities appearing shortly after the Enterprise crosses the galactic barrier.

The moment Mitchell begins reading faster, manipulating objects, and demonstrating control over ship systems, it’s clear something’s wrong. But initial responses are muted—like many corporate environments where emerging risks are downplayed. Compliance teams must be trained to treat anomalies seriously, regardless of the individual’s charisma or seniority.

2. Leadership and Ethical Courage – Friendship vs Responsibility

🖖 Illustrated by: Kirk’s emotional struggle to deal with Mitchell, his long-time friend.

Kirk hesitates—understandably so—because of his relationship with Mitchell. But ultimately, he chooses duty over sentiment. Compliance officers are often put in a similar spot: when someone close to leadership violates ethical norms, will the organization act? Ethical courage means prioritizing institutional integrity over personal comfort.

3. Power Without Accountability – Why Guardrails Matter

🖖 Illustrated by: Mitchell’s growing powers and his assertion of superiority over the crew.

With no checks on his abilities, Mitchell quickly develops a god complex. This is a chilling representation of what happens when key employees—CFOs, procurement officers, or engineers—operate without oversight. Just because someone is brilliant or “indispensable” doesn’t mean they’re beyond the reach of your compliance program.

4. Escalation Protocols and the Role of Outside Advisers

🖖 Illustrated by: Spock’s insistence that Mitchell be isolated and marooned.

Spock serves as outside counsel—offering unemotional advice grounded in logic. Every company needs this voice. Internal politics often cloud judgment; a good compliance officer, like Spock, keeps the focus on what must be done to protect the enterprise. His advice to act decisively is what ultimately saves the crew.

5. Shared Risk and Collective Action – The Role of Allies in Enforcement

🖖 Illustrated by: Dr. Dehner’s decision to sacrifice herself to stop Mitchell.

Dehner, who initially defends Mitchell, comes to see the threat he poses and joins Kirk in neutralizing him. Her journey mirrors that of employees who shift from enabling bad behavior to becoming whistleblowers or allies in enforcement. Compliance success depends on empowering people like Dehner to act before it’s too late.

Final StarLog Reflections

Where No Man Has Gone Before gives us a blueprint for compliance at the edge of the unknown. It reminds us that rapid change, whether from new tech, new hires, or new business environments, demands rapid, courageous compliance responses. Waiting too long to act can mean the difference between course correction and catastrophe.

Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha

Categories
Innovation in Compliance

Innovation in Compliance: Data Defensibility: Enterprise Agentic AI: Governance, Auditability, and the AI Gateway Layer with Nikunj Bajaj

Innovation occurs across many areas, and compliance professionals need not only to be ready for it but also to embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom visits with Nikunj Bajaj, Co-founder & CEO at TrueFoundry, about enterprise agentic AI infrastructure, governance, and hidden costs most organizations are not accounting for.

Nikunj describes TrueFoundry’s platform as a single control plane for enterprises to build, ship, and govern agentic AI applications, inspired by Meta’s internal ML stack, which he says is about a decade ahead of the rest of the industry. He argues enterprises over-focus on model and tool selection when problem definition and effective use are the real constraints. On governance, he identifies two failure modes: avoiding meaningful use cases entirely to sidestep governance risk, or trying to solve all governance problems up front and never reaching ROI. Successful teams implement application-specific controls iteratively, starting with a few high-value use cases rather than hundreds of low-value ones. He highlights that model inference accounts for only about 20% of total generative AI spend, with the majority of spend concentrated in infrastructure, engineering, and debugging, creating cost-allocation and budget-control challenges for compliance teams. For auditability, he argues that an agent without full decision traces is “a liability with an API key,” and walks through how end-to-end tracing enables audit readiness, faster debugging, and proactive attack detection. He closes by advocating centralized control via a unified AI gateway while enabling federated development and tailoring guardrails to whether your exposure surface is external or internal.

Key highlights:

  • Stop Chasing Tools
  • Governance vs Speed
  • Hidden AI Costs
  • Agent Auditability
  • Board Level Priorities

Resources:

Connect with Nikunj Bajaj

Learn More About TrueFoundry

Categories
AI Today in 5

AI Today in 5: June 2, 2026, The Exposing Yourself Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the AI Today In 5. All, from the Compliance Podcast Network. Each day, we consider five stories from the business world, compliance, ethics, risk management, leadership, or general interest about AI.

Top AI stories include:

  1. A compliance gap that can expose your AI systems. (FinTech Global)
  2. CT businesses face new AI law. (HBJ)
  3. Anthropic files to go public. (NYT)
  4. OpenAI sued by FL AG. (WSJ)
  5. Anthropic offers Mythos to the EU. (FT)

For more information on the use of AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.

Categories
Daily Compliance News

Daily Compliance News: June 2, 2026, The Big Trouble Down Under Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • The former Turks and Caicos PM was sentenced to 4 years in prison for corruption. (AP)
  • Storytelling in compliance. (CCI)
  • Another former TD America employee pleads guilty to bribery and corruption. (Washington Times)
  • KPMG Australia Directors agree to reopen the investigation. (SMH)

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.

Categories
Blog

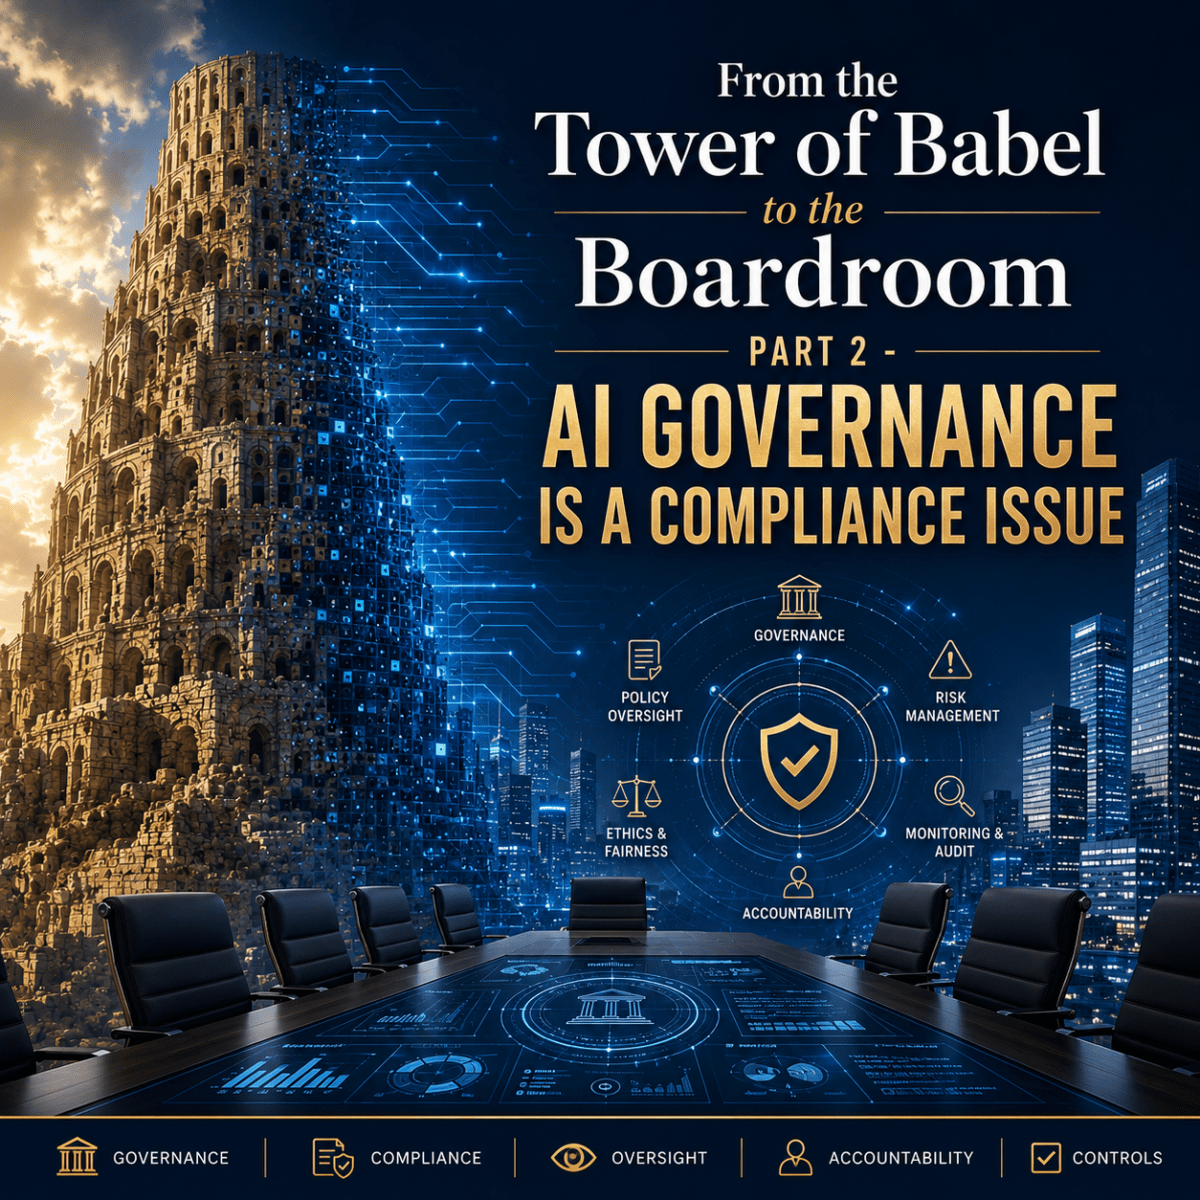
From the Tower of Babel to the Boardroom: Part 2 – AI Governance Is a Compliance Issue

In the first post in this series, we used Magnifica Humanitas to frame the choice facing every board and compliance leader in the age of artificial intelligence. Companies can build a new Tower of Babel, driven by speed, scale, efficiency and power without adequate governance. Or they can follow the path of Nehemiah, rebuilding with discipline, shared responsibility, accountability and the human person at the center. That choice now moves from principle to program design.

AI governance cannot remain in the innovation lab, the IT department or the digital transformation office. It belongs inside the compliance program. Not because compliance should own every AI decision, and not because the CCO should become the chief technologist. AI governance belongs in compliance because AI creates the very risks compliance programs are designed to manage: legal risk, ethical risk, data risk, third-party risk, culture risk, internal controls risk, reporting risk, investigation risk and board oversight risk.

Magnifica Humanitas makes this point in moral language. Pope Leo writes that the use of AI is never a purely technical matter when it enters processes that affect people’s lives, rights, opportunities, status and freedom (Magnifica Humanitas, ¶102). For the modern compliance professional, that is familiar terrain. These are the risks an effective compliance program must identify, assess, control, monitor and remediate.

AI Is Not an Adjacent Risk

The first mistake companies make is treating AI as an adjacent risk. The business says AI is a productivity tool. IT says AI is a systems issue. Legal says AI is a regulatory issue. Privacy says AI is a data issue. Cybersecurity says AI is an access issue. HR says AI is a workforce issue. Internal audit says AI is a control issue. Procurement says AI is a vendor issue. They are all correct.

That is precisely why AI governance must be cross-functional, risk-based and integrated into the compliance program. AI does not respect organizational charts. It moves through data, workflows, vendors, platforms, communications, decisions and employee behavior. It may be embedded inside software already used by the company. Employees may adopt it without formal approval. Vendors may deploy it before procurement or legal fully understands how the tool works. It may be used by compliance itself for monitoring, investigations, hotline triage, third-party due diligence, sanctions screening or training.

The DOJ Has Already Put AI on the Compliance Agenda

The Department of Justice has made clear that AI is now part of compliance program evaluation. The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks whether a company has a process for identifying and managing emerging risks, including risks related to new technologies such as AI. It asks how the company assesses the impact of AI on compliance with criminal laws, whether AI risk is integrated into enterprise risk management, how the company governs AI in commercial operations and in the compliance program, whether controls monitor trustworthiness and reliability, whether AI is limited to intended uses, what human decision-making baseline is used, how accountability is enforced and how employees are trained.

This is where the Encyclical and the ECCP align. Pope Leo calls for responsibility to be clearly defined at every stage, from those who design and develop AI systems to those who use them and rely on them for concrete decisions (Magnifica Humanitas, ¶105). The DOJ asks whether the company has translated that responsibility into risk assessment, controls, testing, training and accountability.

For CCOs, the message is direct. AI governance should be reflected in the risk assessment, policies and procedures, training, third-party risk management, internal controls, monitoring, investigations, discipline, incentives and board reporting. A company that cannot explain how it governs AI will struggle to demonstrate how its compliance program keeps pace with the business.

The CCO’s Role in AI Governance

The CCO does not need to own AI. The CCO does need a seat at the table. Compliance should inform the design of the company’s AI governance model. That model should include a cross-functional AI governance committee with representation from compliance, legal, privacy, cybersecurity, IT, HR, internal audit, procurement, finance and the business. It should define approval rights for high-risk use cases. It should establish documentation standards. It should require risk classification. It should identify prohibited uses. It should provide escalation channels for AI incidents and concerns.

This is the corporate version of Nehemiah’s wall. Pope Leo writes that everyone is given a section of the wall and that shared responsibility across disciplines and communities is the way to build for the common good (Magnifica Humanitas, ¶13). AI governance works the same way. Legal cannot do it alone. IT cannot do it alone. Compliance cannot do it alone. The governance model must assign roles so the whole enterprise can rebuild with discipline.

The CCO should also insist on an inventory of AI use cases. This is the foundational control. The company cannot govern what it cannot see. The inventory should include the business owner, tool name, vendor, purpose, data categories, decision impact, risk rating, applicable policies, human review requirements, testing history, approval date, renewal date and control owner.

From Encyclical Principle to Corporate Governance Requirement

The bridge from Magnifica Humanitas to corporate governance is straightforward. The Encyclical does not give companies an AI procedure manual. It gives them governing principles. The compliance task is to translate those principles into requirements that can be owned, tested, evidenced and improved. Pope Leo is explicit that digital processes should not be imposed from above in opaque or unilateral ways, but should be directed toward the common good with transparency, accountability, meaningful participation, independent checks, algorithmic transparency, equitable access to data and avenues for recourse (Magnifica Humanitas, ¶71).

Human dignity becomes human impact assessment and human review. The common good becomes enterprise risk governance and stakeholder impact. Subsidiarity becomes cross-functional participation, with decisions made close enough to the risk to be informed and accountable. Solidarity becomes attention to affected employees, customers, communities and vulnerable populations. Social justice becomes bias testing, access, recourse and a refusal to let opaque systems create hidden exclusion.

NIST AI RMF and ISO/IEC 42001 as Practical Architecture

Two frameworks can help compliance leaders translate AI principles into program structure. They give operational force to Pope Leo’s warning that it is not enough to invoke ethics in the abstract. He instead calls for robust frameworks, independent oversight, informed users, and institutions capable of governing AI’s effects (Magnifica Humanitas, ¶106). That is precisely the move compliance must make, from AI principles to an AI management system.

The NIST AI Risk Management Framework organizes AI risk management around four functions: Govern, Map, Measure and Manage. For compliance leaders, that is highly practical. Govern means the company has assigned authority, accountability, policies and risk appetite. Map means the company understands the context, purpose, users, affected stakeholders and potential impact of each AI use case. Measure means the company evaluates performance, reliability, bias, data quality, security and control effectiveness. Manage means the company prioritizes risks, implements controls, monitors outcomes, remediates problems and documents decisions.

ISO/IEC 42001 provides a management system model. It focuses on establishing, implementing, maintaining and continually improving an AI management system. For a compliance program that supplies the discipline of policy, objectives, roles, processes, risk assessment, controls, monitoring, performance evaluation, corrective action and continual improvement.

From Policy to Controls

A policy is necessary, but it is not sufficient. A company can have a well-written AI policy and still have a weak AI governance program. The issue is whether the policy has an operational effect.

Pope Leo explains why. Technology is never neutral because it takes on the characteristics of those who devise, finance, regulate and use it (Magnifica Humanitas, ¶9). He later adds that every technical tool embodies choices and priorities through what it measures, what it ignores, what it optimises, and how it classifies people and situations (Magnifica Humanitas, ¶104). For compliance, this means the control environment must cover design, data, use, monitoring, output, and remediation.

COSO has warned that generative AI poses risks of cyber exposure, prompt manipulation, opaque reasoning, model drift, and frequent configuration changes that can affect operations, reporting, and compliance if not addressed with robust internal controls. That is the compliance challenge. AI governance must become a control activity.

Compliance Can Use AI Responsibly

Compliance should not stand outside the AI transformation. AI can help compliance become more effective. It can identify patterns in transactional data. It can assist with third-party risk scoring. It can support sanctions screening. It can help analyze hotline trends. It can improve training design. It can help prioritize monitoring. It can summarize large document sets in investigations. It can support control testing.

Magnifica Humanitas is direct on this point. AI may imitate functions of human intelligence, but it does not possess conscience, experience, responsibility or the capacity to judge good and evil (Magnifica Humanitas, ¶99). It can also create excessive reliance, the impression of objectivity and a weakening of personal judgment (Magnifica Humanitas, ¶100). Compliance professionals should use AI, but they should never surrender professional judgment to it. Human primacy remains the central control.

5 Lessons for the CCO
  1. Treat AI as a human dignity and compliance risk. AI is now part of legal, ethical, operational, data, third-party and cultural risk. The Encyclical reminds us that AI affects rights, opportunities, status, and freedom when it enters into consequential decisions (Magnifica Humanitas, ¶102).
  2. Build and maintain an AI inventory because governance begins with visibility. Every AI use case should have an owner, a purpose, a risk rating, a data classification, a control set, an approval status, and a review cycle.
  3. Govern compliance’s own use of AI because accountability starts at home. Compliance should use AI, but it must document purpose, controls, human review, validation and accountability.
  4. Move from policy to controls because technology is never neutral. AI governance requires approval workflows, data restrictions, testing, monitoring, escalation, remediation and auditability (Magnifica Humanitas, ¶9, ¶104).
  5. Report evidence to the board because accountability requires more than aspiration. Boards need dashboards and documentation showing where AI is used, what risks exist, what controls apply, who is accountable and whether the governance program is effective (Magnifica Humanitas, ¶105).
Conclusion: From Governance Principle to Control Discipline

Magnifica Humanitas challenges us to place the human person at the center of technological transformation. For compliance leaders, that means AI must be governed through risk assessment, controls, accountability, transparency, human oversight and evidence. The DOJ ECCP makes clear that prosecutors will ask how companies govern AI in the business and in compliance. NIST AI RMF and ISO/IEC 42001 provide practical architecture for doing so. COSO gives the internal controls discipline.

The compliance profession should embrace AI. It can make compliance more effective, more data-driven and more responsive. But embracing AI does not mean surrendering judgment to it. The right model is not fear. The right model is governed by adoption.

In the next post, we will move from formal AI governance to the most immediate AI control challenge inside many companies: Shadow AI and Internal Controls. Employees are already using AI tools because they are fast, useful and accessible. The compliance question is whether the company can turn hidden use into governed use before shadow AI becomes the next major control failure.
Categories
AI Today in 5

AI Today in 5: June 1, 2026, The AI is Infrastructure Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the AI Today In 5. All, from the Compliance Podcast Network. Each day, we consider five stories from the business world, compliance, ethics, risk management, leadership, or general interest about AI.

Top AI stories include:

  1. Compliance is becoming infrastructure. (FinTech Global)
  2. AI: What CFOs need to know for fintech. (Tech Funnel)
  3. AI models consistently break EU AI law. (Tech Republic)
  4. AI outpacing governance frameworks. (Insurance Business Mag)
  5. China issues ethical guidelines for AI use. (IAPP)

For more information on the use of AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.

Categories
Daily Compliance News

Daily Compliance News: June 1, 2026, The End of Climate Disclosure Rules Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • Corruption concerns hit Mexico, yet again.  (Bloomberg)
  • SEC wants to kill off climate disclosure rules. (NYT)
  • China threatens to launch trade probes against the EU. (WSJ)
  • Can Trump impose a $100K visa fee? (Reuters)

For more information on the use of AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.

Categories
FCPA Compliance Report

FCPA Compliance Report: Matt Ellis on Cartels, FTO Risk, and Corporate Compliance in Latin America

In this episode, Tom Fox welcomes Matt Ellis of Miller & Chevalier about the ACI “Cartels, TCOs and Compliance in Latin America” forum (July 20–21, Washington, DC) and why cartel/TCO/FTO risk is a timely 2026 compliance priority.

Ellis describes the Trump administration’s focus on cartels, fentanyl, China’s influence, and the expanded enforcement toolkit—FCPA guidance linking to cartel activity, sanctions, AML actions (including FinCEN orders against Mexican financial institutions), and cartel FTO designations implicating the Anti-Terrorism Act. They discuss how cartels infiltrate supply chains, creating “material support” exposure, and why due diligence must go beyond traditional screening to on-the-ground intelligence and nuanced red flags. Ellis notes government interest in compliance expectations, extortion-payment considerations, the Lafarge/ISIS example, anticipated investigations, broader regional risk (Mexico, Venezuela, Colombia, Brazil), and increased multi-agency coordination and potential dialogue with U.S. authorities.

Key highlights:

  • Why This Conference Now
  • Due Diligence Goes Deeper
  • Extortion and Self-Reporting
  • Beyond Mexico Regional Risks
  • Whole-of-Government Focus
  • When to Engage Government

Resources:

Cartels, TCOs and Compliance in Latin America, July 20-21

Matt Ellis on LinkedIn

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.

Categories
From the Editor's Desk

From the Editor’s Desk: Aaron Nicodemus on the May and June in Compliance Week

In this episode of ‘From the Editor’s Desk,’ Tom Fox visits with Aaron Nicodemus to discuss highlights from Compliance Week in May, review the National Conference, which concluded in May and take a look at what is coming down the pike in June in Compliance Week.

They report that federal enforcement is not receding but shifting, with heightened risk from Foreign Terrorist Organization (FTO) designations affecting companies operating in Mexico, Latin America, and Brazil; increased and novel use of the False Claims Act, including actions targeting DEI programs, referencing IBM and PayPal settlements; and growing enforcement roles for states, FINRA, and divergent ESG regimes in the UK and Europe. Guidance to compliance leaders is to “stay the course,” strengthen third-party risk management, and document enhanced due diligence around potential FTO ties. They note AI discussions moving from governance frameworks toward scaling practical compliance use cases. June will feature “Inside the Mind of the CCO” survey results, DEI-related findings, and two webcasts. They also recognize former Compliance Week journalist Allie McDevitt’s ASBE national Gold Award for her Lafarge series, which is cited as a roadmap for FTO-related risk, alongside DOJ messaging on self-reporting to seek declination.

Resources:

Aaron Nicodemus on LinkedIn

Compliance Week