Categories
Trekking Through Compliance

Trekking Through Compliance: Episode 13 – The Conscience of the King

In this episode of Trekking Through Compliance, we consider the episode The Conscience of the King, which aired on December 8, 1966, with a Star Date of 2817.6.

In this episode of Trekking Through Compliance, we turn our attention to The Conscience of the King, a Shakespeare-infused Star Trek story that challenges Captain Kirk—and us—to grapple with the ethics of justice, mercy, and leadership responsibility. When Kirk suspects that the famed actor Anton Karidian is Kodos the Executioner—a governor responsible for ordering the deaths of 4,000 colonists years earlier—he must weigh vengeance, truth, and the costs of reopening old wounds.

As we unpack this episode, we connect Kirk’s internal struggle and ethical decision-making to the real-world challenges compliance professionals face when confronting legacy misconduct, institutional cover-ups, and questions of redemption in corporate culture.

Story Synopsis

Dr. Thomas Leighton calls the Enterprise Planet Q. Leighton suspects Anton Karidian, the leader of a Shakespearean acting troupe currently on the planet, is Kodos the Executioner, the former governor of the Earth colony of Tarsus IV. Kodos ordered that half the population of 8,000 be put to death during a food shortage. Both Leighton and Kirk were eyewitnesses.

Kirk arranges to ferry the acting troupe to its next destination. Spock learns the history of the massacre, Kirk’s connection to it, and that seven of the nine witnesses had died in each case when Karidian’s troupe was nearby. Kirk confronts Karidian with his suspicions. Karidian does not admit to being Kodos.

Karidian, overhearing, is disturbed, and Lenore tries to reassure him by revealing that she has been killing the witnesses to his crimes. Kirk moves to arrest them both. Lenore snatches a phaser and accidentally kills Karidian.

Key highlights:

1. The Weight of Past Decisions—Leadership Never Forgets

🖖Illustrated by: Kirk’s memory of witnessing the atrocities of Tarsus IV as a young man.

Great leaders never leave their past behind—they carry it forward as context and compass. When legacy issues, such as old FCPA violations or dormant discrimination claims, resurface, leaders must face them directly rather than bury them under corporate amnesia.

2. Silent Complicity and Ethical Courage—Speak Up, Even Years Later

🖖Illustrated by: Dr. Leighton’s insistence that Karidian is Kodos, despite the passage of time.

Leighton models the whistleblower’s dilemma: does the pursuit of truth justify disrupting someone’s life decades later? The answer, in compliance, is yes; when lives are harmed or injustice is committed, silence is complicity.

3. Leadership and Doubt—Action Without Certainty

🖖Illustrated by: Kirk’s internal struggle over whether Karidian is truly Kodos and whether justice still matters.

Kirk wrestles with doubt, a hallmark of responsible leadership. Unlike the rigid commander stereotype, Kirk shows us that great leaders pause, reflect, and sometimes hesitate before acting.

4. When the Next Generation Fails—Managing Succession and Oversight

🖖Illustrated by: Lenore Karidian’s vigilante campaign to eliminate witnesses to her father’s past.

Lenore’s misguided sense of loyalty and justice highlights the risks of leadership failure in succession. In a corporate setting, this highlights the importance of mentoring future leaders, integrating ethics into the culture, and establishing oversight during transitions.

5. Justice vs. Mercy—Leadership Must Balance the Two

🖖Illustrated by: Kirk’s decision not to kill Karidian but to hold him accountable through due process.

Ultimately, Kirk refuses to exact revenge. He chooses lawful action over vigilante justice. This restraint is perhaps the greatest leadership lesson of the episode: compliance is not about punishment; it is about principled action.

Final Starlog Reflections

The Conscience of the King is more than a mystery; it is a meditation on the responsibilities of leadership and the ethics of remembrance. Compliance professionals often find themselves at the intersection of institutional memory and moral action. Whether addressing legacy misconduct, evaluating redemptive narratives, or confronting cover-ups, we must carry the same conscience Kirk bears: one rooted in justice, tempered by mercy, and guided by truth.

As we say in the world of compliance, investigate when others ignore the issue. Act when others hesitate. Lead when others bury the past.

Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha

Fiona and Timothy are AI-generated voices.

Categories
Creativity and Compliance

Creativity and Compliance: Compliance 6-Pack: Part 5 – Truth in Comedy – Authenticity and Storytelling for More Credible Compliance

Tom and Ronnie continue their six-part series highlighting the role of improv in compliance. This series links improv lessons to corporate compliance and some of the key tools and strategies Ronnie has brought from his former world of improv to the corporate compliance communications realm. In today’s Improv & Compliance Lesson 5, the lesson focuses on “Truth in Comedy,” linking improv and comedy to ethics and compliance.

Tom and Ronnie begin with Gilda Radner’s quote, “Humor is just truth only faster.” Feldman argues comedy works because it exposes shared truths, and compliance programs build credibility by being authentic about real issues rather than pretending everything is fine. He recommends sharing speak-up and reporting trends, anonymized investigation outcomes, culture survey results, and what happens after reports to build trust. Feldman suggests using true stories—internal case studies or news examples—told in engaging formats (newsletters, podcasts, interviews, videos, reenactments) to create teachable moments, stressing “don’t be boring.” They conclude that truthful, interesting communication and authenticity increase engagement, strengthen training, and improve psychological safety and speak-up culture.

Resources:

Ronnie

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

Creativity and Compliance is a multiple-award-winning podcast and was recently honored as one of the Top 35 Podcasts on Creativity by Feedspot.

Categories
Blog

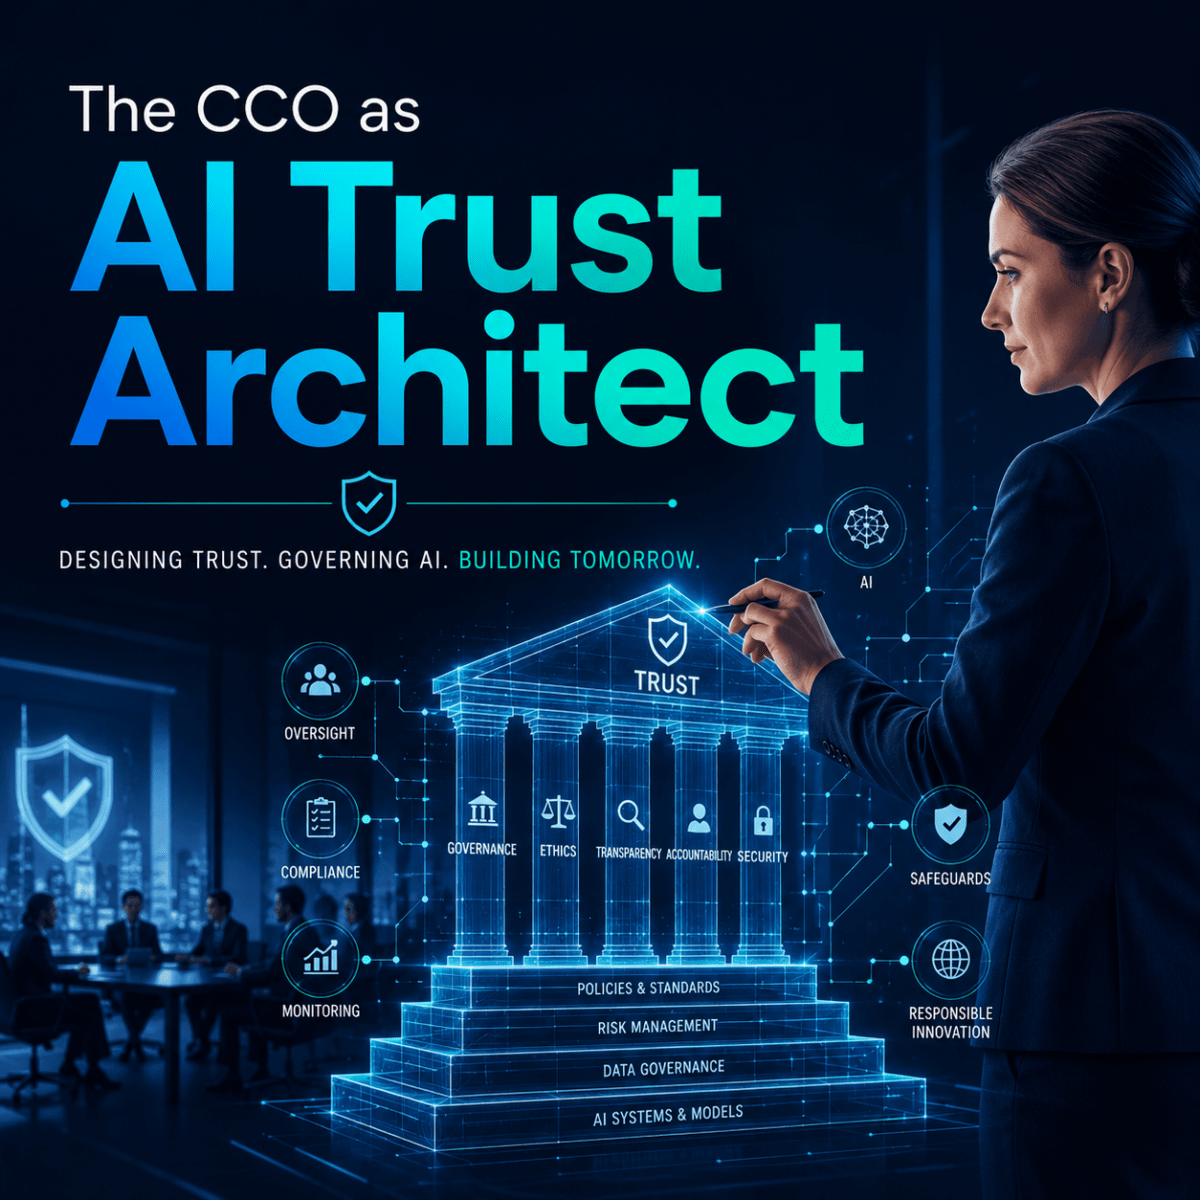
The CCO as AI Trust Architect

The most important AI risk inside many companies may not be that employees are using AI. It may be that employees are using AI and hiding what they are learning. That is the central compliance lesson from Eric Anicich and Jeslyn Brouwers’ HBR article, Why Employees Aren’t Transparent About Their AI Usage. The authors open with a physician who had built a highly effective prompting template inside an approved, HIPAA-compliant AI tool. His colleagues were struggling with the same tool. He believed his template could help them. Yet he did not share it.

The article reports that a study by KPMG and the University of Melbourne, involving more than 48,000 respondents, found that 57% of employees admitted to hiding their AI use at work. More importantly, the authors argue that concealed use is only part of the issue. What employees are learning privately through prompt sequences, chained tools, and successful workflows may matter even more. AI introduces what the authors call the suppression of solutions: employees may be withholding productivity breakthroughs that could help the entire organization.

For the CCO, this creates a new mandate. The compliance function must help bring AI use into the open without becoming the AI police. The CCO must build a governance system that encourages employees to disclose, share, and improve AI-enabled work while still protecting the company from real risks around confidentiality, privacy, IP, bias, inaccurate outputs, cybersecurity, records retention, regulatory representations, and misuse. That is the function the CCO can fulfill: the AI trust function.

Why Hidden AI Use Is a Compliance Problem

Most compliance professionals instinctively focus on the obvious AI risks. Employees may paste confidential data into public tools. They may use AI to draft customer-facing claims without verification. They may generate code, contracts, marketing copy, investigation summaries, due diligence reports, or regulatory submissions without appropriate review. They may rely on AI outputs that are inaccurate, biased, incomplete, or unsupported. Those risks are real.

But the authors point to a second problem: the company may also be losing the benefits of compliant AI experimentation. Productivity gains are once scaled through shared systems and standardized processes. With AI, many gains begin as individual discoveries: a better prompt, a workflow shortcut, a way to summarize information, a way to identify anomalies, or a method that reduces a multi-hour task to minutes. That knowledge is portable, private, and easy to conceal.

This means the CCO must avoid a one-dimensional response. A punitive AI governance program may reduce some visible misuse, but it may also drive experimentation underground. Employees who fear being judged, punished, overworked, or replaced will not share what they are doing. They will protect themselves. That creates the worst of both worlds: risk remains hidden, and useful innovation remains trapped inside individual workflows.

The CCO’s New Role: Govern for Trust, Not Just Control

The author’s core finding is highly relevant to compliance. They surveyed 604 U.S.-based employees who used AI at work daily or multiple times per day. Nearly one in three said they had intentionally withheld AI-related knowledge, workflows, or techniques. Employees in the lowest quartile of organizational trust were nearly four times as likely to withhold AI knowledge as those in the highest quartile (47% versus 14%). A similar pattern appeared for psychological safety, 45% versus 17%.

That finding should feel familiar to compliance professionals. Speak-up culture works the same way. Employees report misconduct when they believe the company will listen, protect them, and act fairly. Employees hide misconduct when they believe the company will punish the messenger, ignore the issue, or retaliate indirectly. AI transparency is now a speak-up issue.

The CCO should therefore treat AI disclosure as part of the company’s broader culture of integrity. The question is not merely, “Are employees using approved AI tools? ”The better question is, ‘Do employees trust us enough to tell us how they are using AI, what they have learned, where they are uncertain, and what risks they see? ”

That is where the compliance function can add unique value. Compliance already understands reporting channels, non-retaliation, policy clarity, training, investigation triage, escalation, monitoring, remediation, third-party risk, and board reporting. Those capabilities can be applied to AI governance if the CCO frames the issue correctly.

Distinguish Experimentation from Misconduct

A major insight in the article is that companies often confuse two very different categories of behavior. One is blameworthy deviance: ignoring rules or cutting corners in ways that harm the organization. The other is exploratory testing: experimenting at the edge of what is known in ways that can generate valuable learning. When companies confuse the second with the first, they punish the behavior they need to encourage. This is directly applicable to the CCO.

An employee who uploads customer personal data into an unapproved public AI tool may have created a serious compliance issue. An employee who uses an approved internal AI tool to create a better first draft of a due diligence memo may have created a learning opportunity. An employee who uses AI to fabricate supporting documentation has engaged in misconduct. An employee who uses AI to test a workflow and then asks compliance whether the use is permissible has done exactly what the company should want. The CCO’s job is to build a framework that makes those distinctions clear.

That means creating red lines, green lanes, and gray zones. Red lines are prohibited uses: confidential data in unapproved tools, AI-generated false records, unreviewed regulatory filings, discriminatory automated decision-making, or any use that circumvents required approvals. Green lanes are encouraged for use: approved tools for summarization, first drafts, brainstorming, translation support, policy search, training development, or internal productivity tasks, where appropriate safeguards are in place. Gray zones are uses that require consultation: HR decisions, customer communications, legal analysis, investigation outputs, high-risk third-party reviews, or regulated submissions.

A compliance program that treats every use of AI as suspicious will teach employees to hide. A compliance program that treats every use of AI as harmless will fail in its duty. The CCO must create the middle path: clear, risk-based, practical, and trusted.

Earn the Disclosure You Want

The article advises leaders to “earn the disclosure” they want. Employees need clear guidance on what AI use is encouraged, what is off-limits, and how to handle gray areas. The authors also warn that companies should not force employees to convert a useful prompt into a long process memo. Lightweight templates, short demos, and practical “show me how you built this” sessions are better ways to turn private methods into reusable knowledge.

That is a practical blueprint for the CCO. A CCO should create an AI disclosure process that is easy to use. It should not feel like an investigation request. It should not require a ten-page form. It should not punish employees for asking questions. The goal is to make disclosure normal.

That is enough to begin. The CCO can then partner with IT, Legal, Privacy, Cybersecurity, HR, Internal Audit, and business leaders to determine whether the workflow should be approved, modified, shared, restricted, or escalated. The key is tone. The message should be: “Show us what you are learning so we can help you use AI safely and scale what works.”

Reward Multiplier Behavior

The article warns against rewarding only individual AI productivity. If employees believe that sharing makes them less distinctive while others benefit, they will hide. Instead, companies should reward reusable workflows, peer adoption, quality improvements, and contributions that help others. The authors recommend giving credit in performance reviews, protecting time for continued experimentation, and closing the loop by telling employees where their contribution was used and what improved. This is where a CCO can help turn AI transparency into culture.

Compliance should not run a generic AI leaderboard that encourages unhealthy competition. Instead, the CCO should help build recognition for responsible AI multipliers: employees who find a better way to do their work, disclose it, help validate it, and enable the company to scale it safely. This turns AI governance from a prohibition system into an integrity system. Employees are not just being told what not to do. They are being recognized for helping the company do better.

In compliance terms, that means rewarding employees who:

  • Identify a safe AI workflow that improves the effectiveness of control.
  • Flag a risky AI use before harm occurs.
  • Develop a prompt that improves due diligence quality.
  • Create a monitoring workflow that identifies anomalies faster.
  • Help colleagues use approved tools properly.
  • Document limitations and human review requirements.
  • Share lessons learned from AI experimentation.

Treat Disclosure as a Contribution

One of the article’s most powerful points is that the manager’s reaction in the first thirty seconds after an employee discloses an AI workflow may be the decisive trust signal. If the employee is treated as though they cut corners, they learn to hide. If the disclosure is treated as something worth understanding, they learn that disclosure pays. The authors also warn that disclosure should not amount to unpaid labor; the employee should demonstrate the method once, and the company should then own the documentation, distribution, and support, while the discoverer keeps the credit. This is a direct instruction to compliance professionals.

A CCO should train managers to respond the same way. Most AI disclosures will not go to compliance first. They will happen in team meetings, performance conversations, project reviews, and manager check-ins. If local managers shame employees for using AI, employees will hide. If local managers automatically add more work to anyone who discloses a productivity gain, employees will hide. If local managers give credit and bring compliance in as a partner, employees will share.

The CCO’s AI Trust Playbook

A CCO who wants to fulfill this function should take five practical steps.

  1. Create a risk-based AI use framework. Define prohibited uses, encouraged uses, and uses requiring consultation. Make the guidance short, practical, and example-driven.
  2. Build a safe AI disclosure channel. This should be separate from the hotline in tone, even if connected administratively. Employees need a place to ask, “Can I use AI this way? ”without feeling as if they are self-reporting misconduct.
  3. Launch structured AI learning sessions. Invite employees to demonstrate useful workflows created with approved tools. Keep documentation light. Capture the use case, data inputs, review controls, risks, and adoption potential.
  4. Partner with HR on incentives. Ensure responsible AI sharing is recognized in performance reviews, promotion discussions, and leadership communications. Reward employees who become AI multipliers, not only those who quietly produce more.
  5. Report AI transparency metrics to leadership and the board. Do not only report policy completion or tool adoption. Report the number of disclosed workflows, number approved for broader use, number modified for risk reasons, number rejected, key risk themes, training gaps, and examples where disclosure improved both productivity and control.

Conclusion

The CCO should not try to own every aspect of AI. IT must own infrastructure. Cybersecurity must own security controls. Legal must advise on legal risks.  Privacy must address data protection. HR must address workforce impacts. Business leaders must own operational use cases. Internal audit must test the program. But the CCO can own the trust architecture.

The bottom line is straightforward. AI governance cannot be built only on restriction, monitoring, and fear. That approach may make the company look controlled while driving the most important AI activity underground.

The CCO has a different opportunity: to build an AI trust function that brings use cases, risks, questions, and innovations into the open. The compliance function should not be the department that says, “Do not use AI.” It should be the function that says, “Use it responsibly, show us what you are learning, and let us help the company scale it safely.” That is how compliance fulfills this function. It turns hidden AI use into visible learning, visible learning into governed practice, and governed practice into ethical business value.
Categories
Blog

The Menagerie, Part 1 – Rules, Mutiny, and the Ethics of Exceptional Compliance

Show Summary

In this article, we beam down into one of the most compelling courtroom dramas in Star Trek canon—The Menagerie, Part 1. This two-part saga is not just a creative reuse of Star Trek’s unaired original pilot (The Cage) but a deep dive into the themes of loyalty, risk, duty, and the tension between rigid compliance and ethical decision-making. When Mr. Spock commandeers the Enterprise in direct violation of Starfleet orders, fabricates communications, and defies his captain, all to bring his former commander, the incapacitated Christopher Pike, to the forbidden planet Talos IV, it sets up one of the most dramatic ethical showdowns in Starfleet history.

In today’s blog post, we examine how this episode provides rich material for compliance professionals, particularly those navigating the delicate balance between adhering to policy and upholding higher principles. We break down five core compliance lessons and link each to specific incidents in the episode that bring them to life. Along the way, we will also consider how compliance leaders can apply these lessons to build more ethical, resilient, and human-centered organizations.

1. Ethical Mutiny: When Breaking the Rules Is the Right Thing to Do

Illustrated by Spock, hijacks the Enterprise by falsifying voice commands from Captain Kirk, overrides ship controls, and charts a course to Talos IV, a planet placed under the most severe travel prohibition in Starfleet history.

This opening act is one of the most jarring in Star Trek’s history. Spock, the emblem of logic and duty, commits mutiny. And he does not hide it. After allowing Kirk and Commodore Mendez to catch up to the Enterprise, he turns himself in and demands a court-martial.

Compliance Lesson:

Doing the right thing for an individual or stakeholder may technically violate internal policy or even law. While compliance is generally rooted in the enforcement of established rules, the ethical dimension of compliance leadership sometimes calls for courage, the kind Spock displays.

For example, think of the whistleblower who exposes illegal conduct despite violating a non-disclosure agreement. Or the compliance officer who bypasses a sluggish internal protocol to alert regulators of an imminent safety risk. These are modern-day echoes of Spock’s actions.

What matters most in these scenarios is intent, proportionality, and documentation. If you break protocol to serve a higher ethical obligation, make your reasoning transparent, and be prepared to accept scrutiny. Spock did just that, and compliance professionals can learn from his model.

2. Informed Consent and the Rights of the Vulnerable

Illustrated by Captain Pike, now confined to a life-support chair following a catastrophic accident, is capable of communicating only through blinking lights, one blink for “yes,” two for “no.” Despite this profound disability, Spock makes decisions on his behalf, presumably with his blessing, to bring him to Talos IV.

Compliance Lesson:

One of the most overlooked yet essential aspects of modern compliance is ensuring that all individuals, regardless of ability or role, have the opportunity to provide informed consent. Too often, we see vulnerable populations—such as individuals with disabilities, language barriers, or economic dependence—marginalized in decision-making processes.

In Spock’s case, we are left to infer that Pike approved of the plan. However, the lack of transparency and documented consent raises important questions. In corporate settings, this would be akin to assuming a disabled or junior employee is on board with a high-risk strategy without fully briefing them or securing a formal agreement.

The key takeaway for compliance professionals is to consistently seek and document informed consent, particularly when an individual’s ability to communicate or resist is compromised. It’s not just about legal risk—it’s about human dignity.

3. Due Process and Transparency in Internal Investigations

Illustrated by Spock’s court-martial, it begins aboard the Enterprise, with Commodore Mendez presiding. Instead of denying the charges, Spock cooperates fully and presents a surprising defense—video footage from a previous classified mission to Talos IV.

Compliance Lesson:

Investigations must be conducted fairly, transparently, and supported by evidence. What makes this incident so interesting is that Spock does not simply confess; he insists on a formal process to air the whole truth. He respects Starfleet’s legal structure and uses it not to avoid punishment but to contextualize his actions.

This approach mirrors what strong compliance programs should look like: not about covering up or avoiding accountability, but about using internal mechanisms, such as hearings, audits, and investigations, to surface the truth rather than suppress it. Always remember that compliance is the guardian of institutional justice and institutional fairness.

Moreover, it emphasizes the importance of allowing investigations to run their course. By submitting himself to judgment, Spock reinforces trust in the system, even as he challenges its rigidity. Competent compliance officers will recognize that transparency and integrity go hand in hand—even during a breach.

4. Data Use, Privacy, and Chain of Custody

Illustrated by: The footage Spock presents to the court-martial board is revealed to be an unauthorized transmission from Talos IV, one of the most tightly controlled sources of information in the galaxy. The footage itself is emotionally charged and deeply personal, raising questions about how it was obtained and used.

Compliance Lesson:

This is a prime example of modern data privacy risks. In today’s world, this would be akin to accessing and sharing confidential patient or employee data without formal approval, even if done with good intent. For compliance professionals, the lesson is clear: the ethical use of data requires a secure chain of custody, limited access, and an articulated purpose. Even benevolent motives, such as restoring dignity to a suffering colleague, do not justify breaching established data protections. If the situation is exceptional, escalation to legal or ethics committees is essential.

5. Leadership Accountability and Ethical Stewardship

Illustrated by Kirk being blindsided by Spock’s actions and struggling with the realization that someone he trusts deeply has broken the chain of command. Yet, Kirk doesn’t retaliate in anger. He allows the investigation to proceed, listens to the evidence, and reflects carefully before responding.

Compliance Lesson:

This is a case study in mature leadership. Compliance leaders are often put in the uncomfortable position of adjudicating actions by trusted colleagues. Emotional responses, especially when loyalty is called into question, can cloud judgment. Kirk’s restraint is a model for those faced with internal breaches by high performers or close allies. Accountability does not mean vengeance; it means ensuring the rules apply equally and fairly, even when your friends are involved. Ethical stewardship encompasses empathy, clarity, and responsibility.

Final ComplianceLog Reflections

The Menagerie, Part 1, is not just a legal drama in space; rather, it is a parable about leading with principle in the face of policy. Spock’s decision to violate orders in the service of a higher ethical goal challenges us to ask, “What do we do when the rules are wrong?” When does policy block compassion? When does protocol punish empathy? Compliance professionals are uniquely positioned at this crossroads every day. And while very few of us will hijack a starship in the name of justice, we will all face situations that test whether we are rule followers or ethical leaders. Let Spock’s courage and Kirk’s humility remind us that compliance is not about blind enforcement. It is about ethical discernment, moral courage, and doing right by people, even when it means breaking the mold.

Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha

Categories
Everything Compliance

Everything Compliance: New Season – The Government Misfires Edition

Welcome to a revamped Everything Compliance! We have a new host, Adam Turteltaub, and a new panelist, Rebecca Walker, who joins returning regulars Matt Kelly, Jonathan Armstrong, and Karen Moore for the next iteration of Everything Compliance.

  • Jonathan Armstrong discusses BP’s leadership upheaval, shareholder ESG concerns, and recurring governance and tone-at-the-top issues, highlighting UK directors’ duties under Section 172 of the Companies Act.
  • Karen Moore reviews IBM’s $17M DOJ False Claims Act settlement tied to alleged DEI-related practices, outlining the recent enforcement scaffolding, key alleged program elements, and ongoing risks beyond the settlement.
  • Matt Kelly summarizes DOJ remarks on “algorithmic antitrust” risk, citing the RealPage litigation and warning that shared AI pricing tools can constitute cartel behavior, with heightened whistleblower incentives.
  • Rebecca Walker explains the EU’s April 21, 2026, anti-corruption directive, which harmonizes offenses across 27 member states, including private bribery and “trading in influence,” large turnover-based penalties, and expected national transposition. The episode closes with brief shout-outs, rants, and themes of compliance culture.

The members of Everything Compliance are:

The award-winning Everything Compliance is a part of the Compliance Podcast Network.

Categories
Trekking Through Compliance

Trekking Through Compliance: Episode 11 – Compliance Lessons from Menagerie, Part 1

In this episode of Trekking Through Compliance, we consider the episode The Menagerie (Part One), which aired on November 17, 1966, Star Date 3012.4.

Story Synopsis

This was the original pilot episode presented to NBC. Set in 2267, the Enterprise arrives at Starbase 11 in response to a subspace call Spock reported receiving from the former captain of the Enterprise, Christopher Pike, under whom Spock had served. Pike cannot move or communicate except by answering yes/no questions with a device operated by his brainwaves. Pike refuses to communicate with anyone except Spock.

Spock, meanwhile, commandeers the Enterprise using falsified recordings of Kirk’s voice and orders the ship to depart under the computer’s control. After several hours, upon learning from the computer that the shuttlecraft lacks enough fuel to return to the starbase, Spock brings them aboard and surrenders, confessing to mutiny. Mendez convenes a hearing, at which Spock requests an immediate court-martial, which requires the presence of three command officers. The tribunal begins, and Spock offers, as his testimony, what appears to be video footage of the Enterprise’s earlier visit to Talos IV in 2254.

In 2267, the scene is interrupted by a message from Starfleet Command, revealing that the images they have been viewing were transmitted from Talos IV. Mendez is placed in command of the Enterprise, but Spock begs Kirk to see the rest of the transmission.

Key highlights:

1. Ethical Mutiny—When Following the Rules Would Break the Mission

🖖 Illustrated by: Spock falsifying orders and commandeering the Enterprise to take Pike to Talos IV.

Spock’s act is textbook mutiny—yet deeply principled. He disobeys protocol to serve the well-being of a former captain who can no longer speak for himself. This parallels real-world dilemmas in which compliance officers must advocate for doing the right thing, even when it contradicts rigid procedures.

2. Whistleblowing with Intent—The Value of Transparent Testimony

🖖 Illustrated by: Spock turning himself in and requesting a formal court-martial to reveal the truth.

Rather than flee or hide from his actions, Spock insists on full transparency, even when the consequences may include imprisonment or execution. Compliance professionals must champion this level of courageous transparency, especially in internal reporting environments.

3. Disability Rights and Inclusion—The Silent Voice Must Still Be Heard

🖖 Illustrated by: Captain Pike communicating only via a blinking light system—yes or no responses.

Despite his physical limitations, Pike’s agency and dignity are respected—especially by Spock. Compliance officers should consider how their programs support employees with disabilities, from accessible reporting channels to inclusive policy design.

4. Data Privacy and Consent—Who Has the Right to Reveal Personal History?

🖖 Illustrated by: Spock transmitting footage of Pike’s original mission to Talos IV as part of his defense.

The court is shown deeply personal footage without Pike’s verbal consent. Companies must walk a fine line between disclosure and discretion, particularly when reputations or protected personal information are involved.

5. Navigating Conflicts Between Law and Ethics—The Role of Judgment in Compliance

🖖 Illustrated by: Spock knowingly violating Starfleet’s highest general order to save Pike from a life of suffering.

Talos IV is strictly off-limits. Spock knows this. Yet he also knows that Talos IV is the only place where Pike can live in peace and happiness. The best compliance leaders prepare teams to apply judgment, not just rules, when navigating moral gray zones.

Final Starlog Reflections

“The Menagerie, Part 1” is one of the most powerful episodes in Star Trek canon, not for its action, but for its ethical implications. It reminds us that sometimes the greatest compliance hero is not the one who follows every rule but the one who understands when rules must bend to protect justice, human dignity, and long-term integrity.

Compliance is not about obedience; it’s about stewardship. Spock may have committed mutiny, but he also modeled moral courage, transparent reporting, and respect for the voiceless. And in that, he speaks volumes to us all.

Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha⁠

Timothy is an AI generate voice.

Categories
Blog

The Corbomite Maneuver: Leadership and Compliance Under Pressure

Show Summary

Today, we explore The Corbomite Maneuver, which is an early and foundational entry in the Star Trek canon that delivers timeless lessons in leadership, ethics, and composure in the face of unknown threats. When the Enterprise encounters a mysterious cube in space and later faces what appears to be certain destruction from the intimidating alien Balok, Captain Kirk takes a calculated risk: a fictitious counter-threat called the “Corbomite Device” to de-escalate the situation.

This high-stakes bluff reveals more than Kirk’s cunning. It is a masterclass in compliance risk management, ethical leadership in complex situations, and the importance of making calm, informed decisions. We unpack how compliance professionals can apply the same principles to navigate regulatory scrutiny, third-party threats, and stakeholder tension.

Key Highlights and Compliance Case Illustrations

1. Managing Crisis with Composure—Don’t Panic, Analyze 

Illustrated by: The crew’s first reaction to the mysterious cube blocking their path.

When the Enterprise is stopped cold in space, Sulu and Bailey urge immediate action. But Kirk, demonstrating leadership, keeps his cool and gathers intel. Compliance professionals often face sudden regulatory inquiries, whistleblower complaints, or media attention. Like Kirk, your first move should be to assess rather than react impulsively.

2. Strategic Communication—The Power of a Thoughtful Bluff

Illustrated by: Kirk inventing the Corbomite Device to convince Balok that attacking the Enterprise would be suicidal.

This moment underscores the importance of narrative control. While outright deception isn’t a compliance tool, shaping how risks are framed, both internally and externally, is critical. Kirk’s bluff is a metaphor for utilizing reputational capital, a strong legal posture, and clear communication to deter bad actors and de-escalate threats.

3. Leveraging Limited Resources—Your Compliance Program Doesn’t Have to Be Perfect to Be Effective

Illustrated by: Kirk making decisions with only seconds to act, minimal data, and no superior officers available.

Compliance professionals rarely have perfect information, an infinite budget, or full executive buy-in. However, by utilizing existing tools creatively, such as incident response protocols or audit data, they can establish credible defenses and deliver timely interventions. As Kirk demonstrates, resourcefulness always beats paralysis.

4. Team Dynamics and Empowerment—Trusting Expertise Under Pressure

Illustrated by: Kirk pushing Bailey to grow, even as he struggles with the stress of command decisions.

Bailey’s emotional reactions highlight the stress compliance officers and mid-level managers face. But Kirk doesn’t bench him. Instead, he coaches him. For compliance leaders, developing team readiness through cross-training, scenario planning, and communication drills pays off when real crises hit.

5. Ethics in Action—Showing Mercy When You Have the Upper Hand

Illustrated by: Kirk choosing to rescue Balok after disarming the threat, rather than leaving him stranded.

After bluffing their way out of danger, the Enterprise crew discovers Balok is testing them. Instead of retaliation, Kirk chooses diplomacy and assistance. Compliance programs must not just prevent misconduct. They should also model ethical leadership. Whether dealing with a whistleblower, a supplier in breach, or a competitor in distress, taking the high road builds long-term trust.

Final ComplianceLog Reflections

The Corbomite Maneuver reminds us that, at heart, compliance professionals are explorers—charting the unknown, managing reputational risk, and resolving tension through intellect, strategy, and ethics. The strongest programs aren’t built on fear—they’re built on leadership under pressure.

So next time you are in the regulatory crosshairs or facing a third-party threat, remember Kirk’s example: steady the ship, evaluate the odds, and trust your training. Sometimes, the best defense is confidence backed by credibility.

Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha

Categories
Great Women in Compliance

Great Women in Compliance: Raising the Bar on Compliance Training

What makes compliance training actually work in 2026? It has come a long way from the days when simply having a training program was considered enough. In this episode, Lisa talks with Kirsten Liston, CEO and Founder of Rethink Compliance, to discuss how expectations for compliance training have evolved over the past two decades and what organizations should be thinking about today. Kirsten discusses her experience in the compliance learning space and shares insights from her recent white paper, “Raising the Bar: A New Standard for Compliance Training.” She reflects on the best ways to create training that is engaging, relevant, and capable of driving real impact in organizations of any size.

Kirsten and Lisa discuss the growing focus on engagement and effectiveness, the challenges of reaching global audiences while maintaining consistency, and the importance of helping employees understand why ethics and compliance matter rather than focusing on the rules. They look ahead to the role AI plays now and will play in the future of compliance learning and why, even as technology advances, human-centered communication remains essential. This conversation offers both a look back at how the field has changed and practical insights for compliance professionals seeking to ensure their training programs continue evolving to meet their unique organizational needs.

Categories
Trekking Through Compliance

Trekking Through Compliance: Episode 10 – The Corbomite Maneuver and Leadership Under Pressure

In this episode of Trekking Through Compliance, we consider the episode “The Corbomite Maneuver, ” which aired on November 10, 1966, with a Star Date of 1512.2.

Novice navigator Lt. Dave Bailey spots a giant spinning multi-colored cube floating in space. He advocates attacking it with phasers. Kirk instead orders the ship to back away from the object. The cube pursues them, emitting harmful radiation, and Kirk reluctantly destroys it. After that, a gigantic glowing sphere approaches the Enterprise, explaining that the destroyed cube was a border marker and that the First Federation will destroy the Enterprise for trespassing into their territory. Kirk tries to bluff Balok, telling him that the Enterprise contains “corbomite,” which automatically destroys any attacker.

Kirk, McCoy, and Bailey form a boarding party to render assistance. They beam over and discover that the “Balok” on their monitor is an effigy. The real Balok, looking like a hyperintelligent human child, enthusiastically welcomes them aboard. He explains that he was merely testing the Enterprise and its crew to discover their true intentions. As Kirk and his crew relax, Balok expresses his desire to learn more about humans and their culture, suggesting that they allow a crew member to remain on his ship as an emissary of the Federation. Bailey happily volunteers, and Balok gives them a tour of his ship.

Key highlights:

1. Managing Crisis with Composure—Don’t Panic, Analyze

🖖 Illustrated by: The crew’s first reaction to the mysterious cube blocking their path.

When the Enterprise is stopped cold in space, Sulu and Bailey urge immediate action. Like Kirk, your first move should be to assess rather than react impulsively.

2. Strategic Communication—The Power of a Thoughtful Bluff

🖖 Illustrated by: Kirk inventing the Corbomite Device to convince Balok that attacking the Enterprise would be suicidal.

This moment underscores the importance of narrative control. Kirk’s bluff is a metaphor for utilizing reputational capital, a strong legal posture, and clear communication to deter bad actors and de-escalate threats.

3. Leveraging Limited Resources—Your Compliance Program Doesn’t Have to Be Perfect to Be Effective

🖖 Illustrated by: Kirk making decisions with only seconds to act, minimal data, and no superior officers available.

Compliance professionals rarely have perfect information, an infinite budget, or full executive buy-in. As Kirk demonstrates, resourcefulness always beats paralysis.

4. Team Dynamics and Empowerment—Trusting Expertise Under Pressure

🖖 Illustrated by: Kirk pushing Bailey to grow, even as he struggles with the stress of command decisions.

Bailey’s emotional reactions highlight the stress compliance officers and mid-level managers face. For compliance leaders, developing team readiness through cross-training, scenario planning, and communication drills pays off when real crises hit.

5. Ethics in Action—Showing Mercy When You Have the Upper Hand

🖖 Illustrated by: Kirk chooses to rescue Balok after disarming the threat rather than leaving him stranded.

After bluffing their way out of danger, the Enterprise crew discovers Balok is testing them. Instead of retaliation, Kirk chooses diplomacy and assistance. Compliance programs must not just prevent misconduct—they should also model ethical leadership.

Final Starlog Reflections

The Corbomite Maneuver reminds us that, at heart, compliance professionals are explorers, charting the unknown, managing reputational risk, and resolving tension through intellect, strategy, and ethics. The strongest programs are not built on fear of violating the law but on leadership under pressure.

So next time you are in the regulatory crosshairs or facing a third-party threat, remember Kirk’s example: steady the ship, evaluate the odds, and trust your training. Sometimes, the best defense is confidence backed by credibility.

Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha

Timothy is an AI-generated voice

Categories
Blog

Why Compliance Gets Branded as the Problem

Every compliance professional has heard the accusation. Compliance is too slow. Compliance does not understand the business. Compliance always says no. Compliance is where deals go to die. That reputation is so common that it has a shorthand: “Dr. No from the Land of No.”

Luis Velasquez’s article, Why Effective Leaders Get Branded as Problems, offers an important way for Chief Compliance Officers to think about this challenge. His central point is that when a leader creates friction, organizations often default to one explanation: the leader is the problem. Yet the article argues that friction usually comes from one of four sources: capability, perception, identity, or system. Because those sources may appear similar on the surface, organizations often collapse them into a single behavioral judgment, leading to poor decisions.

That insight maps directly onto compliance. When compliance creates friction, the organization may assume the compliance function is the problem. Sometimes that is true. Sometimes compliance really is slow, unclear, inconsistent, or disconnected from commercial reality. But often, compliance is not the problem. It is exposing the problem. The CCO’s job is to know the difference.

The Evaluation Trap for Compliance

Velasquez calls this dynamic the “evaluation trap.” Organizations overfocus on visible behavior and underweight the context surrounding it. If there is friction, the easy assumption is that the individual leader is the problem. For compliance, the same trap appears when business leaders say some of the following: “Compliance is blocking the deal. Compliance is slowing us down. Compliance is too rigid. Compliance does not understand how we make money.”

Those statements may contain useful feedback, but they are not a diagnosis. They are conclusions. A good CCO should not reject them defensively, but neither should the CCO accept them at face value. The better question is, “What is really causing the friction?”

Is compliance creating unnecessary delays? Is the business bringing compliance in too late? Is the policy unclear? Is the company’s incentive structure encouraging people to push risk downstream? Is the compliance team applying yesterday’s reputation to today’s improved process? Or is the function’s greatest strength, independence, being overused in a way that makes compliance appear detached from the business? The answer matters because each cause requires a different response.

Why “The Land of No” Is Dangerous

Being known as “The Land of No” is more than a branding problem. It is a control problem. When employees believe compliance exists only to stop things, they stop bringing compliance into decisions early. They delay disclosure. They frame facts selectively. They look for workarounds. They ask for forgiveness instead of guidance. The compliance function then receives issues late, with fewer options and higher stakes. That reinforces the perception that compliance is always saying no.

It becomes a vicious cycle. The business avoids compliance because it fears delay. Compliance receives incomplete or late information. Compliance responds with concern or rejection. The business concludes that compliance is a blocker. The next time, the business waits even longer to engage. That is how a compliance function loses influence while still technically having authority.

The Four Sources of Compliance Friction

Velasquez identifies four sources of leadership friction: a true skill deficit, historical reputation, overextension of identity, and the system as a blocker. Each has a direct compliance equivalent.

1. A True Compliance Capability Deficit

Sometimes the criticism is fair. The compliance team may be too slow. It may issue dense legal guidance that no one can use. It may give inconsistent answers across regions. It may lack business knowledge. It may escalate too many routine issues. It may have no clear intake process, no service-level expectations, no decision trees, and no practical playbooks.

The remedy is operational discipline. Build intake channels. Publish response-time expectations. Create risk-tiered approval paths. Train compliance professionals in business acumen. Give the business practical guidance, not abstract warnings. Measure cycle time, quality of advice, repeat questions, escalation frequency, and stakeholder satisfaction. A compliance function that wants credibility must be professionally managed.

2. Historical Reputation

Sometimes, compliance is judged by an old story. Velasquez describes “organizational drift,” where systems rely on outdated narratives rather than current evidence. Feedback may be based on historical reputation rather than recent interactions. Labels harden even when behavior changes.

In that case, behavior change alone may not be enough. The CCO must manage perception as deliberately as performance. That means asking business leaders for specific, recent examples. It means distinguishing current pain from legacy frustration. It means documenting improvements and communicating them repeatedly. It means publicizing examples where compliance helped a team win business the right way, accelerate a transaction, resolve a third-party issue, or design better controls.

3. Overextension of Compliance Identity

Compliance has core strengths: independence, skepticism, discipline, documentation, escalation, and control. Those strengths are essential. But Velasquez warns that a strength can become a habit, then an identity, and then a constraint. The problem is not always the absence of skill; sometimes it is the overuse of a strength in the wrong context. That is a powerful lesson for compliance.

A compliance function that is appropriately skeptical in a bribery investigation may be unnecessarily skeptical in a low-risk gift review. A team that properly demands documentation for a high-risk distributor may over-document a routine vendor. A CCO who must be firm with the board or regulators may unintentionally use the same posture in early-stage business counseling. The answer is not to weaken compliance. The answer is to expand its range.

Compliance should know when to be an investigator, an adviser, a control designer, an educator, and a decision escalater. Not every question requires the same tone, process, or level of scrutiny. A mature compliance function does not say yes to everything. It knows how to say “Yes, if.” That is very different from simply saying no.

4. The System as the Blocker

Velasquez calls the system-as-blocker issue the most misunderstood trap. What looks like a behavior problem may actually be caused by culture, structures, resources, incentives, or decision rights that make the desired behavior difficult to achieve. The article notes that organizations may say they want one thing while rewarding another. This is the most important lesson for the CCO.

Compliance is often blamed for delays caused elsewhere. Sales may bring a high-risk intermediary into compliance two days before a bid deadline. Procurement may onboard vendors before due diligence is complete. Finance may discover payment issues only after an invoice is pending. Legal may escalate a contract after commercial terms have already been promised. Senior leadership may say compliance matters, while compensation plans reward speed and revenue at any cost.

In reality, the system created the bottleneck. Compliance was simply the first function willing to name it. The CCO should identify these systemic blockers and bring them to management. If the business wants faster third-party approvals, it must engage compliance earlier. If the company wants fewer rejected transactions, it must define risk appetite before the deal is negotiated. If leadership wants a speak-up culture, it must protect reporters and discipline those who retaliate. If the

Building a Compliance Function Known for Solutions

The goal is not to become the “Land of Yes.” That would be worse. A compliance function that says yes to everything is not a compliance function. It is a permission slip. The goal is to become the Land of Know: a place where businesses gain clarity, options, risk intelligence, and practical pathways. That requires a different operating model.

  1. Compliance must engage early. The function should be embedded in strategy discussions, product design, market entry planning, third-party selection, M&A activity, data use, AI deployment, and incentive design. Late-stage compliance review is where trust goes to die.
  2. Compliance must define red lines and green lanes. Business teams should know which activities are prohibited, which require escalation, and which can move quickly through preapproved controls. Ambiguity produces both delay and resentment.
  3. Compliance must communicate in business language. “This violates Section X of Policy Y” may be accurate, but it is rarely sufficient. The better explanation is: “This creates an undisclosed conflict, weakens our audit trail, and could make the payment look improper. Here is how we can restructure it.”
  4. Compliance must offer alternatives. A “no” without a path forward should be reserved for real red-line issues. In most cases, compliance should identify a lower-risk route.
  5. Compliance must measure enablement. Do not only track training completions, hotline numbers, or policy attestations. Track advisory response time, time to third-party decision, percentage of matters resolved with conditions, number of early consultations, repeat issues by business unit, and examples where compliance helped preserve business value.

Sixth, compliance must own its mistakes. When compliance is slow, unclear, inconsistent, or overly rigid, the CCO should say so and fix it. Credibility increases when compliance holds itself to the same level of accountability it expects of the business.

The CCO’s Message to the Business

The CCO should be able to say, “We are not here to stop the business. We are here to help the business grow in a way that can withstand scrutiny. Sometimes that means yes. Sometimes that means yes with controls. Sometimes that means no. But every answer should be timely, clear, risk-based, and tied to the company’s values and obligations.”

That message must be backed by behavior. Business leaders will not judge compliance by slogans. They will judge it by how the function behaves when a deal is urgent, a market is risky, a senior executive is involved, or the answer is uncomfortable.

The lesson from Velasquez’s article is simple but profound. Before deciding that the leader is the problem, ask whether the diagnosis is wrong. For CCOs, the parallel lesson is equally important: before accepting that compliance is the problem, determine what the friction is really telling you.

A strong compliance function should never aspire to be popular at all costs. But it should aspire to be trusted. The way to avoid becoming “The Land of No” is not to say yes more often. It is to become clearer, earlier, more practical, more evidence-based, and more courageous about identifying whether the real issue sits in compliance, the business, or the system itself.