Ed. Note: This month, on his podcast series Popcorn and Compliance, Tom Fox dives deep into the first five Frankenstein movies. Over October, Tom Fox will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolf Man. This blog post accompanies the podcast series.
The first four Frankenstein films provide a useful progression for corporate compliance. Frankenstein examined innovation without adequate governance. Bride of Frankenstein shows leadership that understands risk but lets pressure and rationalization override judgment. Son of Frankenstein moved to inherited risk and the obligations that arise when new leadership discovers legacy problems. The Ghost of Frankenstein asks whether remediation actually works.
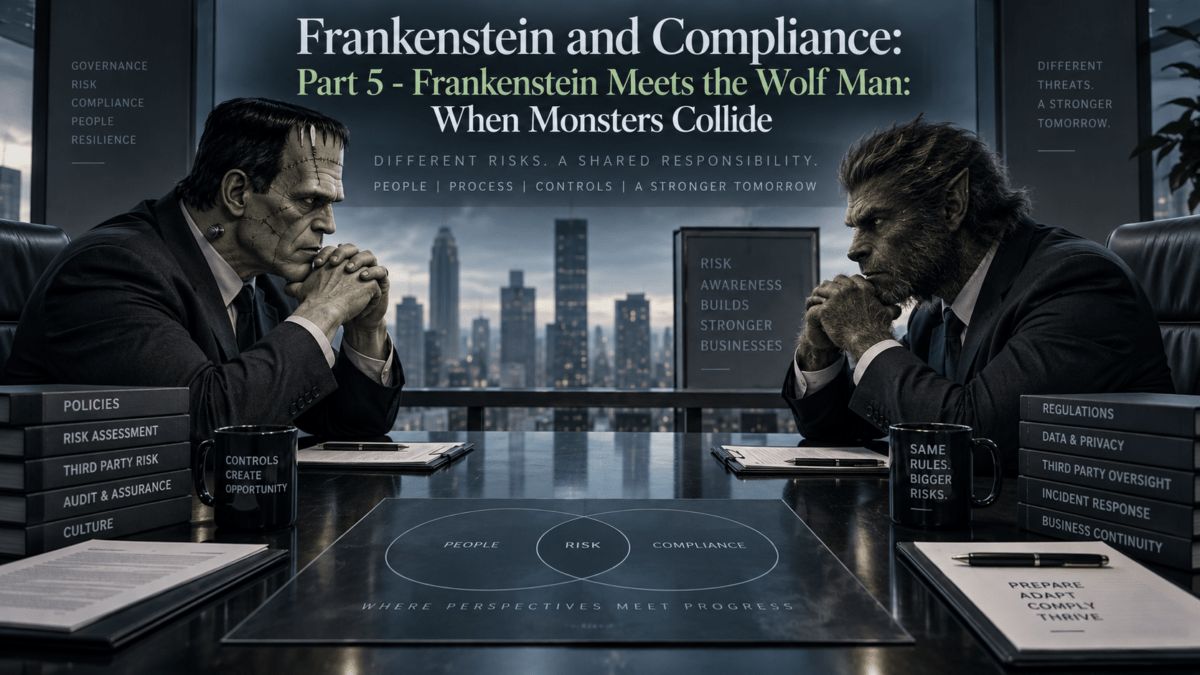
Frankenstein Meets the Wolf Man (1943) changes the risk equation. There are now two monsters. Larry Talbot, played by Lon Chaney Jr., returns from The Wolf Man seeking a way to end the curse that transforms him into a werewolf. His search eventually brings him to the ruins of Frankenstein’s castle, where he discovers the Monster, played in this film by Bela Lugosi. Talbot revives him, Dr. Mannering becomes involved, and the film eventually delivers what its title promises: Frankenstein’s Monster and the Wolf Man collide.
For corporate compliance professionals, the movie provides a useful way to think about enterprise risk. Organizations necessarily divide risk into categories and assign responsibilities to different functions. Compliance may oversee anti-corruption, sanctions, third-party, antitrust, and other regulatory risks. Information Security manages cyber risk. Privacy oversees data protection. HR manages employment-related risks. Finance owns financial controls. Internal Audit provides assurance. Enterprise Risk Management looks across the organization.
That structure is necessary. It can also create silos. The most significant corporate risks do not always remain within the categories management assigns to them. They interact. When they do, the resulting exposure may be greater than the organization sees when each risk is assessed independently. The compliance challenge is not simply identifying each monster. It is understanding what happens when they meet.
Risk Does Not Respect the Organizational Chart
Companies assign risk ownership because someone must be accountable. That is good governance. The problem begins when risk ownership becomes information ownership. Consider a third-party distributor operating in a high-risk market. Compliance may identify concerns about the distributor’s beneficial ownership. Finance may identify unusual payment requests. Information Security may detect suspicious access involving the distributor’s credentials. Internal Audit may identify invoice exceptions. Legal may become aware of litigation or regulatory concerns involving related entities. Each function may respond appropriately to the information it possesses.
Yet the organization may still fail if nobody connects those facts. The compliance issue is therefore not simply whether individual control functions are doing their jobs. It is whether the organization’s governance structure allows information to move across functional boundaries. This distinction matters more as corporate risks become more interconnected.
A cybersecurity event can become a privacy incident. A privacy incident can become a regulatory investigation. A regulatory investigation can create disclosure obligations. A third-party issue can become an anti-corruption problem, which can become a books-and-records problem, which can become a securities issue. Risk categories are useful for management. They are not boundaries that real-world events respect.
The Wolf Man and Frankenstein’s Monster Are Different Risks
One useful aspect of Frankenstein Meets the Wolf Man is that its two principal characters represent different kinds of risk. Larry Talbot understands his condition. He knows that particular circumstances trigger his transformation and that the consequences can be severe. His risk is recurring and linked to identifiable conditions. Frankenstein’s Monster represents something different. He is a legacy risk repeatedly inherited, revived, and unsuccessfully controlled by others.
Put them together and the problem changes. Companies experience similar combinations. A business may have a known third-party risk that becomes significantly more serious when combined with expansion into a high-risk jurisdiction. A weak control environment may become more consequential when management introduces aggressive sales incentives. A cybersecurity vulnerability may become more significant when the company deploys an AI system with access to sensitive information. The risks do not merely accumulate. They can amplify one another. That is why risk assessment should consider interdependencies.
Risk Aggregation Should Be Part of the Compliance Conversation
Traditional compliance risk assessments often organize risks by subject matter.
- Anti-corruption risk.
- Sanctions risk.
- Antitrust risk.
- Third-party risk.
- Privacy risk.
- Conflicts of interest.
- Books and records.
That approach is useful because it creates structure and allows organizations to identify controls and owners. It can also obscure combinations of risk. Consider a company acquiring a business in a high-risk jurisdiction. The acquisition may involve weak financial controls, substantial government interaction, a distributor-based sales model, aggressive growth assumptions, and a local culture unfamiliar with the acquiring company’s compliance expectations. Each issue may appear manageable when assessed separately. Together, they may produce a materially different risk profile.
The CCO should therefore consider adding risk aggregation to the compliance risk assessment process. Where do significant risks intersect? Which business units face several elevated risks simultaneously? Which third parties create exposure across multiple compliance areas? Which strategic initiatives combine new technology, new markets, new partners, and aggressive financial expectations? A heat map that displays risks individually may not reveal these relationships. Compliance should be able to explain not only where the red boxes are but also what happens when several red boxes occupy the same part of the business.
AI Is an Enterprise Risk Multiplier
Artificial intelligence provides one of the clearest modern examples of the problem. Companies sometimes discuss “AI risk” as though it were one category. Unfortunately, it is not. An AI deployment can simultaneously raise privacy, cybersecurity, intellectual property, employment, discrimination, consumer protection, regulatory, third-party, recordkeeping, and reputational issues.
What about an AI tool used to assist hiring decisions? HR may view it as a talent-management system. Information Security may assess the technology vendor. Privacy may examine candidate data. Legal may consider employment requirements. Compliance may evaluate governance and ethical concerns. Procurement may negotiate the contract. Every function may perform its assigned task. The organization still needs someone to evaluate the complete risk picture.
The same issue arises when AI is used for internal investigations, compliance monitoring, customer interactions, sales recommendations, financial decisions, or employee evaluation. This is why AI governance requires cross-functional management.
Frameworks such as the NIST AI Risk Management Framework and ISO/IEC 42001 are useful because they encourage organizations to think about governance, accountability, risk identification, measurement, monitoring, and continual improvement rather than treating AI exclusively as an IT issue. The central business question is not which department owns AI. It is whether the governance structure addresses the risks created by the particular use case.
The CCO Should Be a Connector, Not the Owner of Everything
The increasing interconnectedness of risk raises an important question about the CCO’s role. The answer should not be that Compliance owns every risk involving law, ethics, or reputation. That approach creates its own governance problem.
Business management owns business risk. Information Security should remain accountable for cybersecurity. HR should remain accountable for employment processes. Finance should own financial controls. Legal should provide legal advice. Internal Audit should preserve its independent assurance role. The CCO can nevertheless play an important role as a connector.
Compliance often receives information from multiple parts of the organization. Hotline reports, investigations, third-party due diligence, monitoring results, policy exceptions, training data, regulatory developments, culture assessments, and risk assessments all provide different views of organizational behavior. That perspective can allow Compliance to identify patterns that may not be visible within a single business function. The CCO should therefore ask where information needs to be shared, where cross-functional escalation is necessary, and where significant risks require joint governance. The goal is coordination without diluting accountability.
Mission-Critical Risk and Board Oversight
This also connects to the broader Marchand discussion about board oversight of significant and mission-critical risks. Directors do not need to become operational risk managers. They do need reasonable assurance that management has systems to identify significant risks and escalate material information.
For interconnected risks, that means understanding how management aggregates information.
- Which risks are sufficiently significant to require cross-functional oversight?
- How does management identify emerging combinations of risk?
- Who resolves disagreements between control functions?
- What information reaches the board?
- How are significant risks assigned when they do not fit within one organizational function?
These questions matter most when a risk is central to the company’s business model. The board does not need to manage the monsters. It needs to understand whether management can see when they are moving toward one another.
Practical Actions for the CCO
Frankenstein Meets the Wolf Man suggests several practical actions for compliance leadership. The compliance risk assessment should identify not only individual risks but also significant risk intersections. CCOs should look for business units, markets, third parties, products, and strategic initiatives where multiple elevated risks converge. Compliance should establish relationships and information-sharing mechanisms with Internal Audit, Legal, Finance, HR, Information Security, Privacy, Procurement, and Enterprise Risk Management. Significant cross-functional risks should have clear owners, escalation criteria, and decision rights.
CCOs should also consider whether existing compliance dashboards show relationships among risks or simply report individual metrics. Data from investigations, hotline reports, third-party monitoring, policy exceptions, audit findings, and other sources can become substantially more valuable when analyzed together. For emerging technologies such as AI, Compliance should participate in cross-functional governance while avoiding the temptation to own every associated risk. The objective is not centralized ownership. It is connected governance.
The Compliance Lesson
Frankenstein Meets the Wolf Man completes the compliance progression of the Universal Frankenstein films. Organizations create risks. Leadership can compromise in responding to them. New management can inherit them. Remediation can fail to eliminate them. Then those unresolved risks can interact with other risks.
That final stage matters because modern corporate risk is increasingly interconnected. AI touches privacy, cyber, employment, intellectual property, and regulatory compliance. Third-party risk can implicate corruption, sanctions, human rights, cybersecurity, and financial controls. Compensation can affect culture, sales practices, fraud risk, and books and records. No single function can manage these issues effectively on its own.
The solution is not to eliminate functional ownership. Clear accountability remains essential. The solution is to build governance mechanisms that allow information to move, risks to be considered together, and significant issues to be escalated across organizational boundaries. For the CCO, that means becoming an effective connector while preserving the accountability of the business and other control functions.
For management, it means looking beyond individual risk categories. For the board, it means ensuring that committee structures and reporting processes provide an enterprise view rather than a collection of disconnected risk reports. The ultimate lesson from Frankenstein Meets the Wolf Man is therefore not really about either monster individually. It is about interaction.
A company may understand its corruption risk. It may understand its third-party risk. It may understand its cybersecurity risk. It may understand its AI risk. It may have capable people managing each one. The question is whether anyone understands what happens when those risks meet. That is where compliance moves beyond individual rules and controls and becomes part of enterprise governance.
After five films, the Frankenstein story leaves us with a useful framework for the modern compliance program: govern what you create, learn from what goes wrong, take responsibility for what you inherit, test whether remediation works, and understand where risks intersect. Because in business, as in the movies, managing one monster is difficult enough. The real governance challenge begins when monsters collide.
Check out the podcast version and analysis of this episode of Popcorn and Compliance with Timothy and Fiona.