Categories
Blog

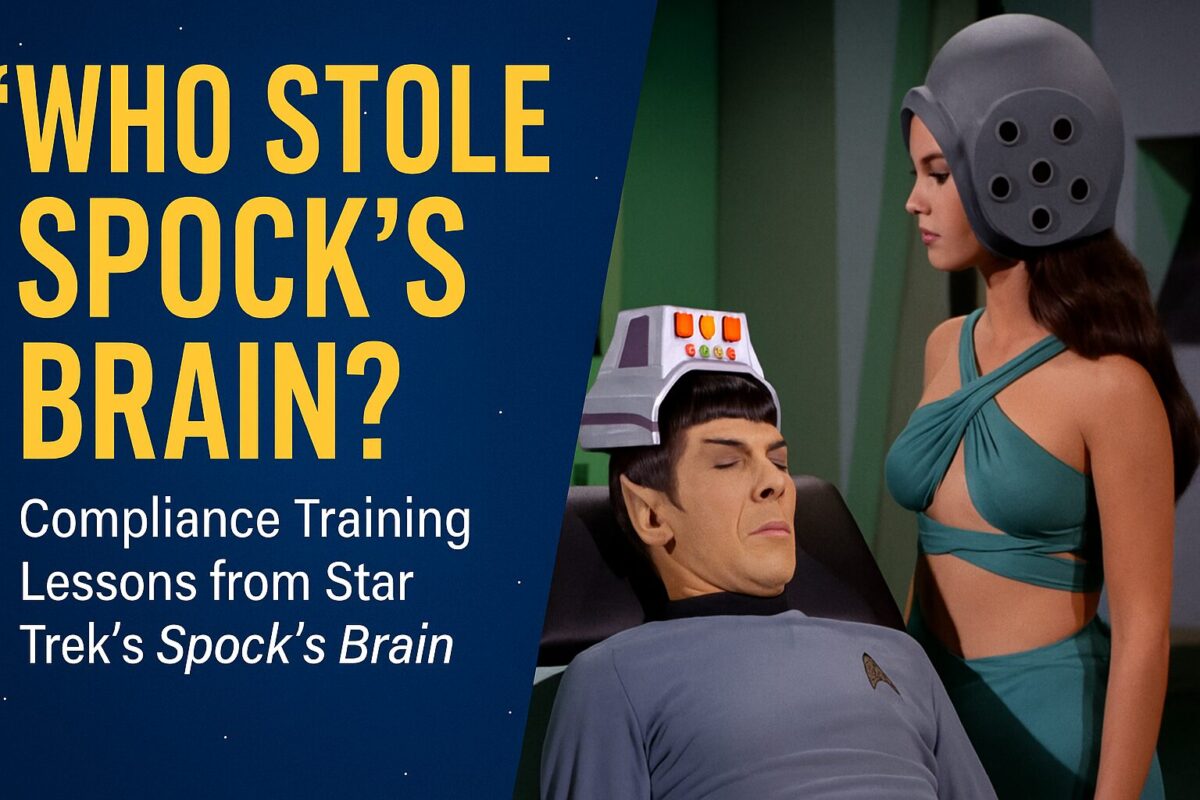
“Who Stole Spock’s Brain?” – Compliance Training Lessons from Star Trek’s Spock’s Brain

Few episodes of Star Trek: The Original Series are as infamous or as misunderstood as “Spock’s Brain.” Dismissed by many as campy science fiction, the episode nevertheless offers a wealth of practical insights for today’s compliance professionals, especially those responsible for developing, maintaining, and delivering effective compliance training programs.

Let’s boldly go where few compliance trainers have gone before and extract some valuable lessons from the Enterprise’s wild quest to retrieve Spock’s missing brain. Along the way, we will see that even the quirkiest stories can teach us how to build smarter, more resilient compliance cultures.

Setting the Stage: When the Unthinkable Happens

For those who have not watched or have not watched recently, “Spock’s Brain” begins with an incident straight out of the compliance professional’s nightmare file: an inexplicable event with catastrophic implications. An unknown intruder boards the Enterprise, incapacitates the crew, and removes Spock’s brain, leaving his body alive but inert.

Captain Kirk, Dr. McCoy, and the rest of the crew must race against time, using every available tool and resource to recover Spock’s brain before it’s too late. What unfolds is a bizarre odyssey that is part rescue mission, part leadership crucible, and, as we’ll see, a perfect metaphor for the compliance training journey.

Today, we consider five key compliance training lessons, each illustrated by a memorable scene from “Spock’s Brain.”

1. When the Unimaginable Strikes, Training Must Enable Action, Not Panic

Illustrated By: The crew awakens to chaos. Spock is incapacitated. The bridge officers, stunned and confused, look to Kirk for leadership.

Compliance Lesson: The unexpected will happen in business. Whether it’s a major regulatory change, a data breach, or a sudden ethics scandal, the initial reaction is often confusion and panic. The true test of a compliance training program is not how well it’s received during routine times, but how effectively it empowers employees to act decisively under pressure.

What should you do? Compliance training must move beyond rote memorization or check-the-box exercises. Instead, it should equip employees with the critical thinking, ethical reasoning, and procedural knowledge they need to respond effectively when the “unimaginable” occurs. Scenario-based training, simulations, and live drills can help build this kind of resilience. In short, training is about readiness, not just awareness.

2. You Can’t Train for Every Event, But You Can Teach Problem-Solving

Illustrated By: Lacking any clear leads, Kirk, McCoy, and Scotty piece together clues using technology, logic, and their collective expertise. There is no manual for “what to do when someone steals your first officer’s brain.”

Compliance Lesson: No training program can anticipate every possible scenario. Regulatory changes, market disruptions, and new types of misconduct are always around the corner. What you can train, however, is a culture of problem-solving, adaptability, and continuous learning.

What should you do? Modern compliance training should focus on building core competencies: How do we spot red flags? How do we escalate issues? Who do we call for help? By emphasizing principles over prescriptive checklists, you empower employees to adapt and innovate—even when they find themselves, metaphorically, searching for a missing piece of the puzzle.

3. Communication Bridges the Knowledge Gap

Illustrated By: The landing party discovers a society split in two: the technologically advanced women who control the planet’s systems, and the men, who live in primitive conditions below. The women possess “the knowledge,” delivered via a helmet-like teaching device, which bestows instant expertise but only temporarily.

Compliance Lesson: The episode’s iconic “teaching helmet” is a comical take on knowledge transfer, but it highlights a real challenge: bridging the gap between compliance expertise and employee understanding. Compliance training can’t simply “download” knowledge into employees’ minds; it requires communication, repetition, and reinforcement.

What should you do? Effective compliance programs use plain language, relatable stories, and multi-modal training (videos, workshops, microlearning) to make complex requirements understandable. And like the helmet, real-world learning is most powerful when it’s immediately relevant to employees’ jobs; just-in-time training, delivered at the point of need, can bridge gaps more effectively than annual courses.

4. Just-in-Time Training—When You Need It Most

Illustrated By: Faced with the daunting task of reattaching Spock’s brain, Dr. McCoy uses the teaching helmet to acquire the necessary surgical skills. He gains instant, but fleeting, expertise enough to attempt the operation, but not enough to complete it without help.

Compliance Lesson: Compliance knowledge, like McCoy’s surgical skills, is often perishable. Employees may learn something in training but forget it when months have passed or when stress levels are high. The best compliance programs recognize this and provide “just-in-time” resources, such as quick-reference guides, FAQs, and on-demand training, for when employees need to take action.

What should you do? Consider building a compliance “knowledge base” accessible to all employees, with short, targeted modules or “how-to” videos for high-risk tasks. Reinforce training with periodic reminders and prompts. And don’t be afraid to re-train in the moment; support employees when they’re “in the operating room,” not just once a year.

5. Teamwork and Psychological Safety Are the Real Secret Sauce

Illustrated By: With Spock’s brain reconnected, he awakens mid-surgery and begins to talk McCoy through the final steps. Kirk, McCoy, and Spock work together seamlessly, overcoming their limitations by relying on each other’s strengths.

Compliance Lesson: The ultimate success of the mission does not rest on the brilliance of any one individual. It is the product of a team that trusts each other, communicates openly, and isn’t afraid to admit when they’re out of their depth. Effective compliance training fosters a similar sense of psychological safety.

What should you do? Employees should feel safe asking questions, raising concerns, and admitting knowledge gaps. Training should encourage discussion and feedback, rather than relying solely on one-way lectures. When compliance becomes a shared journey, employees support each other, fill in knowledge gaps, and ultimately make better decisions, especially when the stakes are high.

Final ComplianceLog Reflections

“Spock’s Brain” may not win any awards for scientific realism or dramatic subtlety, but its outlandish premise serves as a powerful allegory for the daily realities of corporate compliance training. Unexpected risks will arise. Knowledge will lapse. Sometimes, you will need to act with incomplete information and under enormous pressure.

The crew of the Enterprise prevails not because they followed a script, but because they were trained, through experience, teamwork, and relentless problem-solving, to adapt and respond to the unknown. The same should be true of your compliance training program.

The world of compliance, like the universe of Star Trek, is full of strange new worlds and unexpected dangers. As compliance professionals, we can learn much from Kirk, McCoy, and Spock, not just about courage and leadership, but about how to prepare our crews for whatever lies ahead.

A training program inspired by the lessons of “Spock’s Brain” will not only teach the rules but empower employees to act ethically and effectively when it matters most. And that, ultimately, is how we boldly go forward together.

Resources:

⁠⁠Excruciatingly Detailed Plot Summary by Eric W. Weisstein⁠⁠

⁠⁠MissionLogPodcast.com⁠⁠

⁠⁠Memory Alpha

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Citibank and Continuous Monitoring

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our goal is to provide you with bite-sized, actionable tips to help you stay ahead in your compliance efforts. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today, we consider how Citibank used continuous monitoring as an AML tool.

For more information on this topic, refer to The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, 6th edition, recently released by LexisNexis. It is available here.

Categories
Blog

Setting the Tone: Why Top-Level Commitment Is the Heart of Fraud Prevention

In today’s rapidly evolving compliance landscape, one principle has become abundantly clear: effective fraud prevention starts at the top. The Economic Crime and Corporate Transparency Act 2023, with its new offense of failure to prevent fraud, has elevated the expectations for senior leadership and boards across large organizations. Fortunately, the UK government has put out a document entitled “Economic Crime and Corporate Transparency Act 2023: Guidance to organisations on the offence of failure to prevent fraud.” (The Guidance). Section 3.1 of the official guidance, titled “Top Level Commitment,” should be required reading for every compliance professional seeking to build a credible, defensible, and sustainable anti-fraud culture. Today, we take a deep dive into what a top-level commitment is.

The Imperative: Leadership’s Role in Preventing Fraud

Section 3.1 places the responsibility for preventing and detecting fraud squarely on those charged with governance, including the Board of Directors, partners, and senior management. This is not simply a perfunctory statement. The Guidance makes it clear: without authentic buy-in and leadership from the very top, even the best-written policies and controls will falter.

A culture of zero tolerance for fraud must be more than a slogan. The board and senior management must actively foster an environment where fraud is not only discouraged but also considered unthinkable, where profit derived from or assisted by fraud is unequivocally rejected.

Visible Commitment: Not Just Words, But Deeds

What does genuine top-level commitment look like? The Guidance offers a clear framework. It is about visible, consistent action that resonates throughout the organization. This includes:

  • Publicly rejecting fraud, even at the cost of lost business opportunities. Boards and executives must demonstrate that they will walk away from deals if the price compromises their integrity and values.
  • Explaining the business benefits of a strong anti-fraud posture. Protecting the company’s reputation, building trust with customers and business partners, and ensuring long-term sustainability are tangible, valuable outcomes.
  • Backing policies and codes of conduct with consequences. There must be clarity about what happens if someone breaches anti-fraud policies—up to and including contractual and disciplinary action.
  • Acknowledging and endorsing collective anti-fraud efforts. Participation in industry initiatives or trade body actions against fraud demonstrates seriousness of intent.

A leadership statement is only credible if it is backed by real accountability, named roles, and continuous communication.

Governance: Structuring Responsibility for Real Results

Clear governance is the backbone of any fraud prevention framework. Section 3.1 stresses that organizations should define, document, and communicate who is responsible for every aspect of fraud prevention, from risk assessment to whistleblowing, and from detection to disciplinary actions.

Best practice governance includes:

  • Designated responsibility for horizon scanning, risk assessment, policy development, disciplinary action, whistleblowing, investigation, and ongoing review.
  • Direct access for compliance leadership to the board or CEO, even if day-to-day reporting is elsewhere. This ensures critical issues don’t get buried in middle management.
  • Documentation of decisions and actions. Board minutes should capture key compliance decisions, risk reviews, and follow-up actions.
  • Succession planning for compliance leadership. Governance should account for staff turnover and ensure continuity in anti-fraud efforts, even when key personnel are absent or leave the organization.

In some organizations, the board or senior executives will be personally involved in designing fraud prevention measures; in others, they will delegate this responsibility to the Head of Ethics and Compliance while retaining ultimate accountability. The key is active engagement and oversight.

Commitment to Resources: Funding and Training

Fraud prevention is not a costless endeavor. The guidance is explicit: senior management must allocate a reasonable and proportionate budget for compliance leadership, fraud prevention staff, training, and technology, including due diligence tools and platforms. This budget commitment must be sustained for the long term, not just as a one-off initiative.

Training is equally crucial. Senior management must champion not only initial training but also ongoing refreshers and updates, ensuring that all staff, especially those in high-risk roles, are equipped to identify and prevent fraud. Resilience is key: anti-fraud practices must be maintained even when staff are on vacation, sick leave, or when there is turnover.

Leading by Example: The Tone at the Top

The “tone at the top” is more than a catchphrase; it is the bedrock of ethical culture. Senior managers must embody the standards they expect from the rest of the organization. This means:

  • Openly challenging rationalizations for fraud. Whether it’s “everyone does it,” “it’s not material,” or “it’s for the good of the business,” these are dangerous myths that must be confronted.
  • Encouraging early reporting of concerns. Leadership should foster an open culture where staff feel empowered to speak up, no matter how minor the issue may seem. The earlier a problem is raised, the less likely it will snowball into a major scandal.
  • Making ethics a daily practice, not a quarterly campaign. Whether through regular reminders, integration into performance evaluations, or simply modeling the right behaviors, leaders set the ethical weather for the company.

Communication: Reinforcing the Anti-Fraud Message

Top-level commitment must be communicated consistently and credibly to all key audiences, including employees, contractors, agents, suppliers, and business partners. The guidance recommends tailoring the message for different stakeholders; what resonates with employees may differ from what is relevant for contractors or vendors.

Effective anti-fraud communication should:

  • Highlight the organization’s commitment to integrity over short-term gains.
  • Reinforce the real-world consequences of violating anti-fraud policies.
  • Regularly spotlight examples of ethical leadership, transparency, and collective action against fraud.

The Importance of Whistleblowing

Section 3.1 places significant emphasis on whistleblowing—not only establishing clear channels but also creating a culture where speaking up is encouraged and protected. Senior management should ensure:

  • There are safe, independent channels for reporting concerns.
  • Whistleblowers are protected from retaliation.
  • Reports are acted on quickly and transparently.

A strong whistleblowing culture indicates that leadership is committed to identifying and addressing problems before they become systemic.

The “Why” Behind Top-Level Commitment

Why is all of this so critical? Because fraud is adaptive. It thrives in ambiguity, and it flourishes when leadership is distracted, disinterested, or inconsistent. The Economic Crime and Corporate Transparency Act 2023 raises the stakes: organizations now face not just reputational and commercial damage, but also criminal liability if they cannot demonstrate that their prevention procedures were reasonable and implemented with genuine top-level commitment.

The regulators and prosecutors will look for evidence of this commitment. Are senior managers personally invested? Do they walk the talk? Can they demonstrate, with documentation, that anti-fraud policies are embedded in the organization’s DNA?

Practical Steps for Compliance Professionals

What should compliance professionals do today?

  1. Engage with your board and C-suite. Make sure they understand their personal and collective responsibilities under the Act.
  2. Audit your current governance structures. Identify gaps in accountability, communication, or resource allocation.
  3. Refresh your anti-fraud messaging and training. Ensure it is regular, targeted, and endorsed by top management.
  4. Enhance your whistleblowing framework. Benchmark it against best practices and ensure visible support from leadership.
  5. Document everything. If it’s not written down, it didn’t happen. Ensure that minutes, decisions, and compliance actions are accurately recorded.

Conclusion: Leadership Sets the Standard

Section 3.1 is clear: fraud prevention is not just the job of compliance or internal audit. It is the duty of those at the top. Authentic leadership means investing in people, systems, and culture; communicating a vision of integrity; and never wavering, even when the pressure to bend the rules is immense.

For the modern compliance professional, this is both a challenge and an opportunity. With exemplary leadership, organizations can move beyond reactive compliance and build an enduring culture where ethical conduct is the norm and fraud has no place to hide.

Join us tomorrow, where we will consider a fraud risk assessment.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Crowd Sourcing Risk Intelligence

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our goal is to provide you with bite-sized, actionable tips to help you stay ahead in your compliance efforts. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today, we consider how you can use your data to crowdsource your risk intelligence.

For more information on this topic, refer to The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, 6th edition, recently released by LexisNexis. It is available here.

Categories
Blog

Rethinking Compliance: Practical Steps for Adapting to the UK’s New Failure to Prevent Fraud Legislation

The introduction of the Economic Crime and Corporate Transparency Act 2023, specifically the offense of failure to prevent fraud (FTPF), takes effect on 1 September 2025. Every US company doing business in the UK or with UK companies must be aware of this law and its implications for them. The jurisdiction is as broad as or even broader than the US Foreign Corrupt Practices Act (FCPA). Corporate compliance professionals are finding themselves in uncharted territory with this new legal framework, requiring a thorough understanding of how this legislation applies and how it can potentially reshape their compliance strategies. Fortunately, the UK government has put out a document entitled “Economic Crime and Corporate Transparency Act 2023: Guidance to organisations on the offence of failure to prevent fraud.” (The Guidance) Over the next several blog posts, I will explore the Guidance and its implications for US-based compliance professionals.

The FTPF introduces corporate criminal liability for large organizations where an associated individual commits fraud, intending to benefit the organization or its clients. This represents a seismic shift for corporate compliance programs because senior management does not need to have ordered or even been aware of the fraud for liability to attach. The very act itself, if proven to benefit the organization or its clients, triggers organizational accountability.

Which companies exactly fall under this statute? The scope applies specifically to large organizations, defined as incorporated entities or partnerships that meet at least two of the following criteria: having more than 250 employees, a turnover exceeding £36 million, or total assets exceeding £18 million. This definition intentionally includes subsidiaries and partnerships within its ambit, casting a wide net for compliance oversight.

The Guidance clearly defines the types of fraud included under the new offense. These base fraud offenses include fraud by false representation, failing to disclose information, abuse of position, false accounting, cheating the public revenue, and fraudulent trading. Organizations must now look beyond mere regulatory adherence to proactive fraud detection and prevention strategies, given the broad spectrum of fraud covered.

The term “associated person” is critical. It extends beyond employees and explicitly includes agents, subsidiaries, or any other persons providing services for or on behalf of the organization. The Guidance notably excludes those merely supplying goods, emphasizing service relationships as the core focus. Understanding the depth and breadth of these associations will require enhanced due diligence processes, rigorous vetting of service providers, and a fundamental re-evaluation of contractual relationships.

Territoriality is another aspect that compliance professionals must closely evaluate. The offense holds a distinct UK nexus; thus, fraud committed by associated persons must either occur in the UK or involve gains or losses realized within UK boundaries. This global perspective on compliance places significant responsibility on UK-based operations with international associations and activities.

Notably, the Guidance outlines scenarios to clarify ambiguities. Consider, for instance, the fraud committed by the payroll department, which diverted employee pension funds to support other internal projects. Here, the payroll head abuses their position of trust to commit fraud intended to benefit the company’s operations. Even if no senior manager or director was aware of the fraud, the company could still face prosecution under this legislation unless it has demonstrably reasonable procedures in place to prevent such fraud.

In terms of defensive mechanisms, the guidance emphasizes the implementation of “reasonable fraud prevention procedures.” This implies that corporations must adopt tailored compliance systems that consider the specific risks associated with their industry, size, and operational territories. Simply having generic fraud detection tools will likely fall short of satisfying this legal standard. Instead, robust, proactive, risk-specific compliance measures, supported by ongoing training and review, become non-negotiable.

The Serious Fraud Office will lead investigations into the FTPF, and the Crown Prosecution Service will handle any courtroom work. An interesting aspect here is the possibility of Deferred Prosecution Agreements (DPAs) in England and Wales, suggesting that organizations may negotiate terms if fraud prevention measures were deemed insufficient initially but have since been significantly improved.

The Guidance emphasizes the importance of corporate cooperation with enforcement authorities. Organizations that demonstrate transparent reporting, proactive fraud detection efforts, and comprehensive preventive frameworks are likely to receive more favorable prosecutorial discretion and may be eligible for DPAs.

From a compliance perspective, understanding intent to benefit is crucial. The Guidance explicitly notes that even indirect or unrealized benefits to the organization, such as a failed attempt to attract investors through false accounting, could trigger liability. The intent to benefit need not be the primary motivation; any incidental or indirect benefit, financial or otherwise, places the organization at risk. Compliance programs must thus anticipate, monitor, and mitigate even seemingly remote risks.

This guidance represents not only a legal shift but also a call for a cultural transformation within corporations. Compliance professionals must foster an environment where ethical practices are embedded, whistleblowers are supported, and robust prevention frameworks are continuously evaluated and strengthened.

Key Highlights for Corporate Compliance Professionals:

  1. Understand the expanded scope of corporate liability and who qualifies as an associated person.
  2. Clearly identify the specific types of fraud covered under the Act.
  3. Implement tailored and robust fraud prevention procedures.
  4. Recognize the importance of territorial considerations for global operations.
  5. Foster a proactive and ethical organizational culture, supported by strong whistleblowing protocols.

The Economic Crime and Corporate Transparency Act 2023 mandates a higher degree of vigilance, proactive risk management, and cultural alignment with anti-fraud values. Organizations failing to adapt swiftly to this evolving compliance landscape risk severe financial penalties, reputational damage, and operational disruption. Forward-looking compliance professionals will seize this moment to reinforce corporate integrity, safeguard organizational reputation, and ensure lasting resilience against fraud.

The Guidance provides an entire section on compliance with the FTPF. Join us tomorrow as we take a deep dive into its prescripts.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Compliance Responses to Design Intelligence

Welcome to “Compliance Tip of the Day,” the podcast that brings you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our goal is to provide you with bite-sized, actionable tips to help you stay ahead in your compliance efforts. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today, we consider how CCOs and compliance programs need to respond to design intelligence.

For more information on this topic, refer to The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, 6th edition, recently released by LexisNexis. It is available here.

Categories
Great Women in Compliance

Great Women in Compliance – The Compliance Pre-Mortem: Together We Can Do Hard Things Well with Jonathan Aronie

This GWIC episode features a “Great Gentleman in Compliance,” Jonathan Aronie, a leading expert in government investigations and organizational integrity at Sheppard Mullin. Jonathan joins GWIC co-host Hemma Lomax to discuss his career journey, the innovative compliance tool known as the compliance pre-mortem, and the importance of proactive measures in compliance and governance. He also emphasizes the significance of active bystander intervention programs, derived from law enforcement, as highly effective tools for preventing misconduct in organizations. Additionally, Jonathan offers insights into the challenges and benefits of compliance programs, highlighting the need for continuous improvement and strategic empathy in these efforts.

  • The Psychology of Preventative Compliance
  • The ROI of Compliance and Integrity
  • The Concept of Pre-Mortem in Compliance
  • Common Risks and Blind Spots in Compliance
  • Active Bystander Programs vs. Compliance Hotlines
  • Lessons in Compliance and Culture from Policing
  • Building Continuous Improvement Frameworks
 

Biography

Jonathan Aronie is a partner in and the former leader of the firm’s Governmental Practice, resident in Washington, DC. Jonathan is also a founding member and current leader of the firm’s Organizational Integrity Group, a cross-disciplinary team of litigators, regulatory specialists, federal monitors, and ex-prosecutors with extensive experience helping organizations prevent and defend against challenges to their organizational integrity. 

Areas of Practice

Jonathan counsels and represents large and small businesses in some of the country’s most prominent classified and unclassified government contract matters, including bid protests, claims, self-disclosures, internal investigations, Department of Justice investigations, and False Claims Act investigations. As the leader of the firm’s Organizational Integrity Group, Jonathan also dedicates significant time to working with clients to identify and mitigate known and unknown risks before they become problems.

Jonathan’s experience includes litigating under the qui tam provisions of the False Claims Act, conducting early risk-based “legal pre-mortems,” developing and implementing corporate compliance programs, conducting internal investigations (proactive and defensive), and providing advice on the FAR Mandatory Disclosure Rule as well as a variety of federal regulatory and statutory matters. He frequently represents clients before the DOJ, the Government Accountability Office, the General Services Administration, and other defense and civilian agencies. Additionally, Jonathan is cleared at the highest levels and counsels and defends clients in classified matters.

Jonathan has authored more than 100 articles and co-authored what is regarded by many as the leading treatise on the GSA Multiple Award Schedule Program, published by Thomson Reuters. He is a regular speaker at national and international forums, as well as CLE programs, including government-sponsored symposia. He is a regular presenter at Coalition for Government Contracting programs and served on the ABA Task Force that drafted guidance regarding the FAR Mandatory Disclosure Rule.

https://www.sheppardmullin.com/jaronie

Resources

Sheppard Mullin’s Organizational Integrity Group

Active Bystandership for Law Enforcement

Everyone Benefits When An Ethics & Compliance Program Is Integrated Throughout An Organization. By: Jonathan Aronie,

Jonathan Aronie on LinkedIn

Categories
Blog

The Compliance Guide to Designed Intelligence: Part 2 – Rethinking Governance for the Age of AI

Yesterday, I began a two-part review of the article “What Is a Designed Intelligence Environment?” in which authors Michael Schrage and David Kiron examine how enterprises must rethink their intelligence and compliance strategies to survive and thrive in the new world of AI-rich operations. I found their insights for compliance professionals both practical and transformative. Previously, we considered what is Designed Intelligence. Tomorrow, we take a deeper dive into what it means for compliance.

For decades, we have approached compliance through policies, procedures, and periodic reviews, trusting that careful planning and diligent oversight would guide us through the challenges of regulatory change and operational risk. However, the rise of artificial intelligence has forever altered this equation. Now, the decisions that shape our organizations are made not just by people, but by increasingly autonomous machines and systems that learn, adapt, and interact in ways that can outpace human comprehension.

This new reality demands a new approach to compliance, one that goes beyond enforcing existing rules and begins to architect the very environments in which human and machine intelligence operate. The article “What Is a Designed Intelligence Environment? ” offers a timely and robust framework for this challenge. Rather than treat AI as just another tool in the compliance toolbox, it urges us to rethink how knowledge, reasoning, and governance are structured across the enterprise. For the compliance professional, this shift is as profound as it is practical: our mission is no longer to control risk but to orchestrate intelligence itself.

Five Key Takeaways for the Compliance Professional

1. Observability Over Prediction: Embrace Real-Time Monitoring

Traditional compliance programs often rely on the classic cycle of predict, plan, execute, and measure. However, as the article emphasizes, Stephen Wolfram’s principle of computational irreducibility suggests that in highly complex, AI-rich environments, outcomes cannot be predicted; they must be observed as they occur. This is not a theoretical point; rather, it is a practical call to action for compliance.

In a world where both human and machine agents make critical decisions, compliance leaders need to build systems that provide real-time visibility into these interactions. The case of the pharmaceutical R&D pipeline illustrates this vividly: instead of forcing premature rankings of drug candidates, the company built a computational observatory, allowing emergent patterns to drive decision-making. For compliance, this means investing in tools and processes that enable continuous monitoring, immediate detection of anomalies, and dynamic feedback loops, moving from static after-the-fact audits to active, ongoing oversight.

2. Semantic Formalization: Make Compliance Computable

If your compliance program still relies on lengthy policy manuals and inconsistent training, it’s time to elevate it. The article introduces the concept of semantic formalization, defining key business and compliance concepts in a manner that enables both humans and machines to execute and reason with them. This isn’t just data management; it’s about ensuring every stakeholder and system shares a common, computable language for compliance.

For example, a multinational retailer struggling with customer experience (CX) consistency turned things around by building a semantic kernel, a shared ontology for complaints, resolutions, and metrics. Compliance teams must similarly formalize definitions for key terms, including risk, conflict of interest, and reporting obligations. This creates a foundation where both human and AI agents can interpret and act on compliance requirements, ensuring consistency, auditability, and scalability.

3. Translate Between Multiple Realities

Every department, human expert, and AI system in your organization “computes” reality differently. Financial models assess risk through simulations, operations utilize failure analysis, and AI identifies statistical correlations. The article’s exploration of real space, the idea that these are not just different perspectives but fundamentally different computational rule sets, changes the compliance game.

Instead of forcing alignment through top-down mandates, compliance officers must become expert translators and orchestrators of change. The aerospace design review case proves the point: rather than punishing disagreement between engineers and AI, leadership created a real mediator, mapping and reconciling the underlying rules of each party. Compliance professionals should develop frameworks and protocols to make these internal logics explicit, resolve conflicts, and coordinate decision-making without imposing artificial consensus.

4. Do Not Simply Deploy Smarter Tools, But Architect Intelligence Environments

Throwing advanced AI or analytics at compliance problems is not enough. The article argues forcefully that intelligence, whether human or machine, must be designed into the very infrastructure of the enterprise. Most organizations still treat intelligence as an emergent property of tools, rather than an intentional product of environment design.

For compliance, this means working proactively with IT, legal, and operational leaders to design systems where intelligence (learning, reasoning, and adaptation) is orchestrated by default. Real-time observability, semantic formalization, and rule-based mediation must be built into the core of your compliance framework, not added as afterthoughts. This approach enables faster, higher-quality decisions, reduces systemic risk, and enhances organizational agility.

5. From Enforcer to Orchestrator: Redefine the Compliance Role

The most important takeaway is the redefinition of what it means to be a compliance professional in the era of AI. The future of compliance is not just about enforcing standards and conducting audits; it is about orchestrating intelligence across human and machine systems. This means guiding the translation between different rules and perspectives, architecting environments for safe collaboration, and ensuring ethical execution in a world of real-time, adaptive agents.

Compliance officers must expand their skill sets by learning the basics of AI, systems engineering, and data science, developing fluency in semantic modeling, and building cross-functional relationships with technology and business leaders. By leading the design of intelligence environments, compliance professionals can become strategic partners in innovation, not just gatekeepers of risk.

As we enter a new era defined by AI, the compliance profession finds itself at a crossroads. The systems we govern are no longer straightforward, linear, or purely human—they are dynamic, adaptive, and built from the collaboration between people and machines. The article “What Is a Designed Intelligence Environment? ” makes clear that our old tools—checklists, policy manuals, and after-the-fact audits—are no longer sufficient for the task ahead. Instead, we must build environments where intelligence itself is orchestrated, monitored, and governed by design.

This transformation is not about abandoning the core values of compliance, integrity, transparency, and accountability; it is about embracing new methods to uphold them in a complex world. We must shift from prediction to observability, from description to formalization, and from enforcement to orchestration. We must learn to translate and mediate between diverse ways of thinking and design infrastructures that enable human and machine intelligence to flourish safely and ethically.

Categories
Compliance Tip of the Day

Compliance Tip of the Day – Rethinking Corporate AI Governance Through Design Intelligence

Welcome to “Compliance Tip of the Day,” the podcast where we bring you daily insights and practical advice on navigating the ever-evolving landscape of compliance and regulatory requirements. Whether you’re a seasoned compliance professional or just starting your journey, our aim is to provide you with bite-sized, actionable tips to help you stay on top of your compliance game. Join us as we explore the latest industry trends, share best practices, and demystify complex compliance issues to keep your organization on the right side of the law. Tune in daily for your dose of compliance wisdom, and let’s make compliance a little less daunting, one tip at a time.

Today we consider how enterprises must rethink their compliance strategies to survive and thrive in the new world of AI-rich operations.

For more on this topic, check out The Compliance Handbook, a Guide to Operationalizing your Compliance Program, 6th edition which was recently released by LexisNexis. It is available here.

Categories
Innovation in Compliance

Innovation in Compliance – The Power of Accountability and Team Culture with Gina Cotner

Innovation comes in many areas, and compliance professionals need to be ready for it and embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this engaging episode, Tom Fox sits down with Gina Cotner, the founder and CEO & Founder of Athena Executive Services, to explore the importance of team culture and accountability in corporate settings.

Cotner delves into her professional background and the organic development of a strong team culture at Athena. She emphasizes the critical role of accountability as a cultural standard and provides actionable insights for leaders on how to instill this within their organizations. Key takeaways include the significance of consistency, the balance between compassion and accountability, and the role of follow-up as a leadership tool. With real-world examples and practical advice, Cotner provides a comprehensive guide to building and maintaining a high-performing, accountable team.

Key highlights:

  • Gina Cotner’s Professional Background
  • The Importance of Team Culture
  • Accountability in High-Performing Teams
  • Misunderstandings About Accountability
  • Building a Culture of Accountability
  • Consistency and Psychological Safety
  • Follow-Up as a Leadership Tool
  • Compassion in Leadership

Resources:

Follow Athena Executive Services on:

Company’s Website

LinkedIn

Instagram

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn