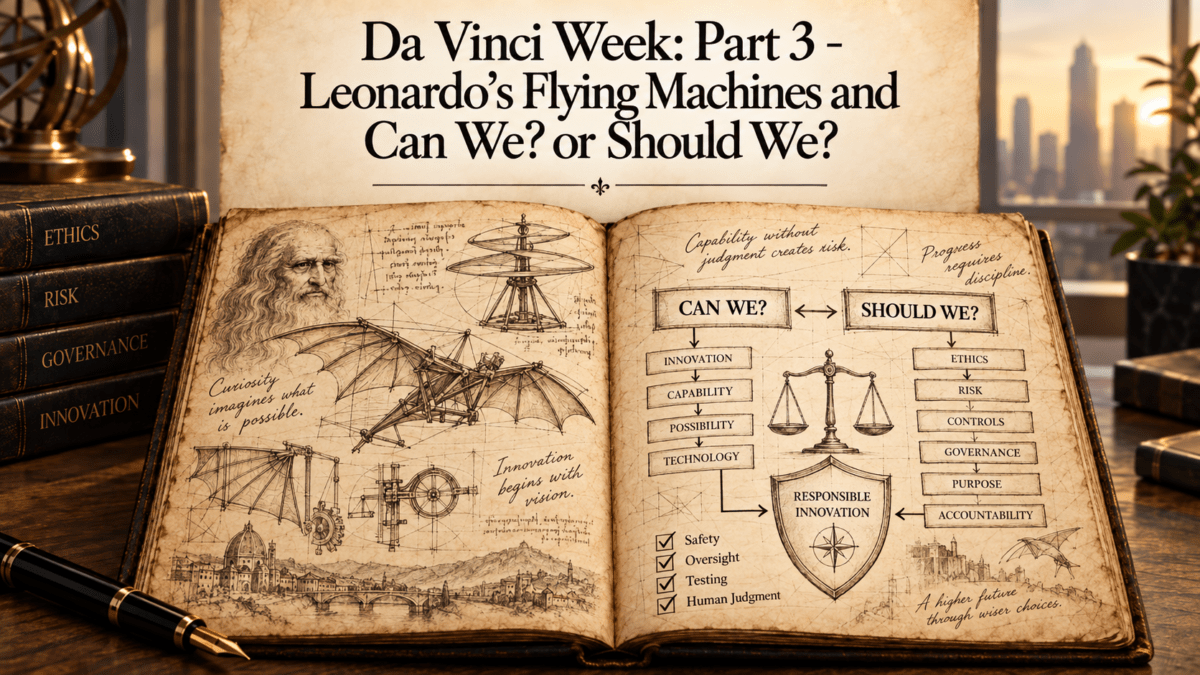
In the first two posts in the Leonardo Compliance Framework, the Mona Lisa gave us Refine, the principle that an effective compliance program improves as the organization learns from experience. Leonardo’s anatomical studies gave us Investigate, the discipline of looking beneath misconduct to understand root causes, control failures, incentives, management decisions, and the organizational systems that produced the outcome. The third principle is Innovate.
For that lesson, we turn to Leonardo’s studies of flight and his designs for flying machines. Leonardo examined birds, air movement, wings, and mechanical systems as he considered whether technology could allow human beings to fly. Many of his concepts were far beyond the practical capabilities of his time, but they demonstrate an important characteristic of Leonardo’s work: he imagined capabilities that did not yet exist and then studied the systems necessary to make them possible.
For corporate compliance professionals in 2026, the analogy to artificial intelligence is particularly useful. AI is expanding what companies can automate, analyze, predict, generate, and increasingly act upon. Organizations are moving beyond using generative AI to draft documents and summarize information. AI systems are becoming embedded in business processes, interacting with corporate data, supporting consequential decisions, communicating with customers, evaluating third parties, and, through increasingly agentic capabilities, taking actions that previously required human intervention.
The compliance challenge is not whether companies should innovate. They will. The challenge is establishing governance that allows innovation to create business value without producing unmanaged legal, ethical, operational, or compliance risk.
AI Governance Is Enterprise Governance
Compliance professionals have sometimes approached emerging technology as primarily the responsibility of IT, Cybersecurity, Data Privacy, or Legal. That division becomes increasingly difficult with AI because these systems can influence many of the activities a corporate compliance already oversees. Indeed the Evaluation of Corporate Compliance Programs (ECCP) anticipates these very concepts in its 2024 edition.
AI may assist with third-party due diligence, contract review, procurement, transaction analysis, hiring, customer communications, investigations, fraud detection, marketing, or pricing. Each application creates a different risk profile. A due diligence system may generate inaccurate information about a business partner. An investigation tool may expose privileged or confidential information. A sales application may generate communications inconsistent with company policies. An agent connected to corporate systems may take actions that historically required human approval.
The ECCP asks the following:
- How does the company assess the potential impact of new technologies, such as artificial intelligence (AI), on its ability to comply with criminal laws?
- Is management of risks related to use of AI and other new technologies integrated into broader enterprise risk management (ERM)strategies?
- What is the company’s approach to governance regarding the use of new technologies such as AI in its commercial business and in its compliance program?
- How is the company curbing any potential negative or unintended consequences resulting from the use of technologies, both in its commercial business and in its compliance program?
Visibility and Risk Should Drive the Control Environment
By 2026, asking whether a company uses AI provides little useful information. Management needs to understand how AI is being used and what authority particular systems possess. A tool that summarizes a public document presents a very different risk profile from a system that influences hiring, approves a third party, communicates with customers, accesses confidential information, initiates a transaction, changes corporate records, or takes actions across interconnected systems.
An AI inventory should therefore identify meaningful use cases, including the business owner, intended purpose, relevant data, third parties involved, decisions influenced by the technology, degree of autonomy, and applicable controls. The objective is not simply to count tools. It is to give management sufficient visibility to identify where material risk exists.
That visibility should support risk classification. Not every AI application requires the same level of governance. Classification should consider the system’s purpose, data sensitivity, potential consequences of error, degree of autonomy, affected populations, ability to review or reverse decisions, and applicable legal or regulatory requirements.
This is familiar territory for compliance professionals. Risk-based programs have long applied different levels of scrutiny to third parties, transactions, investigations, and markets. AI should follow the same principle. Higher-risk systems should receive greater review, stronger controls, and more rigorous monitoring.
Human Oversight Must Preserve Accountability
“Human in the loop” has become common language in AI governance, but the presence of a human does not by itself create an effective control. Meaningful oversight requires defined responsibilities, appropriate expertise, sufficient capacity to review relevant outputs, and authority to challenge or override the system.
If one employee is nominally responsible for reviewing thousands of AI-generated recommendations each day, human oversight may exist on paper without functioning in practice. The same problem arises when employees routinely accept recommendations because they assume the technology is more reliable than their own judgment.
The control should therefore define the reviewer’s responsibilities, the circumstances requiring additional scrutiny, the authority to reject recommendations, and the treatment of material overrides or recurring disagreements between the system and human decision-makers. Most importantly, technology should not create an accountability vacuum. If an AI system contributes to a compliance failure, the organization should still be able to identify the owner of the business process, who approved the use case, who was responsible for monitoring it, and who had authority to intervene.
This becomes increasingly important with agentic systems. Traditional corporate controls generally assume identifiable human actors approve payments, create vendors, review contracts, or authorize higher-risk third parties. When technology performs some of those activities, the organization has effectively delegated authority to a system. The control environment must reflect that delegation while retaining human and organizational accountability for the outcome.
Third-Party AI and Data Risk
Many companies will obtain significant AI capabilities from external vendors rather than develop them internally. The use of a vendor does not transfer accountability for the resulting compliance risk. Traditional third-party risk management principles remain relevant. The company should understand the service provided, the information the vendor receives, how data are used and retained, what subcontractors are involved, how incidents are managed, and what contractual rights the company must obtain information, require remediation, audit, or terminate the relationship.
AI adds a dynamic element because models, features, and business uses can change after initial approval. Monitoring should therefore identify material changes in functionality, data use, vendor practices, or business application that could alter the original risk assessment.
Data governance is equally important. Companies need clear rules regarding which AI systems may access confidential business information, personal data, investigation materials, privileged communications, customer information, trade secrets, source code, and other sensitive information. As enterprise AI systems increasingly operate on internal data, blanket prohibitions will often give way to more precise governance defining approved systems, permissible data, access controls, retention, deletion, and accountability.
These issues require coordination across Compliance, Legal, Privacy, Cybersecurity, IT, Records Management, and the business. Effective governance depends upon clear responsibilities rather than overlapping or fragmented ownership.
Test Before Deployment and Monitor Afterward
Leonardo’s flying machines provide another useful innovation lesson. A design should be tested before it is trusted with a critical task. AI testing should be proportionate to risk. Before deployment, the company should understand whether the system performs as intended, where its limitations lie, how it responds to unusual circumstances, whether users can manipulate it, and whether inaccurate or inconsistent outputs could create material consequences. Testing at implementation is not enough. Business conditions change, vendors update models, employees develop new uses, and system capabilities expand. An application that operated within acceptable parameters when approved may later present a different risk profile.
Higher-risk systems therefore require post-deployment monitoring capable of identifying performance issues, material changes, incidents, and circumstances requiring reassessment. Management should also establish when a system should be modified, restricted, or suspended.
This lifecycle approach creates the connection between Innovate and the next Leonardo principle, Monitor. Responsible innovation is not a one-time approval. Governance should continue throughout the period in which the organization relies upon the technology.
Using NIST and ISO as Governance Architecture
Compliance professionals do not need to invent an AI governance structure from scratch. The NIST AI Risk Management Framework provides a useful approach to governance, mapping, measurement, and management of AI risk, while ISO/IEC 42001 provides a management-system perspective built around responsibilities, processes, documentation, monitoring, and continuous improvement.
For the CCO, their value lies in providing governance architecture rather than another checklist. The relevant measure is not whether a company can say it follows NIST or ISO. It is whether its governance system addresses the actual risks created by its AI applications and whether the resulting controls work in practice. Frameworks provide structure. Management remains responsible for operating the system.
Compliance Should Enable Responsible Innovation
The CCO should avoid two extremes: allowing enthusiasm for AI to outrun governance or creating an approval structure so burdensome that employees circumvent it. A better model is responsible innovation. Compliance can help create clear pathways for lower-risk experimentation while ensuring that higher-risk applications receive appropriate scrutiny. Employees should understand what uses are permitted, which require approval, what categories of information may be used, and when escalation is necessary.
This approach also creates opportunities for a corporate compliance program. AI may improve due diligence, transaction monitoring, investigations, risk assessment, training, and data analysis. The compliance function should be willing to explore those capabilities under the same risk-based governance it expects the business to follow.
A CCO’s contribution should not be measured by how much innovation Compliance prevents. It should be measured in part by whether Compliance helps the enterprise capture value while maintaining appropriate accountability and control.
Before Leaving the Ground
Leonardo’s flying-machine studies represent the willingness to imagine possibilities beyond current practice. The modern compliance lesson is to combine that willingness with disciplined governance. For the CCO, Innovate means helping the enterprise pursue new capabilities through a risk-based system that provides visibility, assigns ownership, preserves meaningful human accountability, tests higher-risk applications, and monitors them as technology and business use evolve. The objective is neither unrestricted adoption nor blanket prohibition. It is responsible innovation capable of producing sustainable business value.
From Innovation to Monitoring
Responsible innovation does not end when technology is approved and deployed. The organization must determine whether systems continue to operate as intended as data, users, vendors, business conditions, and risks change. That brings us to the fourth Leonardo principle: Monitor.
In Blog Post Four, The Last Supper and the Danger of Deterioration, we will use Leonardo’s experimental masterpiece to examine the difference between implementing a control and demonstrating that it remains effective. The discussion will focus on control testing, continuous monitoring, compliance analytics, ownership, remediation, AI monitoring, and the board’s role in evaluating evidence of continuing program effectiveness.