Categories
AI Today in 5

AI Today in 5: October 19, 2026, The Compliance Sprawl Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Cyber compliance gaps. (LS)
  2. FSB releases sound practices for responsible AI. (FSB)
  3. AI runs into insurance issues. (WSJ)
  4. AMA releases governance framework for Agentic AI. (HealthcareDive)
  5. AI fighting against compliance sprawl. (FinTechGlobal)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
FCPA Compliance Report

FCPA Compliance Report: Mike Huneke and Brent Carlson with US Attorney David Metcalf

In this episode, Tom Fox cross-posts an episode of Red Flag Rising featuring U.S. Attorney for the Eastern District of Pennsylvania David Metcalf, joined by co-hosts Mike Huneke and Brent Carlson.

David Metcalf, the U.S. Attorney for the Eastern District of Pennsylvania, brings a practical, business-aware perspective on fraud enforcement and corporate compliance, shaped by experience both in government and as in-house counsel. He notes that white-collar enforcement in his district centers heavily on healthcare fraud but also extends to cybercrime, narcotics trafficking, export controls, and other complex investigations. Metcalf strongly encourages companies to consider self-disclosure in their self-interest, warning that the DOJ will be especially aggressive toward those that do not come forward. At the same time, he stresses that early engagement is the most effective approach, because trust and candid discussion at the outset can create meaningful benefits, including even unpublicized declinations.

 Key highlights:

  • Risk-based compliance shaped by business realities
  • Whistleblower evidence versus compliance rationale perspective
  • Data Analytics-Powered National Fraud Detection Center
  • Data-Driven Detection of Healthcare Fraud Cases
  • Tariff Evasion and Customs Fraud Crackdown
  • DOJ’s relaxed near-miss voluntary disclosure incentive

Resources:

More about U.S. Attorney David Metcalf

The Eastern District of Pennsylvania’s White Collar Justice Program

The DOJ’s National Fraud Enforcement Division

More about the 1950 classic Japanese film “Rashomon”

Contact Brent: brent@redflagsrising.com

More about Brent

Connect with Brent on LinkedIn

Contact Mike: michael.huneke@morganlewis.com

More about Mike

Connect with Mike on LinkedIn

Tom Fox

Instagram

Facebook

YouTube

Twitter

Categories
Daily Compliance News

Daily Compliance News: October 19, 2026, The What is the Face of Fraud Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we cover four stories from the business world, compliance, ethics, risk management, leadership, or general interest for compliance professionals.

Top stories include:

  • Prominent Guatemalan ABC lawyer killed. (Reuters)
  • Corruption: Chinese officials have ‘nowhere to hide’. (SCMP)
  • AI’s next obstacle: insurance. (WSJ)
  • John Carreyou exposes You Can See Everything. (NYT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Blog

BOA Part 1: $1.2 Billion Compliance Failure: When Red Flags Meet Revenue

A compliance program is tested when someone identifies a risk that the business would prefer not to address. The question is not whether compliance can produce a memorandum. The question is whether the organization makes a timely, supportable decision and implements controls that address the concern.

The Bank of America enforcement record provides a detailed examination of that problem. FinCEN (Consent Order) describes repeated internal warnings, testing that identified weaknesses, and customer relationships that continued without controls commensurate with the risks. Its findings place management decisions about revenue and resources at the center of the compliance failure.

For chief compliance officers, the central lesson is straightforward: Identifying a material risk is the beginning of compliance work, not its completion. Over this four-part blog series, we will review the FinCEN Consent Order, OFAC’s Enforcement Release, and the Department of the Treasury’s Press Release to mine each for how this was allowed to occur, how it continued, the governance failures, the marginalization of compliance, and the penalties assessed. Today in Part 1, we examine the governance failure at the heart of the Bank of America enforcement actions: compliance personnel identified significant risks, but management did not ensure those concerns led to timely, effective corrective action.

Understanding the Enforcement Actions

On October 13, 2026, the Department of the Treasury announced enforcement actions involving FinCEN, the Office of the Comptroller of the Currency, and the Office of Foreign Assets Control. Treasury described combined penalties exceeding $1.21 billion for anti-money laundering and sanctions failures.

The penalty structure matters. FinCEN assessed $1.2 billion but credited the bank’s $750 million OCC payment, leaving $450 million payable under the FinCEN Consent Order. OFAC’s separate Enforcement Release states a settlement of $11,662,930. Adding the full FinCEN and OCC assessments together would therefore overstate the combined financial penalty.

The legal posture also matters. Bank of America admitted the facts and violations in the FinCEN Consent Order. It expressly limited its admission of willfulness to the civil Bank Secrecy Act enforcement standard. By contrast, OFAC resolved potential civil liability for apparent violations. These documents should not be characterized as a criminal guilty plea.

The Warnings Were Already Inside the Organization

Consider the relationship identified in the FinCEN Consent Order as Customer A, an online marketplace connecting sellers of salvaged vehicles with domestic and international buyers. The bank had maintained accounts for this customer since 1995. By 2022, compliance personnel had identified concerns involving third-party payments, limited visibility into the source of funds, and repeated fraud-related investigations. In July, compliance recommended that the customer’s accounts be considered for closure. Subsequent internal analysis identified more than 100 customer-related cases between 2020 and August 2022.

This was not simply a disagreement about a customer’s reputation. Compliance was identifying a weakness in the bank’s ability to understand the funds moving through the relationship. An important distinction must remain clear. The Consent Order records that no evidence shows Customer A orchestrated the underlying fraud. The concern was that its accounts appeared to have received and moved fraud proceeds, creating risks the bank needed to address. Suspicion concerning transactions is not proof that the customer knowingly participated in the underlying misconduct.

That distinction makes the compliance lesson more useful. An organization does not need to prove a business partner is a criminal before deciding the relationship requires stronger controls.

When Commercial Importance Becomes the Answer to a Different Question

Following an internal meeting in September 2022, the relationship manager prepared a memorandum describing Customer A as a “large and valued client” generating approximately $6 million in annual revenue. The memorandum emphasized the broader commercial relationship and the business line’s support for retaining it. Compliance personnel continued asking how the underlying risks were being mitigated. FINCEN consent order

Here is the governance problem: commercial value and risk mitigation answer different questions. Revenue explains why the business wants to retain a relationship. It does not establish that the relationship can be maintained within an effective control environment.

Nor does compliance independence require that every recommendation to terminate a relationship prevail. FinCEN expressly states that account closure is not the only appropriate response to heightened financial crime risk. Enhanced monitoring, restrictions on products or services, and other risk-based controls may be appropriate. The real question is whether the alternative works.

A defensible decision to retain a high-risk customer should explain what will change, who will implement it, what evidence will show it works, and what happens if the customer does not meet the agreed conditions. Without those elements, an alternative mitigation plan can become a way to defer the original decision.

A Mitigation Plan Is Not the Same as Mitigation

In March 2023, more than six months after compliance recommended closure, the relationship manager summarized proposed measures, including limiting payments to registered buyers or dealers. Compliance withdrew its closure recommendation based on the communication and implementation of those measures, while reserving the possibility of revisiting the decision.

However, Customer A continued processing third-party payments through its Bank of America account until June 2025. The bank did not adequately update the customer’s risk profile, ongoing monitoring, or other due diligence measures to address the continuing practice. Some other changes were implemented, but the central payment risk persisted.

This is where compliance activity and compliance effectiveness separate. A meeting is an activity. A mitigation plan is an activity. A customer assurance is information. None, standing alone, establishes that the risk has been reduced. For the CCO, the missing discipline is verification. When the organization decides to continue a relationship subject to conditions, those conditions need an owner, an implementation date, evidence requirements, and consequences for nonperformance.

Resources Are Also a Governance Decision

FinCEN found that management’s approach to transaction monitoring was influenced by the resources required to investigate additional cases. When remediation began, the bank estimated that investigative volumes would double and that approximately 750 additional personnel would be needed. FinCEN concluded that the bank had likely avoided hundreds of millions of dollars in compliance-related expenditures during the relevant period. That was FinCEN’s assessment, not a separately calculated figure of realized profit.

The business lesson is not that every compliance function should receive every requested dollar. Resource decisions need to address the actual risk. Management should not resolve a capacity problem by treating the activity that exceeds capacity as less important without a supportable risk basis.

What the CCO and Board Should Ask

As a comparison framework, the DOJ’s Evaluation of Corporate Compliance Programs (ECCP) examines whether a program is well designed, adequately resourced and empowered, and effective in practice. It also asks whether managers tolerate greater compliance risks to pursue revenue and how the company responds when compliance raises concerns. These are useful analytical questions here, not the legal standards under which FinCEN resolved this case.

Board oversight provides another comparison. In Marchand v. Barnhill, the Delaware Supreme Court emphasized the need for a good-faith effort to establish board-level monitoring of a critical compliance risk. Caremark liability involves a demanding bad-faith standard, not automatic liability whenever a control fails. The Bank of America documents discussed here are not Caremark judgments against its directors.

The practical board questions nevertheless follow naturally. Which material compliance recommendations remain unresolved? Which business decisions depend on mitigation that has not been verified? Which deficiencies have appeared repeatedly without an effective response? Those questions move oversight beyond receiving presentations to examining whether management is controlling the risk.

Three Key Takeaways

First, require decisions, not indefinite escalation. Material concerns need accountable decision-makers, documented reasoning, deadlines, and follow-through.

Second, separate commercial justification from control effectiveness. A valuable relationship may be retained, but its revenue does not demonstrate that its risks are mitigated.

Third, verify the conditions supporting the decision. Keep an approved remediation plan open until the organization has evidence that the relevant controls work.

The CCO question: When the business rejects or modifies a compliance recommendation, can you demonstrate that the alternative actually reduced the risk?

Today we examined the governance failure at the heart of the Bank of America enforcement actions: compliance personnel identified significant risks, but management did not ensure that those concerns produced timely, effective corrective action. FinCEN’s findings describe an organization that prioritized customer revenue and resource considerations while known risks persisted without commensurate controls.

The central lesson is not that compliance must prevail in every disagreement or that every high-risk relationship must be terminated. Decisions to retain those relationships must rest on demonstrable risk mitigation, not commercial importance alone. For CCOs, this means establishing accountable decision-makers, deadlines, documented reasoning, and verification that agreed measures work. For boards, it means examining unresolved exposure rather than merely receiving reports of completed activities. A mitigation plan does not establish that a risk has been mitigated. The organization must verify the result.

Join us Tomorrow

Management decisions about compliance don’t stay confined to committee meetings and customer relationship discussions. They also shape the technology that determines which risks receive attention and which remain uninvestigated. In Part 2, we turn to Bank of America’s Event Processor transaction monitoring system and FinCEN’s findings concerning unsupported design choices, investigative thresholds, alert suppression, gaps in monitoring coverage, and inadequate responses to testing.

Our focus shifts from whether management acted on known concerns to whether its automated controls could identify and escalate the relevant activity. We will examine the difference between reducing investigative workload and improving compliance effectiveness, with practical applications for data governance, model validation, and AI oversight. Every CCO must ask whether your technology addresses the intended risk, not simply whether it operates according to its configuration.

Categories
Sunday Book Review

Sunday Book Review: October 18, 2026, The Business Book of the Year – Part 2, Edition

In the Sunday Book Review, Tom Fox considers books that would interest compliance professionals, business executives, or anyone curious about the subject. It could be books about business, compliance, history, leadership, current events, or any other topic that might interest Tom. This is the second of a two-part series on the FT/Standard Chartered Business Books of the Year nominees. This week, we’re covering the second three books. Last week, we covered the first three books.

  1. Project Maven by Katrina Manson
  2. Blood Will Flow by Alex Perry
  3. Prophecy by Carissa Véliz


Resources:

Financial Times/Standard Chartered Business Book of the Year-the shortlist

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Daily Compliance News

Daily Compliance News: October 16, 2026, The Martin Shkreli Again Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we cover four stories from the business world, compliance, ethics, risk management, leadership, or general interest for compliance professionals.

Top stories include:

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
AI Today in 5

AI Today in 5: October 16, 2026, The Green AI Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Cyber compliance gaps. (Industrial Cyber)
  2. From compliance to competence. (Nature)
  3. Bloomberg’s aggressive stance on AI. (WSJ)
  4. Green AI in healthcare. (News Medical Life Sciences)
  5. Building foundations for AI in insurance. (FinTechGlobal)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Popcorn and Compliance

Popcorn and Compliance: Episode 3: Son of Frankenstein – Inheriting the Castle Means Inheriting the Risk

This October, Tom Fox returns to one of his all-time favorites: Universal Pictures’ Classic monsters. Over the years, Tom has explored classics like Dracula, The Mummy, The Wolf Man, and The Invisible Man, as well as films by Val Lewton and Hammer Studios. This year, he wanted to return for a deep dive into the first five Frankenstein movies. He has considered, or will consider, the original Frankenstein, Bride of Frankenstein, Ghost of Frankenstein, and Frankenstein Meets the Wolfman. In this third episode, he considers what many viewers regard as the series’ best: Son of Frankenstein, released in 1939. This is the final film to feature Boris Karloff as Frankenstein’s Monster. In this exploration, Tom Fox uses his AI friends, Timothy and Fiona, to provide commentary.

Film Synopsis:

Son of Frankenstein brings Basil Rathbone into the saga as Wolf von Frankenstein, who returns with his family to his father’s estate hoping to restore the Frankenstein name. Instead, he encounters Bela Lugosi’s extraordinary Ygor and discovers that his father’s Monster, played for the final time by Boris Karloff, is still alive but comatose. Wolf revives him, hoping to vindicate his father’s work, but Ygor has his own plans and uses the Monster to settle old scores. The result is another catastrophe created by a Frankenstein convinced that this time things will be different.

Key highlights:

  • You can inherit risk without creating it.
  • This is the M&A compliance movie.
  • Ygor represents institutional knowledge used for the wrong purpose.
  • Inspector Krogh represents institutional memory.
  • Red flags transform governance responsibility.

Popcorn and Compliance takeaway: You may not have created the Monster, but once you know he is in the basement, he becomes your governance problem.

Timothy and Fiona are AI-generated voices courtesy of NotebookLM.

Categories
Blog

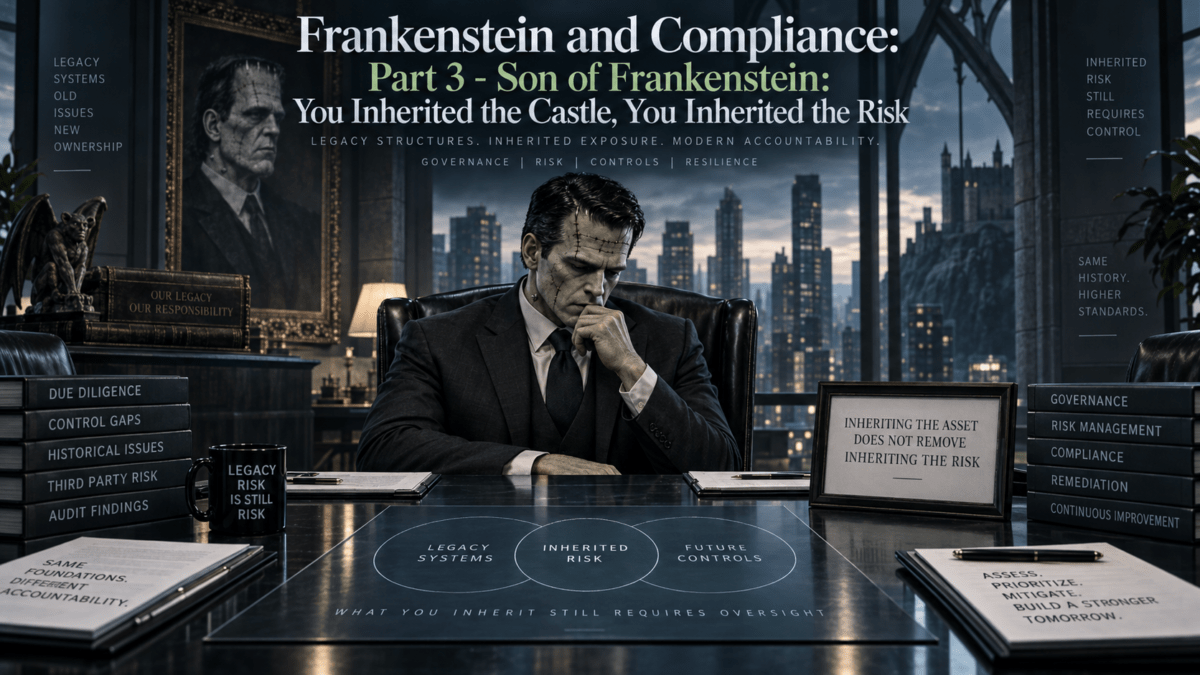
Frankenstein and Compliance: Part 3 – Son of Frankenstein: You Inherited the Castle, You Inherited the Risk

Ed. Note: This month, on his podcast series Popcorn and Compliance, Tom Fox dives deep into the first five Frankenstein movies. Over October, Tom Fox will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolf Man. This blog post accompanies the podcast series.

The first two Frankenstein films present two distinct compliance failures. Frankenstein examined innovation without adequate governance. Bride of Frankenstein shows leadership that understands the risk but lets pressure, ambition, and rationalization override judgment. Son of Frankenstein (1939) presents the next stage: inherited risk, or in the business world, risks through acquisition.

Wolf von Frankenstein, played by Basil Rathbone, returns with his family to his ancestral estate hoping to restore the Frankenstein name. Instead, he encounters Ygor, played by Bela Lugosi, and discovers that his father’s Monster is still alive. Wolf had no role in creating the original problem, but his discovery forces him to decide how to address the legacy he has inherited.

That situation should be familiar to companies following acquisitions, leadership transitions, compliance investigations, or changes in the control environment. New management may have no connection to historical misconduct. An acquiring company may not have created the target’s problematic third-party relationships. A new CCO may inherit investigations and remediation projects that were initiated years earlier. Historical responsibility and current responsibility are different questions. The business issue is how management responds once a legacy risk becomes known.

The Castle Is an Acquisition

Think of Wolf’s return to the Frankenstein estate as an acquisition. He receives the property, assets, name, and opportunity to benefit from his father’s scientific legacy. He also assumes the consequences associated with that legacy. Corporate acquisitions work much the same way. Companies acquire revenue, customers, employees, technology, intellectual property, distribution networks, and market access. They may also inherit high-risk third parties, weak internal controls, questionable historical practices, unresolved investigations, government relationships, and cultural problems.

This is why compliance due diligence should focus on how the target actually conducts business rather than simply whether it has the expected compliance infrastructure. A target may have a Code of Conduct, an anti-corruption policy, annual training, and a hotline. Those are relevant data points, but they do not establish program effectiveness.

Compliance needs to understand the target’s business model and risk profile. Consider such questions as: Where does the business operate? Who are its customers? Does it interact with government agencies or state-owned entities? Which third parties generate or facilitate business? How does the company select and compensate those parties? What does the investigation history reveal? Are there recurring audit or control deficiencies? What does speak-up data indicate? Are significant policy exceptions concentrated in particular markets or business units? The objective is to understand the risk embedded in the business being acquired.

Due Diligence Is the Beginning, Not the End

Even well-designed pre-acquisition due diligence has limitations. Transactions operate under deadlines and time pressures. Access to employees and records may be restricted. (See: Opinion Release 08-02) Data may be incomplete. Privacy requirements may constrain review. Some risks simply do not become visible until the buyer gains access to systems, records, personnel, and financial information after closing. Those limitations make the connection between due diligence and post-acquisition integration critical.

If the buyer cannot complete diligence on a high-risk distributor before closing, that relationship should become a post-closing priority. If investigation records are incomplete, they should be reviewed during integration. If significant controls cannot be tested before the transaction, testing should be incorporated into the integration plan. Compliance should therefore document unresolved diligence issues and carry them forward with assigned owners and deadlines.

This discipline matters because closing creates competing priorities. Management quickly shifts to customers, systems, personnel, financial reporting, cost savings, and expected synergies. Compliance integration can become one workstream among many. An unanswered compliance question doesn’t become less significant once the transaction closes.

Post-Acquisition Integration Is the Operational Test

An acquiring company can conduct excellent due diligence and still create exposure if it fails to integrate the acquired business effectively. Post-acquisition integration is where the buyer’s compliance expectations become operational. Employees need to understand the acquiring company’s Code of Conduct, policies, reporting mechanisms, investigation procedures, third-party requirements, approval processes, and internal controls. High-risk third parties may require additional diligence. Contracts may need updated compliance provisions. Financial controls may need harmonization. Employees need risk-appropriate training.

Integration should also reflect the acquired company’s actual risk profile. A business operating primarily in lower-risk markets with direct sales may require a different approach than a company that depends on agents and distributors in jurisdictions with substantial government interaction. Do not apply the same integration checklist mechanically to every acquisition.

The CCO should know which issues require immediate attention, which can be addressed over a reasonable integration period, and who is accountable for each significant action. Without ownership and monitoring, temporary integration gaps can become lasting control weaknesses.

Ygor and the Informal Organization

Ygor provides one of the movie’s most useful compliance lessons. He understands the Frankenstein estate better than Wolf does. He knows its history, its secrets, and how things actually work. Every organization has a formal structure and an informal operating system. The organizational chart describes reporting relationships. Policies describe required processes. Procedures identify approvals. Employees know how business actually gets done.

They know which approvals receive meaningful scrutiny and which are largely administrative. They know which managers routinely approve exceptions. They know which third parties have special relationships with executives. They know which controls become flexible near quarter-end. They know whether raising a concern is welcomed or career-limiting. This is why compliance risk assessment cannot rely exclusively on documents.

Policies lay out how an organization is supposed to operate. Interviews, focus groups, hotline information, investigations, transaction testing, third-party monitoring, audit findings, and employee surveys can show how it operates in practice. That distinction becomes particularly important following an acquisition. The buyer needs to understand not only the target’s compliance architecture but also its operating culture.

Institutional Memory Is a Compliance Control

Inspector Krogh represents the other side of organizational knowledge. He remembers the consequences of the original Frankenstein experiment because he experienced them personally. His perspective is shaped by history, not by Wolf’s confidence that the past can be managed differently. Companies need mechanisms for preserving similar institutional knowledge.

Investigations produce knowledge. Internal audits produce knowledge. Regulatory inquiries produce knowledge. Compliance monitoring and remediation projects produce knowledge. That knowledge can disappear surprisingly quickly. Employees retire. CCOs leave. Executives change roles. Board members rotate. Investigations close. Outside counsel completes an engagement. Remediation projects are marked complete.

Years later, new management may propose a business arrangement, third-party relationship, market strategy, or control change similar to one the organization previously determined was problematic. An effective compliance program should prevent important lessons from depending entirely on the memories of individual employees.

Significant investigation findings should inform future risk assessments. Root causes should influence control design. Remediation lessons should affect monitoring. Historical third-party concerns should remain available when relationships are reconsidered. An investigation’s purpose is not simply to resolve an allegation. It should also improve the organization’s understanding of its risks.

New Leadership and the Risk of Exceptionalism

Wolf demonstrates another challenge common to leadership transitions. New leaders often believe they can manage risks that previous leaders could not. Sometimes they can. New leadership may bring stronger systems, better controls, additional resources, and improved judgment. The problem arises when confidence leads management to discount why earlier controls or restrictions were established.

A new sales executive may propose reengaging a distributor previously terminated for compliance concerns. A new CEO may reconsider a market that previous management considered too risky. A new business leader may conclude that an approval requirement imposed after earlier misconduct is unnecessarily restrictive. Any of those decisions may be appropriate. Controls should not remain in place indefinitely simply because they are old. But management should understand the history before changing them.

Before removing a control, determine why it was created. Before reengaging a third party, understand why the relationship ended. Before changing monitoring requirements, identify the risk they were designed to address. Some controls become obsolete. Others represent lessons learned. Good governance distinguishes between the two.

Red Flags and the Governance Response

The central compliance issue arises when Wolf learns the Monster is alive. At that point, the question moves from discovery to response. Corporate compliance systems serve a similar purpose. Internal controls, monitoring, Internal Audit, risk assessments, investigations, hotlines, and management reporting should surface significant information.

The effectiveness of those systems depends upon what happens after the information arrives. The Evaluation of Corporate Compliance Programs (ECCP) suggests such inquiries as: Was the issue investigated? Was it escalated appropriately? Did management assign remediation? Was completion tracked? Was effectiveness tested? Did significant information reach the board or appropriate committee? A sophisticated reporting system provides little protection if material concerns repeatedly reach decision-makers without producing action.

For a CCO, this means escalation protocols matter. The organization should understand which issues remain within normal management processes, which require senior management attention, and which warrant board notification.

Legacy Third Parties Require Fresh Review

Inherited third-party relationships deserve particular attention because longevity can create a false sense of security. The distributor has worked with the business for fifteen years. The consultant is well known locally. The customs broker has always handled interactions with government agencies. No significant problems have been reported previously. Those facts provide context. They do not replace risk-based oversight.

Acquisitions and leadership transitions provide an opportunity to reassess significant legacy relationships. Is the third party still necessary? Is the business rationale documented? Is beneficial ownership information current? Has the risk profile changed? Are payment arrangements appropriate? Are contracts current? Has monitoring identified concerns? Longstanding relationships should not automatically be grandfathered into the current compliance program. Some may warrant closer attention precisely because they were established under different controls, different management, and different expectations.

Practical Actions for the CCO

Son of Frankenstein suggests a practical agenda for compliance leadership. Due diligence should examine actual business operations, not just the existence of policies. Unresolved diligence issues should move directly into the integration plan with defined ownership and deadlines. Integration should be risk-based and should include controls, training, reporting mechanisms, investigations, and third-party oversight.

Significant legacy third parties should be reassessed rather than automatically accepted. Preserve investigation findings and past control failures as institutional knowledge and incorporate them into future risk assessments. New leadership should understand why significant controls were established before deciding to eliminate or weaken them. Finally, significant inherited risks should have clear owners. Issues that sit between the transaction team, business leadership, Legal, Compliance, Finance, and Internal Audit can otherwise remain unresolved because everyone assumes someone else is responsible.

The Compliance Lesson

Son of Frankenstein demonstrates the difference between responsibility for creating a problem and responsibility for managing one. Organizations routinely inherit compliance risks through acquisitions, leadership transitions, longstanding business practices, third-party relationships, and unresolved control weaknesses. New management should not be treated as responsible for conduct that occurred before it arrived. Its responsibility begins with the response.

Effective compliance requires the organization to identify inherited risks, prioritize them by significance, assign ownership, integrate acquired operations, preserve institutional knowledge, and verify corrective actions. That is the business lesson from Wolf von Frankenstein’s return to the family estate. The value of an inheritance cannot be separated from its risks.

The next stage of the Frankenstein story raises another familiar compliance issue. Organizations can identify problems, investigate them, revise policies, conduct training, complete remediation plans, and close findings. Yet sometimes the same problem returns.

In our next selection, we consider The Ghost of Frankenstein. In this movie, the compliance issue is no longer discovery or inheritance. It is program effectiveness. If management says the problem has been remediated, what evidence demonstrates that the remediation actually worked?

For a discussion on these topics and a review of the movie, check out Timothy and Fiona in this episode of Popcorn and Compliance.

Categories
Red Flags Rising

Red Flags Rising: S01 E47: David Metcalf, U.S. Attorney for the Eastern District of Pennsylvania

Mike and Brent welcome to the podcast the U.S. Attorney for the Eastern District of Pennsylvania, David Metcalf.

They discuss the U.S. Attorney’s background working as a government lawyer, a lawyer in private practice, and an in-house lawyer at a large company, and what perspectives that varied background has given him (01:42); the potential pitfalls of over-reliance on legal privilege, especially for company employees (09:00); the relevance of the Japanese classic film Rashomon (1950) to investigations and compliance, especially in terms of mooting various perspectives when making decisions where “knowledge” or “willfulness” is relevant (11:06); the important mission and objectives of the U.S. Department of Justice’s (DOJ’s) new National Fraud Enforcement Division (NFED) (13:07); how the U.S. Attorney sees trade and export or import enforcement unfolding nationally and in the Eastern District of Pennsylvania (19:46); the importance of frameworks and tools, such as Brent’s Fraud Four-Circle Framework to identifying and effectively responding to potential issues (23:53); the importance to the DOJ of voluntary disclosures and the incentives being offered to corporations today (26:56); and the broader work of the Eastern District of Pennsylvania, including how they develop and how people can report cases (33:07). They then conclude with the latest edition of Brent’s “Managing Up” segment (34:31).

More about U.S. Attorney David Metcalf

The Eastern District of Pennsylvania’s White Collar Justice Program

The DOJ’s National Fraud Enforcement Division

More about the 1950 classic Japanese film “Rashomon”

Contact Brent: brent@redflagsrising.com

More about Brent

Connect with Brent on LinkedIn

Contact Mike: michael.huneke@morganlewis.com

More about Mike

Connect with Mike on LinkedIn