In the first post in our Leonardo Compliance Framework, the Mona Lisa introduced Refine: the discipline of continuous improvement. An effective compliance program should learn from investigations, monitoring, risk assessments, employee feedback, control failures, and business changes. The program should evolve because the organization knows more today than it knew yesterday. That brings us to the second principle: investigate.
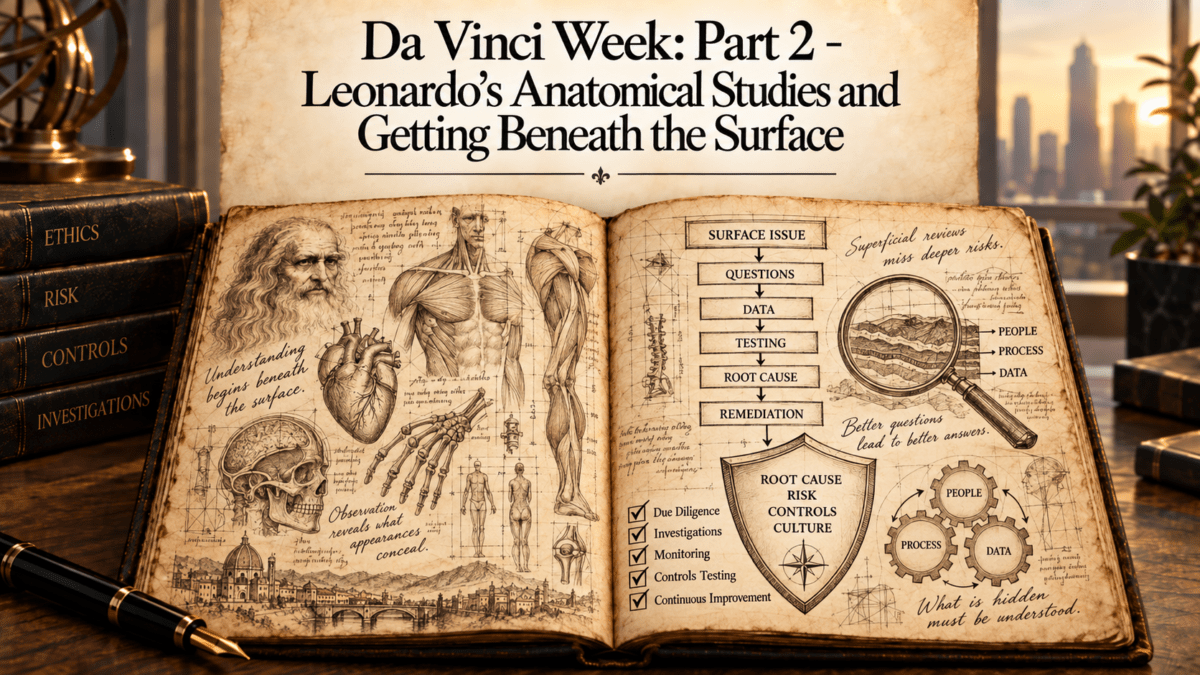
Leonardo was not satisfied with observing the human body from the outside. His anatomical studies examined muscles, bones, organs, movement, and the relationships among different parts of the body because he wanted to understand how the entire system worked. That provides a useful model for the modern Chief Compliance Officer because an effective corporate investigation should accomplish more than determine whether an employee violated a policy. It should help the organization understand why the conduct occurred, which controls failed, what incentives influenced behavior, whether management contributed to the problem, whether similar conditions exist elsewhere, and what should change as a result.
The compliance lesson from Leonardo is to look beneath the visible misconduct and understand the system that produced it.
An Investigation Is More Than a Search for Misconduct
Consider a familiar scenario. An investigation establishes that a sales employee used a consultant to make an improper payment to secure business. The company confirms the misconduct, terminates the employee and consultant, documents the findings, and closes the matter.
That process may answer the immediate legal and disciplinary questions, but it does not necessarily answer the larger compliance question. The company should also understand why it hired the consultant, how it approved the relationship, what due diligence it performed, whether it identified red flags, how it compensated the consultant, and how the resulting invoices and payments moved through the organization. Management should consider whether commercial incentives contributed to the conduct, whether supervisors encountered warning signs, and whether similar consultants are being used elsewhere.
If the company concludes only that one employee violated the anti-corruption policy, it may remove the individual while leaving intact the conditions that allowed the misconduct to occur. The investigation has then addressed the actor without addressing the vulnerability. That is why investigations should be viewed as a source of organizational intelligence.
Root Cause Should Drive Remediation
Root-cause analysis is where Leonardo’s anatomical method becomes particularly relevant. The objective is to move from the visible event to the systems underneath it. The Evaluation of Corporate Compliance Program (ECCP) states, “Finally, a hallmark of a compliance program that is working effectively in practice is the extent to which a company can conduct a thoughtful root.” It asks: What is the company’s root cause analysis of the misconduct at issue? Were any systemic issues identified? Who in the company was involved in making the analysis?
Root-cause analysis helps the company distinguish symptoms from causes, and that distinction should determine remediation. A response directed only at the visible misconduct may create the appearance of action without materially reducing the underlying risk.
This is also why significant investigations should test assumptions about the compliance program. If an intermediary engages in misconduct despite passing third-party due diligence, the company should examine whether the process missed information it reasonably could have identified. If an employee disguises improper payments, Compliance and Finance should understand how the relevant financial controls were circumvented. If retaliation occurs after an employee raises a concern, the organization should determine whether its anti-retaliation controls function in practice.
A well-designed compliance program can still experience misconduct. No reasonable system eliminates all risk. Effectiveness is measured by how the organization detects misconduct, responds, learns from failures, and strengthens the program when it identifies weaknesses.
Follow the Decision Trail
Investigators naturally follow evidence by reviewing documents, interviewing witnesses, analyzing transactions, and reconstructing events. Compliance investigations should also follow the decision trail because misconduct frequently passes through business processes designed to create accountability.
The investigation should identify who selected and approved a problematic third party, who authorized exceptions or unusual compensation, who approved payments, who received warnings, and who decided whether concerns warranted escalation. This becomes especially important when misconduct involves senior personnel, high performers, or commercially significant relationships.
The purpose is not to assign blame indiscriminately across every function connected to an incident. It is to understand where accountability actually resided and whether the people responsible for operating or supervising controls fulfilled those responsibilities.
A decision trail can reveal that misconduct was not simply the act of one individual. Other employees may have facilitated the conduct, ignored warning signs, approved questionable transactions, or failed to escalate information. Conversely, the evidence may demonstrate that established controls operated appropriately and that the individual deliberately circumvented them.
Organizational Justice Requires Consistency
Investigations also play a central role in corporate culture. Employees watch how organizations respond to allegations, particularly when cases involve senior executives or high-performing employees. They notice whether powerful people receive different treatment and whether employees who raise concerns suffer professional consequences. This makes consistency an important component of organizational justice, which the ECCP identifies as a part of every compliance program.
Consistency does not require identical outcomes. Facts, intent, responsibilities, prior conduct, cooperation, supervisory duties, and other legitimate considerations can justify different consequences. What matters is that the organization uses a credible process and applies its standards without creating privileged classes of employees.
Investigation governance is therefore important. The company should establish clear decision rights concerning whether allegations require investigation, who determines scope, who approves closure, how disciplinary decisions are made, when conflicts of interest require independent handling, and when matters involving senior executives should be escalated to the Audit Committee or board. These governance arrangements should be in place before a sensitive case arises.
Accountability should also extend beyond the individual who directly engaged in misconduct. Management behavior matters. A supervisor who ignored repeated warning signs, encouraged excessive risk-taking, approved unjustified exceptions, or created incentives that contributed to misconduct may raise separate accountability issues.
If employees see junior personnel disciplined while supervisors face no consequences for meaningful oversight failures, the company may signal that accountability flows only downward. Credible organizational justice requires a more consistent approach.
Investigation Data Is Enterprise Risk Intelligence
Individual investigations explain specific events. Aggregated investigation data can reveal enterprise-wide patterns, making it an important compliance asset. A CCO must understand which allegations recur, whether particular business units or managers appear repeatedly, where investigations are delayed, what root causes occur most often, whether similar control failures appear across jurisdictions, and whether employees who raise concerns subsequently experience unusual turnover or other adverse outcomes.
Those patterns can identify emerging risks that individual case files may not reveal. The data must be interpreted carefully. A business unit with a high number of hotline reports may have significant cultural problems, or it may have a healthy speak-up environment in which employees trust the reporting system. A location with few reports may have an excellent culture, or employees may fear retaliation.
Investigation data works best when combined with other information, including hotline trends, employee surveys, HR data, audit findings, transaction monitoring, exit interviews, and business knowledge. The objective is not simply to count cases but to use investigative information to understand the organization more effectively. This is the Leonardo approach in practice: observation combined with inquiry.
AI Changes the Investigation Function
Artificial intelligence is also changing corporate investigations. AI tools may assist with document review, chronology development, translation, pattern identification, data analysis, and summarization. Used appropriately, these capabilities may allow investigation teams to analyze larger volumes of information and identify relationships more efficiently.
They also create significant governance issues because investigations frequently involve some of the company’s most sensitive information. Before using AI, the organization should understand what data it will provide to the system, whether the material includes privileged, confidential, personal, or commercially sensitive information, where the data will be processed and retained, and what contractual and technical protections apply. Once again, the ECCP puts this onus on your compliance function.
Reliability is equally important. Investigators need a process to validate AI-assisted analysis and identify inaccurate or unsupported outputs. AI use should not obscure how a significant investigative conclusion was reached or prevent the company from explaining the evidence supporting its decision.
Human accountability should remain clear. AI can assist investigators, but it should not replace professional judgment concerning scope, credibility, findings, discipline, or remediation. The broader governance principles reflected in the NIST AI Risk Management Framework and ISO/IEC 42001 can help organizations think about risk management, human oversight, documentation, and monitoring. Still, the fundamental investigation requirements remain confidentiality, accuracy, fairness, privilege, and defensibility.
Connect Investigations to Remediation and Lessons Learned
Companies sometimes separate investigations and remediation too sharply. Legitimate reasons exist to maintain appropriate independence between fact-finding and certain management decisions, but the compliance program still needs a clear mechanism to convert investigative findings into corrective action.
For significant matters, management should understand what failed, why it failed, whether the weakness could exist elsewhere, what corrective action is required, who owns that action, and how the company will determine whether remediation worked. This turns an investigation from a historical examination into a forward-looking compliance tool. Without that connection, an organization can become highly proficient at investigating the same problem repeatedly without becoming better at preventing it.
Lessons learned should also travel beyond the specific business unit or jurisdiction involved. If an investigation in one market identifies improper distributor discounts caused partly by weak approval controls, the company should consider whether comparable controls exist elsewhere. If employees use personal messaging applications to circumvent company systems, management should assess whether the practice extends beyond the employees involved in the investigation. If an AI incident reveals that employees can deploy unapproved tools without effective technical restrictions, the organization should consider the broader governance implications.
This does not require distributing confidential investigative details throughout the company. It means converting case-specific findings into enterprise risk intelligence. Depending on the issue, the lesson may lead to changes in controls, risk assessments, monitoring, training, policies, management communications, or incentive structures. That is how Investigate feeds Refine.
What the Board Should Understand About Investigations
Boards and Audit Committees should resist evaluating the investigation function primarily through case counts. Knowing how many matters were opened and closed provides useful operational information, but it offers limited insight into program effectiveness.
Directors should understand what the company is learning from investigations. Significant themes, recurring root causes, internal control weaknesses, unusual patterns across business units, retaliation concerns, and the status and effectiveness of remediation all provide more meaningful information about compliance risk.
The board should also understand whether investigative resources match the company’s risk profile. Significant cases should not remain unresolved because the organization lacks appropriate staffing, cross-border expertise, data capabilities, employment-law support, or access to information. Matters involving senior personnel should be handled through processes designed to preserve independence and avoid conflicts.
The board does not need to manage individual investigations. Its role is to understand whether the investigation system provides reliable information about significant compliance risks and whether management responds appropriately to what that system reveals.
Getting Beneath the Surface
Leonardo’s anatomical studies give compliance professionals a useful model for investigations because the visible event may be only the first indication of a larger systemic issue. An improper payment may reveal a third-party weakness that exposes deficiencies in due diligence, technology, ownership, incentives, or management oversight.
The investigator’s task is to understand those connections without allowing every matter to become an unlimited enterprise-wide inquiry. Scope should remain proportionate to the seriousness, complexity, and potential reach of the issue. The objective is disciplined curiosity: understanding whether the evidence points to an isolated act or a broader weakness in the compliance system.
For the CCO, the practical lesson is that investigations should do more than establish whether a rule was violated. Significant matters should help the organization understand the controls, incentives, management decisions, and business conditions that contributed to the conduct. Root-cause analysis should drive remediation, investigation findings should test assumptions about program effectiveness, aggregated case data should inform enterprise risk assessment, and lessons learned should improve controls beyond the immediate matter.
That is Investigate, the second principle of the Leonardo Compliance Framework. Finding misconduct matters, but the greater compliance value comes from understanding the system that produced it and using that knowledge to reduce the likelihood of recurrence.
From Investigation to Innovation
Investigation helps the compliance professional understand how existing systems work and why they sometimes fail. Leonardo, however, was equally interested in systems that did not yet exist, which takes us to the third principle in the Leonardo Compliance Framework: Innovate.
In Blog Post Three, Leonardo’s Flying Machines and AI Governance, we will use Leonardo’s studies of flight to examine responsible innovation in 2026. Artificial intelligence and increasingly agentic technologies are moving from generating information to taking action within business processes, raising new questions about risk classification, human accountability, third-party AI, data governance, testing, monitoring, NIST AI RMF, and ISO/IEC 42001.
Leonardo’s willingness to imagine flight provides the innovation lesson. For the modern CCO, the corresponding governance task is ensuring the enterprise understands the risks, controls, and accountability needed before giving new technology meaningful authority inside the business.