Categories
Blog

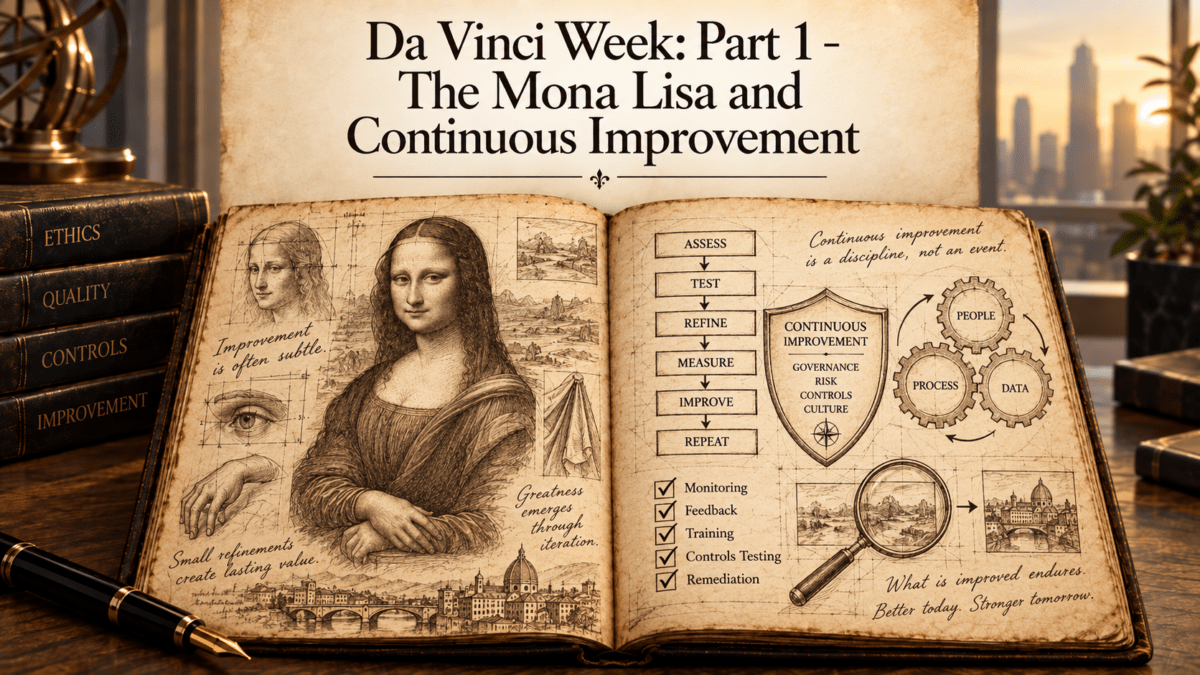
Da Vinci Week: Part 1 – The Mona Lisa and Continuous Improvement

I recently wrote a five-part blog series on compliance through Michelangelo’s lens. In our Michelangelo Compliance Framework, we used five extraordinary projects to explore five disciplines of the modern compliance function: Challenge, Execute, Defend, Build, and Govern. Michelangelo gave us a model of the compliance professional as a builder. His work showed the importance of structure, execution, resilience, accountability, and the ability to turn an ambitious vision into something enduring.

This week, I want to do the same through the lens of Leonardo da Vinci, who gives us a different model. Leonardo was an observer, investigator, experimenter, engineer, anatomist, artist, and relentless student of how things worked. Where Michelangelo offers lessons about building, Leonardo offers lessons about learning. That distinction underpins our five-part Leonardo Compliance Framework: Refine, Investigate, Innovate, Monitor, and Document. In this blog post 1, we begin with Refine and Leonardo’s most famous painting, the Mona Lisa.

The compliance lesson is continuous improvement. An effective compliance program is never truly finished because the business it supports is never truly static. Markets change. Employees change. Third parties change. Regulations change. Technology changes. Criminal methodologies change. Artificial intelligence is accelerating many of those changes simultaneously. For the Chief Compliance Officer (CCO) or compliance professional in 2026, the question is therefore not simply whether the company has a compliance program. The better question is whether the program is materially better today because of what the organization learned yesterday.

The Compliance Program Is Never Finished

One fascinating aspect of the Mona Lisa is Leonardo’s extended relationship with the work. He kept refining it as he developed his understanding of light, anatomy, optics, and human perception. That provides a useful metaphor for compliance because companies often approach compliance initiatives through the language of completion. Policies are issued, training is delivered, third-party systems are implemented, investigations are closed, remediation projects are completed, and risk assessments are presented to the board.

A policy issued three years ago may no longer address how the business operates. A successful third-party implementation may not account for changes in the company’s distribution model. A 100 percent training completion rate does not demonstrate that employees can apply the training when confronting an ethical problem. Closing a remediation item does not establish that the revised control reduced the underlying risk.

Leonardo offers a different approach. Completion should create an opportunity for observation and learning. Management should understand what worked, what did not work as expected, what changed in the business, and whether those lessons justify refinement of the program. That is continuous improvement.

Turn Compliance Failures Into Organizational Knowledge

The DOJ has made clear in the most recent iteration of the Evaluation of Corporate Compliance Programs (ECCP) that continuous improvement sits at the heart of modern expectations for compliance program effectiveness. A risk-based program should evolve as the company’s risks evolve, using risk assessments, investigations, audits, monitoring, employee feedback, transaction data, and lessons learned to inform changes. A company that identifies the same weakness year after year without changing its response has not created an effective learning system.

Leonardo’s approach to understanding the natural world was to look beneath the visible surface. Compliance professionals should apply the same discipline. Misconduct often signals a deeper weakness in the system, and root-cause analysis helps identify it and use the lesson to improve the program.

Risk Assessment Should Produce Management Action

The compliance risk assessment provides another important opportunity for refinement. Companies frequently devote substantial resources to identifying and ranking risks, producing a heat map, presenting the findings to management and the board, and repeating the process the following year.

Here the ECCP asks, “Is the risk assessment current and subject to periodic review?” Is the periodic review limited to a “snapshot” in time or based upon continuous access to operational data and information across functions? Has the periodic review led to updates in policies, procedures, and controls? Do these updates account for risks discovered through misconduct or other compliance program issues?

The principle applies to artificial intelligence. If AI adoption changes the company’s risk profile, the risk assessment should lead to governance action through measures such as an AI inventory, risk classification, approval processes, human oversight, monitoring, or technical controls.

A mature compliance program should be able to draw a line from an identified risk to a management decision. If the risk profile changes while resources, controls, monitoring, and governance remain unchanged, the risk assessment has generated information without generating action.

Use Data to Refine the Program

Leonardo was a relentless observer who recorded what he saw and used those observations to develop new ideas. Modern compliance functions possess an advantage he could scarcely have imagined: enormous quantities of organizational data.

Hotline information can reveal cultural patterns. Investigation data can identify recurring allegations and root causes. HR data may indicate retaliation. Transaction information can identify unusual payments. Third-party data can reveal concentrations of risk, while audit findings can identify recurring control weaknesses.

But these insights are not enough. Are these insights put into practice? The ECCP inquires: Does the company have a process for tracking and incorporating into its periodic risk assessment lessons learned either from the company’s own prior issues or from those of other companies operating in the same industry and/or geographical region?

Compliance analytics should not become a competition to create the most sophisticated dashboard. The objective is better decision-making. A business unit with very few hotline reports, for example, could have an excellent culture or an environment in which employees are reluctant to speak. The number alone does not tell the whole story.

Compliance should therefore combine quantitative information with qualitative evidence, including employee surveys, focus groups, exit interviews, investigations, management discussions, and audit findings. The objective is to understand what the data mean in the business context.

AI Accelerates the Need for Refinement

Artificial intelligence makes continuous improvement increasingly important because AI systems and their uses can change faster than traditional corporate governance cycles.

The ECCP asks companies to consider how emerging technologies such as AI affect their ability to comply with criminal laws, how related risks are incorporated into enterprise risk management, and how organizations mitigate unintended consequences and potential misuse. The ECCP asks some pointed questions: How does the company assess the potential impact of new technologies, such as artificial intelligence (AI), on its ability to comply with criminal laws? Is management of risks related to the use of AI and other new technologies integrated into broader enterprise risk management (ERM) strategies? What is the company’s governance approach to using new technologies such as AI in its commercial business and compliance program? The implication for the CCO is significant: AI risk cannot be treated as a once-a-year compliance exercise.

NIST’s AI Risk Management Framework and ISO/IEC 42001 provide useful approaches to this challenge because both emphasize governance and ongoing risk management. For the CCO, the broader lesson is that AI governance should operate as a management system rather than a policy-writing project. The organization needs to learn from incidents, testing, employee behavior, technological changes, and evolving business use, then adjust governance accordingly. The principle is the same as the Mona Lisa: refinement should follow learning.

Move the Board Conversation From Activity to Learning

Boards and Audit Committees can reinforce this discipline by shifting the compliance conversation. Compliance presentations frequently focus on activity metrics: employees trained, investigations closed, third parties reviewed, policies updated, and remediation items completed. These measures provide useful information about program operations, but they do not necessarily demonstrate effectiveness.

Directors should also understand what the organization learned during the reporting period, what investigations revealed about controls, what monitoring identified that management did not previously know, how the risk profile changed, and what the compliance function changed as a result.

The board should also understand whether those changes worked. This moves oversight from compliance activity to compliance effectiveness. It allows the CCO to present Compliance not simply as a collection of programs and controls but as a management system that identifies risk, learns from experience, and improves organizational decision-making.

The Mona Lisa Principle: Disciplined Refinement

Leonardo’s Mona Lisa gives the modern compliance professional a straightforward lesson about continuous improvement. An effective compliance program should develop through observation, evidence, learning, and a willingness to reconsider earlier decisions when circumstances justify change. The objective is not perpetual revision. It is disciplined refinement.

That distinction matters because continuous improvement can become counterproductive if it produces continuous disruption. Employees need stability, controls need sufficient time to operate, and management needs enough information to distinguish a meaningful trend from temporary noise. A compliance function that repeatedly changes policies, procedures, training, and controls without a clear risk-based rationale can create confusion rather than effectiveness.

Program refinement should therefore follow evidence. An investigation may reveal a systemic control weakness. Employee feedback may demonstrate that a policy is difficult to understand or apply. Monitoring may show that a control generates excessive false positives or is routinely circumvented. A regulatory development may require a different process, while an acquisition, new market, or technological change may materially alter the company’s risk profile. Artificial intelligence may introduce capabilities and risks that did not exist when the original governance structure was designed.

The CCO should have a disciplined process for converting those developments into program changes. Management should understand what triggered the proposed change, what risk it addresses, who owns implementation, and how the organization will determine whether the change produced the intended result. In this sense, continuous improvement should itself be governed.

A mature CCO should also be able to explain why today’s compliance program differs from the one the company operated two or three years ago. The answer should not simply be that policies were updated or new technology was purchased. The program should have changed because the organization learned something about its risks, controls, employees, third parties, culture, or business model and acted on that knowledge.

That is the central lesson of Refine, the first principle of the Leonardo Compliance Framework. Completion should not be confused with effectiveness. Root-cause analysis should produce program improvement, risk assessments should lead to management action, and data should help the organization understand what is happening rather than simply populate dashboards. When the evidence demonstrates that change is necessary, the organization should refine the program and then determine whether the refinement worked.

Leonardo models the compliance professional as a student of the organization. The CCO observes how the business operates, learns from failures and successes, and uses that knowledge to improve the compliance system. The measure of continuous improvement, therefore, is not how often the program changes. It is whether the program becomes more effective because the organization has learned.

From Refinement to Investigation

Continuous improvement depends upon understanding why problems occur. A company cannot meaningfully refine its compliance program if it treats each incident as an isolated act of employee misconduct. It must examine the systems, incentives, controls, management decisions, and behaviors that produced the outcome. That takes us to the second Leonardo principle: Investigate.

In Blog Post Two, we will consider Leonardo’s Anatomical Studies and will use Leonardo’s study of the human body as a framework for corporate investigations. Just as Leonardo looked beneath the surface to understand how interconnected systems functioned, modern compliance investigations should move beyond identifying misconduct to understanding its causes. We will examine how root-cause analysis connects investigations to remediation, why organizational justice matters, how investigation data can reveal systemic weaknesses, and what boards should understand when management reports that an investigation has been closed.
Categories
Sunday Book Review

Sunday Book Review: September 20, 2026, The New Books On Corporate Culture Edition

In the Sunday Book Review, Tom Fox considers books that would interest compliance professionals, business executives, or anyone curious about the subject. It could be books about business, compliance, history, leadership, current events, or any other topic that might interest Tom. In this episode, we look at 4 new books on corporate culture that have been released or will be released in the fall of 2026.

  1. Friction by Maggie Sass and Ross Blankenship
  2. The Corporate Artist by Morgan Sage Norman
  3. Work Shouldn’t Hurt by Dr. Lori Campbell
  4. Simple Rules, Extraordinary Results by Addison Killeen

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Compliance and AI

Compliance and AI: Clarence Chio on how AI Transforms Vendor Risk Into Continuous Evidence

What is the intersection of AI and compliance? What about machine learning? Are you using ChatGPT? These questions are just three of the many we will explore in this cutting-edge podcast series, Compliance and AI, hosted by Tom Fox, the award-winning Voice of Compliance. In this episode, host Tom Fox visits with Clarence Chio, co-founder & CEO of Coverbase.

Chio and Coverbase are helping lead the shift toward AI-driven third-party risk management and vendor security. Drawing on his background in machine learning, security, and compliance, he argues that vendor due diligence is moving beyond slow, human-to-human questionnaire exchanges toward AI agents that can analyze standardized, verified evidence directly. He sees this as the next evolution of trust centers and attestation workflows but cautions that automation should not replace genuine accountability in areas that require human judgment. In his view, the best AI systems will accelerate reviews, flag uncertainty, and escalate gray areas to people rather than hallucinate or blindly accept responses.

Key highlights:

  • AI-Driven Vendor Assurance with Trust MCP
  • 400-Question Vendor Review Paperwork Loop
  • Continuous exposure points in trust centers
  • AI Analyzing Vendor Evidence to Predict Breaches
  • Pristine Questionnaire Answers, Human Judgment in Due Diligence
  • Vendors’ Vulnerabilities Become Your Data Vulnerabilities

Resources:

Coverbase

Clarence Chio on LinkedIn

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
Daily Compliance News

Daily Compliance News: September 18, 2026, The 21 Air Suspended Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • Amazon suspends 21 Air. (NYT)
  • Congress wants FTC to investigate Amazon/Walmart bots. (WSJ)
  • Hamm into Venezuela. (NYT)
  • John Eastman wants the Supreme Court to overturn his disbarment. (Reuters)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Balance in Crisis

Balance in Crisis: Aligning Virtues, Priorities, and Communication

We live in an age of constant motion. We move faster, communicate more, and accomplish more than ever before, yet many people feel exhausted, fragmented, and quietly unsettled. Our lives are full but are not integrated. In this podcast, Balance in Crisis, Kenneth O’Neal challenges the belief that balance is a myth or something achieved by doing less. True balance is built. It results from alignment and intentionally ordering life around what matters most. When values, beliefs, and daily actions are misaligned, even success carries a hidden cost. Burnout, confusion, strained relationships, and loss of purpose often follow. In this inaugural episode, host Tom Fox and Kenneth O’Neal introduce “Balance in Crisis” by discussing how to align virtues, priorities, and communication.

Today, we introduce a podcast series with author Kenneth O’Neal on his new book, Balance in Crisis. O’Neal explains that “balance” means alignment, not an equal 50/50 split of time, between personal life, work life, virtues, values, decisions, and actions. He frames crisis as an “alarm” that wakes people up to misplaced priorities and misalignment, prompting reflection on what the crisis is trying to teach. Drawing from coaching examples, he describes leaders realizing late that overwork damaged family relationships and emphasizes accepting mistakes and creating a plan for a meaningful life. The discussion highlights effective, ongoing communication, asking questions, seeking truth, avoiding blame, and listening, all applied to family and workplace relationships, including marital strain.

Key highlights:

  • What Balance Really Means
  • Recognizing a Crisis
  • Effective Conversations
  • Rebuilding With Openness

Resources:

Kenneth O’Neal

Balance in Crisis

Book a Clarity Call

Categories
Daily Compliance News

Daily Compliance News: September 17, 2026, The Caught on Tape Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • Former top prosecutor in Ukraine caught on tape. (NYT)
  • Cyberattacks on Texas-bound tankers. (WSJ)
  • Hegseth made women compete in men’s fitness. Guess what—they already did. (The War Horse)
  • Must AI companies disclose ‘dangerous events’? (Reuters)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Magnificent 7 Rides Again

The Magnificent 7 Rides Again: Elaine Capers on Returning to Painting After the 2025 Flood

Welcome back to The Magnificent 7 Rides Again, a captivating podcast series that delves into the vibrant world of seven talented female artists painting amid the breathtaking landscapes, wildlife, and vistas of the Texas Hill Country. Join us as we explore their creative journeys, uncover the inspirations behind their work, and celebrate their unique perspectives on art and life. Host Tom Fox welcomes painter Elaine Capers back.

They discuss her past year of creating art after the devastating 2025 flood, which led her to paint one memorializing piece, then spend six weeks not painting before resuming in late April, inspired by blooming mountain laurels. Capers recounts participating in a successful two-day art show at LJ’s Vineyards and exhibiting with the Guadalupe Watercolor Group, where she sold a painting. She describes seasonal changes in Texas greens from fresh lime to dusty olive and fall tones. Capers reflects on how the Magnificent Seven group has challenged her skills and built community, previews West Texas works including a Pecos River scene and an 18×24 “Waldemar Crossing,” and notes repeat collectors, families at shows, and teaching children.

Key highlights:

  • Creative Slump After Flood
  • Mountain Laurels Revival
  • Seeing Seasonal Greens
  • What Magnificent Seven Means
  • Big Piece Waldemar Crossing

Resources:

Elaine Capers on:

Instagram

Facebook

Texas Hill Country Podcast Network

The Hill Country Artists Facebook Page

Categories
Trekking Through Compliance

Trekking Through Compliance: The Science of Star Trek TOS: Wormholes: Real Gravity Behind Fictional Time Travel

Welcome to Trekking Through Compliance. We recently finished Season 8, where we reviewed all 79 episodes of Star Trek: The Original Series (TOS) for compliance, ethics, and leadership lessons. This year, we added analysis from Timothy and Fiona, two AI-generated voices that brought another perspective. I had so much fun this season that I decided to extend it with episodes on the science and science issues in Star Trek TOS. I am joined in this exploration by my good friend Dr. Ben Locwin, a healthcare futurist and astrophysicist, who brings a scientific perspective to the discussion of Star Trek’s technology. In each episode, we use one or more TOS episodes to introduce topics such as warp drive, wormholes, phasers, and medical practice. In the second episode in this series, we look at wormholes. It’s a ton of fun, and I know you will enjoy it.

Locwin explains that black holes are incredibly dense objects with gravity so strong that not even light can escape, and that this extreme gravity can slow time through time dilation. Locwin also points to experiments from NASA and the Air Force that support Einstein’s predictions, showing that time moves more slowly at higher speeds and in stronger gravitational fields. While he discusses wormholes and other theoretical possibilities, he emphasizes that real physics suggests time travel into the past is unlikely because nature may protect itself from paradoxes.

Highlights:

  • Solar Slingshot Whisks Enterprise Back to 1960s
  • Black hole event horizon and time slowing
  • Wormholes needing negative mass

Resources:

⁠⁠Excruciatingly Detailed Plot Summary by Eric W. Weinstein⁠⁠

⁠⁠MissionLogPodcast.com⁠⁠

⁠⁠Memory Alpha

Ben Locwin on LinkedIn

Categories
Hill Country Authors

Hill Country Authors Podcast: Dispatches from Berlin: Carol J. Williams on the Fall of the Berlin Wall and Lessons from Eastern Europe

Welcome to a new season of the award-winning Hill Country Authors Podcast, sponsored by Stoney Creek Publishing. In this podcast, Hill Country resident Tom Fox visits with authors who live in and write about the Texas Hill Country. Host Tom Fox welcomes back journalist and author Carol J. Williams to discuss her historical fiction trilogy, which continues with Dispatches from Berlin, which releases on October 27th.

Carol J. Williams discusses how Soviet economic decline and leaders like Andropov set the stage for Gorbachev’s glasnost and perestroika, the effects of the arms race and summits with Reagan, and how Chernobyl undermined trust in openness. She describes the Soviet Union’s dependence on Eastern Bloc satellites for security and goods, and the critical role of journalism in documenting rapid change. Carol J. Williams recounts the accidental dynamics of November 9, 1989, that opened the Berlin Wall, Helmut Kohl’s reunification strategy, and contrasts Germany’s success with Yugoslavia’s nationalist-driven wars, previewing a third, Sarajevo-based book. She shares where to find book details and preorder links.

Key highlights:

  • Gorbachev Reforms Begin
  • Shortages and Chernobyl Blow
  • Reforms Spread Eastward
  • From Yeltsin to Putin
  • Berlin Wall Opens By Accident
  • Reunification Kohl Strategy

Resources:

Carol J. Williams on Stoney Creek Publishing

Dispatches from Berlin

Podcast Cover Art

Nancy Huffman Fine Art

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

When an Effective CCO Is Labeled Difficult

A business leader calls a Chief Compliance Officer (CCO) difficult after a proposed distributor fails to provide basic ownership information. The transaction is important to the quarter. The CCO has asked for the missing information, explained the concern, and identified what is needed to proceed. In the performance discussion that follows, the focus shifts to whether the CCO understands the business.

This hypothetical presents a governance question. Did the CCO handle the matter poorly, or did an appropriate challenge expose a business practice management would prefer to leave alone? The answer requires evidence about the decision, the CCO’s conduct, and the operating environment. A label provides none of that.

Luis Velasquez examines this diagnostic problem in Why Effective Leaders Get Branded as Problems, published in Harvard Business Review. He identifies four sources of leadership friction: genuine skill deficits, historical reputation, overextension of a leadership strength, and organizational barriers. His framework provides a useful starting point for evaluating CCO effectiveness while protecting the independence necessary to perform the role. The compliance applications below build on his analysis.

Diagnose the Conflict Before Evaluating a CCO

Velasquez describes an evaluation trap in which organizations treat visible behavior as the explanation for friction while giving insufficient attention to context. Once a leader acquires a negative reputation, subsequent assessments can reinforce it without testing whether the original diagnosis was sound.

For compliance, this creates a particular risk. A CCO’s responsibilities include raising concerns that may complicate a transaction, challenge an executive, or require management to change an established practice. Friction can arise while the function is doing its job. It can also arise when compliance communicates poorly, applies inconsistent standards, or takes too long to decide. An effective evaluation must examine both possibilities.

Start with the event behind the criticism. What decision was required? What information was available? What did the compliance request say, when, and why? What alternatives did a CCO identify? Which actions by the business affected the outcome? These questions create a basis for assessing performance without assuming the conclusion.

Address Genuine Skill Gaps Directly

Velasquez’s first category recognizes that leaders sometimes lack a necessary capability. Applied to CCOs, relevant gaps may include unclear communication, weak prioritization, insufficient business knowledge, or ineffective delegation. Consider a CCO who repeatedly sends lengthy technical explanations without identifying the decision management must make. Executives may reasonably struggle to act on the advice. Similarly, a compliance team that treats every request as equally urgent can consume resources while delaying matters that warrant immediate attention.

Those are legitimate performance concerns when supported by recent examples and a clear account of their consequences. Agree on the improvement required, provide support, and assess the result. Independence does not excuse disrespectful conduct, poor execution, or unsupported recommendations. It gives a CCO room to exercise judgment while remaining accountable for the work’s quality and delivery. A sound review evaluates whether a CCO explains concerns clearly and helps the business identify acceptable ways forward where they exist.

Replace Old Reputation With Current Evidence

Velasquez’s second category concerns historical reputation. A leader may change while the organization still relies on an outdated account of how that person operates. A CCO who joined during a serious control failure may initially have imposed tight review requirements. Years later, colleagues may still describe the function as inflexible even after it has introduced clearer thresholds, delegated decisions, and improved turnaround times.

The evaluation process should test whether the criticism reflects current experience. Ask for specific recent interactions, the applicable requirements, and the outcome. Compare those accounts with evidence of how the process now works. Older incidents may remain relevant, but explain their continued significance rather than assume it.

A CCO can contribute by demonstrating improvement through current service measures, examples of resolved issues, and feedback from people who use the process. The objective is an accurate assessment. Favorable anecdotes alone are no more sufficient than a repeated negative label.

Recognize When a Strength Needs a Different Application

Velasquez distinguishes a missing skill from a strength used too broadly. That distinction matters for a compliance leader whose career has rewarded detailed review and personal control of important decisions. Those habits may help stabilize a troubled program. As the business grows, the same approach can create bottlenecks if routine matters still require a CCO’s personal involvement. The leader needs to develop the team and establish clear decision authority while retaining appropriate escalation for significant concerns.

The response should specify where judgment can be delegated, what standards apply, and how quality will be checked. This preserves the value of careful review while changing how it is delivered. A CCO should be willing to examine this possibility candidly. A complaint about delay may reveal poor business planning, an overly centralized compliance process, or both. Correcting one cause does not remove the need to address the other.

Examine Whether the Organization Undermines the Role

Velasquez’s fourth category addresses organizational barriers involving culture, resources, incentives, and decision rights. This is where the implications for compliance independence become particularly significant.

A company may require review before engaging a third party while rewarding executives who commit to start dates before review begins. It may expect timely investigations while restricting access to relevant records. It may ask a CCO to escalate serious concerns and then criticize the escalation as a failure to collaborate.

In each case, evaluate the contradiction alongside a CCO’s response. Coaching the leader to communicate more effectively may help, but it cannot supply missing authority or correct an incentive that rewards bypassing controls. A CCO should document the constraint, its practical consequences, and the proposed correction. Management should identify who will resolve it and by when. Repeated, material barriers belong in discussions with the responsible board committee, particularly when they prevent the function from carrying out agreed responsibilities.

Make Board Support Concrete

Board support for a CCO should be visible in the governance process. Directors need access to an account of significant compliance concerns that explains the facts, management’s response, and any unresolved differences. The responsible committee should also understand the basis for material criticism of a CCO’s performance. Where criticism arises from an executive whose conduct or decisions compliance has challenged, that context warrants examination. It does not automatically invalidate the criticism or establish retaliation.

An appropriately independent review should consider the substance of the concern, how it was raised, and the evidence behind any proposed personnel action. Human resources, legal, and the relevant board leadership should have clear roles consistent with the company’s governance arrangements. Regular private discussions between a CCO and ELT leadership (or the appropriate board committee) can help surface barriers before a performance dispute becomes entrenched. Directors should ask whether compliance has the access, resources, and authority needed to deliver what management expects.

Evaluate Effectiveness With Measures That Fit the Role

An evaluation based heavily on executive satisfaction can discourage necessary challenge. A review based solely on activity counts provides an equally incomplete picture. Assess the quality and timeliness of advice, the prioritization of risk, the development of the team, and the follow-through on significant issues. Consider whether recommendations are supported and whether remediation addresses the underlying problem. Business feedback remains useful when it is specific and examined in context.

The central discipline is to evaluate the work and its consequences. Agreement with management is not a reliable measure of effectiveness; disagreement alone does not demonstrate courage or sound judgment.

Action Steps for the CCO

Use Velasquez’s framework to improve how performance concerns are examined:

  1. Ask for specific evidence. Identify recent events, decisions, and consequences behind broad criticisms. Respond to substantiated concerns directly.
  2. Test all four explanations. Examine skill gaps, outdated reputation, overused strengths, and organizational constraints. Recognize that more than one may contribute.
  3. Agree on meaningful performance measures. Include advice quality, timeliness, prioritization, team capability, and remediation follow-through alongside contextualized business feedback.
  4. Document barriers to effective execution. Record missing resources, restricted access, conflicting incentives, or unclear authority, with proposed corrections and accountable owners.
  5. Establish a credible board review process. Clarify escalation and evaluation arrangements so significant concerns about a CCO and constraints on the role receive informed consideration.

Effective compliance leadership requires both sound judgment and the ability to make that judgment understood. Organizations strengthen accountability when they evaluate those capabilities fairly and address the conditions that prevent a CCO from using them.