Categories
Compliance Into the Weeds

Compliance into the Weeds: Emergency Podcast on Election Results

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into compliance-related topics, literally going into the weeds to explore them more fully. Looking for hard-hitting compliance insights? Look no further than Compliance into the Weeds!

In this special episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss the 2026 election results and what they may mean for compliance.

Key highlights:

  • Corruption investigations in Washington
  • Anti-corruption legislation and enforcement
  • AI regulation and Data Center moratoriums
  • Administration Staffing
  • State AGs and Business Courts in Texas
  • Prediction Markets
  • Supreme Court

 Resources:

Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds, was recently named one of the Top 25 Regulatory Compliance Podcasts, Top 10 Business Law Podcasts, and Top 12 Risk Management Podcasts. Compliance into the Weeds has been awarded a Davey, Communicator, and W3 Award, all for podcast excellence.

Categories
ACI FCPA Conference 2025

ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast Series, Dr. Hemma Lomax

In this episode of the FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series, Dr. Hemma Lomax discusses her panel, “Global Anti-Corruption Risk Assessment Masterclass: Building a Best-in-Class Risk-Based Compliance Program for 2027 and Creating a Single View of Compliance Risk: Leveraging AI to Connect Disparate Data Sources, Identify Emerging Risks, and Strengthen Compliance Oversight.” Some of the issues she discusses in this podcast and her panel presentation are:

  • Building a best-in-class compliance program in 2027
  • Keeping abreast of and using cutting-edge tech for your compliance program.
  • Incorporating emerging risks and Administration priorities into your program.

As global enforcement priorities shift and anti-corruption risks grow more complex, staying ahead requires direct insight from those shaping, interpreting, and navigating the regulatory landscape.

Returning to Washington, DC, this December 10-11, ACI’s flagship FCPA and Global Anti-Corruption Conference brings together an unparalleled gathering of government enforcement officials, in-house compliance leaders, and top legal practitioners from around the world. Gain firsthand insights, benchmark strategies with industry peers, and walk away with practical approaches to strengthen compliance programs, manage emerging risks, and prepare for what’s next. Few events offer this depth of expertise, access, and opportunity to connect with the global anti-corruption community.

I hope you can join us. For event details, click ⁠here⁠. As an extra benefit to podcast listeners, ACI is offering a 10% discount on the ⁠registration⁠ price. Use discount code D10-999-CPN27 to apply your discount.

The Compliance Podcast Network produces the ACI FCPA and Global Anti-Corruption Conference 2026 Speaker Preview Podcast series. ACI sponsors this series.

Categories
AI Today in 5

AI Today in 5: November 4, 2026, The Control and Sovereignty Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Compliance and insider trading on prediction markets.(FinTechGlobal)
  2. US government deregulation is making AI compliance harder. (Forbes)
  3. AI vendors join in liability for clinical AI mistakes. (HealthcareDive)
  4. Can chatbots infringe copyright law? (WSJ)
  5. The UK approach to AI framework. (FT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Great Women in Compliance

Great Women in Compliance: The View from the Starting Line: A New Generation of Compliance

What does the future of compliance look like through the eyes of someone preparing to enter the profession?

This week on Great Women in Compliance, Dr. Hemma R. Lomax welcomes Isabella (Izzy) Siegel, a Northeastern University student whose experiences have already taken her from local courtrooms to the U.S. Attorney’s Office, corporate compliance at TJX, and the United Nations in Geneva.

Izzy shares a fascinating perspective on going to college in the age of AI, watching universities evolve from prohibiting generative AI to teaching students how to use it responsibly. She also reflects on helping develop Copilot training for senior executives, rediscovering the value of foundational legal skills, and seeing firsthand how compliance shapes organizational culture.

One particularly powerful insight emerges from her work with compliance training data covering hundreds of thousands of employees: behind every number is a real person whose experience matters.

The conversation explores curiosity, practical learning, responsible innovation, and Izzy’s ambitions to turn policy and research into tangible impact. She also offers a thoughtful challenge to compliance leaders: embrace different backgrounds and perspectives when building the next generation of the profession.

A refreshing conversation about learning across generations, the evolving relationship between humans and AI, and why the future of compliance is in good hands.

Biography: 

Isabella (Izzy) Siegel is a student at Northeastern University and will graduate in December 2026 with a degree in Political Science and Business Administration. Her experience spans corporate compliance at TJX Companies, legal work with the U.S. Attorney’s Office for the Southern District of New York, and international research in Geneva. Passionate about international law, public policy, and the ethical implications of AI, Izzy is particularly interested in translating research and policy into meaningful, real-world impact. She hopes to build a career at the intersection of law, business, and global affairs.

Categories
Innovation in Compliance

Innovation in Compliance: Why Coverbase, Why Now: Native AI Speed and Evidence-Driven Third-Party Risk Management

Innovation comes in many areas, and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovators, thinkers, and creators on the award-winning Innovation in Compliance podcast. In this episode, host Tom welcomes Coverbase newcomers Brian Shaw (GTM leader) and Constantine Malaxos (Head of Alliances) to discuss why they joined in 2026 and what is changing in third-party risk management (TPRM).

They talk about Coverbase’s “native AI” technology, rapid innovation, and client impact—moving teams from document chasing and backlogs to faster, evidence-backed risk decisions—while complementing existing procurement, contract, and risk systems with time-to-value in weeks. They discuss persistent program pressures such as too many third parties, too few analysts, demand for immediate answers, and the need to separate signal from noise using evidence, not questionnaires, to identify gaps against client-specific requirements. Topics include disclosure-driven “need for speed,” SBOM analysis, continuous monitoring for fast-changing AI risks, and advice to run a proof of concept, avoid “AI-ish” tools, choose trusted partners, and start with the highest-friction hotspot.

Key highlights:

  • Why They Joined Coverbase
  • Why TPRM Matters Now
  • Native AI vs AI-ish
  • ROI and Executive Buy-In
  • Disclosures and Risk Visibility
  • Managing Risk Continuously

Resources:

Brian Shaw on LinkedIn

Constantine Malaxos on LinkedIn

Coverbase

 Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
AI Today in 5

AI Today in 5: November 3, 2026, The Unruly Summer Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Where is AI most widely deployed in compliance? (FinTechGlobal)
  2. An unruly summer of AI. (CCI)
  3. AI visibility is vital for banks. (FinTechMagazine)
  4. How AI is used in healthcare. (LMTribune)
  5. Leadership in the age of AI. (FT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
AI Today in 5

AI Today in 5: November 2, 2026, The Vibration Compliance Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Will synthetic identities fool AI? (FinTechGlobal)
  2. SEC says it is monitoring corporate AI disclosures. (Reuters)
  3. AI and vibration compliance. (JPT)
  4. AI bet on Trump. Oops. (Bloomberg)
  5. Impact of AI in the UK labor market. (FT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
AI Today in 5

AI Today in 5: October 30, 2026, The $500bn Loss Day Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Tackling insurance’s data-ready problem. (FinTechGlobal)
  2. Alphabet (Google) loses $500bn in value in one day. (WSJ)
  3. Growing fears over Chinese AIs. (CW)
  4. Americans reject using AI for medical coverage issues. (Bloomberg)
  5. Nvidia chief targeted by Chinese spy. (NYT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Blog

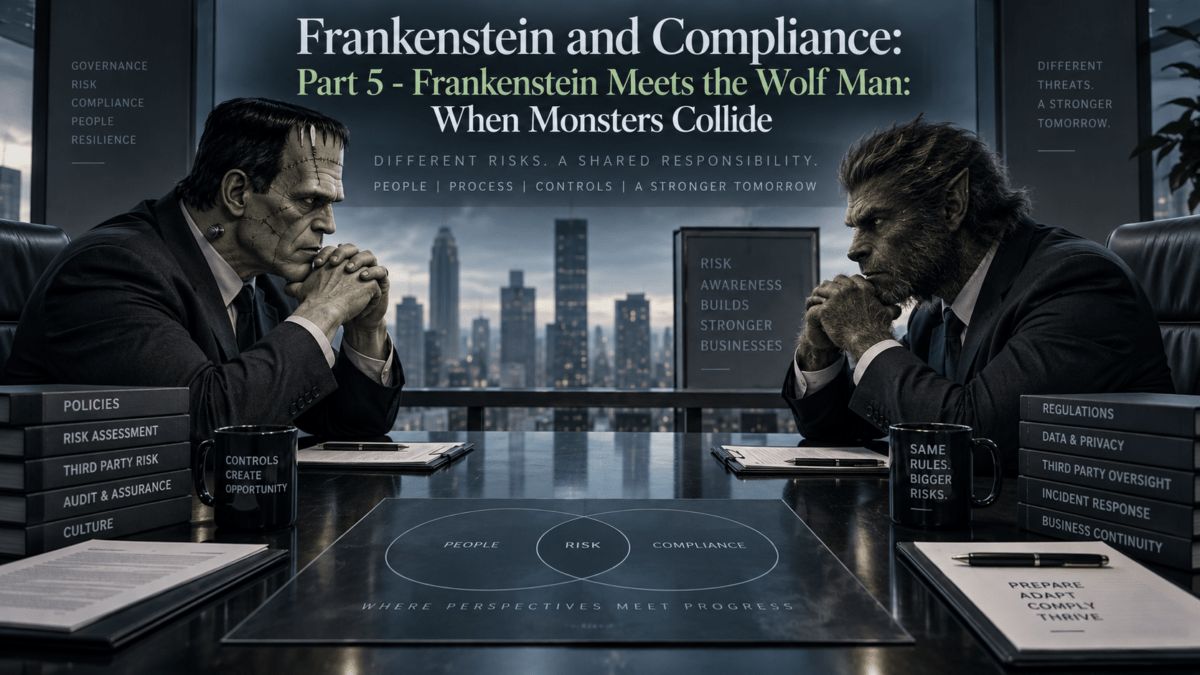
Frankenstein and Compliance: Part 5 – Frankenstein Meets the Wolf Man: When Monsters Collide

Ed. Note: This month, on his podcast series Popcorn and Compliance, Tom Fox dives deep into the first five Frankenstein movies. Over October, Tom Fox will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolf Man. This blog post accompanies the podcast series.

The first four Frankenstein films provide a useful progression for corporate compliance. Frankenstein examined innovation without adequate governance. Bride of Frankenstein shows leadership that understands risk but lets pressure and rationalization override judgment. Son of Frankenstein moved to inherited risk and the obligations that arise when new leadership discovers legacy problems. The Ghost of Frankenstein asks whether remediation actually works. 

Frankenstein Meets the Wolf Man (1943) changes the risk equation. There are now two monsters. Larry Talbot, played by Lon Chaney Jr., returns from The Wolf Man seeking a way to end the curse that transforms him into a werewolf. His search eventually brings him to the ruins of Frankenstein’s castle, where he discovers the Monster, played in this film by Bela Lugosi. Talbot revives him, Dr. Mannering becomes involved, and the film eventually delivers what its title promises: Frankenstein’s Monster and the Wolf Man collide.

For corporate compliance professionals, the movie provides a useful way to think about enterprise risk. Organizations necessarily divide risk into categories and assign responsibilities to different functions. Compliance may oversee anti-corruption, sanctions, third-party, antitrust, and other regulatory risks. Information Security manages cyber risk. Privacy oversees data protection. HR manages employment-related risks. Finance owns financial controls. Internal Audit provides assurance. Enterprise Risk Management looks across the organization. 

That structure is necessary. It can also create silos. The most significant corporate risks do not always remain within the categories management assigns to them. They interact. When they do, the resulting exposure may be greater than the organization sees when each risk is assessed independently. The compliance challenge is not simply identifying each monster. It is understanding what happens when they meet.

Risk Does Not Respect the Organizational Chart

Companies assign risk ownership because someone must be accountable. That is good governance. The problem begins when risk ownership becomes information ownership. Consider a third-party distributor operating in a high-risk market. Compliance may identify concerns about the distributor’s beneficial ownership. Finance may identify unusual payment requests. Information Security may detect suspicious access involving the distributor’s credentials. Internal Audit may identify invoice exceptions. Legal may become aware of litigation or regulatory concerns involving related entities. Each function may respond appropriately to the information it possesses.

Yet the organization may still fail if nobody connects those facts. The compliance issue is therefore not simply whether individual control functions are doing their jobs. It is whether the organization’s governance structure allows information to move across functional boundaries. This distinction matters more as corporate risks become more interconnected.

A cybersecurity event can become a privacy incident. A privacy incident can become a regulatory investigation. A regulatory investigation can create disclosure obligations. A third-party issue can become an anti-corruption problem, which can become a books-and-records problem, which can become a securities issue. Risk categories are useful for management. They are not boundaries that real-world events respect. 

The Wolf Man and Frankenstein’s Monster Are Different Risks

One useful aspect of Frankenstein Meets the Wolf Man is that its two principal characters represent different kinds of risk. Larry Talbot understands his condition. He knows that particular circumstances trigger his transformation and that the consequences can be severe. His risk is recurring and linked to identifiable conditions. Frankenstein’s Monster represents something different. He is a legacy risk repeatedly inherited, revived, and unsuccessfully controlled by others.

Put them together and the problem changes. Companies experience similar combinations. A business may have a known third-party risk that becomes significantly more serious when combined with expansion into a high-risk jurisdiction. A weak control environment may become more consequential when management introduces aggressive sales incentives. A cybersecurity vulnerability may become more significant when the company deploys an AI system with access to sensitive information. The risks do not merely accumulate. They can amplify one another. That is why risk assessment should consider interdependencies. 

Risk Aggregation Should Be Part of the Compliance Conversation

Traditional compliance risk assessments often organize risks by subject matter.

  • Anti-corruption risk.
  • Sanctions risk.
  • Antitrust risk.
  • Third-party risk.
  • Privacy risk.
  • Conflicts of interest.
  • Books and records.

That approach is useful because it creates structure and allows organizations to identify controls and owners. It can also obscure combinations of risk. Consider a company acquiring a business in a high-risk jurisdiction. The acquisition may involve weak financial controls, substantial government interaction, a distributor-based sales model, aggressive growth assumptions, and a local culture unfamiliar with the acquiring company’s compliance expectations. Each issue may appear manageable when assessed separately. Together, they may produce a materially different risk profile. 

The CCO should therefore consider adding risk aggregation to the compliance risk assessment process. Where do significant risks intersect? Which business units face several elevated risks simultaneously? Which third parties create exposure across multiple compliance areas? Which strategic initiatives combine new technology, new markets, new partners, and aggressive financial expectations? A heat map that displays risks individually may not reveal these relationships. Compliance should be able to explain not only where the red boxes are but also what happens when several red boxes occupy the same part of the business.

AI Is an Enterprise Risk Multiplier 

Artificial intelligence provides one of the clearest modern examples of the problem. Companies sometimes discuss “AI risk” as though it were one category. Unfortunately, it is not. An AI deployment can simultaneously raise privacy, cybersecurity, intellectual property, employment, discrimination, consumer protection, regulatory, third-party, recordkeeping, and reputational issues.

What about an AI tool used to assist hiring decisions? HR may view it as a talent-management system. Information Security may assess the technology vendor. Privacy may examine candidate data. Legal may consider employment requirements. Compliance may evaluate governance and ethical concerns. Procurement may negotiate the contract. Every function may perform its assigned task. The organization still needs someone to evaluate the complete risk picture.

The same issue arises when AI is used for internal investigations, compliance monitoring, customer interactions, sales recommendations, financial decisions, or employee evaluation. This is why AI governance requires cross-functional management.

Frameworks such as the NIST AI Risk Management Framework and ISO/IEC 42001 are useful because they encourage organizations to think about governance, accountability, risk identification, measurement, monitoring, and continual improvement rather than treating AI exclusively as an IT issue. The central business question is not which department owns AI. It is whether the governance structure addresses the risks created by the particular use case.

The CCO Should Be a Connector, Not the Owner of Everything

The increasing interconnectedness of risk raises an important question about the CCO’s role. The answer should not be that Compliance owns every risk involving law, ethics, or reputation. That approach creates its own governance problem.

Business management owns business risk. Information Security should remain accountable for cybersecurity. HR should remain accountable for employment processes. Finance should own financial controls. Legal should provide legal advice. Internal Audit should preserve its independent assurance role. The CCO can nevertheless play an important role as a connector.

Compliance often receives information from multiple parts of the organization. Hotline reports, investigations, third-party due diligence, monitoring results, policy exceptions, training data, regulatory developments, culture assessments, and risk assessments all provide different views of organizational behavior. That perspective can allow Compliance to identify patterns that may not be visible within a single business function. The CCO should therefore ask where information needs to be shared, where cross-functional escalation is necessary, and where significant risks require joint governance. The goal is coordination without diluting accountability.

Mission-Critical Risk and Board Oversight

This also connects to the broader Marchand discussion about board oversight of significant and mission-critical risks. Directors do not need to become operational risk managers. They do need reasonable assurance that management has systems to identify significant risks and escalate material information.

For interconnected risks, that means understanding how management aggregates information. 

  • Which risks are sufficiently significant to require cross-functional oversight?
  • How does management identify emerging combinations of risk?
  • Who resolves disagreements between control functions?
  • What information reaches the board?
  • How are significant risks assigned when they do not fit within one organizational function?

These questions matter most when a risk is central to the company’s business model. The board does not need to manage the monsters. It needs to understand whether management can see when they are moving toward one another. 

Practical Actions for the CCO 

Frankenstein Meets the Wolf Man suggests several practical actions for compliance leadership. The compliance risk assessment should identify not only individual risks but also significant risk intersections. CCOs should look for business units, markets, third parties, products, and strategic initiatives where multiple elevated risks converge. Compliance should establish relationships and information-sharing mechanisms with Internal Audit, Legal, Finance, HR, Information Security, Privacy, Procurement, and Enterprise Risk Management. Significant cross-functional risks should have clear owners, escalation criteria, and decision rights.

CCOs should also consider whether existing compliance dashboards show relationships among risks or simply report individual metrics. Data from investigations, hotline reports, third-party monitoring, policy exceptions, audit findings, and other sources can become substantially more valuable when analyzed together. For emerging technologies such as AI, Compliance should participate in cross-functional governance while avoiding the temptation to own every associated risk. The objective is not centralized ownership. It is connected governance.

The Compliance Lesson

Frankenstein Meets the Wolf Man completes the compliance progression of the Universal Frankenstein films. Organizations create risks. Leadership can compromise in responding to them. New management can inherit them. Remediation can fail to eliminate them. Then those unresolved risks can interact with other risks.

That final stage matters because modern corporate risk is increasingly interconnected. AI touches privacy, cyber, employment, intellectual property, and regulatory compliance. Third-party risk can implicate corruption, sanctions, human rights, cybersecurity, and financial controls. Compensation can affect culture, sales practices, fraud risk, and books and records. No single function can manage these issues effectively on its own.

The solution is not to eliminate functional ownership. Clear accountability remains essential. The solution is to build governance mechanisms that allow information to move, risks to be considered together, and significant issues to be escalated across organizational boundaries. For the CCO, that means becoming an effective connector while preserving the accountability of the business and other control functions.

For management, it means looking beyond individual risk categories. For the board, it means ensuring that committee structures and reporting processes provide an enterprise view rather than a collection of disconnected risk reports. The ultimate lesson from Frankenstein Meets the Wolf Man is therefore not really about either monster individually. It is about interaction. 

A company may understand its corruption risk. It may understand its third-party risk. It may understand its cybersecurity risk. It may understand its AI risk. It may have capable people managing each one. The question is whether anyone understands what happens when those risks meet. That is where compliance moves beyond individual rules and controls and becomes part of enterprise governance. 

After five films, the Frankenstein story leaves us with a useful framework for the modern compliance program: govern what you create, learn from what goes wrong, take responsibility for what you inherit, test whether remediation works, and understand where risks intersect. Because in business, as in the movies, managing one monster is difficult enough. The real governance challenge begins when monsters collide.

Check out the podcast version and analysis of this episode of Popcorn and Compliance with Timothy and Fiona.

Categories
Blog

AI in the Audit Room: Why a Signature Is Not Evidence of Effective Oversight

Imagine a company with an AI policy—employees complete training. Important outputs supposedly receive human review. The board sees an approval dashboard and assumes it’s managing the risk. Now ask a different question: What evidence shows that the review changed anything?

That is the central compliance challenge in ECI Compliance Week’s AI in the Audit Room. The report was prepared in conjunction with Workiva. The collection translates its AI Governance Framework into an audit program, connecting 14 controls across three tiers to specific tests and supporting evidence. AI-in-the-Audit-Room For Chief Compliance Officers (CCOs), the lesson is straightforward: AI governance must demonstrate how decisions are controlled, challenged, and improved. A policy describes expectations. An approval records an action. Neither, on its own, proves that a control works.

The Oversight Gap Is an Operational Problem

45.2 percent of the respondents reported training or awareness programs, while 33.8 percent reported usage monitoring or logging by IT or security. Separately, the collection reports that approximately one in four executives in Workiva’s 2026 Midyear Executive Benchmark Survey said internal audits had discovered AI errors after outputs reached external stakeholders or board members. Only 11 percent believed their data quality was sufficient for AI use.

These findings should prompt a practical examination of where assurance occurs. Finding an error after distribution is not the same as preventing unsupported information from reaching a decision-maker. Workiva’s separately labeled partner contribution proposes an “assurance architecture” built around governance, traceability, and defensibility. The useful compliance question is whether management can explain what data informed an output, which model produced it, and what an employee authorized.

For an AI-assisted disclosure, that means following the information back to its source rather than accepting a plausible explanation. Ask whether reviewers can retrieve the supporting material and distinguish verified inputs from unsupported assertions. Traceability should make challenges possible before release, not merely explain a failure afterward.

Tier One: Establish Foundations That Can Be Tested

The framework’s first tier contains five controls: an accountable executive, an AI policy, an AI use inventory, employee AI training, and an annual program review. The accompanying audit tests make those familiar concepts concrete. The accountable executive needs authority and budget. The inventory must cover licensed products, AI embedded in existing software, and tools employees adopted independently. Training must reach actual users and match the policy in force. The annual review must produce findings that lead to action.

For the CCO, start with the inventory. Reconcile it against procurement, identity, and expense records, as the framework recommends. Then examine whether each material use has an owner and an appropriate data classification. Do not stop at asking whether training occurred. Ask which users received it and whether the content addressed their activities.

The same discipline applies to program review. A dated report is not the endpoint. Look for assigned remediation, closure dates, and evidence that the organization changed something because of what it learned.

Tier Two: Make Governance Part of Daily Operations

The second tier covers third-party AI due diligence, an AI speak-up channel, incident response, and employee AI use attestation. The third-party control is particularly important. The framework calls for reassessment when AI functionality arrives through a software update, not merely when the original contract is signed. It also calls for identifying the underlying model provider chain and determining whether customer data is used for training.

For compliance teams, that means connecting procurement and vendor oversight to technology change management. The original supplier approval should not be treated as the final assessment of every capability subsequently introduced. The speak-up and incident controls should work together. An employee who identifies troubling output needs a route to someone with AI governance expertise. Where appropriate, a substantive response should lead to investigation, containment, root-cause analysis, and control changes. Employee attestations should also update the inventory rather than disappear into a training database.

My practical recommendation is to test that entire process with a realistic scenario: an approved tool produces an unsupported claim intended for an external report. Determine who receives the concern, who can stop distribution, and what evidence documents the resolution.

Tier Three: Govern the Use Case and the Authority

The third tier addresses pre-deployment approval, human oversight and output monitoring, AI agent access and security, bias and fairness considerations, and external transparency. A critical distinction is that approving a tool is not the same as approving every use of that tool. The framework calls for separate use-case approval records, including cross-functional review for uses affecting financial reporting, customers, or employees.

For agents, the control table calls for unique identities, least-privilege access, defined limits on autonomous action, reconstructable action logs, and a tested way to stop the system. It also calls for testing decisions that affect people and can produce disparate outcomes and for substantiating public statements about AI. Translate these expectations into demonstrations. Ask the system owner to show an agent’s permissions, reconstruct an action, and produce the results of a shutdown test.

Monitoring should also look beyond internal error rates. The framework treats vendor model changes, public incidents, and regulatory shifts as external signals that require scheduled attention. Ask for the record of those signals and the actions taken, not simply the latest system performance report. For transparency, select a public claim and request its evidence file. The test is not whether the statement sounds reasonable. It is whether the organization can support it.

The Signature Problem: Test Judgment, Not Clicks

The collection’s most useful challenge concerns the human review step. Its “signature problem” describes a reviewer who sees a polished answer but lacks the underlying evidence, discarded alternatives, or meaningful ability to challenge the result. Approval becomes easy; disagreement becomes burdensome. The collection proposes three questions: Can the reviewer change the available options? Can the reviewer see enough evidence to disagree? Does disagreement produce a change? 

The report identifies four metrics: approval rate, edit distance on accepted output, time spent per review, and override consequence. Together, these examine whether reviews vary meaningfully, whether edits are captured and evaluated, whether reviewers have time to examine evidence, and whether overrides lead to action.

For CCOs, the fourth metric offers an immediate starting point. The collection recommends examining the last 20 overrides in an AI-assisted process affecting financial statements, customers, or regulators and asking what changed because of each. That exercise gets beyond a completion dashboard. It connects a reviewer’s judgment to remediation, revised instructions, or an adjusted control.

The collection also recognizes the limits of universal human review at scale. It describes moving human judgment into system boundaries, evaluation criteria, exception handling, sampling, and monitoring. It preserves individual review for specified consequential situations, including irreversible outcomes and cases outside anticipated policy boundaries. The practical lesson is not to remove people from oversight. Instead, place human judgment where it can actually influence outcomes, and give reviewers the evidence, authority, expertise, and time to exercise it.

Do Not Overlook the Inference Gap

Shruti Mukherjee’s contribution extends the discussion to AI’s environmental footprint. She distinguishes model training from inference, the recurring activity of running it, and frames the issue as a governance exposure involving ownership, measurement, third-party information, and substantiated claims. Her proposed audit questions are practical: Who owns the energy and water footprint of AI use? Can the organization measure ongoing consumption? What do supplier contracts disclose? Can the company support its environmental statements?

For the CCO, the broader application is to look beyond familiar risk categories. A benefit claimed in a presentation should not become an external assurance without supporting evidence. Where information is unavailable, document the limitation and identify who is responsible for addressing it.

Practical Takeaways: Bring Evidence to the Board

Start with one material AI-assisted process rather than rewriting an enterprise-wide policy. Trace it from the approved use case through source data, output review, escalation, and final distribution. Ask control owners to produce evidence at each stage.

Next, examine the review process itself. Use the collection’s four metrics to identify where approval activity may be substituting for judgment. Follow overrides through to their consequences and assign responsibility for unresolved weaknesses.

Finally, change the board conversation. Report not only how many tools are approved or how many employees are trained, but also what testing found, which controls failed, what management changed, and which risks remain unresolved.

The board should ask whether management knows where AI is used, whether reviewers can meaningfully challenge it, and whether the organization can reconstruct and support significant actions and public claims. This is where compliance connects governance directly to business execution.

The CCO should ask an equally direct question: When someone identifies that the AI is wrong, does the organization merely record the concern, or does it learn and change? That is the difference between an AI governance program that documents approvals and one that demonstrates effective oversight.