Categories
AI Today in 5

AI Today in 5: October 5, 2026, The Legal Risk Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Could AI stunt lawyers’ training? (Reuters)
  2. Jay Clayton to be named AI Czar. (WSJ)
  3. Compliance purpose-built AI. (Thomson Reuters)
  4. Legal risks piling up for OpenAI. (FT)
  5. Should private AI agents run your life? (WSJ)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Compliance and AI

Compliance and AI: Kunal Chopra on Compliance as Market Access

What is the intersection of AI and compliance? What about Machine Learning? Are you using ChatGPT? These questions are just three of the many we will explore in this cutting-edge podcast series, Compliance and AI, hosted by Tom Fox, the award-winning Voice of Compliance. In this episode, host Tom Fox visits Kunal Chopra, CEO of Certivo, an AI-native regulatory intelligence and compliance management platform for supply chains.

Chopra brings nearly two decades of experience across technology leaders like Amazon, Microsoft, and Groupon to the conversation on AI-powered compliance and regulatory intelligence. Drawing on his supply chain background, he argues that compliance should be treated as a market access function that helps companies enter markets faster, protect revenue, and manage global regulatory change more effectively. He believes AI can transform compliance from a reactive, manual burden into a proactive business enabler by continuously tracking rules, extracting key data from documents, and coordinating communication across the supply chain. In his view, this shift frees teams from repetitive work and makes compliance a strategic driver of growth rather than just a legal necessity.

Key highlights:

  • Scrambling for Certificates to Secure Market Access
  • August Deadlines Drive EU Market Access Risk
  • Visibility Gap Threatening Revenues, Projects, and Market Access
  • AI-Native Compliance Platform with Real-Time Audit Trail
  • Deterministic AI Extracting Supplier Documents, Preventing Hallucinations

Resources:

Connect with Kunal Chopra on LinkedIn

Certivo

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
AI Today in 5

AI Today in 5: October 2, 2026, The Going to the Dark Side Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. How much of compliance spend will go to AI?(FinTechGlobal)
  2. Data privacy issues are holding patients back from AI. (HealthcareDive)
  3. Google releases the most advanced Gemini model. (FT)
  4. Using AI governance to move compliance to an advantage.  (LewisSilkin)
  5. Banks may soon face the dark side of AI. (Reuters)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

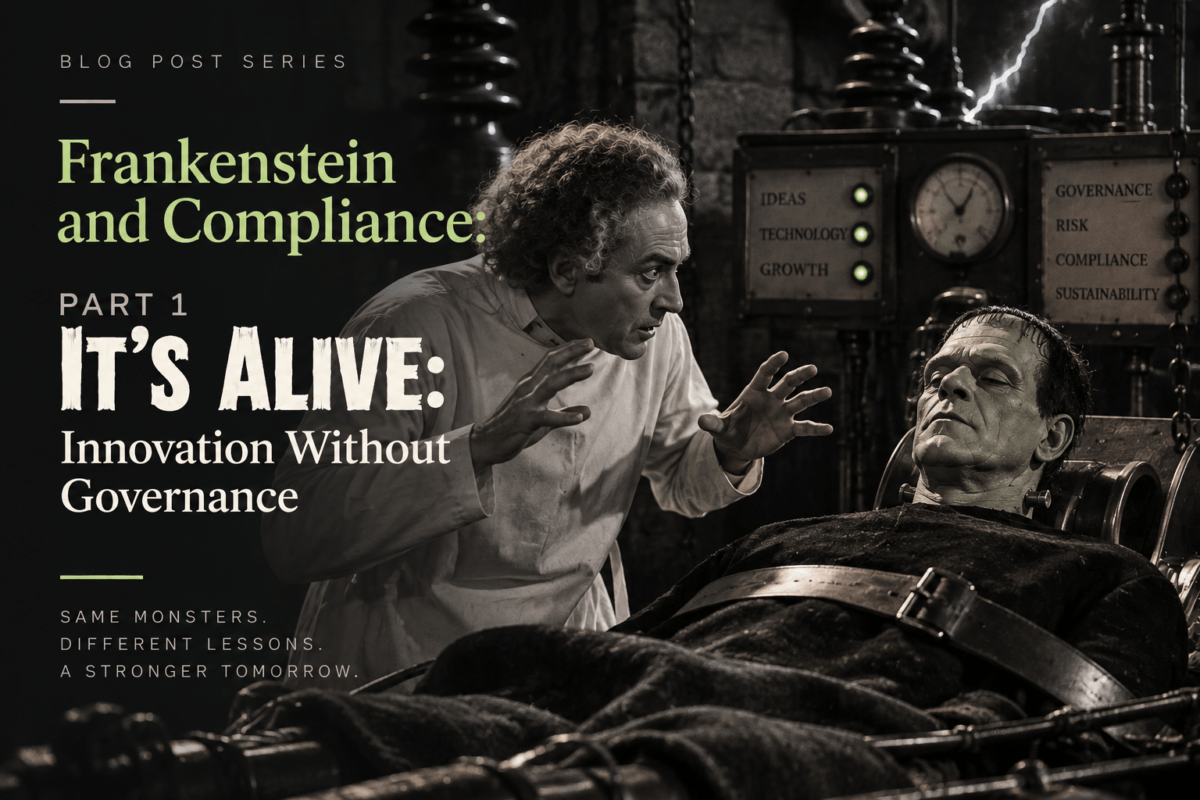
Frankenstein and Compliance: Part 1 – It’s Alive: Innovation Without Governance

Ed. Note: This month, on my podcast series Popcorn and Compliance, I am taking a deep dive into the first five Frankenstein movies. Over October, I will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolfman. The blog post is a companion to the podcast series.

The most famous moment in Frankenstein (1931) comes when Henry Frankenstein’s experiment succeeds. Electricity surges through his laboratory, the body on the table begins to move, and Frankenstein celebrates what he believes is an extraordinary scientific achievement.

“It’s alive!”

For the corporate compliance professional, however, the critical decisions occurred before Henry ever activated his equipment. He had decided to proceed without an adequate risk assessment, effective oversight, meaningful challenge, or a plan for managing the consequences if his experiment succeeded. Viewed through that lens, Frankenstein is not simply a horror movie about a scientist and the Monster he creates. It is a case study in innovation without governance.

That lesson is especially relevant as companies accelerate the adoption of AI and other emerging technologies. Businesses are appropriately focused on innovation, productivity, efficiency, growth, and competitive advantage. Yet technological capability can develop faster than the governance structures needed to manage the resulting risks. The compliance issue is not whether companies should innovate. They must. The issue is whether governance keeps pace with innovation.

The Business Case Was Clear. The Governance Case Was Not.

Henry Frankenstein has a compelling objective. He believes he can accomplish something no one has accomplished before. He assembles the equipment, obtains the materials, develops the technical capability, and builds a team capable of executing the project. In corporate terms, Henry has a strategy, resources, technical expertise, and executive sponsorship. He lacks an effective governance framework.

Before activating his creation, Henry conducts no meaningful risk assessment. He does not identify potential failure scenarios or establish control requirements. He does not define stopping criteria or determine who has authority to challenge the project. No meaningful contingency plan exists for an adverse outcome. This is precisely where compliance should enter the business process.

An effective compliance function should not first encounter a significant new technology when the business seeks approval immediately before deployment. Compliance needs to participate early enough to understand the business objective, identify the associated risks, and help determine appropriate controls.

That does not mean Compliance should own innovation or assume responsibility for the underlying business decision. Risk ownership should remain with the business. Compliance should help ensure that management understands the legal, regulatory, ethical, and control implications of the decision before significant commitments are made.

For the CCO, this raises a practical question: When does Compliance become involved in our company’s innovation process? If the answer is immediately before launch, the organization may already be too far downstream.

AI Has Made the Frankenstein Problem Immediate

Artificial intelligence makes the Frankenstein governance issue particularly relevant. Companies are deploying AI to analyze information, generate content, assist customer service, support investigations, screen candidates, evaluate transactions, enhance due diligence, identify suspicious activity, and improve decision-making. These applications can generate significant business value. They also raise governance questions that organizations must address before deployment.

Organizations need to understand what data an AI application uses, how it obtained that information, who approved the use case, and which regulatory requirements apply. They should determine how outputs are validated, where human review is required, how confidential information is protected, and what happens when a system produces an unexpected or inappropriate result.

There must also be clear accountability. Someone should own the business risk associated with the use case, and the organization should understand who has authority to suspend or terminate the application if circumstances warrant.

The NIST AI Risk Management Framework provides one useful approach through its Govern, Map, Measure, and Manage functions. ISO/IEC 42001 similarly treats AI through a management-system framework emphasizing governance, accountability, risk management, and continual improvement.

Both approaches reinforce a broader compliance principle: technology risk needs governance throughout the lifecycle. Henry Frankenstein has no lifecycle governance. His approach is essentially to build the system, activate it, and evaluate the consequences afterward. That is not an acceptable corporate control environment.

The Abnormal Brain and the Importance of Validating Inputs

One of the film’s most useful compliance scenes occurs before the Monster comes to life. Henry needs a brain for his creation. His assistant Fritz obtains one, but the intended specimen is destroyed. Rather than report what happened, Fritz substitutes another brain, identified in the film as abnormal, without telling Henry. (Abbey Normal—if you know, you know.) The project therefore proceeds after a critical input has changed without the project leader’s knowledge.

For compliance professionals, the scene provides a useful analogy for third-party risk, supply-chain controls, due diligence, and data governance. Organizations routinely rely on information others provide. A distributor provides beneficial ownership information. A vendor completes a compliance certification. An employee submits an expense report. An acquisition target makes representations during due diligence. A supplier certifies compliance with contractual obligations. An AI application relies upon data obtained from multiple sources.

The relevant control question is not simply whether the required information was received. It is whether the organization appropriately validated important information based on risk. Fritz completed his assignment in the narrowest sense. He returned with a brain. The process failed because nobody verified that he returned with the correct brain. That distinction is important for compliance program effectiveness. A completed checklist demonstrates that an activity occurred. Appropriate validation assures that the control achieved its purpose.

Dr. Waldman and Credible Challenge

Henry is not entirely without oversight. Dr. Waldman understands what Henry is attempting and recognizes the potential danger. He raises objections. Henry proceeds anyway. This takes the film from risk assessment into the effectiveness of the challenge function. Many companies can demonstrate that compliance participated in a significant decision. That does not necessarily establish that a compliance professional had meaningful influence over the outcome. A CCO can attend meetings, review proposals, identify concerns, and recommend additional controls. If commercial leadership can routinely disregard those concerns without escalation, the company may have consultation without credible challenge.

This is why the authority, stature, resources, independence, and access of the compliance function matter. The effectiveness of a corporate compliance program becomes most visible when it disagrees with an important business proposal. Boards should therefore look beyond whether your compliance function was consulted. They should understand what happens when a compliance officer disagrees with the business. They need to ask such questions as: Can the CCO escalate a significant concern? Does the CCO have appropriate access to the Audit Committee or board? Are material disagreements documented? Who has authority to accept significant compliance risk? Can commercial management override a compliance objection without further review?

If a CCO can raise a concern but nobody with decision-making authority has to address it, the organization has created the appearance of challenge without its substance. Dr. Waldman had a voice. He lacked the influence to change the decision.

Maria and the Risk of Unintended Consequences

Next we consider one of the most poignant scenes in the movie. The encounter between the Monster and young Maria provides another important business lesson. This is certainly one of the most unforgettable, and indeed tragic, scenes in all the Frankenstein movies. If you have ever seen it, you will never forget it. A small child, Maria, shows the Monster how flowers float on the lake. He imitates what he observes. When the flowers are gone, he throws Maria into the water, apparently expecting her to float as the flowers did. The consequences are tragic. The Monster recognizes a pattern without understanding its context.

That distinction has obvious relevance for artificial intelligence and automated decision-making. A system may identify patterns, generate recommendations, and produce technically consistent outputs without understanding their broader legal, ethical, or business implications. A technically accurate output can still create an inappropriate result.

This is why human oversight cannot exist merely as language in an AI policy. Companies need to determine where human judgment is required, who provides that judgment, what qualifications reviewers need, when automated recommendations can be overridden, and how significant exceptions are documented.

Management should also understand whether human review is substantive or simply procedural. An employee clicking an approval button after an automated recommendation does not necessarily constitute meaningful oversight. The relevant control question is not simply whether the technology performed as designed. It is whether the resulting decision was appropriate.

Innovation Requires Accountability

Henry eventually discovers that creating something and controlling it require different capabilities. Corporate leaders should understand the same distinction. Management establishes incentive structures, sales strategies, compensation plans, technology deployments, acquisition strategies, third-party relationships, and performance expectations. Those decisions shape employee behavior and create risk. Leadership accountability therefore does not begin only after misconduct occurs. It begins with the decisions that establish the operating environment.

For the CCO, this means integrating compliance risk into strategic business decisions. For management, it means risk ownership remains with the business. For the board, oversight should focus on whether management has reasonable systems to identify, manage, monitor, and escalate significant risks. Compliance does not own a business risk simply because the compliance function identifies it. Management remains responsible for the business decision and the risks it creates.

That principle becomes particularly important with emerging technology. The CCO should contribute expertise regarding regulatory requirements, ethical considerations, controls, monitoring, and escalation. Technology leaders should contribute technical expertise. Legal, Privacy, Information Security, HR, Internal Audit, and other functions may have roles depending on the application. Business leadership remains accountable for the decision to deploy the technology and the resulting business risk.

Practical Actions for the CCO

Frankenstein suggests a practical agenda for compliance leadership. Compliance should move upstream and identify significant business processes where its participation adds the most value before making commitments. Emerging technology, acquisitions, market entry, compensation design, significant third parties, and new products are obvious candidates.

Risk assessment should occur before deployment and should address foreseeable legal, compliance, ethical, operational, and reputational consequences. High-risk inputs supplied by employees, vendors, third parties, acquisition targets, or technology systems should receive risk-based validation.

The organization should also define what credible challenge means in practice. Escalation procedures should be clear when Compliance and business leadership disagree about significant risk.

Finally, treat approval as the beginning of governance rather than its conclusion. Test controls, monitor outcomes, analyze exceptions, and update risk assessments as the business and technology evolve. The objective is not to slow innovation. It is to make innovation governable.

The Compliance Lesson

Frankenstein is not an argument against innovation. It is an argument for governance.

Henry Frankenstein failed not because he attempted something extraordinary. He failed because his technical ambition outpaced his ability to identify, understand, govern, and control the resulting risk.

Companies face the same challenge today. Technology will advance. Business models will change. New markets will open. Competitive pressure will accelerate decision-making. New risks will emerge. Compliance’s role is not to stand outside the laboratory and demand that the electricity be turned off.

It is to help ensure that management has assessed the risk, validated critical inputs, established appropriate controls, defined accountability, created meaningful challenge, and determined how the organization will respond if the initiative produces an unexpected result. The best time to build that governance structure is before deployment.

Our next installment moves the compliance analysis forward. In Bride of Frankenstein, Henry no longer faces an unknown risk. He has already experienced the consequences of his original experiment and understands what can go wrong. Then Dr. Pretorius persuades him to return to the laboratory.

The compliance issue is no longer whether leadership identified the risk. It is what happens when leadership knows better, but pressure, ambition, and rationalization push the organization toward the same risk again.

Check out Timothy and Fiona’s commentary on Frankenstein here.
Categories
Daily Compliance News

Daily Compliance News: October 1, 2026, The Welcome to Q4 Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • PwC refuses to sign off on Nidec books. (FT)
  • Trump defends no-touch regulation for AI. (WSJ)
  • Hungary’s reckoning with corruption speeds up. (DW.com)
  • US exits from EU ABC working group. (AP News)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
AI Today in 5

AI Today in 5: September 30, 2026,  The AI in Space Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Space-based property management oversight. (FinTech Global)
  2. OpenAI scraps Astra release. (NYT)
  3. The AI data squeeze. (LawAsia)
  4. Compliance lessons on AI in debt collection. (Inside ARM)
  5. Using AI to monetize compliance. (CRN)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Innovation in Compliance

Innovation in Compliance: Doni Hoti on Embedding Advertising Compliance Into Content Creation

Innovation comes in many areas, and compliance professionals need to not only be ready for it but also embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom welcomes Doni Hoti, co-founder and CEO of Adclear.

Hoti brings a fascinating perspective on embedding compliance directly into content creation. He begins with the shift in advertising and marketing compliance from a slow, “checkpoint” back-office function to an embedded, revenue-enabling capability. Hoti explains that modern content creation involves many stakeholders and must move at near-real-time speed, while enforcement risk and the cost of losing customer trust keep rising. He describes how AI has broken traditional review models by increasing both content volume and speed expectations and how Adclear uses horizon scanning across global regulators, agentic AI, and company-specific policies to deliver more deterministic, auditable compliance guidance tied to rulebooks. Fox and Hoti then turn to third-party and affiliate challenges, regulator-ready documentation and audit trails, and business outcomes such as reduced review SLAs, scalable approvals, and revenue uplift, with marketing increasingly owning the process alongside legal and compliance.

Key highlights:

  • Compliance Disconnect
  • Trust and Shopfront
  • Embed Compliance
  • Third-Party Risks
  • AI as Solution
  • Audit Trail Proof

Resources:

Adclear

Doni Hoti on LinkedIn

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
AI Today in 5

AI Today in 5: September 29, 2026, The Risk Register Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Stale risk registers. (FinTech Global)
  2. What’s under your AI hood. (FinTech Futures)
  3. Nvidia releases SW to stop AI from ‘misbehaving’. (CNBC)
  4. Strengthening global trade compliance with AI. (CA&AS)
  5. US corps adopting cheaper IE, Chinese AI models. (FT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

De-Risking AI Adoption Through Accountability and Effective Governance

A company can publish thoughtful AI principles, appoint a governance committee, and still struggle to answer a basic question: who can stop an AI system when its behavior creates unacceptable business risk? For chief compliance officers and boards, that question reaches the heart of program effectiveness. Policies establish expectations. The real test comes when someone must decide, enforce a boundary, and show what happened.

Pamela Gupta addresses that challenge in De-Risking AI Adoption: The AI Trust Layer: An AI Governance Playbook. Her central argument is that trustworthy AI requires an operating model connecting ownership, controls, deployment decisions, monitoring, and evidence. The book provides a structure for translating responsible AI commitments into repeatable business practices. For compliance professionals, its value lies in explaining how governance can support adoption while keeping accountability attached to the people making consequential decisions.

Making Trust Operational

Gupta defines trustworthy AI through three practical capabilities: people can understand the behavior to expect and its limits, verify what actually occurred, and identify an accountable person when something goes wrong. This moves the discussion toward demonstrable performance.

That approach should resonate with any CCO who has examined the distance between a written procedure and actual business conduct. An AI policy may require human oversight. Whether that oversight works depends on the reviewer’s information, competence, time, and authority to intervene. A human approval step has limited value if the organization rewards automatic acceptance or discourages challenges.

The compliance application is straightforward. For each significant AI use case, identify the business purpose, potential harm, responsible owner, operating limits, and evidence needed to evaluate performance. These questions belong at the beginning of development and procurement, when the answers can still shape the system.

Eight Pillars of AI Governance

The book organizes its methodology around AI TIPS™, Gupta’s framework of eight interconnected pillars: cybersecurity, privacy, ethics and bias, transparency, explainability, regulations, audit, and accountability. Together, they address the different ways AI can create enterprise exposure.

The connections matter. Security controls may protect information against unauthorized access while leaving questions about discriminatory outcomes unresolved. Transparency can establish which data and processes a system uses, while explainability addresses whether people can understand and challenge a particular decision. Independent assurance requires evidence from across these activities.

Gupta also presents mappings to established frameworks and standards, including the NIST AI Risk Management Framework and ISO/IEC 42001. Her purpose is to connect enterprise controls and evidence across multiple governance expectations.

For a compliance team, the practical lesson is to coordinate existing expertise. Privacy, security, legal, risk, audit, and business leaders each hold part of the answer. The CCO can help connect their work through common requirements, escalation procedures, and documented decisions. Business owners must remain answerable for the systems they deploy.

Accountability Must Carry Authority

Accountability receives special treatment throughout the book. Under Gupta’s methodology, a critical accountability failure blocks deployment regardless of the aggregate governance score. A system needs a named owner with authority to accept risk and stop its operation. Consequential uses also require appropriate human override and redress mechanisms.

This is a useful challenge to governance committees that distribute responsibility so broadly that no individual can decide. Participation in a committee does not automatically establish authority over a business process.

CCOs should translate this principle into explicit decision rights. Who approves the use case? Who accepts the remaining risk? Who authorizes exceptions? Who can suspend operation? Who addresses harm to an affected customer or employee? Document and understand those answers before an incident forces the organization to discover whether its governance arrangements work.

Governance Throughout the Lifecycle

Gupta’s gated lifecycle makes these responsibilities actionable. It follows AI from concept and planning through data preparation, development, independent validation, deployment, continuing monitoring, and retirement. Decision gates establish criteria for moving forward and identify the people authorized to approve or refuse progression.

Independent validation is particularly important. The team building a system should face review capable of challenging its assumptions and testing whether performance meets the intended use. Deployment readiness also includes monitoring, incident response, rollback capability, and operational procedures.

For compliance professionals, the lesson extends beyond initial approval. A system’s exposure can change when it receives new data, serves a different population, gains additional permissions, or undergoes a material modification. Gupta calls for defined triggers that return systems to validation.

Apply the same discipline to exceptions. Record the rationale, compensating controls, approver, remediation owner, and expiration date. An exception should remain visible until it is resolved. Retirement deserves similar attention, including appropriate data disposition and preservation of evidence needed to explain earlier decisions.

Measuring Whether Controls Work

The Trust Index gives Gupta’s framework a common measurement approach. It combines control implementation, control effectiveness, residual risk exposure, and compliance status into pillar scores and an overall assessment. The methodology assigns the greatest combined emphasis to whether controls exist and whether they work.

For boards, this creates a way to discuss changes in governance performance and direct attention toward unresolved weaknesses. Gupta also distinguishes inherent risk from current risk after controls. An inherently consequential use case does not become inconsequential because its controls improve.

The compliance implication is to examine the evidence supporting the number. Directors should understand significant weaknesses, testing results, exceptions, and corrective actions. A dashboard becomes useful when it supports decisions about resources, restrictions, and remediation. The underlying assessment must remain open to challenge, especially where a favorable aggregate score could obscure a serious problem in one area.

Governing AI That Takes Action

The book’s treatment of agentic AI deserves senior executives’ attention. An AI system that can invoke tools, modify records, send communications, or initiate transactions introduces questions about delegated business authority. Evaluating the model’s outputs covers only part of that exposure.

Gupta describes an agentic control plane that governs identity, permissions, tools, memory, delegation, observation, and intervention. A central principle is that consequential boundaries must operate outside the agent’s own reasoning. Written instructions alone cannot reliably limit what credentials and connected tools permit.

Consider a compliance application: an agent assisting with third-party onboarding. Management should distinguish permission to summarize diligence materials from permission to approve a supplier, alter payment information, or release a blocked transaction. Each capability requires deliberate authorization and appropriate controls.

Internal controls professionals know this lesson. Delegated authority needs defined limits, traceable actions, and effective intervention. Automation increases the importance of those disciplines because actions can occur faster than a person can review them.

Data and Third Parties Remain Central

Gupta also emphasizes the information an AI system uses when it acts. Policies, customer records, retrieved documents, and stored memory shape its behavior. Even a system operating within its permissions can make a harmful decision when its information is outdated or inappropriate.

For compliance teams, this means governing the sources behind AI advice. An assistant answering employee questions should use approved, current policies with identifiable owners and version histories. Access restrictions should continue to apply when information enters a retrieval system.

Third-party oversight must also reach beyond the primary model provider. Gupta examines tools, connectors, and packaged agent capabilities as supply-chain dependencies. She adds a business continuity question: what happens if a critical model becomes unavailable? Organizations should identify affected processes, evaluate alternatives, and test fallback arrangements before disruption forces an improvised response.

Evidence the Board Can Use

Gupta’s evidence-by-design approach connects the entire operating model. Significant decisions and actions should generate records as work occurs: approvals, validation results, system versions, permissions, relevant context, interventions, and monitoring outcomes. Those records should support reconstruction of a consequential action.

For boards, reporting should connect this evidence to oversight. Which systems carry the greatest exposure? Which controls have failed testing? Which exceptions remain unresolved? What has management restricted, delayed, or rejected? What decisions require board attention?

The CCO’s contribution is to make this reporting actionable and consistent with operational reality. Evidence should reveal where management needs to intervene and whether previous corrective actions achieved their intended result.

A useful starting exercise is to select one consequential AI decision and trace it from initial authorization to its outcome. Ask the owner to produce the supporting evidence. Any missing link identifies a concrete improvement for the governance program to address.

Practical Steps for CCOs and Boards

Gupta recommends starting with an honest readiness assessment and a manageable set of high-impact use cases, then expanding proven governance practices. Apply that approach through five actions:

  1. Inventory consequential AI systems, their owners, permissions, and dependencies.
  2. Establish authority for approval, exceptions, escalation, and suspension.
  3. Test controls against actual business risks and affected populations.
  4. Capture decision evidence during ordinary operations.
  5. Give the board visibility into unresolved exposure and remediation.

The business lesson from De-Risking AI Adoption is that effective governance makes responsible adoption repeatable. For CCOs and boards, the immediate task is to make accountability observable in how AI is approved, operated, challenged, and improved.

Categories
Blog

Andrew McBride Does it Again: His New Guide on Buying Compliance Technology

Compliance technology has become the operational backbone of the modern ethics and compliance program. When technology works, it can make compliance faster, more consistent, measurable, and embedded in business operations. When it doesn’t, the consequences show up everywhere: spreadsheets, manual workarounds, disconnected data, frustrated employees, and compliance professionals spending time administering technology rather than managing risk.

That makes buying compliance technology more than an IT procurement exercise. It is a compliance program effectiveness issue. One commentator on this aspect of AI for compliance is Andrew McBride, founder of the consulting firm Integrity Bridge LLC. McBride recently released Recommended Practice for Buying & Selling Compliance Technology, based on surveys of compliance technology buyers and vendors. Its findings illuminate a fundamental imbalance in the marketplace. I can safely say this paper is the standard for compliance professionals evaluating and purchasing AI-based technology.

CCOs buy compliance technology infrequently. Vendors sell it every day. That imbalance matters. Compliance teams can be oversold on functionality. Vendors can become trapped in opaque procurement exercises. Business requirements can become disconnected from technical requirements. AI capabilities can be accepted without sufficient governance. Contracts can focus extensively on getting into a system while ignoring how the company will eventually get out. For the CCO, the lesson is straightforward. If you want to run compliance like a business, you must learn to buy compliance technology like a business. This is where McBride comes in.

Start With Strategy, Not Software

As a CCO, start with a documented compliance technology strategy aligned with business operations. McBride sees three operational layers for that strategy.

Compliance-owned technology includes platforms compliance directly manages, such as Codes of Conduct, training, whistleblower systems, investigation case management, and workflows for gifts, entertainment, and conflicts.

Compliance-shared technology includes systems operated across functions, such as third-party due diligence, transaction monitoring, and communications monitoring.

Enterprise dependency technology includes compliance systems that may not be owned but depend on ERP, CRM, HRIS, procurement, and financial platforms.

This third category is particularly important. A CCO may believe the company has a third-party risk problem when the real issue is poor vendor master data. Transaction monitoring may generate noise because underlying financial data is inconsistent. Technology strategy therefore begins with understanding the compliance program’s architecture.

Know What Compliance Really Costs

Here, McBride frames the question as, ‘What is the total cost of ownership? ‘How many screening tools are independently licensed by Compliance, Procurement, Finance, Credit, and Legal? How many employees maintain spreadsheets? How many hours are spent chasing approvals or reconciling systems? How much compliance talent is consumed by administration rather than risk management? Those costs matter because an inexpensive system can become extraordinarily expensive once you include the human infrastructure required to run it.

This leads to the recurring question: buy, build, or assemble? Internal IT may propose building custom tools. Sometimes that works, but the calculation must include maintenance, upgrades, staffing, cybersecurity, documentation, and key-person risk. Another option is configuring technology the company already owns. That may reduce licensing costs, but “we already own it” does not mean “it is free.” Configuration, integration, testing, administration, and support still cost money.

Commercial software offers established products and vendor-supported roadmaps, but buying software does not eliminate implementation challenges. Apply the same economic discipline to all three options. Don’t compare the sticker price of commercial software with an internal solution whose real costs have never been calculated.

AI Changes the Conversation

AI is moving into transaction analysis, investigation scoping, interview preparation, monitoring, and other compliance workflows. The opportunity is substantial. So is the governance challenge. The Integrity Bridge research presents an interesting picture. AI use appears widespread, but governance and confidence have not necessarily kept pace. Only about one in four compliance teams surveyed had established a formal governance framework. Fewer than half could articulate how AI demonstrably improved compliance outcomes. Only 41 percent of compliance leaders trusted AI-driven outputs for operational decisions.

At the same time, 84 percent reported efficiency gains, while fewer than half reported actual cost savings. That distinction between efficiency and effectiveness is critical. Doing something faster does not necessarily mean doing it better. The CCO should not simply ask, “Does this product use AI?” The better question is, “What compliance outcome does the AI improve, and how can we demonstrate it?”

AI Governance Starts Under the Hood

“AI-powered” is not a meaningful technical specification. McBride advises that compliance should understand what happens under the hood. Once again, he is spot on. Ask questions such as, “Which model is being used?” What information goes into it? What comes back? Is customer information retained? Can corporate data be used for training? Does a third-party model provider receive the information?

These are compliance governance questions because the data may include investigations, employee information, third-party records, or financial information. The contract should address how that information is handled and establish appropriate restrictions on the use of corporate data and queries.

Next, a series of questions about where the AI can fail. Here McBride suggests: How does the system prevent cross-tenant data leakage? How does it identify unsupported statements, hallucinations, or fabricated citations? What happens when malicious instructions are hidden inside uploaded documents? Most importantly, does the system recognize when it lacks sufficient confidence and escalate the matter to a human?

One of the most important characteristics of compliance AI may not be its ability to answer questions. It may be its ability to recognize when it should not answer them.

Keep Humans in the Control Environment

Agentic AI raises the stakes because technology moves from providing information to taking action. But this requires clear authority boundaries. What systems can the agent access? What records can it change? What decisions can it make? Which actions require approval?

Certain compliance decisions should remain subject to documented human authorization. Closing an investigation, changing third-party screening rules, or approving high-risk onboarding are obvious examples. This is where AI governance becomes internal controls. The organization should demonstrate not merely that humans are theoretically “in the loop,” but where human intervention occurs, who has authority, what approval evidence is retained, and what happens when the AI crosses a defined threshold.

CCOs must also understand AI economics. Traditional platforms may be priced by employees, users, or third parties. AI functionality can introduce consumption pricing tied to tokens, documents, searches, or API calls. Model realistic usage and negotiate appropriate spending caps, alerts, overage controls, and consumption rates.

Turn the RFP Into a Governance Exercise

A good RFP does more than collect vendor responses. It forces the organization to define what it actually needs. McBride highlights vendor frustration with “phantom RFPs,” where an incumbent has effectively been selected, or the process is used primarily to gain renewal leverage. A credible RFP must instead be transparent, disciplined, and operationally grounded.

Start with Procurement. Understand source-to-pay requirements, spending thresholds, cybersecurity reviews, privacy requirements, and contracting procedures before bringing vendors deep into the process. Then give vendors meaningful operational information: employee populations, transaction volumes, existing systems, data maturity, integrations, geographic requirements, and workflow constraints.

Most importantly, force precision into vendor answers. Require vendors to classify functionality as:

  1. Available out of the box.
  2. Available through configuration.
  3. Available through a named third-party integration.
  4. On the roadmap with a committed date.
  5. Not supported.

That discipline can dramatically improve an evaluation and create a record of what was actually promised.

Stop Buying Features. Test Controls.

Feature checklists have limits.

McBride suggests that a better test is a scenario. Suppose a critical third party is added to a sanctions list overnight. Ask the vendor to show exactly what happens. Ask questions such as, “How is the alert generated?” Who receives it? How is it prioritized? Who can override it? How is the matter escalated? What evidence is captured? What appears in the audit trail?

Now you are not evaluating a feature. You are evaluating a control. The same principle applies to sandboxes. A generic vendor sandbox tells you relatively little. Require a guided environment configured around your workflows using synthetic or anonymized data. Make users perform the work. That is where implementation problems begin to reveal themselves.

Look Under the Hood Before You Buy

A beautiful interface can be seductive, but buying compliance technology based primarily on user experience is like buying a house because you like the countertops without checking the plumbing. However, before you make a final selection, conduct due diligence around security controls, hosting, uptime, integrations, implementation resources, and data portability.

Review relevant SOC 2 Type II controls. Speak with peer customers. Consider asking to speak with a customer that recently left the platform. Just as importantly, interview the people who will actually implement the product. The team delivering the sales demonstration may not be the team handling implementation. Know who shows up after the contract is signed.

Begin the Relationship by Planning the Exit

Perhaps the most overlooked element of compliance technology contracting is the exit. Companies spend enormous time determining how information will enter a system and surprisingly little determining how they will get it back. A CSV containing basic fields may not recreate an investigation file or preserve the history of a third-party approval. It may not capture attachments, comments, timestamps, escalations, approvals, or audit trails.

Before signing, define export requirements. Ask questions such as: What formats will be provided? What metadata will be preserved? What happens to attachments? Will the audit trail survive? How long will migration assistance remain available? What will extraction cost? When will the vendor delete remaining copies? Understand how you will leave a compliance technology provider before deciding to join it.

The CCO’s Technology Mandate

Compliance technology doesn’t succeed or fail when Legal finishes negotiating the contract. The outcome is largely determined earlier. Did Compliance understand the business problem? Did it know the true cost of the existing process? Did it understand its data? Did it challenge AI claims? Did it test failure modes and workflows? Did it involve Procurement, IT, Privacy, Security, Legal, and the business at the right points? Did it negotiate for implementation, operation, and exit?

Those questions turn technology procurement into compliance governance. Compliance professionals spend their careers asking businesses to operate with transparency, accountability, documentation, fairness, and integrity. Compliance should bring those same principles into the technology marketplace.

Define what you need. Understand what it costs. Test what the vendor claims. Document what was promised. Build controls around AI. Measure whether the technology improves the program. Make sure you can get your data back when the relationship ends. That is what it means to run compliance like a business.

Practical Takeaways

For the CCO, the mandate is clear: build the strategy before selecting the technology; calculate the Total Cost of Ownership rather than the license cost; treat AI as a governance and internal controls issue; test workflows rather than watch demonstrations; diligence the implementation team; and negotiate data portability and exit before signing.

For boards and senior management, the oversight question is equally straightforward: What compliance risk is this technology addressing, how will management measure whether it improves program effectiveness, and what controls govern its use?

The answer tells you much more than whether Compliance has purchased the latest technology. It tells you whether the organization is building a technology architecture that can support an effective compliance program.

If you do not follow Andrew McBride on LinkedIn, you should. He is leading the discussion on the practical aspects of putting the right AI tool in place for you and your organization. His organization will be displaying at this week’s SCCE CEI, so drop by the Integrity Bridge and find out why I think he is the go-to guy in this area.