Categories
Blog

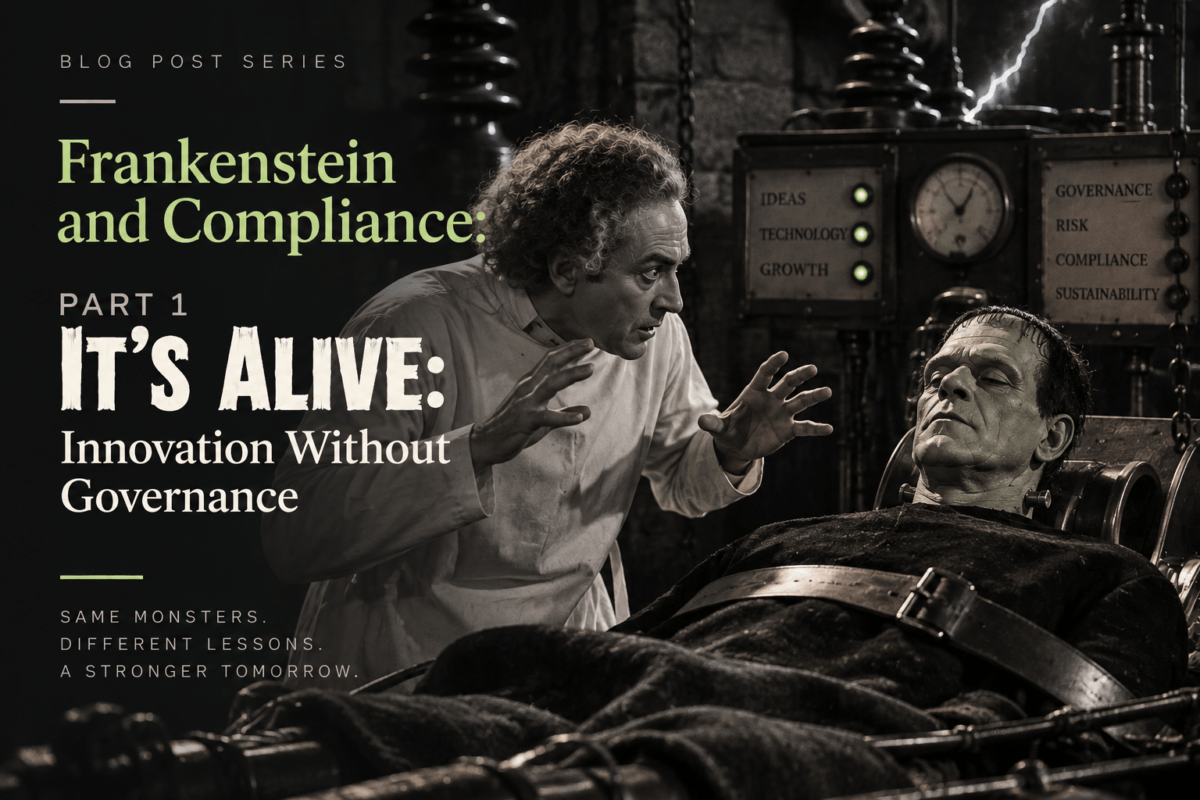
Frankenstein and Compliance: Part 1 – It’s Alive: Innovation Without Governance

Ed. Note: This month, on my podcast series Popcorn and Compliance, I am taking a deep dive into the first five Frankenstein movies. Over October, I will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolfman. The blog post is a companion to the podcast series.

The most famous moment in Frankenstein (1931) comes when Henry Frankenstein’s experiment succeeds. Electricity surges through his laboratory, the body on the table begins to move, and Frankenstein celebrates what he believes is an extraordinary scientific achievement.

“It’s alive!”

For the corporate compliance professional, however, the critical decisions occurred before Henry ever activated his equipment. He had decided to proceed without an adequate risk assessment, effective oversight, meaningful challenge, or a plan for managing the consequences if his experiment succeeded. Viewed through that lens, Frankenstein is not simply a horror movie about a scientist and the Monster he creates. It is a case study in innovation without governance.

That lesson is especially relevant as companies accelerate the adoption of AI and other emerging technologies. Businesses are appropriately focused on innovation, productivity, efficiency, growth, and competitive advantage. Yet technological capability can develop faster than the governance structures needed to manage the resulting risks. The compliance issue is not whether companies should innovate. They must. The issue is whether governance keeps pace with innovation.

The Business Case Was Clear. The Governance Case Was Not.

Henry Frankenstein has a compelling objective. He believes he can accomplish something no one has accomplished before. He assembles the equipment, obtains the materials, develops the technical capability, and builds a team capable of executing the project. In corporate terms, Henry has a strategy, resources, technical expertise, and executive sponsorship. He lacks an effective governance framework.

Before activating his creation, Henry conducts no meaningful risk assessment. He does not identify potential failure scenarios or establish control requirements. He does not define stopping criteria or determine who has authority to challenge the project. No meaningful contingency plan exists for an adverse outcome. This is precisely where compliance should enter the business process.

An effective compliance function should not first encounter a significant new technology when the business seeks approval immediately before deployment. Compliance needs to participate early enough to understand the business objective, identify the associated risks, and help determine appropriate controls.

That does not mean Compliance should own innovation or assume responsibility for the underlying business decision. Risk ownership should remain with the business. Compliance should help ensure that management understands the legal, regulatory, ethical, and control implications of the decision before significant commitments are made.

For the CCO, this raises a practical question: When does Compliance become involved in our company’s innovation process? If the answer is immediately before launch, the organization may already be too far downstream.

AI Has Made the Frankenstein Problem Immediate

Artificial intelligence makes the Frankenstein governance issue particularly relevant. Companies are deploying AI to analyze information, generate content, assist customer service, support investigations, screen candidates, evaluate transactions, enhance due diligence, identify suspicious activity, and improve decision-making. These applications can generate significant business value. They also raise governance questions that organizations must address before deployment.

Organizations need to understand what data an AI application uses, how it obtained that information, who approved the use case, and which regulatory requirements apply. They should determine how outputs are validated, where human review is required, how confidential information is protected, and what happens when a system produces an unexpected or inappropriate result.

There must also be clear accountability. Someone should own the business risk associated with the use case, and the organization should understand who has authority to suspend or terminate the application if circumstances warrant.

The NIST AI Risk Management Framework provides one useful approach through its Govern, Map, Measure, and Manage functions. ISO/IEC 42001 similarly treats AI through a management-system framework emphasizing governance, accountability, risk management, and continual improvement.

Both approaches reinforce a broader compliance principle: technology risk needs governance throughout the lifecycle. Henry Frankenstein has no lifecycle governance. His approach is essentially to build the system, activate it, and evaluate the consequences afterward. That is not an acceptable corporate control environment.

The Abnormal Brain and the Importance of Validating Inputs

One of the film’s most useful compliance scenes occurs before the Monster comes to life. Henry needs a brain for his creation. His assistant Fritz obtains one, but the intended specimen is destroyed. Rather than report what happened, Fritz substitutes another brain, identified in the film as abnormal, without telling Henry. (Abbey Normal—if you know, you know.) The project therefore proceeds after a critical input has changed without the project leader’s knowledge.

For compliance professionals, the scene provides a useful analogy for third-party risk, supply-chain controls, due diligence, and data governance. Organizations routinely rely on information others provide. A distributor provides beneficial ownership information. A vendor completes a compliance certification. An employee submits an expense report. An acquisition target makes representations during due diligence. A supplier certifies compliance with contractual obligations. An AI application relies upon data obtained from multiple sources.

The relevant control question is not simply whether the required information was received. It is whether the organization appropriately validated important information based on risk. Fritz completed his assignment in the narrowest sense. He returned with a brain. The process failed because nobody verified that he returned with the correct brain. That distinction is important for compliance program effectiveness. A completed checklist demonstrates that an activity occurred. Appropriate validation assures that the control achieved its purpose.

Dr. Waldman and Credible Challenge

Henry is not entirely without oversight. Dr. Waldman understands what Henry is attempting and recognizes the potential danger. He raises objections. Henry proceeds anyway. This takes the film from risk assessment into the effectiveness of the challenge function. Many companies can demonstrate that compliance participated in a significant decision. That does not necessarily establish that a compliance professional had meaningful influence over the outcome. A CCO can attend meetings, review proposals, identify concerns, and recommend additional controls. If commercial leadership can routinely disregard those concerns without escalation, the company may have consultation without credible challenge.

This is why the authority, stature, resources, independence, and access of the compliance function matter. The effectiveness of a corporate compliance program becomes most visible when it disagrees with an important business proposal. Boards should therefore look beyond whether your compliance function was consulted. They should understand what happens when a compliance officer disagrees with the business. They need to ask such questions as: Can the CCO escalate a significant concern? Does the CCO have appropriate access to the Audit Committee or board? Are material disagreements documented? Who has authority to accept significant compliance risk? Can commercial management override a compliance objection without further review?

If a CCO can raise a concern but nobody with decision-making authority has to address it, the organization has created the appearance of challenge without its substance. Dr. Waldman had a voice. He lacked the influence to change the decision.

Maria and the Risk of Unintended Consequences

Next we consider one of the most poignant scenes in the movie. The encounter between the Monster and young Maria provides another important business lesson. This is certainly one of the most unforgettable, and indeed tragic, scenes in all the Frankenstein movies. If you have ever seen it, you will never forget it. A small child, Maria, shows the Monster how flowers float on the lake. He imitates what he observes. When the flowers are gone, he throws Maria into the water, apparently expecting her to float as the flowers did. The consequences are tragic. The Monster recognizes a pattern without understanding its context.

That distinction has obvious relevance for artificial intelligence and automated decision-making. A system may identify patterns, generate recommendations, and produce technically consistent outputs without understanding their broader legal, ethical, or business implications. A technically accurate output can still create an inappropriate result.

This is why human oversight cannot exist merely as language in an AI policy. Companies need to determine where human judgment is required, who provides that judgment, what qualifications reviewers need, when automated recommendations can be overridden, and how significant exceptions are documented.

Management should also understand whether human review is substantive or simply procedural. An employee clicking an approval button after an automated recommendation does not necessarily constitute meaningful oversight. The relevant control question is not simply whether the technology performed as designed. It is whether the resulting decision was appropriate.

Innovation Requires Accountability

Henry eventually discovers that creating something and controlling it require different capabilities. Corporate leaders should understand the same distinction. Management establishes incentive structures, sales strategies, compensation plans, technology deployments, acquisition strategies, third-party relationships, and performance expectations. Those decisions shape employee behavior and create risk. Leadership accountability therefore does not begin only after misconduct occurs. It begins with the decisions that establish the operating environment.

For the CCO, this means integrating compliance risk into strategic business decisions. For management, it means risk ownership remains with the business. For the board, oversight should focus on whether management has reasonable systems to identify, manage, monitor, and escalate significant risks. Compliance does not own a business risk simply because the compliance function identifies it. Management remains responsible for the business decision and the risks it creates.

That principle becomes particularly important with emerging technology. The CCO should contribute expertise regarding regulatory requirements, ethical considerations, controls, monitoring, and escalation. Technology leaders should contribute technical expertise. Legal, Privacy, Information Security, HR, Internal Audit, and other functions may have roles depending on the application. Business leadership remains accountable for the decision to deploy the technology and the resulting business risk.

Practical Actions for the CCO

Frankenstein suggests a practical agenda for compliance leadership. Compliance should move upstream and identify significant business processes where its participation adds the most value before making commitments. Emerging technology, acquisitions, market entry, compensation design, significant third parties, and new products are obvious candidates.

Risk assessment should occur before deployment and should address foreseeable legal, compliance, ethical, operational, and reputational consequences. High-risk inputs supplied by employees, vendors, third parties, acquisition targets, or technology systems should receive risk-based validation.

The organization should also define what credible challenge means in practice. Escalation procedures should be clear when Compliance and business leadership disagree about significant risk.

Finally, treat approval as the beginning of governance rather than its conclusion. Test controls, monitor outcomes, analyze exceptions, and update risk assessments as the business and technology evolve. The objective is not to slow innovation. It is to make innovation governable.

The Compliance Lesson

Frankenstein is not an argument against innovation. It is an argument for governance.

Henry Frankenstein failed not because he attempted something extraordinary. He failed because his technical ambition outpaced his ability to identify, understand, govern, and control the resulting risk.

Companies face the same challenge today. Technology will advance. Business models will change. New markets will open. Competitive pressure will accelerate decision-making. New risks will emerge. Compliance’s role is not to stand outside the laboratory and demand that the electricity be turned off.

It is to help ensure that management has assessed the risk, validated critical inputs, established appropriate controls, defined accountability, created meaningful challenge, and determined how the organization will respond if the initiative produces an unexpected result. The best time to build that governance structure is before deployment.

Our next installment moves the compliance analysis forward. In Bride of Frankenstein, Henry no longer faces an unknown risk. He has already experienced the consequences of his original experiment and understands what can go wrong. Then Dr. Pretorius persuades him to return to the laboratory.

The compliance issue is no longer whether leadership identified the risk. It is what happens when leadership knows better, but pressure, ambition, and rationalization push the organization toward the same risk again.

Check out Timothy and Fiona’s commentary on Frankenstein here.
Categories
Blog

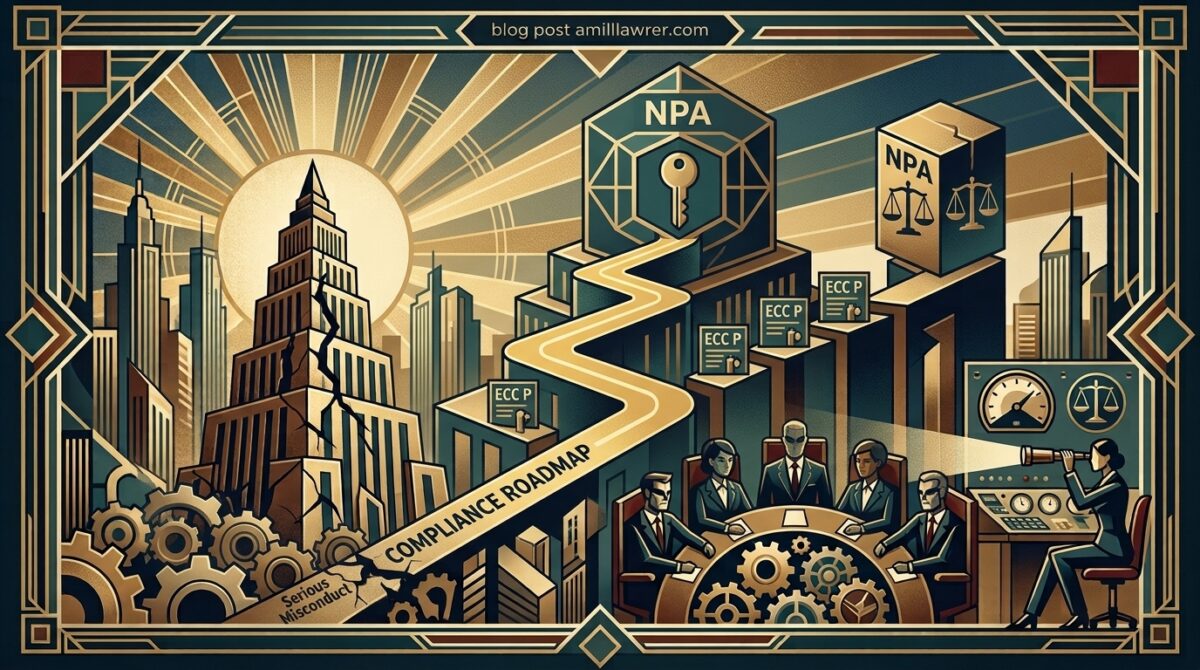
Southern Glazer’s Compliance Roadmap: How the ECCP Helped Turn Serious Misconduct into an NPA

For years, compliance professionals have turned to the Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) to answer a fundamental question: What does an effective compliance program actually look like? Unfortunately, given statements from the early Trump Administration, many compliance professionals feared the Administration would withdraw or otherwise eviscerate the ECCP.

Southern Glazer’s resolution gives us one of the clearest answers in recent memory. The answer is a resounding no: the ECCP is alive and well, even under this DOJ.

Southern Glazer’s entered into a two-year Non-Prosecution Agreement (NPA) with the U.S. Attorney’s Office for the Northern District of California and agreed to pay $12.5 million to resolve a federal criminal investigation involving improper payments, gifts, travel, gift cards, and other benefits. Some of those benefits were facilitated through third-party vendors and concealed through false invoices.

The underlying conduct was serious. Five former Southern Glazer’s employees were indicted in March 2026 for an alleged conspiracy involving commercial bribery and obstruction. Prosecutors alleged that approved vendors and suppliers were used to disguise payments for prepaid gift cards, luxury items, and other benefits through false invoices. Yet Southern Glazer’s itself received an NPA.

For compliance professionals, the most important part of this resolution may be why. The government expressly credited Southern Glazer’s with making significant enhancements to its compliance program beginning in 2023 and, remarkably, specifically noted that the company had aligned those improvements with the factors contained in the ECCP. That makes Southern Glazer’s much more than another bribery enforcement action. It provides a roadmap for remediation.

The ECCP Is Not Sitting on the Shelf

There has been plenty of discussion about what role the ECCP would play in the current enforcement environment. Southern Glazer’s provides a concrete answer. DOJ didn’t merely mention that the company improved compliance. The NPA expressly credited Southern Glazer’s for its “significant efforts to enhance its Compliance Program” and to align that program with DOJ’s evaluation guidance.

That is important. The ECCP should not be treated as an academic document or something pulled from the shelf only after the government arrives. It is a blueprint for building, assessing, and improving a compliance program. Southern Glazer’s demonstrates the potential value of using that blueprint during remediation.

The company did not start from zero. DOJ acknowledged that during the relevant period Southern Glazer’s had compliance policies, a Code of Conduct and employee handbook, trade-practice training, and mechanisms for reporting, investigating, and remediating misconduct. In 2019, the company also notified certain third-party marketing companies that it would no longer process incentives through them and terminated their ability to handle incentives and gift cards. Yet the Statement of Facts makes clear that problems persisted. Employees continued using outside mechanisms for gift cards, travel funds, and other benefits after the 2019 intervention.

This case offers an important compliance lesson. Remediation cannot stop at closing the door through which misconduct previously traveled. Compliance must determine whether employees simply found another door.

Put Resources Behind Compliance

Southern Glazer’s response beginning in 2023 was substantial. Between 2022 and 2024, the company increased compliance headcount by 85 percent and compliance funding by more than 65 percent. It also retained outside compliance experts to advise on program enhancements and best practices. Those numbers matter.

DOJ has repeatedly focused through the ECCP on whether compliance has sufficient resources and authority. Southern Glazer’s provides a practical example of what investment can look like when an organization concludes that its existing compliance infrastructure does not adequately address its risks. This was not simply hiring more investigators after misconduct occurred. Southern Glazer strengthened its compliance architecture.

The General Counsel was promoted to Executive Vice President, Chief Legal and Compliance Officer, reporting directly to the CEO. The company created and filled a Senior Vice President of Compliance & Ethics position. It hired a Vice President and Associate General Counsel for the West region and remapped compliance around five business regions. That is a significant point for boards. If management says compliance is important, look at the organization chart and the budget. Resources are evidence of priorities.

Accountability Had to Follow Misconduct

Southern Glazer’s also addressed individual accountability. The NPA credits the company with removing certain vice presidents and managers for violations of company policy, disciplining additional employees, and replacing senior leadership for California and the West Region. That matters because compliance programs lose credibility quickly when discipline stops at organizational rank.

The Corporate Compliance Agreement takes this concept further. It requires applying disciplinary procedures consistently and fairly, regardless of an employee’s position or perceived importance. When misconduct is discovered, the company must also remediate the resulting harm and assess whether the compliance program itself requires modification. That is precisely the right question after misconduct:

Not simply, Who violated the policy?

But also, What allowed them to do it?

An effective investigation should therefore generate two workstreams. One addresses individual accountability. The other addresses program failure.

Follow the Money

The Southern Glazer’s case is also a powerful internal-controls case. The alleged misconduct involved gift cards, travel, luxury goods, entertainment, marketing expenditures, supplier funds, bill-backs, expense reimbursements, and third-party vendors. According to the Statement of Facts, employees sometimes used altered invoices purporting to reflect legitimate business purposes to circumvent company accounting controls.

Southern Glazer’s responded by moving compliance closer to those transactions. The company imposed a Trade Practice Compliance Audit Program and implemented its “iShop” platform for marketing and promotional spending. It also added mandatory ethics and compliance training and additional compliance resources. That is another important lesson from the ECCP.

Training and policies matter, but compliance effectiveness ultimately has to reach the business process. If bribery risk resides in marketing spend, test marketing spend. If risk resides in bill-backs, audit bill-backs. If employees can manipulate expense descriptions, analyze expense data. If misconduct travels through Accounts Payable, build controls into Accounts Payable. The goal is not simply to tell employees not to engage in misconduct. It is to make misconduct harder to execute and easier to detect.

Rebuild Third-Party Risk Around Payment Controls

The third-party remediation may be the most instructive aspect of the Southern Glazer’s resolution. Third parties were not peripheral to the alleged misconduct. They were part of the mechanism through which value could be transferred and transactions disguised.

Southern Glazer’s responded with a Third-Party Management Program requiring vendors to agree to the company’s compliance and audit standards. Vendors became subject to enhanced due diligence and documentation requirements. The company obtained audit rights. Most importantly, vendors had to be approved before the company could issue payment. Southern Glazer’s also offboarded vendors because of the new requirements. That last point deserves attention.

Third-party compliance frequently becomes an onboarding exercise. Conduct diligence. Assign a risk rating. Obtain contractual language. Approve the vendor. Done. Southern Glazer’s demonstrates why that was insufficient. The control environment must connect onboarding to payment. Accounts Payable should not merely assume that a vendor appearing in the system has passed appropriate compliance controls. The process should prevent payment when required approvals have not occurred. That is compliance embedded into operations.

Compliance Has to Reach the Field

Southern Glazer’s also created a network of state-level “Compliance Champions” responsible for promoting awareness locally and providing additional compliance support. That is particularly relevant for geographically dispersed organizations. Corporate compliance can design excellent policies from headquarters. Risk occurs where employees interact with customers, suppliers, distributors, government officials, and other third parties.

Compliance therefore needs mechanisms to reach those employees and understand what is actually happening locally. The ECCP’s focus on whether a compliance program works in practice is important here. A policy residing on an intranet is not embedded compliance. Employees must know whom to call, understand the rules, and believe compliance understands their business.

Tone at the Top Still Matters

Southern Glazer’s also strengthened senior leadership messaging. The NPA specifically cites communications from the President and CEO reinforcing the importance of ethics and compliance. The company also updated its corporate values around “HEART”: Honesty, Excellence, Agility, Respect, and Teamwork.

Tone at the top is sometimes dismissed as soft compliance. It should not be. But tone only matters when behavior follows the message. Here, leadership messaging was backed by increased resources, management changes, discipline, audit mechanisms, training, third-party controls, and structural changes. That combination is important.

A CEO email saying compliance matters is communication. A CEO message backed by budget, personnel, discipline and controls is governance.

Test Whether the Remediation Actually Works

The final lesson is perhaps the most important. Southern Glazer’s did not simply promise that its enhanced program would work. The Corporate Compliance Agreement requires periodic risk assessments, annual review of policies and procedures, appropriate compliance independence and resources, training, confidential reporting mechanisms, adequately resourced investigations, discipline, M&A procedures, and periodic testing designed to evaluate and improve program effectiveness.

The company must also report annually to the USAO and TTB regarding remediation and implementation of its compliance measures during the NPA. At the end of the term, the CEO, Executive Vice President, and Chief Legal and Compliance Officer must certify that the company has implemented a compliance program that meets the agreement’s requirements and is reasonably designed to detect and prevent trade-practice violations throughout its operations.

That puts real accountability behind remediation.

The Southern Glazer’s Roadmap

Every CCO facing a significant compliance failure should study Southern Glazer’s. The lesson is not that remediation guarantees an NPA. The agreement expressly states that the government reached its decision based on the individual facts and circumstances of this case.

The lesson is that remediation matters, and DOJ has given compliance professionals an unusually detailed picture of what meaningful remediation can look like. Southern Glazer’s strengthened leadership. It increased resources. It brought in outside expertise. It disciplined employees and changed management. It strengthened tone at the top. It pushed compliance into the field. It created new audit mechanisms. It improved training. It rebuilt third-party controls. It connected vendor approval to payment. And it committed to continued risk assessment, monitoring, and testing.

Most significantly, it did these things by expressly aligning its compliance program with the ECCP. For CCOs, that may be the most important takeaway from this entire resolution. Do not wait for prosecutors to use the ECCP to evaluate your compliance program. Use it yourself.

Ask whether your program is well designed. Ask whether it is adequately resourced and empowered to function effectively. Ask whether it works in practice. Then test the answers against your actual risks, transactions, third parties, investigations, and control environment.

Southern Glazer’s demonstrates that the ECCP is more than DOJ guidance. Used properly, it can be a roadmap for remediation, a framework for explaining compliance investment to senior management and the board, and, when misconduct occurs, evidence that the company understood the failure and built a stronger program in response.

That is the compliance lesson from Southern Glazer’s. The best time to align your program with the ECCP is before misconduct occurs. The second-best time is when you discover your existing controls weren’t enough.

Other Resources

Tom and Matt Kelly took a deep dive into the Southern Glazer NPA on this episode of Compliance into the Weeds.

Matt Kelly looked at it on Radical Compliance.

Categories
Blog

When the CEO Has to Go: What Forced Departures Tell Boards and CCOs About Governance

CEO succession is usually discussed as a planning exercise. Boards identify potential successors, develop internal talent, periodically review the succession plan, and prepare for the orderly transition that eventually comes with retirement or another planned departure.

But succession does not always wait for the planning calendar. In an article in the Harvard Law School forum on Corporate Governance, titled Forced CEO Departures, the authors reported on a new study by The Conference Board, developed with ESGAUGE and other collaborators, that examined forced CEO departures among Russell 3000 and S&P 500 companies from 2024 through August 2026. Roughly one in seven CEO succession cases were classified as forced in both 2024 and 2025. In the Russell 3000, 49 forced departures occurred in 2024 and 55 in 2025. The S&P 500 recorded seven and 10, respectively. The forced departure numbers are interesting. The governance implications are more important.

This research on forced CEO departures reminds boards to prepare for unscheduled CEO transitions. For Chief Compliance Officers, the findings raise an equally important question: what information should the compliance function be providing to the board before a leadership problem becomes a leadership crisis?

Forced CEO departures demonstrate that succession planning, executive accountability, corporate performance, investor confidence, culture, and risk oversight cannot be separated into different governance boxes. They ultimately meet in the boardroom. For a Chief Compliance Officer (CCO), they also demonstrate why compliance must function as an organizational sensor capable of identifying patterns that individual incidents may not reveal.

Forced Succession Is a Governance Risk

The report defines a forced departure broadly enough to capture the realities of corporate governance. A departure is forced when evidence indicates that the board, activist investors, an investigation, performance concerns, misconduct, or strategic disagreement materially influenced the timing or terms of the CEO’s exit. Importantly, a departure publicly described as a resignation or retirement may still have been board-driven. That distinction matters.

Boards should not think about CEO succession solely as identifying the person who eventually replaces a successful CEO. Succession planning must also contemplate what happens when the board concludes that the current CEO can no longer lead the organization effectively.

The report’s 2024 and 2025 data make that point. Forced departures represented 14.7 percent and 14.8 percent of Russell 3000 succession cases, respectively. Among the S&P 500, the corresponding figures were 14.3 percent and 15.2 percent. Those figures should change the boardroom conversation.

The question is not simply, “Who succeeds the CEO someday?” It is also, “What happens if we need a new CEO next Monday?”

Performance Is Becoming a Governance Question

Perhaps the most significant finding concerns why CEOs were forced out. Underperformance accounted for 37 percent of Russell 3000 forced departures across the period studied. It increased from 31 percent in 2024 to 44 percent in 2025 and remained the largest category through August 2026. Underperformance, activist pressure, and termination without cause collectively accounted for 70 percent of forced departures during the full period.

For directors, that creates a difficult governance question. When does poor performance become a leadership problem? A single disappointing quarter should not automatically become a referendum on the CEO. External economic conditions, industry disruption, commodity prices, interest rates, geopolitical events, and other factors can affect performance.

Yet boards cannot allow those explanations to become permanent excuses. The report recommends establishing in advance the conditions that trigger a deeper assessment of CEO effectiveness. That assessment should extend beyond financial results to strategic milestones, competitive position, organizational capability, and how the CEO responds to setbacks. That is an important governance discipline. Agreeing on the indicators before the crisis reduces the danger of redefining success after performance deteriorates.

The CCO Has a Different Window Into CEO Effectiveness

Here the compliance function enters the discussion. The report is primarily about CEO succession and board governance. It does not assign the CCO responsibility for evaluating CEO performance. Nor should it. But compliance often sees organizational information through a different lens than Finance, Strategy, HR, or Investor Relations.

A CCO may see whether employees are becoming reluctant to speak up. Compliance may identify retaliation concerns involving senior management. Investigations may reveal recurring management override. Hotline data may show patterns concentrated around particular executives or business units. Third-party reviews may expose pressure to circumvent controls. Internal investigations may demonstrate that employees believe commercial performance is valued more highly than ethical conduct.

One event may mean little. Patterns can mean much more. This is why an effective CCO should not simply report hotline statistics to the board. The CCO should help directors understand what the information may be saying about organizational culture, controls, accountability, and risk.

The question becomes: What does the board need to know to discharge its oversight responsibilities?

That is a very different question from: What compliance information did management ask us to provide?

CEO Accountability and the Control Environment

CCOs should also pay attention to forced CEO departures. The CEO sits at the top of the organization’s control environment. The CEO’s conduct affects incentives, resources, accountability, escalation, management behavior, and whether employees believe controls are genuine requirements or obstacles to business performance.

That means directors assessing leadership should consider more than revenue growth and shareholder returns. They should understand whether management responds appropriately when controls identify problems. Some key questions a CCO might ask include:

Does the CEO support investigations even when they involve high-performing executives? Does management remediate identified weaknesses? Are compliance personnel adequately resourced and empowered? Are executives held accountable consistently? Does information reach the board without being filtered into insignificance?

These questions connect CEO oversight to compliance program effectiveness. They also reinforce why direct access between the CCO and the board or an appropriate board committee matters. The value of that relationship becomes clearest when the information the board needs is information senior management would prefer not to discuss.

Activists May Ask the Questions Boards Should Already Be Asking

The report contains another significant finding.

Among S&P 500 forced departures, activist pressure accounted for five of 10 departures in 2025. Across 2024 through August 2026, activists were associated with eight of 19 forced departures, or 42 percent. The report notes that activist campaigns frequently focus on matters already within the board’s remit, including performance, strategy, capital allocation, portfolio structure, governance, and confidence in management. Forced CEO Departures

There is a governance lesson here. A board should not need an activist investor to tell it which difficult questions to ask. Directors should periodically examine the company through an independent investor lens. Where is performance lagging? Which strategic assumptions have not proved correct? Where has capital allocation failed to produce expected results? What would a sophisticated outsider identify as the company’s vulnerabilities?

For the CCO, there is a parallel exercise. What would a regulator, whistleblower, investigative journalist, plaintiff’s lawyer, or enforcement authority see if they examined the same facts? These perspectives are not substitutes for the board’s business judgment. They are tools for challenging assumptions. Effective oversight requires directors to seek disconfirming information, not just information that supports management’s existing narrative.

Succession Planning Needs a Break-Glass Option

The report recommends that boards maintain an accelerated succession plan alongside traditional succession planning. That distinction is critical. A normal succession plan asks who might become CEO in several years. An accelerated plan asks who takes control tomorrow morning.

The board should know who can provide immediate continuity, which internal executives could become permanent successors, when an external search would be required, and how to retain key executives during the transition. The plan should also address interim authority, compensation, severance arrangements, and employee and investor communications. Compliance should be part of that contingency architecture.

Questions might include: If the departure involves misconduct or an investigation, who controls the investigation after the CEO leaves? Who has authority over document preservation? Who makes disclosure decisions? Who communicates with regulators? What happens if other senior executives are implicated? Does the CCO continue reporting through the same management structure, or should reporting temporarily move directly to the board?

The report itself does not address these questions, but they follow directly from the compliance risks created by an unexpected leadership transition. The worst time to design these protocols is during the crisis.

The Board and CCO Need an Early-Warning System

The larger lesson from the forced-departure data is not that boards should terminate CEOs more quickly. It is that boards should become better prepared to recognize and respond to deteriorating conditions.

The report found no consistent company-size profile for forced turnover. Elevated rates appeared across the revenue spectrum. The more meaningful indicators were company-specific factors, including persistent underperformance, strategic misalignment, and investor scrutiny. Forced CEO Departures

That suggests boards need an integrated early-warning system.

  • Financial performance is one signal.
  • Strategic execution is another.
  • Investor sentiment is another.
  • Compliance and culture data should be another.

The CCO can contribute by identifying trends in allegations, investigations, retaliation, control overrides, disciplinary decisions, third-party exceptions, and other indicators that may reveal stress inside the organization. The board then has the responsibility to connect the dots.

Questions for the Board and CCO

Boards should periodically ask whether they have defined the conditions that would trigger a reassessment of CEO effectiveness; whether they have a genuine emergency succession plan rather than simply a long-term succession plan; whether directors receive information about culture, investigations, controls, and retaliation without inappropriate management filtering; and whether they understand recurring concerns raised by shareholders, employees, auditors, compliance, and other stakeholders.

CCOs should ask different questions. Are we giving the board data or insight? Are recurring issues being presented as isolated events? Are senior executives subject to the same accountability standards as everyone else? Does the CCO have a practical route to the board when senior management itself presents the risk? If the CEO suddenly departed tomorrow because of an investigation, could Compliance continue operating without interruption?

Those can be uncomfortable questions. Yet, they are also precisely the questions effective governance requires. Forced CEO departures are not simply stories about executives losing their jobs. They stress-test the governance system around those executives.

The board’s responsibility is to ensure it can recognize when leadership circumstances have materially changed and act deliberately, not reactively. The CCO’s responsibility is different but complementary: ensure that compliance, culture, control, and investigation information that can inform that judgment reaches the board clearly and promptly.

A board should never discover during a CEO crisis that the warning signs were there all along. A better governance model identifies those signals early, understands what they mean, maintains credible succession alternatives, and establishes decision processes before they are needed. That is not planning for failure. It is planning for effective oversight.

Categories
Compliance Into the Weeds

Compliance into the Weeds: Southern Glazer’s NPA: How Remediation and ECCP Alignment Drove a Favorable Settlement

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into compliance-related topics, literally going into the weeds to explore a subject in greater depth. Looking for hard-hitting compliance insights? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss the Southern Glazer NPA.

The Southern Glazer Wine and Spirits’ non-prosecution agreement is a rare example where prosecutors credited compliance program remediation, rather than self-disclosure or extensive cooperation, as central to a favorable outcome. Southern Glazer, the largest US liquor distributor, faced a major California kickback and bribery scheme involving five former employees, fabricated records, sham agreements, and luxury benefits to retailers and others, along with alleged tax impacts. The company resolved the matter with a $12.5 million payment and a two-year NPA requiring the CEO and CCO to certify program effectiveness. Tom and Matt review how the NPA affirms DOJ’s Evaluation of Corporate Compliance Programs as still relevant and detail remediation steps: major headcount and budget increases, upgraded compliance leadership, audits of marketing spend, enhanced training, strengthened third-party controls and AP payment blocks, outside reviews, and tone-at-the-top messaging.

Key highlights:

  • Southern Glazer Case Setup
  • Industry Risks and Scheme
  • ECCP Guidance Still Matters
  • Program Overhaul Timeline
  • Concrete Remediation Metrics
  • DOJ Signals Under Trump Era

Resources:

Matt in Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds was most recently honored as one of the Top 25 Regulatory Compliance Podcasts, a Top 10 Business Law Podcast, and a Top 12 Risk Management Podcast. Compliance into the Weeds has received Davey, Communicator, and W3 Awards, all for podcast excellence.

Categories
Blog

Andrew McBride Does it Again: His New Guide on Buying Compliance Technology

Compliance technology has become the operational backbone of the modern ethics and compliance program. When technology works, it can make compliance faster, more consistent, measurable, and embedded in business operations. When it doesn’t, the consequences show up everywhere: spreadsheets, manual workarounds, disconnected data, frustrated employees, and compliance professionals spending time administering technology rather than managing risk.

That makes buying compliance technology more than an IT procurement exercise. It is a compliance program effectiveness issue. One commentator on this aspect of AI for compliance is Andrew McBride, founder of the consulting firm Integrity Bridge LLC. McBride recently released Recommended Practice for Buying & Selling Compliance Technology, based on surveys of compliance technology buyers and vendors. Its findings illuminate a fundamental imbalance in the marketplace. I can safely say this paper is the standard for compliance professionals evaluating and purchasing AI-based technology.

CCOs buy compliance technology infrequently. Vendors sell it every day. That imbalance matters. Compliance teams can be oversold on functionality. Vendors can become trapped in opaque procurement exercises. Business requirements can become disconnected from technical requirements. AI capabilities can be accepted without sufficient governance. Contracts can focus extensively on getting into a system while ignoring how the company will eventually get out. For the CCO, the lesson is straightforward. If you want to run compliance like a business, you must learn to buy compliance technology like a business. This is where McBride comes in.

Start With Strategy, Not Software

As a CCO, start with a documented compliance technology strategy aligned with business operations. McBride sees three operational layers for that strategy.

Compliance-owned technology includes platforms compliance directly manages, such as Codes of Conduct, training, whistleblower systems, investigation case management, and workflows for gifts, entertainment, and conflicts.

Compliance-shared technology includes systems operated across functions, such as third-party due diligence, transaction monitoring, and communications monitoring.

Enterprise dependency technology includes compliance systems that may not be owned but depend on ERP, CRM, HRIS, procurement, and financial platforms.

This third category is particularly important. A CCO may believe the company has a third-party risk problem when the real issue is poor vendor master data. Transaction monitoring may generate noise because underlying financial data is inconsistent. Technology strategy therefore begins with understanding the compliance program’s architecture.

Know What Compliance Really Costs

Here, McBride frames the question as, ‘What is the total cost of ownership? ‘How many screening tools are independently licensed by Compliance, Procurement, Finance, Credit, and Legal? How many employees maintain spreadsheets? How many hours are spent chasing approvals or reconciling systems? How much compliance talent is consumed by administration rather than risk management? Those costs matter because an inexpensive system can become extraordinarily expensive once you include the human infrastructure required to run it.

This leads to the recurring question: buy, build, or assemble? Internal IT may propose building custom tools. Sometimes that works, but the calculation must include maintenance, upgrades, staffing, cybersecurity, documentation, and key-person risk. Another option is configuring technology the company already owns. That may reduce licensing costs, but “we already own it” does not mean “it is free.” Configuration, integration, testing, administration, and support still cost money.

Commercial software offers established products and vendor-supported roadmaps, but buying software does not eliminate implementation challenges. Apply the same economic discipline to all three options. Don’t compare the sticker price of commercial software with an internal solution whose real costs have never been calculated.

AI Changes the Conversation

AI is moving into transaction analysis, investigation scoping, interview preparation, monitoring, and other compliance workflows. The opportunity is substantial. So is the governance challenge. The Integrity Bridge research presents an interesting picture. AI use appears widespread, but governance and confidence have not necessarily kept pace. Only about one in four compliance teams surveyed had established a formal governance framework. Fewer than half could articulate how AI demonstrably improved compliance outcomes. Only 41 percent of compliance leaders trusted AI-driven outputs for operational decisions.

At the same time, 84 percent reported efficiency gains, while fewer than half reported actual cost savings. That distinction between efficiency and effectiveness is critical. Doing something faster does not necessarily mean doing it better. The CCO should not simply ask, “Does this product use AI?” The better question is, “What compliance outcome does the AI improve, and how can we demonstrate it?”

AI Governance Starts Under the Hood

“AI-powered” is not a meaningful technical specification. McBride advises that compliance should understand what happens under the hood. Once again, he is spot on. Ask questions such as, “Which model is being used?” What information goes into it? What comes back? Is customer information retained? Can corporate data be used for training? Does a third-party model provider receive the information?

These are compliance governance questions because the data may include investigations, employee information, third-party records, or financial information. The contract should address how that information is handled and establish appropriate restrictions on the use of corporate data and queries.

Next, a series of questions about where the AI can fail. Here McBride suggests: How does the system prevent cross-tenant data leakage? How does it identify unsupported statements, hallucinations, or fabricated citations? What happens when malicious instructions are hidden inside uploaded documents? Most importantly, does the system recognize when it lacks sufficient confidence and escalate the matter to a human?

One of the most important characteristics of compliance AI may not be its ability to answer questions. It may be its ability to recognize when it should not answer them.

Keep Humans in the Control Environment

Agentic AI raises the stakes because technology moves from providing information to taking action. But this requires clear authority boundaries. What systems can the agent access? What records can it change? What decisions can it make? Which actions require approval?

Certain compliance decisions should remain subject to documented human authorization. Closing an investigation, changing third-party screening rules, or approving high-risk onboarding are obvious examples. This is where AI governance becomes internal controls. The organization should demonstrate not merely that humans are theoretically “in the loop,” but where human intervention occurs, who has authority, what approval evidence is retained, and what happens when the AI crosses a defined threshold.

CCOs must also understand AI economics. Traditional platforms may be priced by employees, users, or third parties. AI functionality can introduce consumption pricing tied to tokens, documents, searches, or API calls. Model realistic usage and negotiate appropriate spending caps, alerts, overage controls, and consumption rates.

Turn the RFP Into a Governance Exercise

A good RFP does more than collect vendor responses. It forces the organization to define what it actually needs. McBride highlights vendor frustration with “phantom RFPs,” where an incumbent has effectively been selected, or the process is used primarily to gain renewal leverage. A credible RFP must instead be transparent, disciplined, and operationally grounded.

Start with Procurement. Understand source-to-pay requirements, spending thresholds, cybersecurity reviews, privacy requirements, and contracting procedures before bringing vendors deep into the process. Then give vendors meaningful operational information: employee populations, transaction volumes, existing systems, data maturity, integrations, geographic requirements, and workflow constraints.

Most importantly, force precision into vendor answers. Require vendors to classify functionality as:

  1. Available out of the box.
  2. Available through configuration.
  3. Available through a named third-party integration.
  4. On the roadmap with a committed date.
  5. Not supported.

That discipline can dramatically improve an evaluation and create a record of what was actually promised.

Stop Buying Features. Test Controls.

Feature checklists have limits.

McBride suggests that a better test is a scenario. Suppose a critical third party is added to a sanctions list overnight. Ask the vendor to show exactly what happens. Ask questions such as, “How is the alert generated?” Who receives it? How is it prioritized? Who can override it? How is the matter escalated? What evidence is captured? What appears in the audit trail?

Now you are not evaluating a feature. You are evaluating a control. The same principle applies to sandboxes. A generic vendor sandbox tells you relatively little. Require a guided environment configured around your workflows using synthetic or anonymized data. Make users perform the work. That is where implementation problems begin to reveal themselves.

Look Under the Hood Before You Buy

A beautiful interface can be seductive, but buying compliance technology based primarily on user experience is like buying a house because you like the countertops without checking the plumbing. However, before you make a final selection, conduct due diligence around security controls, hosting, uptime, integrations, implementation resources, and data portability.

Review relevant SOC 2 Type II controls. Speak with peer customers. Consider asking to speak with a customer that recently left the platform. Just as importantly, interview the people who will actually implement the product. The team delivering the sales demonstration may not be the team handling implementation. Know who shows up after the contract is signed.

Begin the Relationship by Planning the Exit

Perhaps the most overlooked element of compliance technology contracting is the exit. Companies spend enormous time determining how information will enter a system and surprisingly little determining how they will get it back. A CSV containing basic fields may not recreate an investigation file or preserve the history of a third-party approval. It may not capture attachments, comments, timestamps, escalations, approvals, or audit trails.

Before signing, define export requirements. Ask questions such as: What formats will be provided? What metadata will be preserved? What happens to attachments? Will the audit trail survive? How long will migration assistance remain available? What will extraction cost? When will the vendor delete remaining copies? Understand how you will leave a compliance technology provider before deciding to join it.

The CCO’s Technology Mandate

Compliance technology doesn’t succeed or fail when Legal finishes negotiating the contract. The outcome is largely determined earlier. Did Compliance understand the business problem? Did it know the true cost of the existing process? Did it understand its data? Did it challenge AI claims? Did it test failure modes and workflows? Did it involve Procurement, IT, Privacy, Security, Legal, and the business at the right points? Did it negotiate for implementation, operation, and exit?

Those questions turn technology procurement into compliance governance. Compliance professionals spend their careers asking businesses to operate with transparency, accountability, documentation, fairness, and integrity. Compliance should bring those same principles into the technology marketplace.

Define what you need. Understand what it costs. Test what the vendor claims. Document what was promised. Build controls around AI. Measure whether the technology improves the program. Make sure you can get your data back when the relationship ends. That is what it means to run compliance like a business.

Practical Takeaways

For the CCO, the mandate is clear: build the strategy before selecting the technology; calculate the Total Cost of Ownership rather than the license cost; treat AI as a governance and internal controls issue; test workflows rather than watch demonstrations; diligence the implementation team; and negotiate data portability and exit before signing.

For boards and senior management, the oversight question is equally straightforward: What compliance risk is this technology addressing, how will management measure whether it improves program effectiveness, and what controls govern its use?

The answer tells you much more than whether Compliance has purchased the latest technology. It tells you whether the organization is building a technology architecture that can support an effective compliance program.

If you do not follow Andrew McBride on LinkedIn, you should. He is leading the discussion on the practical aspects of putting the right AI tool in place for you and your organization. His organization will be displaying at this week’s SCCE CEI, so drop by the Integrity Bridge and find out why I think he is the go-to guy in this area.

Categories
FCPA Compliance Report

FCPA Compliance Report: From Prosecutor to White Collar Lawyer to CCO and Back: Mike Koenig

In this episode, Tom Fox welcomes Mike Koenig to talk about his career and his recent move back to private practice after a 5-year stint at JBS. Mike is one of the few folks to move from private practice to an in-house CCO role, then back to private practice.

Mike began by reviewing his career, from 25 years in private practice and a 2003 DOJ Fraud Section stint prosecuting corporate fraud to becoming chief compliance officer at JBS in August 2021 amid DOJ and SEC settlement agreements requiring an effective compliance program. He describes learning to operate within business-driven priorities by building relationships, learning the business and culture, “educating not dictating,” and securing C-suite, board, and audit committee buy-in, including CEO-driven training completion. He explains that he uses trusted outside experts and focuses on the specific problem to solve rather than “boiling the ocean.” After JBS completed the settlements and listed on the NYSE in June 2025, he returned to private practice at Friedman Kaplan to advise on investigations and compliance, emphasizing concise, solution-oriented counsel. He warns against de-prioritizing compliance despite reduced enforcement, urges risk assessments (tariffs, export controls, and human rights), and recommends using DOJ compliance guidance to review programs.

Key highlights:

  • Career Journey Recap
  • Joining JBS In-House
  • Building Compliance Fast
  • Relationships Not Dictates
  • Leadership Buy-In
  • FCPA Pause or a Wake-Up Call
  • Compliance Through 2030

Resources:

Mike Koenig on LinkedIn

Mike Koenig at Friedman Kaplan

Friedman Kaplan

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
AI Today in 5

AI Today in 5: September 24, 2026, The Complicating Compliance Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Flock says it will set limits. (WSJ)
  2. Mental health strains on AI workers. (FT)
  3. Does the EU AI Act complicate compliance? (IAPP)
  4. Boards say they need more from management on AI. (CCI)
  5. Compliance teams struggling with AI auditing. (FinTech Global)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Great Women in Compliance

Great Women in Compliance: Together, What We Can Do: Sharon Seivert on Ethics, Systems and the Six Powers

What if ethics and compliance weren’t something we bolted onto organizations but something built into how the organization actually works?

In this episode of Great Women in Compliance, Dr. Hemma R. Lomax talks with Sharon Seivert, Founder and CEO of Core Coaching & Consulting and creator of the SIX POWERS® framework, about organizational health, human agency, and building integrity from the inside out.

For Sharon, the work is deeply personal. She shares how the loss of her brother John in a workplace accident shaped her commitment to healthier systems and raises a question at the heart of the conversation: when something goes wrong, do we focus only on the individual event, or do we allow what happened to teach the system?

Sharon and Hemma explore what becomes possible when organizations are treated as living systems capable of learning, adapting, and recovering, and why ethics and compliance professionals should not have to do that work alone.

Highlights include:

  • Sharon’s personal connection to ethics, compliance, and workplace safety
  • The SIX POWERS® framework: Core, Vision, Mission, Interactions, Structure, and Synergy
  • Why purpose and principles can act as an organizational “tuning fork”
  • The difference between individual responsibility and systemic responsibility
  • Finding and using your own “hub of power”
  • The hidden costs of ethical compromise
  • Why near misses should teach the system, not simply disappear into a case file
  • Building organizations with enough “wobble” to adapt, recover, and evolve
  • Why, ultimately, together we can do hard things well

Further reading from A Thinking Game

Sharon Seivert: Powering the Future: A Six Powers Roadmap & Compass. Evolve Organizations. Activate Leaders. Ignite Purpose.

Available on Amazon

This conversation also helped inspire Hemma’s latest A Thinking Game article, “A Community of Many Splendid Torches,” which explores what becomes possible when individual acts of courage, care, and participation are understood as part of a larger human system.

A Thinking Game on LinkedIn

A Thinking Game on Substack

Bio

Sharon Seivert is the Founder and CEO of Core Coaching & Consulting, LLC, where she works at the intersection of leadership, systems thinking, and organizational health. A former CEO in healthcare and business consulting, Sharon brings decades of experience helping leaders, teams, and organizations navigate complex change.

She has written multiple books on her signature SIX POWERS® framework, a holistic approach designed to strengthen leadership and organizational health from the inside out. Her work brings together purpose, strategy, relationships, and systems thinking to help individuals and organizations become more integrated, resilient, and capable of lasting transformation.

Sharon is also a leadership coach, business consultant, and speaker, working with organizations ranging from startups to Fortune 500 companies and with a global community committed to healthier ways of living and leading.

Categories
Innovation in Compliance

Innovation in Compliance: Inside EB-5: Immigration, Finance, Compliance and Governance Collide

Innovation comes in many areas, and compliance professionals need to not only be ready for it but also embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom welcomes Michelle Tavares, a former federal government forensic accountant and former USCIS EB-5 compliance officer who helped rewrite the EB-5 statute into the Reform and Integrity Act (RIA).

Michelle Tavares brings a rare blend of forensic accounting, securities litigation, and federal investigative experience to her perspective on EB-5 visa program compliance and adjudication. Having worked on white-collar crime matters and immigration policy, and as a compliance officer for the EB-5 program, she helped shape the Reform and Integrity Act, which strengthened oversight, penalties, and investor protections. Tavares believes the old EB-5 framework lacked meaningful enforcement, and she argues that USCIS now properly scrutinizes regional centers, attorneys, and related parties through background checks, AML/KYC review, and a broader integrity lens. From her viewpoint, successful EB-5 filings depend on consistent, credible evidence across immigration, securities, banking, and governance issues, with better guidance helping honest organizations avoid preventable compliance mistakes.

Key highlights:

  • EB5 Compliance, Penalties, and AML-KYC Overhaul
  • Four lenses on every EB5 transaction
  • Preponderance of Evidence in EB-5 Compliance Narratives
  • Vetting vendors, promoters, and experts for EB5 compliance

Resources:

Standard & Proof Investigations

Counsel Ready

Michelle Tavares on LinkedIn

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Innovation in Compliance was recently honored as the Number 4 podcast in Risk Management by 1,000,000 Podcasts

Categories
AI Today in 5

AI Today in 5: September 15, 2026, The Medical AI Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. What’s holding back AI in financial services? (FinTech Global)
  2. EU demands AI companies meet safety requirements. (The Jerusalem Post)
  3. Data quality is holding back AI in banks. (Asian Banking & Finance)
  4. Cybersecurity enhanced with AI. (FinTech Magazine)
  5. Trump Administration moving to deploy AI in medicine. (NYT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.