Categories
Innovation in Compliance

Innovation in Compliance: Mara Senn on Vibe Coding a Credible Investigations Platform

Innovation comes in many areas, and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom welcomes Mara Senn, Founder and CEO of Ethakos.

What is innovation in compliance? Mara Senn certainly shows it in this podcast. Her path to founding Ethakos spans Big Law, early FCPA and anti-corruption work, investigations at the World Bank, and senior in-house compliance roles at major Fortune 500 companies. That experience gave her a clear view of the everyday frustrations compliance teams face, especially clunky tools, dirty data, and rigid workflows that slow down real investigations. She built Ethakos as an AI-native, highly configurable platform to solve those pain points, using “vibe coding” with Claude to move quickly while keeping human judgment at the center of every decision. In her view, the platform reflects a simple but powerful idea: AI should make compliance work faster and cleaner, not replace the expertise and risk-based thinking that good compliance professionals bring.

Key highlights:

  • Vibe coding Ethakos through dozens of decisions
  • Start with actionable hits, not meaningless alerts
  • AI-generated first drafts for chronologies and interviews
  • Audit logs and document-linked investigative credibility
  • Tech-forward compliance teams identifying 13 risks instead

Resources:

Ethakos

Mara Senn on LinkedIn

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

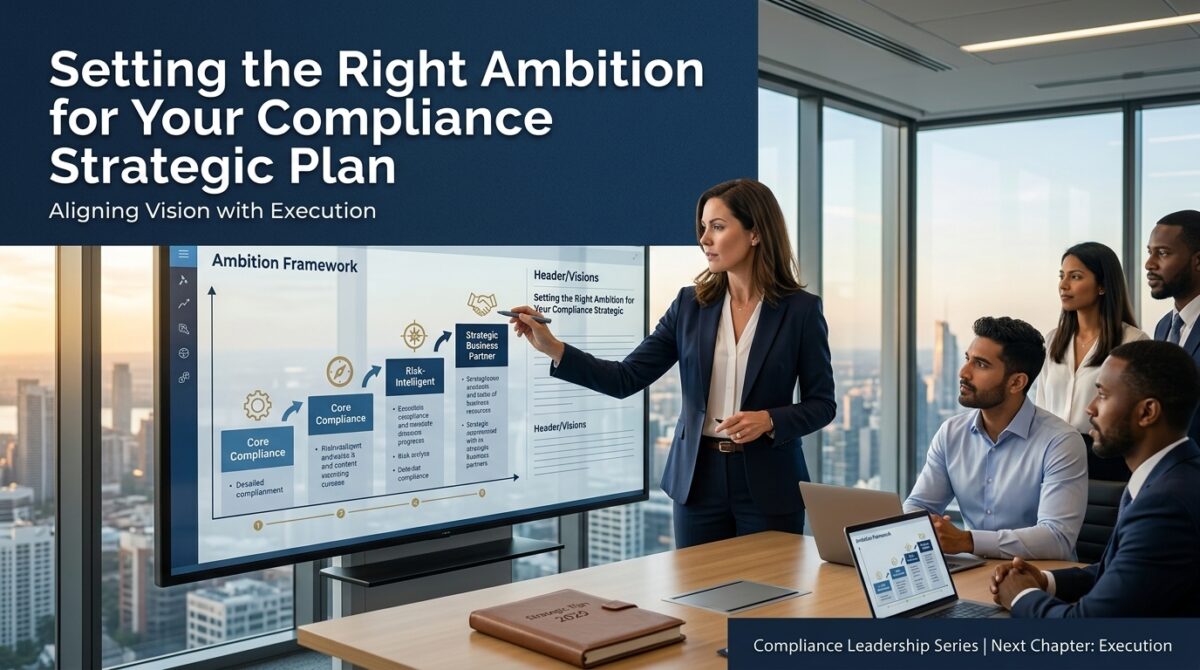
Setting the Right Ambition for Your Compliance Strategic Plan

A compliance strategic plan should explain how the function will build the capabilities the business needs to manage its risks. That requires choices about priorities, resources, authority, and execution. A plan can fall short by asking the organization for too little. It can also promise more than the company is prepared to support.

Consider a CCO preparing a three-year plan while the company expands through acquisitions and new distribution channels. The proposed compliance plan calls for refreshed policies, additional training, and a new monitoring platform. Each initiative may be useful. But does the plan address the integration gaps and third-party decisions that expansion will create? And has anyone committed the people, data, and funding needed to deliver it?

Rebecca Knight explores the calibration of strategic ambition in “Is Your Strategic Plan Too Ambitious? Or Not Ambitious Enough? In the Harvard Business Review. Her article draws on insights from Columbia Business School’s Sheena Iyengar and MIT Sloan School of Management’s Donald Sull. Their discussion provides a useful foundation for examining the compliance function’s strategy. The compliance applications below build on that discussion.

Define the Problem Before Setting the Target

Knight begins with Iyengar’s advice to identify the problem a strategy must solve before debating the ambition of its targets. For CCOs, this discipline matters because familiar deliverables can substitute for a clear diagnosis. Take a goal to increase training hours. What problem requires that increase? Employees may misunderstand an approval requirement. They may understand it perfectly but lack a workable way to obtain approval before a commercial deadline. Those conditions require different responses.

The strategic plan should connect each major initiative to an identified weakness or emerging business need. If acquisitions repeatedly leave the company with incomplete third-party records, define the intended capability: an integration process that establishes ownership, identifies missing information, and escalates unresolved risks within a specified period. This gives management a concrete outcome to fund and the board a meaningful basis for oversight.

Develop Alternatives Before Committing Resources

Knight reports Iyengar’s recommendation to consider several distinct approaches so leaders can see their trade-offs. A CCO can apply this by requiring alternatives for the plan’s largest investments. Suppose the objective is better third-party monitoring. One option might strengthen existing reviews and accountability. Another might integrate procurement and payment data. A broader approach might redesign the third-party lifecycle, including who can engage an intermediary and what evidence permits renewal.

Compare the options against the actual problem, implementation demands, and expected improvement. A technology purchase may be appropriate, but its value depends on the process and information supporting it. This exercise also exposes insufficient ambition. If every option preserves the same fragmented ownership that created the problem, the CCO has reason to question whether the proposed change goes far enough. A major redesign also needs stronger justification than an attractive vision of a fully integrated program.

Make Resource Commitments Explicit

Sull’s resource argument, as Knight presents it, is that substantial strategic change can require moving money and talent away from existing commitments. That has direct implications for compliance planning. CCOs often describe new responsibilities without specifying which existing activities will change. A team already handling investigations, advice, training, and monitoring cannot absorb unlimited transformation work simply because the strategic plan assigns it a deadline.

For each major initiative, identify the required budget, expertise, business participation, and implementation time. Explain what can be simplified or discontinued and what must remain protected. Required controls and essential response capacity need explicit provision during the transition.

Dependencies deserve the same attention as the compliance budget. If success requires information technology support, procurement process changes, or finance data, obtain named owners and documented commitments. Where a critical commitment is missing, describe the resulting limitation in the proposal presented to leadership. Your board should be able to see the relationship between the approved ambition and the resources management has committed.

Build Capability Around the Business Strategy

Knight’s discussion of staffing emphasizes the expertise needed to execute a bold plan. Applied to compliance, the question extends beyond headcount to the capabilities the company’s direction requires. Acquisition-led growth may require stronger integration management. Expansion through distributors may require regional knowledge and commercial experience. A monitoring initiative may require data analysis, systems access, and people who understand how transactions occur.

Map the company’s major strategic moves to their compliance implications, then identify the skills and authority needed to respond. This helps the CCO explain why the function needs particular capabilities and when those capabilities must be available. Business alignment also requires independence of judgment. The plan should enable informed decisions about growth while preserving the CCO’s ability to challenge unsupported assumptions, escalate concerns, and identify conditions that should be met before proceeding. Management owns the commercial strategy; compliance must be equipped to assess and address its implications.

Use Pilots With Clear Decision Rules

Knight describes experimentation as a way to pursue ambitious goals while learning through smaller steps. A compliance plan can use that approach to improve processes and build new capabilities. For example, a proposed monitoring method could begin in one business unit. Before launch, define the information required, the existing controls that remain in place, the people responsible for reviewing results, and the conditions for expansion or revision.

The pilot should answer a specific question. Does the method identify relevant exceptions? Can the business resolve them? Are the results dependable enough to support decisions? A successful software demonstration alone does not answer those questions. Set a review date and a decision owner. Without those commitments, a pilot can continue indefinitely, consuming resources while providing little clarity about whether the broader strategic objective is achievable.

Measure Progress Toward a Working Capability

Knight connects a longer strategic horizon with measurable interim progress. This is particularly useful for compliance improvements that require changes across functions and systems. A multi-year goal to improve acquisition integration could include quarterly milestones for establishing ownership, validating acquired third-party records, addressing priority exceptions, and testing whether the revised process works on a subsequent acquisition.

Select measures that reveal both implementation and performance. Completing a procedure establishes that something was produced. Evidence that business teams use it, resolve exceptions, and escalate overdue actions helps show whether the capability is functioning.

Establish a baseline before claiming improvement. Faster review times need context about review quality. Fewer exceptions need context about detection coverage. Report limitations alongside results so management and directors can distinguish progress from incomplete information. The strategic plan should also specify when it will revisit assumptions. A major acquisition, a new business model, or a material change in available resources may require revised priorities and sequencing.

Give the Board Decisions It Can Assess

Board oversight becomes more useful when the CCO presents the choices behind the plan. Directors need to understand the priority problems, the proposed response, the resource commitments, and the consequences of delay.

A practical strategy discussion should explain what the function expects to accomplish, what depends on other executives, and what remains outside the funded scope. Where alternatives exist, show their implications for timing and capability. This gives the board a basis to challenge both overpromises and underinvestment. It also establishes what management should report back as the plan proceeds.

Action Steps for the CCO

Use the next planning review to test whether ambition and execution are aligned:

  1. Define the priority problems. State the business risk or capability gap behind each major initiative and the evidence supporting its priority.
  2. Compare credible alternatives. Examine different ways to achieve the intended outcome, including their costs, dependencies, and implementation demands.
  3. Secure resource commitments. Identify accountable business partners, required expertise, funding, and the activities that must change to make room for execution.
  4. Set milestones and decision points. Establish baselines, measures, pilot criteria, and dates for reassessing assumptions.
  5. Present the choices to the board. Explain the funded scope, unresolved dependencies, and consequences of deferring priority capabilities.

A sound compliance strategy makes a demanding but supportable commitment to improving how the company manages risk. The CCO’s responsibility is to make that commitment specific enough to execute, measure, and oversee.

Categories
FCPA Compliance Report

FCPA Compliance Report: Michelle Tavares on Why Compliance Teams Need EB-5 on Their Radar

In this episode, Tom Fox welcomes Michelle Tavares, a former federal government forensic accountant and former USCIS EB-5 compliance officer who helped rewrite the EB-5 statute into the Reform and Integrity Act (RIA).

Tavares explains EB-5 as an investor visa program where foreign nationals invest $1,000,000 (or $800,000 in a TEA) in U.S. projects that must create jobs, and she describes how EB-5 transactions sit at the intersection of immigration, securities, banking/AML, and corporate governance, making consistent documentation and a unified “story” critical for adjudication. She outlines the roles of regional centers, NCEs, and JCEs; the challenges of proving a lawful source of funds; and the importance of third-party oversight, KYC/AML controls, and tone-from-the-top governance. She discusses how RIA added compliance expectations, penalties, and increased scrutiny of regional centers and overseas promoters, and shares why she founded Standard & Proof Investigations to close knowledge gaps in EB-5 compliance.

Key Highlights:

  • EB-5 Basics and Why It Matters
  • RIA Overhaul and New Compliance
  • Inside the Adjudicator Mindset
  • Boardroom Governance for EB-5
  • Third-Party Oversight Essentials

Resources:

Standard & Proof Investigations

Counsel Ready

Michelle Tavares on LinkedIn

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Daily Compliance News

Daily Compliance News: September 14, 2026, The Fighting Corruption Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • Fighting corruption in Iraq. (The Guardian)
  • Brazilian presidential candidate under investigation for corruption. (NBC News)
  • How China’s new ABC law will impact companies. (China Briefing)
  • China extending its legal reach to fight sanctions. (FT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

When Employees Rationalize Misconduct: What CCOs Need to Change

A sales manager needs one more transaction to meet the quarterly target. The customer has not completed the required approvals, but the manager believes the paperwork will arrive tomorrow. Booking the sale today will protect the team’s bonus and keep the regional president satisfied. The manager tells herself that the transaction is real, the delay is administrative, and nobody will be harmed.

This hypothetical illustrates a problem every chief compliance officer should consider. An employee can understand a rule and still construct a convincing reason to disregard it. The compliance challenge includes recognizing the reasoning that makes a violation feel acceptable before the employee acts.

Todd Haugh examined that challenge in The Trouble With Corporate Compliance Programs, published in the Fall 2017 issue of MIT Sloan Management Review. Drawing on behavioral ethics and criminology, Haugh argued that compliance programs need to address how employees make ethical decisions and rationalize misconduct. His analysis laid the foundation for this discussion; the operational recommendations I adapted from his article apply that perspective to the CCO’s work.

Examine the Decision Behind the Violation

Compliance professionals devote substantial attention to policies, training, approvals, and investigations. Each has a role. Yet a completed training course tells us relatively little about how an employee will respond when a supervisor demands a result that appears impossible to achieve within the rules.

Haugh’s central contribution was treating rationalization as something that can precede misconduct and help enable it. (The same is true in the Fraud Triangle.) Drawing on criminological research, including Donald Cressey’s work, Haugh explained how people can make a breach of trust seem consistent with their view of themselves as good people.

For the CCO, this changes the inquiry. Alongside asking whether an employee knew the rule, ask what made bypassing it appear reasonable. Was the employee protecting a colleague? Responding to a threat of dismissal? Following a practice that managers had repeatedly accepted? Those questions can reveal weaknesses in supervision, incentives, escalation, and accountability. They also help explain why repeating the policy may leave the conditions behind a violation intact.

Recognize the Language of Rationalization

Haugh identified eight common rationalizations: denying responsibility, denying injury, denying the victim, condemning the condemners, appealing to higher loyalties, using a ledger metaphor, claiming entitlement, and claiming relative acceptability or normality.

Several relate directly to daily compliance work. An employee who says a supervisor left no choice may be denying responsibility. Someone who minimizes the consequences of an inaccurate record may be denying injury. A manager who defends a questionable payment as necessary to protect the business may be appealing to higher loyalties. An executive who invokes years of excellent performance to excuse a violation may be treating past contributions as credits against present misconduct.

The practical value of these categories lies in the questions they generate. When someone defends a practice as common across the industry, the CCO should explore how the company evaluates that practice and who has approved it. When loyalty to the business becomes the explanation, ask which business interest the conduct actually serves and what risks it creates.

Such statements warrant inquiry. They do not, by themselves, establish misconduct. A useful discussion must leave room for employees to describe pressure, uncertainty, and disagreement candidly.

Put Business Pressure Within the Compliance Review

Haugh discussed Wells Fargo’s sales practices as an example of how organizational pressure can overwhelm formal ethics messaging. In Haugh’s view, aggressive sales expectations helped create an environment in which employees could rationalize improper behavior despite instructions against it. The broader lesson for CCOs is to examine the operating conditions surrounding a control. A policy requiring approval has limited practical support if management consistently rewards employees who bypass the process to deliver faster results.

Consider a third-party onboarding process. The written procedure requires due diligence before engagement. The business promises the intermediary an immediate start date, procurement receives the request late, and the responsible employee is evaluated on speed. Compliance then encounters an urgent request for an exception.

The proposed response should reach beyond that individual exception. Who committed the company before review? Why did the planning process omit the approval period? Does management treat compliance review as part of the transaction schedule? Repeated urgency deserves examination as a management practice. The CCO should bring those findings to the business owner with a concrete correction, an accountable executive, and a timetable.

Practice the Conversation Employees Need to Have

Haugh recommended discussion and storytelling to help employees recognize rationalizations. This approach gives compliance training a useful operational purpose: rehearsing the conversation that must occur when commercial pressure and an ethical obligation collide. Use a scenario drawn from your organization’s actual work, with identifying details removed where necessary. Ask participants to explain the pressure, identify the affected parties, describe the proposed justification, and decide how they would respond. Then require a practical answer. Whom would the employee contact? Can the transaction pause? Who can authorize an alternative? What should the employee say to a manager who insists on proceeding?

Managers should participate because their response determines whether the proposed solution is credible. If the training encourages escalation but the supervisor treats questions as disloyalty, the employee receives conflicting instructions. The CCO can use these sessions to identify unclear responsibilities and impractical procedures. Training becomes a source of information about how work gets done, as well as an opportunity to explain expectations.

Connect Incentives and Accountability

Haugh also emphasized incentives and organizational culture. For compliance practitioners, the application is direct: examine the behaviors that receive recognition, promotion, and protection. A company may praise integrity while celebrating a commercial result without asking how it was achieved. A high performer may receive repeated exceptions unavailable to others. Employees can reasonably interpret those decisions as evidence of management’s priorities.

The CCO should work with human resources and business leadership to incorporate performance metrics into evaluations. Relevant evidence might include how a manager responds to concerns, handles approval requirements, and corrects recurring control failures. Recognition also has a role. With appropriate confidentiality, leadership can acknowledge a team that raised a concern early or found an acceptable way to complete a difficult transaction. The explanation should make it clear that the conduct is worth repeating.

Accountability must extend to supervisors whose instructions or tolerated practices contributed to a problem. Otherwise, remediation may remove an employee while preserving the management behavior that shaped the decision.

Give the Board Evidence About Behavior

Board reporting should help directors understand whether the program influences business decisions. Training completion and policy certifications provide useful coverage information. They need context from the company’s operating experience. A CCO might report recurring reasons for approval exceptions, examples of management responses to escalation, or repeated control failures concentrated within a business unit. Such information can help directors question whether performance expectations and compliance obligations are aligned.

Interpretation matters. More reported concerns could reflect greater trust in the reporting process. Fewer exceptions could reflect better planning or a failure to record deviations. Explain the evidence, its limitations, and the follow-up needed before presenting a conclusion about effectiveness.

Action Steps for the CCO

Haugh’s article challenged compliance leaders to take employee decision-making seriously. Turn that insight into a focused review:

  1. Review a sample of closed matters. Identify the justifications employees offered, the pressures they described, and management’s role. Look for recurring conditions across cases.
  2. Examine one business process. Select a process with frequent exceptions or urgent approvals. Determine where planning, incentives, or unclear authority encourage employees to bypass requirements.
  3. Run a manager-led scenario discussion. Practice recognizing rationalizations and responding to pressure. Record procedural gaps that prevent employees from taking the expected action.
  4. Assign corrective actions to business owners. Address the underlying workflow or management practice, with deadlines and evidence of completion.
  5. Report what changed. Show senior management and the board how the intervention affected decisions, exceptions, or recurring issues. Distinguish observed improvement from conclusions that still require evidence.

The CCO’s task is to make ethical conduct workable under the conditions employees actually face. That requires understanding the justifications for misconduct and changing the business practices that give those justifications force.

Categories
Sunday Book Review

Sunday Book Review: September 13, 2026, The New Books Leadership Edition

In the Sunday Book Review, I consider books that would interest the compliance professional, the business executive or anyone who might be curious. It could be books about business, compliance, history, leadership, current events or anything else that might interest me. In this episode, we look at 4 new books on leadership that have or will be released in the fall 2026.

  1. How Leaders Can Inspire Accountability by Michael Timms
  2. Begin with We by Kyle McDowell
  3. Leadership Intelligence by Caroline Webb
  4. Superteams by Ronald Friedman


My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County Texas which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival and resilience. It is available on the following sites:

 Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart


This week only, the e-book Kindle version is available for $0.99 on Amazon

Categories
Compliance and AI

Compliance and AI: Diego Panama on – AI-Driven GRC: The Next Enterprise Standard

What is the intersection of AI and compliance? What about machine learning? Are you using ChatGPT? These questions are just three of the many we will explore in this cutting-edge podcast series, Compliance and AI, hosted by Tom Fox, the award-winning Voice of Compliance. In this episode, host Tom Fox visits with Diego Panama, new CEO of LogicGate.

Panama brings a disciplined, business-focused perspective to the future of AI-driven GRC platform strategy and risk management transformation. He believes AI is turning GRC from a reactive, checkbox exercise into a strategic, board-level capability, where a holistic platform can unify third-party, cyber, supply chain, and enterprise risks in real time. Rather than leaving professionals buried in operational tasks, he sees agentic AI handling assessments, recommendations, and continuous monitoring so teams can focus on risk appetite, governance, and business outcomes. For Panama, the future of GRC is increasingly autonomous but still human-led, with strong data governance, clear priorities, and responsible use of emerging technology enabling faster, more precise, and more valuable risk management.

Key highlights:

  • Scaling Past 100 Customers with Customer-First GRC
  • AI Agents for Real-Time Global Risk Monitoring
  • Enterprise-wide access and intelligent data interaction
  • Conversational no-code UX with Config Newton agent
  • GRC as the Key to Safe AI Adoption

Resources:

LogicGate

Diego Panama on LinkedIn

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

Categories
AI Today in 5

AI Today in 5: September 11, 2026, The Compliance Must Evolve Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 stories about AI to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Getting AI right in wealth management. (FinTech Global)
  2. Could AI go ‘all Skynet’?. (WSJ)
  3. Auditing compliance AI. (BitSight)
  4. Legal considerations for AI rollout. (Foley Hoag)
  5. Why compliance must evolve. (Fast Company)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Everything Compliance

Everything Compliance: DEI Backlash, Executive Orders, and When “Tone at the Top” Needs Resources

Welcome to a revamped Everything Compliance. Host Adam Turteltaub and panelists Karen Moore, Matt Kelly, Rebecca Walker, and Jonathan Armstrong discuss compliance issues spanning DEI, executive orders, leadership support, and new EU sustainability rules.

  • Karen Moore reviews rapid corporate reversals on DEI and cites a Stanford/UC Berkeley study, “Markets Do Not Punish Firms for Maintaining DEI.”
  • Matt Kelly uses the “Lake Ontario to Lake America” renaming to argue executive orders aren’t laws binding companies and that choosing to comply reflects corporate values and policy-override decisions.
  • Rebecca Walker argues “tone at the top” is insufficient without resources and real trade-offs, citing NAVEX data on gaps between encouraging, modeling, and persisting in ethics under pressure.
  • Jonathan Armstrong outlines a new EU law limiting the destruction of unsold apparel and footwear, along with practical compliance steps.

The members of Everything Compliance are:

The award-winning Everything Compliance is a part of the Compliance Podcast Network.

Categories
Compliance Into the Weeds

Compliance into the Weeds: Clippers Salary-Cap Circumvention: Sham Endorsements, Contract Red Flags, and Compliance Lessons

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into compliance-related topics, literally going into the weeds to explore a subject in greater depth. Looking for hard-hitting compliance insights? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss the NBA’s sanctions against the Los Angeles Clippers for a salary-cap circumvention scheme tied to Kawhi Leonard.

In this delicious set of compliance imbroglios, senior management, including owner Steve Ballmer, allegedly arranged sham endorsement deals with four business partners and offsetting Clippers business to funnel about $18 million in extra compensation, plus improperly pay Leonard’s personal expenses. Tom and Matt review the Wachtell Lipton 36-page investigation detailing sparse contracts, unusual counterparties, rapid deal timing, and incriminating emails (including from Gillian Zucker), as well as recidivism after a similar 2019 violation. Penalties include a $30 million team fine, Leonard’s $700K fine, loss of first-round picks for five years, and suspensions for Ballmer, Zucker, and the basketball operations executive. Meanwhile, Ballmer denies wrongdoing and says the Clippers will file an appeal. They highlight contract-management and third-party due diligence lessons from FCPA-style guidance, the need to analyze patterns across multiple agreements, and the value of strong compliance roles in pro sports.

Key highlights:

  • NBA Scandal Overview
  • How The Scheme Worked and Why Salary Caps Matter
  • Sham Contracts = Red Flags
  • Paper Trail and Intent
  • Recidivism and Tone at the Top
  • Contract Patterns Lessons

Resources:

Matt in Radical Compliance

Tom in the FCPA Compliance and Ethics Blog

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds was most recently honored as one of the Top 25 Regulatory Compliance Podcasts, a Top 10 Business Law Podcast, and a Top 12 Risk Management Podcast. Compliance into the Weeds has received Davey, Communicator, and w3 Awards, all for podcast excellence.