Categories
Blog

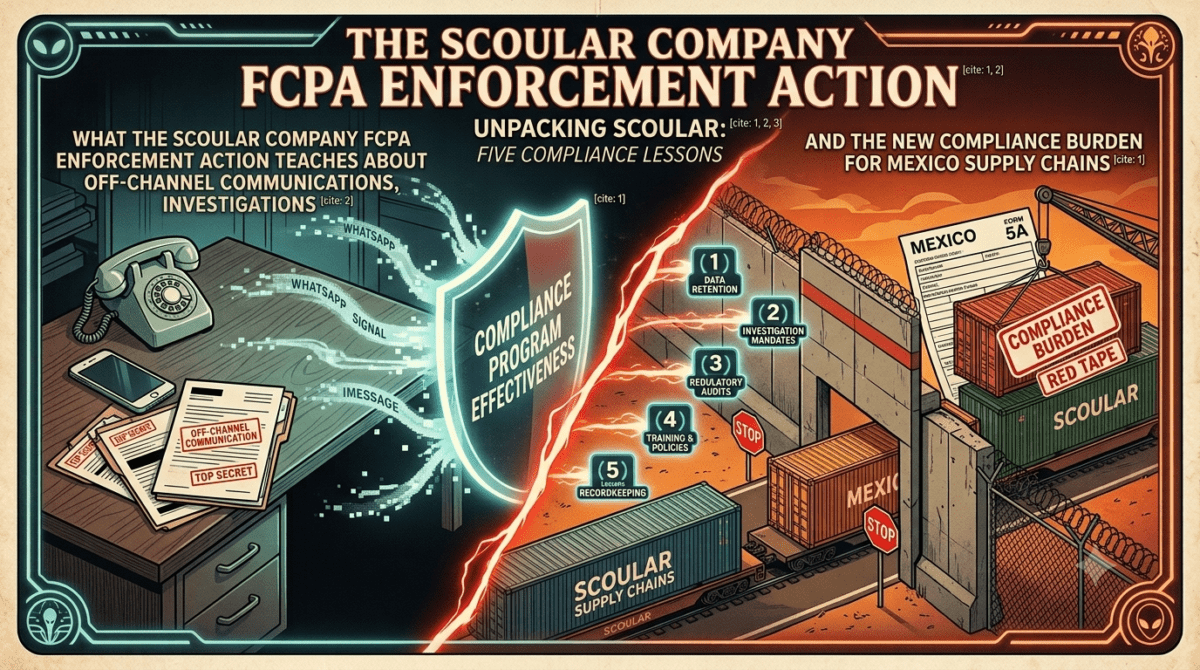
What Scoular Teaches About Off-Channel Communications, Investigations, and Compliance Program Effectiveness

WhatsApp was not a footnote in The Scoular Company FCPA resolution. It was part of the operating system of the alleged bribery scheme. According to the Department of Justice Press Release (we are still waiting on the DPA and Criminal Information), Scoular Company employees communicated about shipments and bribes through WhatsApp and other means. Today I want to explore the issue of off-channel communication and what it means for your compliance program.

The compliance lesson is not simply that Scoular Company employees used WhatsApp. It is that an informal communications channel became embedded in a high-risk business process involving customs officials, third-party brokers, payment approvals, and financial records. Once that happens, messaging governance is no longer an information technology issue. It is an anti-corruption control.

Off-Channel Became the Business Channel

The phrase “off-channel” can be misleading. If employees regularly use WhatsApp to authorize payments, direct third parties, and solve customs problems, the application is not outside the business. It is where the business is being conducted. That distinction matters.

A company may have excellent controls inside its enterprise resource planning system. It may require purchase orders, segregation of duties, invoice matching, and documented approvals. Those controls can be bypassed if the substantive decision is made in a private chat and the formal system merely records the result. At Scoular Company, the reinspection invoice was one side of the control failure. The WhatsApp discussion was the other one.

The invoice gave the payment a facially legitimate description. The messaging channel allegedly supplied the knowledge, direction, and authorization behind it. Compliance teams should test both sides together. A recurring round-dollar customs charge becomes more significant when matched to a message asking a broker to get a train released. A failed inspection becomes more significant when followed by an off-channel approval and immediate border clearance. Communications analytics and transaction analytics should not operate as separate disciplines.

Enforcement Priorities Can Change. Evidence Does Not.

In my podcast with Matteson Ellis, Member and Latin America Practice Lead at Miller & Chevalier, we addressed the shift in federal enforcement attention surrounding off-channel communications. Ellis made the more durable point: even when a regulator changes its emphasis, WhatsApp messages remain evidence of knowledge, intent, authorization, concealment, and circumvention of control.

Ellis observed that the DOJ press release suggests Scoular’s internal investigation obtained access to relevant WhatsApp communications. That access was important because retrieving such data can be difficult, particularly when employees use personal devices, local privacy law limits review, or messages have not been retained. His conclusion should command the attention of every CCO. The off-channel issue may have become quieter, but the Scoular resolution can be read as bringing it back to the center of corporate investigations. A prosecutor does not need a standalone recordkeeping case to use a WhatsApp message as proof of an FCPA violation.

The 2024 ECCP Provides the Road Map

The DOJ’s 2024 Evaluation of Corporate Compliance Programs (ECCP) does not demand a single technology solution. It asks whether the company’s approach is reasonable for its business needs and risk profile. That is the correct standard because messaging use varies by country, function, and commercial reality. The ECCP organizes the inquiry around three practical areas:

  • Communication channels. What electronic channels do employees actually use? How does use vary by jurisdiction and business function? What retention and deletion settings apply, and why did the company permit them?
  • Policy environment. Can the company preserve communications when devices are replaced? What do privacy, security, employment, and bring-your-own-device rules permit? Can the company review business messages on personal devices, and are employees required to transfer business records into company systems?
  • Risk management. Has the company ever exercised its access rights? What happens when an employee refuses access or violates the policy? Has messaging use impaired an investigation or the company’s response to prosecutors?

These are effectiveness questions. A written prohibition will not satisfy them if the business routinely ignores it, managers approve transactions in private chats, and the company cannot retrieve the records when misconduct surfaces.

A Defensible Program Starts With Commercial Reality

Ellis explained that an outright WhatsApp ban may not be practical in Latin America, where the application is widely used for business. A policy that conflicts with how employees, customers, and third parties actually work may drive communications further underground. The better approach is to define what may occur on the platform.

Ellis suggested limiting WhatsApp to logistical and administrative communications while keeping substantive commercial transactions and approvals inside controlled systems. That distinction is particularly important for customs payments, discounts, government interactions, third-party instructions, and exceptions to standard procedures.

A defensible framework should include the following controls:

  • Map actual use: Survey high-risk functions and jurisdictions to determine which applications, devices, disappearing-message settings, and informal groups employees use.
  • Classify communications: Separate low-risk logistics from approvals, commitments, payment decisions, government interactions, and other substantive business records.
  • Build technical access: Use company-managed devices or approved enterprise integrations where appropriate so business communications can be retained, searched, placed on legal hold, and produced.
  • Address local law: Analyze privacy, employment, consent, monitoring, and data-transfer requirements before an investigation begins. The access right must be lawful and operational.
  • Create preservation protocols: Define what occurs when an employee changes devices, leaves the company, becomes subject to a legal hold, or refuses access to business communications.
  • Enforce the rules: Test compliance, investigate violations, apply consequences consistently, and examine whether supervisors tolerated or encouraged off-channel approvals.

Investigations Must Be Ready Before the Message Disappears

Off-channel governance is tested in the first hours of an investigation. The company must identify relevant custodians, devices, applications, group chats, backup settings, linked desktops, and cloud accounts. It must issue a preservation notice that employees understand and implement. It must also determine whether consent, works council consultation, or another local-law step is required before collecting data.

The investigative team should not examine messaging data in isolation. It should connect communications to:

  • Accounts-payable records
  • Customs broker invoices
  • Inspection results
  • Shipment identifiers
  • Clearance times
  • Approval logs
  • Bank data

This is where Scoular Company FCPA enforcement action becomes a model for a broader control lesson. The message can explain the invoice, and the invoice can corroborate the message. Ellis emphasized the value of having protocols ready before access is needed. That is critical. Negotiating employee consent, locating backups, and determining ownership of a device after a subpoena or whistleblower allegation arrives is not a defensible strategy. It is a delay, and delay can destroy evidence and cooperation.

Boards Should Treat Messaging as a Governance Risk

Boards do not need to select the retention platform or approve device settings. They do need assurance that management understands how high-risk business is actually conducted and can preserve the evidence required to investigate misconduct. The board should receive more than confirmation that a policy exists. It should receive information on:

  • Policy exceptions
  • Control testing
  • Employee violations
  • Disciplinary outcomes
  • Collection failures
  • Investigation delays
  • High-risk jurisdictions and functions

For companies operating across the U.S.-Mexico border, customs, logistics, sales, procurement, and government-facing teams deserve particular attention. This is an oversight issue. If management cannot retrieve communications involving payments to government-facing third parties, the company may be unable to determine what occurred, identify responsible individuals, remediate the control failure, or cooperate effectively with prosecutors.

Questions for CCOs

  1. Which messaging platforms do employees and third parties actually use in our highest-risk markets?
  2. Can an employee approve a customs payment, direct a broker, or authorize an exception through WhatsApp?
  3. Can we lawfully and promptly preserve and retrieve business messages from company and personal devices?
  4. Have we tested those capabilities through a mock investigation or legal hold?
  5. Do transaction-monitoring reviews incorporate relevant messaging evidence when an anomaly is escalated?
  6. Have we disciplined employees and supervisors for circumventing approved channels?

The Bottom Line

Scoular Company did not become an off-channel communications case because employees happened to use WhatsApp. WhatsApp mattered because employees allegedly used it to facilitate and discuss a bribery scheme that operated through customs brokers and disguised invoices for six years. That is the compliance lesson. The channel, the payment, the third party, and the business outcome must be viewed as one control environment.

Companies should not ask whether WhatsApp is good or bad. They should ask whether the communications occurring there are permitted, preserved, accessible, monitored on a risk basis, and connected to the company’s formal approval and financial systems. If the company cannot answer those questions, its most important business records may be sitting on the device it controls least.
Categories
Blog

The Odyssey and Compliance, Part 5 – Peace in Ithaca: Building the Program After the Crisis

Today, we conclude our five-part series on some of the intersections of. On Monday, we began with the Trojan Horse as a control failure. On Tuesday, we looked at The Lotus-Eaters: Culture Drift and the Comfort of Forgetting. On Wednesday, Circe’s Island: Third-Party Influence and Culture Capture. On Thursday, we reviewed The Cattle of Helios, Non-Negotiables, and Control Breaches. Today, we conclude with Odysseus making his way home to Ithaca and to his wife, Penelope, and their son, Telemachus, in the tale of Peace in Ithaca: Building the Program After the Crisis.

Odysseus finally makes it home. After ten years of war and ten more years of wandering, he returns to Ithaca, confronts the suitors, reclaims his house, and restores his position. The bow is strung. The suitors are defeated. The great crisis is over. Roll credits, cue heroic music, and let everyone go back to normal. Except, of course, that is not how governance works.

The story does not really end when Odysseus wins. Ithaca still has to be governed. The household has to be restored. Trust has to be rebuilt. Loyalties have to be sorted out. The damage done by years of disorder has to be addressed. Penelope, Telemachus, the servants, the suitors’ families, and the broader community all have to live with what comes next.

That is the overlooked compliance lesson at the end of The Odyssey: winning the confrontation is not the same as rebuilding the system. For corporate compliance, Ithaca is the company after an enforcement action, a scandal, a cyber breach, a restatement, a leadership crisis, a whistleblower investigation, a failed audit, or a major control breakdown. The dramatic event may be over. The press release may be issued. The investigation may be closed. The bad actors may be gone. But the real question remains: what changes must be made so that the same story does not happen again?

The Corporate Translation

Every organization wants to believe that removing the wrongdoer solves the problem. Terminate the employee. Discipline the manager. Replace the vendor. Restate the numbers. Settle the matter. Announce new leadership. Launch a refreshed values campaign. Hold a town hall. Add a slide to the annual training deck. All of those may be necessary.

None of them is sufficient. A crisis reveals more than individual misconduct. It reveals how the organization enabled the misconduct, overlooked it, tolerated it, rationalized it, or failed to respond sooner. It exposes weaknesses in governance, incentives, supervision, reporting, monitoring, controls, culture, and accountability.

That is why post-crisis remediation cannot be treated as corporate housekeeping. It is not the ceremonial sweeping of the hall after the suitors have been removed. It is the hard work of rebuilding Ithaca so the suitors do not return wearing different badges. The corporate lesson is simple: winning the investigation is not the same as rebuilding trust.

“Works in Practice” Is the Hard Question

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks three core questions: whether the program is well designed, whether it is adequately resourced and empowered to function effectively, and whether it works in practice. The ECCP makes clear that prosecutors consider how a company’s program performed at the time of misconduct and at the time of a charging decision or resolution.

That third question—does it work in practice? —is the Ithaca question. It is one thing to have a Code of Conduct. It is another thing to know whether employees believe it. It is one thing to have a hotline. It is another thing to know whether people trust it. It is one thing to discipline misconduct. It is another matter to know whether discipline is consistent across ranks, geographies, and revenue contributions.

A compliance program does not work because it is beautifully documented. A compliance program works when it changes decisions, identifies risks, encourages escalation, supports ethical behavior, and improves when reality proves that the initial design was not enough. Odysseus could reclaim the palace in a day. Rebuilding confidence in the palace would take longer. So it is with compliance.

Remediation Is Not a Memo

One of the great corporate temptations after a crisis is to confuse activity with remediation. There will be committees. There will be project plans. There will be executive updates. There will be dashboards in shades of green, yellow, and red. There will be a new policy with a title long enough to require its own table of contents. But the question is not whether the company became busier. The question is whether the company has become better.

Effective remediation begins with root cause analysis. What happened? Why did it happen? Who was involved? Who should have known? Which controls failed? Which controls did not exist? Were employees trained? Were managers supervising? Were incentives distorting behavior? Were prior warnings ignored? Were similar issues found elsewhere?

Then, remediation must move from diagnosis to design. Policies may need to change. Controls may need to be strengthened. Reporting channels may need to be rebuilt. Training may need to be targeted. Third-party relationships may need review. Compensation systems may need adjustment. Governance committees may need clearer authority. Data analytics may need to identify patterns earlier.

And then comes the part companies sometimes skip: testing and ongoing monitoring. A control is not considered remediated just because someone wrote that it was. A control is remediated when it has been implemented, tested, validated, and shown to work. Otherwise, Ithaca has merely repainted the door.

Monitoring and Testing: Trust, but Verify Ithaca

After a crisis, leadership often wants to move on. That impulse is understandable. No one wants to live forever in the investigation report. Employees are tired. Managers are defensive. The board wants assurance. Customers want stability. Regulators want evidence. The business wants to get back to business. But moving on too quickly is how organizations repeat themselves.

Monitoring and testing are the tools that keep memory alive without keeping the organization trapped in the past. Monitoring asks, “What are we seeing now? Testing asks, “Do the controls actually work?” Together, they turn compliance from a promise into evidence.

This is where ISO 37301 offers a useful management-system lens. ISO describes ISO 37301 as a compliance management systems standard for establishing, developing, implementing, evaluating, maintaining, and improving an effective and responsive compliance management system. That language matters because it treats compliance as a cycle, not a shrine. Establish. Implement. Evaluate. Maintain. Improve.

Culture Reset Requires More Than New Words

After misconduct, companies often rediscover culture with the enthusiasm of a traveler who has just realized the map was upside down. Suddenly, everyone wants to talk about values. Tone at the top. Speak-up culture. Accountability. Transparency. Trust.

But a culture reset requires more than new words from senior leadership. Employees are sophisticated consumers of corporate messaging. They know when a town hall is sincere and when it is theater. They know whether leaders who caused the pressure are still being rewarded. They know whether people who raised concerns were protected or isolated. They know whether the company wants the truth or merely closure.

A real culture reset asks hard questions. Are managers rewarded for ethical leadership? Are employees comfortable escalating concerns? Are investigations fair and timely? Are lessons learned communicated without unnecessary secrecy? Are senior leaders held accountable? Are compliance and audit findings taken seriously? Are business goals achievable without cutting corners? Culture is not reset by announcing that trust has been restored. Trust is restored when employees see different behavior over time.

Governance After the Storm

Ithaca’s problem was not only that the suitors behaved badly. It was the governance structure that allowed them to occupy the house for too long. That is a corporate issue as well.

After a crisis, boards and executive teams should examine whether governance failed. Did the right committees receive the right information? Did compliance have sufficient independence? Were risk owners clearly identified? Did internal audit, legal, HR, finance, security, and compliance coordinate effectively? Were red flags escalated? Did leadership understand the risk, or were they receiving sanitized reporting?

Governance redesign is not glamorous. It lacks the narrative thrill of Odysseus stringing the bow. But it is what prevents the next group of suitors from discovering that no one is really watching the door.

The Compliance Takeaway

The end of The Odyssey is not just about return. It is about restoration. That distinction matters for compliance officers and business leaders. After a crisis, the organization must resist the urge to declare victory too soon. The investigation may identify what happened. Discipline may address who was responsible. But remediation must answer the deeper question: what will be different? A mature compliance program uses a crisis as evidence. It monitors. It tests. It learns. It redesigns governance. It strengthens controls. It resets culture through action. It measures whether the program works in practice, not merely whether it exists on paper.

Odysseus came home and won back Ithaca. The compliance challenge is harder. You have to make Ithaca governable again.

Categories
Blog

The Odyssey and Compliance, Part 3 – Circe’s Island: Third-Party Influence and Culture Capture

We continue our series of compliance lessons from The Odyssey. Today, we consider the tale of Circe’s Island and how third parties can not simply influence but also capture organizations.

Odysseus had seen danger before. He had survived war, storms, and the occasional poor travel decision that would have caused any modern risk committee to request an immediate meeting. But then he came to Circe’s island, where the threat did not begin with open violence. It began with hospitality. Circe welcomed Odysseus’s men. She offered food. She offered a drink. She offered comfort. Then, in one of the more memorable compliance-adjacent transformations in Greek mythology, she turned them into swine.

Subtle? Not especially. Useful for corporate compliance? Absolutely. In the corporate world, third parties rarely transform employees into literal pigs. That would at least make the investigation easier. The modern version is quieter. A consultant becomes indispensable. A reseller knows “how things work here.” A lobbyist explains that the official process is for amateurs. A distributor normalizes side payments. A strategic partner begins to shape internal decisions. A vendor’s gifts, favors, travel, and access slowly change what employees consider acceptable.

No one wakes up and says, “Today I shall surrender my professional judgment.” Instead, judgment softens and then stretches. Then outsourced. That is Circe’s island.

The Corporate Translation

Circe is the consultant, agent, lobbyist, reseller, distributor, broker, introducer, or strategic partner who makes questionable conduct feel sophisticated. She does not have to say, “Break the rules.” That would be too obvious. She says something more dangerous:

“This is how business is done.”

“Everyone uses this structure.”

“You are being too rigid.”

“The policy was not written for this situation.”

“You can trust me.”

“We have relationships you do not have.”

That is the language of culture capture. The third party does not merely provide a service. The third party begins to influence the organization’s standards. This is why third-party risk is not just a procurement issue. It is not just an anti-bribery issue. It is not just a contracting issue. It is a cultural issue. The most dangerous third parties do not always demand a bribe. Sometimes they simply change what your people think is normal.

The Paperwork Trap

Most companies have a third-party process. There is a questionnaire. There is a risk rating. There is a certification. There is a contract clause. Somewhere, there may even be a spreadsheet with conditional formatting, because nothing says “control environment” like a cell turning amber. These tools matter. But paperwork alone does not manage influence.

A company can collect every form and still miss the real risk. Whom is this third party influencing? Who inside the company is advocating for them? Why are they needed? What access do they have? What discretion do they exercise? Are they interacting with government officials, customers, healthcare professionals, regulators, state-owned entities, procurement teams, or other sensitive stakeholders? Are they being paid in a way that makes sense? Are they actually doing the work? Are they unusually close to the decision-maker?

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks whether companies apply risk-based due diligence to third-party relationships and understand the qualifications, associations, business rationale, reputation, compensation, and actual services performed by third parties. It also asks whether companies engage in ongoing monitoring through refreshed due diligence, training, audits, or certifications.

That is the point. Third-party compliance is not a one-time onboarding ritual. It is a relationship management discipline. Circe’s danger was not that she existed. The danger was that Odysseus’s men entered her house without understanding the risk.

Gifts, Hospitality, and the Slow Erosion of Judgment

Gifts and hospitality are often discussed as if the only question is whether the amount is above or below a policy threshold. That is too narrow. A meal may be permissible and still influential. A conference invitation may be properly approved and still create pressure. A vendor-sponsored trip may be documented and still tilt the relationship. A series of small favors may do more damage to independence than one obviously improper gift.

Compliance officers understand this. Business leaders sometimes resist it because influence is uncomfortable to discuss. No one wants to admit that lunch, access, flattery, or convenience can affect judgment. We prefer to believe we are all rational actors, floating above human weakness like minor gods with expense reports. We are not.

Behavioral ethics teaches a humbler lesson: people are influenced by relationships, reciprocity, loyalty, fatigue, social norms, and self-interest. A third party who becomes a friend, fixer, sponsor, or “trusted guide” can reshape decisions without issuing a single improper instruction.

That is why gifts-and-hospitality controls should look beyond monetary value. They should examine frequency, timing, recipient role, pending decisions, public-sector touchpoints, tender activity, regulatory matters, and cumulative patterns. The better question is not only, “Was this gift allowed? “The better question is, “What might this gift be trying to make feel normal? ”

Conflicts of Interest: Circe with a Business Card

Conflicts of interest are another form of enchantment. The employee recommends a vendor owned by a family member. A manager hires a consultant whom he previously employed. A procurement lead has a side investment in a supplier. A sales executive pushes a reseller because the reseller has promised future employment. A board member has ties to a strategic partner.

Often, the conflicted person does not experience the conflict as corruption. They experience it as trust.

“I know them.”

“They are good people.”

“They understand our business.”

“This will move faster.”

That may all be true. It may also be irrelevant. Conflicts do not require proof that someone acted dishonestly. A conflict means that personal interest may interfere with, or appear to interfere with, professional judgment. In compliance, appearance matters because trust matters. Circe did not need to tell the crew they were compromised. They simply became something other than what they had been. That is what unmanaged conflicts do. They transform decision-makers into advocates for interests they may not even fully recognize.

Risk-Based Due Diligence Means Asking Better Questions

A strong third-party program should be risk-based. That does not mean treating every vendor like a potential international crime syndicate. It means applying the right level of scrutiny to the right relationship. The office coffee supplier probably does not need the same review as a customs broker, government-facing consultant, high-commission sales agent, data processor, clinical partner, reseller, lobbyist, or distributor in a high-risk market.

Risk-based due diligence should ask direct questions:

What will this third party do for us?

Why do we need them?

Who selected them?

What relationships do they bring?

How will they be paid?

What access will they receive?

What decisions can they influence?

What laws, regulations, or policy areas do they touch?

What red flags appeared, and how were they resolved?

The ECCP also emphasizes risk assessment across factors such as business partners, third-party use, gifts, travel, entertainment, and other areas that may contribute to the risk of misconduct. That is a useful reminder: third-party risk rarely travels alone. It often brings friends. Gifts risk. Conflicts are risky. Books-and-records risk. Data risk. Sanctions risk. Cyber risk. Antitrust risk. Fraud risk. Reputational risk. Circe’s island is crowded.

Training the People Who Meet Circe

Third-party policies are necessary, but people need training before they sit across the table from Circe. Sales teams need to understand the red flags for resellers and agents. Procurement teams need to spot conflicts and unusual payment terms. Finance needs to recognize vague invoices, round-dollar payments, split payments, and services that cannot be verified. Legal needs to ensure that contracts describe real services and include rights to audit, termination, compliance, and cooperation. Business sponsors need to understand that “I trust them” is not due diligence.

The ECCP asks whether training and communications are tailored to the audience and whether companies provide practical guidance, case studies, and ways for employees to get ethics advice as issues arise. It also contemplates training for appropriate agents and business partners. That is exactly right.

Do not train employees only on the policy. Train them in the moment. The moment when the consultant says the invoice needs to be vague. The moment when the distributor asks for payment to an offshore account. The moment when the lobbyist says no one can know about the meeting. The moment when the vendor offers to fly the team to a “strategy session” at a resort, suspiciously light on strategy. The moment when the business sponsor says, “Compliance is slowing this down.” That is where the program either works or becomes decorative.

What a Better Program Does

A better third-party program examines influence, not just paperwork. It connects due diligence, contracting, training, payment controls, gifts and hospitality, conflict disclosures, monitoring, audits, and termination rights. It reviews third-party activity after onboarding. It checks whether services were actually performed. It compares compensation to market value. It looks for unusual payment structures. It refreshes diligence when risk changes. It trains business sponsors, not just compliance staff. It monitors the internal champions who may become too close to the third party they manage.

Most importantly, it permits employees to be skeptical. Not cynical. Skeptical. There is a difference. Cynicism says everyone is corrupt. Skepticism says facts, controls, and accountability should support trust. Odysseus survived Circe because he received a warning, protection, and guidance before walking into the risk. Your employees need the same, preferably without needing Hermes to appear with magical herbs.

The Compliance Takeaway

Circe’s island is not just a story about transformation. It is a story about influence. Third parties can help companies grow, enter new markets, solve complex problems, and operate more effectively. Many are essential. Many are ethical. Many know things the company genuinely needs to know. But a third party should never become a substitute for the company’s judgment. When a consultant, agent, reseller, lobbyist, vendor, or strategic partner begins to redefine what is acceptable, the company has moved from third-party management to third-party capture.

That is the lesson for compliance officers and business leaders. Do not ask only whether the forms are complete. Ask whether the relationship is changing behavior. Ask whether gifts, conflicts, access, dependence, or pressure are making questionable conduct feel normal. Ask whether employees still know where the company’s standards end and Circe’s influence begins. Because in business, as in mythology, transformation rarely announces itself. One day, your people are professionals exercising independent judgment. The next day, they are defending the island.

Join us on Thursday for Post 4, where we consider The Cattle of Helios: Non-Negotiables and Control Breaches.

Categories
Blog

The Bosch Declineation, Part 5: Warnings in an Insufficient Compliance System

This final post in the Bosch series should not end with a victory lap about the DOJ Declination. That would be the wrong lesson. Bosch earned real credit for what it did after discovery: it disclosed, cooperated, remediated, added 66 trade compliance employees, expanded U.S. trade compliance resources, and resolved the matter with DOJ and BIS. Those are serious steps, and compliance professionals should not dismiss them.

But the Declination should not be mistaken for vindication. Bosch avoided prosecution because of what it did after the failure, not because the compliance program worked before the failure. The uncomfortable lesson is that Bosch apparently had to suffer an enforcement crisis, a $36 million BIS penalty, disgorgement, and a very public Order (and reputational hit) before it fully resourced and restructured the function. That is a very expensive way to find religion.

The core thesis of this series is that Bosch is the rare enforcement action that rewards post-discovery conduct while simultaneously exposing a pre-discovery compliance program that was under-resourced, under-expertized, and too willing to treat red flags as paperwork. Bosch did not lack all compliance infrastructure. That is what makes the case more troubling. It had processes. It had trade compliance personnel. It had internal blocks. It had external warnings. It had business personnel receiving certifications. It had opportunities to stop, ask, escalate, and reassess. Yet the wrong answer became institutional truth.

The failure was not one bad legal interpretation

Every compliance failure has a beginning. In Bosch, the initial guidance was erroneous regarding the impact of the August 2020 rule change on sales to Huawei. But that was not the whole failure. Bad advice happens. Complex regulations are difficult. People make mistakes. A mature compliance program is not measured by whether it never produces the wrong answer. It is measured by whether it can identify, challenge, correct, and contain the wrong answer before it metastasizes into operating policy. Bosch failed that test.

The BIS Order said Bosch had established export compliance processes, including U.S. export compliance processes, but its U.S. export compliance team lacked sufficient expertise and resources to address the August 2020 changes. During much of the relevant period, Bosch’s U.S. export controls team primarily consisted of two employees, only one of whom was primarily tasked with U.S. export controls advice.

That is not a rounding error. That is a resource model visibly misaligned with the risk profile of a global technology and manufacturing company with hundreds of thousands of employees, hundreds of subsidiaries, complex supply chains, and high-risk customers. Compliance professionals should say this plainly: you cannot run mission-critical regulatory risk on heroic undercapacity and then be surprised when the system breaks.

Expertise matters, and generic compliance experience is not enough

One of the sharper lessons from Bosch is that “having compliance people” is not the same thing as having the right compliance expertise. The Evaluation of Corporate Compliance Programs (ECCP) asks whether compliance personnel have the appropriate experience and qualifications for their roles, whether those qualifications have changed over time, how the company invests in further training, and who reviews the performance of the compliance function. Bosch’s facts read like an answer key in reverse.

The relevant compliance personnel misunderstood the rule, conflated separate concepts, and repeatedly relied on a flawed conclusion. That misunderstanding then became the basis for releasing orders and continuing sales. The issue was not merely a knowledge gap. It was an expertise governance failure: no second-level review, no effective challenge process, no documented reassessment trigger, and no apparent mechanism to say, “This conclusion is too consequential to rest on a thin and possibly confused analysis.”

For CCOs, the hard question is not whether your compliance team is busy. Everyone’s team is busy. The question is whether your team has the technical depth to manage the risks your business actually creates. If the answer is no, the next question is why the business is permitted to keep operating as if the answer were yes.

The company had warnings and treated them as noise

The most damning part of the Bosch story is not the original mistake. It is the persistence of the mistake after multiple warning signs. Company Four warned Bosch that equipment used in its factories included U.S.-export-controlled items and that products worked on by Company Four for Huawei might be prohibited from export. Company One asked Bosch personnel to sign a certification that should have forced reconciliation with Bosch’s prior guidance. Company Five told Bosch that products containing items manufactured by Company Five could not be provided to Huawei without authorization and even referenced the Seagate penalty. Contract manufacturer certifications repeated the same basic warning: these were not ordinary commercial forms; they were control documents.

This is where COSO Principle 15 becomes useful. Principle 15 is not only about what the company communicates outward to third parties. It also recognizes that third parties can provide information back to management about the effectiveness of internal controls and regulatory communications.

Bosch failed to treat third-party communications as control information. That is a blunt but fair reading. Supplier warnings were received. Certifications were signed. Objections were routed. But the organization lacked a system to convert that information into escalation, reconsideration, documentation, and action. That should bother every CCO. The problem was not that the information was hidden. The problem was that it was visible, yet it still did not matter enough.

Business pressure became a control weakness

The Bosch Order also shows how business pressure can quietly become a compliance override. When the U.S. trade compliance professional requested information from Bosch businesses, BST did not provide it. The response cited a “dire allocation situation” and the need to spare the team time. The order says that had BST answered the specific questions, Bosch’s U.S. trade compliance personnel likely would have identified the issue. That fact should stop compliance professionals cold.

A compliance information request tied to a major regulatory change should not be optional. It should not be negotiable because the business is under pressure. It should not depend on whether a senior business leader believes the issue was already “clarified.” The moment commercial urgency is allowed to excuse incomplete compliance fact-gathering, the control environment has already bent.

The hard question for CCOs is simple: when compliance asks for information necessary to assess legal risk, can the business say no? If the answer is yes, the company lacks an authorized compliance program, once again violating not only the tenets of a best-practice compliance program but also those of the ECCP. It has a request-and-hope function.

Remediation was real, but late

Bosch deserves credit for remediation. Adding 66 trade compliance employees is not a cosmetic move. Expanding U.S. trade compliance resources is meaningful. Updating policies and procedures to clarify U.S. export control jurisdiction and licensing requirements is exactly the kind of tangible remediation DOJ and BIS expect.

But compliance professionals should not miss the obvious: those resources came after the failure. The better compliance question is why those resources were not there before. Why did it take a public enforcement action to reveal that the compliance function was not staffed or expert for the company’s risk profile? Boards and senior executives often ask whether compliance needs more people. Bosch suggests a sharper question: what will it cost if we wait until the government answers that question for us?

Hard questions for compliance professionals

The Bosch series leaves CCOs with hard questions.

Who owns complex regulatory change from interpretation through operational implementation?

Who validates high-risk legal or compliance advice before the business relies on it?

Does high-risk advice have a lifecycle, including assumptions, facts reviewed, date issued, owner, and reassessment triggers?

Can compliance force a business unit to respond to fact-gathering requests before shipments can continue?

Are supplier letters, certifications, refusals, and regulatory objections tracked as compliance intelligence?

Are procurement, logistics, supply chain, legal, production, and contract management trained to recognize red flags in third-party communications?

Who reviews whether compliance has sufficient expertise, not just sufficient headcount?

Can the compliance function stop, hold, or escalate transactions when the facts are incomplete?

Does the internal audit test whether compliance blocks are released for sound reasons, or merely whether they were processed?

When a supplier tells the company, “You may have a compliance problem,” does the company investigate the warning or look for another supplier?

Those are not academic questions. Bosch shows what happens when the answers are weak.

The final word

Bosch is not a story about a company with no compliance program. It is more troubling than that. It is a story about a company with a compliance infrastructure that still failed when the business needed judgment, expertise, escalation, and courage.

The final lesson is systemic. Bosch’s failure was not one bad legal interpretation. It was a systemic breakdown: a wrong answer became institutional truth because no one had the expertise, authority, process, or discipline to challenge it.

That is the compliance lesson worth remembering. Not the declination. Not the headline penalty. Not even the technical export control issue. The real lesson is that compliance programs fail when they cannot recognize and act on the information already in front of them. Bosch had the warnings. It did not have a compliance system.

Categories
Blog

The Bosch Delineation: Part 3 – Bosch and the ECCP: When Compliance Expertise and Resources Fail

As most readers know, sometimes when I get going on a multipart blog series, I either get carried away or simply cannot stop. Maybe sometimes it is both. This week is beginning to seem like one of those times. Today, I recorded an episode of Compliance into the Weeds with my co-host Matt Kelly, and we discussed some very interesting points from the enforcement action that I decided to keep going. (The episode will post on Wednesday, June 24.)

Over the past couple of blog posts, I have reviewed the DOJ Declination through the lens of the National Security Division. Today, I want to look at the BIS enforcement action and mine it for a different set of lessons learned.

The BIS enforcement is a useful case study for compliance professionals because it is not merely a story about a company without a compliance program. Rather, Bosch had export compliance processes, including U.S. export compliance processes. The failure was more subtle and more important: the compliance function lacked sufficient expertise and staffing to interpret a major regulatory change, translate that change into operational requirements, challenge incomplete business responses, and revisit advice when contrary facts emerged. BIS charged Bosch with 109 violations involving approximately $72.4 million in exports to Huawei without required authorization.

That is precisely the kind of failure the DOJ’s Evaluation of Corporate Compliance Programs (ECCP) is designed to test. Under ECCP Section II, prosecutors ask whether the compliance program is “adequately resourced and empowered to function effectively.” Section II.B, “Autonomy and Resources,” directs prosecutors to examine whether compliance personnel have sufficient qualifications, seniority, and stature; sufficient resources, including staff to audit, document, and analyze; and sufficient autonomy from management, including access to the board or audit committee.

As laid out in the BIS enforcement action, Bosch failed in the Expertise requirement. The enforcement action stated:

Bosch’s U.S. export compliance team did not have sufficient expertise or resources at the time to adequately address the August 2020 changes to the EAR, namely, the FOP Rule, which expanded restrictions on Huawei. Bosch’s failure to have an effective U.S. export controls compliance program in place for BST and ETAS at this time contributed directly to the violations at issue in these charges.

Bosch also failed in the Resources requirement. Here, the enforcement action stated:

During most of the relevant period, Bosch’s export controls compliance team in the United States consisted primarily of two employees. These employees were responsible for advising Bosch’s central trade compliance function, based in Germany, and Bosch’s non-U.S. businesses on compliance with U.S. export control regulations. Only one of these employees was tasked primarily with advising on compliance with U.S. export controls. The second employee provided part-time assistance with U.S. export controls compliance while also focusing on U.S. customs and tariffs compliance. The U.S. trade compliance team included other employees primarily focused on U.S. customs and tariffs, who could occasionally assist with minor, discrete export controls questions.

1. Did compliance personnel have the right experience and qualifications?

The ECCP asks whether compliance and control personnel have the appropriate experience and qualifications for their roles and responsibilities. That question sits at the center of the Bosch enforcement action.

During much of the relevant period, Bosch’s U.S. export controls compliance team primarily consisted of two employees. Only one was tasked primarily with advising on U.S. export controls; the second provided part-time export controls assistance while also focusing on customs and tariffs. Other U.S. trade compliance personnel were primarily customs and tariffs employees who could occasionally assist with minor export controls questions.

That staffing model proved inadequate for the risk. BIS found that Bosch’s U.S. export compliance team lacked sufficient expertise or resources to address the August 2020 changes to the EAR, and that this failure directly contributed to the violations. Communications between U.S. and German trade compliance personnel showed confusion about the Foreign Direct Product Rule (FDPR). That confusion produced erroneous guidance: a Germany-based trade compliance employee advised BST (a Bosch German entity) management that if products contained less than 25% U.S. content and the U.S. content was not classified under certain ECCNs, there was no impact and no license requirement. BIS explained that this advice improperly confused and conflated the De Minimis Rule with the FDPR.

For compliance professionals, the lesson is direct. Experience and qualifications cannot be evaluated generically. “Trade compliance experience” is not the same as deep expertise in a specific high-risk, fast-changing legal regime. A compliance team may be experienced enough for ordinary classification, screening, and documentation work, but underqualified for a complex regulatory change affecting a major restricted customer, foreign production, production equipment, software, suppliers, and end-user certifications.

The same issue appeared in Bosch’s German subsidiaries, collectively known as ETAS, in the enforcement action. Bosch trade compliance personnel reviewed automotive software sales to Huawei but incorrectly concluded that the FDPR applied only to physical goods, not software. BIS said Bosch personnel repeatedly advised ETAS that the restrictions did not apply to CycurHSM software.

The broader point is that qualifications must match the company’s risk profile. For a global technology company operating across complex supply chains, compliance expertise must be technical, up to date, and operationally fluent.

2. Did the level of experience and qualifications change over time?

The ECCP also asks whether the level of experience and qualifications in compliance and control roles changed over time. Bosch is a warning about static capability in a dynamic risk environment.

After the original August 2020 advice, Bosch received repeated warnings that should have triggered reassessment. Company Four warned BST that equipment used in its factories included U.S. export-controlled equipment and that products worked on by Company Four for Huawei could be prohibited under the EAR. BST did not analyze whether that warning conflicted with Bosch’s internal understanding.

A Bosch trade compliance professional in the United States also sent a September 4, 2020, request for information to Bosch businesses, including BST. The request sought detailed information about production lines, production equipment, and U.S.-origin software and technology used in production. BST did not answer the specific questions. The BST Executive responded that the products had already been “clarified” as not impacted and cited a “dire allocation situation.” BIS found that, had BST answered the questions, Bosch’s U.S. trade compliance personnel likely would have identified the sensors as within the FDPR’s product scope.

The failure was not merely the first wrong answer. It was the absence of a mechanism to upgrade expertise, revisit assumptions, and escalate conflicting information. A mature compliance program treats major legal change as a trigger for a surge of resources, specialist review, and documented reassessment. It also treats repeated inconsistent data points as evidence that the original advice may no longer be reliable.

3. How did the company invest in training and development?

The ECCP asks how the company invests in further training and development of compliance and control personnel. Bosch shows that training cannot be limited to compliance staff alone.

Between 2021 and 2024, BST employees signed multiple compliance certifications for semiconductor manufacturers under contract. Those certifications stated that items produced by the manufacturers were subject to the EAR and required BST to certify that it would not provide such items to an entity with a footnote 1 designation. The relevant employees later explained that they signed because they did not understand that Huawei was a covered entity.

That is a gatekeeper training failure. Procurement, logistics, production, contract management, and customer-response personnel were all part of the control environment. They received supplier certifications, customer requests, internal guidance, and external warnings. Yet the process did not ensure they understood what those documents meant or when they had to escalate.

The lesson is practical: high-risk certifications should not be treated as administrative paperwork. They are control documents. Employees who sign them need tailored, role-based training. They should understand restricted-party designations, escalation triggers, the consequences of inaccurate certifications, and the limits of relying on old guidance.

Compliance personnel also need continuing education. Where regulations are complex and fast-moving, development should include external specialist support, second-level review of high-risk advice, lessons learned from enforcement actions, and technical briefings with engineering and supply chain personnel. Obviously, the regulations changed in 2020, but it appears Bosch trade compliance professionals received training on this change.

4. Who reviewed the performance of the compliance function?

The ECCP’s final question asks who reviews the performance of the compliance function and what the review process is. Bosch illustrates why that review must go beyond activity metrics.

BIS found that Bosch’s internal controls were insufficient to ensure that compliance advice was broadly distributed, independently reviewed, or reassessed to confirm that it was correct or updated for new facts. Bosch also implemented internal blocks on Huawei orders, but German trade compliance personnel repeatedly released those orders based on the erroneous August 2020 advice from the US trade compliance team.

A meaningful review process would have asked different questions: Were high-risk legal interpretations independently validated? Were assumptions documented? Were unanswered business information requests escalated? Were supplier warnings reconciled against prior advice? Were order-block releases reviewed for quality, not just processed for speed? Were compliance personnel empowered to say, “No complete data, no release”?

Performance review of compliance should include legal quality, escalation discipline, documentation, red-flag closure, audit findings, and whether the function has sufficient staff to do the work expected of it. It should also include board or audit committee visibility when resource constraints affect the company’s ability to manage material compliance risks.

Lessons learned for compliance professionals

The Bosch order offers several broader lessons.

  1. Compliance resources must be risk-based. A global company cannot judge staffing by historical headcount or budget inertia. Staffing must be measured against regulatory complexity, geographic scope, business volume, customer risk, and the operational burden of collecting facts.
  2. Specialist expertise matters. A general compliance function may identify issues, but complex regulatory regimes require personnel or advisors with deep subject-matter knowledge.
  3. Business pressure is a control risk. The “dire allocation situation” response mattered because it showed how operational urgency can displace compliance fact-gathering. A strong program requires mandatory responses to requests for compliance information.
  4. Advice must have a lifecycle. High-risk compliance advice should identify assumptions, facts reviewed, legal basis, owner, date issued, and reassessment triggers. It should not become a permanent operating authority unless periodically reviewed.
  5. Gatekeepers must be trained as gatekeepers. Employees who sign certifications, release orders, onboard suppliers, or respond to customers are part of the compliance control system.

The Bosch case is a reminder that a compliance program can have policies, procedures, and blocks and still fail. The ECCP asks whether compliance is adequately resourced and empowered. Bosch shows why that question matters. The issue is not whether compliance was present. The issue is whether compliance had the expertise, staff, authority, and review mechanisms necessary to function effectively when the business needed it most.

Categories
Blog

What Interruptions Reveal About Corporate Culture

Every Chief Compliance Officer talks about culture. Every company claims to value ethics, integrity, respect, inclusion, and speak-up behavior. Those words appear in codes of conduct, CEO messages, training decks, town halls, leadership offsites, and annual ethics campaigns. Yet culture is not built into the code of conduct. It is revealed in the meeting.

That is the central lesson of Research: What Interruptions Reveal About Company Culture by William Degbey, Benjamin Laker, Baniyelme Zoogah, Sanjay Kumar Singh, and Ghulam Murtaza. The authors argue that workplace culture is shaped less by formal statements and engagement programs than by everyday interaction patterns, especially interruptions in meetings. Their research found that interruptions, redirections, and moments where employees were spoken over were not merely interpersonal annoyances. They were signals of whose voice carried weight in the room.

For the CCO, that finding should land with force. A company can have a beautifully written value of “speak up.” Still, if employees learn in ordinary meetings that certain people are cut off, ignored, or not credited for their ideas, the real culture is not to speak up. It is speak-only-if-you-have-power. That is a compliance issue.

Culture Is What Happens Before the Hotline

Compliance professionals often think about speak-up culture in terms of hotline reports, investigation data, employee surveys, and anti-retaliation policies. Those are important. The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks whether a company has a trusted reporting mechanism, whether employees feel comfortable using it, whether reporting is encouraged or chilled, and whether employees can raise concerns without fear of retaliation.

But by the time an employee reaches the hotline, the culture has already taught that person a great deal. It has taught them that if management listens. It has taught them whether disagreement is welcome. It has taught them whether bad news is punished. It has taught them whether junior employees can challenge senior leaders. It has taught them whether women, employees from underrepresented groups, remote employees, finance staff, compliance staff, or local market employees are taken seriously.

The author’s most important compliance lesson is that interruptions are cultural data. They are small, repeated, observable signals that show whether the company’s stated values are protected in daily business interactions or suspended when authority, speed, revenue, or hierarchy enters the room.

Why This Matters to Ethics and Integrity

Ethics and integrity depend on voice. Employees must be willing to raise concerns, ask questions, challenge assumptions, and slow down decisions when something does not look right. If the organization’s meeting culture teaches employees that unfinished concerns can be interrupted, redirected, or appropriated, then the company is training people not to speak.

The authors found that many senior leaders interpreted interruptions as signs of efficiency and engagement. They saw energetic cross-talk as evidence of a productive culture. Yet the follow-up study found that others experienced the same conduct as exclusionary and predictable. Interruptions were disproportionately directed at women and employees from underrepresented racial and ethnic groups. In the follow-up study, 19 of 27 interviewees described women being interrupted more frequently than men; all seven Black women interviewed described early-stage interruptions, and five said others later resurfaced their ideas without attribution.

For compliance, that is not simply an inclusion issue, though it certainly is. It is also a risk-detection issue. If certain voices are routinely cut off, then certain risks will be underreported. If certain employees must speak faster, more defensively, or only when explicitly invited, the company loses early warning signals. If some ideas are accepted only when repeated by someone with greater status, then the company is not evaluating risk on its merits. It is evaluating risk through hierarchy. That is how ethical blind spots form.

The Silent Cost of Being Interrupted

One of the most powerful findings in the article is that interruptions changed employee behavior. Twenty-one of the 27 participants in the follow-up study said they changed how they contributed to meetings. Some spoke faster or more defensively. Some pre-structured arguments to avoid being cut off. Some waited for explicit permission to speak. Others stopped contributing unless necessary. That is exactly what a CCO should worry about.

A healthy compliance culture does not require employees to perform perfectly polished courage. It gives employees room to raise half-formed concerns, ask awkward questions, and test whether something feels wrong before they have built a legal brief around it. Many compliance issues begin as fragments: “Something about this consultant does not feel right.” “The customer is asking for unusual documentation.” “The timing of this payment seems odd.” “Why are we routing this through that entity? ”I am not sure the data use matches what we told customers.” Those are early-stage compliance signals. They need space.

If the meeting culture rewards only fast, polished, confident speech, then employees who need time to frame a concern may never get the chance. The authors note that faster and more confident-sounding speech was often treated as more authoritative. In comparison, slower or less forceful speech was treated as incomplete and therefore easier to interrupt. For a CCO, the lesson is clear: do not build a compliance program that only works for the loudest person in the room.

From Tone at the Top to Conduct in the Room

Compliance professionals have long emphasized “tone at the top.” That remains important. But this article reminds us that tone at the top is incomplete unless it becomes conduct in the room.

The DOJ expects companies to demonstrate that compliance policies and procedures are integrated into operations and that a culture of compliance is embedded in day-to-day activities. That is precisely where meeting behavior matters. Meetings are where risk appetite becomes real. They are where employees learn whether the company actually values integrity when there is a deal to close, a target to hit, or a senior executive to satisfy.

A CCO should, therefore, ask:

What happens when ethics enters the meeting?

Does the room slow down?

Does the leader protect the person raising the concern?

Does someone capture the issue and assign a follow-up?

Does the business discuss controls and alternatives?

Or does the concern get interrupted, minimized, joked away, or pushed offline?

The answers will tell you more about culture than a slogan.

Reading Interruptions as Compliance Data

The authors recommend that leaders stop treating interruptions as isolated incidents and begin reading them as data. It suggests observing who gets interrupted, when the interruption occurs, and what happens to the idea afterward. Is the idea acknowledged? Is it dropped? Is it later picked up without credit? That framework can be directly adapted into a compliance culture assessment.

A CCO can ask compliance, internal audit, HR, or an outside facilitator to observe selected meetings where risk decisions are made. These might include third-party approval committees, deal review meetings, product governance meetings, investigations triage meetings, M&A diligence sessions, safety committees, privacy reviews, or regional leadership calls.

The observer should not simply count who speaks. This is not about policing manners. It is about understanding whether the company’s ethical culture allows risk information to travel upward and across the organization.

Slow the Meeting to Surface the Risk

The article warns that speed and forced momentum can amplify inequality. Faster conversations often favor those who already feel entitled to the floor. Those who anticipate interruption compress their thinking, hesitate, or wait for a clear opening. The authors recommend slowing the interaction: let people finish, pause before responding, reinforce the norm when someone is cut off, and rotate facilitation. This is deeply relevant to compliance.

Many corporate failures occur not because no one saw the risk, but because the organization moved past it too quickly. The payment had to go out. The distributor had to be approved. The quarter had to close. The launch date had to be met. The customer had to be retained. In that environment, “speed” can become a cultural value that overwhelms integrity. A CCO should help leaders build an “integrity pause” into decision-making.

Protect the Contribution, Not the Ego

The article also makes an important distinction. Calling out interrupters or turning every interruption into a lesson on etiquette often does not work. It can escalate the moment and personalize the issue. The better approach is to protect the contribution directly. The authors suggest short interventions such as “Let them finish,” “I want to hear the rest of that point,” and “Let’s come back to the idea that was just interrupted.” This is practical guidance for CCOs and compliance professionals.

When someone raises a compliance concern and is interrupted, the compliance professional does not need to accuse anyone of bad intent. This helps to create psychological safety around risk information. They tell the room that compliance concerns are not interruptions to business. They are part of doing business properly.

The CCO as Culture Observer

A CCO cannot improve culture solely by issuing policies. Policies matter, but culture is reinforced through repeated behavior. The DOJ guidance recognizes that policies and procedures must give effect to ethical norms and be integrated into day-to-day operations. That means the CCO must look beyond policy architecture and ask how people actually behave when decisions are being made.

Not every interruption is retaliation. Not every fast-paced meeting is unethical. Not every dominant speaker is a compliance risk. But patterns matter. Repeated interruption of certain people, functions, geographies, or types of concerns is cultural data. A CCO should treat it as such.

Turning the Article into a Compliance Playbook

A practical CCO response could include five steps.

  1. Add meeting behavior to the culture assessment. Ask employees whether they can finish raising concerns in meetings, whether leaders invite dissent, whether objections to risk are credited, and whether certain voices are routinely ignored.
  2. Observe high-risk meetings. Select a sample of decision-making forums and map interruptions, credit, follow-up, and closure. The goal is not surveillance. The goal is to understand whether the company’s values show up when risk is discussed.
  3. Train leaders on protecting concerns. Leadership training should include simple phrases or the preservation of unfinished risk points. A manager does not need to become a compliance expert to say, “Let’s hear the rest of that concern.”
  4. Build structured dissent into key decisions. For high-risk approvals, require a final risk round before the decision. Ask compliance, finance, legal, HR, internal audit, cybersecurity, or local-market leaders whether they see an unresolved issue.
  5. Report cultural signals to the board. Boards should hear more than hotline statistics. They should understand whether the organization’s meeting culture supports candor, dissent, and ethical escalation.

Improving Corporate Culture Around Ethics and Integrity

The broader message for compliance professionals is that ethics and integrity must become observable behaviors. Employees should see integrity in how meetings are run, how concerns are handled, how dissent is credited, how leaders respond to uncertainty, and how the company treats people who slow down a decision for the right reason.

The bottom line is straightforward. The words on the wall do not prove a culture of ethics and integrity. It is proven by who gets to speak, who gets heard, and what happens when someone raises a concern that slows the room down. For the CCO, the lesson from this article is powerful: look at the meetings. That is where the culture is already speaking.

Categories
Blog

The False Alignment Trap in Compliance Transformation

A major compliance initiative rarely fails because the Chief Compliance Officer (CCO) did not work hard enough. It usually fails because the organization never reached a true agreement on what the initiative was supposed to accomplish.

That is the core lesson from The False Alignment Trap by Julia Dhar, Kristy R. Ellmer, and Philip Jameson. The authors argue that many change efforts fail because senior leaders believe they agree on the “why,” “what,” and “how” of change when, in fact, they do not. A stitched-together flower is an apt metaphor for corporate change: from a distance, the initiative may look whole; up close, it may be held together by fragile threads.

For the CCO instituting a major compliance initiative, this insight is critical. Whether the project is a global third-party risk overhaul, a new sanctions screening program, an AI governance framework, a speak-up culture campaign, or a full redesign of the compliance operating model, the CCO cannot settle for polite nods around the executive table. The CCO must secure true agreement.

The authors frame the three questions every change program must answer: why are we changing, what are we changing, and how will the change occur? It also makes an important distinction between “alignment” and “agreement.” Alignment may mean that executives are not actively blocking one another. An agreement means leaders have made a detailed and explicit compact that allows them to move together and hold one another accountable. That distinction should be posted on every CCO’s wall.

Why This Matters to Compliance

A major compliance initiative always changes more than the compliance department. It changes how a sales function approves intermediaries. It changes how procurement selects vendors. It changes how finance reviews payments. It changes how HR handles discipline and incentives. It changes how legal, internal audit, cybersecurity, operations, and the business share data. It may change who can approve a deal, how quickly a transaction can move, and what documentation must be in place before revenue is booked. That means compliance transformation is not simply a compliance project. It is an enterprise change project.

The Department of Justice’s 2024 Evaluation of Corporate Compliance Programs (ECCP) asks three fundamental questions: whether the program is well designed, whether it is applied earnestly and in good faith through adequate resources and empowerment, and whether it works in practice. DOJ also asks whether senior management has articulated standards clearly, disseminated them in unambiguous terms, and demonstrated adherence by example. Those expectations cannot be met if the C-suite is only “conceptually aligned” on compliance.

A CCO may believe the company has agreed to strengthen compliance. The CEO may believe the initiative is about satisfying the board. The CFO may believe it is about reducing investigation costs. The head of sales may believe it is about avoiding bad distributors but not slowing growth. The general counsel may believe it is about reducing enforcement exposure. Operations may believe it is another documentation exercise. HR may believe it is about training completion rates. Everyone says yes. Everyone means something different. That is the false alignment trap.

The First Lesson: Never Launch on Slogans Alone

Compliance leaders love phrases such as “culture of compliance,” “tone at the top,” “risk-based approach,” “speak-up culture,” and “doing business the right way.” These phrases are useful, but they are not implementation plans. The authors warn that executives often think they agree because their conversations are insufficiently specific. Leaders may agree on a broad goal, but disagree sharply on the levers, trade-offs, timeline, funding, and operational consequences.

For a CCO, this means “we need a stronger third-party program” is not enough. The leadership team must agree on what that means in practice. Does it mean fewer third parties? More due diligence? More audits? Centralized onboarding? Automated screening? New contractual rights? Mandatory business justification? Enhanced payment controls? A right to terminate non-responsive intermediaries? A slower sales cycle in high-risk markets? Until those questions are answered, the CCO does not have agreement. The CCO has a slogan.

The Second Lesson: Silence Is Not Commitment

One of the most dangerous moments in compliance transformation is the executive meeting where everyone nods. The authors describe the “false consensus effect,” where leaders overestimate the extent to which others share their beliefs. It also describes the tendency of executives to pretend to agree rather than surface disagreement. In one example, executives used vague phrases such as “I am aligned,” “partly aligned,” and “conceptually aligned,” even though real disagreement remained unresolved.

Compliance professionals see this all the time. A regional president says, “We fully support the new due diligence process.” What she may mean is, “We support it unless it slows down strategic distributors.” A sales leader says, “We support compliance training.” What he may mean is, “We support it as long as it does not take people out of the field during the quarter.” A procurement leader says, “We support vendor controls.” What he may mean is, “We support them for new vendors, but not for legacy vendors.”

The CCO’s job is to make those reservations visible before launch. That does not mean creating conflict for conflict’s sake. It means creating a process where disagreement becomes a source of better design.

The Third Lesson: Invite Dissent Early

The authors recommend provoking an early exchange. Leaders should write down what they agree with, what they disagree with, and what they are unsure about. The authors specifically note that written reactions can reduce groupthink. They also recommend asking questions that invite contrary views, such as “What could go wrong with this approach?”

This is directly applicable to compliance. Before launching a major compliance initiative, the CCO should ask each executive to answer, in writing:

What risk are we trying to reduce?

What business process will this initiative change?

What are you worried this initiative will disrupt?

What resources will your function need?

What decisions are you willing to give up or share?

What part of this proposal do you not support?

Where do you believe compliance is underestimating the operational impact?

These questions are uncomfortable. That is the point. A compliance initiative that cannot survive executive-level dissent in a planning meeting will not survive business-level resistance during implementation.

The Fourth Lesson: Deferred Agreement Becomes Compliance Debt

The authors warn against the idea that leaders can “sort out the details later.” That may work for small experiments, but the authors argue that it is dangerous for transformative organizational change because vague or contradictory premises create confusion, delay, and employee frustration. They describe deferred agreement as a debt that leaders expect to repay quickly but often never repay at all. For compliance, deferred agreement is especially costly.

When the CCO launches without a clear executive agreement, the business will find the gaps. If sales and compliance disagree on third-party approval standards, the business will escalate every hard case. If finance and compliance disagree on payment controls, exceptions will multiply. If HR and legal disagree on discipline standards, investigations will produce inconsistent outcomes. If IT and compliance disagree on data ownership, monitoring dashboards will never mature. The result is not simply inefficiency. It is a control failure.

A CCO should treat unresolved executive disagreement as a known risk. It should be tracked, assigned, escalated, and resolved before the initiative moves from design to deployment.

The Fifth Lesson: Watch for the Three Failure Modes

The authors identify three consequences of false alignment: paralysis, hyperactivity, and tunnel vision. These are also classic symptoms of a failing compliance initiative.

Paralysis occurs when teams are stuck between competing executive priorities. In compliance, this looks like endless working groups, repeated risk assessments, draft policies that never finalize, and technology projects that remain in “requirements gathering” for months.

Hyperactivity occurs when teams launch too many initiatives to please too many stakeholders. In compliance, this looks like a dozen training campaigns, multiple dashboards, overlapping third-party reviews, new certifications, new attestations, and new committees, but no meaningful risk reduction.

Tunnel vision occurs when teams make progress on the wrong thing. In compliance, this may mean achieving 100% training completion while employees still do not know how to raise concerns. It may mean onboarding vendors faster while missing beneficial ownership risk. It may mean closing investigations more quickly while weakening root cause analysis.

The CCO should use these three symptoms as early warning indicators. If the initiative is stuck, too busy, or moving in the wrong direction, the problem may not be execution. It may be false alignment at the top.

Lessons in Building True Agreement for a Compliance Initiative

The authors offer a five-step path to true agreement: set clear parameters, provoke an early exchange, have a substantive debate, reach a formal verdict, and send a unified message. That framework can be translated directly into a CCO playbook.

  1. Set clear parameters. The CCO should define the decision rights before the project begins. Who decides the risk appetite? Who approves the budget? Who owns business process changes? What decisions require CEO approval? What issues go to the board? What happens if a regional business leader disagrees?
  2. Provoke an early exchange. The CCO should require written input from the CEO, CFO, general counsel, CHRO, CIO, internal audit, procurement, and key business leaders. This is where hidden objections should surface.
  3. Have a quality debate. The CCO should hold one-on-one conversations with executives before the group decision meeting. The point is not to lobby for superficial support. The point is to understand red lines, trade-offs, and operational realities.
  4. Come to a formal verdict. The authors recommend asking for each individual’s agreement, documenting the decision, and creating a formal record of the agreed terms. For a compliance initiative, this should become a written executive charter. It should specify scope, budget, timeline, metrics, decision rights, business obligations, and escalation paths.
  5. Send a unified message. The authors warn against each executive’s team receiving its own version of events. Instead, the decision should be broadcast simultaneously in a single format to everyone who needs to know. For compliance, this is essential. Employees should hear one message: this is why we are changing; this is what will change; this is what will not change; this is who owns what; and this is how success will be measured.

The bottom line is clear. A major compliance initiative is not successful because the CCO announces it, the board approves it, or the executive team says it is “aligned.” It is successful when the company reaches true agreement on the risk, the change, the trade-offs, the ownership, and the evidence of effectiveness.

For the compliance professional, The False Alignment Trap provides a powerful reminder: do not launch a transformation on implied consent. Build the compact first. Then execute.

Categories
Blog

Can Compliance Own Enterprise Resilience?

It has been some time since I checked in with the Harvard Business Review for some blog posts. To remedy this deficiency, I will write this week’s blog posts based on recent HBR articles that caught my interest. Today, we begin with The Case for Hiring a Chief Resilience Officer, which argues that there is a major governance gap inside most organizations. It is that no single executive is accountable for coordinating enterprise-wide resilience and recovery when failures cascade across functions. The article looks at a chief resilience officer (CResO) role which would be responsible for aligning continuity planning, recovery objectives, crisis response, and organizational learning across an enterprise.

The authors begin by noting that the July 2024 CrowdStrike outage will be remembered as more than a technology failure. It was a governance lesson. A routine software update caused cascading operational disruption across airlines, hospitals, logistics systems, and other critical services. The technical root cause mattered, but it was not the only lesson. The larger issue was how quickly a single failure could ripple across functions, third parties, customer obligations, regulatory expectations, and business operations. The article articulated this as the case for a CResO, because many organizations have no single executive accountable for coordinating enterprise-wide resilience and recovery when disruption crosses organizational boundaries.

For the corporate compliance function, that argument should sound familiar. Compliance professionals have spent years explaining that risk does not respect departmental boundaries. Bribery risk can arise from sales incentives, third-party relationships, financial controls, gifts and hospitality, and management pressure. Data risk can sit in technology, privacy, procurement, HR, and customer operations. AI risk can sit in product development, vendor management, legal, cybersecurity, records retention, and board oversight.

Operational resilience is the same kind of problem. It is not only an IT issue. It is not only a business continuity issue. It is not only a risk management issue. It is a governance issue, a controls issue, a documentation issue, a third-party issue, and a board oversight issue. That makes it a compliance issue as well.

The Compliance Significance of Resilience

The central insight behind the CResO role is that most organizations already have pieces of resilience, but they do not always have resilience governance. Risk teams assess exposure. Cybersecurity teams protect systems. Operations teams manage delivery. Business continuity teams write plans and run exercises. Procurement manages vendors. Legal evaluates obligations. Communications handles stakeholders. Compliance monitors controls, policies, reporting, and escalation. Each function may be doing its job. The problem appears when no one owns the integrated answer.

That is why operational resilience has become a regulatory and governance priority. The Basel Committee defines operational resilience as the ability to deliver critical operations through disruption and emphasizes governance, mapping interdependencies, third-party dependency management, business continuity testing, and incident management. The FCA in the UK similarly focuses on important business services, impact tolerances, mapping, testing, vulnerability remediation, lessons learned, and communications planning. In the EU, the Digital Operational Resilience Act (DORA) has elevated digital operational resilience, technology and information third-party risk, incident reporting, and resilience testing into a formal financial sector regulatory framework.

For compliance professionals, the message is clear. Resilience is moving from planning to evidence. Regulators, boards, and senior management will increasingly ask not simply whether the company had a plan, but whether the company knew its critical services, mapped its dependencies, tested severe but plausible scenarios, documented vulnerabilities, assigned accountability, and remediated weaknesses.

That is familiar territory for compliance. The DOJ Evaluation of Corporate Compliance Programs (ECCP) asks whether a compliance program is well designed, adequately resourced and empowered, and works in practice. It also asks whether improvements to compliance and internal controls have been tested to show they would prevent or detect similar misconduct in the future. Those questions are not limited to bribery, fraud, or sanctions. They reflect a broader governance discipline: design, authority, resources, testing, remediation, and proof.

Can Compliance Absorb the CResO Role?

The answer is yes, but only under the right conditions. A compliance function can absorb the resilience governance role if it has the mandate, authority, resources, data access, and board visibility to do the job. It cannot absorb the role if the organization merely adds resilience to the CCO’s already crowded list of responsibilities without giving compliance the ability to coordinate across technology, operations, procurement, cybersecurity, finance, legal, human resources, communications, and business leadership. This distinction matters.

Compliance can own the governance framework for resilience. It can help define standards, require documentation, monitor remediation, test controls, escalate gaps, and report to the board. It can ensure that resilience obligations are embedded into policies, third-party oversight, incident response, investigations, root cause analysis, training, and internal controls.

Compliance should not become the operator of every resilience process. The first line must still own business services. Technology must still own systems. Cybersecurity must still own cyber defense. Procurement must still own vendor contracting and supplier performance. Operations must still own delivery. Legal must still advise on obligations. Communications must still manage stakeholder messaging. The CCO can serve as the enterprise resilience governance leader, but not as a substitute for operational ownership. That is the practical dividing line.

When Compliance Is the Right Home

Compliance is a strong candidate to absorb the CResO function when resilience is framed as an enterprise governance and controls discipline. This is especially true in organizations where the compliance function already has mature capabilities in risk assessment, policy governance, third-party risk management, investigations, remediation tracking, board reporting, training, monitoring, and documentation. In that model, compliance can bring several advantages.

First, compliance understands cross-functional risk. A well-designed compliance program already reaches into the business, finance, procurement, HR, legal, internal audit, IT, and senior leadership. That horizontal view is essential for resilience.

Second, compliance understands evidence. Resilience cannot be built on verbal assurance. It requires inventories, dependency maps, testing records, incident reports, remediation plans, escalation logs, board materials, and lessons learned. Compliance professionals know how to create a record that demonstrates program effectiveness.

Third, compliance understands accountability. A resilience program without accountable owners will become a collection of meetings. Compliance can help define who owns each critical service, each dependency, each recovery objective, and who must act when testing identifies a vulnerability.

Fourth, compliance understands third-party risk. Many resilience failures begin outside the company’s walls. A critical software provider, cloud provider, logistics partner, manufacturer, payroll vendor, or data processor can disrupt the company’s ability to deliver. Compliance can help connect due diligence, contracting, ongoing monitoring, audit rights, incident notification, and exit planning into a resilience framework.

Finally, compliance understands board reporting. Resilience is a board-level issue because disruption can affect customers, investors, regulators, employees, and the company’s license to operate. The FCA has emphasized that boards need enough information to understand the firm’s resilience approach, who is responsible for it, and the organization’s ability to recover important business services within impact tolerances. Those are governance questions. Compliance is built to translate them into a management system.

When Compliance Should Not Absorb the Role

Compliance should not assume the CResO role if the function lacks operational authority, technical depth, crisis-management access, or senior-level support. A CCO who is asked to “own resilience” without the resources to do so has not been empowered. That CCO has been handed accountability without control. There are several warning signs.

If compliance does not have direct access to the CEO, executive committee, and board, it cannot coordinate enterprise resilience. If compliance cannot require action from technology, operations, procurement, and business units, it cannot close resilience gaps. If compliance lacks data on critical services, vendor concentration, system dependencies, recovery times, incident history, and testing results, it cannot evaluate resilience in practice. If compliance is already under-resourced, resilience will become another paper responsibility.

That would be a mistake. The worst outcome would be to move resilience into compliance as a label while leaving the real decision-making elsewhere. That creates the appearance of governance without its substance.

A Better Model: Compliance as Resilience Governor

For many companies, the right answer is not a binary choice between a standalone CResO and a compliance-owned resilience function. The better model may be compliance as a resilience governor. Under this approach, the company appoints a senior resilience owner, either as a CResO (chief risk and resilience officer) or as a named executive with enterprise authority. Compliance then provides the governance architecture: standards, controls, testing expectations, third-party requirements, escalation procedures, documentation rules, remediation tracking, and board reporting.

This model preserves first-line ownership while giving the organization a consistent second-line framework. It also allows compliance to ask the questions that matter:

Who owns each critical business service? What are the maximum tolerable disruptions? What systems, people, facilities, data, and third parties support each service? What severe but plausible scenarios have been tested? What vulnerabilities were identified? Who owns remediation? What evidence shows that remediation worked? What has been reported to the board?

These are not theoretical questions. They are the difference between a plan and a program.

Five Lessons for Compliance Professionals

  1. Resilience is now a compliance program issue. It involves governance, controls, accountability, documentation, testing, remediation, and board oversight.
  2. Compliance can absorb the resilience governance role, but not the operational role. The CCO can govern the framework. The business must still own delivery.
  3. Authority matters. A compliance-led resilience function must have CEO support, board visibility, cross-functional access, and the ability to require remediation.
  4. Evidence is essential. Dependency maps, scenario tests, incident reports, remediation records, and board materials are what turn resilience from aspiration into proof.
  5. The board should focus on accountability before structure. Whether the company appoints a CResO, places resilience under risk, or builds a compliance-led governance model, the core question remains the same: who owns the enterprise response when disruption crosses every boundary?

The practical compliance lesson is straightforward. Resilience cannot remain a collection of disconnected plans. It must become an operating discipline. For some companies, that discipline will require a dedicated Chief Resilience Officer. For others, a mature, properly empowered compliance function can assume the governance role. But no company should leave resilience to assumption, informal coordination, or after-the-fact improvisation.

In today’s risk environment, the ability to recover is not only an operational strength. It is evidence of effective governance.

Categories
Blog

From the Tower of Babel to the Boardroom: Part 5 – Workforce Transformation, Third-Party Risk, and Modern Slavery

Artificial intelligence often appears frictionless. A prompt goes in. An answer comes out. A report is summarized. A risk score is generated. A customer interaction is automated. A compliance analyst receives a faster answer. A business process becomes more efficient. Yet there is nothing frictionless about AI.

Behind every AI tool sits a human supply chain. Some workers label data, moderate content, train models, build infrastructure, mine minerals, assemble devices, maintain data centers, write code, manage vendors, and absorb the consequences when automation changes the nature of work. There are third parties, subcontractors, cloud providers, data brokers, model developers, implementation consultants, and business users. There are people whose labor, data, dignity, and livelihoods may be affected long before the board ever sees an AI dashboard. Now we turn to the human supply chain of AI: workforce transformation, third-party risk, and modern slavery.

The Magnifica Humanitas Lesson: AI Is Never Disembodied

Magnifica Humanitas makes a powerful point for compliance professionals: AI is not immaterial or magical. Pope Leo states, “Nothing in the world of AI is immaterial or magical.” That is a moral statement, but it is also a governance statement. The Encyclical explains that AI depends on natural resources, energy infrastructure, digital platforms, and human labor, including data labeling, model training, content moderation, and the extraction of materials needed for devices and microprocessors (Magnifica Humanitas, ¶173).

That is a direct compliance lesson. The risk does not begin when the company deploys an AI tool. The risk begins when the company selects the vendor, approves the use case, provides data, accepts contractual terms, relies on outputs, and fails to ask who and what sits behind the technology. The Encyclical is equally direct that digital systems can amplify hidden forms of exploitation and that supply chains supporting the technology industry should become transparent so competitive advantage is not built on hidden exploitation (Magnifica Humanitas, ¶179).

The document also speaks directly to work. It teaches that work is not simply an instrument, but a setting in which people develop, contribute, cooperate, support their families, and build together (Magnifica Humanitas, ¶148-149). It warns that AI can improve productivity while also de-skilling workers, subjecting them to automated surveillance, forcing them to adapt to the pace of machines, and eroding their agency (Magnifica Humanitas, ¶150). For the CCO, this means AI governance is not only about model risk. It is also about people’s risk.

From Encyclical Principle to Corporate Governance Requirement

The bridge from Magnifica Humanitas to corporate governance is straightforward. Pope Leo calls for human-centred technology, social criteria for innovation, verifiable measures to protect employment, retraining, worker participation, and a corporate commitment to include the quality and dignity of work among the indicators of success (Magnifica Humanitas, ¶156). In corporate governance language, that means AI adoption should include workforce impact assessment, role-based training, human review, bias testing, privacy controls, speak-up protections, and board reporting.

The Encyclical also calls for preventive ethical verification, or due diligence, across the digital economy, with priority given to worker protection, the fight against forced labor, and assessment of the social impact of data-driven business models (Magnifica Humanitas, ¶179). For compliance professionals, that is third-party risk management. It means vendor due diligence, subcontractor transparency, audit rights, data provenance, labor standards, modern slavery review, incident reporting, and ongoing monitoring.

This is where the moral language of Magnifica Humanitas becomes the operating language of compliance. Human dignity becomes human rights due diligence. Shared responsibility becomes cross-functional governance. Transparency becomes supply chain visibility. Accountability includes naming owners, documentation, monitoring, testing, challenge, and remediation.

Workforce Transformation Is a Compliance Issue

AI will change work. That is not speculation. It is already changing how employees draft, analyze, monitor, investigate, review, report, and decide. The question is whether companies will manage this transformation with governance, transparency, and care, or allow automation to wash through the workforce as a cost-reduction exercise.

Compliance should not attempt to own a workforce strategy. That belongs with management, HR, legal, finance, and business leadership. But compliance should have a voice because workforce transformation creates culture risk, speak-up risk, retaliation risk, discrimination risk, privacy risk, monitoring risk, and internal controls risk. The Encyclical warns that innovation pursued solely for cost reduction and profit can produce job insecurity, inequality, and social instability (Magnifica Humanitas, ¶151).

A company using AI to evaluate employees, monitor productivity, screen applicants, assess performance, recommend discipline, or allocate opportunities should ask hard questions. What data is being used? Has the tool been tested for bias? Are employees informed? Can individuals challenge errors? Is human review required? Are managers trained not to over-rely on AI outputs? Is the tool increasing fairness, or simply making questionable decisions faster?

AI adoption should also include change management. Employees need training on approved AI use, prohibited data inputs, required human review, and escalation of concerns. They also need assurance that raising concerns about AI will not be punished. The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks whether companies train employees on emerging technologies such as AI and whether companies have controls to monitor AI trustworthiness, reliability, intended use, human decision-making, and accountability. That is not only a technology expectation. It is a cultural expectation.

Third-Party AI Risk Is Not Ordinary Vendor Risk

AI vendors are not ordinary vendors when they touch sensitive data, influence consequential decisions, support compliance processes, provide core infrastructure, or rely on opaque subcontracting chains. A company may believe it is buying software. In reality, it may be acquiring a new decision system, a new data processor, a new compliance dependency, and a new supply chain exposure.

Magnifica Humanitas warns that major economic and technological actors can exercise de facto power over data, expertise, access, visibility, and opportunity. It calls for transparency, accountability, meaningful participation, independent checks, algorithmic transparency, equitable data access, and avenues for recourse (Magnifica Humanitas, ¶71-72). For the CCO, that is a vendor governance mandate.

The ECCP already provides the compliance architecture. A well-designed compliance program should apply risk-based due diligence to third-party relationships, understand the business rationale, assess the risks posed, include appropriate contract terms, monitor third parties through updated due diligence, training, audits, and certifications, and use data to evaluate vendor risk during the relationship. Apply that directly to AI vendors.

The company should know what the AI tool does, what data it uses, whether company data will train or improve the model, where data is stored, who has access, what subcontractors are involved, whether outputs are explainable, what human review is required, how incidents are reported, and whether the vendor can support audit rights. The company should also ask whether the vendor uses third parties for data labeling, content moderation, model evaluation, or technical support, and what labor standards apply to those providers.

An AI vendor questionnaire should not stop at cybersecurity and privacy. It should cover human rights, labor standards, modern slavery risk, data provenance, subcontractor transparency, model governance, incident reporting, auditability, and exit rights.

Modern Slavery Risk in the AI Supply Chain

The risk of modern slavery may seem far removed from enterprise AI adoption. It is not. Magnifica Humanitas challenges that assumption by reminding us that the digital economy depends on physical infrastructure, extracted resources, hidden labor, and vulnerable workers. It specifically identifies data labeling, model training, content moderation, resource extraction, and trafficking-enabled misuse of digital platforms as part of the moral challenge of AI (Magnifica Humanitas, ¶173).

For compliance professionals, the lesson is straightforward. AI supply chain risk should be folded into third-party risk management and human rights due diligence. The company should not assume that because an AI provider has a sophisticated interface, the underlying chain is clean. Procurement and compliance should ask who performs outsourced labeling, testing, moderation, data enrichment, and support work. They should assess whether workers are paid fairly, protected from exposure to harmful content, free from coercion, and supported by appropriate safeguards.

This is especially important where vendors rely on lower-cost labor markets, opaque subcontracting, high-volume content review, or resource extraction. The issue is not whether every AI vendor is high risk. The issue is whether the company has a defensible process to identify which vendors, services, geographies, and labor practices require enhanced review.

The Encyclical makes this corporate obligation unusually concrete: supply chains underpinning the technology industry and digital economy should become more transparent; companies and investors should adopt clear due diligence criteria; and digital platforms should cooperate to prevent communication, payment, and profiling tools from becoming channels for recruitment and control of victims (Magnifica Humanitas, ¶179). A modern AI third-party program should therefore include labor and human rights due diligence at onboarding, contractual commitments, audit rights, subcontractor approval rights, certifications, incident reporting, and ongoing monitoring.

Frameworks for Governing the Human Supply Chain

NIST and ISO/IEC provide a practical structure for this work. NIST’s Generative AI Profile calls for acceptable use policies that address proprietary and open-source AI technologies, data, contractors, consultants, and other third-party personnel. It also identifies the need to document generative AI value-chain risks, plan for failures or incidents involving third-party data or systems, and continuously monitor third-party AI systems in deployment.

ISO/IEC 42001 provides a management-system approach for organizations that develop, provide, or use AI-based products or services. It supplies the governance discipline compliance professionals understand: policy, roles, risk assessment, controls, monitoring, performance evaluation, corrective action, and continual improvement.

COSO adds the internal controls discipline. COSO’s GenAI guidance emphasizes that generative AI is moving into operations and boardrooms faster than traditional governance models anticipated, and that risks such as cyber exposure, prompt manipulation, opaque reasoning, model drift, and configuration changes can jeopardize operations, reporting, and compliance if not addressed through robust internal controls.

Together, these frameworks point to the same conclusion. AI supply chain governance must be documented, controlled, monitored, tested, and improved.

Board Oversight: The Human Cost Must Be Visible

Boards do not need to manage AI vendors. They do need to oversee the systems management used to identify, assess, monitor, and remediate material AI risks. Under Caremark principles, directors must make a good-faith effort to oversee company operations. The board’s obligation is not technical mastery. It is a reporting and monitoring system that shows management has responded to the Encyclical’s accountability and due diligence mandate.

For AI, the board should ask whether management has visibility into the human supply chain. Which AI vendors are critical? Which tools affect employees, customers, suppliers, or compliance decisions? Which vendors use subcontractors? Which AI tools rely on sensitive data? What labor and human rights risks have been identified? What workforce impacts are expected? What retraining is planned? What AI-related incidents have occurred? What open remediation items remain?

Magnifica Humanitas closes this portion of its analysis with a shared responsibility principle: innovation must be guided by institutions, businesses, intermediary organizations, educational communities, and citizens so that it serves integral human development rather than becoming a source of exclusion and dominance (Magnifica Humanitas, ¶180-181). The board failure will not be that the directors did not understand every model parameter. The failure would be failing to ask whether management has a reasonable system to govern AI’s human, third-party, and supply chain impacts.

5 Lessons for the CCO
  1. Map the human supply chain. The company should know the vendors, subcontractors, data sources, infrastructure providers, and outsourced labor that support material AI tools.
  2. Treat high-impact AI vendors as high-risk third parties. AI vendors that touch sensitive data, support consequential decisions, or affect compliance processes require enhanced due diligence, contractual protections, and ongoing monitoring.
  3. Build human rights and modern slavery risk into AI due diligence. Vendor reviews should address labor practices, subcontractors, content moderation, data labeling, resource extraction, worker protections, and geographic risk.
  4. Govern workforce transformation. AI adoption should include training, retraining, human review, transparency, privacy protections, bias testing, and speak-up channels for employee concerns.
  5. Report evidence to the board. Boards need visibility into AI vendor risk, workforce impact, supply chain exposure, incidents, remediation, and control testing.
Conclusion: From Babel to Responsible Reconstruction

The AI age will reward companies that innovate. But it will also test whether those companies can govern innovation with discipline, transparency, responsibility, and human primacy. The lesson of Magnifica Humanitas is that AI must remain at the service of the human person. That includes the employee whose job is changing, the worker hidden in the supply chain, the community affected by resource extraction, the customer subject to an automated decision, and the board charged with oversight.

This five-part series began with the Tower of Babel and the boardroom. Babel was power without humility. Nehemiah was rebuilding with responsibility. For the modern compliance professional, that is the AI governance choice. Pope Leo frames the alternative as progress that serves people or progress that subjects them to the mentality of power (Magnifica Humanitas, ¶129). We can allow AI to grow through hidden use, opaque vendors, weak controls, synthetic trust, and invisible human cost. Or we can build an AI governance program grounded in risk assessment, controls, accountability, transparency, human review, third-party diligence, workforce care, and board reporting.

The next step is to convert these five lessons into a practical board-ready AI governance checklist. That checklist should give directors, CCOs, general counsel, audit leaders, risk leaders, and CEOs a structured way to ask the right questions, demand the right evidence, and govern AI before AI governs the enterprise.

Categories
Blog

From the Tower of Babel to the Boardroom: Part 1 – Governing AI

Artificial intelligence is no longer a future issue for boards, CEOs, general counsel, chief compliance officers, audit leaders, or risk professionals. It is already inside the enterprise. It is in employee workflows, vendor platforms, data analytics, customer engagement, monitoring tools, investigations support, training design, due diligence, and decision-making processes. The compliance question is no longer whether the company will use AI. The real question is whether the company will govern AI before AI becomes embedded into the business without accountability, transparency, controls, or human judgment.

That is the danger of the modern Tower of Babel. Babel was not a failure of engineering. It was a failure of purpose, humility, and governance. It was a project built on power without accountability and ambition without restraint. For modern corporations, ungoverned AI can become a similar project. It may promise efficiency, scale, speed, and competitive advantage. Yet without proper governance, it can also produce bias, opacity, data misuse, weakened accountability, employee overreliance, vendor risk, and board blind spots.

What Is Magnifica Humanitas?

Magnifica Humanitas is an Encyclical Letter issued by Pope Leo XIV on May 15, 2026, titled “On Safeguarding the Human Person in the Time of Artificial Intelligence.” (Magnifica Humanitas herein). The document places AI within the long tradition of Catholic social teaching and asks how humanity should respond to the “new things” of the digital age. Pope Leo frames AI not as a narrow technology issue but as a profound question about human dignity, work, truth, freedom, power, data, social justice, and the common good. The letter opens with two biblical images, the Tower of Babel and the rebuilding of Jerusalem under Nehemiah, to present the central choice of the AI age: will we construct systems of domination, or will we build communities of shared responsibility? (Magnifica Humanitas, paras. 1, 7-10).

The significance of Pope Leo issuing Magnifica Humanitas is that he places AI in the same broad moral and social category as prior industrial and economic disruptions. He expressly connects the document to the legacy of Pope Leo XIII and Rerum Novarum, the 1891 encyclical that responded to the labor, capital, and social disruptions of the industrial age. Pope Leo writes that digitalization, AI, and robotics are rapidly transforming the world, shaping decision-making and affecting both human dignity and the common good (Magnifica Humanitas, paras. 3-4). For this five-part series, we will use Magnifica Humanitas as the foundation for translating its core concepts into practical lessons for the modern compliance professional, the board, and the executive leadership team. This will not be a theological series. It will be a governance series. We will apply the moral force of the Encyclical Letter to compliance program design, board oversight, internal controls, data governance, third-party risk, workforce transformation, and corporate trust.

The Compliance Lesson of Babel

The Tower of Babel is a powerful compliance metaphor because it shows what happens when a project has capability but lacks discipline. Pope Leo describes Babel as an impressive feat with “a single language, a single technology, a single direction,” yet one that sacrificed human dignity for efficiency and sought power through self-sufficiency (Magnifica Humanitas, para. 7). In corporate language, Babel is the business transformation project that mistakes technical capability for good governance.

Pope Leo’s warning is direct: technology is never neutral because it takes on the characteristics of those who design, finance, regulate, and use it (Magnifica Humanitas, para. 9). That sentence should sit in every boardroom AI discussion. AI is not neutral in the compliance sense either. It reflects data, design, deployment, vendor, incentive, and governance choices. The first board question is therefore simple: What are we building?

Nehemiah as the Governance Model

If Babel is the warning, Nehemiah is the governance model. In Magnifica Humanitas, Pope Leo contrasts Babel with the rebuilding of Jerusalem. Nehemiah listens, inspects the damage, assigns responsibility, coordinates work, addresses opposition, and rebuilds section by section. The city is reborn through shared responsibility, not through the initiative of a single person (Magnifica Humanitas, para. 8).

That is the model compliance professionals should bring to AI governance. The CCO does not need to become a data scientist. The board does not need to manage model architecture. But the organization needs a disciplined governance structure that brings together compliance, legal, privacy, cybersecurity, IT, HR, internal audit, procurement, finance, and the business. AI governance cannot sit in a silo. It must be cross-functional because AI risk is cross-functional.

For compliance, that means asking practical questions. Where is AI being used? What problem is it solving? What data does it access? Who approved it? What risks were identified? What controls were designed? What human review is required? What could go wrong? How would we know? Who is accountable if the AI produces a harmful or unlawful result? Those are not anti-innovation questions. They are business discipline questions.

From Encyclical Principle to Corporate Governance Requirement

The bridge from Magnifica Humanitas to corporate governance is straightforward. Human dignity becomes a human impact assessment. The common good becomes enterprise risk governance and stakeholder impact. Subsidiarity becomes cross-functional governance, meaningful participation, and decision-making as close as possible to the affected process. Transparency becomes documentation, explainability, board reporting, and auditability. Accountability includes named owners, escalation rights, challenge mechanisms, and remediation.

Pope Leo makes this bridge explicit when he calls for responsible planning, human and social impact assessment, inclusion of the vulnerable, digital literacy, and guiding research and industry toward justice and peace (Magnifica Humanitas, para. 14). He also warns that control over platforms, infrastructure, data, and computing power can become opaque and evade oversight, producing dependency, exclusion, manipulation, and inequality (Magnifica Humanitas, para. 95). For the CCO and the board, that is the language of AI inventory, data governance, vendor management, access controls, model oversight, incident response, and internal audit testing. That is not only a moral framework. It is a corporate governance requirement.

AI Governance and the DOJ ECCP

The Department of Justice has already made AI a compliance program issue. The logic now runs together. Pope Leo provides the mandate for moral governance. The DOJ Evaluation of Corporate Compliance Programs (ECCP) supplies the compliance program test. The ECCP asks whether companies have a process for identifying and managing emerging risks, including risks related to new technologies such as AI; whether AI risk is integrated into enterprise risk management; how AI is governed in the business and in the compliance program; whether controls monitor trustworthiness and reliability; whether AI is limited to intended uses; what human decision-making baseline exists; how accountability is enforced; and how employees are trained.

That is a roadmap for the CCO. AI governance should be part of the compliance risk assessment. It should be reflected in policies and procedures. It should include training and communications. It should be monitored, audited, and improved. It should generate evidence. The company should be able to show not only that it has an AI policy but also that the policy has an operational effect. In other words, AI governance must move from aspiration to controls.

Board Oversight and Caremark

For boards, AI governance also raises Caremark oversight considerations. Directors are not expected to run the company’s AI systems. They are expected to make a good-faith effort to ensure that reasonable reporting and monitoring systems are in place for central compliance risks. In Marchand v. Barnhill (Bluebell Ice Cream), the Delaware Supreme Court emphasized that boards must make a good-faith effort to put in place a reasonable board-level system of monitoring and reporting around central compliance risks.

The board obligation is not technical mastery. It is a reporting and monitoring system that shows management has responded to the Encyclical’s accountability mandate. If Pope Leo requires that responsibility be defined, decisions be justified, systems be monitored, harms be challenged, and errors be remedied (Magnifica Humanitas, para. 105), then the board must ask whether management has built a governance system capable of producing that evidence. The board does not need technical comfort. It needs governance confidence.

Human Primacy as a Control

One of the most important lessons from Magnifica Humanitas is that AI is a tool, not a moral actor. Pope Leo explains that AI systems may imitate language, analysis, behavior, and even empathy, but they do not possess lived experience, conscience, wisdom, moral responsibility, or the capacity to understand what they produce (Magnifica Humanitas, para. 99). That matters deeply when AI affects employment, reputation, access, rights, opportunities, or treatment.

For compliance professionals, human primacy must be designed into AI governance. Human review is not a bureaucratic obstacle. It is a control. Pope Leo warns that sensitive decisions concerning employment, credit, access to services, and reputational risk are being delegated to automated systems that lack compassion, mercy, forgiveness, or the hope that people can change (Magnifica Humanitas, para. 102). The company should decide which AI outputs can be used automatically, which require review, which require escalation, and which uses should be prohibited altogether. The more consequential the decision, the stronger the human oversight must be.

5 Lessons for the CCO
  1. Treat AI as a human dignity and compliance risk. AI should be included in the compliance risk assessment, enterprise risk management process, and board reporting because it can affect rights, opportunities, status, freedom, privacy, and trust.
  2. Build an AI inventory because governance begins with visibility. The company cannot govern what it cannot see. The inventory should include business tools, vendor tools, embedded AI, compliance tools, and employee use of public AI.
  3. Require controls before scale because technology is never neutral. AI policies must be supported by approval processes, data controls, access controls, monitoring, testing, escalation, and remediation.
  4. Preserve human judgment because accountability cannot be outsourced. Human review should be required for high-risk and consequential decisions. Accountability must remain with people, not systems.
  5. Give the board evidence because governance requires reporting, monitoring, and remediation. Boards need dashboards, metrics, incident reporting, audit findings, risk rankings, and documentation that AI governance is working.
Conclusion: From Babel to Compliance Program Design

The lesson of Babel is not that building is wrong. The lesson is that building without humility, accountability, and purpose leads to fracture. AI is here to stay, and compliance professionals should embrace its promise. AI can improve monitoring, strengthen risk analysis, support investigations, enhance training, and identify patterns that humans might miss. But it must be governed with vigilance, responsibility, transparency, and human primacy.

Magnifica Humanitas gives us the mandate for moral governance. The ECCP gives us the compliance program questions. Caremark gives boards the oversight framework. Together, they point to the same conclusion: AI governance must be built before AI risk becomes unmanageable.

In the next post, we will move from principle to program design. We will examine why AI governance is a compliance program issue, how the CCO should help structure AI oversight, and how compliance can use AI responsibly while governing the risks AI creates.