Paying a penalty and demonstrating an effective compliance program are different tasks. The AMEX enforcement actions make that distinction concrete.
In Part 1, we examined the OCC’s $350 million civil money penalty and findings concerning risk assessment, customer information, suspicious activity reporting, resources, training, and independent testing. The Federal Reserve’s Order focuses on enterprise-level change. Its starting point is board oversight.
For compliance professionals across industries, that is the opportunity: use the remediation requirements to challenge your own governance and controls. The orders bind the named entities. The broader applications below are recommendations, not claims that banking-specific obligations apply to every company.
Board oversight must produce accountable decisions
Within 90 days of the order’s effective date, AMEX’s board must submit a written oversight plan to the Federal Reserve. The plan must explain how directors will hold senior management accountable for remediation, ensure adequate resources, oversee an effective enterprise-wide BSA/AML compliance risk management program, and secure effective reporting and escalation. The board’s responsibilities expressly encompass remediation under both the Federal Reserve order and the OCC order.
Notice the allocation of responsibility. The board oversees. Senior management executes. Neither role should disappear into an instruction that “compliance will handle it.” For another company applying this lesson, I recommend that each material remediation item identify an accountable executive, responsible business owner, required resources, completion criteria, and independent reviewer. The CCO should help coordinate and challenge the work without becoming the default owner of every operational control.
COSO’s Internal Control–Integrated Framework provides a corresponding board-oversight benchmark. Under Principle 2, directors should independently oversee internal control development and performance. Translate that principle into board practice. Record the questions directors asked, the evidence management provided, resource decisions, and the follow-up required. A presentation should support an oversight decision, not substitute for one.
Make enterprise-wide compliance operational
The Federal Reserve requires AMEX to submit an acceptable plan within 90 days to improve enterprise-wide BSA/AML compliance risk management. Required content includes business-line and legal-entity policies, customer due diligence, cross-business-line suspicious activity reporting, and transaction-monitoring methodologies. Establish, analyze, test, and document monitoring rules and thresholds, paying attention to factors such as customer, product, or service, and geography.
That requirement suggests a practical exercise for any CCO: select a significant risk and trace how the organization treats it. Who collects the relevant information? Who assesses it? What triggers review? Which team investigates? When does senior management receive the issue? What reaches the board? But do not stop at the organization chart. The order calls for risk-based oversight of BSA/AML systems and the use of information from network partnerships, ATM partners, and third parties supporting compliance.
For a nonfinancial company, a comparable review could follow a high-risk distributor relationship from onboarding through orders, payments, exceptions, and termination. Test the handoffs, including information held by outside providers. The Federal Reserve also requires the travel-related services subsidiary to submit an acceptable Office of Foreign Assets Control (OFAC) compliance plan within 90 days. It must address risk assessment, ongoing job-appropriate training, and enhanced policies and screening procedures. This is a distinct sanctions-compliance remediation requirement; it should not be recast as a finding of a particular prohibited transaction.
Use COSO to examine the connections between controls
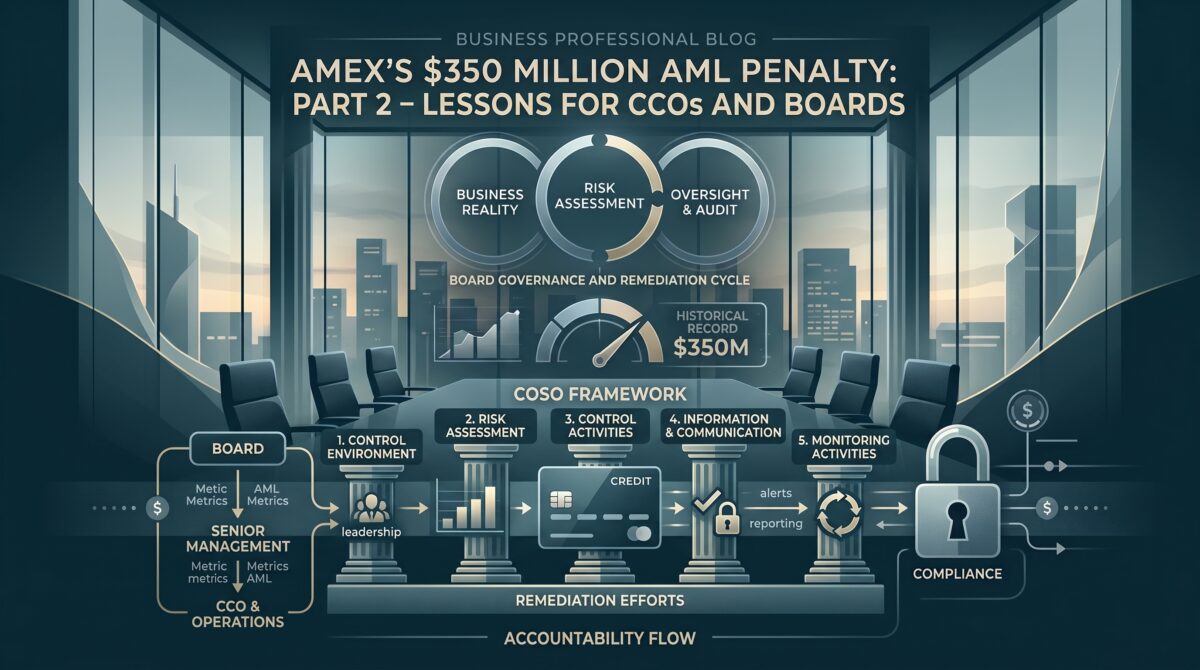
COSO organizes internal control around five components: control environment, risk assessment, control activities, information and communication, and monitoring activities. The framework emphasizes that these components must work together, not exist as separate administrative exercises. Applied to the AMEX findings, I recommend testing a connected chain of evidence.
Begin with the commercial activity and its risk assessment. Identify the resulting control, the person responsible, the information required, the escalation decision, and the independent test. Then examine what happens when one element fails. For example, don’t accept a customer-risk rating as useful just because a system has a completed field. Ask whether supporting information is reliable, whether the rating changes monitoring, and whether testing confirms that the resulting controls address the assessed risk.
COSO’s Principles 16 and 17 reinforce evaluating controls and promptly communicating deficiencies to those responsible for correction, including senior management and directors where appropriate. The practical point is to test relationships between controls, not merely their individual existence. Otherwise, management may demonstrate that every department completed its task without demonstrating that the overall risk was addressed.
Resource commitments need an operational explanation
The Federal Reserve requires the board to ensure senior management has adequate resources for required remediation. Make that discussion more useful than a comparison of this year’s compliance budget with last year’s. You should perform a capacity assessment for each critical control. Identify the workload, expertise, systems, quality-review capacity, and unresolved dependencies. Where management proposes automation, require evidence that the tool handles the relevant risk and that someone owns exceptions.
The DOJ’s 2024 ECCP provides a useful cross-check: evaluate program design, resources and authority, and effectiveness in practice. Its resource analysis should also examine personnel qualifications and compliance’s access to the board.
A board paper should therefore explain what a resource request will accomplish and what risk remains without it. Ask management to identify work that cannot be completed to the required standard, rather than presenting an unexplained staffing total.
Accountability must survive changes in personnel
Paragraph 4 of the Federal Reserve order deserves careful attention. Based on the firm’s investigative record compiled from 2024 to the order’s issuance, it prohibits the firm from directly or indirectly retaining individuals who meet all three specified conditions: participation in the underlying misconduct, formal disciplinary action connected to it, and separation or legal termination connected to that misconduct. The restriction covers retention as an officer, employee, agent, consultant, or contractor within the firm or its subsidiaries or affiliates.
This is not a blanket prohibition covering everyone who was investigated. The conditions are cumulative. The order also requires continued cooperation and substantial assistance with Federal Reserve investigations of parties affiliated with the involved institution.
For other CCOs, the lesson is to connect substantiated investigation outcomes with hiring, contracting, and vendor controls. Subject to applicable employment and privacy requirements, test whether a person excluded through one channel could return through another. Require documented review rather than allowing a change in job title or engagement structure to bypass accountability.
Remediation requires evidence, not just a timetable
The Federal Reserve requires implementation timelines with specific component deadlines. Approved plans must be adopted within ten days of approval and then promptly implemented. Amendments or rescissions require prior approval from the Reserve Bank. Board or authorized committee progress reports are due within 45 days after the end of the first full calendar quarter following the order and each quarter thereafter, addressing actions, schedules, and results. The 90-day submissions are plan deadlines, not requirements to complete every remediation measure within 90 days. For your program, distinguish a completed task from a corrected risk. A revised procedure is a deliverable. Evidence that employees apply it correctly is a different milestone.
The ECCP similarly examines root-cause analysis, control testing, lessons learned, and whether improvements can prevent or detect similar misconduct. The ECCP asks, “What methodology has the company used to identify, analyze, and address the particular risks it faces? What features of the company reduce its exposure to such risks? Is the company’s approach to risk management proactive or reactive? What information has the company identified and collected to help detect the type of misconduct in question? How has that information informed the company’s compliance program?” Use those questions to challenge proposed closure evidence.
The bottom line is that you must demonstrate implementation and an appropriately independent reviewer to evaluate operating effectiveness. Define the testing period, evidence, and acceptable results before the item is marked complete.
CCO actions and board questions
- For the CCO: build one end-to-end evidence trail. Select a material risk and connect the assessment, controls, information, decisions, escalation, testing, and corrective action. Identify exactly where evidence is missing.
- For the board: challenge ownership and capability. Which executive owns the unresolved risk? What resources are missing? What decision does management need from directors now?
- For both: define success before declaring completion. What independent evidence supports closure? Have the underlying causes been addressed? What would alert us that the problem has returned?
Summary
The bottom line is that a compliance program must reflect the business’s actual risks and demonstrate that its controls work. The OCC’s central finding was a mismatch between the bank’s risk assessment and its operations: the assessment emphasized relatively narrow deposit activities while inadequately addressing dominant credit and charge card products. Weak customer identification, due diligence, suspicious activity reporting, independent testing, staffing, and job-specific training compounded that failure.
AMEX processed about $13 billion in suspected trade-based money laundering activity between June 2014 and May 2025 without timely identifying and reporting its full scope. It carefully distinguishes those findings from a conclusion that AMEX itself laundered that amount. The broader lesson is that completing assessments, filing reports, and delivering training do not, by themselves, establish program effectiveness.
We next considered the shift from compliance failures to governance and remediation, emphasizing that directors must oversee the work while senior management remains accountable for execution. Remediation should have identifiable executive and business owners, adequate resources, clear completion criteria, and independent review, rather than becoming an undefined assignment for the compliance department.
Drawing on COSO’s Internal Control Framework and the DOJ’s Evaluation of Corporate Compliance Programs, we reviewed how risk assessments, controls, information, escalation, and monitoring work together, and whether personnel and systems can perform the required work. The practical message for CCOs and boards is to distinguish a completed task from a corrected risk: a revised procedure is not proof of effective remediation. Leaders should require evidence that underlying causes have been addressed, controls operate effectively, and recurring problems will be detected. Risk alignment, accountability, and demonstrated effectiveness must become part of how the business is governed.