Categories
FCPA Compliance Report

FCPA Compliance Report: From Prosecutor to White Collar Lawyer to CCO and Back: Mike Koenig

In this episode, Tom Fox welcomes Mike Koenig to talk about his career and his recent move back to private practice after a 5-year stint at JBS. Mike is one of the few folks to move from private practice to an in-house CCO role, then back to private practice.

Mike began by reviewing his career, from 25 years in private practice and a 2003 DOJ Fraud Section stint prosecuting corporate fraud to becoming chief compliance officer at JBS in August 2021 amid DOJ and SEC settlement agreements requiring an effective compliance program. He describes learning to operate within business-driven priorities by building relationships, learning the business and culture, “educating not dictating,” and securing C-suite, board, and audit committee buy-in, including CEO-driven training completion. He explains that he uses trusted outside experts and focuses on the specific problem to solve rather than “boiling the ocean.” After JBS completed the settlements and listed on the NYSE in June 2025, he returned to private practice at Friedman Kaplan to advise on investigations and compliance, emphasizing concise, solution-oriented counsel. He warns against de-prioritizing compliance despite reduced enforcement, urges risk assessments (tariffs, export controls, and human rights), and recommends using DOJ compliance guidance to review programs.

Key highlights:

  • Career Journey Recap
  • Joining JBS In-House
  • Building Compliance Fast
  • Relationships Not Dictates
  • Leadership Buy-In
  • FCPA Pause or a Wake-Up Call
  • Compliance Through 2030

Resources:

Mike Koenig on LinkedIn

Mike Koenig at Friedman Kaplan

Friedman Kaplan

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

This week only, the Kindle e-book version is available for $0.99 on Amazon.

Categories
Blog

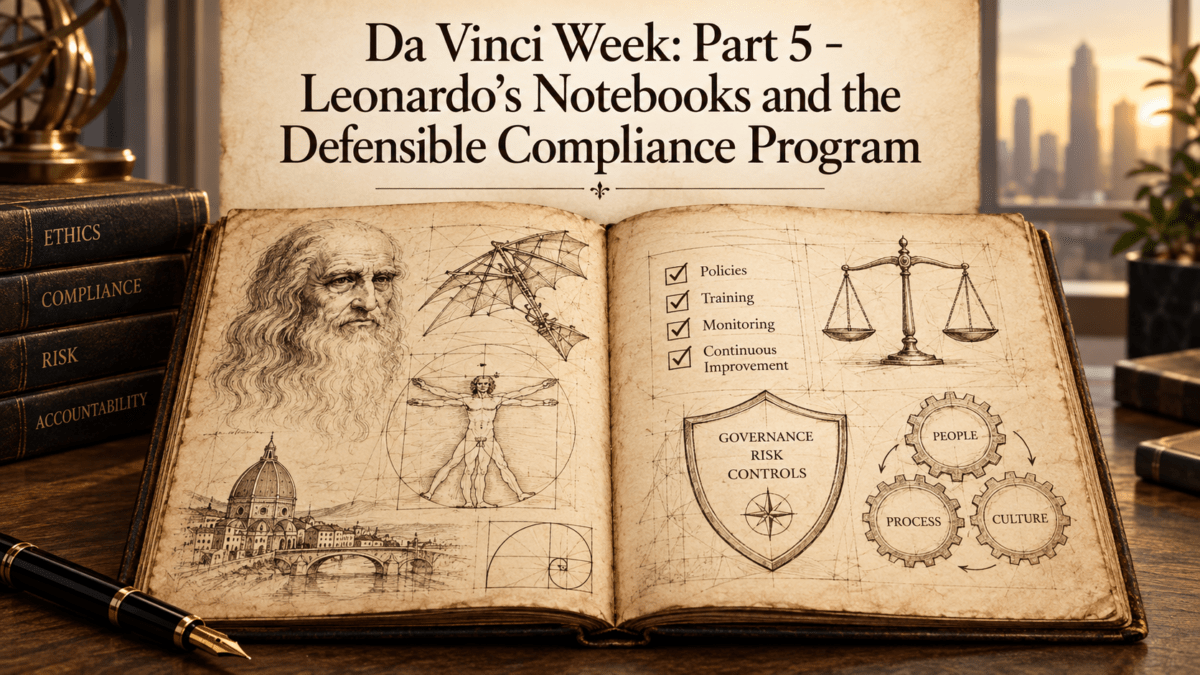
Da Vinci Week: Part 5 – Leonardo’s Notebooks and the Defensible Compliance Program

In the first four posts in the Leonardo Compliance Framework, we used Leonardo’s work to explore the compliance disciplines of Refine, Investigate, Innovate, and Monitor.  For our final blog post, the lesson comes not from a single Leonardo masterpiece but from the extraordinary collection of notebooks he created throughout his life. Leonardo recorded observations about anatomy, engineering, mechanics, water, optics, mathematics, architecture, flight, weapons, and the natural world. He drew machines, recorded experiments, posed questions, explored ideas, and returned repeatedly to subjects that interested him.

The compliance lesson goes beyond good note-taking. Leonardo externalized knowledge. He created a record of observations, ideas, questions, and reasoning that otherwise would have existed only in his mind. Modern corporations face a similar challenge. A CCO may understand why a particular control exists. An investigator may remember why an inquiry was expanded. A regional compliance officer may know why a distributor received enhanced scrutiny. An audit committee may understand why management accepted a particular residual risk. An AI governance committee may know why it approved a particular use case with specific limitations.

Then people leave, responsibilities change, businesses are reorganized, and memories fade. The policy remains, but the reasoning disappears. That is why documentation should be viewed as a component of compliance governance rather than simply an administrative obligation.

If It Is Not Documented, the Organization May Not Know It

Compliance professionals know the maxim that if something is not documented, it did not happen. That formulation can be overly simplistic, but it points toward a genuine problem. Organizations often know more than their systems preserve.

Consider a high-risk distributor approved five years ago. The compliance file may contain due diligence reports, certifications, contractual provisions, and an approval. Yet the people involved may have known far more. They may have discussed a government relationship, considered terminating the proposed engagement, obtained additional information, imposed enhanced controls, and ultimately concluded that the residual risk was manageable.

If the file contains only the final approval, a future reviewer may know what the company decided without understanding why. That distinction matters. Good compliance documentation should preserve significant reasoning, not simply outcomes.

This does not mean every routine decision requires a lengthy memorandum. Documentation should remain proportional to risk. A routine low-risk approval may require little explanation. A significant exception involving elevated corruption risk, a senior executive, a sensitive investigation, or a consequential AI application may warrant considerably more.

Risk-based documentation is part of a defensible compliance program.

Documentation Creates Institutional Memory

One of the most significant vulnerabilities in many compliance programs is the concentration of institutional knowledge in particular individuals. Every organization has employees who know why things work the way they do.

A longtime compliance officer remembers why a control was implemented after an investigation. An internal audit executive understands why a particular business unit receives enhanced testing. A finance employee knows why payments to a particular category of third parties require additional approval. An investigator remembers a series of cases that revealed a recurring management problem.

That knowledge has value. A new CCO should be able to understand why major components of the program exist. A new audit committee chair should understand significant unresolved compliance risks. A new investigator should be able to identify relevant historical matters. A new control owner should understand what problem the control was designed to address. Institutional memory should belong to the institution.

Documentation Supports Accountability

Clear documentation also helps answer one of the most important questions in corporate governance: who decided?

Organizations make thousands of decisions involving compliance risk. Most are routine. Some are consequential.

When a significant risk is accepted, the company should be able to identify the person or governance body with authority to accept it.

This is particularly important for exceptions.

If a high-risk third party is approved despite significant red flags, who approved the relationship? If an investigation involving a senior executive is narrowed, who authorized the scope change? If a remediation deadline is extended, who approved the extension and what interim controls are operating? If an AI system is permitted to influence consequential decisions, who approved the use case and under what conditions?

These are governance questions.

Documentation creates a decision trail.

That trail allows management, internal audit, the board, and, when necessary, regulators or enforcement authorities to understand how the organization exercised judgment.

A defensible compliance program does not require perfect decisions. Business decisions involve uncertainty.

It should, however, be able to demonstrate that significant decisions were made through an appropriate process by people with the authority and information necessary to make them.

Remediation Requires Evidence

The Michelangelo series emphasized the difference between closing a project and solving the underlying problem. Leonardo’s notebooks add another dimension: the organization should preserve evidence of what it changed and why.

Suppose an investigation identifies weak approval controls over distributor discounts. Management agrees to remediate the issue by modifying system permissions and requiring additional review.

The compliance record should identify the deficiency, remediation owner, planned corrective action, expected completion date, and evidence required for closure. When management reports that remediation is complete, the record should support that conclusion.

Was the system actually modified? Were users informed? Did testing confirm that the revised control operates as intended? Were similar vulnerabilities evaluated elsewhere? This creates a defensible chain from problem to solution.

Finding → Root Cause → Remediation → Ownership → Validation → Closure

That chain matters to the CCO because it shows compliance findings lead to management action. Internal Audit values it because it supports assurance. It is valuable to the board because it provides evidence that identified risks are being addressed. Documentation converts remediation from a promise into an accountable process.

AI Makes Documentation More Important

Artificial intelligence may make the documentation principle more important than ever in the modern compliance program. AI governance involves decisions that may be difficult to reconstruct after the fact if they are not documented when made.

A company evaluating a significant AI use case should preserve enough information to understand the system’s intended purpose, business owner, risk classification, relevant data, identified risks, testing, required controls, human oversight, approval conditions, and monitoring expectations.

The record should also reflect material changes.

An AI application approved as a low-risk productivity tool may later gain access to sensitive internal data. A vendor may change the underlying model. A system may become integrated into a consequential business process. An application initially used to recommend actions may eventually be authorized to take them. The governance record should evolve with the system.

This matters because AI can complicate traditional assumptions about decision-making. When a human employee makes a decision, organizations generally know who made it. When an AI system influences or takes an action, accountability can become less obvious.

Documentation should prevent that ambiguity from becoming an accountability gap. The company should be able to reconstruct what the system was authorized to do, who approved that authority, what controls applied, and who was responsible for monitoring its operation.

NIST AI RMF and ISO/IEC 42001 both reinforce the broader value of structured governance, risk management, documentation, monitoring, and continuous improvement. For the CCO, the important point is not simply alignment with a framework. It is the ability to demonstrate how the organization governed the technology in practice.

Documentation Should Feed Organizational Learning

Documentation becomes most valuable when the organization uses it. Investigation records can reveal recurring root causes. Exception records can identify controls employees routinely struggle to follow. Third-party approval records can reveal recurring risk patterns. Remediation documentation can show which corrective actions are effective. AI governance records can identify use cases generating repeated incidents or overrides.

The organization can analyze these records to improve the compliance program. This closes the loop between all five Leonardo principles.

  • Documentation captures what monitoring reveals.
  • Monitoring identifies issues requiring investigation.
  • Investigations generate lessons that drive refinement.
  • Refinement can support responsible innovation.
  • Innovation creates new risks that require monitoring and documentation.

The framework is therefore not linear. It is a learning cycle. That is perhaps the most important Leonardo lesson for the modern CCO.

Completing the Leonardo Compliance Framework

With Leonardo’s notebooks, we complete our five-part framework:

Refine-> Investigate-> Innovate-> Monitor-> Document

Together, these principles describe compliance as an organizational learning system. Effective programs learn from experience, investigate failures to understand root causes, support innovation within appropriate governance, monitor whether controls continue to work, and preserve what the organization learns so that knowledge informs future decisions.

The Mona Lisa taught us to Refine. Compliance programs should improve because organizations learn from experience, changing risks, investigations, employee feedback, and data. Leonardo’s anatomical studies taught us to Investigate. Misconduct should be examined beneath the surface so the organization understands root causes, control failures, incentives, management behavior, and systemic vulnerabilities. His flying machines taught us to Innovate. Compliance should help the company capture the value of emerging technology while maintaining risk-based governance, meaningful human oversight, and clear accountability. The Last Supper taught us to Monitor. Controls can deteriorate as the environment changes, making testing, analytics, ownership, remediation, and continuing oversight essential to program effectiveness. Leonardo’s notebooks teach us to Document.

That provides the essential contrast with Michelangelo. His framework of Challenge, Execute, Defend, Build, and Govern taught a CCO how to construct and operate an effective compliance program. Leonardo teaches a CCO how to keep that program learning and adapting. The modern compliance function needs both disciplines because strong controls can become obsolete if the organization fails to recognize changes in its business, technology, and risk environment.

That combination matters even more in 2026. AI is accelerating business change, geopolitical developments can rapidly alter risk, third-party ecosystems continue to expand, and boards need evidence that compliance systems work in practice. The CCO cannot administer yesterday’s compliance program while the business builds tomorrow’s operating model.

Leonardo’s notebooks leave us with a simple compliance mandate: learn from what the organization does, preserve what it learns, and use that knowledge to make the organization better.

Categories
Blog

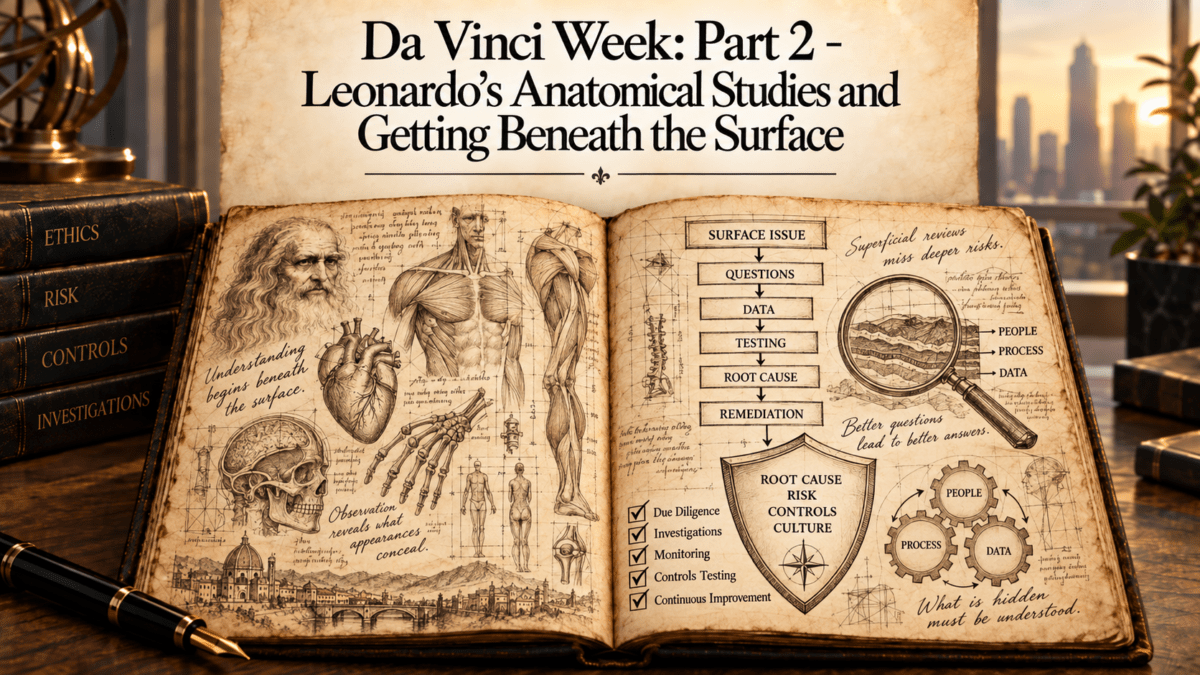
Da Vinci Week: Part 2 – Leonardo’s Anatomical Studies and Getting Beneath the Surface

In the first post in our Leonardo Compliance Framework, the Mona Lisa introduced Refine: the discipline of continuous improvement. An effective compliance program should learn from investigations, monitoring, risk assessments, employee feedback, control failures, and business changes. The program should evolve because the organization knows more today than it knew yesterday. That brings us to the second principle: investigate.

Leonardo was not satisfied with observing the human body from the outside. His anatomical studies examined muscles, bones, organs, movement, and the relationships among different parts of the body because he wanted to understand how the entire system worked. That provides a useful model for the modern Chief Compliance Officer because an effective corporate investigation should accomplish more than determine whether an employee violated a policy. It should help the organization understand why the conduct occurred, which controls failed, what incentives influenced behavior, whether management contributed to the problem, whether similar conditions exist elsewhere, and what should change as a result.

The compliance lesson from Leonardo is to look beneath the visible misconduct and understand the system that produced it.

An Investigation Is More Than a Search for Misconduct

Consider a familiar scenario. An investigation establishes that a sales employee used a consultant to make an improper payment to secure business. The company confirms the misconduct, terminates the employee and consultant, documents the findings, and closes the matter.

That process may answer the immediate legal and disciplinary questions, but it does not necessarily answer the larger compliance question. The company should also understand why it hired the consultant, how it approved the relationship, what due diligence it performed, whether it identified red flags, how it compensated the consultant, and how the resulting invoices and payments moved through the organization. Management should consider whether commercial incentives contributed to the conduct, whether supervisors encountered warning signs, and whether similar consultants are being used elsewhere.

If the company concludes only that one employee violated the anti-corruption policy, it may remove the individual while leaving intact the conditions that allowed the misconduct to occur. The investigation has then addressed the actor without addressing the vulnerability. That is why investigations should be viewed as a source of organizational intelligence.

Root Cause Should Drive Remediation

Root-cause analysis is where Leonardo’s anatomical method becomes particularly relevant. The objective is to move from the visible event to the systems underneath it. The Evaluation of Corporate Compliance Program (ECCP) states, “Finally, a hallmark of a compliance program that is working effectively in practice is the extent to which a company can conduct a thoughtful root.” It asks: What is the company’s root cause analysis of the misconduct at issue? Were any systemic issues identified? Who in the company was involved in making the analysis?

Root-cause analysis helps the company distinguish symptoms from causes, and that distinction should determine remediation. A response directed only at the visible misconduct may create the appearance of action without materially reducing the underlying risk.

This is also why significant investigations should test assumptions about the compliance program. If an intermediary engages in misconduct despite passing third-party due diligence, the company should examine whether the process missed information it reasonably could have identified. If an employee disguises improper payments, Compliance and Finance should understand how the relevant financial controls were circumvented. If retaliation occurs after an employee raises a concern, the organization should determine whether its anti-retaliation controls function in practice.

A well-designed compliance program can still experience misconduct. No reasonable system eliminates all risk. Effectiveness is measured by how the organization detects misconduct, responds, learns from failures, and strengthens the program when it identifies weaknesses.

Follow the Decision Trail

Investigators naturally follow evidence by reviewing documents, interviewing witnesses, analyzing transactions, and reconstructing events. Compliance investigations should also follow the decision trail because misconduct frequently passes through business processes designed to create accountability.

The investigation should identify who selected and approved a problematic third party, who authorized exceptions or unusual compensation, who approved payments, who received warnings, and who decided whether concerns warranted escalation. This becomes especially important when misconduct involves senior personnel, high performers, or commercially significant relationships.

The purpose is not to assign blame indiscriminately across every function connected to an incident. It is to understand where accountability actually resided and whether the people responsible for operating or supervising controls fulfilled those responsibilities.

A decision trail can reveal that misconduct was not simply the act of one individual. Other employees may have facilitated the conduct, ignored warning signs, approved questionable transactions, or failed to escalate information. Conversely, the evidence may demonstrate that established controls operated appropriately and that the individual deliberately circumvented them.

Organizational Justice Requires Consistency

Investigations also play a central role in corporate culture. Employees watch how organizations respond to allegations, particularly when cases involve senior executives or high-performing employees. They notice whether powerful people receive different treatment and whether employees who raise concerns suffer professional consequences. This makes consistency an important component of organizational justice, which the ECCP identifies as a part of every compliance program.

Consistency does not require identical outcomes. Facts, intent, responsibilities, prior conduct, cooperation, supervisory duties, and other legitimate considerations can justify different consequences. What matters is that the organization uses a credible process and applies its standards without creating privileged classes of employees.

Investigation governance is therefore important. The company should establish clear decision rights concerning whether allegations require investigation, who determines scope, who approves closure, how disciplinary decisions are made, when conflicts of interest require independent handling, and when matters involving senior executives should be escalated to the Audit Committee or board. These governance arrangements should be in place before a sensitive case arises.

Accountability should also extend beyond the individual who directly engaged in misconduct. Management behavior matters. A supervisor who ignored repeated warning signs, encouraged excessive risk-taking, approved unjustified exceptions, or created incentives that contributed to misconduct may raise separate accountability issues.

If employees see junior personnel disciplined while supervisors face no consequences for meaningful oversight failures, the company may signal that accountability flows only downward. Credible organizational justice requires a more consistent approach.

Investigation Data Is Enterprise Risk Intelligence

Individual investigations explain specific events. Aggregated investigation data can reveal enterprise-wide patterns, making it an important compliance asset. A CCO must understand which allegations recur, whether particular business units or managers appear repeatedly, where investigations are delayed, what root causes occur most often, whether similar control failures appear across jurisdictions, and whether employees who raise concerns subsequently experience unusual turnover or other adverse outcomes.

Those patterns can identify emerging risks that individual case files may not reveal. The data must be interpreted carefully. A business unit with a high number of hotline reports may have significant cultural problems, or it may have a healthy speak-up environment in which employees trust the reporting system. A location with few reports may have an excellent culture, or employees may fear retaliation.

Investigation data works best when combined with other information, including hotline trends, employee surveys, HR data, audit findings, transaction monitoring, exit interviews, and business knowledge. The objective is not simply to count cases but to use investigative information to understand the organization more effectively. This is the Leonardo approach in practice: observation combined with inquiry.

AI Changes the Investigation Function

Artificial intelligence is also changing corporate investigations. AI tools may assist with document review, chronology development, translation, pattern identification, data analysis, and summarization. Used appropriately, these capabilities may allow investigation teams to analyze larger volumes of information and identify relationships more efficiently.

They also create significant governance issues because investigations frequently involve some of the company’s most sensitive information. Before using AI, the organization should understand what data it will provide to the system, whether the material includes privileged, confidential, personal, or commercially sensitive information, where the data will be processed and retained, and what contractual and technical protections apply. Once again, the ECCP puts this onus on your compliance function.

Reliability is equally important. Investigators need a process to validate AI-assisted analysis and identify inaccurate or unsupported outputs. AI use should not obscure how a significant investigative conclusion was reached or prevent the company from explaining the evidence supporting its decision.

Human accountability should remain clear. AI can assist investigators, but it should not replace professional judgment concerning scope, credibility, findings, discipline, or remediation. The broader governance principles reflected in the NIST AI Risk Management Framework and ISO/IEC 42001 can help organizations think about risk management, human oversight, documentation, and monitoring. Still, the fundamental investigation requirements remain confidentiality, accuracy, fairness, privilege, and defensibility.

Connect Investigations to Remediation and Lessons Learned

Companies sometimes separate investigations and remediation too sharply. Legitimate reasons exist to maintain appropriate independence between fact-finding and certain management decisions, but the compliance program still needs a clear mechanism to convert investigative findings into corrective action.

For significant matters, management should understand what failed, why it failed, whether the weakness could exist elsewhere, what corrective action is required, who owns that action, and how the company will determine whether remediation worked. This turns an investigation from a historical examination into a forward-looking compliance tool. Without that connection, an organization can become highly proficient at investigating the same problem repeatedly without becoming better at preventing it.

Lessons learned should also travel beyond the specific business unit or jurisdiction involved. If an investigation in one market identifies improper distributor discounts caused partly by weak approval controls, the company should consider whether comparable controls exist elsewhere. If employees use personal messaging applications to circumvent company systems, management should assess whether the practice extends beyond the employees involved in the investigation. If an AI incident reveals that employees can deploy unapproved tools without effective technical restrictions, the organization should consider the broader governance implications.

This does not require distributing confidential investigative details throughout the company. It means converting case-specific findings into enterprise risk intelligence. Depending on the issue, the lesson may lead to changes in controls, risk assessments, monitoring, training, policies, management communications, or incentive structures. That is how Investigate feeds Refine.

What the Board Should Understand About Investigations

Boards and Audit Committees should resist evaluating the investigation function primarily through case counts. Knowing how many matters were opened and closed provides useful operational information, but it offers limited insight into program effectiveness.

Directors should understand what the company is learning from investigations. Significant themes, recurring root causes, internal control weaknesses, unusual patterns across business units, retaliation concerns, and the status and effectiveness of remediation all provide more meaningful information about compliance risk.

The board should also understand whether investigative resources match the company’s risk profile. Significant cases should not remain unresolved because the organization lacks appropriate staffing, cross-border expertise, data capabilities, employment-law support, or access to information. Matters involving senior personnel should be handled through processes designed to preserve independence and avoid conflicts.

The board does not need to manage individual investigations. Its role is to understand whether the investigation system provides reliable information about significant compliance risks and whether management responds appropriately to what that system reveals.

Getting Beneath the Surface

Leonardo’s anatomical studies give compliance professionals a useful model for investigations because the visible event may be only the first indication of a larger systemic issue. An improper payment may reveal a third-party weakness that exposes deficiencies in due diligence, technology, ownership, incentives, or management oversight.

The investigator’s task is to understand those connections without allowing every matter to become an unlimited enterprise-wide inquiry. Scope should remain proportionate to the seriousness, complexity, and potential reach of the issue. The objective is disciplined curiosity: understanding whether the evidence points to an isolated act or a broader weakness in the compliance system.

For the CCO, the practical lesson is that investigations should do more than establish whether a rule was violated. Significant matters should help the organization understand the controls, incentives, management decisions, and business conditions that contributed to the conduct. Root-cause analysis should drive remediation, investigation findings should test assumptions about program effectiveness, aggregated case data should inform enterprise risk assessment, and lessons learned should improve controls beyond the immediate matter.

That is Investigate, the second principle of the Leonardo Compliance Framework. Finding misconduct matters, but the greater compliance value comes from understanding the system that produced it and using that knowledge to reduce the likelihood of recurrence.

From Investigation to Innovation

Investigation helps the compliance professional understand how existing systems work and why they sometimes fail. Leonardo, however, was equally interested in systems that did not yet exist, which takes us to the third principle in the Leonardo Compliance Framework: Innovate.

In Blog Post Three, Leonardo’s Flying Machines and AI Governance, we will use Leonardo’s studies of flight to examine responsible innovation in 2026. Artificial intelligence and increasingly agentic technologies are moving from generating information to taking action within business processes, raising new questions about risk classification, human accountability, third-party AI, data governance, testing, monitoring, NIST AI RMF, and ISO/IEC 42001.

Leonardo’s willingness to imagine flight provides the innovation lesson. For the modern CCO, the corresponding governance task is ensuring the enterprise understands the risks, controls, and accountability needed before giving new technology meaningful authority inside the business.

Categories
Blog

When an Effective CCO Is Labeled Difficult

A business leader calls a Chief Compliance Officer (CCO) difficult after a proposed distributor fails to provide basic ownership information. The transaction is important to the quarter. The CCO has asked for the missing information, explained the concern, and identified what is needed to proceed. In the performance discussion that follows, the focus shifts to whether the CCO understands the business.

This hypothetical presents a governance question. Did the CCO handle the matter poorly, or did an appropriate challenge expose a business practice management would prefer to leave alone? The answer requires evidence about the decision, the CCO’s conduct, and the operating environment. A label provides none of that.

Luis Velasquez examines this diagnostic problem in Why Effective Leaders Get Branded as Problems, published in Harvard Business Review. He identifies four sources of leadership friction: genuine skill deficits, historical reputation, overextension of a leadership strength, and organizational barriers. His framework provides a useful starting point for evaluating CCO effectiveness while protecting the independence necessary to perform the role. The compliance applications below build on his analysis.

Diagnose the Conflict Before Evaluating a CCO

Velasquez describes an evaluation trap in which organizations treat visible behavior as the explanation for friction while giving insufficient attention to context. Once a leader acquires a negative reputation, subsequent assessments can reinforce it without testing whether the original diagnosis was sound.

For compliance, this creates a particular risk. A CCO’s responsibilities include raising concerns that may complicate a transaction, challenge an executive, or require management to change an established practice. Friction can arise while the function is doing its job. It can also arise when compliance communicates poorly, applies inconsistent standards, or takes too long to decide. An effective evaluation must examine both possibilities.

Start with the event behind the criticism. What decision was required? What information was available? What did the compliance request say, when, and why? What alternatives did a CCO identify? Which actions by the business affected the outcome? These questions create a basis for assessing performance without assuming the conclusion.

Address Genuine Skill Gaps Directly

Velasquez’s first category recognizes that leaders sometimes lack a necessary capability. Applied to CCOs, relevant gaps may include unclear communication, weak prioritization, insufficient business knowledge, or ineffective delegation. Consider a CCO who repeatedly sends lengthy technical explanations without identifying the decision management must make. Executives may reasonably struggle to act on the advice. Similarly, a compliance team that treats every request as equally urgent can consume resources while delaying matters that warrant immediate attention.

Those are legitimate performance concerns when supported by recent examples and a clear account of their consequences. Agree on the improvement required, provide support, and assess the result. Independence does not excuse disrespectful conduct, poor execution, or unsupported recommendations. It gives a CCO room to exercise judgment while remaining accountable for the work’s quality and delivery. A sound review evaluates whether a CCO explains concerns clearly and helps the business identify acceptable ways forward where they exist.

Replace Old Reputation With Current Evidence

Velasquez’s second category concerns historical reputation. A leader may change while the organization still relies on an outdated account of how that person operates. A CCO who joined during a serious control failure may initially have imposed tight review requirements. Years later, colleagues may still describe the function as inflexible even after it has introduced clearer thresholds, delegated decisions, and improved turnaround times.

The evaluation process should test whether the criticism reflects current experience. Ask for specific recent interactions, the applicable requirements, and the outcome. Compare those accounts with evidence of how the process now works. Older incidents may remain relevant, but explain their continued significance rather than assume it.

A CCO can contribute by demonstrating improvement through current service measures, examples of resolved issues, and feedback from people who use the process. The objective is an accurate assessment. Favorable anecdotes alone are no more sufficient than a repeated negative label.

Recognize When a Strength Needs a Different Application

Velasquez distinguishes a missing skill from a strength used too broadly. That distinction matters for a compliance leader whose career has rewarded detailed review and personal control of important decisions. Those habits may help stabilize a troubled program. As the business grows, the same approach can create bottlenecks if routine matters still require a CCO’s personal involvement. The leader needs to develop the team and establish clear decision authority while retaining appropriate escalation for significant concerns.

The response should specify where judgment can be delegated, what standards apply, and how quality will be checked. This preserves the value of careful review while changing how it is delivered. A CCO should be willing to examine this possibility candidly. A complaint about delay may reveal poor business planning, an overly centralized compliance process, or both. Correcting one cause does not remove the need to address the other.

Examine Whether the Organization Undermines the Role

Velasquez’s fourth category addresses organizational barriers involving culture, resources, incentives, and decision rights. This is where the implications for compliance independence become particularly significant.

A company may require review before engaging a third party while rewarding executives who commit to start dates before review begins. It may expect timely investigations while restricting access to relevant records. It may ask a CCO to escalate serious concerns and then criticize the escalation as a failure to collaborate.

In each case, evaluate the contradiction alongside a CCO’s response. Coaching the leader to communicate more effectively may help, but it cannot supply missing authority or correct an incentive that rewards bypassing controls. A CCO should document the constraint, its practical consequences, and the proposed correction. Management should identify who will resolve it and by when. Repeated, material barriers belong in discussions with the responsible board committee, particularly when they prevent the function from carrying out agreed responsibilities.

Make Board Support Concrete

Board support for a CCO should be visible in the governance process. Directors need access to an account of significant compliance concerns that explains the facts, management’s response, and any unresolved differences. The responsible committee should also understand the basis for material criticism of a CCO’s performance. Where criticism arises from an executive whose conduct or decisions compliance has challenged, that context warrants examination. It does not automatically invalidate the criticism or establish retaliation.

An appropriately independent review should consider the substance of the concern, how it was raised, and the evidence behind any proposed personnel action. Human resources, legal, and the relevant board leadership should have clear roles consistent with the company’s governance arrangements. Regular private discussions between a CCO and ELT leadership (or the appropriate board committee) can help surface barriers before a performance dispute becomes entrenched. Directors should ask whether compliance has the access, resources, and authority needed to deliver what management expects.

Evaluate Effectiveness With Measures That Fit the Role

An evaluation based heavily on executive satisfaction can discourage necessary challenge. A review based solely on activity counts provides an equally incomplete picture. Assess the quality and timeliness of advice, the prioritization of risk, the development of the team, and the follow-through on significant issues. Consider whether recommendations are supported and whether remediation addresses the underlying problem. Business feedback remains useful when it is specific and examined in context.

The central discipline is to evaluate the work and its consequences. Agreement with management is not a reliable measure of effectiveness; disagreement alone does not demonstrate courage or sound judgment.

Action Steps for the CCO

Use Velasquez’s framework to improve how performance concerns are examined:

  1. Ask for specific evidence. Identify recent events, decisions, and consequences behind broad criticisms. Respond to substantiated concerns directly.
  2. Test all four explanations. Examine skill gaps, outdated reputation, overused strengths, and organizational constraints. Recognize that more than one may contribute.
  3. Agree on meaningful performance measures. Include advice quality, timeliness, prioritization, team capability, and remediation follow-through alongside contextualized business feedback.
  4. Document barriers to effective execution. Record missing resources, restricted access, conflicting incentives, or unclear authority, with proposed corrections and accountable owners.
  5. Establish a credible board review process. Clarify escalation and evaluation arrangements so significant concerns about a CCO and constraints on the role receive informed consideration.

Effective compliance leadership requires both sound judgment and the ability to make that judgment understood. Organizations strengthen accountability when they evaluate those capabilities fairly and address the conditions that prevent a CCO from using them.

Categories
Blog

Does Your Board Have the Expertise and Independence to Oversee Compliance

A board can have impressive credentials and still lack the experience needed to challenge management on the company’s most significant compliance risks. Directors may understand finance, strategy, and operations in broad terms while struggling to recognize how misconduct could arise within a particular business model. Effective oversight requires relevant knowledge and the willingness to use it when the answers become uncomfortable.

For the chief compliance officer, that makes board capability a practical program issue. The quality of oversight influences the questions management must answer, the resources compliance receives, and what happens when a concern conflicts with a commercial priority. Today we examine board composition in the article Measuring Board Fit — Evidence from Elliott’s Campaign at Norwegian Cruise Line, from the Harvard Law School Forum on Corporate Governance. Their analysis uses AI to compare directors’ professional backgrounds with company strategy and with one another. It offers a starting point for a broader compliance question: Does this board have the expertise and independent judgment to oversee the risks this company actually faces?

Look Beyond the Skills Matrix

DesJardine and Mertens argue that conventional skills matrices can conceal meaningful differences in experience. Two directors may receive the same designation for operations or risk management while bringing very different capabilities to the boardroom.

The compliance application is straightforward. A risk management designation should prompt further inquiry into the nature, relevance, and recency of that experience. Has the director overseen a business using intermediaries in difficult markets? Has the director managed the integration of acquired companies? Examined an investigation involving senior leadership? Challenged a compensation structure that encouraged questionable conduct? No director needs to possess every capability. The board and its committees do need an informed basis for questioning management across the company’s priority risks.

The CCO can help define that basis. Translate the risk assessment into the experience and understanding needed for oversight. Where third-party conduct creates substantial exposure, explain the commercial relationships, payment practices, and escalation decisions directors need to understand. This gives the nominating and governance committee a more useful description than a generic request for compliance expertise.

Read the Norwegian Findings Carefully

The authors apply their method to Norwegian Cruise Line Holdings before and after Elliott Investment Management’s campaign, comparing its board with those of three cruise industry peers. They report that the company’s board-to-company similarity score increased from 0.382 to 0.396 following the changes. Average director-to-board similarity declined from 0.729 to 0.701, which they interpret as more distinct professional perspectives.

Those results describe changes in the authors’ measures of professional alignment and overlap. They do not establish that the reconstituted board became more effective at compliance oversight, that individual directors exercised greater independence, or that misconduct risk declined. That distinction matters for CCOs. An assessment can identify questions about composition without answering how directors perform. A board with relevant backgrounds still needs reliable information, sufficient time, and the resolve to follow an issue through. The practical response is to combine an examination of credentials with evidence of the board’s oversight process.

Examine Independence Through the Oversight Process

The authors acknowledge that their method cannot assess integrity, interpersonal skills, or willingness to challenge a chief executive. Those limitations point directly to the independent judgment compliance oversight requires. Consider a hypothetical board discussion about a distributor generating substantial revenue while repeatedly failing to provide requested ownership information. Management recommends extending the relationship during further review. A director with relevant experience may recognize how significant the missing information is. The next question is whether the board presses management to explain the proposed safeguards, decision authority, and consequences of continued delay.

The CCO should help create the conditions for that discussion. Present the facts, uncertainties, available options, and recommendation clearly. Identify who owns the decision and what would trigger escalation. Provide access to the underlying analysis where needed.

Direct access to the responsible committee and opportunities for discussion without management present can support candid oversight. Follow-up is equally important. An unresolved concern should return with updated evidence and a clear account of management’s actions. A difficult question has value when the governance process ensures it receives an adequate answer.

Make Expertise Usable Through Better Information

Even an experienced director can struggle with reports that emphasize activity while obscuring unresolved risk. Assess board capability and reporting quality together. A presentation may show that due diligence reviews are complete without explaining the exceptions approved. Investigation statistics may omit repeated issues within one business unit. Remediation updates may describe actions as finished without showing whether the revised controls work.

A CCO should organize reporting around decisions and consequences. Explain the issue, the evidence, management’s response, and what remains unresolved. When a commercial objective conflicts with a compliance recommendation, make that tension clear. Directors can then apply their experience to a concrete problem. Does the proposed response address the cause? Is the responsible executive accountable for delivery? What evidence will show that the correction is working? These questions help convert professional knowledge into oversight of program effectiveness.

Preserve Perspectives That Challenge Assumptions

The authors examine both alignment with company strategy and similarity among directors. That combination highlights a tension: a board needs relevant experience while retaining perspectives that question the organization’s assumptions. For compliance, industry familiarity can help a director spot questionable practices. It can also leave accepted business conventions insufficiently examined. Experience from another sector may expose weaknesses in customer treatment, escalation, or control ownership that insiders have normalized.

A CCO should therefore avoid equating a closely matched background with superior judgment. Ask what the board needs to understand and where a different perspective could improve its questions. Director education can help close specific knowledge gaps. Sessions built around the company’s actual processes, anonymized matters, and emerging business changes can give directors a better foundation for challenge. Persistent gaps may also warrant discussion of committee expertise or board recruitment, with those decisions remaining with the appropriate governance bodies.

Use AI Assessment as a Diagnostic Input

DesJardine and Mertens use contextualized word embeddings, a technique that turns text into numerical representations, to compare professional and company profiles. The approach can surface similarities that broad categories miss. For a board considering such analysis, the CCO and governance team should ask what information supports each profile and what the resulting score actually measures. Public biographies and media coverage provide an incomplete record of a director’s contributions. The volume and character of available material may differ substantially between candidates.

Company disclosures also describe the organization through a particular lens. Similarity to that description does not necessarily establish the expertise needed to address an overlooked risk or challenge an unsuccessful strategy. Use the output to inform interviews, reference discussions, and committee deliberations. Ask how sensitive the result is to source selection and whether the underlying evidence supports the interpretation. Record significant limitations. A numerical score should help the board investigate a capability question; appointment and evaluation decisions require accountable human judgment.

Action Steps for the CCO

Bring a practical assessment of oversight capability to the next discussion with the committee chair:

  1. Map priority risks to oversight knowledge. Identify what directors need to understand about the company’s business practices, controls, and escalation decisions.
  2. Provide evidence of capability gaps. Work with the corporate secretary and general counsel to inform education and composition discussions, using specific examples rather than broad labels.
  3. Strengthen the conditions for independent challenge. Establish clear access, candid reporting, and follow-up arrangements for unresolved concerns, including matters involving senior management.
  4. Test the usefulness of board reporting. Ensure directors can see material exceptions, recurring issues, remediation evidence, and decisions requiring their attention.
  5. Apply scrutiny to AI assessments. Examine source quality, missing information, and the limits of similarity measures before incorporating results into governance decisions.

Effective compliance oversight depends on directors who understand the company’s risks and are prepared to question how management addresses them. The CCO can strengthen that oversight by making capability needs explicit and ensuring the board receives the evidence needed to exercise its judgment.

Categories
Blog

Setting the Right Ambition for Your Compliance Strategic Plan

A compliance strategic plan should explain how the function will build the capabilities the business needs to manage its risks. That requires choices about priorities, resources, authority, and execution. A plan can fall short by asking the organization for too little. It can also promise more than the company is prepared to support.

Consider a CCO preparing a three-year plan while the company expands through acquisitions and new distribution channels. The proposed compliance plan calls for refreshed policies, additional training, and a new monitoring platform. Each initiative may be useful. But does the plan address the integration gaps and third-party decisions that expansion will create? And has anyone committed the people, data, and funding needed to deliver it?

Rebecca Knight explores the calibration of strategic ambition in “Is Your Strategic Plan Too Ambitious? Or Not Ambitious Enough? In the Harvard Business Review. Her article draws on insights from Columbia Business School’s Sheena Iyengar and MIT Sloan School of Management’s Donald Sull. Their discussion provides a useful foundation for examining the compliance function’s strategy. The compliance applications below build on that discussion.

Define the Problem Before Setting the Target

Knight begins with Iyengar’s advice to identify the problem a strategy must solve before debating the ambition of its targets. For CCOs, this discipline matters because familiar deliverables can substitute for a clear diagnosis. Take a goal to increase training hours. What problem requires that increase? Employees may misunderstand an approval requirement. They may understand it perfectly but lack a workable way to obtain approval before a commercial deadline. Those conditions require different responses.

The strategic plan should connect each major initiative to an identified weakness or emerging business need. If acquisitions repeatedly leave the company with incomplete third-party records, define the intended capability: an integration process that establishes ownership, identifies missing information, and escalates unresolved risks within a specified period. This gives management a concrete outcome to fund and the board a meaningful basis for oversight.

Develop Alternatives Before Committing Resources

Knight reports Iyengar’s recommendation to consider several distinct approaches so leaders can see their trade-offs. A CCO can apply this by requiring alternatives for the plan’s largest investments. Suppose the objective is better third-party monitoring. One option might strengthen existing reviews and accountability. Another might integrate procurement and payment data. A broader approach might redesign the third-party lifecycle, including who can engage an intermediary and what evidence permits renewal.

Compare the options against the actual problem, implementation demands, and expected improvement. A technology purchase may be appropriate, but its value depends on the process and information supporting it. This exercise also exposes insufficient ambition. If every option preserves the same fragmented ownership that created the problem, the CCO has reason to question whether the proposed change goes far enough. A major redesign also needs stronger justification than an attractive vision of a fully integrated program.

Make Resource Commitments Explicit

Sull’s resource argument, as Knight presents it, is that substantial strategic change can require moving money and talent away from existing commitments. That has direct implications for compliance planning. CCOs often describe new responsibilities without specifying which existing activities will change. A team already handling investigations, advice, training, and monitoring cannot absorb unlimited transformation work simply because the strategic plan assigns it a deadline.

For each major initiative, identify the required budget, expertise, business participation, and implementation time. Explain what can be simplified or discontinued and what must remain protected. Required controls and essential response capacity need explicit provision during the transition.

Dependencies deserve the same attention as the compliance budget. If success requires information technology support, procurement process changes, or finance data, obtain named owners and documented commitments. Where a critical commitment is missing, describe the resulting limitation in the proposal presented to leadership. Your board should be able to see the relationship between the approved ambition and the resources management has committed.

Build Capability Around the Business Strategy

Knight’s discussion of staffing emphasizes the expertise needed to execute a bold plan. Applied to compliance, the question extends beyond headcount to the capabilities the company’s direction requires. Acquisition-led growth may require stronger integration management. Expansion through distributors may require regional knowledge and commercial experience. A monitoring initiative may require data analysis, systems access, and people who understand how transactions occur.

Map the company’s major strategic moves to their compliance implications, then identify the skills and authority needed to respond. This helps the CCO explain why the function needs particular capabilities and when those capabilities must be available. Business alignment also requires independence of judgment. The plan should enable informed decisions about growth while preserving the CCO’s ability to challenge unsupported assumptions, escalate concerns, and identify conditions that should be met before proceeding. Management owns the commercial strategy; compliance must be equipped to assess and address its implications.

Use Pilots With Clear Decision Rules

Knight describes experimentation as a way to pursue ambitious goals while learning through smaller steps. A compliance plan can use that approach to improve processes and build new capabilities. For example, a proposed monitoring method could begin in one business unit. Before launch, define the information required, the existing controls that remain in place, the people responsible for reviewing results, and the conditions for expansion or revision.

The pilot should answer a specific question. Does the method identify relevant exceptions? Can the business resolve them? Are the results dependable enough to support decisions? A successful software demonstration alone does not answer those questions. Set a review date and a decision owner. Without those commitments, a pilot can continue indefinitely, consuming resources while providing little clarity about whether the broader strategic objective is achievable.

Measure Progress Toward a Working Capability

Knight connects a longer strategic horizon with measurable interim progress. This is particularly useful for compliance improvements that require changes across functions and systems. A multi-year goal to improve acquisition integration could include quarterly milestones for establishing ownership, validating acquired third-party records, addressing priority exceptions, and testing whether the revised process works on a subsequent acquisition.

Select measures that reveal both implementation and performance. Completing a procedure establishes that something was produced. Evidence that business teams use it, resolve exceptions, and escalate overdue actions helps show whether the capability is functioning.

Establish a baseline before claiming improvement. Faster review times need context about review quality. Fewer exceptions need context about detection coverage. Report limitations alongside results so management and directors can distinguish progress from incomplete information. The strategic plan should also specify when it will revisit assumptions. A major acquisition, a new business model, or a material change in available resources may require revised priorities and sequencing.

Give the Board Decisions It Can Assess

Board oversight becomes more useful when the CCO presents the choices behind the plan. Directors need to understand the priority problems, the proposed response, the resource commitments, and the consequences of delay.

A practical strategy discussion should explain what the function expects to accomplish, what depends on other executives, and what remains outside the funded scope. Where alternatives exist, show their implications for timing and capability. This gives the board a basis to challenge both overpromises and underinvestment. It also establishes what management should report back as the plan proceeds.

Action Steps for the CCO

Use the next planning review to test whether ambition and execution are aligned:

  1. Define the priority problems. State the business risk or capability gap behind each major initiative and the evidence supporting its priority.
  2. Compare credible alternatives. Examine different ways to achieve the intended outcome, including their costs, dependencies, and implementation demands.
  3. Secure resource commitments. Identify accountable business partners, required expertise, funding, and the activities that must change to make room for execution.
  4. Set milestones and decision points. Establish baselines, measures, pilot criteria, and dates for reassessing assumptions.
  5. Present the choices to the board. Explain the funded scope, unresolved dependencies, and consequences of deferring priority capabilities.

A sound compliance strategy makes a demanding but supportable commitment to improving how the company manages risk. The CCO’s responsibility is to make that commitment specific enough to execute, measure, and oversee.

Categories
Blog

When Employees Rationalize Misconduct: What CCOs Need to Change

A sales manager needs one more transaction to meet the quarterly target. The customer has not completed the required approvals, but the manager believes the paperwork will arrive tomorrow. Booking the sale today will protect the team’s bonus and keep the regional president satisfied. The manager tells herself that the transaction is real, the delay is administrative, and nobody will be harmed.

This hypothetical illustrates a problem every chief compliance officer should consider. An employee can understand a rule and still construct a convincing reason to disregard it. The compliance challenge includes recognizing the reasoning that makes a violation feel acceptable before the employee acts.

Todd Haugh examined that challenge in The Trouble With Corporate Compliance Programs, published in the Fall 2017 issue of MIT Sloan Management Review. Drawing on behavioral ethics and criminology, Haugh argued that compliance programs need to address how employees make ethical decisions and rationalize misconduct. His analysis laid the foundation for this discussion; the operational recommendations I adapted from his article apply that perspective to the CCO’s work.

Examine the Decision Behind the Violation

Compliance professionals devote substantial attention to policies, training, approvals, and investigations. Each has a role. Yet a completed training course tells us relatively little about how an employee will respond when a supervisor demands a result that appears impossible to achieve within the rules.

Haugh’s central contribution was treating rationalization as something that can precede misconduct and help enable it. (The same is true in the Fraud Triangle.) Drawing on criminological research, including Donald Cressey’s work, Haugh explained how people can make a breach of trust seem consistent with their view of themselves as good people.

For the CCO, this changes the inquiry. Alongside asking whether an employee knew the rule, ask what made bypassing it appear reasonable. Was the employee protecting a colleague? Responding to a threat of dismissal? Following a practice that managers had repeatedly accepted? Those questions can reveal weaknesses in supervision, incentives, escalation, and accountability. They also help explain why repeating the policy may leave the conditions behind a violation intact.

Recognize the Language of Rationalization

Haugh identified eight common rationalizations: denying responsibility, denying injury, denying the victim, condemning the condemners, appealing to higher loyalties, using a ledger metaphor, claiming entitlement, and claiming relative acceptability or normality.

Several relate directly to daily compliance work. An employee who says a supervisor left no choice may be denying responsibility. Someone who minimizes the consequences of an inaccurate record may be denying injury. A manager who defends a questionable payment as necessary to protect the business may be appealing to higher loyalties. An executive who invokes years of excellent performance to excuse a violation may be treating past contributions as credits against present misconduct.

The practical value of these categories lies in the questions they generate. When someone defends a practice as common across the industry, the CCO should explore how the company evaluates that practice and who has approved it. When loyalty to the business becomes the explanation, ask which business interest the conduct actually serves and what risks it creates.

Such statements warrant inquiry. They do not, by themselves, establish misconduct. A useful discussion must leave room for employees to describe pressure, uncertainty, and disagreement candidly.

Put Business Pressure Within the Compliance Review

Haugh discussed Wells Fargo’s sales practices as an example of how organizational pressure can overwhelm formal ethics messaging. In Haugh’s view, aggressive sales expectations helped create an environment in which employees could rationalize improper behavior despite instructions against it. The broader lesson for CCOs is to examine the operating conditions surrounding a control. A policy requiring approval has limited practical support if management consistently rewards employees who bypass the process to deliver faster results.

Consider a third-party onboarding process. The written procedure requires due diligence before engagement. The business promises the intermediary an immediate start date, procurement receives the request late, and the responsible employee is evaluated on speed. Compliance then encounters an urgent request for an exception.

The proposed response should reach beyond that individual exception. Who committed the company before review? Why did the planning process omit the approval period? Does management treat compliance review as part of the transaction schedule? Repeated urgency deserves examination as a management practice. The CCO should bring those findings to the business owner with a concrete correction, an accountable executive, and a timetable.

Practice the Conversation Employees Need to Have

Haugh recommended discussion and storytelling to help employees recognize rationalizations. This approach gives compliance training a useful operational purpose: rehearsing the conversation that must occur when commercial pressure and an ethical obligation collide. Use a scenario drawn from your organization’s actual work, with identifying details removed where necessary. Ask participants to explain the pressure, identify the affected parties, describe the proposed justification, and decide how they would respond. Then require a practical answer. Whom would the employee contact? Can the transaction pause? Who can authorize an alternative? What should the employee say to a manager who insists on proceeding?

Managers should participate because their response determines whether the proposed solution is credible. If the training encourages escalation but the supervisor treats questions as disloyalty, the employee receives conflicting instructions. The CCO can use these sessions to identify unclear responsibilities and impractical procedures. Training becomes a source of information about how work gets done, as well as an opportunity to explain expectations.

Connect Incentives and Accountability

Haugh also emphasized incentives and organizational culture. For compliance practitioners, the application is direct: examine the behaviors that receive recognition, promotion, and protection. A company may praise integrity while celebrating a commercial result without asking how it was achieved. A high performer may receive repeated exceptions unavailable to others. Employees can reasonably interpret those decisions as evidence of management’s priorities.

The CCO should work with human resources and business leadership to incorporate performance metrics into evaluations. Relevant evidence might include how a manager responds to concerns, handles approval requirements, and corrects recurring control failures. Recognition also has a role. With appropriate confidentiality, leadership can acknowledge a team that raised a concern early or found an acceptable way to complete a difficult transaction. The explanation should make it clear that the conduct is worth repeating.

Accountability must extend to supervisors whose instructions or tolerated practices contributed to a problem. Otherwise, remediation may remove an employee while preserving the management behavior that shaped the decision.

Give the Board Evidence About Behavior

Board reporting should help directors understand whether the program influences business decisions. Training completion and policy certifications provide useful coverage information. They need context from the company’s operating experience. A CCO might report recurring reasons for approval exceptions, examples of management responses to escalation, or repeated control failures concentrated within a business unit. Such information can help directors question whether performance expectations and compliance obligations are aligned.

Interpretation matters. More reported concerns could reflect greater trust in the reporting process. Fewer exceptions could reflect better planning or a failure to record deviations. Explain the evidence, its limitations, and the follow-up needed before presenting a conclusion about effectiveness.

Action Steps for the CCO

Haugh’s article challenged compliance leaders to take employee decision-making seriously. Turn that insight into a focused review:

  1. Review a sample of closed matters. Identify the justifications employees offered, the pressures they described, and management’s role. Look for recurring conditions across cases.
  2. Examine one business process. Select a process with frequent exceptions or urgent approvals. Determine where planning, incentives, or unclear authority encourage employees to bypass requirements.
  3. Run a manager-led scenario discussion. Practice recognizing rationalizations and responding to pressure. Record procedural gaps that prevent employees from taking the expected action.
  4. Assign corrective actions to business owners. Address the underlying workflow or management practice, with deadlines and evidence of completion.
  5. Report what changed. Show senior management and the board how the intervention affected decisions, exceptions, or recurring issues. Distinguish observed improvement from conclusions that still require evidence.

The CCO’s task is to make ethical conduct workable under the conditions employees actually face. That requires understanding the justifications for misconduct and changing the business practices that give those justifications force.

Categories
Blog

Odyssey Week: Leadership – Athena in the Boardroom: Independent Oversight and Counsel

Ed. Note: I was finally able to see the movie The Odyssey. To say it blew me away was an understatement. Even though it didn’t follow Homer’s work precisely or use ancient Greek, I still thought it was great cinema. Anytime you get people talking about the Greek classics, that is a win in my book. So check out the movie and enjoy it. Zendaya was great as Athena.

Athena does not row the ship. She does not lash herself to the mast, fight the Cyclops, navigate Scylla and Charybdis, or drag Odysseus’s crew away from every bad decision they seem determined to make. She is not in the trenches every day. She does not submit expense reports, approve vendors, review discount requests, or sit through the quarterly business review where someone explains why this deal is “strategic.” But Athena changes the journey.

She sees what Odysseus cannot see. She warns. She guides. She challenges. She protects. She appears at decisive moments when courage alone is not enough, and cleverness is about to become self-harm with better branding. That is why Athena belongs in the boardroom.

For corporate compliance, Athena represents independent oversight and wise counsel: the person, function, or governance body able to say, “That may win the deal, but it may also wreck the kingdom.” A compliance function that cannot challenge leadership is not Athena. Rather, it is simply decoration to meet a legal, statutory, or contractual requirement.

The Corporate Translation

Every company says it values compliance independence. The question is what that means when the business wants something. It is easy to celebrate compliance when compliance supports the decision already made. It is easy to invite the Chief Compliance Officer (CCO) to the meeting after the deal is signed, the press release is drafted, and the train has left the station with several questionable third parties in the dining car. That is not independence. That is archaeology.

Independent oversight means compliance has the authority, access, and resources to influence decisions before risk is accepted. It means the board hears directly from compliance. It means escalation does not depend on whether a business leader feels emotionally prepared for bad news. It means compliance can challenge high performers, powerful executives, and sacred business strategies without being treated as disloyal.

Athena does not exist to admire Odysseus. She exists to help him survive himself.

Access Is Not the Same as Influence

Many compliance officers technically have access to leadership. They attend meetings. They submit reports. They provide updates. They own several slides in the board deck, usually after cybersecurity and before “other business.” But access is not the same as influence.

Real access means compliance can raise concerns in a setting where they matter. It means there are private sessions with the board or audit committee. It means compliance can speak without management filtering, softening, or translating the message into something more comfortable. It means the board asks questions that go beyond “Any major issues?” which is the governance equivalent of asking a teenager whether school was fine.

The DOJ’s 2024 Evaluation of Corporate Compliance Programs (ECCP) focuses directly on whether compliance and control functions have autonomy and resources, including sufficient stature, sufficient staffing and resources, and autonomy from management, such as direct access to the board or audit committee. That is not a technical footnote. It is a central governance point. If the compliance function only reaches the board through management, the board may be hearing the music after someone else has adjusted the volume.

Authority Must Be Real

A compliance function without authority is like Athena without wisdom: impressive in name only. Authority means compliance can stop, modify, or escalate a transaction. It means policies are not optional when revenue is large enough. It means compliance concerns are documented, tracked, and resolved. It means the business must explain why it wants to proceed despite risk, not merely pressure compliance to “be practical.”

Practical compliance is not weak compliance. Practical compliance helps the business find a lawful and ethical path forward. But there is a difference between being practical and being domesticated. A good compliance function does not say no for sport. It says no when the facts, risks, and values of the company require it. It says, “not that way.” It says, “not with that intermediary.” It says, “not without diligence.” It says, “not until we understand the data, the customer, the payment, the conflict, or the control failure.”

The ECCP specifically asks how a company has responded when compliance raised concerns and whether transactions or deals have been stopped, modified, or further scrutinized because of compliance concerns. That is the right question. The ECCP states at one point, “Have they persisted in that commitment in the face of competing interests or business objectives?” Not whether compliance attended the meeting. Whether compliance changed the outcome. The ECCP further asked, “What role has compliance played in the company’s strategic and operational decisions? How has the company responded to specific instances where compliance raised concerns? Have some transactions or deals been stopped, modified, or further scrutinized as a result of compliance concerns?”

Resources Are a Statement of Values

Companies reveal what they value through budget. A board can praise compliance all day long. Still, if the function lacks staffing, technology, data access, training budget, investigative resources, and experienced personnel, the message is clear: “We support compliance, but preferably at a discount.”

No one would ask sales to grow revenue without systems, people, and market data. No one would ask finance to close the books with three spreadsheets, two interns, and a heroic attitude. Yet compliance teams are often expected to monitor global risk with underpowered tools and just enough headcount to keep the training completion dashboard from turning red.

That is not empowerment. That is wishful thinking. The ECCP asks whether compliance personnel have sufficient staffing to audit, document, analyze, and act on compliance efforts, whether resources are comparable to other parts of the company, and whether compliance has access to relevant data for timely monitoring and testing. Regarding funding and resources, the ECCP asks, “Has there been sufficient staffing for compliance personnel to effectively audit, document, analyze, and act on the results of the compliance efforts? Has the company allocated sufficient funds for the same? Have there been times when requests for resources by compliance and control functions have been denied, and if so, on what grounds? Does the company have a mechanism to measure the commercial value of investments in compliance and risk management?”

Those questions should make boards uncomfortable in a productive way. If the business has world-class tools to capture opportunity but outdated tools to detect risk, that imbalance is itself a governance decision.

Escalation: The Road from Concern to Action

Athena’s guidance matters because it reaches Odysseus when action is still possible. That is also the purpose of escalation. A well-designed escalation process moves concerns to the right people at the right time with enough information to make a decision. A weak escalation process traps concerns in email chains, local management reviews, or “let’s monitor this” limbo until the problem becomes a reportable event, a whistleblower complaint, or a headline.

Escalation should not depend on personality. It should not depend on whether the compliance officer is unusually persistent, politically skilled, or willing to become unpopular before breakfast. It should be built into governance.

What must be escalated? To whom? Within what timeframe? With what documentation? What happens when business and compliance disagree? Who decides? How are unresolved concerns reported to senior leadership or the board? These are not theoretical questions. They are the mechanics of wise counsel. Because without escalation, Athena is whispering in a locked room.

The Board’s Role: Ask Better Questions

Boards do not need to manage the compliance program day to day. That is not their role. But boards do need to oversee whether the program is real. That means asking better questions. The board should also pay attention to the moments when compliance loses. If compliance raised concerns and the business proceeded anyway, what happened? Was the decision documented? Were compensating controls added? Was the board informed? Did the risk later materialize? You learn a great deal about culture by examining what happens when wise counsel is inconvenient.

The Compliance Takeaway

Athena does not represent bureaucracy. She represents judgment. That distinction matters. Compliance officers are sometimes caricatured as the people who slow things down, complicate decisions, or drain the romance out of heroic commercial ambition. But the best compliance functions do something far more important: they help the organization see clearly before it acts.

They bring risk into the room. They challenge assumptions. They protect the company from cleverness without discipline. They help leaders understand that winning the deal, entering the market, launching the product, or pleasing the customer is not success if the path taken damages the company’s integrity.

Independent oversight is not ceremonial access. It is authority, resources, escalation, data, board engagement, and the organizational courage to let compliance challenge power. Odysseus needed Athena because brilliance has blind spots. So does every company.

The question is whether your Athena is truly in the boardroom or merely listed on the org chart.

Join us Tomorrow

Athena teaches that independent oversight is not ceremonial access but real authority, resources, escalation, data, board engagement, and the courage to let compliance challenge power. But that lesson only matters if the organization is willing to apply it to its most celebrated leaders, not merely its easiest targets. That brings us to Odysseus: the brilliant, strategic, results-driven leader every board wants and the very leader who can become the company’s most dangerous compliance risk when success becomes a shield. If Athena is the voice saying, “That may win the deal, but it may also wreck the kingdom,” Odysseus is the leader who wins the deal and forces the organization to ask whether anyone had the authority, courage, and independence to challenge how he did it. I hope you will join us tomorrow.

Categories
From the Editor's Desk

From the Editor’s Desk: Aaron Nicodemus on the August and September in Compliance Week

In this episode of ‘From the Editor’s Desk,’ Tom Fox visits with Compliance Week editor-in-chief Aaron Nicodemus to discuss highlights from Compliance Week in August, take a look at what is coming down the pike in September in Compliance Week, and discuss the upcoming Third Party Risk Management and Supply Chain Summit in Chicago.

Tom and Aaron review key August coverage and upcoming priorities. They discuss new columnist Ben Mason’s “The Hidden Cost of Compliance Leadership,” outlining five recurring burdens for compliance leaders: independence that is often only theoretical, job risk from doing the role properly (including survey findings that nearly 70% of compliance officers have experienced retaliation), inability to voice doubts internally, the invisibility of effective prevention work, and weak leadership support—creating isolation and prompting ideas for safe forums such as the vetted CW app and event roundtables. Nicodemus highlights his Mayo Clinic whistleblower story alleging AI use may endanger patient privacy and outpace internal guardrails. He also describes a National Conference “Practitioner’s Briefing” distilling six Chatham House themes, previews a September 1MDB case study on enablers, plans AI-governance essays for National Compliance Officers Day, and promotes the Oct. 28–29 Chicago TPRM Summit.

Resources:

Aaron Nicodemus on LinkedIn

Compliance Week

Third Party Risk Management and Supply Chain Summit

Categories
Blog

Dolly Parton and the Compliance Value of a Life Well Governed

Dolly Parton died this week. Her death closed one of the most remarkable careers in American entertainment, but it did not close the institutions, ideas, and expectations she built. For corporate compliance professionals, that durability is what makes her story more than a tribute. It becomes a lesson in how values can be converted into governance. Today I want to honor Parton, what she did, and what she stood for, and perhaps hope that her life will inspire all of us to be just a little better.

Parton was one of twelve children. Parton began singing on local radio and television as a child and appeared at the Grand Ole Opry at thirteen. She wrote her first song at age 6. She moved to Nashville after high school, established herself as a songwriter, and became a national star through The Porter Wagoner Show. She then built a solo career that crossed country, pop, film, television, theater, publishing, tourism, and philanthropy. She recorded more than fifty albums, wrote roughly 3,000 songs, won ten Grammy Awards, and created works such as “Jolene,” “I Will Always Love You,” and “9 to 5” that became part of the American vocabulary. One of the most amazing facts I learned while researching this piece was that “Jolene” and “I Will Always Love You” were written on the same day. How is that for creative inspiration?

Parton did not run a corporate compliance program, and her career should not be forced into that frame. Yet she demonstrated something every CCO and Board of Directors needs to understand: culture becomes credible when stated values, hard decisions, operating systems, and visible conduct reinforce one another over time. Her public identity rested on kindness, independence, dignity, humor, and respect. She repeatedly made those commitments tangible in contracts, businesses, philanthropy, and crisis response.

Her entrepreneurship deserves equal attention. Parton moved from performer to owner, producer, publisher, and partner, most visibly through Dollywood and the enterprises built around it. The portfolio was diverse, but it was not random. Music, storytelling, family entertainment, Appalachian identity, hospitality, and community investment all reinforced a coherent promise. Compliance professionals should recognize the governance advantage of that clarity. Diversification creates new legal, operational, third-party, and reputational risks, but a stable purpose helps leaders decide which opportunities fit, which controls must travel with the business, and which deals to decline.

Independence Before Applause

Parton understood the difference between access to power and surrender to it. She left Porter Wagoner in 1974 to build an independent career, expressing gratitude for the partnership without allowing it to define her future. She later declined an opportunity for Elvis Presley to record “I Will Always Love You” when his manager demanded a share of the publishing rights—saying no cost her an extraordinary short-term opportunity. Retaining ownership preserved the long-term value of her work, especially when Whitney Houston’s recording became a worldwide success. Business Insider called it “her smartest business move.”

That decision should resonate with compliance leaders. Independence is not a paragraph in a charter. It is the authority to resist pressure when revenue, status, or a powerful executive makes acquiescence attractive. A CCO needs direct access to the board, control over investigative escalation, sufficient resources, and protection against retaliation. Chuck Watson once said, “Sometimes the best deal is the one you don’t make.” A board should test whether that independence works when it is expensive, inconvenient, and unpopular. If compliance can say no only when nothing important is at stake, it is not independent.

Purpose Made Operational

Parton’s philanthropy offers an equally powerful lesson in program effectiveness. She created the Dollywood Foundation in 1988 to improve educational outcomes in her home county. Its Buddy Program paired students and offered a financial incentive for graduation; the dropout rate for the participating classes fell from 35 percent to 6 percent. In 1995, inspired by her father’s inability to read and write, she launched the Imagination Library. What began in Sevier County became a network operating across five countries that has delivered more than 300 million free books to young children.

This was not the purpose of branding. It was purpose translated into a defined population, a repeatable delivery model, local partnerships, funding, data, and measurable results. That is the same transition the Department of Justice asks companies to make when it evaluates whether a compliance program is well designed, adequately resourced, and working in practice. A value in the code of conduct must become an owner, a control, an escalation path, testing, and remediation. Intent is the beginning of a compliance program, not proof of one.

Listen to the People Who Experience Power

Parton’s film and song “9 to 5” gave popular form to workplace realities many employees already knew: power can be abused, unfairness can become routine, and people with the least authority often carry the greatest burden. The song endured because it recognized the lived experience behind organizational charts. It made a workplace issue visible without turning the people affected into abstractions.

Compliance programs fail when they listen only upward. Hotline statistics, exit interviews, culture surveys, investigation themes, retaliation allegations, and manager-level trends must reach leaders in a form that supports action. Boards should ask whether employees believe they can speak without losing status, opportunity, or employment. They should also ask whether the organization learns from weak signals before they become red flags. A speak-up system is not effective because a telephone number exists. It is effective when people trust the process and see consistent, fair outcomes.

Trust Earned Through Response

Parton’s businesses remained closely connected to the community that formed her. Dollywood became Sevier County’s largest employer, while its stated operating culture emphasizes hospitality, authenticity, collaboration, and respect. The company supports employee development, including tuition assistance. When wildfires devastated East Tennessee, Parton helped organize direct support for affected families. During the COVID-19 pandemic, her $1 million gift established a Vanderbilt research fund that supported work connected to the Moderna vaccine.

The compliance lesson is that reputation is a lagging indicator of accumulated conduct. Trust is built before a crisis through thousands of ordinary decisions about employees, customers, communities, and counterparties. A crisis tests it through the speed, fairness, transparency, and competence of the response. A company cannot purchase credibility with a campaign after years of contrary conduct. The best crisis communication remains a well-governed response supported by facts, accountable owners, and visible follow-through.

A Board Agenda Worthy of the Lesson

Parton’s legacy was unusually broad, but its organizing logic was simple. Know what matters. Protect it when pressure arrives. Build systems that carry values beyond the founder. Listen to people whose voices are easiest to overlook. Measure whether the work changes outcomes. Repeat the conduct long enough that stakeholders can rely on it.

  • For directors, that logic produces five practical questions. What principles will the company not trade away for a transaction or quarterly target?
  • Does the CCO possess real independence, resources, information, and access?
  • Which data prove that stated values operate at the employee and third-party level?
  • Are speak-up and investigation systems producing trust, learning, and remediation?
  • When the company faces a crisis, can the board see decisions, owners, deadlines, testing, and closure rather than a record showing only that management made a presentation?

Dolly Parton understood that a carefully created image can open a door, but only character and performance can keep it open for seven decades. Compliance leaders often describe their goal as building a culture of integrity. Her career reminds us what that requires: independent judgment, operational discipline, attention to the less powerful, measurable impact, and consistency when no applause is guaranteed. That is not only a fitting business lesson from her life; it is a demanding standard for every organization that wants to be trusted.