Categories
Innovation in Compliance

Innovation in Compliance: Compliance Evangelists Fighting Modern Slavery Together with Matt Friedman

Innovation comes in many areas, and compliance professionals need to not only be ready for it but also embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom Fox visits with Matt Friedman, who provides a 2026 update to the fight against the international scourge of human trafficking and modern slavery and discusses his latest book, Awakening the Advocate.

Friedman is a leading voice in the fight against human trafficking and modern slavery, known for founding and leading the Mekong Club and for more than 35 years of advocacy, policy work, and corporate engagement. He views modern slavery as a vast, still underaddressed crisis, where tens of millions remain trapped while the number of survivors helped and criminals convicted remains far too small to match the scale of the problem. Friedman believes the biggest barrier is not compassion but awareness and that educating employees inside companies can “wake up” lawyers, bankers, marketers, and other professionals who already have the instincts to help. From his perspective, ESG and compliance efforts can protect the business while also driving meaningful anti-slavery action, making corporate compliance a practical engine for both risk reduction and social change.

Key highlights:

  • Compliance Evangelists Fighting Modern Slavery Together
  • Leadership Briefings and Procurement Risk Assessments
  • Board-Level Awareness Protects Reputation and Brand Value
  • AI sifting data to uncover scam-center patterns
  • Modern Slavery Risks Make ESG’s Future Uncertain

Resources:

Matt Friedman on LinkedIn

The Mekong Club

Awakening the Advocate on Amazon.com

Innovation in Compliance was recently honored as the Number 4 podcast in Risk Management by 1,000,000 Podcasts.

Categories
Blog

Connected Compliance: Part 2 – From Risk Register to Risk Radar

An effective compliance program is not a collection of disconnected policies, training modules, hotline reports, and investigation files. It is an operating system. Culture determines whether employees will use it. Risk assessment tells the organization where it must adapt. Investigations test whether the system responds credibly. Whistleblower programs reveal whether employees trust it enough to speak. Blog 1 examined communication as the control that connects those elements. In this Part 2, we examine what compliance must do with the intelligence that communication produces.

The traditional risk assessment was built for a world that moved more slowly. Compliance gathered a group of leaders, reviewed enforcement trends, scored familiar risks, produced a heat map, and returned to the exercise the following year. That process still has value, but it is no longer enough.

Today, a new market restriction, customer demand, artificial intelligence deployment, supply-chain disruption, sanctions measure, or data rule can alter the company’s risk profile before the annual plan is approved. The central question is therefore not whether the organization has a risk register. It is whether compliance has a risk radar that can detect change, decide what matters, assign ownership, and translate the signal into action.

Every Compliance Risk Has a Political Dimension

Compliance obligations do not develop in a vacuum. They reflect choices made by governments about national security, trade, technology, labor, privacy, corruption, competition, and corporate accountability. For a multinational company, those choices may conflict, overlap, or change with little notice. Particularly in this political age, the single most-used byword is volatility.

That makes geopolitical awareness a compliance capability. It does not require the CCO to become a foreign-policy analyst. It requires the compliance function to understand how political priorities can become legal obligations, enforcement pressure, customer expectations, or operational constraints. Export controls can reshape product access. Sanctions can alter payment and counterparty risk. Forced-labor requirements can reach deep into a supply chain. AI rules can change how a business collects data, develops products, and makes decisions.

The practical lesson is that legal change is often the last stage in a longer policy development process. Compliance should monitor the earlier signals: legislative proposals, agency speeches, enforcement patterns, trade measures, customer questions, supplier difficulties, and operational workarounds. These indicators do not all demand a program change, but they should enter a disciplined triage process.

What the DOJ Is Really Asking

The Department of Justice has made dynamic risk assessment part of the effectiveness inquiry. The 2024 Evaluation of Corporate Compliance Programs (ECCP) directs prosecutors to consider “emerging risks as internal and external circumstances impacting the company’s risk profile evolve.” This risk profile can change due to factors outside a company’s control or its own business decisions. Moreover, the ECCP language moves risk assessment beyond a scheduled document and into continuous management.

DOJ then asks: “Is the company’s approach to risk management proactive or reactive?” The distinction is critical. A reactive program updates controls after a failure, enforcement action, or audit finding. A proactive program uses operational information across functions to identify change before misconduct occurs. The ECCP also asks whether periodic review is merely a point-in-time exercise or draws on continuing access to operational data, and whether the results lead to updates in policies, procedures, and controls.

The enforcement question is not whether the company predicted every development. No program can. The question is whether the company had a reasonable process for identifying material changes, directing resources to higher-risk areas, documenting its decisions, and revising the program over time.

Build the Risk Radar From Multiple Signals

A dynamic risk process begins with a wider field of vision. Regulatory alerts and outside counsel updates are useful, but they show only part of the environment. Some of the earliest warnings come from inside the business. Sales may see unusual customer demands in a new market. Procurement may find suppliers unable to provide origin information. Finance may identify payment routes that no longer fit the expected transaction. Information security may discover employees using unapproved AI tools. Human resources may raise concerns about retaliation or pressure related to performance targets. Audit may identify recurring exceptions. Hotline reports and investigations may reveal a pattern that a heat map missed.

Compliance should bring these signals together through a repeatable cadence. A quarterly cross-functional review can examine changes in the business model, geography, products, third parties, technology, enforcement, and employee concerns. High-velocity risks may require monthly or event-driven review. The objective is not to create another committee. It is to establish a reliable place where weak signals are compared, challenged, and assigned.

Or simply look at the changes wrought by the Trump Administration in 2026 alone. Venezuela is now open for business. How about the Democratic Republic of Congo? See here and here. Of course there is Iran, but you have to ask what week it is and are we doing business with Iran or are we at war with Iran.

Give One Person the Clock

Emerging risks often fall between organizational boxes. Legal understands the rule. Compliance sees the control issue. Operations owns the process. Procurement controls the supplier relationship. Technology owns the system. To use a well-worn maxim, if everyone is in charge, no one is in charge. In the corporate world, when everyone is generally responsible, no one is specifically accountable. This is both why and where compliance needs to step up its game.

Every material risk needs a named owner with the authority to convene the necessary functions, set deadlines, escalate disagreements, and report on the disposition. That person does not perform every task. The owner keeps the clock, maintains the decision record, and ensures that the issue does not disappear between meetings.

Governance should also define escalation triggers. A credible framework identifies which developments require immediate executive attention, which can be handled through a working group, and which should remain under observation. Without thresholds, organizations either under-escalate material risk or flood leadership with undeveloped issues.

Use a Two-Speed Assessment

Not every signal requires an enterprise-wide risk assessment. Compliance needs two speeds. The first is rapid triage. A small group of subject-matter experts identifies the potential legal obligation, affected operations, time horizon, severity, available data, current controls, and immediate containment needs. This is where AI can play a key role in compliance, essentially superforecasting risks to enable quick, efficient risk management strategies when volatility hits. Additionally, such an approach may lead to a decision to monitor, take interim action, or launch a deeper review.

The second is formal assessment. Complex or high-impact risks may require structured interviews, data analysis, control testing, external counsel, forensic support, or scenario planning. The deeper process should be proportionate to the exposure, not triggered simply because the issue is new. This two-speed model protects agility without sacrificing rigor. It also creates evidence that the company made a reasoned decision. A short written triage record can show what information was considered, who participated, why the company chose its response, and when the issue will be reviewed again.

Convert Assessment Into Real Controls

The most common failure is not the inability to identify risk. It is the failure to convert assessment into a viable risk management strategy and then to implement, monitor, and improve your business operations. A new questionnaire, certification, or policy may create documentation, but documentation alone does not mitigate the underlying exposure.

Consider third-party risk. A supplier questionnaire can identify missing information, but the control lies in what happens next: enhanced diligence, contractual protection, source verification, payment restrictions, audit rights, monitoring, remediation, or a decision not to proceed. The same principle applies to AI. An AI-use policy matters, but effective governance also requires an inventory of use cases, approval gates, data controls, human oversight, testing, monitoring, and accountability.

Each response should identify the control objective, owner, implementation date, evidence, and testing method. Compliance should also ask what existing control can be adapted before building a separate program. Strong governance, escalation, training, data access, and investigation processes are reusable infrastructure across risk domains.

Resource allocation is part of that conversion. If a changing risk profile calls for deeper third-party monitoring, faster export review, or additional AI oversight, the organization must decide what people, technology, and budget will support the response. Compliance cannot claim to be risk-based when yesterday’s priorities continue to dictate today’s resources. The allocation decision, including any accepted constraint, should be visible and documented.

Treat Change Management as a Control

A technically correct response can still fail if employees do not understand it or the business cannot implement it. New requirements frequently collide with established incentives, systems, customer commitments, and local practice. Change management should therefore be part of the control design. Explain why the risk changed. Identify which decisions and workflows are affected. Train the employees and gatekeepers who must act differently. Provide a practical escalation route. Test understanding. Gather feedback. Then revise the process when implementation exposes friction or unintended consequences. For a full discussion of change management as a compliance control, listen to the podcast Ronnie Feldman and I did with Caveni Wong on this episode of Creativity and Compliance.

This is where blog post 1’s communication discipline comes into play. Compliance cannot adapt to risk through broadcast messages alone. It needs a two-way channel that tells employees what changed and tells compliance whether the response works in practice.

Measure Adaptation, Not Activity

The number of risk meetings or completed assessments says little about effectiveness. Better measures test whether the organization moves from signal to decision and from decision to control. Useful indicators include the time required to triage a material development, percentage of actions with named owners and deadlines, overdue remediation, control implementation and testing results, repeat exceptions, unresolved ownership disputes, and lessons incorporated from investigations.

Compliance should also examine whether resources shifted when risk shifted. A program that identifies a higher risk but leaves staffing, monitoring, and controls unchanged has produced analysis without management. The result should be a closed loop: detect, assess, assign, mitigate, test, and learn. That loop turns risk assessment from an annual artifact into a management process.

That transition is where program credibility is tested. Join us tomorrow as we consider how organizations scope investigations, preserve independence, establish consistency, document decisions, and convert findings into remediation. A dynamic risk process helps the company see the signal. A credible investigation determines what happened and what the organization must do next.

Bonus Questions for Compliance Professionals

  1. Which internal and external signals can change the company’s risk profile between formal assessments?
  2. Who has specific ownership for emerging risks that cross legal, compliance, operations, procurement, finance, and technology?
  3. What criteria determine whether an issue is monitored, triaged, escalated, or formally assessed?
  4. Can the company show how a recent risk assessment changed a policy, control, resource allocation, or business decision?
  5. Do substantive mitigation and ongoing monitoring support questionnaires and certifications?
  6. How quickly can the organization move from a weak signal to a documented decision?
  7. What recent investigation finding should change the current risk assessment?

Categories
Blog

Connected Compliance: Part 1 – Communication as the Operating System of Compliance

An effective compliance program is not a collection of disconnected policies, training modules, hotline reports, and investigation files. It is an operating system. Culture determines whether employees will use it. Risk assessment tells the organization where it must adapt. Investigations test whether the system responds credibly. Whistleblower programs reveal whether employees trust it enough to speak. Over this four-part blog post series, we will examine those connections, beginning with the discipline that makes every other element work: communication.

Compliance professionals often describe communication as one element of a program. That description is too narrow. Communication is the operating system through which employees learn expectations, seek advice, identify risk, report concerns, and judge whether management means what it says. If that system is slow, generic, inaccessible, or untrusted, even well-designed controls can fail in practice.

This matters because a compliance program does not become effective when a policy is published or training is completed. It becomes effective when an employee facing pressure knows what to do, understands where to go, and believes that asking for help will not create a career problem. Communication is therefore not simply messaging. It is a preventive control, a detection mechanism, and a source of management information.

Communication Is a Control, Not a Campaign

Many organizations still approach compliance communication as a calendar exercise. They send a Code of Conduct message, deliver annual training, publish a hotline reminder, and count distribution. Those activities may be necessary, but they do not establish whether the message reached the employee at the moment of risk.

An effective communication control has four characteristics.

  1. It is accessible, so employees can find guidance without having to navigate a maze.
  2. It is relevant, so examples reflect the decisions employees actually face.
  3. It is interactive so that employees can ask questions and test judgment.
  4. It is responsive, so the organization uses employee feedback to improve policies, training, and controls.

These distinctions are important. A campaign pushes information out. A control creates a reliable exchange of information. That exchange gives compliance an early view of confusion, pressure, process weakness, and emerging misconduct. It also gives employees a practical path to lawful and ethical decisions.

What the DOJ Is Really Asking

The Department of Justice has moved the compliance discussion away from paper design and toward operational effectiveness. The three fundamental questions in the 2024 Evaluation of Corporate Compliance Programs (ECCP) examine the program’s design, empowerment, and whether it works in practice.

For culture, the DOJ asks, “Does the company seek input from all levels of employees?” It then asks, “What steps has the company taken in response to its measurement of the compliance culture?” Those questions place two obligations on compliance. First, the company must listen across levels, functions, and locations. Second, it must demonstrate that listening changed something. Data without response is observation, not effectiveness.

The ECCP also directs prosecutors to examine policy accessibility, training effectiveness, the availability of guidance, and whether employees know when to seek advice. Taken together, these questions make communication evidence. A company should be able to show not only what it said but also who could access it, whether employees understood it, how they used it, and what management learned from it.

Build Channels Around Employee Behavior

Employees do not experience the company through a single channel. They communicate through managers, messaging platforms, internal websites, employee groups, town halls, mobile devices, and informal workplace networks. A compliance program that relies on one formal channel will miss important signals.

The practical response is a channel portfolio. Policies should be searchable and written in language employees can use. Guidance should be available through live compliance contacts and appropriate digital tools. Reporting options should include the hotline, web intake, direct contact with compliance or human resources, and management escalation. Communications should reach operational employees who may not sit at a computer, as well as global employees who may face language or cultural barriers.

Compliance also needs to listen where employees are already speaking. That may include internal collaboration channels, employee surveys, focus groups, office visits, and patterns in questions received by the compliance team. Any monitoring must be consistent with law, privacy expectations, company policy, and records-management requirements. The goal is not surveillance. The goal is to understand the employee experience before a cultural weakness becomes a control failure.

Face-to-face contact remains especially valuable. A visit to a business unit can reveal whether employees understand a policy, whether managers create pressure, and whether the local process matches the written procedure. It also changes how employees see compliance. A familiar adviser is easier to contact than a distant function that appears only during training or an investigation.

Replace Training Completion With Decision Readiness

Completion rates answer whether an employee opened a course. They do not answer whether the employee can recognize a conflict, challenge a questionable payment, escalate an export-control concern, or pause the use of an unapproved AI tool. As Hui Chen continually reminds us, it is about results, not inputs.

Training should therefore be built around decision readiness. Scenario-based sessions allow employees to work through realistic gray areas and explain why one course of action is safer than another. Shorter, targeted modules can address risk by role. Experienced employees may be able to demonstrate proficiency through testing, while supervisors may require additional training because they receive concerns and translate policy into daily conduct.

Relevance is a control feature. Employees are more likely to retain training that reflects their workplace, business model, and actual risk. A procurement team needs different scenarios from a sales team. A manager needs to understand retaliation and escalation. An engineer needs clear boundaries around data, cybersecurity, and AI. Localization must also address more than translation. Examples, delivery methods, and escalation paths should make sense in the local operating environment. The measurement should move beyond completion. Useful indicators include questions asked after training, repeat areas of confusion, scenario performance, requests for advice, policy-page use, control exceptions, and whether similar misconduct declines over time.

Make Leadership Visible and Consistent

Tone at the top loses force when it sounds scripted or appears only once a year. Employees judge leadership commitment through repeated choices: which risks receive attention, whether high performers are disciplined, whether managers welcome questions, and whether business pressure routinely overrides control requirements.

Compliance communication is stronger when leaders explain expectations in their own voices and connect them to business responsibilities. The chief executive can frame integrity as part of strategy. Finance can address books and records. Human resources can speak to respect, retaliation, and accountability. Business leaders can explain why escalation protects customers and sustainable growth.

Middle management is equally important. Most employees experience culture through their direct supervisor. Managers should be trained to receive concerns, avoid promises they cannot keep, protect confidentiality, escalate promptly, and prevent retaliation. If employees hear an ethical message from senior leadership but experience dismissal from a supervisor, the local message will win. Consistency completes the control. The organization must apply standards across rank, geography, and commercial importance. Unequal treatment communicates more powerfully than any policy statement.

Use Data Without Losing the Human Signal

Technology can help compliance measure reach and engagement. Policy-page analytics can show whether employees use key resources. Digital guidance tools can identify common questions. Investigation and reporting data can reveal trends by issue, region, or function. Training results can show where judgment remains weak.

These data points should be treated as signals, not verdicts. High question volume may indicate confusion, but it may also show that employees trust compliance. An increase in reports may reflect more misconduct, a successful awareness campaign, or greater confidence in the reporting process. Low reporting may indicate a healthy environment, or it may be a warning that employees believe speaking up is futile.

The best analysis combines quantitative and qualitative evidence. Compliance should compare usage data with employee interviews, survey responses, investigation themes, audit findings, exit information, and observations from business partners. It should protect privacy, limit access, and avoid metrics that encourage the wrong behavior. A target that simply seeks fewer reports can suppress the very information the company needs.

Convert Listening Into Action

The strongest evidence of culture is not the survey itself. It is what the company does next. If employees cannot find a policy, redesign access. If repeated questions reveal ambiguity, rewrite the guidance. If a region reports little despite known risk, test for fear or channel barriers. If investigations identify manager misconduct, adjust training, incentives, supervision, and discipline.

This requires a closed-loop process. Gather information. Analyze it for themes and root causes. Assign ownership for action. Document the decision. Communicate appropriate changes. Then measure whether the change worked. That process turns communication into continuous improvement and creates a defensible record of program evolution.

It also connects this first installment to the rest of the series. Employee questions and reporting patterns are early risk indicators. Investigation quality tells employees whether the company acts on what it hears. Whistleblower-program credibility determines whether critical information enters the system at all. Each element depends on the others.

From Culture to a Shifting Risk Environment

Communication gives compliance something more valuable than reach. It provides intelligence. Questions about a new market, an AI application, a third party, a customer demand, or a supply-chain disruption may be the first evidence that the risk environment has changed.

Join us tomorrow for our next installment, where we will examine how compliance can convert those signals into dynamic risk assessment, clear ownership, and adaptive controls. A shifting risk environment cannot be managed by an annual exercise alone. It requires the listening discipline established here.

Bonus Questions for Compliance Professionals

  1. Can employees find practical guidance at the moment they face a risky decision?
  2. Which groups, locations, or shifts are least engaged with compliance resources, and why?
  3. What evidence shows that employee feedback has changed the program?
  4. Are managers prepared to receive concerns, escalate them, protect confidentiality, and prevent retaliation?
  5. Do current metrics reward learning and trust, or do they unintentionally reward silence?
  6. What recent employee question should be treated as an emerging-risk signal?
Categories
Trekking Through Compliance

Trekking Through Compliance: Episode 42 – Objectivity Under Fire: What “Obsession” Teaches Compliance Leaders

In the world of corporate compliance, the most challenging issues are often not the ones found in policies and procedures but the ones that hit close to home. When an investigation, a potential violation, or a risk becomes personal, even the most seasoned compliance professionals can struggle to maintain objectivity, leadership, and ethical clarity.

No episode of Star Trek: The Original Series captures this dilemma more powerfully than “Obsession.” Today, we have five key leadership lessons for compliance professionals, each illustrated by a scene from this classic episode.

Lesson 1: The Danger of Letting Past Failures Drive Present Decisions

Illustrated by: Early in “Obsession,” Captain Kirk becomes fixated on the mysterious cloud creature, which he encountered as a young officer. He blames himself for not destroying it years ago, feeling responsible for the deaths of his former crewmates. This guilt clouds his judgment, leading him to pursue the creature at the expense of his current mission and crew.

Compliance Lesson: It is natural for past failures or unresolved issues to haunt compliance professionals, whether it is a missed red flag, a mishandled investigation, or a colleague’s misconduct that slipped through the cracks. However, leadership means acknowledging these feelings without letting them dictate current actions. Fixating on the past can compromise your objectivity, impair decision-making, and erode team trust.

Create a structured debrief process after investigations and audits that encourages candid discussions of lessons learned—but draw a clear line between healthy reflection and self-blame. If you notice yourself or a colleague ruminating on a past failure, seek outside perspective from a mentor or coach.

Lesson 2: Beware of Conflicts Between Personal Motivations and Organizational Mission

Illustrated by: The pursuit of the creature leads him to override the advice of Spock and McCoy, risking a critical rendezvous with the USS Yorktown, which is carrying vital medical supplies. His vendetta threatens to derail the Enterprise’s primary mission and put others at risk.

Compliance Lesson: Personal motivations, even those rooted in a sense of justice or accountability, can create conflicts with the organization’s broader mission. For compliance leaders, it’s essential to recognize when personal feelings, loyalties, or ambitions are at odds with what’s best for the company, stakeholders, or compliance program as a whole.

Regularly revisit your program’s core mission and values. Before making significant decisions, pause to ask, “Am I doing this for the right reasons? Is this truly about compliance and ethics, or is my agenda creeping in? “Encourage a culture of peer challenge, where team members can safely question each other’s motivations in high-stakes situations.

Lesson 3: Listen to Your Team—Even When You Disagree

Illustrated by: Throughout the episode, Spock, McCoy, and other crew members challenge Kirk’s judgment, pointing out the risks of his obsession. Kirk initially rebuffs their advice, convinced that only he understands the threat. It is only when he finally listens to his officers that he can devise an effective plan to confront the creature.

Compliance Lesson: Leadership in compliance is not about always being right; rather, it is about fostering a culture that welcomes diverse perspectives, especially when an issue becomes personal. Leaders must actively seek and value dissenting opinions and be open to changing course based on credible advice, even if it stings.

During high-stress or personal cases, explicitly ask your team for feedback and alternative viewpoints. Consider creating “devil’s advocate” roles in investigations and setting ground rules that ensure even junior team members can raise concerns without fear of reprisal.

Lesson 4: Maintain Professional Distance—Don’t Let Emotions Overwhelm Ethics

Illustrated by: Kirk’s obsession nearly leads him to take unnecessary risks, endangering himself and his crew. His emotional investment clouds his judgment, and he pushes past reasonable boundaries in pursuit of what he believes is justice. Only when he regains his professional composure does he successfully lead his crew to resolve the crisis.

Compliance Lesson: When issues become personal, whether due to relationships, past failures, or high stakes, it is easy for emotions to override ethics and professionalism. Compliance leaders must learn to recognize when they are too close to a situation and take deliberate steps to regain perspective.

Build time for reflection into your workflow, especially during emotionally charged investigations. When possible, delegate or recuse yourself from cases where you cannot maintain impartiality. Seek support from trusted colleagues or external advisors to help you keep perspective and objectivity.

Lesson 5: The Power of Accountability—Owning Up to Mistakes and Moving Forward

Illustrated by: At the episode’s conclusion, Kirk reflects on his actions with McCoy, admitting that his personal feelings clouded his judgment and nearly led to disaster. He doesn’t make excuses but owns up to his mistakes and takes the lessons to heart, recommitting himself to his duty as captain.

Compliance Lesson: True leadership is not about perfection but about accountability. When personal issues intrude and mistakes are made, the best compliance leaders acknowledge their errors, communicate them transparently, and model a commitment to continuous improvement. This builds credibility, trust, and resilience within the team and across the organization.

Foster a culture of accountability at all levels. After challenging cases, hold post-mortems to identify both successes and failures, and publicly recognize leaders and team members who model accountability. Use mistakes as learning opportunities, not sources of shame.

Final ComplianceLog Reflections

“Obsession” stands as a reminder that even the best leaders are vulnerable when the stakes become personal. But it also shows the power of self-awareness, teamwork, and accountability to bring us back to our best selves. For compliance professionals, the message is clear: We must learn to recognize when our history, emotions, or motivations are shaping our decisions; then pause, reflect, and act in line with our values and mission.

By encouraging diverse viewpoints, maintaining professional boundaries, and owning our mistakes, we can transform moments of personal challenge into opportunities for growth and organizational strength. That is the essence of ethical leadership in compliance.

So, as you navigate your next difficult investigation or compliance challenge, especially the one that hits close to home, remember Kirk’s journey. Do not shy away from what is personal. Embrace it, learn from it, and lead with courage, humility, and integrity.

  Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha

Timothy and Fiona are AI-generated voices.

Categories
Blog

When Employees Are Drowning in Compliance Change

Compliance professionals know the drill. A new policy is issued. A new training module goes live. A new third-party platform is rolled out. A new AI use standard is announced. A new M&A integration plan hits the field. A new sanctions update requires immediate attention. Each initiative may be defensible on its own. Taken together, they can overwhelm the very employees the compliance program depends upon.

That is the central compliance lesson from David Grossman’s MIT Sloan Management Review article, “When Employees Are Drowning in Change.” Grossman argues that effective leaders do not simply manage change; they manage how people experience change. His article identifies three disciplines that matter: make dialogue nonnegotiable, align leaders around a shared change narrative, and sequence change with employee capacity in mind. For compliance professionals, this is not merely a communications issue. It is a program effectiveness issue.

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks three core questions: Is the program well designed? Is it adequately resourced and empowered? Does it work in practice? The DOJ also makes clear that prosecutors look at whether compliance policies, training, reporting lines, incentives, discipline, and controls are integrated into the company’s operations and workforce. That means a compliance change that employees cannot absorb is not fully implemented. It may exist in a slide deck, an LMS platform, a policy portal, or a board report. But if it does not change behavior, it is not yet operating as a control.

Compliance Fatigue Is a Real Risk

Compliance professionals often think about risk in categories: anti-corruption, sanctions, fraud, conflicts, privacy, cybersecurity, antitrust, money laundering, books and records, and now AI governance. Employees do not experience risk in neat categories. They experience messages, requirements, approvals, certifications, controls, deadlines, and consequences.

That distinction matters. A sales manager may receive anti-bribery training, a gifts-and-hospitality update, a new distributor due diligence process, a revised approval matrix, an AI acceptable use notice, and a speak-up campaign in the same quarter. Compliance may see six separate risk-based initiatives. The employee sees a wall of instructions.

When that happens, the program creates noise. Employees may technically complete training but not internalize it. They may certify to policies but not understand how to apply them. They may attend a town hall but not know what has changed in their daily work. Worse, they may stop asking questions because the system feels too heavy to navigate. That is where Grossman’s change management lessons become directly relevant to the Chief Compliance Officer and the compliance team.

Make Dialogue a Compliance Control

The first discipline is dialogue. In compliance, dialogue should not be treated as a courtesy or a soft engagement tool. It is a control input.

The ECCP asks whether training and communications are tailored to the audience’s size, sophistication, subject matter expertise, needs, interests, and values. It also asks whether employees can ask questions arising out of training and whether the company measures training effectiveness, engagement, learning, and behavioral impact. This is a direct invitation for compliance teams to move beyond “push” communications. A one-way compliance rollout looks like this: publish the policy, assign the training, send three reminder emails, track completion, and report 98% completion to leadership.

A better model looks like this: identify the affected employee groups, ask where the new requirement will create friction, test the message with managers, build scenarios from real operational issues, provide a practical decision tool, hold short Q&A sessions, track questions and exceptions, and adjust the rollout based on what employees tell you.

Dialogue also requires closing the loop. When employees raise concerns about a new control, compliance does not have to accept every suggestion. But it should explain what it heard, what it changed, and what it could not change. Silence breeds skepticism. In compliance, skepticism becomes a workaround.

Build One Compliance Change Narrative

Grossman’s second discipline is alignment around a shared change narrative. This may be the most underused tool in the compliance function. Compliance teams frequently communicate in fragments. Legal explains the law. Compliance explains the policy. Internal audit explains control gaps. HR explains discipline. IT explains system access. Procurement explains third-party onboarding. Finance explains approval requirements. Each message may be accurate. Together, they may feel disconnected.

A compliance change narrative answers four practical questions:

  • Where have we been?
  • Where are we today?
  • Where are we going?
  • What must employees do differently?

For example, an AI governance rollout should not begin with a policy citation. It should begin with the business reality: employees are already using AI tools; the company wants innovation; customer and confidential information must be protected; decisions must remain accountable; and the company needs a consistent control framework. Then the compliance team can explain the required behavior: approved tools, prohibited uses, human review, data restrictions, escalation points, and monitoring.

This is also where middle management becomes essential. The DOJ expects senior leaders to communicate ethical standards clearly and demonstrate adherence by example. It also asks how middle management reinforces those standards and encourages employees to abide by them. In practice, employees often take their cues not from the CCO but from their direct supervisor. If the supervisor treats a new compliance requirement as administrative noise, the employee will do the same. Before any significant program change, compliance should align leaders on the story. Not a script. A shared narrative. What risk are we addressing? Why now? What will be easier? What will be harder? What support will employees receive? What does good look like?

Sequence Change With Capacity in Mind

The third discipline is sequencing. This is where compliance teams can create immediate business value. Grossman’s article notes that organizations often fail not because they are doing too much, but because they are doing too much at the same time without discipline. Compliance is vulnerable to this problem because every risk owner believes their initiative is urgent. The answer is not to do less compliance. The answer is to sequence compliance change with the same rigor applied to capital projects, technology rollouts, or major business transformations.

A mature compliance function should maintain a compliance change calendar. It should show what is hitting which employee population, when, and why. It should identify collision points. It should distinguish regulatory deadlines from preferred deadlines. It should flag high-risk groups that are already carrying heavy control burdens, such as sales, procurement, finance, logistics, government affairs, and third-party management teams.

The ECCP supports this risk-based discipline. Prosecutors ask whether the company deploys compliance resources in a risk-based manner, whether risk assessments are current, and whether updates to policies, procedures, and controls reflect lessons learned and evolving risks. Sequencing is part of that risk-based resource allocation. It is how compliance protects both the business and the control environment.

This is especially important in M&A integration. After closing, compliance must integrate codes, policies, hotline access, third-party controls, financial controls, training, investigation protocols, and audit plans. The DOJ specifically asks about the post-transaction compliance program, compliance oversight of the new business, incorporation into risk assessments, and post-acquisition audits. If compliance imposes all requirements on the acquired business at once, it may create both formal coverage and practical confusion. A sequenced plan gives employees a path from old expectations to new standards.

Measure Whether the Change Landed

Completion rates are not enough. Certifications are not enough. Attendance is not enough. The ECCP asks whether the program works in practice, whether it evolves, whether the company uses data to assess the program’s effectiveness, and whether it measures culture and seeks input from all levels of the organization. That means compliance change management must be measurable.

For training and communication, useful measures include questions asked, policy search data, guidance requests, hotline and speak-up trends, control exceptions, approval delays, audit findings, investigation themes, manager feedback, and pulse survey results. The issue is not simply whether employees received the message. The issue is whether they understood it, trusted it, and used it.

This is the practical bridge between Grossman’s article and the ECCP. Change management is not separate from the effectiveness of the compliance program. It is how effectiveness is achieved.

Practical Takeaways

  1. Create a compliance change inventory. List every major policy, training, system, control, campaign, certification, and reporting change scheduled for the next two quarters.
  2. Map the impact by employee group. Identify who is being asked to absorb the most change and whether those employees sit in high-risk roles.
  3. Require a change narrative for every significant rollout. The narrative should explain the risk, the business rationale, the required behavior, and the available support.
  4. Build dialogue into the process. Use listening sessions, manager huddles, Q&A channels, post-training feedback, and office hours. Then close the loop.
  5. Sequence based on risk and capacity. Not every compliance initiative can be first. Prioritize what is legally required, what addresses the highest risk, and what enables other controls to work.
  6. Measure behavior, not just delivery. Report to leadership on whether the change landed in the business, not merely whether the email was sent or the training was completed.

The compliance lesson is clear. Employees do not fail to follow compliance programs only because they lack information. Sometimes they fail because the organization has given them too much change, too little context, and no practical path to execution. A better compliance program does not simply say more. It listens better, aligns better, sequences better, and measures whether the business can actually do what compliance has asked.

Categories
Blog

Full-Court Compliance: What the Knicks’ Championship Teaches CCOs About Winning the Right Way

While later surpassed by the Michael Jordan Bulls and the back-to-back NBA Champs, my (then) hometown heroes, the Houston Rockets, my favorite NBA team from my teen years was the two-time NBA champs, the New York Knicks. I can still name the starting lineup from the 70-71 champs (Walt Frazier, Dick Barnett, Dave DeBusschere, Bill Bradley, and Willis Reed). So, while I live down the road from San Antonio, I was one of the very few people in Kerrville, TX, rooting for the Knicks.

Today, the New York Knicks are NBA champions for the first time since the 1972-73 season, and for compliance professionals, the story is more than basketball. It is a case study in governance, risk appetite, culture, talent strategy, controls, remediation, and execution under pressure. As reported by ESPN, New York defeated the San Antonio Spurs in five games to win its first NBA championship in 53 years, with Jalen Brunson scoring 45 points in the closeout Game 5 and earning Finals MVP honors.

The scoreboard tells the story of a team that operated under pressure:

Game Score
Game 1 at San Antonio Knicks 105, Spurs 95
Game 2 at San Antonio Knicks 105, Spurs 104
Game 3 at New York Spurs 115, Knicks 111
Game 4 at New York Knicks 107, Spurs 106
Game 5 at San Antonio Knicks 94, Spurs 90

ESPN’s Finals matchup summary listed the Knicks as the 4-1 series winners, based on those five-game results.

For CCOs, the championship lesson starts with roster construction. Leon Rose, the Knicks’ president of basketball operations and chief roster architect, did not build this team by chasing headlines. He built it the way an effective CCO builds a compliance program: with a clear risk assessment, disciplined resource allocation, cultural fit, control remediation, and continuous monitoring.

Start with Jalen Brunson. The Knicks acquired Brunson through free agency in 2022, and NBA.com described him as the central acquisition in Rose’s rebuild. Brunson later agreed to a below-market extension, which gave the organization flexibility to retain and add other players. That is a compliance principle in the form of basketball. You do not spend all your capital on one control and leave no budget for investigations, training, data analytics, third-party management, and monitoring. Brunson was the control owner, but the program still needed a full system around him.

Then came the risk-based gap analysis. Rose did not simply ask, “Who is available? ” He asked the compliance equivalent of, “What risk remains unmitigated? ”The answer was size, defense, positional versatility, rebounding, and playoff resilience. Karl-Anthony Towns arrived through a 2024 three-team trade with Minnesota, giving the Knicks elite frontcourt skill and passing. OG Anunoby came from Toronto in 2023 because the Knicks needed a high-end defender who could handle elite wings and still contribute offensively. Mikal Bridges came from Brooklyn in 2024 as a multi-position wing who could defend and shoot. Josh Hart arrived in a 2023 trade with Portland, bringing toughness, energy, leadership, and the intangible glue that every good system requires.

That is how a compliance officer should think about program design. Policies alone are not enough. Training alone is not enough. Hotline data alone is not enough. A championship compliance program needs anti-corruption controls, third-party due diligence, internal accounting controls, sanctions screening, speak-up culture, investigation protocols, data testing, and board reporting. Each element has a role. Each element covers a gap. Each element must work under stress.

The Knicks also demonstrated the value of cultural due diligence. Brunson, Bridges, and Hart carried a Villanova connection, but the lesson is not nostalgia. The lesson is known as performance under known pressure. Rose understood that talent without fit is a control failure waiting to happen. Compliance leaders understand this point well. A technically gifted executive who rejects controls, bypasses procurement, bullies internal audit, or treats legal review as an obstacle is not a high performer. That executive is a risk amplifier.

The Bridges trade is especially instructive. Rose paid a significant price, sending multiple first-round assets to Brooklyn. NBA.com described it as one of Rose’s biggest and most questioned risks before Bridges proved his value in the postseason. In terms of compliance, this was not risk avoidance. It was risk governance. The question for any board is not whether a strategy carries risk. All meaningful strategies carry risk. The question is whether management has identified the risk, documented the rationale, designed mitigation, and monitored outcomes.

Game 4 was the stress test. The Knicks trailed by 29 points and still beat the Spurs 107-106, completing the largest comeback in NBA Finals history under modern play-by-play tracking. In compliance, this is where paper programs fail, and real programs prove themselves. A company can look strong during the annual training season. The test comes when a whistleblower allegation arrives before the close of a quarter, a high-risk distributor is tied to a government official, a sanctions rule changes overnight, or a business leader asks for an exception because “the deal is too important.”

The Knicks did not win because they avoided adversity. They won because their controls held when adversity arrived. NBA.com noted that every game in the series was within five points in the last five minutes, and the Knicks erased double-digit deficits throughout the Finals. That is program effectiveness. A compliance program is not effective because the code of conduct is polished. It is effective because people make the right decisions when the score is close, the pressure is high, and the wrong shortcut looks attractive.

Finally, Rose made the coaching decision. Mike Brown replaced Tom Thibodeau in 2025, and NBA.com reported that Brown’s approach helped win over the locker room and make strategic changes during the playoff run. This is remediation. Mature organizations do not confuse past success with future sufficiency. Thibodeau helped move the Knicks forward, but Rose concluded that the next stage required a different operating model. CCOs face the same challenge when a legacy control, legacy investigator, legacy third-party process, or legacy reporting structure no longer fits the risk environment.

The Knicks’ championship was not an accident. It was the result of governance, discipline, culture, and controls. That is why CCOs should study it. Define your risk appetite before the season starts. Build around culture, not just talent. Spend resources where the risk assessment shows the gaps. Treat major decisions as board-defensible governance judgments. Most importantly, test whether your program can perform in the final five minutes, because that is where championships and compliance failures are decided.

Categories
Trekking Through Compliance

Trekking Through Compliance: Episode 14 – Investigative Lessons from Balance of Terror

In this episode of Trekking Through Compliance, we consider the episode Balance of Terror, which aired on December 15, 1966, Star Date 1709.1.

In this episode of Trekking Through Compliance, we analyze “Balance of Terror,” the tense, submarine-style showdown between the Enterprise and a Romulan Bird-of-Prey, which introduces one of Star Trek’s most enduring adversaries. The story unfolds as a mystery: Who attacked the Earth outposts? What is this new weapon? Who are the Romulans? And what do their sudden appearances mean for the Federation?

We review the critical investigative lessons this episode offers for compliance professionals: the importance of situational analysis, managing internal bias, respecting operational security, and knowing when to act and when to wait. In this cat-and-mouse episode, we find the foundations of modern investigative best practices.

Key highlights:

1. Situational Awareness and Evidence Gathering—Don’t Jump to Conclusions

🖖Illustrated by: The destruction of Outposts 2 and 3 and the cryptic communication from Outpost 4.

Captain Kirk begins his investigation without clear evidence, gathering fragmented data from the surviving outpost’s transmissions and assessing the damage patterns. For compliance professionals, this illustrates the importance of establishing a clear fact pattern before reaching a conclusion. Investigations must be driven by objective evidence, not assumptions.

2. Managing Internal Bias—Appearance Is Not Proof

🖖Illustrated by: Lieutenant Stiles’ suspicion of Mr. Spock based on the physical resemblance between Romulans and Vulcans.

Stiles immediately targets Spock as a potential traitor, despite a complete lack of evidence, simply because Romulans and Vulcans share a similar appearance. This moment serves as a cautionary tale about compliance: biases, whether conscious or unconscious, can derail investigations and damage team morale.

3. Strategic Surveillance—Investigate Without Provoking Retaliation

🖖Illustrated by: Kirk shadowing the Romulan ship to determine intent and capabilities before engaging.

Rather than charging into conflict, Kirk chooses to observe the Romulan ship’s behavior. In compliance investigations, particularly those involving fraud or misconduct, covert observation and the secure handling of information are crucial to preventing tip-offs or escalation.

4. Chain of Custody and Documentation—Recording and Communicating the Facts

🖖Illustrated by: The tactical logs Kirk reviews and Spock’s technical input during the confrontation.

Throughout the engagement, Kirk relies on detailed sensor data, eyewitness accounts, and Spock’s analysis to make decisions. Compliance professionals must ensure the proper documentation of interviews, timelines, and data sources for both internal review and external audit.

5. Ethical Leadership During Investigations—Calm in the Face of Conflict

🖖Illustrated by: Kirk’s balance between decisiveness and restraint, even when provoked by Romulan attacks.

Kirk refuses to act out of fear or anger—even as tensions rise. He models ethical leadership by protecting lives, upholding treaty obligations, and maintaining moral clarity. In high-stakes compliance investigations, emotional discipline and ethical consistency are vital.

Final Starlog Reflections

Balance of Terror is a masterclass in investigative poise, procedural discipline, and ethical clarity under pressure. As the Enterprise crew faces a new adversary cloaked in invisibility, we see what real leadership looks like when facts are scarce and risks are high.

For compliance professionals, this episode is a reminder that investigations require patience, vigilance, and integrity. Bias must be checked, facts must be verified, and trust must be earned. The threat may be hidden, but your investigative principles must always remain visible.

Resources:

Excruciatingly Detailed Plot Summary by Eric W. Weisstein

MissionLogPodcast.com

Memory Alpha

Categories
Blog

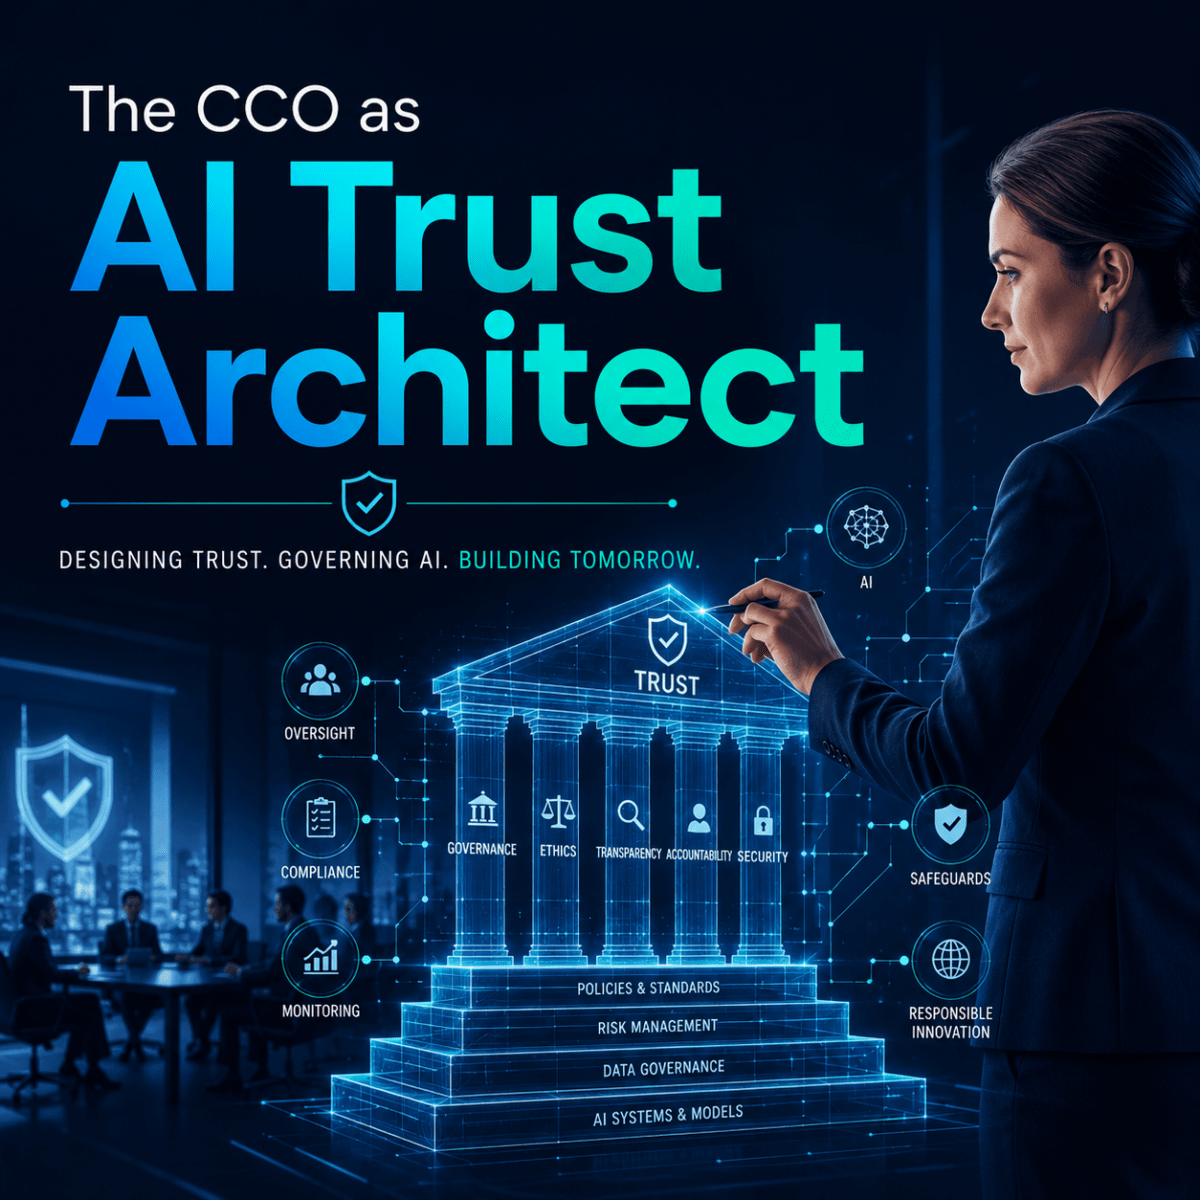
The CCO as AI Trust Architect

The most important AI risk inside many companies may not be that employees are using AI. It may be that employees are using AI and hiding what they are learning. That is the central compliance lesson from Eric Anicich and Jeslyn Brouwers’ HBR article, Why Employees Aren’t Transparent About Their AI Usage. The authors open with a physician who had built a highly effective prompting template inside an approved, HIPAA-compliant AI tool. His colleagues were struggling with the same tool. He believed his template could help them. Yet he did not share it.

The article reports that a study by KPMG and the University of Melbourne, involving more than 48,000 respondents, found that 57% of employees admitted to hiding their AI use at work. More importantly, the authors argue that concealed use is only part of the issue. What employees are learning privately through prompt sequences, chained tools, and successful workflows may matter even more. AI introduces what the authors call the suppression of solutions: employees may be withholding productivity breakthroughs that could help the entire organization.

For the CCO, this creates a new mandate. The compliance function must help bring AI use into the open without becoming the AI police. The CCO must build a governance system that encourages employees to disclose, share, and improve AI-enabled work while still protecting the company from real risks around confidentiality, privacy, IP, bias, inaccurate outputs, cybersecurity, records retention, regulatory representations, and misuse. That is the function the CCO can fulfill: the AI trust function.

Why Hidden AI Use Is a Compliance Problem

Most compliance professionals instinctively focus on the obvious AI risks. Employees may paste confidential data into public tools. They may use AI to draft customer-facing claims without verification. They may generate code, contracts, marketing copy, investigation summaries, due diligence reports, or regulatory submissions without appropriate review. They may rely on AI outputs that are inaccurate, biased, incomplete, or unsupported. Those risks are real.

But the authors point to a second problem: the company may also be losing the benefits of compliant AI experimentation. Productivity gains are once scaled through shared systems and standardized processes. With AI, many gains begin as individual discoveries: a better prompt, a workflow shortcut, a way to summarize information, a way to identify anomalies, or a method that reduces a multi-hour task to minutes. That knowledge is portable, private, and easy to conceal.

This means the CCO must avoid a one-dimensional response. A punitive AI governance program may reduce some visible misuse, but it may also drive experimentation underground. Employees who fear being judged, punished, overworked, or replaced will not share what they are doing. They will protect themselves. That creates the worst of both worlds: risk remains hidden, and useful innovation remains trapped inside individual workflows.

The CCO’s New Role: Govern for Trust, Not Just Control

The author’s core finding is highly relevant to compliance. They surveyed 604 U.S.-based employees who used AI at work daily or multiple times per day. Nearly one in three said they had intentionally withheld AI-related knowledge, workflows, or techniques. Employees in the lowest quartile of organizational trust were nearly four times as likely to withhold AI knowledge as those in the highest quartile (47% versus 14%). A similar pattern appeared for psychological safety, 45% versus 17%.

That finding should feel familiar to compliance professionals. Speak-up culture works the same way. Employees report misconduct when they believe the company will listen, protect them, and act fairly. Employees hide misconduct when they believe the company will punish the messenger, ignore the issue, or retaliate indirectly. AI transparency is now a speak-up issue.

The CCO should therefore treat AI disclosure as part of the company’s broader culture of integrity. The question is not merely, “Are employees using approved AI tools? ”The better question is, ‘Do employees trust us enough to tell us how they are using AI, what they have learned, where they are uncertain, and what risks they see? ”

That is where the compliance function can add unique value. Compliance already understands reporting channels, non-retaliation, policy clarity, training, investigation triage, escalation, monitoring, remediation, third-party risk, and board reporting. Those capabilities can be applied to AI governance if the CCO frames the issue correctly.

Distinguish Experimentation from Misconduct

A major insight in the article is that companies often confuse two very different categories of behavior. One is blameworthy deviance: ignoring rules or cutting corners in ways that harm the organization. The other is exploratory testing: experimenting at the edge of what is known in ways that can generate valuable learning. When companies confuse the second with the first, they punish the behavior they need to encourage. This is directly applicable to the CCO.

An employee who uploads customer personal data into an unapproved public AI tool may have created a serious compliance issue. An employee who uses an approved internal AI tool to create a better first draft of a due diligence memo may have created a learning opportunity. An employee who uses AI to fabricate supporting documentation has engaged in misconduct. An employee who uses AI to test a workflow and then asks compliance whether the use is permissible has done exactly what the company should want. The CCO’s job is to build a framework that makes those distinctions clear.

That means creating red lines, green lanes, and gray zones. Red lines are prohibited uses: confidential data in unapproved tools, AI-generated false records, unreviewed regulatory filings, discriminatory automated decision-making, or any use that circumvents required approvals. Green lanes are encouraged for use: approved tools for summarization, first drafts, brainstorming, translation support, policy search, training development, or internal productivity tasks, where appropriate safeguards are in place. Gray zones are uses that require consultation: HR decisions, customer communications, legal analysis, investigation outputs, high-risk third-party reviews, or regulated submissions.

A compliance program that treats every use of AI as suspicious will teach employees to hide. A compliance program that treats every use of AI as harmless will fail in its duty. The CCO must create the middle path: clear, risk-based, practical, and trusted.

Earn the Disclosure You Want

The article advises leaders to “earn the disclosure” they want. Employees need clear guidance on what AI use is encouraged, what is off-limits, and how to handle gray areas. The authors also warn that companies should not force employees to convert a useful prompt into a long process memo. Lightweight templates, short demos, and practical “show me how you built this” sessions are better ways to turn private methods into reusable knowledge.

That is a practical blueprint for the CCO. A CCO should create an AI disclosure process that is easy to use. It should not feel like an investigation request. It should not require a ten-page form. It should not punish employees for asking questions. The goal is to make disclosure normal.

That is enough to begin. The CCO can then partner with IT, Legal, Privacy, Cybersecurity, HR, Internal Audit, and business leaders to determine whether the workflow should be approved, modified, shared, restricted, or escalated. The key is tone. The message should be: “Show us what you are learning so we can help you use AI safely and scale what works.”

Reward Multiplier Behavior

The article warns against rewarding only individual AI productivity. If employees believe that sharing makes them less distinctive while others benefit, they will hide. Instead, companies should reward reusable workflows, peer adoption, quality improvements, and contributions that help others. The authors recommend giving credit in performance reviews, protecting time for continued experimentation, and closing the loop by telling employees where their contribution was used and what improved. This is where a CCO can help turn AI transparency into culture.

Compliance should not run a generic AI leaderboard that encourages unhealthy competition. Instead, the CCO should help build recognition for responsible AI multipliers: employees who find a better way to do their work, disclose it, help validate it, and enable the company to scale it safely. This turns AI governance from a prohibition system into an integrity system. Employees are not just being told what not to do. They are being recognized for helping the company do better.

In compliance terms, that means rewarding employees who:

  • Identify a safe AI workflow that improves the effectiveness of control.
  • Flag a risky AI use before harm occurs.
  • Develop a prompt that improves due diligence quality.
  • Create a monitoring workflow that identifies anomalies faster.
  • Help colleagues use approved tools properly.
  • Document limitations and human review requirements.
  • Share lessons learned from AI experimentation.

Treat Disclosure as a Contribution

One of the article’s most powerful points is that the manager’s reaction in the first thirty seconds after an employee discloses an AI workflow may be the decisive trust signal. If the employee is treated as though they cut corners, they learn to hide. If the disclosure is treated as something worth understanding, they learn that disclosure pays. The authors also warn that disclosure should not amount to unpaid labor; the employee should demonstrate the method once, and the company should then own the documentation, distribution, and support, while the discoverer keeps the credit. This is a direct instruction to compliance professionals.

A CCO should train managers to respond the same way. Most AI disclosures will not go to compliance first. They will happen in team meetings, performance conversations, project reviews, and manager check-ins. If local managers shame employees for using AI, employees will hide. If local managers automatically add more work to anyone who discloses a productivity gain, employees will hide. If local managers give credit and bring compliance in as a partner, employees will share.

The CCO’s AI Trust Playbook

A CCO who wants to fulfill this function should take five practical steps.

  1. Create a risk-based AI use framework. Define prohibited uses, encouraged uses, and uses requiring consultation. Make the guidance short, practical, and example-driven.
  2. Build a safe AI disclosure channel. This should be separate from the hotline in tone, even if connected administratively. Employees need a place to ask, “Can I use AI this way? ”without feeling as if they are self-reporting misconduct.
  3. Launch structured AI learning sessions. Invite employees to demonstrate useful workflows created with approved tools. Keep documentation light. Capture the use case, data inputs, review controls, risks, and adoption potential.
  4. Partner with HR on incentives. Ensure responsible AI sharing is recognized in performance reviews, promotion discussions, and leadership communications. Reward employees who become AI multipliers, not only those who quietly produce more.
  5. Report AI transparency metrics to leadership and the board. Do not only report policy completion or tool adoption. Report the number of disclosed workflows, number approved for broader use, number modified for risk reasons, number rejected, key risk themes, training gaps, and examples where disclosure improved both productivity and control.

Conclusion

The CCO should not try to own every aspect of AI. IT must own infrastructure. Cybersecurity must own security controls. Legal must advise on legal risks.  Privacy must address data protection. HR must address workforce impacts. Business leaders must own operational use cases. Internal audit must test the program. But the CCO can own the trust architecture.

The bottom line is straightforward. AI governance cannot be built only on restriction, monitoring, and fear. That approach may make the company look controlled while driving the most important AI activity underground.

The CCO has a different opportunity: to build an AI trust function that brings use cases, risks, questions, and innovations into the open. The compliance function should not be the department that says, “Do not use AI.” It should be the function that says, “Use it responsibly, show us what you are learning, and let us help the company scale it safely.” That is how compliance fulfills this function. It turns hidden AI use into visible learning, visible learning into governed practice, and governed practice into ethical business value.

Categories
Blog

What Interruptions Reveal About Corporate Culture

Every Chief Compliance Officer talks about culture. Every company claims to value ethics, integrity, respect, inclusion, and speak-up behavior. Those words appear in codes of conduct, CEO messages, training decks, town halls, leadership offsites, and annual ethics campaigns. Yet culture is not built into the code of conduct. It is revealed in the meeting.

That is the central lesson of Research: What Interruptions Reveal About Company Culture by William Degbey, Benjamin Laker, Baniyelme Zoogah, Sanjay Kumar Singh, and Ghulam Murtaza. The authors argue that workplace culture is shaped less by formal statements and engagement programs than by everyday interaction patterns, especially interruptions in meetings. Their research found that interruptions, redirections, and moments where employees were spoken over were not merely interpersonal annoyances. They were signals of whose voice carried weight in the room.

For the CCO, that finding should land with force. A company can have a beautifully written value of “speak up.” Still, if employees learn in ordinary meetings that certain people are cut off, ignored, or not credited for their ideas, the real culture is not to speak up. It is speak-only-if-you-have-power. That is a compliance issue.

Culture Is What Happens Before the Hotline

Compliance professionals often think about speak-up culture in terms of hotline reports, investigation data, employee surveys, and anti-retaliation policies. Those are important. The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) asks whether a company has a trusted reporting mechanism, whether employees feel comfortable using it, whether reporting is encouraged or chilled, and whether employees can raise concerns without fear of retaliation.

But by the time an employee reaches the hotline, the culture has already taught that person a great deal. It has taught them that if management listens. It has taught them whether disagreement is welcome. It has taught them whether bad news is punished. It has taught them whether junior employees can challenge senior leaders. It has taught them whether women, employees from underrepresented groups, remote employees, finance staff, compliance staff, or local market employees are taken seriously.

The author’s most important compliance lesson is that interruptions are cultural data. They are small, repeated, observable signals that show whether the company’s stated values are protected in daily business interactions or suspended when authority, speed, revenue, or hierarchy enters the room.

Why This Matters to Ethics and Integrity

Ethics and integrity depend on voice. Employees must be willing to raise concerns, ask questions, challenge assumptions, and slow down decisions when something does not look right. If the organization’s meeting culture teaches employees that unfinished concerns can be interrupted, redirected, or appropriated, then the company is training people not to speak.

The authors found that many senior leaders interpreted interruptions as signs of efficiency and engagement. They saw energetic cross-talk as evidence of a productive culture. Yet the follow-up study found that others experienced the same conduct as exclusionary and predictable. Interruptions were disproportionately directed at women and employees from underrepresented racial and ethnic groups. In the follow-up study, 19 of 27 interviewees described women being interrupted more frequently than men; all seven Black women interviewed described early-stage interruptions, and five said others later resurfaced their ideas without attribution.

For compliance, that is not simply an inclusion issue, though it certainly is. It is also a risk-detection issue. If certain voices are routinely cut off, then certain risks will be underreported. If certain employees must speak faster, more defensively, or only when explicitly invited, the company loses early warning signals. If some ideas are accepted only when repeated by someone with greater status, then the company is not evaluating risk on its merits. It is evaluating risk through hierarchy. That is how ethical blind spots form.

The Silent Cost of Being Interrupted

One of the most powerful findings in the article is that interruptions changed employee behavior. Twenty-one of the 27 participants in the follow-up study said they changed how they contributed to meetings. Some spoke faster or more defensively. Some pre-structured arguments to avoid being cut off. Some waited for explicit permission to speak. Others stopped contributing unless necessary. That is exactly what a CCO should worry about.

A healthy compliance culture does not require employees to perform perfectly polished courage. It gives employees room to raise half-formed concerns, ask awkward questions, and test whether something feels wrong before they have built a legal brief around it. Many compliance issues begin as fragments: “Something about this consultant does not feel right.” “The customer is asking for unusual documentation.” “The timing of this payment seems odd.” “Why are we routing this through that entity? ”I am not sure the data use matches what we told customers.” Those are early-stage compliance signals. They need space.

If the meeting culture rewards only fast, polished, confident speech, then employees who need time to frame a concern may never get the chance. The authors note that faster and more confident-sounding speech was often treated as more authoritative. In comparison, slower or less forceful speech was treated as incomplete and therefore easier to interrupt. For a CCO, the lesson is clear: do not build a compliance program that only works for the loudest person in the room.

From Tone at the Top to Conduct in the Room

Compliance professionals have long emphasized “tone at the top.” That remains important. But this article reminds us that tone at the top is incomplete unless it becomes conduct in the room.

The DOJ expects companies to demonstrate that compliance policies and procedures are integrated into operations and that a culture of compliance is embedded in day-to-day activities. That is precisely where meeting behavior matters. Meetings are where risk appetite becomes real. They are where employees learn whether the company actually values integrity when there is a deal to close, a target to hit, or a senior executive to satisfy.

A CCO should, therefore, ask:

What happens when ethics enters the meeting?

Does the room slow down?

Does the leader protect the person raising the concern?

Does someone capture the issue and assign a follow-up?

Does the business discuss controls and alternatives?

Or does the concern get interrupted, minimized, joked away, or pushed offline?

The answers will tell you more about culture than a slogan.

Reading Interruptions as Compliance Data

The authors recommend that leaders stop treating interruptions as isolated incidents and begin reading them as data. It suggests observing who gets interrupted, when the interruption occurs, and what happens to the idea afterward. Is the idea acknowledged? Is it dropped? Is it later picked up without credit? That framework can be directly adapted into a compliance culture assessment.

A CCO can ask compliance, internal audit, HR, or an outside facilitator to observe selected meetings where risk decisions are made. These might include third-party approval committees, deal review meetings, product governance meetings, investigations triage meetings, M&A diligence sessions, safety committees, privacy reviews, or regional leadership calls.

The observer should not simply count who speaks. This is not about policing manners. It is about understanding whether the company’s ethical culture allows risk information to travel upward and across the organization.

Slow the Meeting to Surface the Risk

The article warns that speed and forced momentum can amplify inequality. Faster conversations often favor those who already feel entitled to the floor. Those who anticipate interruption compress their thinking, hesitate, or wait for a clear opening. The authors recommend slowing the interaction: let people finish, pause before responding, reinforce the norm when someone is cut off, and rotate facilitation. This is deeply relevant to compliance.

Many corporate failures occur not because no one saw the risk, but because the organization moved past it too quickly. The payment had to go out. The distributor had to be approved. The quarter had to close. The launch date had to be met. The customer had to be retained. In that environment, “speed” can become a cultural value that overwhelms integrity. A CCO should help leaders build an “integrity pause” into decision-making.

Protect the Contribution, Not the Ego

The article also makes an important distinction. Calling out interrupters or turning every interruption into a lesson on etiquette often does not work. It can escalate the moment and personalize the issue. The better approach is to protect the contribution directly. The authors suggest short interventions such as “Let them finish,” “I want to hear the rest of that point,” and “Let’s come back to the idea that was just interrupted.” This is practical guidance for CCOs and compliance professionals.

When someone raises a compliance concern and is interrupted, the compliance professional does not need to accuse anyone of bad intent. This helps to create psychological safety around risk information. They tell the room that compliance concerns are not interruptions to business. They are part of doing business properly.

The CCO as Culture Observer

A CCO cannot improve culture solely by issuing policies. Policies matter, but culture is reinforced through repeated behavior. The DOJ guidance recognizes that policies and procedures must give effect to ethical norms and be integrated into day-to-day operations. That means the CCO must look beyond policy architecture and ask how people actually behave when decisions are being made.

Not every interruption is retaliation. Not every fast-paced meeting is unethical. Not every dominant speaker is a compliance risk. But patterns matter. Repeated interruption of certain people, functions, geographies, or types of concerns is cultural data. A CCO should treat it as such.

Turning the Article into a Compliance Playbook

A practical CCO response could include five steps.

  1. Add meeting behavior to the culture assessment. Ask employees whether they can finish raising concerns in meetings, whether leaders invite dissent, whether objections to risk are credited, and whether certain voices are routinely ignored.
  2. Observe high-risk meetings. Select a sample of decision-making forums and map interruptions, credit, follow-up, and closure. The goal is not surveillance. The goal is to understand whether the company’s values show up when risk is discussed.
  3. Train leaders on protecting concerns. Leadership training should include simple phrases or the preservation of unfinished risk points. A manager does not need to become a compliance expert to say, “Let’s hear the rest of that concern.”
  4. Build structured dissent into key decisions. For high-risk approvals, require a final risk round before the decision. Ask compliance, finance, legal, HR, internal audit, cybersecurity, or local-market leaders whether they see an unresolved issue.
  5. Report cultural signals to the board. Boards should hear more than hotline statistics. They should understand whether the organization’s meeting culture supports candor, dissent, and ethical escalation.

Improving Corporate Culture Around Ethics and Integrity

The broader message for compliance professionals is that ethics and integrity must become observable behaviors. Employees should see integrity in how meetings are run, how concerns are handled, how dissent is credited, how leaders respond to uncertainty, and how the company treats people who slow down a decision for the right reason.

The bottom line is straightforward. The words on the wall do not prove a culture of ethics and integrity. It is proven by who gets to speak, who gets heard, and what happens when someone raises a concern that slows the room down. For the CCO, the lesson from this article is powerful: look at the meetings. That is where the culture is already speaking.

Categories
Blog

Why Compliance Gets Branded as the Problem

Every compliance professional has heard the accusation. Compliance is too slow. Compliance does not understand the business. Compliance always says no. Compliance is where deals go to die. That reputation is so common that it has a shorthand: “Dr. No from the Land of No.”

Luis Velasquez’s article, Why Effective Leaders Get Branded as Problems, offers an important way for Chief Compliance Officers to think about this challenge. His central point is that when a leader creates friction, organizations often default to one explanation: the leader is the problem. Yet the article argues that friction usually comes from one of four sources: capability, perception, identity, or system. Because those sources may appear similar on the surface, organizations often collapse them into a single behavioral judgment, leading to poor decisions.

That insight maps directly onto compliance. When compliance creates friction, the organization may assume the compliance function is the problem. Sometimes that is true. Sometimes compliance really is slow, unclear, inconsistent, or disconnected from commercial reality. But often, compliance is not the problem. It is exposing the problem. The CCO’s job is to know the difference.

The Evaluation Trap for Compliance

Velasquez calls this dynamic the “evaluation trap.” Organizations overfocus on visible behavior and underweight the context surrounding it. If there is friction, the easy assumption is that the individual leader is the problem. For compliance, the same trap appears when business leaders say some of the following: “Compliance is blocking the deal. Compliance is slowing us down. Compliance is too rigid. Compliance does not understand how we make money.”

Those statements may contain useful feedback, but they are not a diagnosis. They are conclusions. A good CCO should not reject them defensively, but neither should the CCO accept them at face value. The better question is, “What is really causing the friction?”

Is compliance creating unnecessary delays? Is the business bringing compliance in too late? Is the policy unclear? Is the company’s incentive structure encouraging people to push risk downstream? Is the compliance team applying yesterday’s reputation to today’s improved process? Or is the function’s greatest strength, independence, being overused in a way that makes compliance appear detached from the business? The answer matters because each cause requires a different response.

Why “The Land of No” Is Dangerous

Being known as “The Land of No” is more than a branding problem. It is a control problem. When employees believe compliance exists only to stop things, they stop bringing compliance into decisions early. They delay disclosure. They frame facts selectively. They look for workarounds. They ask for forgiveness instead of guidance. The compliance function then receives issues late, with fewer options and higher stakes. That reinforces the perception that compliance is always saying no.

It becomes a vicious cycle. The business avoids compliance because it fears delay. Compliance receives incomplete or late information. Compliance responds with concern or rejection. The business concludes that compliance is a blocker. The next time, the business waits even longer to engage. That is how a compliance function loses influence while still technically having authority.

The Four Sources of Compliance Friction

Velasquez identifies four sources of leadership friction: a true skill deficit, historical reputation, overextension of identity, and the system as a blocker. Each has a direct compliance equivalent.

1. A True Compliance Capability Deficit

Sometimes the criticism is fair. The compliance team may be too slow. It may issue dense legal guidance that no one can use. It may give inconsistent answers across regions. It may lack business knowledge. It may escalate too many routine issues. It may have no clear intake process, no service-level expectations, no decision trees, and no practical playbooks.

The remedy is operational discipline. Build intake channels. Publish response-time expectations. Create risk-tiered approval paths. Train compliance professionals in business acumen. Give the business practical guidance, not abstract warnings. Measure cycle time, quality of advice, repeat questions, escalation frequency, and stakeholder satisfaction. A compliance function that wants credibility must be professionally managed.

2. Historical Reputation

Sometimes, compliance is judged by an old story. Velasquez describes “organizational drift,” where systems rely on outdated narratives rather than current evidence. Feedback may be based on historical reputation rather than recent interactions. Labels harden even when behavior changes.

In that case, behavior change alone may not be enough. The CCO must manage perception as deliberately as performance. That means asking business leaders for specific, recent examples. It means distinguishing current pain from legacy frustration. It means documenting improvements and communicating them repeatedly. It means publicizing examples where compliance helped a team win business the right way, accelerate a transaction, resolve a third-party issue, or design better controls.

3. Overextension of Compliance Identity

Compliance has core strengths: independence, skepticism, discipline, documentation, escalation, and control. Those strengths are essential. But Velasquez warns that a strength can become a habit, then an identity, and then a constraint. The problem is not always the absence of skill; sometimes it is the overuse of a strength in the wrong context. That is a powerful lesson for compliance.

A compliance function that is appropriately skeptical in a bribery investigation may be unnecessarily skeptical in a low-risk gift review. A team that properly demands documentation for a high-risk distributor may over-document a routine vendor. A CCO who must be firm with the board or regulators may unintentionally use the same posture in early-stage business counseling. The answer is not to weaken compliance. The answer is to expand its range.

Compliance should know when to be an investigator, an adviser, a control designer, an educator, and a decision escalater. Not every question requires the same tone, process, or level of scrutiny. A mature compliance function does not say yes to everything. It knows how to say “Yes, if.” That is very different from simply saying no.

4. The System as the Blocker

Velasquez calls the system-as-blocker issue the most misunderstood trap. What looks like a behavior problem may actually be caused by culture, structures, resources, incentives, or decision rights that make the desired behavior difficult to achieve. The article notes that organizations may say they want one thing while rewarding another. This is the most important lesson for the CCO.

Compliance is often blamed for delays caused elsewhere. Sales may bring a high-risk intermediary into compliance two days before a bid deadline. Procurement may onboard vendors before due diligence is complete. Finance may discover payment issues only after an invoice is pending. Legal may escalate a contract after commercial terms have already been promised. Senior leadership may say compliance matters, while compensation plans reward speed and revenue at any cost.

In reality, the system created the bottleneck. Compliance was simply the first function willing to name it. The CCO should identify these systemic blockers and bring them to management. If the business wants faster third-party approvals, it must engage compliance earlier. If the company wants fewer rejected transactions, it must define risk appetite before the deal is negotiated. If leadership wants a speak-up culture, it must protect reporters and discipline those who retaliate. If the

Building a Compliance Function Known for Solutions

The goal is not to become the “Land of Yes.” That would be worse. A compliance function that says yes to everything is not a compliance function. It is a permission slip. The goal is to become the Land of Know: a place where businesses gain clarity, options, risk intelligence, and practical pathways. That requires a different operating model.

  1. Compliance must engage early. The function should be embedded in strategy discussions, product design, market entry planning, third-party selection, M&A activity, data use, AI deployment, and incentive design. Late-stage compliance review is where trust goes to die.
  2. Compliance must define red lines and green lanes. Business teams should know which activities are prohibited, which require escalation, and which can move quickly through preapproved controls. Ambiguity produces both delay and resentment.
  3. Compliance must communicate in business language. “This violates Section X of Policy Y” may be accurate, but it is rarely sufficient. The better explanation is: “This creates an undisclosed conflict, weakens our audit trail, and could make the payment look improper. Here is how we can restructure it.”
  4. Compliance must offer alternatives. A “no” without a path forward should be reserved for real red-line issues. In most cases, compliance should identify a lower-risk route.
  5. Compliance must measure enablement. Do not only track training completions, hotline numbers, or policy attestations. Track advisory response time, time to third-party decision, percentage of matters resolved with conditions, number of early consultations, repeat issues by business unit, and examples where compliance helped preserve business value.

Sixth, compliance must own its mistakes. When compliance is slow, unclear, inconsistent, or overly rigid, the CCO should say so and fix it. Credibility increases when compliance holds itself to the same level of accountability it expects of the business.

The CCO’s Message to the Business

The CCO should be able to say, “We are not here to stop the business. We are here to help the business grow in a way that can withstand scrutiny. Sometimes that means yes. Sometimes that means yes with controls. Sometimes that means no. But every answer should be timely, clear, risk-based, and tied to the company’s values and obligations.”

That message must be backed by behavior. Business leaders will not judge compliance by slogans. They will judge it by how the function behaves when a deal is urgent, a market is risky, a senior executive is involved, or the answer is uncomfortable.

The lesson from Velasquez’s article is simple but profound. Before deciding that the leader is the problem, ask whether the diagnosis is wrong. For CCOs, the parallel lesson is equally important: before accepting that compliance is the problem, determine what the friction is really telling you.

A strong compliance function should never aspire to be popular at all costs. But it should aspire to be trusted. The way to avoid becoming “The Land of No” is not to say yes more often. It is to become clearer, earlier, more practical, more evidence-based, and more courageous about identifying whether the real issue sits in compliance, the business, or the system itself.