Da Vinci Week: Part 4 – The Last Supper and the Danger of Deterioration
In the previous post in the Leonardo Compliance Framework, Leonardo’s flying machines gave us Innovate, the principle that Compliance should help organizations capture the benefits of emerging technology while establishing governance appropriate to the risks. Yet approving and deploying a new technology, control, or compliance process does not demonstrate that it will remain effective over time. The organization must continue to evaluate whether the system operates as intended as the business and its risk environment change. That brings us to the fourth principle in the Leonardo Compliance Framework: Monitor.
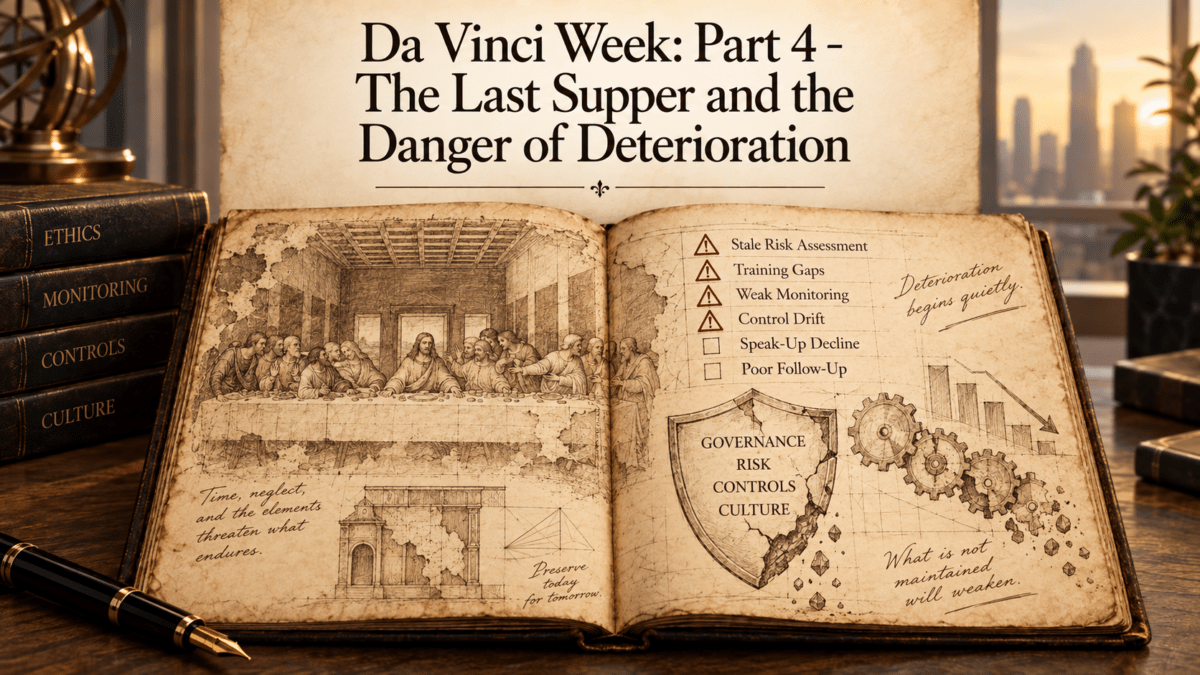
For this lesson, we turn to Leonardo’s The Last Supper. Leonardo experimented with a painting technique that provided greater artistic flexibility than conventional fresco methods. The result was extraordinary, but the physical work proved vulnerable to deterioration, and environmental conditions and later damage compounded those problems.
For compliance professionals, the lesson is not that experimentation was a mistake. It is that implementation represents the beginning of the control lifecycle rather than its conclusion. A system that operates effectively when introduced may weaken as people, processes, technology, incentives, and business conditions change. Modern compliance program effectiveness therefore requires more than evidence that a control exists. Management needs evidence that the control continues to work.
Implementation Is Not Effectiveness
Companies appropriately recognize major implementation milestones. A new third-party platform goes live, an updated Code of Conduct is launched, an investigation protocol is approved, or a sanctions-screening system is installed. These accomplishments demonstrate that the organization has taken action, but they do not establish that the underlying risk is being managed effectively.
Consider a third-party due diligence system implemented across a global enterprise. At launch, the workflow operates as designed. Business sponsors submit required information, higher-risk third parties receive enhanced review, approvals are documented, and Compliance can monitor the process. Two years later, an acquisition may have added thousands of vendors, employees may have developed workarounds because they consider the process too slow, regional teams may interpret risk classifications differently, and data feeds may no longer operate consistently. The system still exists, and the policy remains in force, but the control environment has changed.
This is the central monitoring challenge. Controls operate inside dynamic organizations. A gifts and entertainment process may become inadequate when the company enters markets involving greater interaction with government officials. Sanctions controls may require adjustment following significant geopolitical developments. A conflict-of-interest process may become less effective after an acquisition substantially expands the workforce. Controls designed for one business model may no longer fit another.
Effective monitoring should therefore connect directly to risk assessment. When the company’s risk environment changes, management should evaluate whether the controls designed for the previous environment remain appropriate. Successful implementation at one point in time cannot establish continuing effectiveness.
Monitoring and Testing Provide Different Evidence
Compliance professionals should distinguish between monitoring and testing because each provides different information about the control environment. Monitoring is generally continuous or recurring. It observes transactions, trends, exceptions, employee behavior, third-party activity, hotline information, investigation patterns, and other indicators that may reveal changes in risk or control performance. Testing is more focused and determines whether a particular control is appropriately designed and operating as intended.
Consider a control requiring enhanced approval for high-risk third parties. Monitoring may reveal the number of high-risk relationships being approved, how long reviews take, which business units generate the most exceptions, and whether particular patterns are developing. Testing may examine a sample of approved relationships to determine whether required due diligence was performed, red flags were resolved appropriately, approvals occurred at the correct level, and documentation supports the final decision.
Monitoring provides signals about what may be changing. Testing provides evidence about whether specific controls perform as expected. Together, they allow the CCO to move beyond the existence of a control and assess its effectiveness.
That distinction is particularly important when presenting compliance information to senior management and the board. Activity metrics may demonstrate that processes are operating, but control testing provides a stronger basis for determining whether those processes are managing the intended risk.
Ownership Turns Monitoring Into Accountability
Monitoring becomes considerably less effective when control ownership is unclear. This is a recurring problem in compliance because responsibilities often cross functional boundaries. Compliance may own the policy, Procurement may operate the process, IT may own the technology, Finance may process the payment, and the business may own the commercial relationship. When the control fails, each function may reasonably believe another function was responsible.
Effective control design should therefore identify an accountable owner responsible for ensuring that the control operates as intended. Compliance may provide oversight and challenge, and Internal Audit may provide independent assurance, but first-line functions should understand their responsibility for managing the underlying business risk.
Ownership should extend to the results of monitoring and testing. If testing identifies repeated exceptions, someone must determine whether the process requires modification. If a data feed fails, someone must restore it. If employees routinely circumvent a control, management must address the underlying behavior or process weakness. Monitoring without ownership produces information without accountability. The objective is not simply to identify control deficiencies but to create a management response to them.
Use Data to Identify Deterioration Earlier
Data analytics has significantly expanded the ability of compliance functions to identify changes in risk and control performance. Traditional monitoring often depended on periodic reviews of relatively small samples. Modern analytics can help organizations identify patterns across larger populations and, in some circumstances, detect changes earlier.
Payment data may reveal unusual transaction patterns, while procurement information can identify repeated overrides or vendor concentrations. Third-party data may identify expired due diligence or changes in risk characteristics. Hotline and investigation data can reveal shifts in allegations and recurring root causes, while HR information may provide signals concerning retaliation or culture.
The objective is not to collect the greatest possible volume of information or create the most sophisticated dashboard. The purpose is to identify data that help management determine whether risks are changing or controls are weakening. Exceptions are particularly valuable in this respect. An individual exception is not necessarily evidence of misconduct because legitimate business circumstances may justify deviation from a standard process. Patterns of exceptions, however, can reveal important information about the control environment.
If one business unit generates substantially more third-party exceptions than comparable operations, Compliance should understand the reason. Repeated overrides near quarter-end may indicate commercial pressure. Due diligence consistently completed after engagement may indicate that the formal process no longer reflects how the business actually operates.
A mature program should therefore examine the frequency, rationale, approving authority, concentration, and recurrence of significant exceptions. When exceptions become routine, they can create an unofficial alternative process that exists alongside the formal control environment. Data become valuable when they reveal that divergence early enough for management to respond.
Investigations, Monitoring, and Remediation Should Form a Feedback Loop
Investigations provide some of the strongest evidence about how controls operate under actual business conditions. Their findings should therefore influence what a compliance program monitors. If an investigation discovers that employees circumvented third-party controls by classifying consultants as ordinary vendors, remediation should address the immediate classification weakness, while monitoring should examine whether comparable patterns exist elsewhere. If an investigation identifies improper discounts used to create funds for inappropriate payments, transaction monitoring can be adjusted to identify similar discount patterns. If a retaliation investigation reveals adverse employment consequences shortly after an employee raised a concern, a compliance professional could consider whether HR data can identify comparable patterns.
This creates a feedback loop. Investigations explain how a control failed in a particular case, monitoring helps determine whether the same weakness exists elsewhere or is recurring, and remediation addresses the underlying problem. Monitoring has limited value if the organization does not act on what it learns. When testing identifies a significant deficiency, management should understand why it occurred, whether it is systemic, what risk it creates, what corrective action is required, and who owns that remediation. The organization should then validate that the corrective action addressed the weakness.
This last step is important because remediation completion and remediation effectiveness are different concepts. Issuing a revised procedure or completing additional training may satisfy a project milestone without solving the underlying problem. Follow-up testing provides evidence that the remediation worked.
The compliance learning cycle should therefore move from investigation to monitoring, from monitoring to remediation, and from remediation to validation.
AI Requires Continuing Monitoring
AI provides a particularly clear example of why approval and implementation cannot end the governance process. A company may conduct extensive review before deploying an AI application by assessing the vendor, testing the system, evaluating data use, classifying risk, and establishing human oversight. Those steps are important, but the system and its operating environment can change after deployment.
Vendors may update models, employees may develop new uses, data may change, integrations may expand access, and capabilities may increase. For higher-risk applications, monitoring should therefore be proportionate to the potential consequences and may include performance testing, incident monitoring, review of material overrides, validation of outputs, and reassessment following significant changes in functionality or use.
Agentic systems deserve particular attention because monitoring may need to address not only the quality of outputs but also the actions a system performs, the permissions it exercises, and whether it remains within its approved authority. The broader principle is the same as for any other compliance control. Governance should continue for as long as the organization relies upon the system.
Culture Also Requires Monitoring
Corporate culture presents a different monitoring challenge because no single metric establishes whether an organization has a strong ethical culture. Hotline reporting rates provide useful information but require interpretation. High reporting may indicate significant problems or employee confidence in the reporting system. Low reporting may reflect a healthy environment or fear of speaking up. Employee surveys provide additional information but capture sentiment at a particular moment, while investigation data reflect only matters that become known.
Compliance should therefore build a broader picture using multiple indicators, including reporting trends, employee surveys, exit interviews, focus groups, disciplinary information, HR data, investigation findings, and management assessments. Changes across these indicators may reveal emerging issues in particular business units, management teams, or employee populations.
Culture monitoring is especially important after leadership changes, acquisitions, restructurings, layoffs, or significant changes in incentives because these events can alter employee perceptions and behavior quickly. Formal policies may remain unchanged while the operating culture deteriorates. As with other compliance risks, the objective is not perfect measurement. It is obtaining enough reliable information to identify material changes and respond appropriately.
The Danger of Deterioration
The Last Supper provides a useful reminder that implementation captures a moment in time while organizations continue to evolve. Personnel, technology, incentives, business models, markets, and risks change, and controls that once worked can weaken in response. An effective compliance program therefore needs monitoring, testing, clear ownership, useful data, and validated remediation. These disciplines allow the organization to identify deterioration before a control weakness becomes a larger compliance failure.
The practical lesson for the CCO is that implementation should never be confused with effectiveness. Monitoring and testing should provide different but complementary evidence about control performance. Ownership should ensure that findings produce action, analytics should identify meaningful changes rather than simply populate dashboards, and remediation should be validated before the organization concludes that the underlying problem has been solved. That is Monitor, the fourth principle of the Leonardo Compliance Framework. A control deserves continuing confidence only when the organization has continuing evidence that it works.
From Monitoring to Documentation
Monitoring tells the organization what is happening, but institutional learning depends upon preserving what the organization learns. A company may conduct an effective investigation, identify a root cause, redesign a control, test the remediation, and reach a thoughtful risk decision, yet much of that value can disappear if the reasoning exists only in the memories of the people involved.
That brings us to the fifth and final Leonardo principle: Document. In Blog Post Five, Leonardo’s Notebooks: Documentation the Defensible Compliance Program, we will use Leonardo’s extraordinary record of observations, drawings, experiments, and ideas to examine documentation as a governance discipline. The discussion will focus on preserving significant compliance reasoning, establishing accountability, creating institutional memory, documenting remediation and AI governance decisions, and ensuring that what the organization learns today remains available to the people responsible for managing its risks tomorrow.