Categories
Blog

AMEX’s $350 Million AML Penalty: Part 2 – Lessons for CCOs and Boards

Paying a penalty and demonstrating an effective compliance program are different tasks. The AMEX enforcement actions make that distinction concrete.

In Part 1, we examined the OCC’s $350 million civil money penalty and findings concerning risk assessment, customer information, suspicious activity reporting, resources, training, and independent testing. The Federal Reserve’s Order focuses on enterprise-level change. Its starting point is board oversight.

For compliance professionals across industries, that is the opportunity: use the remediation requirements to challenge your own governance and controls. The orders bind the named entities. The broader applications below are recommendations, not claims that banking-specific obligations apply to every company.

Board oversight must produce accountable decisions

Within 90 days of the order’s effective date, AMEX’s board must submit a written oversight plan to the Federal Reserve. The plan must explain how directors will hold senior management accountable for remediation, ensure adequate resources, oversee an effective enterprise-wide BSA/AML compliance risk management program, and secure effective reporting and escalation. The board’s responsibilities expressly encompass remediation under both the Federal Reserve order and the OCC order.

Notice the allocation of responsibility. The board oversees. Senior management executes. Neither role should disappear into an instruction that “compliance will handle it.” For another company applying this lesson, I recommend that each material remediation item identify an accountable executive, responsible business owner, required resources, completion criteria, and independent reviewer. The CCO should help coordinate and challenge the work without becoming the default owner of every operational control.

COSO’s Internal Control–Integrated Framework provides a corresponding board-oversight benchmark. Under Principle 2, directors should independently oversee internal control development and performance. Translate that principle into board practice. Record the questions directors asked, the evidence management provided, resource decisions, and the follow-up required. A presentation should support an oversight decision, not substitute for one.

Make enterprise-wide compliance operational

The Federal Reserve requires AMEX to submit an acceptable plan within 90 days to improve enterprise-wide BSA/AML compliance risk management. Required content includes business-line and legal-entity policies, customer due diligence, cross-business-line suspicious activity reporting, and transaction-monitoring methodologies. Establish, analyze, test, and document monitoring rules and thresholds, paying attention to factors such as customer, product, or service, and geography.

That requirement suggests a practical exercise for any CCO: select a significant risk and trace how the organization treats it. Who collects the relevant information? Who assesses it? What triggers review? Which team investigates? When does senior management receive the issue? What reaches the board? But do not stop at the organization chart. The order calls for risk-based oversight of BSA/AML systems and the use of information from network partnerships, ATM partners, and third parties supporting compliance.

For a nonfinancial company, a comparable review could follow a high-risk distributor relationship from onboarding through orders, payments, exceptions, and termination. Test the handoffs, including information held by outside providers. The Federal Reserve also requires the travel-related services subsidiary to submit an acceptable Office of Foreign Assets Control (OFAC) compliance plan within 90 days. It must address risk assessment, ongoing job-appropriate training, and enhanced policies and screening procedures. This is a distinct sanctions-compliance remediation requirement; it should not be recast as a finding of a particular prohibited transaction.

Use COSO to examine the connections between controls

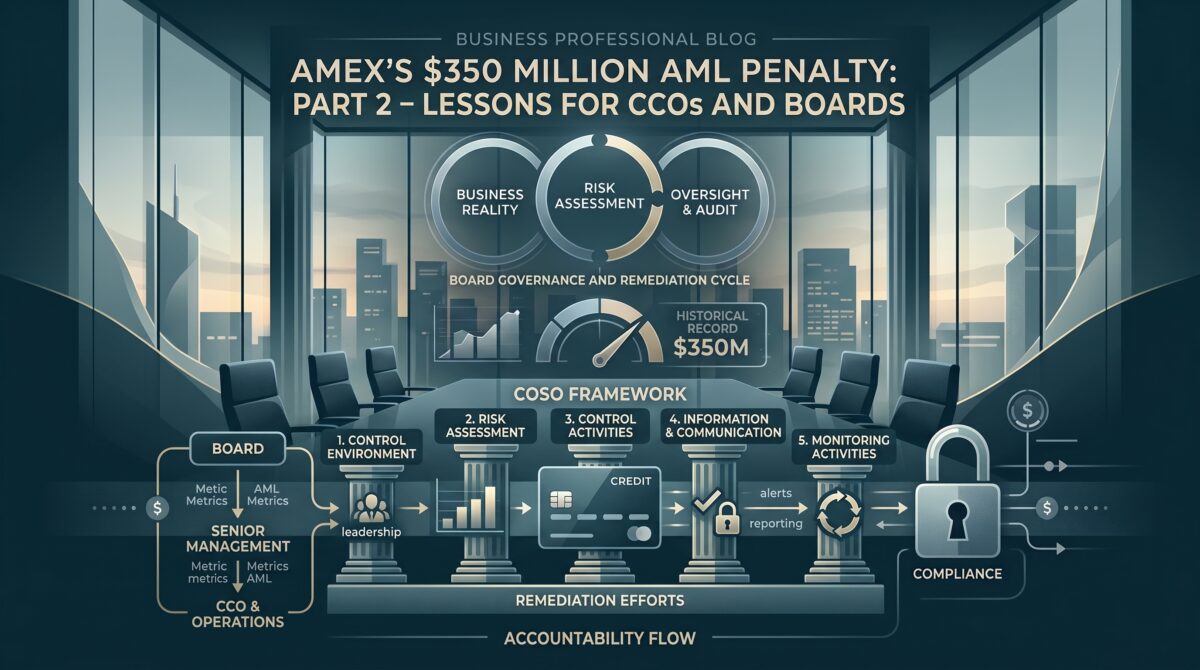
COSO organizes internal control around five components: control environment, risk assessment, control activities, information and communication, and monitoring activities. The framework emphasizes that these components must work together, not exist as separate administrative exercises. Applied to the AMEX findings, I recommend testing a connected chain of evidence.

Begin with the commercial activity and its risk assessment. Identify the resulting control, the person responsible, the information required, the escalation decision, and the independent test. Then examine what happens when one element fails. For example, don’t accept a customer-risk rating as useful just because a system has a completed field. Ask whether supporting information is reliable, whether the rating changes monitoring, and whether testing confirms that the resulting controls address the assessed risk.

COSO’s Principles 16 and 17 reinforce evaluating controls and promptly communicating deficiencies to those responsible for correction, including senior management and directors where appropriate. The practical point is to test relationships between controls, not merely their individual existence. Otherwise, management may demonstrate that every department completed its task without demonstrating that the overall risk was addressed.

Resource commitments need an operational explanation

The Federal Reserve requires the board to ensure senior management has adequate resources for required remediation. Make that discussion more useful than a comparison of this year’s compliance budget with last year’s. You should perform a capacity assessment for each critical control. Identify the workload, expertise, systems, quality-review capacity, and unresolved dependencies. Where management proposes automation, require evidence that the tool handles the relevant risk and that someone owns exceptions.

The DOJ’s 2024 ECCP provides a useful cross-check: evaluate program design, resources and authority, and effectiveness in practice. Its resource analysis should also examine personnel qualifications and compliance’s access to the board.

A board paper should therefore explain what a resource request will accomplish and what risk remains without it. Ask management to identify work that cannot be completed to the required standard, rather than presenting an unexplained staffing total.

Accountability must survive changes in personnel

Paragraph 4 of the Federal Reserve order deserves careful attention. Based on the firm’s investigative record compiled from 2024 to the order’s issuance, it prohibits the firm from directly or indirectly retaining individuals who meet all three specified conditions: participation in the underlying misconduct, formal disciplinary action connected to it, and separation or legal termination connected to that misconduct. The restriction covers retention as an officer, employee, agent, consultant, or contractor within the firm or its subsidiaries or affiliates.

This is not a blanket prohibition covering everyone who was investigated. The conditions are cumulative. The order also requires continued cooperation and substantial assistance with Federal Reserve investigations of parties affiliated with the involved institution.

For other CCOs, the lesson is to connect substantiated investigation outcomes with hiring, contracting, and vendor controls. Subject to applicable employment and privacy requirements, test whether a person excluded through one channel could return through another. Require documented review rather than allowing a change in job title or engagement structure to bypass accountability.

Remediation requires evidence, not just a timetable

The Federal Reserve requires implementation timelines with specific component deadlines. Approved plans must be adopted within ten days of approval and then promptly implemented. Amendments or rescissions require prior approval from the Reserve Bank. Board or authorized committee progress reports are due within 45 days after the end of the first full calendar quarter following the order and each quarter thereafter, addressing actions, schedules, and results. The 90-day submissions are plan deadlines, not requirements to complete every remediation measure within 90 days. For your program, distinguish a completed task from a corrected risk. A revised procedure is a deliverable. Evidence that employees apply it correctly is a different milestone.

The ECCP similarly examines root-cause analysis, control testing, lessons learned, and whether improvements can prevent or detect similar misconduct. The ECCP asks, “What methodology has the company used to identify, analyze, and address the particular risks it faces? What features of the company reduce its exposure to such risks? Is the company’s approach to risk management proactive or reactive? What information has the company identified and collected to help detect the type of misconduct in question? How has that information informed the company’s compliance program?” Use those questions to challenge proposed closure evidence.

The bottom line is that you must demonstrate implementation and an appropriately independent reviewer to evaluate operating effectiveness. Define the testing period, evidence, and acceptable results before the item is marked complete.

CCO actions and board questions

  • For the CCO: build one end-to-end evidence trail. Select a material risk and connect the assessment, controls, information, decisions, escalation, testing, and corrective action. Identify exactly where evidence is missing.
  • For the board: challenge ownership and capability. Which executive owns the unresolved risk? What resources are missing? What decision does management need from directors now?
  • For both: define success before declaring completion. What independent evidence supports closure? Have the underlying causes been addressed? What would alert us that the problem has returned?

Summary

The bottom line is that a compliance program must reflect the business’s actual risks and demonstrate that its controls work. The OCC’s central finding was a mismatch between the bank’s risk assessment and its operations: the assessment emphasized relatively narrow deposit activities while inadequately addressing dominant credit and charge card products. Weak customer identification, due diligence, suspicious activity reporting, independent testing, staffing, and job-specific training compounded that failure.

AMEX processed about $13 billion in suspected trade-based money laundering activity between June 2014 and May 2025 without timely identifying and reporting its full scope. It carefully distinguishes those findings from a conclusion that AMEX itself laundered that amount. The broader lesson is that completing assessments, filing reports, and delivering training do not, by themselves, establish program effectiveness.

We next considered the shift from compliance failures to governance and remediation, emphasizing that directors must oversee the work while senior management remains accountable for execution. Remediation should have identifiable executive and business owners, adequate resources, clear completion criteria, and independent review, rather than becoming an undefined assignment for the compliance department.

Drawing on COSO’s Internal Control Framework and the DOJ’s Evaluation of Corporate Compliance Programs, we reviewed how risk assessments, controls, information, escalation, and monitoring work together, and whether personnel and systems can perform the required work. The practical message for CCOs and boards is to distinguish a completed task from a corrected risk: a revised procedure is not proof of effective remediation. Leaders should require evidence that underlying causes have been addressed, controls operate effectively, and recurring problems will be detected. Risk alignment, accountability, and demonstrated effectiveness must become part of how the business is governed.
Categories
Innovation in Compliance

Innovation in Compliance: Dr. David Gruder on Collaborative Accountability and the Psychology of Compliance

Innovation comes in many areas, and compliance professionals need to not only be ready for it but embrace it. Join Tom Fox, the Voice of Compliance, as he visits with top innovative minds, thinkers, and creators in the award-winning Innovation in Compliance podcast. In this episode, host Tom interviews Dr. David Gruder, a clinical and organizational development psychologist.

Dr. Gruder is trained in long-range master planning and is an ordained interfaith rabbi, bringing psychological and spiritual principles to business, culture, and compliance. He introduces “collaborative accountability” as a growth-oriented alternative to coercive, shame-based accountability and outlines four interlocking procedures: accountability-capable agreements, consistently elevating best practices, converting breakdowns into growth opportunities, and collaborative disengagement. He defines accountability as taking responsibility for the impacts of how one spends life energy on those to whom commitments are made, distinguishing good intentions from measurable commitments. Gruder describes three competing futures, regressionism, “Homo machina” transhumanism, and “Homo spiritus,” and urges leaders to align vision, mission, and ethics accordingly. He defines organizational nimbleness as resilience plus innovation and emphasizes marrying legal and psychological compliance.

Key highlights:

  • Spiritual Lens at Work
  • Collaborative Accountability
  • Why Psychology Matters
  • Defining True Accountability
  • Humanity’s Three Futures
  • Business Ethics and Influence

Resources:

  • DrGruder.com
  • TheCESS.com
  • Facebook: @davidgruder / @drdavidgruder
  • X (Twitter): @davidgruder
  • LinkedIn: linkedin.com/in/gruder
  • Instagram: @drgruder
  • YouTube: @DavidGruder

Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Innovation in Compliance was recently honored as the Number 4 podcast in Risk Management by 1,000,000 Podcasts

Categories
AI Today in 5

AI Today in 5: October 13, 2026, The 10 Person Compliance Team Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. Does AI prefer AI-written resumes? (FT)
  2. Using AI can give fintechs a 10-person compliance team. (Pymnts)
  3. AI fuels the M&A machine. (WSJ)
  4. Collapsing your compliance vendor stack. (FinTechGlobal)
  5. AI creates fake murder hotline tips. (Reuters)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Daily Compliance News

Daily Compliance News: October 13, 2026, The Not Working with ICE Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we cover four stories from the business world, compliance, ethics, risk management, leadership, or general interest for compliance professionals.

Top stories include:

  • Does AI prefer AI-written resumes? (FT)
  • Prepare for a new wave of congressional investigations. (Bloomberg)
  • Will the US sanction the ICC into oblivion? (WSJ)
  • Target says it is not working with ICE. (NYT)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Blog

AMEX’s $350 Million AML Penalty: Part 1 – What Went Wrong

A compliance risk assessment should describe the business the company actually conducts. What happens when it does not?

The AMEX enforcement actions provide a consequential answer. On October 8, 2026, the Office of the Comptroller of the Currency (OCC) announced a $350 million civil monetary penalty (OCC Penalty) and a cease-and-desist order(OCC Order) against American Express Company and American Express Travel Related Services Company, Inc. (collectively, AMEX) for Bank Secrecy Act and anti-money laundering deficiencies. The Federal Reserve separately issued a cease-and-desist order (FED Order) against AMEX. The OCC Press Release noted that the monetary penalty was imposed by the OCC, not both agencies.

For Chief Compliance Officers, directors, counsel, and internal auditors, the central lesson extends beyond banking: a compliance program must reflect the business’s actual risks, and oversight must demand evidence that it works. Over the next couple of blog posts, we will explore the Orders and Penalties. Today, we’ll start with what went wrong at AMEX.

What the enforcement record establishes

The OCC found violations involving the BSA/AML program, suspicious activity reporting, customer due diligence, and customer identification. According to the OCC Order, from approximately June 2014 through May 2025, the bank processed approximately $13 billion in suspected trade-based money laundering activity. That figure includes suspicious card charges and associated repayments. In some cases, the activity passed through accounts linked to bank insiders. The bank periodically reported suspicious activity but lacked the controls and monitoring capabilities to identify and report its full scope promptly.

Precision matters. The $13 billion figure does not mean AMEX laundered that amount, nor should it be described as $13 billion in distinct criminal proceeds. The findings concern suspected activity and failures in detection, evaluation, and reporting. The reference to insider-associated accounts also does not establish that every associated individual knowingly participated in misconduct.

The risk assessment did not match the business

The OCC’s most instructive finding concerns the program’s starting point. The bank’s risk assessment focused on its relatively narrow demand deposit products and services while giving insufficient attention to its more dominant credit and charge card products. This was a mismatch between the business being conducted and the risks being assessed.

For a CCO, the question should be immediate: does our assessment accurately represent how our company generates revenue, moves money, serves customers, and uses intermediaries?

The DOJ’s 2024 Evaluation of Corporate Compliance Programs (ECCP) begins its risk-assessment analysis by understanding the company’s business and examining how compliance scrutiny and resources address its risks. The ECCP asks “how the company has identified, assessed, and defined its risk profile, including specific factors that mitigate the company’s risk, and the degree to which the program devotes appropriate scrutiny and resources to the remaining spectrum of risks.” That provides a useful comparison here, not an additional finding against AMEX or the legal basis for these orders.

Consider a hypothetical manufacturer that rigorously reviews employee expenses but inadequately evaluates high-risk distributor payments. The expense controls may function exactly as designed. They still do not answer the more consequential risk question. The lesson is that the largest business line does not always present the greatest compliance risk. Management should demonstrate a defensible relationship between business activities, assessed risks, and control coverage. Completing an assessment is not the same as assessing the right business.

Customer information failures undermined monitoring

The OCC identified weaknesses in two distinct functions. Customer identification procedures did not adequately support a reasonable belief that the bank knew each customer’s true identity. Ongoing customer due diligence did not effectively establish the nature and purpose of customer relationships, undermining risk ratings and monitoring. Read together, these findings describe more than incomplete onboarding files. They connect customer knowledge to the ability to recognize transactions that warrant further investigation.

For businesses outside banking, the useful analogy is the difference between collecting a distributor’s documents and understanding what the distributor actually does. Who is involved? What commercial purpose does the relationship serve? What activity would fall outside that purpose?

The OCC also found systemic breakdowns in suspicious activity monitoring, investigation, and reporting, resulting in late, missed, or incomplete suspicious activity reports (SARs). Those failures extended beyond suspected trade-based money laundering to other suspicious activity. Importantly, the bank did file some reports. The OCC criticized the bank for failing to promptly identify and report the full scope of the activity.

That distinction should change how a compliance committee evaluates performance. Ask what the reporting process covered, what it missed, and how those conclusions were tested. A report count alone does not establish the answer. The same challenge should be applied to investigation totals, due diligence completions, and training statistics.

Audit, resources, and training did not provide effective safeguards

The OCC found that the internal audit did not effectively monitor BSA/AML compliance. Independent testing was neither appropriately scoped nor effective relative to the bank’s risk profile, contributing to delayed detection and remediation of deficiencies. The key takeaway is that an audit plan should challenge the compliance program’s assumptions, not simply confirm that documented procedures were followed. Testing a process against an incomplete view of risk can leave the underlying problem untouched.

The findings also addressed staffing and capability. Historically, the bank has not supported its BSA/AML program with appropriate resources, including personnel with the necessary skills, expertise, and training. Employee training did not adequately address job-specific responsibilities, impairing identification, escalation, and reporting of risks and suspicious activity.

For compliance leadership, those findings support a practical distinction: headcount, competence, and operational capacity should be assessed separately. Hiring more people should not substitute for determining which expertise a control requires.

Likewise, training should be evaluated against decisions employees must make. Can an investigator recognize a relevant pattern? Can an account manager identify a concern and route it correctly? Can a director challenge an explanation of control effectiveness? These are better questions to bring to the next program review than whether everyone completed the assigned course.

The Federal Reserve extended the concern to the enterprise

The FED Order identified significant deficiencies in the enterprise-wide financial crimes risk management program, including transaction monitoring, fraud referral processes, third-party risk assessment, and financial crimes risk management. Its order directs the AMEX board to address management accountability, remediation resources, program effectiveness, and reporting and escalation.

The broader governance lesson is not that the compliance department alone must work harder. Management responsibilities and board information should be examined alongside the technical controls. A remediation plan should identify who must act, what resources are required, and how directors will know whether the action worked.

AMEX’s public response

In its October 8 public statement, AMEX said internal and external reviews identified areas for improvement. It described investments in people, technology, training, governance, and oversight, as well as cooperation with regulators and law enforcement. Chairman and Chief Executive Officer Stephen J. Squeri stated, “While we have made meaningful progress, we know there is more work to do.”

The company also said the penalty would not affect full-year 2026 guidance, that the orders imposed no asset cap, and that anticipated remediation costs would not affect 2027 guidance. These are company statements, including forward-looking expectations, not regulatory findings about remediation effectiveness. The Federal Reserve separately acknowledged cooperation and remedial actions already undertaken. Progress deserves recognition, but corrective work should not be confused with demonstrated completion.

Three practical takeaways

  1. Start with business reality. Compare the risk assessment with actual products, transaction flows, customer relationships, and third-party arrangements. Require explanations for significant gaps in coverage.
  2. Challenge evidence of effectiveness. Ask the internal audit to test whether controls identify the risks that matter, not merely whether staff follow procedures. Examine decision quality and timeliness alongside activity counts.
  3. Make capability a governance discussion. Bring the board a clear account of required expertise, unresolved resource constraints, and the risks those constraints leave exposed.

The question for the next board meeting is straightforward: What evidence demonstrates that our compliance program addresses the business we actually operate?

Join us tomorrow, in Part 2, as we examine how the Federal Reserve’s remediation requirements can help CCOs and directors turn that question into accountable action.

Categories
FCPA Compliance Report

Natural Disaster Expo 2026 Speaker Series: John Capodice on Disaster Recovery’s Blind Spot: Planning for Access

Welcome to Natural Disasters Expo Houston! For its fifth year, Natural Disasters Expo USA comes back to Houston on October 14–15, 2026, at the George R. Brown Convention Center. And there’s no better place. This city knows what it takes to prepare for disasters, respond, and rebuild afterward.

For two days, industry leaders, government agencies, first responders, and resilience professionals will come together with one shared goal: helping communities weather the next storm stronger than the last. Explore new solutions and technology, learn from front-line experts, and meet the partners who will help you turn preparedness into action. Whether you’re here to learn, share, or collaborate, you’re part of the effort to build a more resilient nation.

Tom interviews John Capodice, Executive Vice President at Sterling Site Access Solutions, about Sterling’s role in disaster recovery when utilities face anomalous events and need to restore power rapidly.

Capodice previews his Disaster Expo presentation on quickly deploying safe temporary roads, bridges, and man-camp platforms, explaining Sterling’s capabilities as the world’s largest manufacturer of matting and access products to create stable access when storm-damaged ground or unsafe crossings prevent entry. He emphasizes a common “blind spot” in disaster recovery: access is often the first victim of a storm, and planning reduces time lost and costs. Sterling offers pre-incident consulting to identify weak spots, establish MSAs, and support utilities, co-ops, and other sectors, including wind, solar, and civil projects, with safe, efficient work platforms.

Resources:

Natural Disasters Expo USA

Get your Ticket

Conference Agenda

Speakers 2026

Categories
FCPA Compliance Report

FCPA Compliance Report: Steph Holmes on Managing the Long Tail of Hotline Reports

In this episode, Tom Fox welcomes back his friend and colleague Steph Holmes of EQS Group. They take a deep dive into the “long tail” of hotline/whistleblower reports and why retaliation risk persists after an investigation closes, serving as a key indicator of organizational culture.

Holmes recommends starting with a retaliation-specific risk assessment, especially as EU whistleblower rules shift the burden to employers to prove they did not retaliate. They discuss creating scalable, risk-based visibility into significant post-complaint employment actions (e.g., termination, demotion, compensation, RIF selection) while sharing only minimum necessary context, emphasizing timing, decision-maker involvement, prior retaliation concerns, and strong documentation. Holmes highlights less obvious retaliation signals (negative review shifts, exclusion, increased scrutiny, unfavorable assignments) and suggests periodic check-ins, pulse surveys, and potential AI-enabled trend detection. They also stress training managers to “listen up,” respond appropriately, and escalate concerns, and to use feedback to improve speak-up confidence.


Key highlights:

  • Hotline Long Tail
  • Retaliation Risk Assessment
  • RIF And Confidentiality Gaps
  • Subtle Retaliation Signals
  • Training Managers
  • Culture Impact And Feedback

Resources:

Steph Holmes on LinkedIn

EQS Group

 Tom Fox

Instagram

Facebook

YouTube

Twitter

LinkedIn

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
AI Today in 5

AI Today in 5: October 12, 2026, The Surviving an Audit Edition

Welcome to AI Today in 5, the newest addition to the Compliance Podcast Network. Each day, Tom Fox will bring you 5 AI stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to AI Today in 5. All from the Compliance Podcast Network. Each day, we consider five stories from the business world on compliance, ethics, risk management, leadership, or general interest in AI.

Top AI stories include:

  1. AI demanding a ‘verification tax.’ (NYT)
  2. Does using AI for pricing raise antitrust concerns? (Reuters)
  3. How AI can help fix cybersecurity compliance. (Help Net Security)
  4. Can your AI survive a regulator’s audit? (FinTechGlobal)
  5. 4 CA laws reshaping rules for workplace AI. (EpsteinBeckerGreen)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Daily Compliance News

Daily Compliance News: October 12, 2026, The AI Verification Tax Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we cover four stories from the business world, compliance, ethics, risk management, leadership, or general interest for compliance professionals.

Top stories include:

  • AI demanding a ‘verification tax.’ (NYT)
  • Does using AI for pricing raise antitrust concerns? (Reuters)
  • What’s a $100K AMEX bill between friends? (Yahoo!News)
  • Can you bet on a jury outcome (Answer: you bet!). (WSJ)

My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Blog

Modern Philosophers and Compliance: Part 5 – Hans Jonas and Responsibility for the Future of Corporate Compliance

This week we have concluded our lengthy exploration of the philosophical underpinnings of the modern corporate compliance program. We have examined Hannah Arendt and her concepts of personal responsibility and how they relate to the modern compliance program; Simone de Beauvoir and the conditions for ethical action in a corporation; John Rawls and institutional justice and fairness in a corporate compliance program; and Jürgen Habermas and the governance of speaking up. In Part 5, we conclude by looking at Hans Jonas and the responsibility for the future of corporate compliance programs.

A corporate decision can continue affecting people long after its sponsors have moved on. Technology makes that possibility especially important. A system approved for a limited purpose can expand across business units, influence thousands of decisions, and create consequences that emerge gradually. Hans Jonas asks us to consider the responsibility that power entails.

For the Chief Compliance Officer (CCO), that perspective changes the approval question. What evidence supports proceeding, what harm could follow, and who will remain responsible as circumstances change? These questions connect ethical responsibility with the practical governance of technology, particularly artificial intelligence.

Technological Power Expands Responsibility

In The Imperative of Responsibility (1984), Jonas reconsidered ethics in light of technological power. His concerns included ecological destruction, nuclear threats, and genetic engineering. The scale and reach of human action created duties extending toward posterity and the environment.

His argument reaches beyond responsibility for an immediate transaction. Decisions can affect the conditions under which others will live, including people unable to challenge those decisions today. The ethical horizon must therefore extend beyond the decision-maker’s own interests and present relationships.

The application to corporate compliance is an interpretation of that argument. Jonas did not write an AI approval checklist. His philosophy nevertheless provides a reason to examine the duration, scale, and reversibility of technological choices. A company’s responsibility should reflect the consequences its capabilities make possible.

This perspective complements the earlier Enlightenment chapters. Evidence and clear reasoning remain essential. Jonas asks what responsibilities follow when the organization can act on that knowledge at a scale whose full consequences remain uncertain. For compliance, the answer begins with disciplined anticipation and continues throughout the activity’s life.

The Approval Whose Consequences Keep Growing

What do you think about the following situation? A multinational company purchases an AI tool to prioritize third-party due diligence. The tool ranks potential intermediaries using corporate records, transaction information, and public data. During a pilot, it reduces the time required to identify files for additional review.

Management approves a broader deployment. Over the following year, procurement teams begin treating low-risk scores as permission to abbreviate diligence. The vendor changes the model. The company expands into countries poorly represented in the original testing. Responsibility for reviewing performance splits among procurement, technology, and compliance.

Later, an investigation finds that several intermediaries with incomplete ownership records received low-risk scores. The model treated missing information as weak evidence of risk, while reviewers interpreted the scores as evidence that meaningful checks had been completed. No one had tested that assumption in the new markets.

The scenario does not establish that AI inevitably weakens diligence. It shows how a limited approval can take on a different operational meaning. A prioritization tool became a basis for reducing scrutiny. Changes in use, data, and responsibility accumulated after the initial decision.

Jonas helps the CCO frame the governance issue. The approval must account for how the system could develop and what its outputs could enable. Responsibility includes the conditions for expansion, the information needed to detect failure, and the authority to intervene before harm spreads.

The DOJ Connection Through Emerging Risk

The Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) explicitly addresses emerging technology. It asks how companies assess AI’s impact on criminal-law compliance, integrate technology risk into enterprise risk management, and address unintended consequences and misuse. It also examines controls supporting trustworthy, reliable use.

These inquiries make technology governance part of the compliance effectiveness assessment. A company using AI within its own compliance function should apply the same discipline it expects from business operations. The stated purpose of improving compliance does not establish that the tool works appropriately.

In our question above, the CCO should define the approved use precisely, as mission creep is always to be avoided. Prioritizing review is different from authorizing a third party. The decision record should explain what the score means, what it cannot establish, and which diligence requirements remain mandatory. Users need instructions that preserve those distinctions under commercial pressure.

Changes should trigger review according to their significance. A new market, a material vendor update, or a proposal to automate approvals may require additional testing and authorization. The company should assign an accountable owner who can obtain the necessary evidence across functions. Shared participation works best when responsibility for the final decision remains clear.

Uncertainty Calls for Proportionate Safeguards

Companies rarely possess complete information before introducing a technology. See generally Andrew McBride in Recommended Practice for Buying & Selling Compliance Technology, which is based on surveys of compliance technology buyers and vendors. Governance must make uncertainty visible and connect it to a defensible decision. The relevant questions include the severity of possible harm, the number of people affected, the ability to detect errors, and the possibility of reversing the consequences.

A tool that suggests training topics raises different concerns than one that determines which allegations to investigate. The latter can affect whether misconduct is detected at all. Its potential benefit should be assessed alongside the consequences of overlooking a credible concern.

For the third-party tool, a practical safeguard would be to sample low-risk classifications for independent review. Testing only the files the model flags leaves false reassurance largely unexamined. The company should also assess how missing records, unfamiliar languages, and changes in business conditions affect performance.

Deployment can be limited while those questions are tested. Appropriate measures might include restricted uses, defined populations, additional review, or a delay where critical evidence is missing. These are proposed governance responses to the hypothetical. Their suitability depends on the use case and the harm at stake.

The business case should include the cost of maintaining those safeguards. A project whose expected savings depend on eliminating the review needed for reliable operation has an unresolved design problem. Compliance should make that tradeoff explicit before approval and when the project’s economics change.

Turning Responsibility into Continuing Governance

The NIST AI Risk Management Framework provides a voluntary approach to managing AI risks. Its core functions are Govern, Map, Measure, and Manage. Together, they offer an organizational structure for understanding uses and impacts, evaluating risks, and determining responses throughout the AI lifecycle.

Applied to our hypothetical, governance assigns ownership and approval authority. Mapping identifies where the model operates, who relies on its scores, and who could be harmed by error. Measurement tests performance under relevant conditions. Management determines whether to proceed, add safeguards, restrict use, or suspend the tool. These activities should inform one another as evidence changes.

ISO/IEC 42001:2023 specifies requirements for establishing, implementing, maintaining, and continually improving an AI management system. Its relevance here is the organizational discipline of sustained responsibility. The company needs repeatable processes that survive personnel changes and remain connected to actual use.

These frameworks serve different purposes from DOJ’s prosecutorial guidance. Adopting a framework or obtaining certification does not establish compliance with every applicable law or prove that a particular deployment is effective. The company still needs evidence that its controls address the risks of its own activities.

The practical objective is to maintain a record that connects the approved purpose, responsible people, test results, changes, incidents, and remedial decisions. That record enables the next owner to understand why the system was approved and what conditions remain essential to its continued use.

Intervention Must Remain Possible

Responsibility becomes difficult to exercise when the organization cannot change course. Before deployment, determine who can suspend the system, what circumstances require escalation, and how business will continue during an interruption. A fallback process must be sufficiently resourced to operate when needed.

In the hypothetical, repeated unexplained low-risk scores involving missing ownership records could trigger restricted use and a review of affected files. The response should examine past decisions and current performance. Correcting the model does not resolve every consequence of earlier reliance on it.

Vendor arrangements also matter. (See McBride, above.) The company should seek information and contractual provisions appropriate to its risks, including notice of material changes, access to relevant performance evidence, and cooperation with investigations. When adequate visibility is unavailable, decision-makers should account for that limitation in deciding whether and how to use the tool.

Human review requires similar scrutiny. A named reviewer adds little protection if that person lacks time, training, supporting information, or authority to question an output. Test whether reviewers can identify errors and whether their interventions produce corrective action. Human responsibility needs operational support.

Board Oversight Must Extend Beyond Launch

Boards need a view of material technology risks over time. Approval-stage reporting often emphasizes expected benefits. Subsequent oversight should examine whether those assumptions remain valid, whether the use has expanded, and whether the organization retains the resources and authority needed to manage it.

The ECCP examines the information used in board oversight and compliance access to governing authorities. For significant AI deployments, the CCO can use those channels to report unresolved limitations, incidents, changes in use, and overdue corrective actions. Technical detail should explain a decision the board needs to understand.

Directors should ask whose interests the business case omits. Future customers, workers, communities, or business partners may bear costs not reflected in the current project budget. The analysis should consider foreseeable consequences and explain material uncertainties without pretending to predict every outcome.

Accountability should also survive the original sponsor’s departure. Assign continuing ownership, require documented handovers, and maintain review obligations through reorganizations and vendor changes. A system’s effects may persist for years. Its governance should not depend on one individual remembering the conditions attached to launch.

Five Key Jonas Takeaways for the Compliance Professional

  1. Assess consequences across time and scale. Consider who could be affected, how harm might accumulate, and whether decisions can be reversed. Include foreseeable effects beyond the immediate business case.
  2. Define the approved use and review material changes. Specify what a system may do, what its outputs establish, and which decisions require human authorization. Reassess expansion, vendor updates, and changes in operating conditions.
  3. Match safeguards to uncertainty and potential harm. Test the errors that routine monitoring could miss. Use staged deployment, independent review, or restrictions where the evidence does not support broader reliance.
  4. Preserve the ability to intervene and remediate. Establish suspension authority, workable alternatives, and a process for reviewing past decisions. Verify that human reviewers have the resources and authority to act.
  5. Make responsibility endure beyond the project team. Maintain ownership, evidence, and review obligations through organizational change. Give the board a clear account of unresolved risk and the decisions required.

Jonas brings our series to a fitting conclusion. Arendt asks who exercises judgment. Beauvoir asks whether people can act on it. Rawls tests the fairness of the rules, and Habermas examines whether concerns influence decisions. Jonas extends responsibility to the consequences that outlast those discussions and to people who cannot participate in them.

Together, these perspectives give compliance professionals a practical agenda for governing corporate power. Build processes that let people question, decide, explain, and correct their actions. Then ask the final board question: what obligations will this decision leave to others, and what have we put in place today to meet them?