Categories
Daily Compliance News

Daily Compliance News: May 15, 2026, The Adani Walks Free Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • Nigerian ex-oil minister gets 75 years for corruption. (Reuters)
  • Adani pledges $10bn and gets a free pass. (NYT)
  • Commit fraud, self-report, and walk free in SDNY. (FT)
  • The US makes more corruption claims against Mexico. (The Guardian)

For more information on the use of AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.

Categories
Blog

The Culture Builder’s Trilogy: Part 3 – The Art of Celebration: What Compliance Chooses to Honor Becomes Culture

Ed. Note: We conclude our three-part blog post series on three recent books by Hemma Lomax and Ashley Dubriwny. There are The Art of Ideation, The Art of Celebration, and The Art of Implementation.

The final book in Hemma Lomax and Ashley Dubriwny’s trilogy, The Art of Celebration, completes the arc. Ideation imagines what is possible. Implementation gives that possibility form. Celebration sustains the culture by recognizing what matters, reinforcing what works, and creating the memory that carries the organization forward.

For compliance professionals, celebration may sound like the least obvious compliance discipline. That would be a mistake. The authors make clear that celebration is not decorative. It is strategic. It is a feedback system. It teaches people what the culture values. It turns behaviors into norms and norms into identity. The compliance lesson is profound: what the organization celebrates, it multiplies.

Lesson One: Recognition Is a Control Signal

The DOJ’s Evaluation of Corporate Compliance Programs (ECCP) focuses on incentives and consequences, providing compliance professionals with a regulatory rationale to take compliance seriously. The DOJ’s compensation and clawback Pilot Report states that prosecutors consider whether companies use positive incentives for ethical behavior and compliance leadership, whether compensation systems include compliance criteria, and whether companies penalize breaches of the compliance program.

That means recognition is not merely an HR activity. It is part of the control environment. When a company celebrates only sales growth, deal speed, cost reduction, or heroic problem-solving after avoidable chaos, employees learn what really matters. When a company celebrates employees who pause a transaction over a red flag, escalate a concern, improve a control, cooperate in an investigation, or protect a colleague from retaliation, employees learn a different lesson. The question for the CCO is not whether the company celebrates. Every company celebrates something. The question is whether those celebrations are aligned with the Code, controls, risk appetite, and ethical commitments.

Lesson Two: Celebration Can Strengthen Speak-Up Culture

The Art of Celebration explains that appreciation and recognition can foster conditions of trust, belonging, openness, and moral reasoning. The book ties celebration to the willingness to speak up, take healthy risks, protect colleagues, and choose integrity. This has direct compliance relevance. Employees do not report concerns simply because the hotline exists. They report when they believe the organization values truth over comfort. They report when managers respond with care. They report when prior reporters were not punished, isolated, or ignored.

Celebration can reinforce this. A company should not publicly identify confidential reporters, but it can celebrate the behavior of raising concerns, asking hard questions, and improving systems. It can share anonymized stories showing that reports led to meaningful improvements. It can recognize managers who receive concerns well. It can reward teams that identify and remediate control gaps before they become enforcement problems.

Lesson Three: Celebration Must Be Aligned, or It Becomes Dangerous

The authors are careful to address the shadow side of celebration. Misaligned recognition can distort culture. They cite examples where companies celebrated the wrong behaviors, including aggressive sales targets, engineering brilliance without ethical oversight, deal-making over transparency, speed over safety, and ambition over rigor.

This is where compliance professionals should pay close attention. Wells Fargo did not fail because it lacked stated values. It failed because its operating incentives and recognition systems pushed employees to open accounts at any cost. Boeing’s 737 MAX crisis offers another cautionary tale about what can happen when cost, schedule, and production pressure overwhelm engineering judgment and safety culture. Volkswagen shows the risk of celebrating technical performance while ethical guardrails lag. Celebration is therefore not harmless. It is a governance tool. If the company celebrates the wrong thing, it creates evidence of cultural misalignment. If it celebrates the right thing, it demonstrates culture in practice.

Lesson Four: Metrics of Morale Must Be Ethical

One of the most forward-looking sections of The Art of Celebration addresses the “metrics of morale.” The authors explore how organizations can use communications data, sentiment analysis, wearables, AI-assisted pattern recognition, and cultural dashboards better to understand trust, stress, belonging, and burnout. They also warn that these tools must be used as coaching, not surveillance, systems. Participation should be voluntary, data should be aggregated, and insights should improve systems rather than punish individuals.

That is a critical lesson in AI governance. AI can help compliance detect cultural signals, emerging risks, retaliation patterns, training gaps, and control friction. But AI can also chill speech, invade privacy, amplify bias, or turn culture monitoring into employee surveillance. For CCOs, the right framework is clear. Use AI to improve governance, risk sensing, and employee support. Anchor it in transparency, purpose limitation, access controls, human review, and documented risk assessment. Align the work with NIST AI Risk Management Framework, ISO/IEC 42001, privacy principles, and the company’s own AI governance program.

Lesson Five: Rituals Preserve Culture Under Pressure

The book’s discussion of rituals is especially important for compliance. Rituals are repeated practices that teach a community what to remember. In compliance, rituals can include investigation debriefs, quarterly risk reviews, third-party red-flag meetings, manager speak-up moments, annual code refresh discussions, control-owner certifications, AI use reviews, and post-remediation lessons learned.

A ritual is stronger than a reminder. A reminder tells people to do something. A ritual teaches people who they are. This matters under pressure. When a quarter-end target is at risk, when a sales team faces a red flag, or when a senior leader wants to move quickly, the organization will not live up to the words in its code. It will fall to the level of its practiced rituals. If those rituals include escalation, challenge, documentation, and accountability, the culture has muscle memory.

Compliance Application

Celebration belongs in the compliance program because it helps answer one of the DOJ’s most important practical questions: Does the company incentivize compliance and ethical behavior in a meaningful way? The Criminal Division’s compensation pilot report states that companies that proactively design compensation systems to incentivize ethical behavior and that adopt company policies are better positioned to prevent misconduct, generate reports, address incidents before they escalate, and build a company-wide culture of compliance.

A mature compliance program should therefore examine recognition, promotion, compensation, awards, leadership messaging, and performance management as part of the control environment. The CCO should ask not only what misconduct is punished but also what integrity is honored.

CCO Questions

  • What behaviors does the company currently celebrate, formally and informally?
  • Do performance reviews, promotions, bonuses, and awards reflect ethical leadership and control ownership?
  • Are speak-up, cooperation, remediation, and control improvements recognized as business contributions?
  • Do we use cultural data and AI responsibly, or are we creating surveillance risk?
  • What rituals reinforce the compliance program under pressure?

Practical Takeaways

  1. Inventory what the company celebrates in awards, town halls, performance reviews, and leadership communications.
  2. Align recognition with the Code, internal controls, speak-up expectations, and risk management priorities.
  3. Create anonymized speak-up success stories that show reporting leads to improvement.
  4. Review incentive structures for misconduct risk and compliance-positive behaviors.
  5. Build compliance rituals that preserve culture: pre-mortems, post-investigation lessons learned, recognition of control owners, third-party red-flag reviews, and AI governance check-ins.

Conclusion: The Compliance Culture Builder’s Discipline

Taken together, Hemma Lomax and Ashley Dubriwny’s trilogy offers compliance professionals something more than a culture-building framework. It offers a practical operating model for program effectiveness. The Art of Ideation reminds us that compliance begins with better questions, deeper listening, and the courage to design around employees’ lived experiences. The Art of Implementation shows that even the best ideas fail unless they are operationalized through alignment, ownership, testing, adoption, and iteration. The Art of Celebration completes the cycle by showing that culture is sustained by what the organization chooses to recognize, repeat, and remember. This is the full arc of a mature compliance program: imagine wisely, execute consistently, and reinforce intentionally.

For the CCO, the message is clear. Culture is not an abstraction, and it is not a slogan. It is built through the systems employees use, the controls they trust, the concerns they feel safe raising, the incentives they see rewarded, the investigations they experience as fair, and the stories leaders choose to elevate. The DOJ’s ECCP asks whether a compliance program is well designed, adequately resourced, empowered to function, and working in practice. This trilogy gives compliance professionals a human-centered way to answer those questions with evidence. Ideation creates the insight. Implementation creates the operating discipline. Celebration creates the cultural memory.

The larger lesson is that compliance professionals are not simply policy owners, trainers, investigators, or risk managers. They are culture builders. They help organizations decide what matters, operationalize those commitments, and ensure they endure under pressure. In an era of AI governance, third-party complexity, speak-up expectations, incentive scrutiny, and board oversight, this work is more important than ever. The compliance programs that will matter most are not the ones with the most polished documents. They are the ones where employees know how to act, leaders know what to reinforce, controls work in practice, and the organization honors integrity as a business discipline.

That is the power of the trilogy. It takes us from possibility to practice to permanence. It reminds us that compliance effectiveness is not created in a single policy rollout, annual training event, or investigation report. It is created over time through disciplined attention to what people need, how work happens, and what the organization chooses to celebrate. For the modern compliance professional, this is both the challenge and the opportunity: to build a culture where ethics is not episodic, controls are not ornamental, and integrity is not merely stated. It is lived, reinforced, and carried forward.

Categories
Compliance Into the Weeds

Compliance into the Weeds: The DOJ Trainwreck and the Rising Risk Calculus for Compliance and Self-Disclosure

The award-winning Compliance into the Weeds is the only weekly podcast that takes a deep dive into a compliance-related topic, literally going into the weeds to explore it more fully. Looking for some hard-hitting insights on compliance? Look no further than Compliance into the Weeds! In this episode of Compliance into the Weeds, Tom Fox and Matt Kelly discuss how internal dysfunction at the U.S. Department of Justice is creating uncertainty for corporate compliance teams and corporations more generally.

Focusing on a reported turf battle between the long-standing Fraud Section in the Criminal Division, established in 1955 and central to FCPA enforcement and compliance guidance, and a newly created national Fraud Division, which was initially framed as targeting government benefits fraud. They argue the reorganization could drain expertise, reduce future DOJ guidance, and distort enforcement into politically selective actions, citing IBM’s $17 million settlement and an EEOC case involving The New York Times and Smartmatic’s experience. They also highlight DOJ staffing losses with a net 20% fewer lawyers, loss of experienced attorneys, reliance on inexperienced hires and bonuses, and warn that the volatility may chill voluntary self-disclosure despite DOJ messaging encouraging it.

Key highlights:

  • DOJ Train Wreck Overview
  • Fraud Section vs Fraud Division
  • Political Enforcement Reality
  • Self-Disclosure Gets Riskier
  • What Companies Should Do Now

Resources:

Matt on Radical Compliance

Tom

Instagram

Facebook

YouTube

Twitter

LinkedIn

A multi-award-winning podcast, Compliance into the Weeds was most recently honored as one of the Top 25 Regulatory Compliance Podcasts, a Top 10 Business Law Podcast, and a Top 12 Risk Management Podcast. Compliance into the Weeds has been conferred a Davey, a Communicator Award, and a W3 Award, all for podcast excellence.

Categories
Blog

The Culture Builder’s Trilogy: Part 2 – The Art of Implementation: Where Compliance Culture Lives or Dies

Ed. Note: We are in the midst of a three-part blog post series on three recent books by Hemma Lomax and Ashley Dubriwny. There are The Art of Ideation, The Art of Celebration, and The Art of Implementation.

If The Art of Ideation is about imagining better compliance, The Art of Implementation is about making it real. Hemma Lomax and Ashley Dubriwny write that implementation is where culture lives or dies. That single sentence could serve as a mission statement for every Chief Compliance Officer.

Compliance professionals know this problem well. A program can include a strong code of conduct, a comprehensive policy inventory, a well-designed training calendar, a hotline, third-party procedures, and investigation protocols. Yet the DOJ does not ask whether a company has merely created compliance artifacts. It asks whether the program works in practice. It goes directly to the DOJ’s Evaluation of Corporate Compliance Programs (ECCP). The ECCP continues to ask whether a program is well-designed, adequately resourced, empowered to function effectively, and working in practice. That is why The Art of Implementation matters. It moves from aspiration to action. It asks how values become systems, how ideas become habits, and how culture becomes durable.

Lesson One: Mindset Before Method

The book begins with a critical insight: implementation begins with how you think. Lomax and Dubriwny identify four commitments of the culture builder’s mindset: empathy before enforcement, curiosity over control, influence rather than insistence, and legacy as a lens. For compliance professionals, this is not a rejection of enforcement. It is a recognition that enforcement without trust creates fear, not culture. A CCO must enforce standards, discipline misconduct, and protect the company. But a CCO must also understand why employees resist, where controls create friction, and how people make decisions under pressure.

This is the difference between a compliance function that says “no” and one that helps the business get to “yes, with controls.” The former may be respected in moments of crisis. The latter is trusted before the crisis arrives.

Lesson Two: Think, Build, Ship, Adopt, Tweak

One of the strongest frameworks in the book is the five forces of implementation: think, build, ship, see it adopted, and tweak. The model is practical and deeply consistent with the ECCP. “Think” means design the change with empathy. “Build” means operationalize the intention. A ship means starting before every detail is perfect. Adoption means embedding the practice into the culture. “Tweak” means to learn, adjust, and improve.

This is what compliance program effectiveness should look like. A CCO should not wait three years to discover that annual training did not change behavior. A third-party control should not remain unchanged after repeated red flags. An AI acceptable use policy should not sit static while employees quietly adopt new tools. A speak-up program should not wait for a scandal before testing whether employees trust it. The compliance application is straightforward. Build compliance like a product. Test. Measure. Listen. Improve.

Lesson Three: Alignment Accelerates Implementation

The book’s discussion of alignment is essential for compliance. Lomax and Dubriwny use Ocean’s Eleven as a cultural reference point. The plan works not because one person is brilliant, but because purpose, people, and process are aligned. Implementation fails when a good idea lacks the right coalition, operational fit, or timing.

This is a core challenge for the CCO. Compliance cannot implement an effective third-party program without the support of procurement, finance, legal, sales, audit, and business leadership. Compliance cannot govern AI without IT, data science, privacy, cybersecurity, HR, legal, and business users. Compliance cannot build a speak-up culture without managers. Stakeholder mapping is therefore not an administrative exercise. It is a governance control. It identifies who can accelerate the initiative, who can block it, who must own it, and who must maintain it after launch.

Lesson Four: Find Failure First

The pre-mortem section of The Art of Implementation is one of the most useful tools for compliance professionals. The authors ask teams to imagine that an initiative has failed and then work backward to identify why. This is precisely how CCOs should approach major program changes. Before launching a new hotline platform, ask why employees might still avoid reporting. Before deploying AI-assisted monitoring, ask about potential privacy, bias, transparency, and explainability concerns. Before rolling out a third-party due diligence platform, ask why business teams might work around it. Before redesigning incentives, ask what unintended behaviors the new metrics could create.

Pre-mortems are internal controls in action. They force the organization to identify failure modes before the market, the regulator, the whistleblower, or the plaintiff does. They can be and are a powerful tool at your disposal as a CCO or compliance professional.

Lesson Five: Movements Beat Mandates

A particularly powerful theme in the book is the distinction between mandates and movements. Mandates may produce obedience. Movements produce ownership. For compliance professionals, this is a critical distinction.

The Wells Fargo fake sale scandal remains a cautionary tale about mandates, metrics, and fear-based performance pressure. Employees may comply with the apparent demand for results while violating the organization’s deeper values. That is why incentives matter. The DOJ has emphasized that companies should use both incentives and consequences to promote compliance. Its compensation and clawback pilot report states that affirmative metrics and benchmarks can reward compliance-promoting behavior and that financial penalties can deter risky behavior.

This is where compliance culture becomes real. Employees need to see that ethical leadership, controlled discipline, speaking up, and responsible business performance are recognized, promoted, and rewarded. They also need to see that misconduct, retaliation, and willful blindness have consequences.

Compliance Application

The CCO’s implementation challenge is to convert program design into operational evidence. That evidence includes adoption data, control testing, investigation metrics, remediation tracking, third-party monitoring, AI use inventories, exception reporting, and incentive alignment. Implementation also requires courage. A CCO must be willing to ship pilots, gather feedback, and make changes. The compliance function must stop equating launch with success. Launch is the beginning. Adoption, evidence, and improvement are the proof.

CCO Questions

  • Which compliance initiatives have been launched but not adopted?
  • Do we have stakeholder maps for our most important compliance priorities?
  • Are we running pre-mortems before major program changes, including AI governance, third-party risk, speak-up enhancements, and incentive redesign?
  • Do our incentives reward ethical behavior, promote control over ownership, and ensure transparency?
  • What compliance practices would continue if the current CCO left tomorrow?

Practical Takeaways

  1. Identify one compliance initiative that stalled and run a pre-mortem on why it failed.
  2. Build a stakeholder map for AI governance or third-party risk.
  3. Convert one compliance aspiration into a measurable operating practice.
  4. Review incentives and promotion criteria for compliance signals.
  5. Treat implementation as the evidence layer of the compliance program. Regulators do not reward intentions. They evaluate what works.

Implementation is where compliance culture is tested. It is where the organization discovers whether its ideas can survive business pressure, competing priorities, operational friction, and human resistance. Yet even the best-implemented program must still be sustained. Controls must be reinforced. Speak-ups must be protected. Ethical behavior must be recognized. Employees should see that integrity, not just performance, is valued by the organization. That is the work of the third book in the trilogy, The Art of Celebration.

Join us tomorrow for Part 3, where we will turn to celebration as a compliance discipline and explore how recognition, incentives, rituals, morale metrics, and cultural memory shape what employees believe the company truly values.

Categories
Blog

The Culture Builder’s Trilogy: Part 1 – The Art of Ideation: Compliance Begins with Better Questions

Ed. Note: over the next three blog posts, I will be running a short series on three recent books by Hemma Lomax and Ashley Dubriwny. There are The Art of Ideation, The Art of Celebration, and The Art of Implementation.

Hemma Lomax and Ashley Dubriwny’s The Art of Ideation is, on one level, a practical guide for culture builders. On another level, it is a challenge to compliance professionals: stop treating compliance as a function that merely publishes rules, delivers training, and waits for reports. Start treating compliance as a discipline of curiosity, engagement, design, and shared intelligence.

The book begins with a simple but powerful premise. Culture builders need ideas, but more importantly, they need the skill to generate better ideas through peer ideation, storytelling, and crowdsourcing intelligence. Lomax and Dubriwny describe the spark that came from compliance professionals exchanging creative approaches at a conference table and then ask why that energy should be limited to a once-a-year event. Their answer is to make ideation intentional, repeatable, and community-based.

For compliance professionals, this is not a soft concept. It goes directly to the DOJ’s Evaluation of Corporate Compliance Programs (ECCP). The ECCP continues to ask whether a program is well-designed, adequately resourced, empowered to function effectively, and working in practice. The compliance lesson from The Art of Ideation is clear: a program that does not ask better questions will not get better answers.

Lesson One: Know Your Audience Before You Design the Control

One of the book’s strongest lessons comes from the São Paulo story. Hemma arrives in Brazil to speak to more than 200 sales executives. Rather than deliver a generic compliance presentation, she uses images and experiences from the city itself to connect with the local audience. The lesson is not simply that visuals work. The deeper lesson is that compliance must demonstrate cultural awareness before it asks for behavioral change.

Too many compliance programs are still designed from the top down. Policies are written in legal language. Training is translated late, if at all. Hotline posters are posted in areas where employees do not work. Codes of Conduct speak to an imagined employee rather than the actual workforce.

The ECCP lens is unforgiving here. A risk-based program must be tailored to the company’s risk profile, business model, workforce, geography, and operations. If field employees, sales teams, or third-party-facing personnel cannot access guidance in the moment of need, the control may exist on paper but fail in practice.

Lesson Two: Storytelling Is a Control Enhancement

Dubriwny’s discussion of training emphasizes that facts alone rarely change behavior. Stories create context, emotion, and recall. In compliance, that matters because most misconduct does not arise from someone misunderstanding a policy title. It arises in moments of pressure, ambiguity, fear, loyalty, or perceived business necessity. A good compliance story can show what a conflict of interest feels like. It can show why a facilitation payment creates risk. It can show how retaliation begins quietly. It can show a manager what it means to receive a concern well.

This is especially important for a culture of speaking up. Employees do not speak up because a poster says they can. They speak up because they believe the organization will listen, protect them, and act. The Art of Ideation repeatedly returns to the need to meet people where they are, involve them, and design engagement pathways that feel safe. That maps directly onto the ECCP’s focus on confidential reporting, anti-retaliation, and investigation processes, as well as employees’ trust in those systems.

Lesson Three: The Code of Conduct Should Be Designed to Work

The book’s chapter on Codes of Conduct is especially useful for CCOs. It asks whether the Code is an external artifact, a regulatory box-checking document, or a decision-making tool for employees. The answer should be all the above, but the priority must be the employee user. That is a powerful compliance point. A code should not merely state values. It should operationalize them. It should be accessible, visually clear, mobile-friendly, translated appropriately, and supported by examples that reflect real roles, geographies, and pressures. The authors argue that a Code should be co-created, tested, and designed so people can see themselves in it.

This has implications for internal controls. A policy no one reads is not a meaningful control. A code no one uses is not a cultural anchor. A decision tree that helps an employee escalate a third-party red flag is more valuable than a beautifully written paragraph no one remembers.

Lesson Four: Crowdsourcing Risk Intelligence Is Compliance Modernization

Perhaps the most compliance-relevant section of the book is the discussion of crowdsourcing intelligence. Lomax and Dubriwny argue that leadership does not have a monopoly on the perspectives needed to identify risk. Employees across functions, geographies, and levels see vulnerabilities long before they appear in formal reporting channels. This is exactly where modern compliance must go. Annual risk assessments remain useful, but they are not enough on their own. A CCO needs real-time, near-real-time, and frontline input. This includes surveys, focus groups, collaboration tools, investigation themes, hotline trends, third-party feedback, and data analytics.

AI governance fits here as well. The book encourages responsible experimentation with AI, including using AI to make policies more accessible, generate first drafts, synthesize information, and provide decision-useful guidance. In compliance terms, AI should not be a gimmick. It should be governed, risk-assessed, monitored, and used to improve the employee experience.

Compliance Application

For the compliance professional, ideation is not brainstorming for its own sake. It is how the CCO identifies gaps, improves controls, tests training, strengthens speak-up systems, modernizes the Code, and uses AI responsibly. It is how compliance moves from headquarters’ assumptions to operational intelligence.

The lesson is also relevant to investigations. The book’s discussion of investigations emphasizes empathy, transparency, gratitude toward participants, and learning from the process. That is an important reminder that investigations are not simply fact-finding exercises. There are moments when employees decide whether the compliance function is credible.

CCO Questions

  • Does our compliance function know how employees actually experience our Code, training, reporting channels, investigation process, and third-party controls?
  • Are we using peer ideation, frontline feedback, and cross-functional input to improve the program?
  • Where are we still relying on headquarters assumptions rather than operational evidence?
  • How are we using AI to improve accessibility, consistency, risk sensing, and employee guidance without weakening confidentiality, privacy, or human judgment?

Practical Takeaways

  1. Redesign one compliance communication from the user’s perspective. Make it shorter, clearer, more accessible, and easier to act on.
  2. Create an ideation circle around one major compliance risk, such as third-party due diligence, gifts and entertainment, speaking up, or AI use.
  3. Test your Code of Conduct with employees from different geographies and functions before the next refresh.
  4. Add crowdsourced risk intelligence to your risk assessment process.
  5. Treat ideation as a compliance control. Better questions produce better evidence, and better evidence produces a more effective program.

Ideation is where the compliance professional begins to see what is possible. It gives the CCO better questions, stronger engagement, richer risk intelligence, and a more human understanding of how employees experience the program. But ideas alone do not create culture. A redesigned code, a better speak-up message, a sharper AI policy, or a new third-party risk insight only matters if it moves from concept to practice. That is where the second book in the trilogy, The Art of Implementation, takes us next.

Join us tomorrow in Part 2, where we will examine how compliance professionals turn good ideas into operating discipline through alignment, stakeholder ownership, pre-mortems, adoption, incentives, and the hard work of making values real inside the business.

Categories
Blog

Compliance Week 2026: AI Governance Highlights

The 21st Annual Compliance Week Conference made one point unmistakably clear: AI is no longer a technology issue sitting outside the compliance function. It is now a governance, risk, controls, culture, and accountability issue. Across the conference, AI appeared in nearly every discussion, from practical tools for compliance teams to regulatory uncertainty, shadow AI, third-party risk, and board oversight. The central message for compliance professionals was clear: AI must be governed with the same discipline, documentation, monitoring, and continuous improvement as any other enterprise risk.

That should not surprise any Chief Compliance Officer. The DOJ’s Evaluation of Corporate Compliance Programs (2024 ECCP) has long asked whether a compliance program is well-designed, adequately resourced, empowered to function effectively, and working in practice. Those same questions now apply to AI. The issue is not whether an organization is using AI. It almost certainly is. The issue is whether the company knows where AI is being used, who approved it, the risks it creates, the controls that apply, and whether those controls are being monitored.

AI Is Now a Compliance Governance Issue

The first major theme from Compliance Week 2026 was governance. AI may be exciting, efficient, and creative, but without governance, it can quickly become a source of unmanaged enterprise risk. That governance challenge begins with oversight. Who owns AI risk? Who approves AI use cases? Who determines whether a tool is appropriate for use with company data? Who has the authority to stop an AI project that is not meeting its stated purpose? These are not theoretical questions. They are the basic operating questions of an effective compliance program.

A company should not treat AI as a series of disconnected experiments. It should treat AI as part of the enterprise control environment. That means clear governance structures, documented approvals, defined risk owners, escalation protocols, monitoring, testing, and board reporting. The board does not need to become a group of AI engineers. But directors do need to understand whether management has created a defensible AI governance framework. They should ask how AI risks are identified, how high-risk use cases are reviewed, how third-party AI vendors are assessed, and how the company detects unauthorized AI use.

Shadow AI Is the Risk Hiding in Plain Sight

One of the strongest compliance lessons from the conference was the danger of shadow AI. Employees are already using AI tools, often because they are efficient, accessible, and easy to deploy. The problem is that ease of use can defeat governance. If employees are using ChatGPT, Claude, Gemini, Copilot, or other tools without authorization, training, or data restrictions, the company has a control gap. Confidential business information, financial data, personal information, customer information, or regulated data can move into systems the company does not control. That creates legal, privacy, cybersecurity, contractual, and reputational risk.

The answer is not simply to prohibit AI. That approach is unlikely to work. The better answer is to identify the tools being used, classify them by risk, authorize appropriate use cases, train employees, monitor usage, and make clear what data can and cannot be entered into an AI system. A strong AI governance program should include an AI use register. It should identify approved tools, owners, business purposes, data categories, risk ratings, controls, monitoring obligations, and renewal or reassessment dates. Without that inventory, a company cannot credibly claim to govern AI risk.

The Compliance Risk Management Model Already Works

One of the most important insights from the conference was that compliance professionals already have the right risk management framework. AI risk does not require abandoning the compliance discipline. It requires applying it.

The framework is familiar. Identify the risk. Develop a risk management strategy. Train employees. Implement the strategy. Monitor performance. Use data to improve your strategy continuously. That is the compliance operating model. It is also the right model for AI governance.

The 2024 ECCP emphasized risk-based compliance, data access, continuous improvement, and the effectiveness of controls in practice. Those expectations fit naturally into AI governance. A company should ask whether its AI controls are designed around actual risks, whether compliance has access to AI-related data, whether employees understand acceptable use, and whether the company can prove that its controls operate effectively. The lesson is straightforward. Do not build AI governance as a technology policy alone. Build it as a compliance program.

AI Risk Has Three Core Dimensions

The conference also highlighted the need to separate AI risk into practical categories. For compliance officers, three risk areas deserve immediate attention.

First, internal risk. This includes employee use of AI, shadow AI, unauthorized tools, misuse of confidential information, lack of training, and gaps in approval processes.

Second, external risk. This involves AI systems that affect customers, patients, consumers, investors, or other external stakeholders. These tools may raise issues involving fairness, privacy, transparency, discrimination, consumer protection, and regulatory obligations.

Third, third-party risk. Vendors, consultants, service providers, and sales agents may introduce AI into the company’s operations. A third-party vendor using AI in screening, analytics, customer service, data processing, or decision support can pose a risk to the company, even when the company did not build the tool.

This is where compliance must bring discipline. Third-party AI risk should be part of due diligence, contracting, audit rights, monitoring, and renewal. Companies should ask vendors what AI tools they use, what data those tools process, whether subcontractors are involved, how outputs are validated, and whether the company has audit rights over AI-related controls.

ROI Must Begin With the Business Purpose

AI projects should begin with a simple question: what problem are we trying to solve? Too many AI initiatives begin with pressure to “use AI” rather than a clear business case. That is not governance. That is technology enthusiasm without control or discipline. A compliance-minded AI review should ask whether the proposed tool has a defined use case, measurable business value, appropriate controls, and a clear owner. It should also ask whether the project is drifting from its original purpose. Mission creep is a real AI risk. A tool approved for one purpose can quickly be used for another. That creates new risks and may invalidate the original approval.

The more regulated the use case, the more important this analysis becomes. AI used in healthcare, employment, finance, consumer decisions, investigations, sanctions screening, or third-party risk management demands heightened scrutiny. ROI may not always appear as a direct financial return. Sometimes the business value is avoiding regulatory exposure, improving consistency, strengthening documentation, or reducing unmanaged risk.

Training Is No Longer Optional

AI training must move beyond general awareness. Employees need practical, role-based instruction. They need to know which tools are approved. They need to know what data is prohibited. They need to understand when human review is required. They need to know how to report AI concerns, errors, bias, hallucinations, or misuse. They also need to understand that AI output is not a substitute for professional judgment.

For compliance teams, training should include investigators, auditors, third-party managers, procurement, legal, finance, HR, IT, and business leaders. The message should be clear: AI can support the work, but it does not remove accountability.

Build AI In, Do Not Bolt It On

One of the most practical insights from the conference was that AI should be built into business processes, not bolted on afterward. That distinction matters. Bolted-on AI becomes a tool without governance. Built-in AI becomes part of the control environment.

For example, in third-party risk management, AI can help analyze due diligence responses, identify red flags, monitor adverse media, track contract obligations, and support ongoing risk scoring. But it must be embedded into a process with human oversight, escalation protocols, audit trails, and testing. The same applies to investigations, hotline analytics, policy management, training, and monitoring. AI should strengthen compliance processes, not bypass them.

The CCO Must Have a Seat at the AI Table

The compliance function should not wait to be invited into AI governance. It should claim its role. The CCO brings the language of risk, controls, accountability, documentation, monitoring, and culture. Those are precisely the disciplines AI governance requires. Compliance should help design AI approval workflows, risk assessments, training, third-party reviews, monitoring plans, and board reporting.

This does not mean compliance owns every AI decision. It means compliance must be part of the governance architecture. AI governance should be cross-functional, with legal, compliance, IT, privacy, cybersecurity, internal audit, procurement, HR, and the business working together. But compliance must ensure that the program is not simply innovative. It must be defensible.

Practical Takeaways for Compliance Professionals

  1. Create an AI inventory. Know what tools are being used, by whom, for what purpose, and with what data.
  2. Establish an AI governance committee. Include compliance, legal, IT, privacy, cybersecurity, internal audit, procurement, and business leadership.
  3. Build a risk-based approval process. High-risk AI use cases should require enhanced review, documentation, testing, and escalation.
  4. Address shadow AI directly. Do not assume employees are waiting for policy guidance. Identify actual use and bring it into governance.
  5. Train by role and risk. General AI awareness is not enough. Employees need practical rules for approved tools, prohibited data, human review, and reporting.
  6. Extend third-party risk management to AI. Vendor diligence, contracts, audit rights, monitoring, and renewal reviews should include AI-specific questions.
  7. Monitor and improve. AI governance is not a one-time policy exercise. It requires testing, metrics, incident review, and continuous improvement.

Board Questions

  1. Do we have an inventory of AI tools currently used across the enterprise?
  2. Who approves AI use cases, and how are high-risk uses escalated?
  3. How do we detect and manage shadow AI?
  4. What data is prohibited from being entered into AI tools?
  5. How are third-party AI vendors reviewed, contracted, monitored, and audited?
  6. What AI metrics does management provide to the board?
  7. Who has the authority to pause or terminate an AI project that creates unacceptable risk?

CCO Questions

  1. Is compliance involved before AI tools are deployed?
  2. Do our policies distinguish between approved, restricted, and prohibited uses of AI?
  3. Can we prove employees have been trained on AI risks?
  4. Do we have a documented AI risk assessment process?
  5. Are AI controls tested by internal audit or another independent function?
  6. Are AI incidents, errors, and misuse captured through speak-up and escalation systems?
  7. Can we show regulators that our AI governance works in practice?

Conclusion

Compliance Week 2026 confirmed that AI has crossed the threshold from emerging technology to core compliance risk. The companies that succeed will not be those that chase every new tool. They will be the companies that govern AI with discipline. For the modern CCO, this is the moment to step forward. AI governance belongs squarely within the compliance conversation because it involves risk, accountability, culture, controls, third parties, monitoring, and board oversight. Those are the foundations of effective compliance.

AI may change the tools. It does not change the obligation. Governance still matters. Controls still matter. Culture still matters. Accountability still matters. And compliance must help lead the way.

Categories
Blog

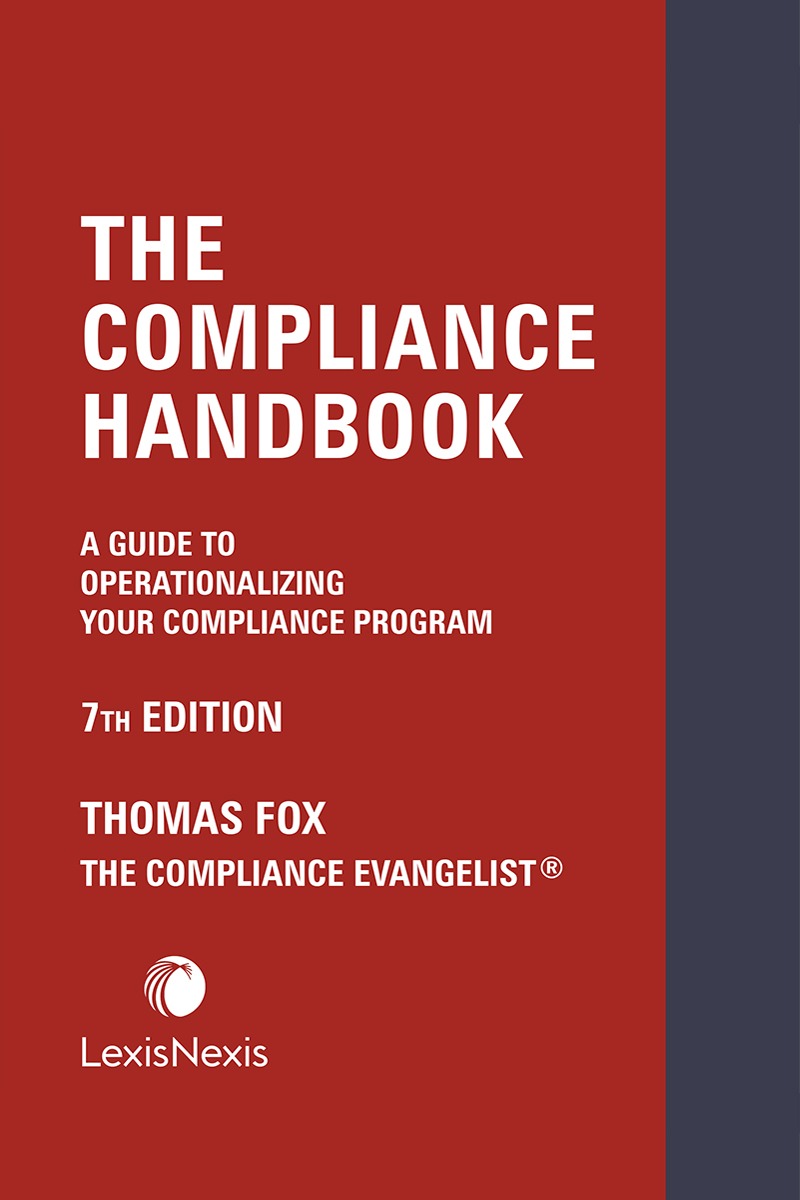
The Compliance Handbook, 7th Edition

As the Compliance Evangelist, I am pleased to announce the release of The Compliance Handbook, Seventh Edition. I believe it is the best single-author handbook for compliance professionals and about compliance professionals. Beautifully packaged, edited, and published by the country’s top legal and compliance publisher, LexisNexis.

This edition is an update of the Compliance Handbook, 7th edition. The handbook is a must-read for all ethics and compliance professionals. The Seventh Edition provides practical, helpful solutions to important ethics and compliance issues. It is comprehensive, accessible, and a must-have for every ethics and compliance professional.

As noted, I have teamed up with the country’s top legal and compliance publisher, LexisNexis Legal & Professional, to add to its winning series of compliance offerings. The Compliance Handbook, 7th edition, provides seasoned compliance professionals and those new to the profession with practical, actionable guidance and tools to design, implement, and continually enhance a best-practices compliance program. Why the need for this update?

Noted compliance maven Karen Moore said in the book’s foreword.

There is an increasing awareness that compliance and ethics stand at a unique crossroads—the intersection of human behavior and decision-making and of corporate identity, purpose, and mission. We operate at all levels of the organization: we satisfy the board, seek to understand strategy in the C-suite, engage middle managers, and stay relevant to the factory floor and frontline workers. We reconcile the need to defend the enterprise with the need to believe in its individuals. All that, within an increasingly complex landscape of shifting regulations, emerging risk areas, and geopolitical instability.

The Compliance Handbook, 7th edition, provides an in-depth look at the latest thinking and trends for the full range of critical compliance topics, including:

  • Compliance and business ventures;
  • Third-party risk management
  • The Board’s Role in Compliance
  • Continuous improvement;
  • Compliance innovation; and
  • And much more.

The Compliance Handbook, 7th edition, also takes a close look at the roles of all professionals with compliance responsibility, from Compliance Officers and Boards of Directors to Human Resources, Internal Audit and Internal Controls, and Communications and Training professionals. Understanding compliance responsibilities across the organization remains a key theme for both the Department of Justice (DOJ) and the Securities and Exchange Commission (SEC). In this 6th edition, I expand on the concepts articulated in previous editions for operationalizing your compliance program.

What’s new for the 7th edition?

  • Key compliance enforcement actions, DOJ pronouncements, and all things compliance from 2025;
  • The revised section on the use of AI in a best practices compliance program.
  • The significant revisions to the chapter on data analytics, and
  • Looking forward to compliance in 2030 and beyond.

The Compliance Handbook, 7th edition, incorporates the most current government pronouncements governing best practices compliance programs, including the 2024 Evaluation of Corporate Compliance Programs; the new DOJ whistleblower initiative; ideas on innovation in compliance training, data, and its use in improving and maintaining corporate culture; the continued evolution of AI in compliance; and much more.

The Compliance Handbook, 7th edition, is available in both print and eBook editions.  Visit the LexisNexis® Store at https://lexisnexis.com/fox20

To save 20% on The Compliance Handbook: A Guide to Operationalizing Your Compliance Program, please use the promotion code FOX20.

Offer expires December 31, 2026. The offer applies to new orders only, before shipping and taxes are calculated, and shipped to a U.S. address. Discount will be applied to each applicable product after code FOX20 is entered.

Categories
Great Women in Compliance

Great Women in Compliance: DOJ’s New Fraud Division: Practical Insights for Compliance Professionals

In this episode, Lisa and Ellen speak with Leigha Simonton and Jennifer Beidel, former prosecutors and now partners at Dykema Gossett. They discuss the changes in the U.S. Department of Justice, focusing on the National Fraud Enforcement Division and shifts in enforcement priorities.

They discuss the spotlight on fraud involving federal funds, especially in healthcare, PPP loans, and other government programs. They discuss the new structure of the criminal fraud division and how that may change the government’s approach to prosecuting cases. At the same time, they also note that many experienced prosecutors and agents have left the DOJ, creating a gap between stated priorities and capacity and expertise.

Leigha and Jennifer also provide practical guidance for ethics and compliance professionals. They confirm that a risk assessment is critical and that any company that received federal funds, such as PPP loans, should remain vigilant for possible exposure under the current enforcement trends.

Even with these changes, they reiterate that effective, well-tested compliance programs do matter if the U.S. government is considering (or engaging in) prosecution. A proactive program—not the tick-the-box type—demonstrates implementation and remediation, increasing the likelihood of a declination.

This is a great episode for those of us trying to understand the US DOJ’s current enforcement landscape amid uncertainty.

Categories
Daily Compliance News

Daily Compliance News: May 4, 2026, The May The 4th Be With You Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • DOJ loses 25% of all lawyers. (FT)
  • The Trump Administration is to push forward with tariffs based on forced labor. (NYT)
  • Baer told the rehire about AML sanctions and the whistleblower. (Bloomberg)
  • Senior lawyers must pay for junior lawyers’ misuse of AI. (Reuters)

For more information on the use of AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.

Categories
Daily Compliance News

Daily Compliance News: May 1, 2026, The May Day Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All, from the Compliance Podcast Network. Each day, we consider four stories from the business world, compliance, ethics, risk management, leadership, or general interest for the compliance professional.

Top stories include:

  • Insiders winning on polymarkets? (FT)
  • KNDS investigates bribery allegations ahead of IPO. (FT)
  • OpenAI is sued over the Canada massacre. (WSJ)
  • DOJ wins access to KKR and its lawyers’ emails. (Bloomberg)

For more information on the use of AI in compliance programs, Tom Fox’s new book, Upping Your Game, is available. You can purchase a copy of the book on Amazon.com.

To learn about the intersection of Sherlock Holmes and the modern compliance professional, check out Tom’s latest book, The Game is Afoot-What Sherlock Holmes Teaches About Risk, Ethics and Investigations on Amazon.com.