Categories
Blog

Frankenstein and Compliance: Part 5 – Frankenstein Meets the Wolf Man: When Monsters Collide

Ed. Note: This month, on his podcast series Popcorn and Compliance, Tom Fox dives deep into the first five Frankenstein movies. Over October, Tom Fox will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolf Man. This blog post accompanies the podcast series.

The first four Frankenstein films provide a useful progression for corporate compliance. Frankenstein examined innovation without adequate governance. Bride of Frankenstein shows leadership that understands risk but lets pressure and rationalization override judgment. Son of Frankenstein moved to inherited risk and the obligations that arise when new leadership discovers legacy problems. The Ghost of Frankenstein asks whether remediation actually works. 

Frankenstein Meets the Wolf Man (1943) changes the risk equation. There are now two monsters. Larry Talbot, played by Lon Chaney Jr., returns from The Wolf Man seeking a way to end the curse that transforms him into a werewolf. His search eventually brings him to the ruins of Frankenstein’s castle, where he discovers the Monster, played in this film by Bela Lugosi. Talbot revives him, Dr. Mannering becomes involved, and the film eventually delivers what its title promises: Frankenstein’s Monster and the Wolf Man collide.

For corporate compliance professionals, the movie provides a useful way to think about enterprise risk. Organizations necessarily divide risk into categories and assign responsibilities to different functions. Compliance may oversee anti-corruption, sanctions, third-party, antitrust, and other regulatory risks. Information Security manages cyber risk. Privacy oversees data protection. HR manages employment-related risks. Finance owns financial controls. Internal Audit provides assurance. Enterprise Risk Management looks across the organization. 

That structure is necessary. It can also create silos. The most significant corporate risks do not always remain within the categories management assigns to them. They interact. When they do, the resulting exposure may be greater than the organization sees when each risk is assessed independently. The compliance challenge is not simply identifying each monster. It is understanding what happens when they meet.

Risk Does Not Respect the Organizational Chart

Companies assign risk ownership because someone must be accountable. That is good governance. The problem begins when risk ownership becomes information ownership. Consider a third-party distributor operating in a high-risk market. Compliance may identify concerns about the distributor’s beneficial ownership. Finance may identify unusual payment requests. Information Security may detect suspicious access involving the distributor’s credentials. Internal Audit may identify invoice exceptions. Legal may become aware of litigation or regulatory concerns involving related entities. Each function may respond appropriately to the information it possesses.

Yet the organization may still fail if nobody connects those facts. The compliance issue is therefore not simply whether individual control functions are doing their jobs. It is whether the organization’s governance structure allows information to move across functional boundaries. This distinction matters more as corporate risks become more interconnected.

A cybersecurity event can become a privacy incident. A privacy incident can become a regulatory investigation. A regulatory investigation can create disclosure obligations. A third-party issue can become an anti-corruption problem, which can become a books-and-records problem, which can become a securities issue. Risk categories are useful for management. They are not boundaries that real-world events respect. 

The Wolf Man and Frankenstein’s Monster Are Different Risks

One useful aspect of Frankenstein Meets the Wolf Man is that its two principal characters represent different kinds of risk. Larry Talbot understands his condition. He knows that particular circumstances trigger his transformation and that the consequences can be severe. His risk is recurring and linked to identifiable conditions. Frankenstein’s Monster represents something different. He is a legacy risk repeatedly inherited, revived, and unsuccessfully controlled by others.

Put them together and the problem changes. Companies experience similar combinations. A business may have a known third-party risk that becomes significantly more serious when combined with expansion into a high-risk jurisdiction. A weak control environment may become more consequential when management introduces aggressive sales incentives. A cybersecurity vulnerability may become more significant when the company deploys an AI system with access to sensitive information. The risks do not merely accumulate. They can amplify one another. That is why risk assessment should consider interdependencies. 

Risk Aggregation Should Be Part of the Compliance Conversation

Traditional compliance risk assessments often organize risks by subject matter.

  • Anti-corruption risk.
  • Sanctions risk.
  • Antitrust risk.
  • Third-party risk.
  • Privacy risk.
  • Conflicts of interest.
  • Books and records.

That approach is useful because it creates structure and allows organizations to identify controls and owners. It can also obscure combinations of risk. Consider a company acquiring a business in a high-risk jurisdiction. The acquisition may involve weak financial controls, substantial government interaction, a distributor-based sales model, aggressive growth assumptions, and a local culture unfamiliar with the acquiring company’s compliance expectations. Each issue may appear manageable when assessed separately. Together, they may produce a materially different risk profile. 

The CCO should therefore consider adding risk aggregation to the compliance risk assessment process. Where do significant risks intersect? Which business units face several elevated risks simultaneously? Which third parties create exposure across multiple compliance areas? Which strategic initiatives combine new technology, new markets, new partners, and aggressive financial expectations? A heat map that displays risks individually may not reveal these relationships. Compliance should be able to explain not only where the red boxes are but also what happens when several red boxes occupy the same part of the business.

AI Is an Enterprise Risk Multiplier 

Artificial intelligence provides one of the clearest modern examples of the problem. Companies sometimes discuss “AI risk” as though it were one category. Unfortunately, it is not. An AI deployment can simultaneously raise privacy, cybersecurity, intellectual property, employment, discrimination, consumer protection, regulatory, third-party, recordkeeping, and reputational issues.

What about an AI tool used to assist hiring decisions? HR may view it as a talent-management system. Information Security may assess the technology vendor. Privacy may examine candidate data. Legal may consider employment requirements. Compliance may evaluate governance and ethical concerns. Procurement may negotiate the contract. Every function may perform its assigned task. The organization still needs someone to evaluate the complete risk picture.

The same issue arises when AI is used for internal investigations, compliance monitoring, customer interactions, sales recommendations, financial decisions, or employee evaluation. This is why AI governance requires cross-functional management.

Frameworks such as the NIST AI Risk Management Framework and ISO/IEC 42001 are useful because they encourage organizations to think about governance, accountability, risk identification, measurement, monitoring, and continual improvement rather than treating AI exclusively as an IT issue. The central business question is not which department owns AI. It is whether the governance structure addresses the risks created by the particular use case.

The CCO Should Be a Connector, Not the Owner of Everything

The increasing interconnectedness of risk raises an important question about the CCO’s role. The answer should not be that Compliance owns every risk involving law, ethics, or reputation. That approach creates its own governance problem.

Business management owns business risk. Information Security should remain accountable for cybersecurity. HR should remain accountable for employment processes. Finance should own financial controls. Legal should provide legal advice. Internal Audit should preserve its independent assurance role. The CCO can nevertheless play an important role as a connector.

Compliance often receives information from multiple parts of the organization. Hotline reports, investigations, third-party due diligence, monitoring results, policy exceptions, training data, regulatory developments, culture assessments, and risk assessments all provide different views of organizational behavior. That perspective can allow Compliance to identify patterns that may not be visible within a single business function. The CCO should therefore ask where information needs to be shared, where cross-functional escalation is necessary, and where significant risks require joint governance. The goal is coordination without diluting accountability.

Mission-Critical Risk and Board Oversight

This also connects to the broader Marchand discussion about board oversight of significant and mission-critical risks. Directors do not need to become operational risk managers. They do need reasonable assurance that management has systems to identify significant risks and escalate material information.

For interconnected risks, that means understanding how management aggregates information. 

  • Which risks are sufficiently significant to require cross-functional oversight?
  • How does management identify emerging combinations of risk?
  • Who resolves disagreements between control functions?
  • What information reaches the board?
  • How are significant risks assigned when they do not fit within one organizational function?

These questions matter most when a risk is central to the company’s business model. The board does not need to manage the monsters. It needs to understand whether management can see when they are moving toward one another. 

Practical Actions for the CCO 

Frankenstein Meets the Wolf Man suggests several practical actions for compliance leadership. The compliance risk assessment should identify not only individual risks but also significant risk intersections. CCOs should look for business units, markets, third parties, products, and strategic initiatives where multiple elevated risks converge. Compliance should establish relationships and information-sharing mechanisms with Internal Audit, Legal, Finance, HR, Information Security, Privacy, Procurement, and Enterprise Risk Management. Significant cross-functional risks should have clear owners, escalation criteria, and decision rights.

CCOs should also consider whether existing compliance dashboards show relationships among risks or simply report individual metrics. Data from investigations, hotline reports, third-party monitoring, policy exceptions, audit findings, and other sources can become substantially more valuable when analyzed together. For emerging technologies such as AI, Compliance should participate in cross-functional governance while avoiding the temptation to own every associated risk. The objective is not centralized ownership. It is connected governance.

The Compliance Lesson

Frankenstein Meets the Wolf Man completes the compliance progression of the Universal Frankenstein films. Organizations create risks. Leadership can compromise in responding to them. New management can inherit them. Remediation can fail to eliminate them. Then those unresolved risks can interact with other risks.

That final stage matters because modern corporate risk is increasingly interconnected. AI touches privacy, cyber, employment, intellectual property, and regulatory compliance. Third-party risk can implicate corruption, sanctions, human rights, cybersecurity, and financial controls. Compensation can affect culture, sales practices, fraud risk, and books and records. No single function can manage these issues effectively on its own.

The solution is not to eliminate functional ownership. Clear accountability remains essential. The solution is to build governance mechanisms that allow information to move, risks to be considered together, and significant issues to be escalated across organizational boundaries. For the CCO, that means becoming an effective connector while preserving the accountability of the business and other control functions.

For management, it means looking beyond individual risk categories. For the board, it means ensuring that committee structures and reporting processes provide an enterprise view rather than a collection of disconnected risk reports. The ultimate lesson from Frankenstein Meets the Wolf Man is therefore not really about either monster individually. It is about interaction. 

A company may understand its corruption risk. It may understand its third-party risk. It may understand its cybersecurity risk. It may understand its AI risk. It may have capable people managing each one. The question is whether anyone understands what happens when those risks meet. That is where compliance moves beyond individual rules and controls and becomes part of enterprise governance. 

After five films, the Frankenstein story leaves us with a useful framework for the modern compliance program: govern what you create, learn from what goes wrong, take responsibility for what you inherit, test whether remediation works, and understand where risks intersect. Because in business, as in the movies, managing one monster is difficult enough. The real governance challenge begins when monsters collide.

Check out the podcast version and analysis of this episode of Popcorn and Compliance with Timothy and Fiona.
Categories
Blog

AI in the Audit Room: Why a Signature Is Not Evidence of Effective Oversight

Imagine a company with an AI policy—employees complete training. Important outputs supposedly receive human review. The board sees an approval dashboard and assumes it’s managing the risk. Now ask a different question: What evidence shows that the review changed anything?

That is the central compliance challenge in ECI Compliance Week’s AI in the Audit Room. The report was prepared in conjunction with Workiva. The collection translates its AI Governance Framework into an audit program, connecting 14 controls across three tiers to specific tests and supporting evidence. AI-in-the-Audit-Room For Chief Compliance Officers (CCOs), the lesson is straightforward: AI governance must demonstrate how decisions are controlled, challenged, and improved. A policy describes expectations. An approval records an action. Neither, on its own, proves that a control works.

The Oversight Gap Is an Operational Problem

45.2 percent of the respondents reported training or awareness programs, while 33.8 percent reported usage monitoring or logging by IT or security. Separately, the collection reports that approximately one in four executives in Workiva’s 2026 Midyear Executive Benchmark Survey said internal audits had discovered AI errors after outputs reached external stakeholders or board members. Only 11 percent believed their data quality was sufficient for AI use.

These findings should prompt a practical examination of where assurance occurs. Finding an error after distribution is not the same as preventing unsupported information from reaching a decision-maker. Workiva’s separately labeled partner contribution proposes an “assurance architecture” built around governance, traceability, and defensibility. The useful compliance question is whether management can explain what data informed an output, which model produced it, and what an employee authorized.

For an AI-assisted disclosure, that means following the information back to its source rather than accepting a plausible explanation. Ask whether reviewers can retrieve the supporting material and distinguish verified inputs from unsupported assertions. Traceability should make challenges possible before release, not merely explain a failure afterward.

Tier One: Establish Foundations That Can Be Tested

The framework’s first tier contains five controls: an accountable executive, an AI policy, an AI use inventory, employee AI training, and an annual program review. The accompanying audit tests make those familiar concepts concrete. The accountable executive needs authority and budget. The inventory must cover licensed products, AI embedded in existing software, and tools employees adopted independently. Training must reach actual users and match the policy in force. The annual review must produce findings that lead to action.

For the CCO, start with the inventory. Reconcile it against procurement, identity, and expense records, as the framework recommends. Then examine whether each material use has an owner and an appropriate data classification. Do not stop at asking whether training occurred. Ask which users received it and whether the content addressed their activities.

The same discipline applies to program review. A dated report is not the endpoint. Look for assigned remediation, closure dates, and evidence that the organization changed something because of what it learned.

Tier Two: Make Governance Part of Daily Operations

The second tier covers third-party AI due diligence, an AI speak-up channel, incident response, and employee AI use attestation. The third-party control is particularly important. The framework calls for reassessment when AI functionality arrives through a software update, not merely when the original contract is signed. It also calls for identifying the underlying model provider chain and determining whether customer data is used for training.

For compliance teams, that means connecting procurement and vendor oversight to technology change management. The original supplier approval should not be treated as the final assessment of every capability subsequently introduced. The speak-up and incident controls should work together. An employee who identifies troubling output needs a route to someone with AI governance expertise. Where appropriate, a substantive response should lead to investigation, containment, root-cause analysis, and control changes. Employee attestations should also update the inventory rather than disappear into a training database.

My practical recommendation is to test that entire process with a realistic scenario: an approved tool produces an unsupported claim intended for an external report. Determine who receives the concern, who can stop distribution, and what evidence documents the resolution.

Tier Three: Govern the Use Case and the Authority

The third tier addresses pre-deployment approval, human oversight and output monitoring, AI agent access and security, bias and fairness considerations, and external transparency. A critical distinction is that approving a tool is not the same as approving every use of that tool. The framework calls for separate use-case approval records, including cross-functional review for uses affecting financial reporting, customers, or employees.

For agents, the control table calls for unique identities, least-privilege access, defined limits on autonomous action, reconstructable action logs, and a tested way to stop the system. It also calls for testing decisions that affect people and can produce disparate outcomes and for substantiating public statements about AI. Translate these expectations into demonstrations. Ask the system owner to show an agent’s permissions, reconstruct an action, and produce the results of a shutdown test.

Monitoring should also look beyond internal error rates. The framework treats vendor model changes, public incidents, and regulatory shifts as external signals that require scheduled attention. Ask for the record of those signals and the actions taken, not simply the latest system performance report. For transparency, select a public claim and request its evidence file. The test is not whether the statement sounds reasonable. It is whether the organization can support it.

The Signature Problem: Test Judgment, Not Clicks

The collection’s most useful challenge concerns the human review step. Its “signature problem” describes a reviewer who sees a polished answer but lacks the underlying evidence, discarded alternatives, or meaningful ability to challenge the result. Approval becomes easy; disagreement becomes burdensome. The collection proposes three questions: Can the reviewer change the available options? Can the reviewer see enough evidence to disagree? Does disagreement produce a change? 

The report identifies four metrics: approval rate, edit distance on accepted output, time spent per review, and override consequence. Together, these examine whether reviews vary meaningfully, whether edits are captured and evaluated, whether reviewers have time to examine evidence, and whether overrides lead to action.

For CCOs, the fourth metric offers an immediate starting point. The collection recommends examining the last 20 overrides in an AI-assisted process affecting financial statements, customers, or regulators and asking what changed because of each. That exercise gets beyond a completion dashboard. It connects a reviewer’s judgment to remediation, revised instructions, or an adjusted control.

The collection also recognizes the limits of universal human review at scale. It describes moving human judgment into system boundaries, evaluation criteria, exception handling, sampling, and monitoring. It preserves individual review for specified consequential situations, including irreversible outcomes and cases outside anticipated policy boundaries. The practical lesson is not to remove people from oversight. Instead, place human judgment where it can actually influence outcomes, and give reviewers the evidence, authority, expertise, and time to exercise it.

Do Not Overlook the Inference Gap

Shruti Mukherjee’s contribution extends the discussion to AI’s environmental footprint. She distinguishes model training from inference, the recurring activity of running it, and frames the issue as a governance exposure involving ownership, measurement, third-party information, and substantiated claims. Her proposed audit questions are practical: Who owns the energy and water footprint of AI use? Can the organization measure ongoing consumption? What do supplier contracts disclose? Can the company support its environmental statements?

For the CCO, the broader application is to look beyond familiar risk categories. A benefit claimed in a presentation should not become an external assurance without supporting evidence. Where information is unavailable, document the limitation and identify who is responsible for addressing it.

Practical Takeaways: Bring Evidence to the Board

Start with one material AI-assisted process rather than rewriting an enterprise-wide policy. Trace it from the approved use case through source data, output review, escalation, and final distribution. Ask control owners to produce evidence at each stage.

Next, examine the review process itself. Use the collection’s four metrics to identify where approval activity may be substituting for judgment. Follow overrides through to their consequences and assign responsibility for unresolved weaknesses.

Finally, change the board conversation. Report not only how many tools are approved or how many employees are trained, but also what testing found, which controls failed, what management changed, and which risks remain unresolved.

The board should ask whether management knows where AI is used, whether reviewers can meaningfully challenge it, and whether the organization can reconstruct and support significant actions and public claims. This is where compliance connects governance directly to business execution.

The CCO should ask an equally direct question: When someone identifies that the AI is wrong, does the organization merely record the concern, or does it learn and change? That is the difference between an AI governance program that documents approvals and one that demonstrates effective oversight.

Categories
Blog

The Missing Link in Compliance: Building an Effective Advice Function

In a best-practices compliance program, a policy explains the rules. Training can introduce the risks. But when an employee faces an unfamiliar request, they still need to know what to do now, before making a commitment that changes everything. The question may arrive while a customer waits, a payment is pending, or a team prepares to launch a product. At that moment, “please consult the policy” may identify a resource without resolving the decision. Compliance should equip people before they improvise, not merely evaluate their improvisation afterward.

Your corporate compliance function should routinely advise employees on all compliance-related issues. But when did you last evaluate this ‘advice function’ as part of the compliance program? Training should help employees recognize when a question exists. Guidance should help resolve it in the actual circumstances.

A mature design therefore asks where important decisions occur, who needs help, and how quickly your compliance function can respond. A small company may use a straightforward contact arrangement with clear backups. A larger organization may need specialist routing across functions and time zones to ensure complete coverage. Neither should depend entirely on employees knowing the right person personally.

Make the route visible in the workflow where the question arises. An approval screen, travel process, vendor request, or data-sharing step can direct the user to the right assistance without requiring a search of the entire intranet.

The Corporate Translation: A Question Before the Commitment

Consider a hypothetical business development team preparing an important demonstration. An external platform could make the presentation more compelling. A team member suggests uploading records from an existing customer so the demonstration reflects real business conditions. The deadline is tomorrow. The platform has not been reviewed for that use.

One employee remembers the company’s data-handling training but is unsure whether a limited demonstration falls within the existing rules. The employee needs an answer before the upload, not a general reminder the following week. A useful response identifies the immediate boundary, the facts requiring review, and a workable alternative. For example, the adviser may explain that company policy requires pausing the proposed upload while the team uses approved synthetic demonstration data.

The commercial objective continues through an authorized route. The unresolved platform assessment remains a separate task with an owner. That is preventive compliance: reducing uncertainty while there is still an opportunity to choose a better course.

Distinguish Advice, Approval, and Reporting

Employees should not have to understand the company’s organizational structure before asking for help. But the company must distinguish what happens after the question arrives. Compliance advice and counseling explain expectations and possible courses of action. Approval authorizes a defined activity within delegated authority. Reporting communicates a concern that may require assessment or investigation. One conversation can involve all three. It should not silently substitute one for another.

In the demonstration example, explaining the synthetic-data option does not approve the external platform for unrestricted use. A security assessment may inform the decision without completing a contractual review. A disclosure that records have already been uploaded requires a different response than a prospective question. State the status clearly. Identify what is authorized, what is prohibited under the applicable requirements, what remains unresolved, and who owns the next decision. Do not describe every advice request as a suspected violation. At the same time, do not leave credible allegations in an informal advice queue because the original employee selected the wrong category.

Ask for the Facts That Change the Answer

A useful intake process gathers enough information to understand the decision without unnecessarily complicating the request. Ask what the employee proposes to do, which parties are involved, what has already happened, and when the next irreversible step occurs. Identify the relevant information, payment, benefit, representation, or commitment.

Then ask what could change the answer. In our hypothetical, that may include the type of records, existing permissions, platform terms, intended audience, and whether the information would remain stored afterward. Let the employee say a fact is unknown. An intake form should not force a confident answer where none exists.

A compliance professional should avoid collecting unrelated personal information or demanding a full investigation before providing preliminary guidance. Begin with a safe interim direction where appropriate, then assign the additional review. But a compliance professional should also test the claimed deadline. Some deadlines reflect genuine operational needs. Others reflect a late request or an assumption that nobody can change the schedule.

Make the Response Usable

Your employee needs a response they can act on, not one they can only admire for its precision. Explain the concern in business terms. Identify the action that may proceed and the action that must wait—state any conditions, the responsible decision-maker, and what new facts would require reconsideration. In our hypothetical, a practical response might confirm an approved demonstration method, identify the owner of the external-platform review, and explain that permission for the demonstration does not authorize later customer-data uploads.

Preserve the reasoning proportionately. A brief written answer may be enough for a straightforward question. A consequential decision may require a fuller record and formal approval. Do not use conditional language that nobody owns. “Proceed once all requirements are satisfied” is incomplete unless someone knows which requirements apply and who verifies completion. Yes, you knew I would slip in Document Document Document at some point.

Give Advisers Authority and Reliable Backup

A corporate compliance function needs authority, access, and resources to influence decisions before risk is accepted. Timely advice is one way to operationalize that independence. A compliance professional should know when it can answer directly and when another function must decide. Give advisers escalation routes for unresolved legal, technical, operational, and commercial questions.

Provide backup for absence and specialist coverage. A program that relies on one expert to answer every urgent message recreates key-person risk. Define what happens when business and compliance disagree. Preserve the competing assessments and route them to the authorized decision-maker. Do not allow repeated requests to different advisers to produce an undocumented approval search.

Maintain an appropriate record of previous advice so that the next adviser can see the relevant history. Restrict sensitive information and involve counsel when legal privilege or other protections may apply; do not promise protections the process cannot guarantee. Employees should be able to trust the service without being told that every conversation is secret or every answer is final.

Measure Helpfulness, Not Just Response Speed

A fast acknowledgment is useful. It is not the same as a resolved question. Measure time to an actionable response, time to final resolution, and reasons for delay. Separate time spent waiting for missing information from time lost because the request had no owner.

Review whether employees understood the answer and followed the approved path. Sample a small number of completed requests and compare the guidance with the subsequent transaction or activity. Also look for unnecessary complexity. If routine questions repeatedly require several functions to restate the same policy, clarify the process rather than celebrating the volume of collaboration.

The 2024 Evaluation of Corporate Compliance Programs asks whether employees know when to seek compliance advice, how to do so, and whether they are willing to do so. Availability alone does not answer either question. Use feedback carefully. Satisfaction is relevant, but a correct refusal may disappoint the requester. Conversely, a popular answer may be insufficiently supported. Assess the reasoning, the clarity of the next step, and the result. Speed belongs in that assessment but should not dominate it.

Managers Determine Whether Asking Feels Practical

Imagine an employee using the advice service correctly, only to hear from their manager that the question should never have been raised. The channel exists. The local message defeats it. A culture of speaking up exists only if it’s matched by a culture of listening up.

Managers should model asking early, providing necessary facts, and responding constructively when the answer changes the plan. Include those behaviors in manager training and leadership expectations, and evaluate them through real examples. Give teams protected time for review. A manager cannot repeatedly create last-minute commitments and then treat the resulting control discussion as evidence that compliance is slow.

Equally, compliance should examine its own delays. An inaccessible or inconsistent service should not place the burden of its design failures on the employee. Train managers to receive uncertainty without demanding an immediate conclusion. “Let us establish the facts before we commit” is a useful leadership response. Where concerns involve the manager, provide another route. Advice should not require the permission of the person whose instruction is being questioned.

Turn Repeated Questions into Better Design

An advice log can reveal where policies, training, and workflows leave employees uncertain. Repeated questions about one approval may indicate vague or imprecise instructions or even an unclear policy. Questions arriving after commitments may indicate that the control sits too late in the process. Different answers to the same facts may indicate that advisers need alignment. Treat those patterns as hypotheses to investigate, not conclusions to impose.

NIST SP 800-50 Revision 1 approaches cybersecurity and privacy learning through audience needs, behavior change, evaluation, and improvement. Applying that learning-cycle logic to compliance guidance can help connect recurring questions with targeted program changes. For the demonstration team, a useful improvement might be an approved dataset library and a clear route for reviewing external tools. That would address the underlying business need rather than simply repeat the prohibition. Test the revision with the people performing the work. Can they find the approved materials? Do the materials meet the legitimate purpose? Do they know when a different use needs review?

The Compliance Takeaway

The bottom line for a compliance professional is to recognize the situation, explain the issue, provide usable help, and do so before the critical encounter. For companies, that means making advice available where decisions happen. It means clear ownership, appropriate expertise, reliable escalation, and answers that distinguish permission from unresolved questions.

The business should not need a heroic employee to find the one person who understands the issue. Nor should compliance require a crisis before it becomes accessible.

Return to the demonstration. The employee asked before uploading the records. The adviser identified a responsible alternative. The team continued its work without treating the deadline as permission to ignore the concern. That is the result to design for.

The best time to explain the antidote is before someone needs to recover from the exposure.

Categories
Blog

The Metaverse and Compliance: Governing Behavior, Trust, and Delegated Authority

Imagine a virtual meeting in which an employee’s avatar nods in agreement. A colleague interprets that gesture as support for a business decision. But software, not the employee, generated the nod. Would your organization know the difference? More importantly, would its approval controls?

That hypothetical illustrates the governance challenge Patrick Henz raises in “The psychological impact of the Metaverse.” Henz explores how virtual environments could reshape socialization, identity, trust, and decision delegation to artificial intelligence.

His article is explicitly a prediction and an invitation to discussion, not proof that every anticipated psychological effect will occur. That distinction matters. Compliance should neither dismiss emerging risks nor present speculation as established evidence. Metaverse. Henz: For Chief Compliance Officers, the central question is practical: How should a company govern an environment that could influence both what people do and how they understand their relationships with technology?

Start with the Environment, Not the Marketing Label

Henz defines the Metaverse as interconnected, persistent virtual worlds with continuity of identity, communications, assets, and other data. An isolated virtual meeting platform does not satisfy that definition simply because its supplier uses the label. He also distinguishes professional and educational applications from private and leisure uses, while recognizing that the boundaries can overlap. His professional examples include learning with digital twins and using gamification to support participation. Metaverse. Henz

For compliance, this suggests beginning with the actual business activity. Is the company providing training, facilitating collaboration, selling products, or allowing software to represent employees? Each purpose warrants different controls. A simulation for practicing equipment operation raises different questions from an autonomous representative participating in a confidential negotiation.

Before approving a pilot, document its purpose, participants, data flows, and permitted actions. Identify which functions remain under direct human control. Assess the proposed activity rather than treating “the Metaverse” as a single risk category.

Socialization and Roles: Carry the Culture into the Platform

Henz argues that experiences across physical and virtual environments may influence one another. An avatar’s appearance, the treatment it receives, and the roles a user adopts could affect self-understanding and behavior beyond a particular session. These are proposed effects, not inevitable outcomes. His discussion of “cocooning” adds an important qualification. Being physically alone does not necessarily mean feeling lonely. Virtual interaction may restore social contact, even as it substitutes for some physical experiences.

The compliance implication is not to diagnose employees through their platform usage. It is to examine whether the company’s environment supports inclusion, respectful conduct, and access to human assistance. Henz identifies harassment as a concern and discusses safety features that can separate an avatar from surrounding characters. Metaverse. Henz translates that concern into operational questions. Can an employee leave an uncomfortable interaction immediately? Can the employee report it without confronting the other participant? Who receives the report?

Extend conduct expectations to company-sponsored virtual interactions. Establish an investigation process that identifies relevant participants and preserves necessary evidence without indiscriminately recording everyone. Test those procedures before launch. An accessible reporting button means little if nobody is accountable for responding. A different employee representation should not mean a lower standard of corporate conduct.

Humanization of AI: Familiarity Is Not Assurance

Henz distinguishes human-controlled avatars from “Virtual Beings,” or VBs, controlled by AI. He suggests that an appealing representation, responsive behavior, and even a fictional biography could encourage a user to perceive a relationship with software. His virtual dog example makes the issue concrete. A digital companion might offer comfort and facilitate social interaction. Metaverse. Henz: The same companion could also use knowledge about its user to influence behavior, including encouraging longer platform use.

Henz also discusses motivated reasoning: a person’s desire for a relationship may affect what that person accepts as real. For compliance, the issue is not whether a digital character seems friendly. It is whether the organization encourages users to place inappropriate trust in it.

Consider a proposed virtual compliance assistant. A supportive personality might make it easier to ask questions. It should not obscure whether the assistant is authorized to interpret policy, receive confidential allegations, or approve an exception. Make its artificial nature, limitations, and escalation options clear. Test whether employees understand those distinctions, rather than assuming a disclosure statement resolves the problem. A personable interface is a design choice. It is not evidence that the underlying advice is reliable.

Influence: Examine the Incentives Behind the Experience

Henz describes how a virtual platform could capture user inputs, potentially including eye movements through compatible equipment. He warns that an AI-controlled character could use this information to respond persuasively, with an appealing appearance boosting perceived trustworthiness.

Henz further raises the possibility that constant, apparently unconditional attention from a Virtual Being could alter expectations of human relationships. Metaverse. Henz: For a workplace, I would treat that as a reason to preserve human support and challenge, not as a finding that virtual colleagues necessarily undermine empathy or healthy professional relationships.

The corporate application is to examine how data collection shapes behavior. For a proposed platform, ask what information is collected, why it is necessary, and whether it is used to personalize assistance or steer decisions. Ask the vendor what its system is designed to optimize. Time spent on a platform does not necessarily equal the value it delivers to an employee.

Set boundaries before deployment. Identify unacceptable uses of behavioral information, restrict unnecessary collection, and establish review requirements for changes to personalization. This is also a third-party oversight issue. Assign responsibility for reviewing the supplier’s incentives and actual practices, not merely its product demonstration. An ethics review should ask whether the experience helps people make informed choices or makes it harder for them to recognize that they are being influenced.

Offloading: Delegation Requires Defined Authority

Henz’s discussion of “offloading to the Virtual Being” brings the analysis directly into internal controls. He imagines an avatar becoming capable of autonomous activity, such as attending a meeting and summarizing it for its user. He also describes software-generated gestures, including nodding, and connections to calendars and other tools. These examples explain why the opening hypothetical matters. Metaverse. Henz

For a business, observing a meeting, expressing agreement, and authorizing action should be treated as different activities. A system permitted to perform the first should not automatically acquire permission to perform the others. Define the representative’s authority before connecting it to business workflows. Specify what it may access, communicate, recommend, and execute. Reserve designated decisions for explicit human approval.

Keep records that distinguish human instructions from automated actions. Establish a way to revoke permissions and suspend the representative when its behavior departs from its approved purpose. For consequential decisions, require an approval record rather than inferring assent from a gesture, simulated presence, or meeting attendance. Delegating a task should not obscure who remains accountable for the result.

Governance Must Include Testing, Not Merely Approval

Henz concludes by calling for supervisory oversight and continuing study of psychological effects as the technology develops. He emphasizes the opportunity to benefit users alongside the risk of exploiting their vulnerabilities, which suggests a cross-functional review involving compliance, legal, information security, human resources, technology, and the business owner. The precise structure should match the proposed use. Creating another committee does not replace assigning decision-making authority.

Start with a bounded pilot and documented assumptions. Test whether participants recognize AI-controlled characters, understand their authority, and can reach a human when needed. Include both benefits and risks in the assessment. Building on Henz’s discussion of learning applications, a company could pilot an immersive compliance scenario that lets employees practice challenging an inappropriate instruction. Evaluate employees’ choices and the support they need, not merely whether they finish the exercise. Define the conditions for modifying or stopping the pilot. Review incidents, user feedback, and control failures before expanding deployment. The board should receive information about material risks, unresolved limitations, and management’s response, rather than an assurance based solely on participation or enthusiasm.

Practical Takeaways for CCOs and Boards

Start by mapping the experience. Identify who participates, what the system observes, how it may influence behavior, and whether it can act on anyone’s behalf. Give each significant risk an accountable owner. Then test the controls against realistic scenarios. Use a harassment report, an ambiguous AI recommendation, and an unauthorized action to determine whether escalation and intervention actually work.

Finally, require evidence before expansion. Ask whether users understand the technology, whether employees can get human help, and whether management can show that delegated authority stays within approved limits. Henz’s perspective does not supply a finished corporate compliance framework. It supplies questions about human behavior that a technology-only assessment could miss.

The board’s closing question should be straightforward: Can management demonstrate that this experience supports employee judgment without confusing identity, manufacturing trust, or obscuring accountability? That is where the compliance assessment should begin, regardless of what the platform is called.

Categories
Blog

CFIUS in 2026 and Beyond: Why Foreign Investment Risk Must Become a Core Compliance Priority

For years, many corporate compliance professionals saw the Committee on Foreign Investment in the United States (CFIUS) as primarily a concern for mergers-and-acquisitions attorneys. When a foreign investor sought to acquire a U.S. business, the legal team evaluated potential national security concerns, determined whether to file, and navigated the regulatory review process. Once the transaction closed, the matter often moved off the compliance radar. That approach is increasingly difficult to defend.

The recently released 2025 CFIUS Annual Report to Congress shows that foreign investment oversight has evolved into a sophisticated regulatory regime that includes transaction screening, national security investigations, mitigation agreements, ongoing compliance monitoring, and enforcement. In an analysis by Thaddeus McBride and Faith Dibble, CFIUS Annual Report Reveals Enforcement Trends highlights several developments that should command the attention of Chief Compliance Officers (CCOs), General Counsel, and corporate boards.

The key takeaway is that CFIUS compliance must become part of an organization’s broader enterprise risk management and internal controls framework. For compliance professionals, this creates both new responsibilities and opportunities to demonstrate the strategic value of an effective compliance program.

CFIUS Activity Remains High, and Scrutiny Is Intensifying

The numbers tell an important story. During 2025, CFIUS reviewed or assessed 347 covered transactions through written notices and declarations. Overall filing volume increased about 7 percent from 2024, driven primarily by a 21 percent increase in declarations.

Written notices remained relatively stable, declining approximately 1 percent. At first glance, the growing popularity of declarations might suggest that companies are finding more efficient ways to navigate the CFIUS process. However, the underlying statistics tell a more complicated story.

In 2024, approximately 78 percent of declarations resulted in CFIUS concluding action. That figure declined to approximately 66 percent in 2025. Meanwhile, the percentage of declarations resulting in requests for full written notices increased from 15 percent to 26 percent. This is significant. A declaration provides an abbreviated review process, generally involving a 30-day assessment. A full written notice involves an initial 45-day review, potentially followed by an additional 45-day investigation. For companies pursuing cross-border acquisitions, these timelines create substantial transaction uncertainty.

The compliance lesson: CFIUS risk assessment must occur during the earliest stages of transaction planning, not after the parties have negotiated their principal commercial terms.

CCOs should work closely with legal, corporate development, finance, and business leadership to ensure national security considerations are integrated into acquisition due diligence. The objective is not simply to determine whether a filing is required. It is to understand how regulatory risk may affect transaction structure, timing, valuation, and post-acquisition operations.

National Security Risk Extends Beyond Traditional Defense Industries

Another important finding concerns the industries attracting CFIUS attention. In 2025, finance, information, and services accounted for about 49.5 percent of non-real estate notices, while manufacturing accounted for another 39.5 percent. Together, these sectors accounted for nearly 90 percent of notices.

This demonstrates that CFIUS scrutiny extends well beyond traditional defense contractors and aerospace manufacturers. Companies in financial services, technology, telecommunications, data analytics, advanced manufacturing, and other commercial industries may hold assets that raise national security concerns.

Those assets may include sensitive personal information, proprietary technology, critical infrastructure, government contracts, or supply chain capabilities. Consider a foreign investor acquiring a U.S. technology company whose principal business involves collecting and analyzing consumer data.

The transaction may appear commercially straightforward. However, access to sensitive personal information, cybersecurity systems, or technology infrastructure could introduce significant national security considerations.

For CCOs, this means traditional anti-corruption and sanctions diligence is no longer sufficient when evaluating cross-border investments. A comprehensive assessment should examine beneficial ownership, sensitive technology, cybersecurity, data access, export controls, government relationships, and supply chain dependencies.

This is where compliance can provide real business value. By identifying these risks early, compliance professionals can help leadership make informed investment decisions before the organization commits substantial financial and operational resources.

Mitigation Agreements Are Continuing Compliance Obligations

Perhaps the most consequential findings for compliance professionals concern mitigation and enforcement. During 2025, CFIUS imposed mitigation measures and conditions in approximately 12 percent of transactions. At year-end, the committee monitored 234 mitigation agreements and conditions and conducted 40 compliance site visits.

These figures show that CFIUS oversight often continues long after a transaction closes. A mitigation agreement is not simply a legal document negotiated to obtain regulatory approval.

It establishes operational obligations that may require continuing monitoring, reporting, restrictions on access to information or technology, and other safeguards. Failure to implement those obligations effectively can create significant compliance and enforcement exposure.

This should sound familiar to anyone who has followed the Department of Justice’s approach to corporate compliance. Although CFIUS operates under a distinct legal framework, the underlying compliance principles mirror those in the DOJ’s Evaluation of Corporate Compliance Programs.

The compliance lesson: Every CFIUS mitigation agreement should be translated into an operational compliance framework with clearly assigned responsibilities. That framework should include documented procedures, employee training, testing, escalation protocols, and periodic management reporting. Internal audit should evaluate whether the organization is meeting its obligations.

The board or an appropriate board committee should receive meaningful information about significant mitigation requirements and compliance performance. The objective is to show not merely that the company agreed to certain restrictions, but that those restrictions work in practice.

Non-Notified Transactions Are Becoming an Enforcement Priority

During 2025, the committee investigated 90 potential non-notified transactions, opened 62 formal inquiries, and requested filings in nine cases. Two additional transactions were voluntarily submitted before CFIUS issued formal filing requests. These statistics show that CFIUS does not rely exclusively on companies to identify and report potentially covered transactions.

The committee obtains information through government agencies, congressional notifications, media reports, commercial databases, public tips, classified information, and voluntary disclosures. This has profound implications for corporate compliance.

Historically, some organizations may have viewed not filing as the conclusion of their CFIUS analysis. That assumption is increasingly risky. CFIUS can examine completed transactions and require parties to address national security concerns after closing. In certain circumstances, those concerns may result in mitigation obligations or divestiture.

The 2025 report identified seven transactions that parties abandoned after CFIUS could not identify acceptable mitigation or the parties declined proposed mitigation measures. Two matters also resulted in presidential orders prohibiting acquisitions or requiring divestment. For boards and senior executives, the implications are substantial.

The compliance lesson: Organizations should establish a documented process to evaluate CFIUS jurisdiction and filing obligations for relevant acquisitions and investments. Where management determines that a voluntary filing is unnecessary, the decision should be supported by a documented risk assessment. This documentation should explain the transaction’s ownership structure, relevant national security considerations, and rationale for the filing decision. A defensible decision-making process is essential to effective compliance governance.

Voluntary Self-Disclosure Must Be Part of the Compliance Conversation

The annual report also highlights CFIUS’s continued attention to voluntary self-disclosures involving potential mandatory-filing failures and violations of mitigation obligations. Importantly, the report notes that many instances of noncompliance do not result in penalties. This should not be interpreted as regulatory indifference. Rather, it reinforces the importance of identifying potential violations, investigating them promptly, and considering appropriate disclosure and remediation.

For compliance professionals familiar with the DOJ’s Corporate Enforcement and Voluntary Self-Disclosure Policy, the broader principle is recognizable. Regulators place significant importance on how organizations respond when problems are discovered. However, CFIUS disclosure and enforcement procedures are distinct from DOJ criminal enforcement policies. Companies should not assume that DOJ disclosure incentives automatically apply to CFIUS matters.

The appropriate response starts with a credible internal process to identify and escalate concerns. Employees responsible for implementing mitigation agreements must understand their obligations and know how to report potential violations. Compliance teams should establish procedures to investigate concerns, preserve relevant evidence, determine root causes, and evaluate corrective action. Where a potential violation is identified, legal and compliance leadership should assess whether voluntary disclosure is appropriate under the applicable CFIUS framework.

What CCOs Should Do Now

The 2025 annual report provides a practical roadmap for strengthening foreign investment compliance.

  1. Incorporate CFIUS considerations into the enterprise risk assessment. Identify business activities, investment structures, and assets that may create national security exposure.
  2. Integrate CFIUS screening into transaction approval procedures. Require appropriate legal and compliance review before significant cross-border investments advance.
  3. Strengthen third-party and beneficial ownership diligence. Understanding who ultimately owns or controls an investor can be essential to identifying regulatory concerns.
  4. Establish ongoing monitoring for mitigation agreements. Assign control owners, set performance expectations, test periodically, and document remediation.
  5. Develop escalation and investigation procedures for potential violations. Ensure employees understand how to report concerns and management understands when disclosure decisions must be considered.
  6. Provide the board with meaningful reporting on material CFIUS risks, significant mitigation obligations, and emerging regulatory developments.

Conclusion: CFIUS Compliance Is a Lifecycle Responsibility

The 2025 CFIUS Annual Report reveals an enforcement environment characterized by sustained transaction activity, increased scrutiny of abbreviated filings, continuing mitigation oversight, and growing attention to transactions that were never submitted for review.

The fundamental lesson is straightforward. CFIUS risk begins before a transaction is signed and may continue long after the transaction closes. For CCOs, the challenge is to ensure that foreign investment compliance is integrated into governance, risk management, internal controls, and organizational accountability.

The companies best positioned to manage this environment will be those that identify national security risks early, make informed filing decisions, operationalize mitigation commitments, and continuously evaluate compliance effectiveness. CFIUS should no longer be viewed solely as a transaction approval process.

It is an ongoing compliance obligation that requires the same discipline, oversight, and commitment to continuous improvement expected of any effective corporate compliance program.

Categories
Blog

Frankenstein and Compliance: Part 4 – The Ghost of Frankenstein: Declaring the Monster Dead Is Not a Control

Ed. Note: This month, on his podcast series Popcorn and Compliance, Tom Fox dives deep into the first five Frankenstein movies. Over October, Tom Fox will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolf Man. This blog post accompanies the podcast series.

The first three Frankenstein films trace a recognizable progression in compliance. Frankenstein examined innovation without adequate governance. Bride of Frankenstein explored what happens when leadership recognizes a risk but lets pressure and rationalization override judgment. Son of Frankenstein shifts to inherited risk and the responsibility of new leadership to address problems its predecessors created. The Ghost of Frankenstein (1942) raises the next question. What happens when the organization believes the problem has already been addressed?

By the fourth film, no credible argument suggests that Frankenstein’s Monster represents an unknown risk. Communities have confronted him. Members of the Frankenstein family have attempted to control him. The consequences are well established. Yet the Monster remains. This time, Ygor, again played by Bela Lugosi, brings the Monster, now played by Lon Chaney Jr., to Ludwig Frankenstein, Henry Frankenstein’s other son. Ludwig initially wants nothing to do with his family’s legacy. He eventually concludes that he can solve the problem through a brain transplant. The proposed solution appears technically sophisticated. It is also compromised when Ygor and Ludwig’s colleague Bohmer secretly substitute Ygor’s brain for the intended brain.

For corporate compliance professionals, The Ghost of Frankenstein is a case study in remediation and control effectiveness. Companies routinely investigate misconduct, revise policies, conduct training, implement corrective actions, and close audit findings. Those activities matter, but they don’t prove the underlying risk has been reduced. The relevant compliance question is not whether management completed the remediation plan. It is whether the remediation worked.

Closure Is an Administrative Status

Compliance, Internal Audit, Legal, Finance, and business management are familiar with corrective-action plans. An issue is identified. Management develops remediation. Actions are assigned. Deadlines are established. Policies may be revised, systems changed, training delivered, or controls added. Eventually, the required actions are completed, and the finding is marked closed. That process is not inherently wrong. Organizations need a disciplined method for tracking remediation. The risk comes when administrative closure becomes confused with risk reduction.

Suppose an investigation finds that employees circumvented a third-party approval requirement. Management revises the policy and retrains the business. Both actions may be appropriate. They also may have little effect if the original problem arose because sales targets encouraged employees to bypass the process and local managers routinely approved exceptions. The policy was not necessarily the root cause. Training was not necessarily the solution. A closed action item therefore tells management that a required activity occurred. It does not automatically establish that the control environment changed. That distinction is central to compliance program effectiveness.

Start With Root Cause

Ludwig Frankenstein approaches the Monster as a technical problem. Replace the brain, and the problem is solved. Compliance can fall into the same trap with remediation. Organizations sometimes start corrective action before they have adequately identified why the failure occurred. Effective remediation should begin with root-cause analysis.

Suppose a salesperson makes an improper payment through a third-party distributor. The immediate facts may be straightforward. The employee violated policy, the payment was inappropriate, and the third party was involved. A root-cause analysis goes further.

Why was the third party selected? Was due diligence adequate? Were red flags identified? Did anyone override the process? Was the compensation structure unusually aggressive? Did management communicate unrealistic sales expectations? Were invoices sufficiently detailed? Did Finance question the payments? Had similar issues occurred previously? Did employees believe management would support them if they delayed the transaction? These questions shift the analysis from the individual event to the system that allowed it to happen.

Individual accountability remains important. A company should not use systemic explanations to excuse deliberate misconduct. But disciplining an employee does not repair a control environment. A strong remediation plan addresses both.

Repeat Findings Are Information

Recurring compliance issues should receive particular attention.

  • If Internal Audit repeatedly identifies the same control weakness, that is information.
  • If multiple investigations identify similar conduct in the same business unit, that is information.
  • If hotline reports repeatedly raise concerns about the same management behavior, that is information.
  • If third-party monitoring continually identifies the same documentation gaps, that is information.

Repeat issues may indicate that previous remediation addressed symptoms rather than causes. They may also indicate weak implementation, insufficient resources, inadequate supervision, or management resistance. The CCO should therefore have a mechanism to identify recurrence across data sources.

An audit finding may appear unrelated to a hotline complaint. A hotline complaint may appear unrelated to a third-party exception. A third-party exception may appear unrelated to an investigation. Viewed together, they may demonstrate a common control problem. This is where compliance data becomes more valuable than compliance statistics. The objective is not simply to count investigations, audit findings, policy exceptions, or hotline reports. The goal is to identify patterns that tell management how the organization operates.

Bohmer and Management Override

The brain-transplant sequence provides the film’s strongest internal-control lesson. Ludwig develops a plan to replace the Monster’s brain. Whatever one thinks of the underlying objective, the process is defined, and the outcome is intended. Then Bohmer and Ygor subvert it.

Control isn’t defeated because nobody designed a process. It fails because individuals with access and opportunity manipulate the process. That is management override. Corporate controls often assume authorized individuals will use their authority as intended. That assumption requires testing.

  • A manager can approve an expense.
  • A finance executive can authorize a journal entry.
  • A procurement leader can approve a vendor.
  • A senior executive can authorize a policy exception.
  • An administrator can change system permissions.
  • A business leader can influence a third-party decision.

Those authorities are necessary for business operations. They can also create risk when one individual possesses excessive discretion or when oversight is weak. Segregation of duties, approval thresholds, access controls, audit trails, independent review, exception reporting, and transaction monitoring exist partly to address this problem. For the CCO, the question is not simply whether a control exists. It is whether someone can circumvent it and whether the organization would know.

COSO and the Broader Control Environment

The Ghost of Frankenstein also provides an opportunity to consider the COSO Internal Control Integrated Framework. Controls do not operate in isolation. The control environment establishes expectations, authority, accountability, and standards of conduct. Risk assessment identifies threats to organizational objectives. Control activities translate those risks into specific preventive or detective measures. Information and communication ensure the right people receive relevant information. Monitoring determines whether the system continues to operate effectively.

Compliance failures often occur when organizations focus too narrowly on a single control activity. A company identifies misconduct involving gifts and entertainment, so it lowers approval thresholds. That may be useful.

  • But what if managers continue encouraging employees to find ways around the limits?
  • What if expense descriptions are vague?
  • What if Finance does not review unusual patterns?
  • What if senior executives routinely receive exceptions?
  • What if employees believe questioning an expense submitted by a powerful executive will damage their careers?

The approval threshold may be well designed. The broader control environment remains weak. This is why compliance should work closely with Internal Audit, Finance, HR, Legal, and business management. Compliance risk rarely fits neatly within one control owner.

Design Effectiveness and Operating Effectiveness

One of the most useful distinctions in controls work is between design effectiveness and operating effectiveness. A control may be well designed. That does not mean it operates effectively. Consider third-party due diligence. The company may have a strong written process requiring risk classification, beneficial ownership review, screening, business justification, approval, contractual protections, and periodic monitoring. On paper, the control appears robust. Then testing reveals that business sponsors routinely submit incomplete information, reviewers approve files without resolving red flags, contracts are signed before diligence is complete, and periodic reviews are months overdue. The control design is not necessarily the problem. It is execution.

Conversely, employees may execute a poorly designed control exactly as instructed, even as it fails to address the relevant risk. Compliance needs to understand both. This matters especially when validating remediation. Management should not simply confirm that a new control was implemented. Someone should determine whether the control is appropriately designed and whether it operates consistently in practice. That is how an organization moves from remediation activity to evidence of effectiveness.

Investigations Should Improve the Program

Investigations represent one of the richest sources of compliance intelligence available to a company. They show where actual conduct differs from expected conduct. Yet organizations sometimes treat investigations primarily as case-management exercises. An allegation arrives, the company investigates, decides whether to substantiate it, takes disciplinary action where appropriate, and closes the matter. That process resolves the case. It does not necessarily improve the compliance program.

For significant matters, a compliance professional should ask what the investigation teaches the organization.

  • Did a control fail?
  • Was a policy unclear?
  • Was supervision inadequate?
  • Were incentives relevant?
  • Did the reporting system work?
  • Was retaliation alleged?
  • Were similar concerns raised previously?
  • Did management respond appropriately when warning signs appeared?
  • Should monitoring change?
  • Should the risk assessment change?

The investigation should feed the compliance program. Otherwise, the organization may become very efficient at investigating the same problem repeatedly.

Test the Remediation

Perhaps the most important lesson from The Ghost of Frankenstein is that remediation requires validation. Management implements a corrective action. Someone should return later and determine whether it worked. The timing and depth of testing should depend on risk. A significant control failure may require independent validation by Internal Audit, Compliance testing, or another qualified function. Lower-risk matters may be validated through management review or monitoring. The important point is that the organization should define what success looks like before declaring the remediation effective.

The Compliance Lessons

The Ghost of Frankenstein demonstrates a basic principle of compliance program effectiveness. Activity is not the same as effectiveness. A company can revise a policy, deliver training, add an approval, complete a corrective-action plan, and close an audit finding. Each action may be appropriate. The compliance question is whether those actions changed the risk.

That requires root-cause analysis, well-designed controls, disciplined implementation, monitoring, testing, and accountability. It also requires management to recognize that some failures are not caused by employees misunderstanding the rules. They may result from incentives, authority structures, management override, weak supervision, or a control environment that rewards the wrong behavior.

The goal of remediation is not to demonstrate that the organization did something. It is to demonstrate that the organization learned something and changed accordingly. That is why declaring the Monster dead is not a control. The evidence comes from whether he stays dead.

Our final installment of my Universal Classic Monster Movie Month for 2026 takes the Frankenstein compliance story in a different direction. After four films dealing largely with one persistent risk, Universal brings another major risk into the picture. In Frankenstein Meets the Wolf Man, the issue is no longer simply whether an organization can identify, govern, inherit, or remediate a single compliance problem. It is what happens when independently managed risks begin to interact. For modern companies confronting AI, cybersecurity, privacy, third-party, sanctions, anti-corruption, financial, and operational risks, that may be the most important governance question of all: What happens when the risks we manage separately collide?

For a review of the movie and audio analysis, check out Timothy and Fiona’s take on it in Popcorn and Compliance.

Categories
Daily Compliance News

Daily Compliance News: October 22, 2026, The CCOs as Strategic Advisors Edition

Welcome to the Daily Compliance News. Each day, Tom Fox, the Voice of Compliance, brings you compliance-related stories to start your day. Sit back, enjoy a cup of morning coffee, and listen in to the Daily Compliance News. All from the Compliance Podcast Network. Each day, we cover four stories from the business world, compliance, ethics, risk management, leadership, or general interest for compliance professionals.

Top stories include:

  • The Cornell scandal offers lessons for high-stakes internal reviews. (Bloomberg Law)
  • You can use ‘compliance’ and corruption in laws. (Trend.az)
  • CCOs as strategic advisors. (CCI)
  • AML tech improving compliance. (TechBullion)

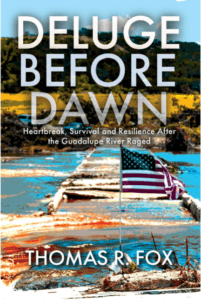
My first work of general non-fiction is now out: Deluge Before Dawn, the story of the 2025 flood in Kerr County, Texas, which killed 119 people and devastated a county. It is a story of tragedy, heartbreak, survival, and resilience.

It is available on the following sites:

Amazon.com

Stoney Creek Publishing

Barnes and Noble

Texas A&M University Press

Bookshop.org

Google.Books

Walmart

Categories
Blog

Frankenstein and Compliance: Part 3 – Son of Frankenstein: You Inherited the Castle, You Inherited the Risk

Ed. Note: This month, on his podcast series Popcorn and Compliance, Tom Fox dives deep into the first five Frankenstein movies. Over October, Tom Fox will consider Frankenstein, The Bride of Frankenstein, The Son of Frankenstein, The Ghost of Frankenstein, and Frankenstein Meets the Wolf Man. This blog post accompanies the podcast series.

The first two Frankenstein films present two distinct compliance failures. Frankenstein examined innovation without adequate governance. Bride of Frankenstein shows leadership that understands the risk but lets pressure, ambition, and rationalization override judgment. Son of Frankenstein (1939) presents the next stage: inherited risk, or in the business world, risks through acquisition.

Wolf von Frankenstein, played by Basil Rathbone, returns with his family to his ancestral estate hoping to restore the Frankenstein name. Instead, he encounters Ygor, played by Bela Lugosi, and discovers that his father’s Monster is still alive. Wolf had no role in creating the original problem, but his discovery forces him to decide how to address the legacy he has inherited.

That situation should be familiar to companies following acquisitions, leadership transitions, compliance investigations, or changes in the control environment. New management may have no connection to historical misconduct. An acquiring company may not have created the target’s problematic third-party relationships. A new CCO may inherit investigations and remediation projects that were initiated years earlier. Historical responsibility and current responsibility are different questions. The business issue is how management responds once a legacy risk becomes known.

The Castle Is an Acquisition

Think of Wolf’s return to the Frankenstein estate as an acquisition. He receives the property, assets, name, and opportunity to benefit from his father’s scientific legacy. He also assumes the consequences associated with that legacy. Corporate acquisitions work much the same way. Companies acquire revenue, customers, employees, technology, intellectual property, distribution networks, and market access. They may also inherit high-risk third parties, weak internal controls, questionable historical practices, unresolved investigations, government relationships, and cultural problems.

This is why compliance due diligence should focus on how the target actually conducts business rather than simply whether it has the expected compliance infrastructure. A target may have a Code of Conduct, an anti-corruption policy, annual training, and a hotline. Those are relevant data points, but they do not establish program effectiveness.

Compliance needs to understand the target’s business model and risk profile. Consider such questions as: Where does the business operate? Who are its customers? Does it interact with government agencies or state-owned entities? Which third parties generate or facilitate business? How does the company select and compensate those parties? What does the investigation history reveal? Are there recurring audit or control deficiencies? What does speak-up data indicate? Are significant policy exceptions concentrated in particular markets or business units? The objective is to understand the risk embedded in the business being acquired.

Due Diligence Is the Beginning, Not the End

Even well-designed pre-acquisition due diligence has limitations. Transactions operate under deadlines and time pressures. Access to employees and records may be restricted. (See: Opinion Release 08-02) Data may be incomplete. Privacy requirements may constrain review. Some risks simply do not become visible until the buyer gains access to systems, records, personnel, and financial information after closing. Those limitations make the connection between due diligence and post-acquisition integration critical.

If the buyer cannot complete diligence on a high-risk distributor before closing, that relationship should become a post-closing priority. If investigation records are incomplete, they should be reviewed during integration. If significant controls cannot be tested before the transaction, testing should be incorporated into the integration plan. Compliance should therefore document unresolved diligence issues and carry them forward with assigned owners and deadlines.

This discipline matters because closing creates competing priorities. Management quickly shifts to customers, systems, personnel, financial reporting, cost savings, and expected synergies. Compliance integration can become one workstream among many. An unanswered compliance question doesn’t become less significant once the transaction closes.

Post-Acquisition Integration Is the Operational Test

An acquiring company can conduct excellent due diligence and still create exposure if it fails to integrate the acquired business effectively. Post-acquisition integration is where the buyer’s compliance expectations become operational. Employees need to understand the acquiring company’s Code of Conduct, policies, reporting mechanisms, investigation procedures, third-party requirements, approval processes, and internal controls. High-risk third parties may require additional diligence. Contracts may need updated compliance provisions. Financial controls may need harmonization. Employees need risk-appropriate training.

Integration should also reflect the acquired company’s actual risk profile. A business operating primarily in lower-risk markets with direct sales may require a different approach than a company that depends on agents and distributors in jurisdictions with substantial government interaction. Do not apply the same integration checklist mechanically to every acquisition.

The CCO should know which issues require immediate attention, which can be addressed over a reasonable integration period, and who is accountable for each significant action. Without ownership and monitoring, temporary integration gaps can become lasting control weaknesses.

Ygor and the Informal Organization

Ygor provides one of the movie’s most useful compliance lessons. He understands the Frankenstein estate better than Wolf does. He knows its history, its secrets, and how things actually work. Every organization has a formal structure and an informal operating system. The organizational chart describes reporting relationships. Policies describe required processes. Procedures identify approvals. Employees know how business actually gets done.

They know which approvals receive meaningful scrutiny and which are largely administrative. They know which managers routinely approve exceptions. They know which third parties have special relationships with executives. They know which controls become flexible near quarter-end. They know whether raising a concern is welcomed or career-limiting. This is why compliance risk assessment cannot rely exclusively on documents.

Policies lay out how an organization is supposed to operate. Interviews, focus groups, hotline information, investigations, transaction testing, third-party monitoring, audit findings, and employee surveys can show how it operates in practice. That distinction becomes particularly important following an acquisition. The buyer needs to understand not only the target’s compliance architecture but also its operating culture.

Institutional Memory Is a Compliance Control

Inspector Krogh represents the other side of organizational knowledge. He remembers the consequences of the original Frankenstein experiment because he experienced them personally. His perspective is shaped by history, not by Wolf’s confidence that the past can be managed differently. Companies need mechanisms for preserving similar institutional knowledge.

Investigations produce knowledge. Internal audits produce knowledge. Regulatory inquiries produce knowledge. Compliance monitoring and remediation projects produce knowledge. That knowledge can disappear surprisingly quickly. Employees retire. CCOs leave. Executives change roles. Board members rotate. Investigations close. Outside counsel completes an engagement. Remediation projects are marked complete.

Years later, new management may propose a business arrangement, third-party relationship, market strategy, or control change similar to one the organization previously determined was problematic. An effective compliance program should prevent important lessons from depending entirely on the memories of individual employees.

Significant investigation findings should inform future risk assessments. Root causes should influence control design. Remediation lessons should affect monitoring. Historical third-party concerns should remain available when relationships are reconsidered. An investigation’s purpose is not simply to resolve an allegation. It should also improve the organization’s understanding of its risks.

New Leadership and the Risk of Exceptionalism

Wolf demonstrates another challenge common to leadership transitions. New leaders often believe they can manage risks that previous leaders could not. Sometimes they can. New leadership may bring stronger systems, better controls, additional resources, and improved judgment. The problem arises when confidence leads management to discount why earlier controls or restrictions were established.

A new sales executive may propose reengaging a distributor previously terminated for compliance concerns. A new CEO may reconsider a market that previous management considered too risky. A new business leader may conclude that an approval requirement imposed after earlier misconduct is unnecessarily restrictive. Any of those decisions may be appropriate. Controls should not remain in place indefinitely simply because they are old. But management should understand the history before changing them.

Before removing a control, determine why it was created. Before reengaging a third party, understand why the relationship ended. Before changing monitoring requirements, identify the risk they were designed to address. Some controls become obsolete. Others represent lessons learned. Good governance distinguishes between the two.

Red Flags and the Governance Response

The central compliance issue arises when Wolf learns the Monster is alive. At that point, the question moves from discovery to response. Corporate compliance systems serve a similar purpose. Internal controls, monitoring, Internal Audit, risk assessments, investigations, hotlines, and management reporting should surface significant information.

The effectiveness of those systems depends upon what happens after the information arrives. The Evaluation of Corporate Compliance Programs (ECCP) suggests such inquiries as: Was the issue investigated? Was it escalated appropriately? Did management assign remediation? Was completion tracked? Was effectiveness tested? Did significant information reach the board or appropriate committee? A sophisticated reporting system provides little protection if material concerns repeatedly reach decision-makers without producing action.

For a CCO, this means escalation protocols matter. The organization should understand which issues remain within normal management processes, which require senior management attention, and which warrant board notification.

Legacy Third Parties Require Fresh Review

Inherited third-party relationships deserve particular attention because longevity can create a false sense of security. The distributor has worked with the business for fifteen years. The consultant is well known locally. The customs broker has always handled interactions with government agencies. No significant problems have been reported previously. Those facts provide context. They do not replace risk-based oversight.

Acquisitions and leadership transitions provide an opportunity to reassess significant legacy relationships. Is the third party still necessary? Is the business rationale documented? Is beneficial ownership information current? Has the risk profile changed? Are payment arrangements appropriate? Are contracts current? Has monitoring identified concerns? Longstanding relationships should not automatically be grandfathered into the current compliance program. Some may warrant closer attention precisely because they were established under different controls, different management, and different expectations.

Practical Actions for the CCO

Son of Frankenstein suggests a practical agenda for compliance leadership. Due diligence should examine actual business operations, not just the existence of policies. Unresolved diligence issues should move directly into the integration plan with defined ownership and deadlines. Integration should be risk-based and should include controls, training, reporting mechanisms, investigations, and third-party oversight.

Significant legacy third parties should be reassessed rather than automatically accepted. Preserve investigation findings and past control failures as institutional knowledge and incorporate them into future risk assessments. New leadership should understand why significant controls were established before deciding to eliminate or weaken them. Finally, significant inherited risks should have clear owners. Issues that sit between the transaction team, business leadership, Legal, Compliance, Finance, and Internal Audit can otherwise remain unresolved because everyone assumes someone else is responsible.

The Compliance Lesson

Son of Frankenstein demonstrates the difference between responsibility for creating a problem and responsibility for managing one. Organizations routinely inherit compliance risks through acquisitions, leadership transitions, longstanding business practices, third-party relationships, and unresolved control weaknesses. New management should not be treated as responsible for conduct that occurred before it arrived. Its responsibility begins with the response.

Effective compliance requires the organization to identify inherited risks, prioritize them by significance, assign ownership, integrate acquired operations, preserve institutional knowledge, and verify corrective actions. That is the business lesson from Wolf von Frankenstein’s return to the family estate. The value of an inheritance cannot be separated from its risks.

The next stage of the Frankenstein story raises another familiar compliance issue. Organizations can identify problems, investigate them, revise policies, conduct training, complete remediation plans, and close findings. Yet sometimes the same problem returns.

In our next selection, we consider The Ghost of Frankenstein. In this movie, the compliance issue is no longer discovery or inheritance. It is program effectiveness. If management says the problem has been remediated, what evidence demonstrates that the remediation actually worked?

For a discussion on these topics and a review of the movie, check out Timothy and Fiona in this episode of Popcorn and Compliance.

Categories
Blog

The Locked-Room Compliance Problem: Seven Lessons from John Dickson Carr

I don’t just enjoy movies for my annual October Movie Monster-fest. I have been reading Tom Mead’s Joseph Spector mysteries, and the puzzles have brought me back to a question every compliance professional should recognize: What happens when the evidence shows that something occurred, but everyone insists the controls made it impossible?

Imagine an unauthorized payment. Finance says two approvals were required. Technology says access was restricted. Management says the procedures were clear. Yet the money left the company. There is your locked room.

John Dickson Carr offers a useful starting point. In Chapter 17 of The Hollow Man, his detective, Dr. Fell, describes seven categories of locked-room mystery. These are explanations of apparently impossible events, not seven mandatory writing rules or a compliance framework. Nevertheless, they invite a productive investigative habit: challenge the assumptions that make the evidence seem impossible. (See 7 Types of Locked Room Mystery)

Spoiler notice: This article discusses locked-room mechanisms that may reveal how some mystery plots work.

1. An Accident That Looks Like Murder: Test the Premise

Fell’s first category in The Hollow Man removes the murderer altogether. A fatal accident inside the room creates circumstances that suggest murder. The investigator, searching for an ingenious escape route, tries to explain something that never happened. That is a useful warning for internal investigations. Before asking how an employee defeated a control, establish whether anyone deliberately defeated it.

Consider a hypothetical duplicate payment. An investigator might suspect collusion between an employee and a supplier. But the explanation could be a poorly configured system, an ambiguous invoice reference, or overlapping responsibilities during a transition. Those possibilities require different evidence and different remediation.

The point is not to excuse misconduct. It is to avoid treating the allegation as the conclusion. An investigation should test competing explanations, including evidence that contradicts its opening theory. Finding an error rather than fraud should refine accountability, not end the inquiry.

Ask: What evidence would distinguish deliberate misconduct from error or process failure?

2. Poison Gas: Examine the Environment

In the second category, Fell describes poison gas overcoming the victim. The resulting distress may disturb the furniture, making it look like a struggle with an attacker. The room tells a story, but the apparent story misidentifies the cause. My compliance parallel is the operating environment.

Imagine investigators discovering that several analysts bypassed required reviews. Focusing only on individual decisions might produce several disciplinary recommendations. Looking at the environment could reveal something else: supervisors demanding immediate clearance, unresolved staffing requests, and employees learning that escalation brings criticism rather than assistance.

Those conditions would not automatically excuse individual decisions. They would become additional hypotheses to investigate. The mistake is to attribute a pattern entirely to personal failings without examining the conditions in which people worked. Another training module may address neither the workload nor the managerial instructions.

Ask: What pressures, incentives, and supervisory behaviors surrounded the decisions under investigation?

3. The Mechanical Trap: Look Before the Event

Fell’s third category in The Hollow Man involves a trap placed in the room and activated later by the victim. The murderer can be elsewhere when the fatal event occurs. An investigator who focuses only on who was present at that moment starts with an unnecessarily narrow timeline. The compliance equivalent is a process altered before an apparently routine transaction.

Suppose someone changes a supplier’s payment information. Weeks later, an ordinary payment run uses that information. The employees processing the payment may follow their assigned steps while relying on a record whose integrity was compromised earlier. The investigative question is therefore larger than who approved the final transaction. Who established the underlying data? Who could change it? What evidence shows which version the approvers saw? Do not confuse the moment a loss becomes visible with the moment its cause was introduced. Review the relevant changes, permissions, and dependencies leading up to the event.

Action: Reconstruct the setup as carefully as the execution.

4. Suicide Disguised as Murder: Challenge the Attribution

The fourth category concerns a suicide arranged to resemble murder, potentially to incriminate an innocent person. In Fell’s discussion, the apparent crime scene is not merely evidence of an event. It attempts to direct the investigator toward a particular explanation. The compliance analogy is staged attribution, not the death itself.

Consider a hypothetical manager who instructs an employee outside the formal workflow to process an exception. The employee’s name remains in the system. The manager subsequently presents that record as proof that the employee acted alone. The record might be authentic and still tell an incomplete story.

An investigator should examine who created the evidence, what it actually establishes, and what surrounding communications may qualify it. Neither a senior executive’s account nor a compelling accusation should substitute for corroboration. Apply that discipline without treating a reporting employee as presumptively unreliable.

Ask: Does this evidence establish responsibility, or merely show whose name appears in the file?

5. Impersonation After Death: Separate Identity from Appearance

In Fell’s fifth category, the murderer impersonates a victim who has already been killed. Observers believe they have seen the victim alive, placing the death later than it actually occurred. Identity and chronology reinforce the same mistaken conclusion. For compliance professionals, the analogy is an approval that appears to establish more than it does.

Imagine a transaction record carrying a director’s username. Does that prove the director personally reviewed the transaction? Before answering, examine delegated authority, account access, and how any automated workflow operates. A legitimate delegation and an unauthorized use could produce superficially similar records.

The timestamp needs equal attention. Does it record the decision, the system entry, or a later processing step? The mistake is turning a familiar name and precise-looking time into unquestioned proof. Precision in a record is not the same as certainty about its meaning.

Action: Verify the actor, authority, and meaning of the timestamp before assigning accountability.

6. Murder from Outside the Room: Reconsider the Boundary

Fell’s sixth category allows the murderer to act from outside while circumstances suggest that the killing required someone inside. The apparent impossibility depends on a mistaken assumption about where the attacker needed to be. This offers an analogy for control boundaries.

Imagine a restricted finance application receiving supplier information from another system. Investigators confirm that nobody improperly accessed the finance application and conclude that the transaction could not have been manipulated. But that conclusion leaves the incoming information unexamined.

Follow the transaction upstream. What information did procurement, an outsourced service provider, or a business partner provide? Which team validated it? What changes could occur before the finance control began operating?

A control may function as designed within its boundary while leaving a consequential dependency outside the investigation. The appropriate response isn’t necessarily to abandon the control but to understand and address that dependency.

Ask: What can influence this process without passing through the control we tested?

7. Murder During Discovery: Preserve the Scene

Fell’s seventh category reverses the timing assumption again. The victim is initially unconscious, not dead. The murderer joins those forcing entry and commits the killing amid the confusion. Everyone assumes the fatal act preceded discovery, although discovery provided the opportunity. For an investigator, this raises a different concern: what happens after the problem is reported?

Suppose a manager immediately “cleans up” the relevant records. Technology changes permissions. Finance corrects the supplier file. Each action may have a legitimate purpose, but investigators now face a changed environment. Do not mistake the condition you encounter for the condition that existed when the event occurred.

Contain ongoing harm, but document interventions and preserve pre-change evidence wherever possible. Identify who accessed relevant records after the allegation and what they changed. Helpful intent should not remove an action from the chronology.

Action: Include the response to discovery in the investigation, not merely the events preceding it.

What the CCO and Board Should Take Away

Carr’s categories suggest a discipline for compliance: separate the event from its explanation. Carry that discipline into your next program review, including a DOJ ECCP or COSO-based assessment. Select a closed investigation and ask whether its conclusion addressed the original assumptions, the evidence that challenged them, and the conditions that allowed the event.

For the CCO, the practical task is to connect findings to corrective action. Establish ownership, define what successful remediation means, and test whether the change addresses the demonstrated cause. For directors, move beyond asking whether the control existed. Ask management: What did the investigation establish about how the control actually operated, and what evidence supports the proposed fix?

Never close a locked-room compliance problem with the statement, “That could not have happened.” That statement belongs at the beginning of the investigation. In compliance, the locked door is not an explanation. It is an assumption to test.

Categories
Blog

Modern Philosophers and Compliance: Part 5 – Hans Jonas and Responsibility for the Future of Corporate Compliance

This week we have concluded our lengthy exploration of the philosophical underpinnings of the modern corporate compliance program. We have examined Hannah Arendt and her concepts of personal responsibility and how they relate to the modern compliance program; Simone de Beauvoir and the conditions for ethical action in a corporation; John Rawls and institutional justice and fairness in a corporate compliance program; and Jürgen Habermas and the governance of speaking up. In Part 5, we conclude by looking at Hans Jonas and the responsibility for the future of corporate compliance programs.

A corporate decision can continue affecting people long after its sponsors have moved on. Technology makes that possibility especially important. A system approved for a limited purpose can expand across business units, influence thousands of decisions, and create consequences that emerge gradually. Hans Jonas asks us to consider the responsibility that power entails.

For the Chief Compliance Officer (CCO), that perspective changes the approval question. What evidence supports proceeding, what harm could follow, and who will remain responsible as circumstances change? These questions connect ethical responsibility with the practical governance of technology, particularly artificial intelligence.

Technological Power Expands Responsibility

In The Imperative of Responsibility (1984), Jonas reconsidered ethics in light of technological power. His concerns included ecological destruction, nuclear threats, and genetic engineering. The scale and reach of human action created duties extending toward posterity and the environment.

His argument reaches beyond responsibility for an immediate transaction. Decisions can affect the conditions under which others will live, including people unable to challenge those decisions today. The ethical horizon must therefore extend beyond the decision-maker’s own interests and present relationships.

The application to corporate compliance is an interpretation of that argument. Jonas did not write an AI approval checklist. His philosophy nevertheless provides a reason to examine the duration, scale, and reversibility of technological choices. A company’s responsibility should reflect the consequences its capabilities make possible.

This perspective complements the earlier Enlightenment chapters. Evidence and clear reasoning remain essential. Jonas asks what responsibilities follow when the organization can act on that knowledge at a scale whose full consequences remain uncertain. For compliance, the answer begins with disciplined anticipation and continues throughout the activity’s life.

The Approval Whose Consequences Keep Growing

What do you think about the following situation? A multinational company purchases an AI tool to prioritize third-party due diligence. The tool ranks potential intermediaries using corporate records, transaction information, and public data. During a pilot, it reduces the time required to identify files for additional review.

Management approves a broader deployment. Over the following year, procurement teams begin treating low-risk scores as permission to abbreviate diligence. The vendor changes the model. The company expands into countries poorly represented in the original testing. Responsibility for reviewing performance splits among procurement, technology, and compliance.

Later, an investigation finds that several intermediaries with incomplete ownership records received low-risk scores. The model treated missing information as weak evidence of risk, while reviewers interpreted the scores as evidence that meaningful checks had been completed. No one had tested that assumption in the new markets.

The scenario does not establish that AI inevitably weakens diligence. It shows how a limited approval can take on a different operational meaning. A prioritization tool became a basis for reducing scrutiny. Changes in use, data, and responsibility accumulated after the initial decision.

Jonas helps the CCO frame the governance issue. The approval must account for how the system could develop and what its outputs could enable. Responsibility includes the conditions for expansion, the information needed to detect failure, and the authority to intervene before harm spreads.

The DOJ Connection Through Emerging Risk

The Department of Justice’s Evaluation of Corporate Compliance Programs (ECCP) explicitly addresses emerging technology. It asks how companies assess AI’s impact on criminal-law compliance, integrate technology risk into enterprise risk management, and address unintended consequences and misuse. It also examines controls supporting trustworthy, reliable use.

These inquiries make technology governance part of the compliance effectiveness assessment. A company using AI within its own compliance function should apply the same discipline it expects from business operations. The stated purpose of improving compliance does not establish that the tool works appropriately.

In our question above, the CCO should define the approved use precisely, as mission creep is always to be avoided. Prioritizing review is different from authorizing a third party. The decision record should explain what the score means, what it cannot establish, and which diligence requirements remain mandatory. Users need instructions that preserve those distinctions under commercial pressure.

Changes should trigger review according to their significance. A new market, a material vendor update, or a proposal to automate approvals may require additional testing and authorization. The company should assign an accountable owner who can obtain the necessary evidence across functions. Shared participation works best when responsibility for the final decision remains clear.

Uncertainty Calls for Proportionate Safeguards

Companies rarely possess complete information before introducing a technology. See generally Andrew McBride in Recommended Practice for Buying & Selling Compliance Technology, which is based on surveys of compliance technology buyers and vendors. Governance must make uncertainty visible and connect it to a defensible decision. The relevant questions include the severity of possible harm, the number of people affected, the ability to detect errors, and the possibility of reversing the consequences.

A tool that suggests training topics raises different concerns than one that determines which allegations to investigate. The latter can affect whether misconduct is detected at all. Its potential benefit should be assessed alongside the consequences of overlooking a credible concern.

For the third-party tool, a practical safeguard would be to sample low-risk classifications for independent review. Testing only the files the model flags leaves false reassurance largely unexamined. The company should also assess how missing records, unfamiliar languages, and changes in business conditions affect performance.

Deployment can be limited while those questions are tested. Appropriate measures might include restricted uses, defined populations, additional review, or a delay where critical evidence is missing. These are proposed governance responses to the hypothetical. Their suitability depends on the use case and the harm at stake.

The business case should include the cost of maintaining those safeguards. A project whose expected savings depend on eliminating the review needed for reliable operation has an unresolved design problem. Compliance should make that tradeoff explicit before approval and when the project’s economics change.

Turning Responsibility into Continuing Governance

The NIST AI Risk Management Framework provides a voluntary approach to managing AI risks. Its core functions are Govern, Map, Measure, and Manage. Together, they offer an organizational structure for understanding uses and impacts, evaluating risks, and determining responses throughout the AI lifecycle.

Applied to our hypothetical, governance assigns ownership and approval authority. Mapping identifies where the model operates, who relies on its scores, and who could be harmed by error. Measurement tests performance under relevant conditions. Management determines whether to proceed, add safeguards, restrict use, or suspend the tool. These activities should inform one another as evidence changes.

ISO/IEC 42001:2023 specifies requirements for establishing, implementing, maintaining, and continually improving an AI management system. Its relevance here is the organizational discipline of sustained responsibility. The company needs repeatable processes that survive personnel changes and remain connected to actual use.

These frameworks serve different purposes from DOJ’s prosecutorial guidance. Adopting a framework or obtaining certification does not establish compliance with every applicable law or prove that a particular deployment is effective. The company still needs evidence that its controls address the risks of its own activities.

The practical objective is to maintain a record that connects the approved purpose, responsible people, test results, changes, incidents, and remedial decisions. That record enables the next owner to understand why the system was approved and what conditions remain essential to its continued use.

Intervention Must Remain Possible

Responsibility becomes difficult to exercise when the organization cannot change course. Before deployment, determine who can suspend the system, what circumstances require escalation, and how business will continue during an interruption. A fallback process must be sufficiently resourced to operate when needed.

In the hypothetical, repeated unexplained low-risk scores involving missing ownership records could trigger restricted use and a review of affected files. The response should examine past decisions and current performance. Correcting the model does not resolve every consequence of earlier reliance on it.

Vendor arrangements also matter. (See McBride, above.) The company should seek information and contractual provisions appropriate to its risks, including notice of material changes, access to relevant performance evidence, and cooperation with investigations. When adequate visibility is unavailable, decision-makers should account for that limitation in deciding whether and how to use the tool.

Human review requires similar scrutiny. A named reviewer adds little protection if that person lacks time, training, supporting information, or authority to question an output. Test whether reviewers can identify errors and whether their interventions produce corrective action. Human responsibility needs operational support.

Board Oversight Must Extend Beyond Launch

Boards need a view of material technology risks over time. Approval-stage reporting often emphasizes expected benefits. Subsequent oversight should examine whether those assumptions remain valid, whether the use has expanded, and whether the organization retains the resources and authority needed to manage it.

The ECCP examines the information used in board oversight and compliance access to governing authorities. For significant AI deployments, the CCO can use those channels to report unresolved limitations, incidents, changes in use, and overdue corrective actions. Technical detail should explain a decision the board needs to understand.

Directors should ask whose interests the business case omits. Future customers, workers, communities, or business partners may bear costs not reflected in the current project budget. The analysis should consider foreseeable consequences and explain material uncertainties without pretending to predict every outcome.

Accountability should also survive the original sponsor’s departure. Assign continuing ownership, require documented handovers, and maintain review obligations through reorganizations and vendor changes. A system’s effects may persist for years. Its governance should not depend on one individual remembering the conditions attached to launch.

Five Key Jonas Takeaways for the Compliance Professional

  1. Assess consequences across time and scale. Consider who could be affected, how harm might accumulate, and whether decisions can be reversed. Include foreseeable effects beyond the immediate business case.
  2. Define the approved use and review material changes. Specify what a system may do, what its outputs establish, and which decisions require human authorization. Reassess expansion, vendor updates, and changes in operating conditions.
  3. Match safeguards to uncertainty and potential harm. Test the errors that routine monitoring could miss. Use staged deployment, independent review, or restrictions where the evidence does not support broader reliance.
  4. Preserve the ability to intervene and remediate. Establish suspension authority, workable alternatives, and a process for reviewing past decisions. Verify that human reviewers have the resources and authority to act.
  5. Make responsibility endure beyond the project team. Maintain ownership, evidence, and review obligations through organizational change. Give the board a clear account of unresolved risk and the decisions required.

Jonas brings our series to a fitting conclusion. Arendt asks who exercises judgment. Beauvoir asks whether people can act on it. Rawls tests the fairness of the rules, and Habermas examines whether concerns influence decisions. Jonas extends responsibility to the consequences that outlast those discussions and to people who cannot participate in them.

Together, these perspectives give compliance professionals a practical agenda for governing corporate power. Build processes that let people question, decide, explain, and correct their actions. Then ask the final board question: what obligations will this decision leave to others, and what have we put in place today to meet them?